

SBOM software helps you generate, manage, and analyze software bills of materials to get complete insight into every component in your codebase. If you’re responsible for software security, compliance, or auditing, finding the best SBOM software is essential to reduce risk, defend against vulnerabilities, and meet evolving regulatory demands.
This guide will help you quickly compare top SBOM solutions, so you can choose the right fit for your team’s workflows and security priorities.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

SBOM Software Comparison Table
This comparison table summarizes pricing details for my top SBOM software selections:
Sorted by: Default
| Tool | Starting Price | Website | |
|---|---|---|---|
Best for scanning imported embedded SBOMs | 4.3 out of 5 | $350/month Free plan available | Book Demo |
Best for integrating compliance into pipelines | 4.7 out of 5 | $1,000/dev/year Free demo available | Website |
Best for developer-centric vulnerability detection | 4.6 out of 5 | $25/contributing developer/month Free plan + free demo available | Website |
Best for open source risk visibility | Not rated | Pricing upon request Free demo available | Website |
Best for multi-point software artifact attestation | 1.0 out of 5 | Pricing upon request Free demo available | Website |
Best for continuous vulnerability monitoring | Not rated | Pricing upon request Free demo available | Website |
Best for automated component risk identification | Not rated | $1,200/year Free demo available | Website |
Best for supply chain integrity verification | Not rated | Pricing upon request Free demo available | Website |
Best for dependency lifecycle management | Not rated | Pricing upon request Free plan + free demo available | Website |
Best for verifying supplier component claims | Not rated | Pricing upon request Free demo available | Website |


Best SBOM Software Reviews
Below are my detailed summaries of the best SBOM software that made it onto my shortlist. My reviews offer a detailed look at the features, best use cases, and integrations of each platform to help you find the best one for you.
 Best for scanning imported embedded SBOMs
- Free plan available
- From $350/month
Visit WebsiteCustomer Rating:4.3/5
Aikido Security surfaces CVE details and fix paths per dependency. Aikido Security is a DevSecOps code security platform that combines dependency scanning, SBOM generation, container image scanning, license risk analysis, and vulnerability detection across source code, containers, and embedded systems.
Who Is Aikido Security Best For?
Aikido Security is a strong fit for DevSecOps teams that need to scan, monitor, and export SBOMs across source code, containers, and embedded systems from a single platform.
Why I Picked Aikido Security
I picked Aikido Security as one of the best because it's the only tool I've found that lets you upload self-generated embedded-system SBOMs directly via API, then immediately scans them for CVEs and license risks. That's a real advantage if you're working with Buildroot or Yocto builds, where your software inventory lives outside a standard repo. I also like that CycloneDX exports include optional VEX analysis, so you can flag exactly which vulnerabilities are exploitable and share that context with third parties.
Aikido Security Key Features
- Reachability analysis: Builds a call graph of modules, functions, and data flows to determine whether a vulnerable dependency is actually reachable from your application's entry points.
- CI/CD security gates: Enforces configurable security policies on pull requests and releases, blocking changes that exceed a defined severity threshold across SCA, SAST, IaC, secrets, and license scans.
- Multi-format SBOM export: Generates SBOMs in SPDX 2.3, CycloneDX 1.6, or CSV, with exports scopeable by repository, container image, team, or branch.
- License risk identification: Flags dual licensing, restrictive terms, and other license risks across repositories and container images, with plain-language obligation descriptions and adjustable risk scoring.
Aikido Security Integrations
Aikido Security offers documented marketplace integrations with GitHub, GitLab Cloud, Azure Repos, Bitbucket Cloud, Jira, Linear, GitHub Actions, GitLab CI/CD, Docker Hub, and GitHub Container Registry. Its REST API and webhooks support custom SBOM uploads and integrations.
Pros and Cons
Pros:
- Exports SPDX, CycloneDX, and CSV
- Reachability analysis reduces irrelevant alerts
- Scans imported embedded-system SBOMs
Cons:
- Historical container-image records are limited
- Yocto SBOMs require manual merging
Learn more about Aikido Security: Best for integrating compliance into pipelines
- Free demo available
- Up to $1,000/dev/year (billed annually)
Visit WebsiteCustomer Rating:4.7/5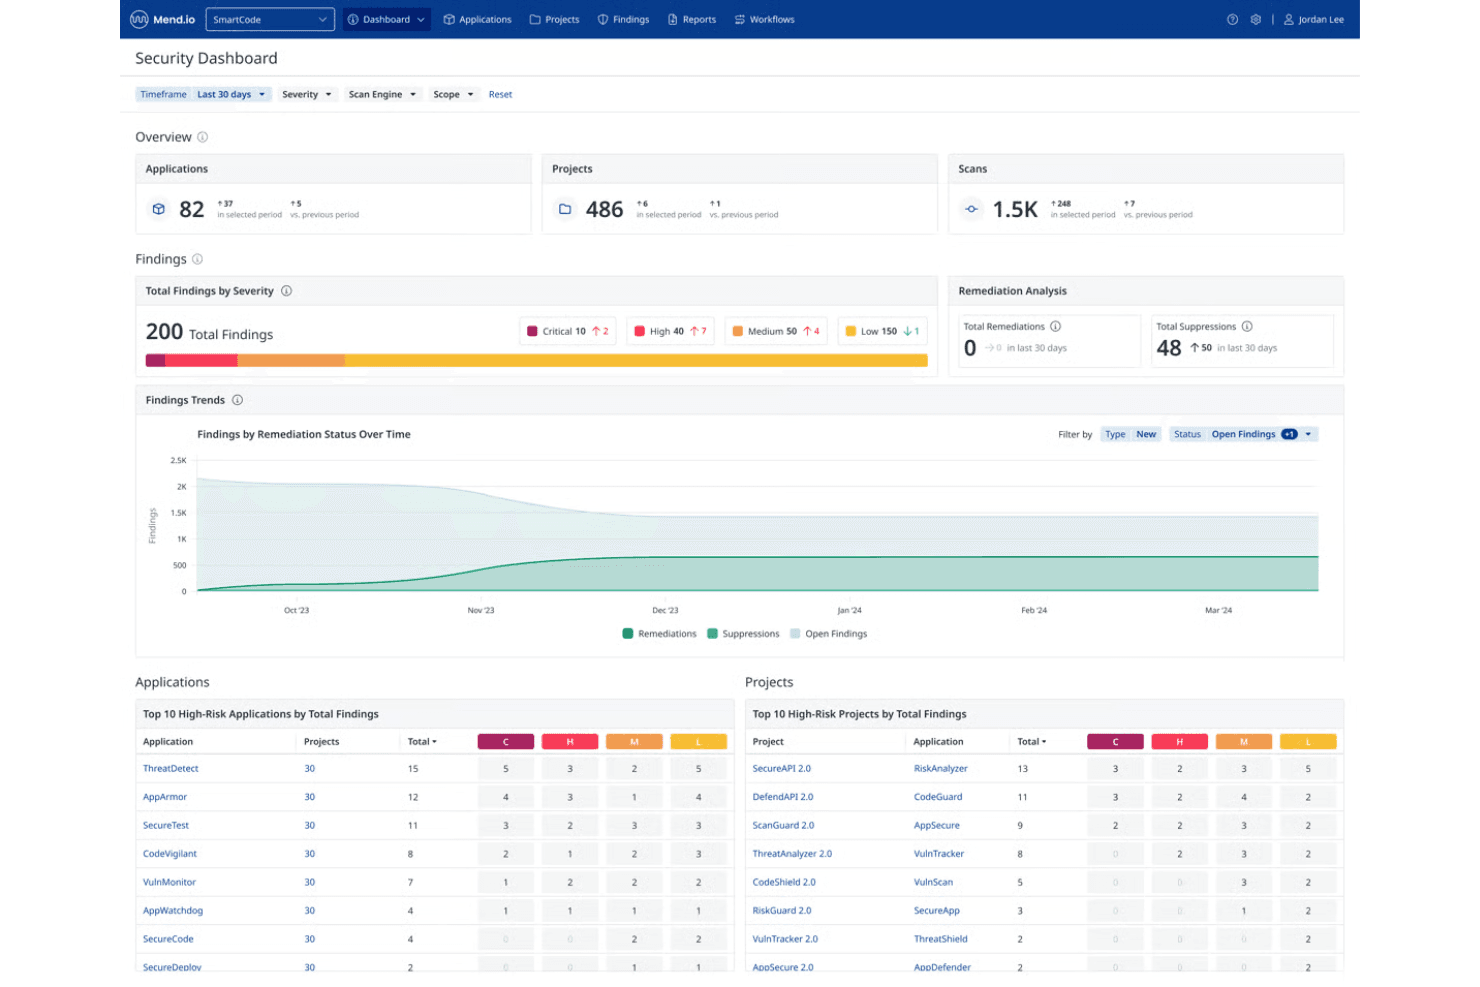
Mend.io maintains SBOMs, VEX data, SPDX/CycloneDX files, and third-party SBOMs. Mend AppSec is an application security platform that unifies SAST, SCA, and container scanning with automated SBOM generation in SPDX and CycloneDX formats, VEX data output, vulnerability prioritization, and license compliance.
Who Is Mend.io Best For?
Mend AppSec is a strong fit for DevSecOps teams and application security engineers who need SBOM generation and vulnerability compliance built directly into their CI/CD pipelines.
Why I Picked Mend.io
I picked Mend.io as one of the best because it builds SBOM compliance directly into the CI/CD pipeline rather than treating it as an afterthought. Every build automatically generates SPDX or CycloneDX SBOMs with VEX data attached, so downstream consumers can immediately see which vulnerabilities are actually exploitable. I also like that the same scan simultaneously feeds vulnerability prioritization using CVSS 4.0, EPSS, and reachability analysis, plus license compliance tracking through the Legal OS Inventory.
Mend.io Key Features
- SBOM generation at org, app, or project scope: Generate dependency SBOMs at organization, application, or project level, with options for per-project or aggregated output across multiple projects.
- Third-party SBOM import: Import SBOMs from tools like cdxgen and Syft in CycloneDX or SPDX formats, with imported projects then monitored for new vulnerabilities.
- Malicious-package detection: Scans open-source dependencies for threats including typosquatting, dependency confusion, data exfiltration, and backdoors.
- Legal OS Inventory: Tracks component licenses with risk scoring, violation alerts, and the ability to assign or override licenses at the organization level.
Mend.io Integrations
Mend.io integrates with GitHub, GitLab, Azure DevOps, Bitbucket, Jenkins, CircleCI, Docker, Amazon ECR, Azure Container Registry, and JFrog Artifactory. It also offers REST APIs for custom integrations and supports CI/CD workflows.
Pros and Cons
Pros:
- Tracks licenses alongside vulnerability triage
- Reachability helps prioritize exploitable dependency findings
- Builds emit SPDX/CycloneDX SBOMs with VEX
Cons:
- False positives can add manual vulnerability triage
- Imports omit source VEX and vulnerability data
Learn more about Mend.io: 3Best for developer-centric vulnerability detection
Snyk
- Free plan + free demo available
- From $25/contributing developer/month
Visit WebsiteCustomer Rating:4.6/5
Snyk scans dependencies, containers, IaC, and exports SBOMs in workflows. Snyk is a developer security platform that scans open source dependencies, containers, and infrastructure-as-code for vulnerabilities while generating and exporting SBOMs directly within developer workflows.
Who Is Snyk Best For?
Snyk is a natural fit for development teams that want security and SBOM generation built into their existing coding and CI/CD workflows.
Why I Picked Snyk
I've included Snyk in my top picks because it's the only tool on this list that surfaces vulnerability findings directly inside the IDE and pull request review, so developers catch open source risks before code ever merges. I particularly like that the Snyk CLI can both generate SBOMs in CycloneDX and SPDX formats and run snyk sbom test against an existing SBOM file to check it for known vulnerabilities.
On top of that, Snyk's Risk Score goes beyond raw CVSS severity by factoring in reachability, exploit maturity, and EPSS scores, which keeps my team focused on what actually matters.
Snyk Key Features
- License compliance scanning: Identifies the license type for every open source package in your project and flags licenses that conflict with your usage policies.
- Dependency graph: Visualizes your full dependency tree, including transitive dependencies, so you can trace exactly where a vulnerable package enters your codebase.
- Automated fix pull requests: Generates pull requests with version upgrades to remediate vulnerable dependencies directly in your repository.
- Container image scanning: Scans Docker and OCI images for vulnerable OS packages and application dependencies layer by layer.
Snyk Integrations
Integrations include GitHub, GitLab, Bitbucket, Azure Repos, Jenkins, CircleCI, GitHub Actions, Azure Pipelines, Jira, and Slack.
Pros and Cons
Pros:
- One-click fix creates PRs for vulnerabilities
- Exports SBOMs in CycloneDX and SPDX formats
- Supports 16 programming languages natively
Cons:
- CLI provides less SBOM detail than UI
- False positives trigger unnecessary vulnerability alerts
Learn more about Snyk: Best for open source risk visibility
- Free demo available
- Pricing upon request

Black Duck SCA identifies OSS components, license issues, and supply risks. Black Duck SCA is a software composition analysis tool that detects open source components across source code, binaries, containers, and code snippets, while managing vulnerability, license compliance, and supply chain risks across the SDLC.
Who Is Black Duck Software Composition Analysis Best For?
Black Duck SCA is a strong fit for enterprise security and legal teams managing large codebases with heavy open source usage across multiple languages and environments.
Why I Picked Black Duck Software Composition Analysis
Black Duck SCA earns its spot on my shortlist because of the depth of its open source risk visibility, which goes further than any other SCA tool I've evaluated.
What sets it apart is the Black Duck Security Advisories (BDSAs), where the Cybersecurity Research Center's analysts validate and augment CVE data, so my team isn't waiting weeks for NVD to catch up on newly disclosed vulnerabilities.
I also rely on its snippet scanning to catch partial open source code that carries license obligations but never shows up in a package manifest.
Black Duck Software Composition Analysis Key Features
- SBOM generation and export: Generate SBOMs in SPDX and CycloneDX formats directly from scan results for compliance reporting and audits.
- Binary scanning: Detect open source components in compiled binaries and containers where source code isn't available.
- Policy management: Define and enforce open source usage policies across teams, flagging violations automatically during builds.
- Upgrade guidance: Surface fix recommendations and suggested version upgrades for vulnerable components directly within scan results.
Black Duck Software Composition Analysis Integrations
Integrations include GitHub, GitLab, Bitbucket, Jenkins, Azure DevOps, GitHub Actions, Jira Software, Slack, Microsoft Teams, and JFrog Artifactory.
Pros and Cons
Pros:
- Policy management enforces open source rules
- Accurate detection of transitive dependencies
- Scans binary files without source code access
Cons:
- Scans run slowly on large codebases
- Initial setup is complex and involved
Learn more about Black Duck Software Composition Analysis: Best for multi-point software artifact attestation
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:1/5
Scribe Security shares SBOMs, signed attestations, VEX, and compliance evidence. Scribe Security Trust Hub is a SaaS platform for software supply chain security that generates, manages, and shares SBOMs alongside cryptographically signed attestations, VEX advisories, and SDLC compliance evidence across software producers and consumers.
Who Is Scribe Security Trust Hub Best For?
Scribe Security Trust Hub suits software development teams that need to prove code integrity and meet supply chain security compliance requirements for their customers or regulators.
Why I Picked Scribe Security Trust Hub
I picked Scribe Security Trust Hub because it's one of the few SBOM platforms that generate cryptographic attestations at every stage of the pipeline, not just at the point of release. What sets it apart is how it captures evidence across source control, CI/CD, and deployment, then aggregates those attestations at the artifact, product, and release levels.
I also like its policy-as-code guardrails, which can block releases that lack required SBOMs or signature verification before they ever reach production.
Scribe Security Trust Hub Key Features
- Centralized SBOM management: Create, store, and share SBOMs alongside associated vulnerabilities, license data, and exploitability scores in one place.
- VEX advisory authoring: Generate and publish Vulnerability Exploitability Exchange (VEX) advisories so consumers know which vulnerabilities in your SBOM are actually exploitable.
- Automated SBOM sharing workflows: Share SBOMs, compliance evidence, and attestations with customers or auditors through controlled, automated distribution workflows.
- SLSA-aligned build metadata tracking: Capture build environment records, including user identity, timestamps, and process metadata, in an audit-ready format to support SLSA and NIST SSDF compliance.
Scribe Security Trust Hub Integrations
Scribe Security Trust Hub integrates with Microsoft Entra ID, Bitbucket, CircleCI, GitHub, GitLab, Jenkins, and Travis CI. It's also available on the AWS Marketplace, and an API is available for custom integrations.
Pros and Cons
Pros:
- Enforces SLSA and SSDF compliance automatically
- Built-in SBOM sharing with external stakeholders
- Attests artifacts across every pipeline stage
Cons:
- English-only interface limits global teams
- Very few third-party user reviews available
Learn more about Scribe Security Trust Hub: Best for continuous vulnerability monitoring
- Free demo available
- Pricing upon request

Cybeats oversees SBOM lifecycles, license risk, vulnerabilities, and vendors. Cybeats is an SBOM lifecycle management platform that covers SBOM generation, storage, vulnerability lifecycle management, license risk assessment, and vendor SBOM ingestion across both SBOM Studio and SBOM Consumer products.
Who Is Cybeats Best For?
Cybeats is a strong fit for security engineers and procurement teams at product-manufacturing companies that need to both manage their own SBOMs and evaluate software risk from third-party vendors.
Why I Picked Cybeats
I picked Cybeats as one of the best because its SBOM Consumer product is built specifically for the vendor side of continuous vulnerability monitoring, which is rare. When a new CVE drops, real-time alerting fires against ingested vendor SBOMs automatically, so my team isn't manually re-checking component lists.
I also like the contextualized threat intelligence layer, which helps prioritize which vulnerabilities actually matter before my team spends time on remediation.
Cybeats Key Features
- SBOM inventory and management: Store, organize, and enrich SBOMs across your entire software portfolio in a centralized repository.
- Vulnerability lifecycle management with VEX and VDP: Track vulnerabilities from identification through remediation using VEX statements and vulnerability disclosure policies.
- Licensing risk assessment: Analyze open source license obligations across all software components to flag compliance issues before they escalate.
- SBOM sharing and exchange: Securely distribute SBOMs to customers or request them from technology providers directly through the platform.
Cybeats Integrations
Cybeats connects SBOM data with existing asset management systems, such as CMDBs or software inventory tools. It integrates with Veracode for SBOM management and offers a GitHub Action to automate SBOM imports into SBOM Studio.
A partnership with Keysight Technologies also brings binary analysis capabilities into the platform. An API is available for custom integrations.
Pros and Cons
Pros:
- Separate products for producers and consumers
- Built-in VEX workflow for vulnerability response
- Supports both CycloneDX and SPDX formats
Cons:
- No publicly listed pricing for budgeting
- Limited third-party native integrations available
Learn more about Cybeats: Best for automated component risk identification
- Free demo available
- From $1,200/year

Sonatype manages SBOM compliance, VEX notes, licenses, and vulnerability risks. Sonatype SBOM Manager is an SBOM compliance platform that automates SBOM ingestion, license management, VEX annotation, and component vulnerability monitoring across first- and third-party software.
Who Is Sonatype SBOM Manager Best For?
Sonatype SBOM Manager is a strong fit for security and compliance teams at software-producing enterprises managing large, complex software supply chains.
Why I Picked Sonatype SBOM Manager
Sonatype SBOM Manager earns its spot on my shortlist because of how it automates component risk identification at scale across both first- and third-party software. I particularly like its VEX annotation workflow, which lets my team track the status and justification of each disclosed vulnerability directly within the SBOM.
Its component intelligence also validates vulnerabilities against Sonatype's own data, so I'm not chasing false positives across a sprawling component inventory.
Sonatype SBOM Manager Key Features
- CycloneDX and SPDX format support: Import and manage SBOMs across both major standard formats, with centralized storage for original and augmented versions.
- AI and Hugging Face model scanning: Inspect AI components and models across first- and third-party SBOMs to surface potential risks before they enter production.
- License obligation workflow: Generates a checklist of actionable tasks for each component and license to resolve open source compliance issues.
- CI/CD pipeline integration: Connects directly into existing pipelines via API to automate SBOM workflows and enforce compliance at every development stage.
Sonatype SBOM Manager Integrations
Integrations include Sonatype Lifecycle, Nexus Repository, Jenkins, GitHub, GitLab, Bitbucket, Jira, CircleCI, Bamboo, and Docker.
Pros and Cons
Pros:
- Built-in AI and Hugging Face scanning
- Supports both CycloneDX and SPDX formats
- Continuous vulnerability monitoring across ingested SBOMs
Cons:
- Policy customization requires a Sonatype Lifecycle license
- No publicly available pricing for budgeting
Learn more about Sonatype SBOM Manager: Best for supply chain integrity verification
- Free demo available
- Pricing upon request

Lineaje secures software supply chains with SBOMs, risk checks, and compliance. Lineaje is a full-lifecycle software supply chain security platform that covers SBOM generation, contextualized risk assessment, self-healing builds, third-party vendor risk management, and regulatory compliance across your entire software portfolio.
Who Is Lineaje Best For?
Lineaje is a strong fit for security and DevSecOps teams at software-producing organizations that need end-to-end visibility into their open source and third-party component risks.
Why I Picked Lineaje
Lineaje earns its spot as one of the best on my shortlist because its supply chain integrity capabilities go well beyond SBOM generation. What I find compelling is geo-provenance tracking, which flags components based on their country of origin and highlights tamper risks before they reach a build.
I also like the self-healing build feature in SBOM360, which auto-fixes vulnerable dependencies in source code and containers rather than just reporting them.
Lineaje Key Features
- SCA360 contextual risk assessment: Scan code and containers within your security boundary, then unify and prioritize vulnerability findings by reachability, severity, exploitability, and maintainability.
- SBOM360 Hub SBOM management: Create, ingest, publish, update, and privately share SBOMs and VEX statements with customers, with search across 170 attributes.
- Third-party risk manager: Ingest and auto-validate vendor SBOMs against industry regulations, track risk across software versions, and identify zero-days in supplier software.
- Gold Open Source catalogue: Access a curated library of vulnerability-free, fully-attested open source packages and container images before they enter your build pipeline.
Lineaje Integrations
Lineaje has a documented partnership with Opsera that combines supply chain intelligence with CI/CD pipeline orchestration, enabling automated vulnerability remediation and secure image delivery. SCA360 is designed to integrate with existing scanning tools to unify findings across source code and containers.
Pros and Cons
Pros:
- Strong federal and regulatory compliance support
- Auto-generates fix plans for vulnerabilities
- Deep provenance and tamper detection capabilities
Cons:
- Multi-product portfolio can feel overwhelming initially
- Limited third-party reviews and community feedback
Learn more about Lineaje: Best for dependency lifecycle management
- Free plan + free demo available
- Pricing upon request

Endor Labs detects dependency risks, SBOM gaps, malicious packages, and secrets. Endor Labs is an application security platform built around software composition analysis (SCA), SBOM generation and management, dependency lifecycle tracking, malicious package detection, and secrets detection across source code, containers, and CI/CD pipelines.
Who Is Endor Labs Best For?
Endor Labs suits AppSec and DevSecOps teams that need SBOM compliance reporting alongside continuous dependency monitoring in a single platform.
Why I Picked Endor Labs
I picked Endor Labs as one of the best because its approach to dependency lifecycle management goes well beyond basic SBOM generation. The SBOM Hub centralizes first- and third-party SBOMs in one place, supports both CycloneDX and SPDX formats, and plugs into CI pipelines to auto-generate an updated SBOM every time a new version ships.
What I find most useful is the continuous risk monitoring: once a dependency is tracked in the Hub, Endor Labs automatically updates its risk profile as new CVEs and security advisories are published, without requiring you to recreate the SBOM from scratch.
Endor Labs Key Features
- Malicious package detection: Scans open source packages for typosquatting, dependency confusion, and obfuscated exfiltration scripts before they're imported into your codebase.
- Package Firewall: Blocks vulnerable and malicious packages before they reach developer machines or CI pipelines, enforcing allow/deny policies at the point of ingestion.
- VEX generation: Produces Vulnerability Exploitability eXchange (VEX) documents alongside SBOMs to declare which vulnerabilities are not exploitable in your specific application context.
- Upgrade impact analysis: Maps the blast radius of a dependency upgrade across your codebase before you apply it, so you can assess breaking changes before committing to a fix.
Endor Labs Integrations
Integrations include GitHub, GitLab, Jenkins, Jira, Slack, Bitbucket, Buildkite, CircleCI, Microsoft Defender for Cloud, and Vanta.
Pros and Cons
Pros:
- Centralized hub for first and third-party SBOMs
- Automated SBOM updates with new advisories
- Reachability analysis filters out unexploitable CVEs
Cons:
- Limited language support compared to some competitors
- Initial onboarding requires significant configuration effort
Learn more about Endor Labs: Best for verifying supplier component claims
- Free demo available
- Pricing upon request

Finite State checks firmware, binaries, SBOMs, VEX docs, and compliance risks. At its core, Finite State is a product security and SBOM platform built around firmware and binary analysis, covering software composition analysis, vulnerability detection, VEX document generation, and compliance reporting.
Who Is Finite State Best For?
Finite State is a strong fit for product security engineers and supply chain risk managers at hardware manufacturers who need to validate the accuracy of third-party supplier SBOMs against what's actually running in firmware.
Why I Picked Finite State
I've included Finite State in my top picks because it's the only SBOM tool I've used that lets my team actually verify what a supplier says is in their firmware against what binary analysis finds. It's binary SCA scans firmware images directly, so I don't have to trust supplier-provided SBOMs at face value.
When there's a mismatch, I can pull component-level evidence to back it up, which is something most source-code-only tools simply can't do.
Finite State Key Features
- VEX document generation: Create Vulnerability Exploitability eXchange documents to communicate the exploitability status of CVEs tied to specific products.
- Multi-format SBOM export: Generate and export SBOMs in both CycloneDX and SPDX formats to meet different regulatory and customer requirements.
- Compliance reporting: Run automated compliance checks against frameworks like FDA cybersecurity guidance and IEC 62443 directly within the platform.
- CVE prioritization: Automatically score and rank vulnerabilities by severity and exploitability to help your team triage findings across large component inventories.
Finite State Integrations
Finite State offers native CI/CD integrations with Jenkins, GitHub Actions, and GitLab CI, along with CLI tools and a REST API for custom integrations. The platform also supports importing third-party scan results from tools like GitLab SAST, DAST, and Container Scan, which lets you consolidate findings from your existing security tooling into one place.
Pros and Cons
Pros:
- Strong regulatory compliance mapping for devices
- Automatic SBOM-to-firmware discrepancy detection
- Binary-level firmware scanning without source code
Cons:
- Scan processing times can be slow
- Limited applicability outside embedded firmware use cases
Learn more about Finite State:
Other SBOM Software
Here are some additional SBOM software options that didn’t make it onto my shortlist, but are still worth checking out:
- 11ManifestBest for automated supply chain documentation
- 12CybellumBest for product security across device portfolios
- 13XygeniBest for detecting active code tampering
- 14GitLabBest for built-in CI workflow compatibility
- 15CheckmarxBest for AI-powered vulnerability discovery
- 16AnchoreBest for policy-driven compliance automation
- 17FOSSABest for audit-ready due diligence reporting
- 18JFrog XrayBest for deep IDE integration support
- 19ChainguardBest for SLSA-compliant artifact provenance
- 20ONEKEYBest for connected device lifecycle coverage
How I Evaluate SBOM Software
I split my evaluation into two layers—the baseline capabilities a tool must deliver (like generating CycloneDX or SPDX SBOMs from containers and binaries) and the differentiators that determine which tool fits your specific pipeline, compliance mandate, or supply chain risk model.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score into a percentage. Each tool needs to achieve a minimum total score of 65% to be considered for inclusion.
- SBOM Generation: I check whether a tool can scan beyond just source manifests—generating SBOMs from container images, compiled binaries, and build artifacts matters when you're shipping pre-built software.
- Standard Format Support: Each tool should support SPDX and CycloneDX import and export, since customers and regulators will ask for SBOMs in specific formats you can't always predict.
- Vulnerability Detection: I look for correlation against multiple vulnerability databases (NVD, GitHub Advisory, OSV) rather than a single feed, plus clear risk scoring that helps prioritize what to patch first.
- License & Compliance Tracking: Tools earn higher marks when they go beyond detecting license types and offer a policy engine where you can set rules—like flagging AGPL components in proprietary builds automatically.
- SBOM Repository & Lifecycle Management: I evaluate how each tool stores and versions SBOMs over time, including whether you can diff two versions to spot unexpected dependency changes between releases.
- CI/CD & Toolchain Integration: Native plugins for platforms like Jenkins, GitHub Actions, and GitLab CI matter, but I also look for API access that lets platform engineering teams embed SBOM generation into custom pipelines.
Once I have a list of tools that meet this criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
VEX support is a major differentiator. When a CVE hits a library you ship but the vulnerable code path isn't reachable, you need a way to communicate that. VEX documents let you tell downstream consumers exactly which vulnerabilities apply, cutting false-positive noise. Binary and container analysis also separates vendors—tools that generate SBOMs from compiled artifacts cover pre-built software that source-only scanning misses. I also evaluate continuous vulnerability monitoring, where the tool alerts you when newly disclosed CVEs affect components in previously shipped releases.
Beyond Features
Deployment flexibility matters a lot in this space. Teams in defense or critical infrastructure often need air-gapped or self-hosted options, so I check whether a vendor supports those models alongside SaaS. Regulatory alignment is another factor I weigh—specifically whether the tool maps outputs to frameworks like EO 14028, NTIA minimum elements, or the EU Cyber Resilience Act. I also look at SBOM sharing capabilities, since many organizations need to distribute SBOMs to customers or ingest them from upstream suppliers to get full supply chain visibility.
How to Choose SBOM Software
It’s easy to get bogged down in long feature lists and complex pricing structures. To help you stay focused as you work through your unique software selection process, here’s a checklist of factors to keep in mind:
| Factor | What to Consider |
|---|---|
| FactorScalability | What to ConsiderWill the tool handle your codebase and dependency growth over time? Consider future product expansion and evolving team or regulatory requirements. |
| FactorIntegrations | What to ConsiderDoes it connect natively with your CI/CD, repositories, registries, and ticketing systems? Validate official integrations with core platforms in use. |
| FactorCustomizability | What to ConsiderCan you tailor workflows, policy rules, and reporting to fit your security process? Beware rigid tools built only for simple or generic workflows. |
| FactorEase of use | What to ConsiderWill your engineering, security, and compliance teams be able to use the tool without extensive training? Test with real workflows before deciding. |
| FactorImplementation and onboarding | What to ConsiderIs the deployment process straightforward, or are there complex infrastructure needs? Ask about migration, support, and time from purchase to value. |
| FactorCost | What to ConsiderAre pricing tiers clear, and how fast could costs ramp as you add users, pipelines, or artifacts? Factor in both upfront and recurring expenses. |
| FactorSecurity safeguards | What to ConsiderDoes the tool support secure deployment needs such as SSO, RBAC, or air-gapped installs? Check audit logging and compliance with internal policies. |
| FactorCompliance requirements | What to ConsiderCan the vendor document alignment with your industry mandates, like EO 14028, NTIA, or international standards? Request mapped evidence or attestations. |
What Is SBOM Software?
SBOM software automatically generates a software bill of materials (SBOM) that inventories all components, dependencies, and their licenses in a codebase or artifact.
These tools help teams track open-source and third-party libraries, monitor vulnerabilities, and maintain compliance with industry and regulatory requirements during the entire software development and deployment lifecycle.
Features
When selecting SBOM software, keep an eye out for the following key features:
- SBOM generation: Produces an up-to-date inventory of all software components, dependencies, and metadata by scanning source code, containers, or binaries.
- Format support: Offers import and export support for industry-standard SBOM formats such as SPDX, CycloneDX, and SWID for broad compatibility.
- Vulnerability detection: Correlates listed components against vulnerability databases, identifying known risks and alerting teams to issues throughout the software lifecycle.
- License compliance tracking: Identifies and tracks open-source and proprietary licenses, helping organizations spot potential conflicts and meet compliance requirements.
- CI/CD integration: Embeds into build pipelines, source repositories, and artifact registries to automate SBOM generation during continuous integration and deployment.
- SBOM repository: Provides secure, centralized storage for all generated SBOMs, enabling versioning, access control, and historical comparisons.
- Component diffing: Tracks changes between SBOM versions to highlight added, removed, or updated components across releases.
- Custom policy enforcement: Let teams define and automate security and license checks, blocking deployments that don’t meet organizational standards.
- SBOM sharing and distribution: Allows secure sharing of SBOMs with customers, partners, or regulators through dedicated portals or distribution mechanisms.
Benefits
Implementing SBOM software provides several benefits for your team and your business. Here are a few you can look forward to:
- Improved supply chain visibility: Gain insight into all software components and dependencies used in your products, reducing the risk of hidden vulnerabilities.
- Faster vulnerability response: Get real-time alerts when new CVEs affect your deployed components, so your team can prioritize and remediate threats quickly.
- Automated compliance: Meet regulatory and customer requirements with standardized SBOM formats and license tracking built into your development process.
- Reduced license risk: Quickly identify open-source license conflicts and obligations that could introduce legal exposure or compliance issues.
- Smooth collaboration: Share up-to-date SBOMs securely with internal teams, customers, and auditors to build trust and speed up communication.
- Change tracking and auditability: Track changes to components across releases, making it easy to audit software history and demonstrate due diligence.
- Deployment flexibility: Choose tools that fit your infrastructure, whether cloud-based, on-premises, or air-gapped, to align with your business and security needs.
Costs and Pricing
Selecting SBOM software requires an understanding of the various pricing models and plans available. Costs vary based on features, team size, add-ons, and more. The table below summarizes common plans, their average prices, and typical features included in SBOM software solutions:
Plan Comparison Table for SBOM Software
| Plan Type | Average Price | Common Features |
|---|---|---|
| Plan TypeFree Plan | Average Price$0 | Common FeaturesSupports basic SBOM generation, limited vulnerability scanning, manual exports, and community support. |
| Plan TypePersonal Plan | Average Price$10-$30/user/month | Common FeaturesIncludes advanced format support, individual license tracking, basic policy checks, and email notifications. |
| Plan TypeBusiness Plan | Average Price$40-$80/user/month | Common FeaturesAdds CI/CD integrations, centralized SBOM repository, automated compliance alerts, team management, and API access. |
| Plan TypeEnterprise Plan | Average Price$100+/user/month | Common FeaturesOffers dedicated onboarding, custom policy enforcement, air-gapped deployment, advanced RBAC, and priority support. |
SBOM Software FAQs
Here are some answers to common questions about SBOM software:
Do I need SBOM software if my team builds everything from scratch?
Yes, SBOM software is still valuable even if your team writes most code in-house. Most projects rely on third-party dependencies, open source software, or frameworks, and SBOM tools help track and manage these components for security and compliance. Tracking every software package is essential, as hidden security risks can exist within any development ecosystem.
How often should we update our SBOMs?
You should update your SBOMs with every release and whenever there are changes to your codebase or dependencies. This ensures your inventory is accurate and supports fast vulnerability responses when new vulnerabilities emerge. Keeping this up to date is a primary way SBOs help organizations defend against sophisticated supply chain attacks and handle security incidents.
Can SBOM software integrate with our existing CI/CD pipelines?
Yes, most SBOM tools offer plugins or API-based integration for popular CI/CD tools such as Jenkins, GitHub Actions, or GitLab CI. This enables automated SBOM generation, tracking of software dependencies, and security vulnerability checks as part of your deployment process. This automated data exchange provides a machine-readable inventory of every software product you deploy, whether running on Linux or other platforms.
What regulatory standards require SBOMs?
Regulations like the U.S. government Executive Order 14028, FDA premarket cybersecurity guidance, and the EU Cyber Resilience Act are driving the use of SBOMs. Many industries anticipate that outlining the minimum elements of a system—including license information—will become a contractual requirement for federal agencies and the broader federal government.
How secure is the data managed by SBOM software?
SBOM software can be deployed as SaaS, on-premises, or in air-gapped environments. Look for role-based access controls, encryption, and compliance certifications to align with your organization’s security policies and reduce data exposure risks.