

10 Best Drata Alternatives in 2026

Best Drata Alternatives Shortlist


The best Drata alternatives help your team automate evidence collection, manage GRC audits across multiple frameworks, and scale compliance without adding overhead. If you’re comparing alternatives, you’re likely looking for a tool to handle growing regulatory demands, integrate compliance with your other security technology, and provide reliable support when standards or audit expectations shift.
In this guide, I’ll break down which alternatives handle multi-framework complexity, automate routine compliance work, and deliver the kind of expert support IT leaders actually rely on—so you can find the right fit.
What Is Drata?
Drata is an automated security and compliance platform that helps IT and security teams manage ongoing compliance tasks. The platform collects evidence, monitors security controls, and supports audits for frameworks like SOC 2, ISO 27001, and HIPAA.
Drata integrates with cloud and IT systems to improve documentation and risk management, making it easier for organizations to meet regulatory requirements and maintain audit-ready compliance across multiple standards.
Why Trust Our Software Recommendations
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Compare the Best Drata Alternatives
This comparison table summarizes pricing details for my top alternative selections:
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for multi-framework audits at a flat rate | Free demo available | Pricing upon request | Website | |
| 2 | Best for managing 160+ frameworks without duplication | Free demo available | Pricing upon request | Website | |
| 3 | Best for unified privacy, TPRM, and AI governance | Free demo available | Pricing upon request | Website | |
| 4 | Best for compliance with a dedicated GRC expert | Free demo available | Pricing upon request | Website | |
| 5 | Best for enterprise GRC beyond SOC 2 | Free demo available | Pricing upon request | Website | |
| 6 | Best for compliance with in-house auditor support | Free demo + free trial available | Pricing upon request | Website | |
| 7 | Best for bundled VRM and compliance automation | Free demo available | Pricing upon request | Website | |
| 8 | Best for sales-cycle security reviews at scale | Free demo available | Pricing upon request | Website | |
| 9 | Best for AI-validated evidence collection | Free demo available | Pricing upon request | Website | |
| 10 | Best for enterprise multi-framework GRC at scale | Free demo available | Pricing upon request | Website |
Drata Alternatives Reviews
Below are my detailed summaries of the best alternatives, covering key features, pros and cons, and pricing to help you find the best one.
Scrut
Best for multi-framework audits at a flat rate
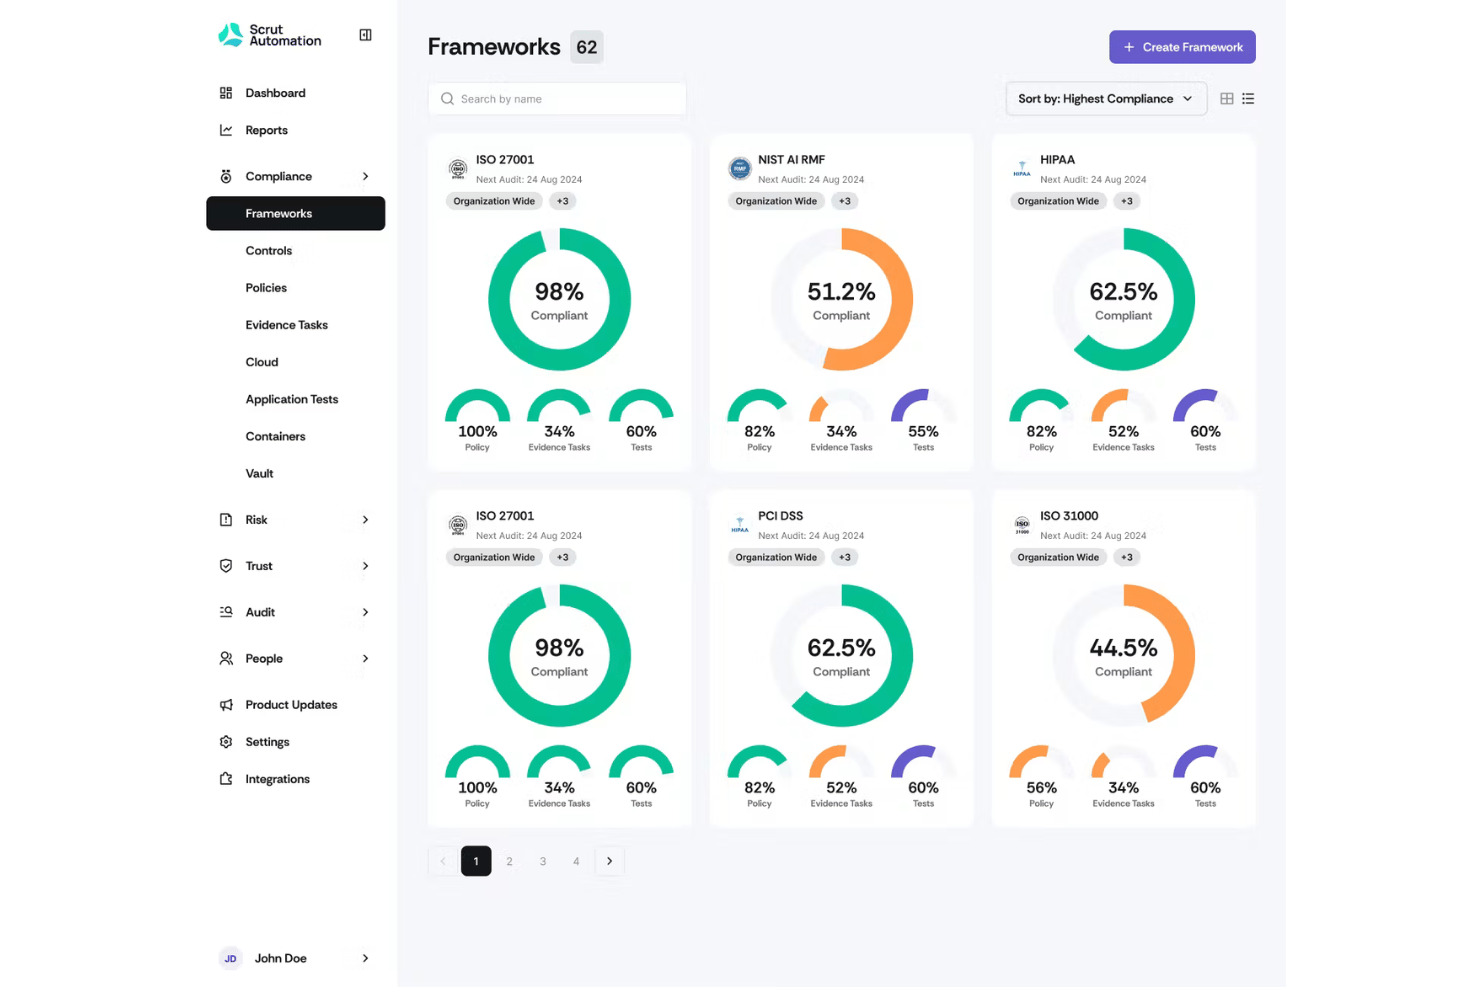
Scrut (Scrut Automation) is a cloud-based governance, risk, and compliance management platform designed for IT, security, and compliance teams who need to automate controls and improve audit preparation across multiple regulatory frameworks.
Who Is Scrut Best For?
Scrut works well for security and compliance teams in finance, healthcare, or SaaS that need to navigate complex and overlapping regulatory requirements without overwhelming their teams.
Why Scrut Is a Good Drata Alternative
I picked Scrut as one of the best options because it lets you handle multi-framework audits with straightforward pricing. I like that it automates compliance tasks and manages risk across regulatory standards in one cloud platform. That flexibility saves time when juggling overlapping frameworks and frequent audits.
Scrut Key Features
- Automated evidence collection: Gathers audit evidence continuously from connected cloud systems and operational tools.
- Custom control mapping: Maps internal policies and controls across multiple frameworks within a unified interface.
- Real-time risk dashboards: Displays consolidated risk postures, active threats, and open tasks in an interactive view.
- Vendor risk assessments: Tracks, evaluates, and documents third-party vendor risks through built-in questionnaires and automated workflows.
Scrut Integrations
Scrut offers native integrations with AWS, Microsoft Azure, Google Cloud Platform, Okta, GitHub, Jira, Freshservice, and Salesforce. An API is also available for custom integrations.
Pros and Cons
Pros:
- Audit-ready evidence library with version tracking
- Continuous control monitoring across environments
- Built-in policy templates for common frameworks
Cons:
- Limited documentation for some configuration tasks
- Workflow automation lacks advanced branching

Best for managing 160+ frameworks without duplication
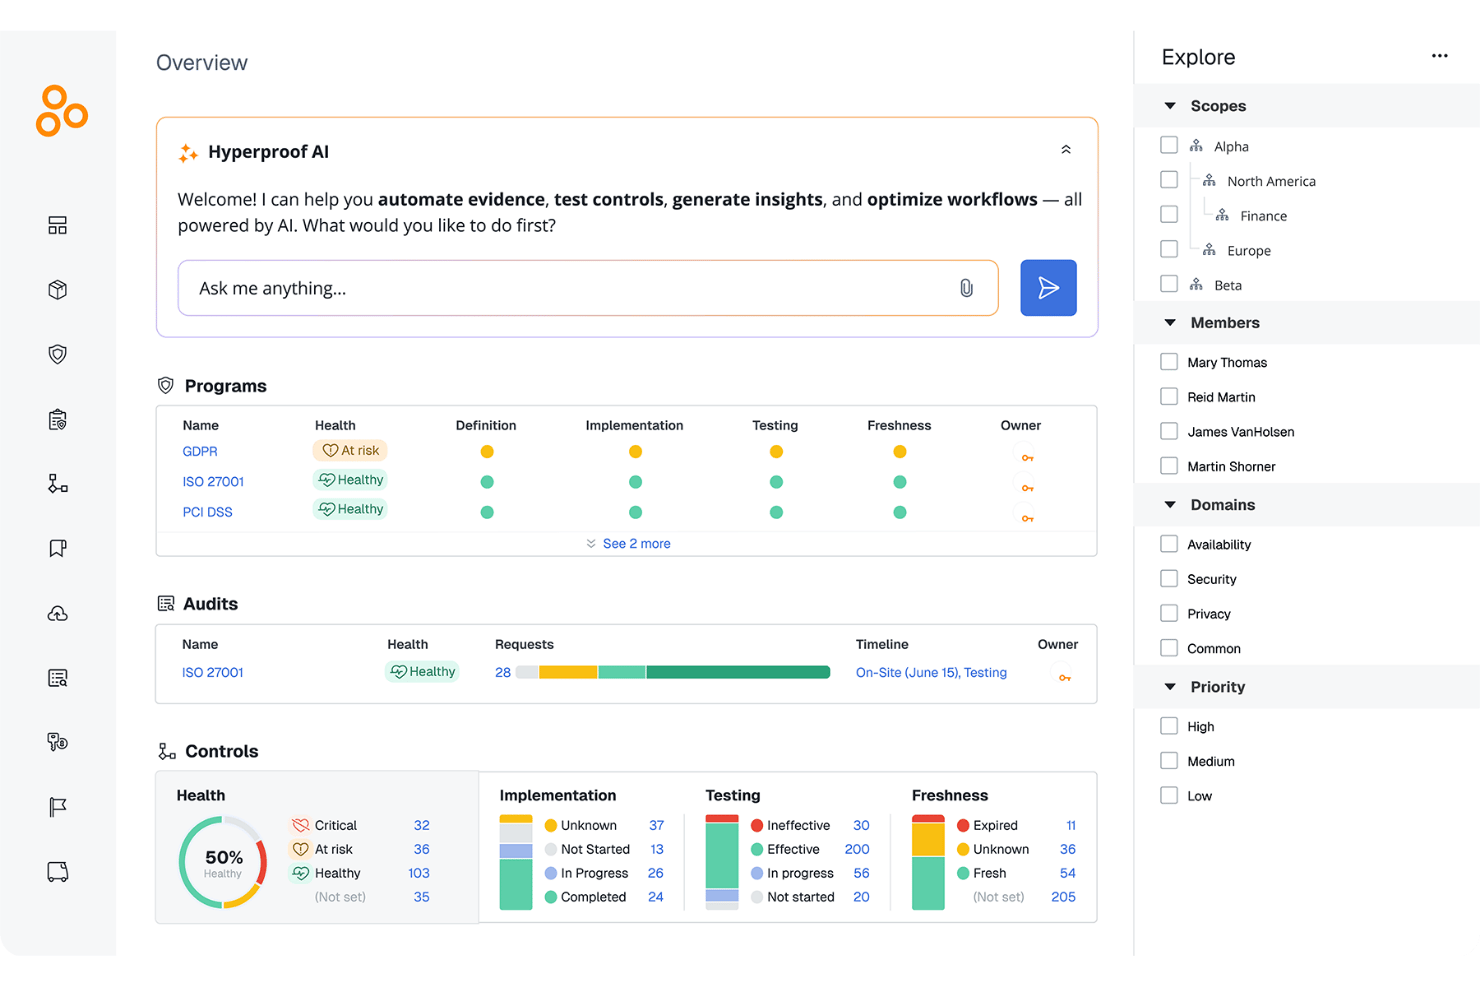
Hyperproof is a cloud-based platform designed for compliance, audit, and risk professionals who need a unified space to manage and automate complex risk management workflows.
Who Is Hyperproof Best For?
Hyperproof is best suited for mid-market and enterprise organizations with dedicated GRC teams that need to scale complex risk management programs and manage dozens of frameworks across multiple business units.
Why Hyperproof Is a Good Drata Alternative
I picked Hyperproof as one of the best because it helps manage over 160 regulatory frameworks without duplicate work. It excels at tying operational risk directly to control health, allowing enterprise security teams to track operational gaps and manage audit readiness in real time across localized regulatory landscapes.
Hyperproof Key Features
- Hypersync automated collection: Uses specialized connectors to sync continuous compliance evidence from connected cloud and developer platforms.
- Task assignment and workflow management: Assign tasks, set deadlines, and oversee progress for compliance activities across teams.
- Freshness & health tracking: Calculates evidence status automatically to alert control owners before audit artifacts expire or become stale
- Flexible scopes & organizational units: Enables multi-tenant oversight by grouping controls, frameworks, and evidence by specific business units, sub-brands, or geographic locations.
Hyperproof Integrations
Hyperproof AI offers native integrations with tools like AWS, Microsoft Azure, Google Drive, Confluence, Jira, Asana, and GitHub. It also supports custom integrations through SDK and API.
Pros and Cons
Pros:
- Tracks real-time compliance status in one dashboard
- Maps controls across multiple standards simultaneously
- Scales with complex architectures
Cons:
- Limited self-service support for troubleshooting issues
- Initial setup comes with a steep learning curve
OneTrust
Best for unified privacy, TPRM, and AI governance
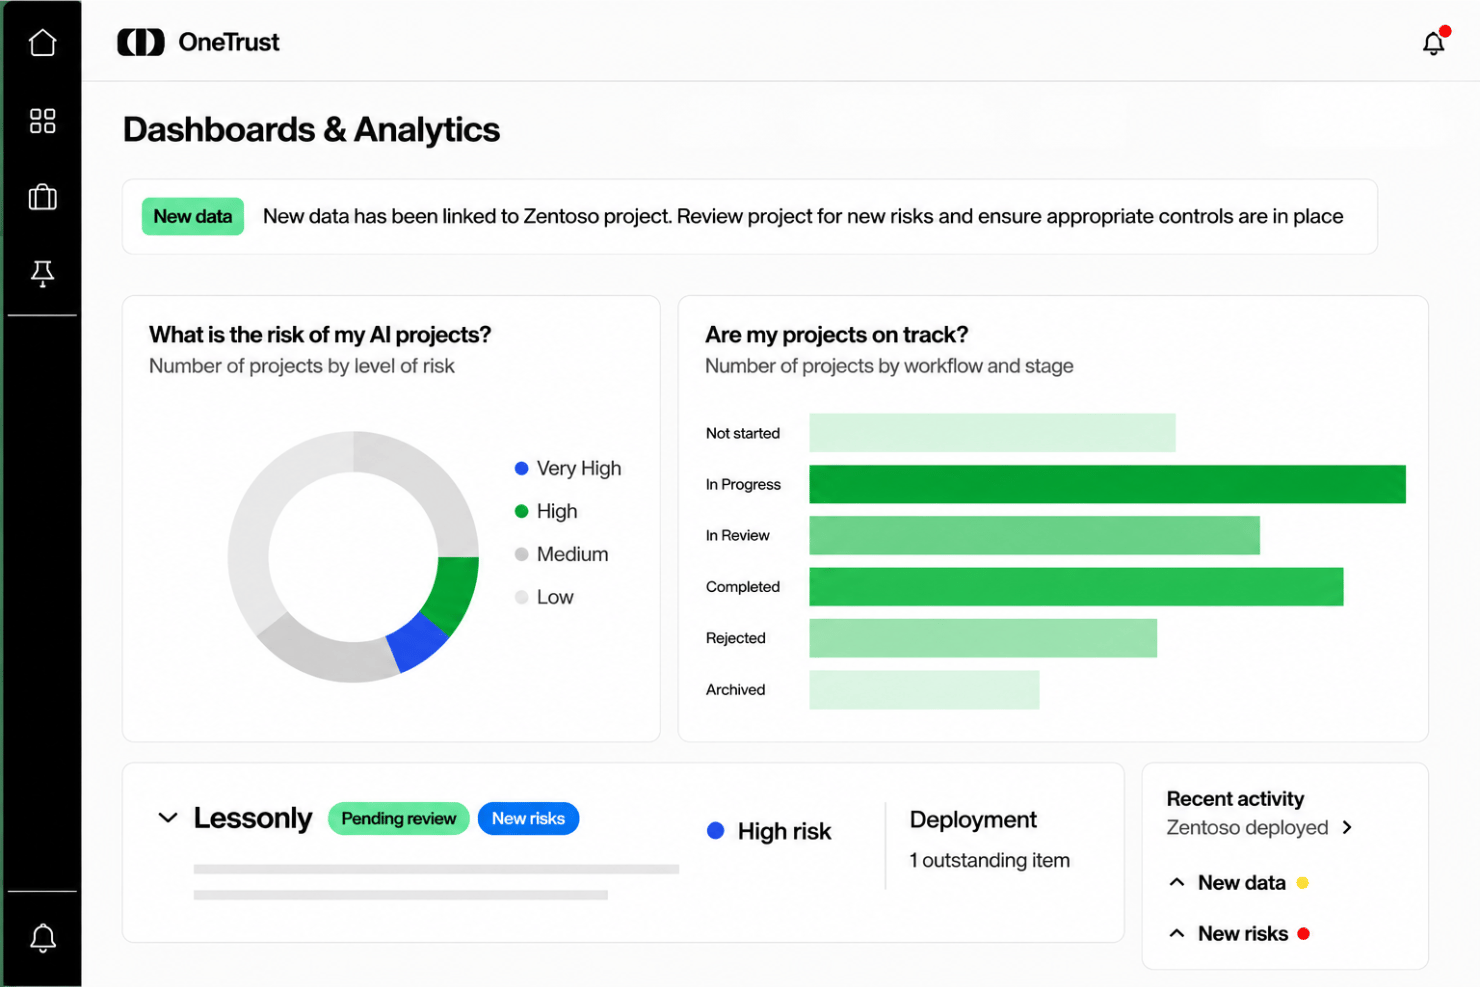
OneTrust is an enterprise trust management platform designed to unify privacy rights automation, regulatory consent, third-party risk, and compliance operations into a single operational architecture.
Who Is OneTrust Best For?
OneTrust is best suited for multinational corporations and large enterprises that need to enforce global data privacy laws alongside standard IT compliance frameworks.
Why OneTrust Is a Good Drata Alternative
I picked OneTrust as one of the best for organizations whose compliance requirements extend far beyond standard IT and cloud security audits. I have used it to centralize compliance workflows, stay current with privacy regulations, and manage complex vendor relationships globally. I like that OneTrust’s AI governance tools keep compliance aligned as regulations change across jurisdictions.
OneTrust Key Features
- Automated policy management: Keep policies up to date and accessible with built-in automation tools.
- Risk assessment engine: Perform structured risk assessments with customizable templates and scoring.
- Audit-ready reporting: Generate detailed, exportable compliance and risk audit reports on demand.
- AI data governance: Catalogs AI models across the organization to monitor regulatory risk, policy drift, and sensitive data leakage in AI pipelines.
OneTrust Integrations
OneTrust offers native integrations with Adobe, Microsoft 365, Snowflake, Acoustic, SAP, and Slack. An API is available for custom integrations.
Pros and Cons
Pros:
- Workflow builder supports custom compliance processes
- Automated evidence collection reduces manual workload
- Centralizes privacy, third-party risk, and AI compliance
Cons:
- Customer support response can be slow
- Non-intuitive navigation across modules

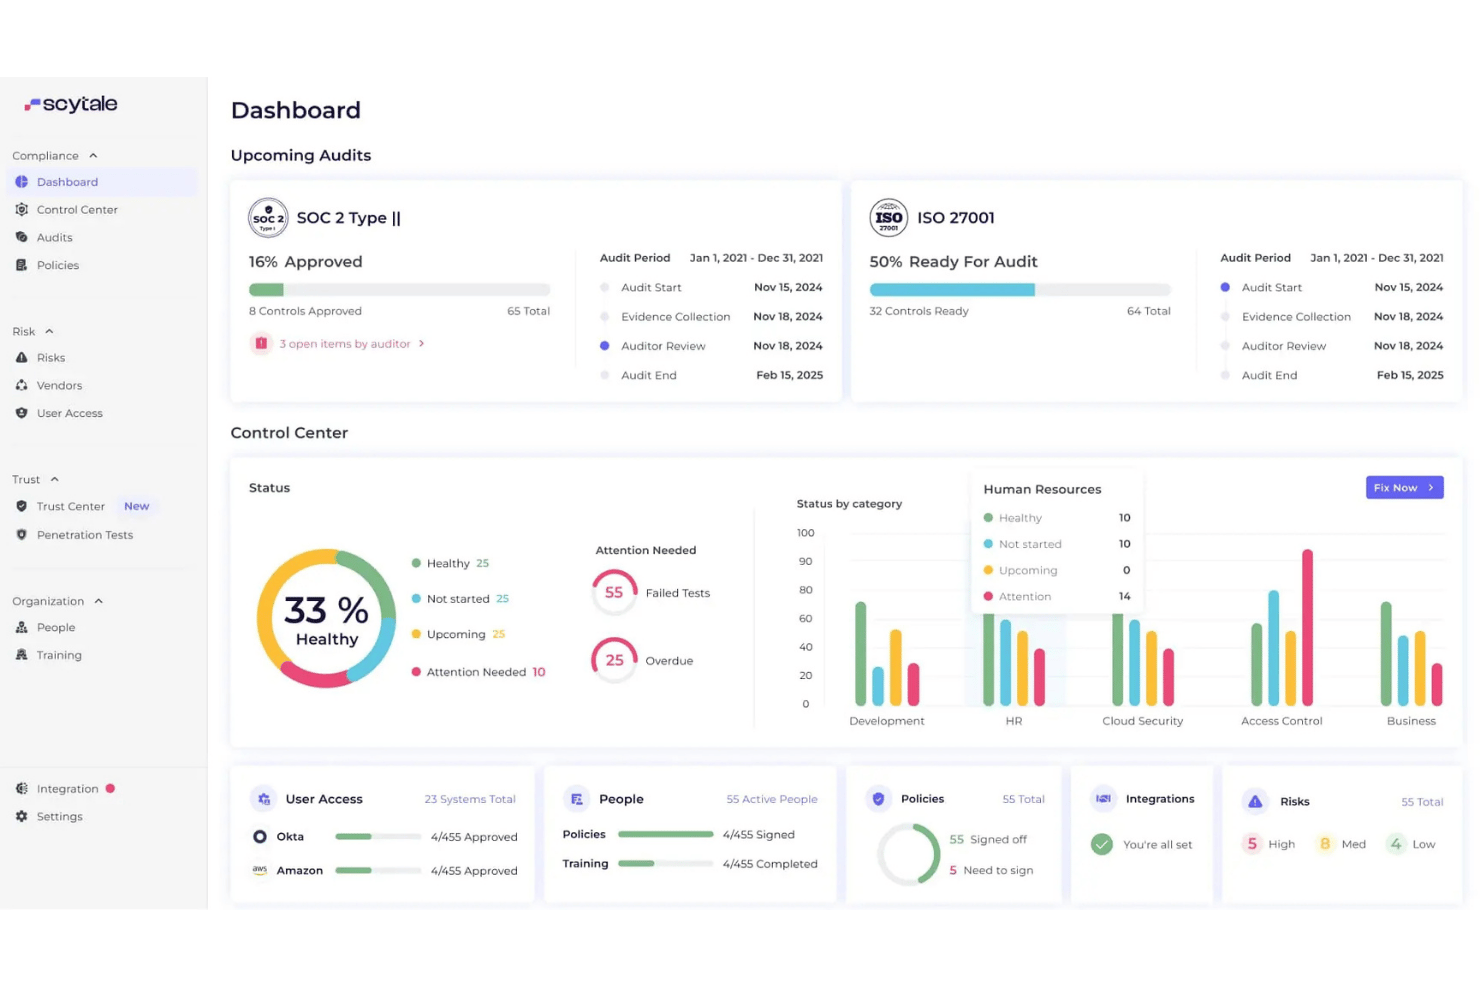
Scytale is a risk and compliance automation platform that helps compliance teams manage multiple frameworks, automate audit evidence collection, and centralize policy documentation.
Who Is Scytale Best For?
Scytale is a strong fit for IT, security, and compliance teams in regulated industries that want hands-on guidance managing audits and frameworks.
Why Scytale Is a Good Drata Alternative
I picked Scytale as one of the best because every client gets a dedicated GRC expert who actively guides our compliance journey, answers complex audit questions, and helps map requirements across frameworks. I like that they offer hands-on support to manage multiple standards at once.
Scytale Key Features
- Continuous access reviews: Tracks user access permissions across cloud systems and workspace applications to flag privilege risks automatically.
- Risk assessment templates: Provides structured templates for identifying and documenting risks.
- Centralized policy management: Stores, updates, and tracks all compliance policies in one location.
- Custom reporting: Generates reports tailored to various frameworks or audit requirements.
Scytale Integrations
Scytale provides 100+ integrations with tools like AWS, Google Workspace, Bob, Intercom, Lever, Microsoft Entra ID, and Vercel. An API for custom integrations is also available.
Pros and Cons
Pros:
- Customizable dashboard for real-time compliance status
- Automated workflows for policy and risk reviews
- GRC expert helps oversee compliance
Cons:
- Certain customizations require vendor involvement
- Public integration options remain unclear
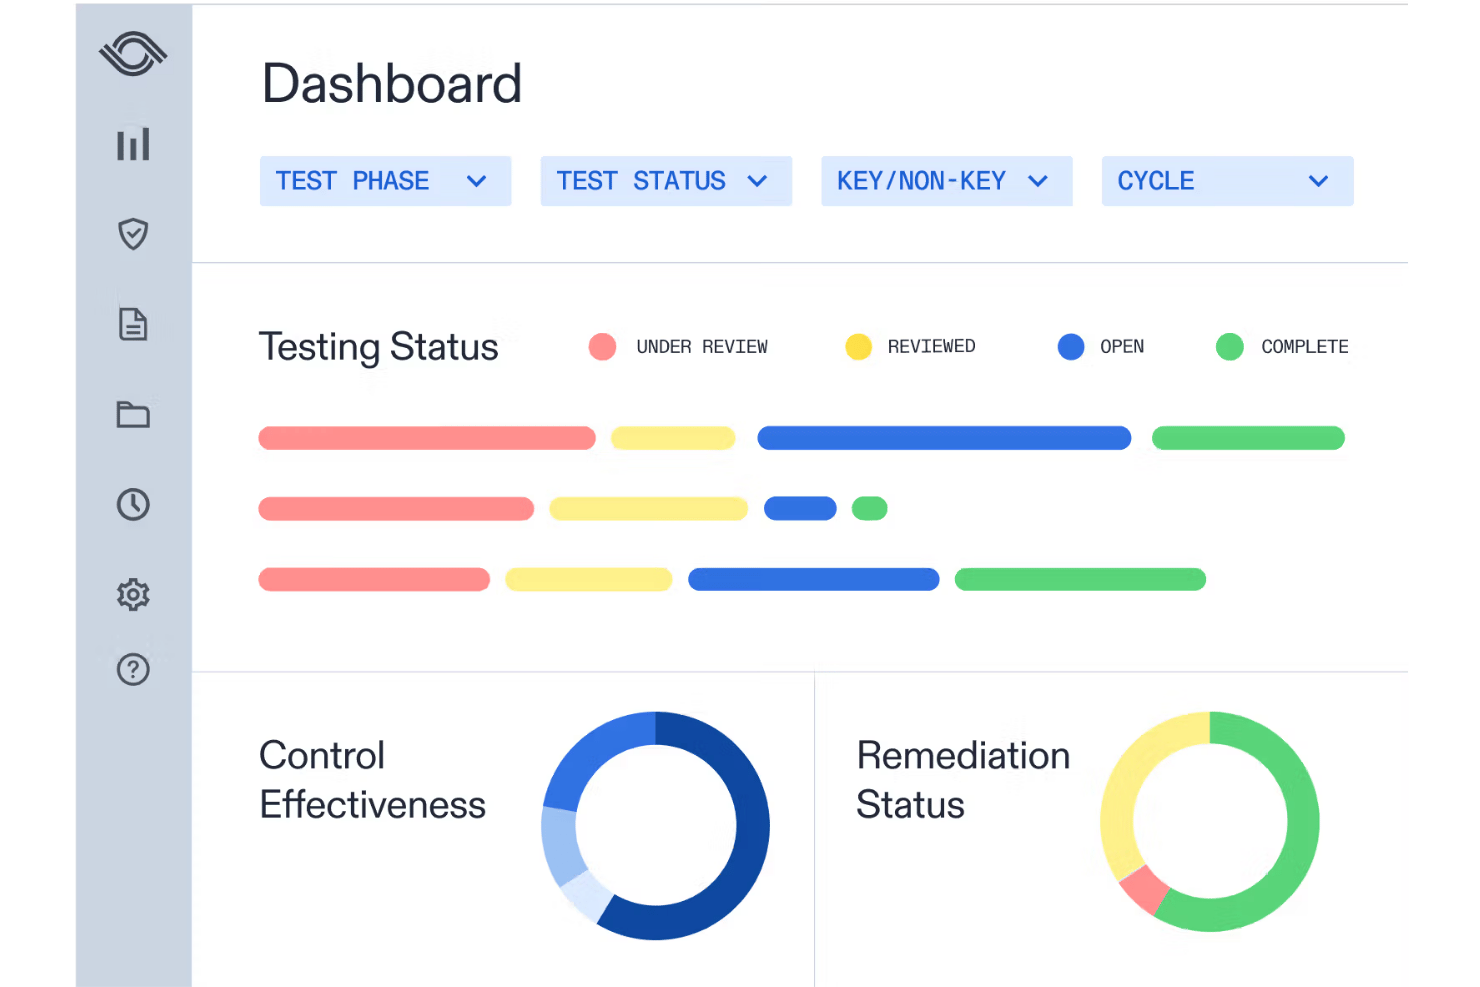
Optro is an enterprise GRC and AI governance platform that connects IT risk, internal audit, third-party risk, and continuous compliance into an agentic system of action.
Who Is Optro Best For?
Optro is a strong choice for mature enterprise organizations and public companies that need to connect SOX, IT compliance, and emerging AI risk frameworks across large, cross-functional departments.
Why Optro Is a Good Drata Alternative
I picked Optro because I rely on its enterprise-grade controls mapping and audit trails when managing multiple compliance frameworks. Its risk management tools make scaling GRC processes across departments straightforward, especially when regulations get complex for larger organizations. Optro is where I go when I need more than SOC 2 coverage.
Optro Key Features
- Connected risk architecture: Maps internal controls across enterprise risk management (ERM) modules to translate compliance drift into actionable operational insights.
- Custom reporting engine: Build tailored reports across frameworks, teams, and sites to meet audit or stakeholder requirements.
- Agentic AI & natural-language workflows: Use GRC-trained AI agents to automate control testing, draft narrative descriptions, and optimize issue remediation processes.
- Issue management module: Track, assign, and resolve compliance and risk issues from a central dashboard.
Optro Integrations
Optro integrates with AWS, Microsoft Azure, Google Cloud Platform, Snowflake, Jira, ServiceNow, Workday, and GitHub. An API and MCP for custom connections are also available.
Pros and Cons
Pros:
- Built for enterprise-scale risk management needs
- Includes audit-ready evidence collection and reporting
- Handles multi-framework compliance beyond SOC 2
Cons:
- Deployment and configuration require dedicated planning
- Interface may overwhelm smaller IT teams
Best for compliance with in-house auditor support
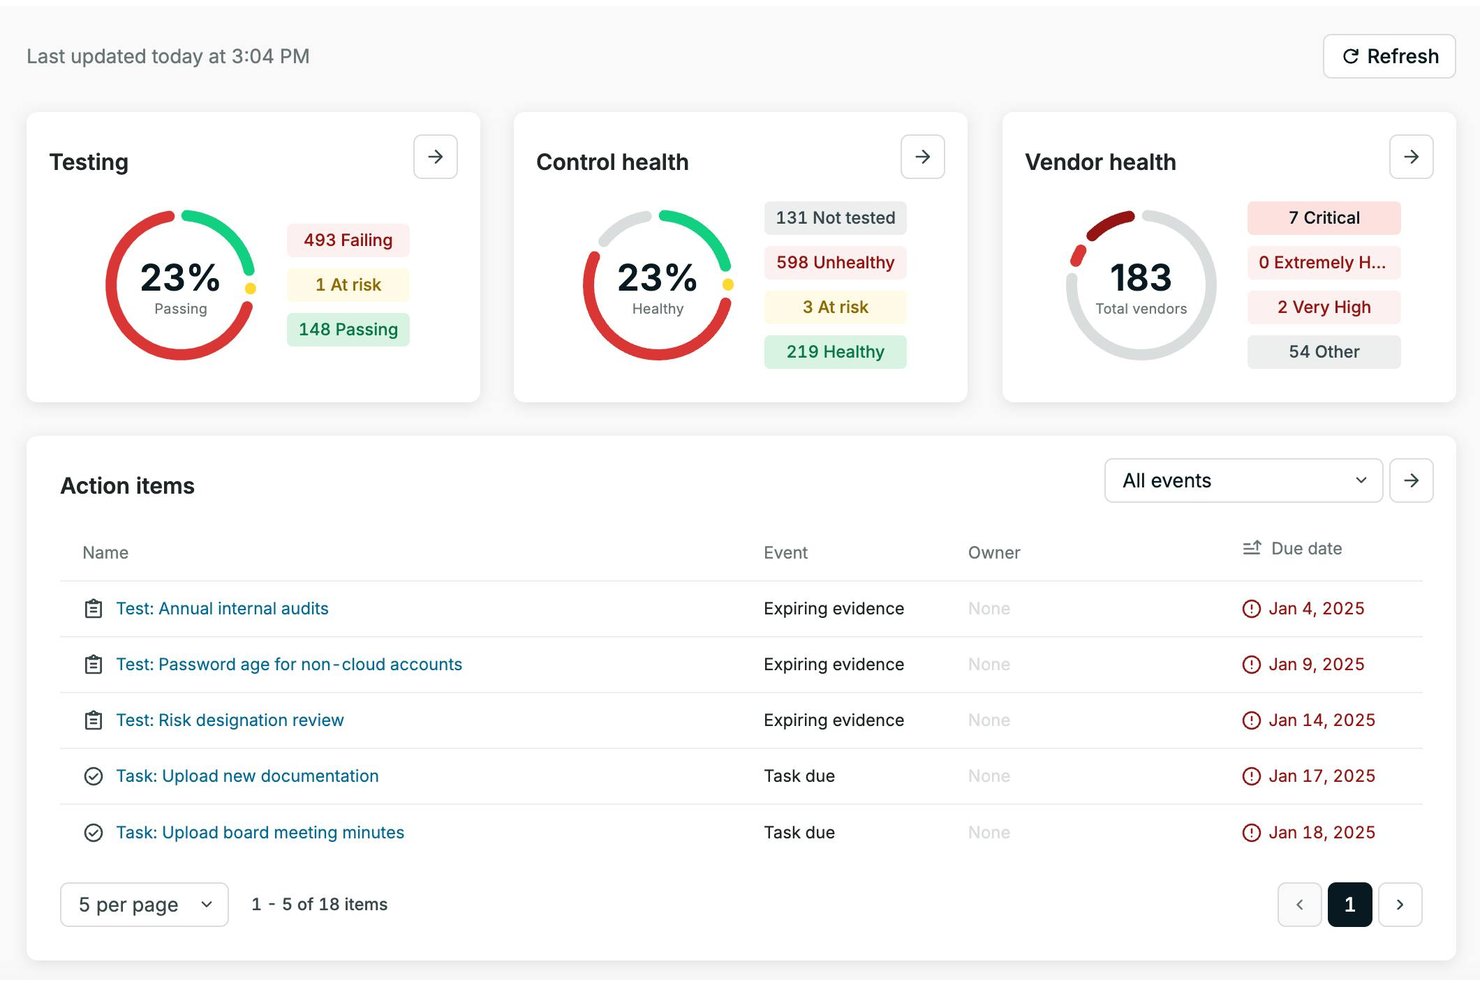
Secureframe is an automated security and compliance tool designed to help fast-scaling startups and mid-market companies achieve and maintain continuous audit readiness across major regulatory frameworks.
Who Is Secureframe Best For?
Secureframe is best suited for growing SaaS startups, IT teams, and mid-market organizations that need a guided, highly structured compliance automation platform supported by in-house compliance experts.
Why Secureframe Is a Good Drata Alternative
I picked Secureframe because it helps automate compliance workflows across frameworks like SOC 2, ISO 27001, and HIPAA, all in one place. I like that Secureframe links to in-house auditors who review your controls and evidence as you progress, making audit prep far less stressful. This direct auditor support is something I rarely see in other risk management platforms.
Secureframe Key Features
- Policy management: Provides pre-built, customizable security policy templates tailored to target frameworks.
- Audit readiness & partner network: Works alongside vetted third-party auditors, allowing companies to complete audits directly within or through the platform.
- Continuous monitoring dashboard: Tracks controls and security posture in real time across your connected assets.
- Third-party vendor management: Lets you assess, monitor, and manage risk from external vendors within the same platform.
Secureframe Integrations
Secureframe offers native integrations with AWS, Azure, Google Cloud Platform, Okta, Google Workspace, Microsoft 365, Slack, GitHub, GitLab, Jira, and Zoom. An API is also vailable for custom integrations.
Pros and Cons
Pros:
- Automated data aggregation across connected systems
- Supports multiple frameworks in a single dashboard
- In-house auditors assist with compliance review
Cons:
- Reporting lacks granular filtering options
- Customization of workflows is somewhat limited

Sprinto
Best for bundled VRM and compliance automation
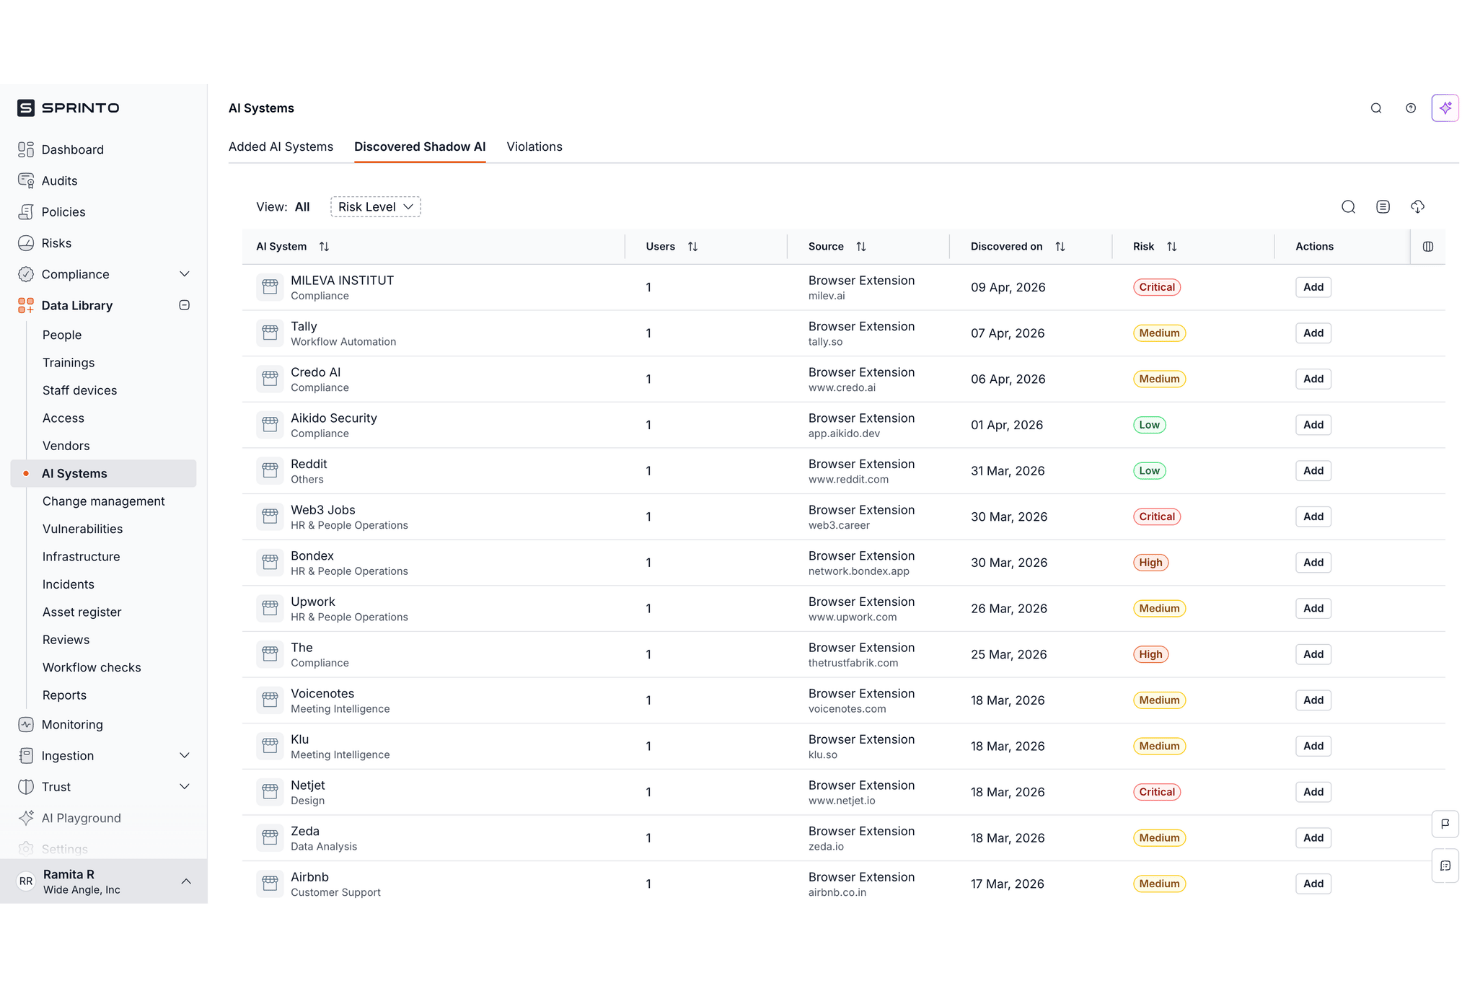
Sprinto is an automated compliance management platform designed to help fast-growing cloud businesses eliminate manual audit tasks, continuously monitor security controls, and get SOC 2, ISO 27001, and HIPAA certifications.
Who Is Sprinto Best For?
Sprinto is best suited for startups and cloud-native software companies that want an affordable, highly guided automation platform to pass audits with minimal disruption to engineering teams.
Why Sprinto Is a Good Drata Alternative
I picked Sprinto for my shortlist because it offers bundled vendor risk management and compliance automation. I use its risk assessment workflows to dig into third-party risks while keeping compliance reporting audit-ready. I like that Sprinto automatically gathers control evidence, making regulatory responses smoother and less manual.
Sprinto Key Features
- Adaptive control mapping: Automatically converts complex compliance framework requirements into clear, actionable daily engineering tasks.
- Automated remediation workflows: Provides step-by-step guidance and automated fixes for common security failures before an auditor flags them.
- Continuous health monitoring: Scans cloud infrastructure, code repositories, and identity providers to detect drift and non-compliant assets.
- Audit-ready dashboards: Provides real-time visualizations of risk and compliance posture across vendors and internal teams.
Sprinto Integrations
Sprinto offers native integrations with AWS, Google Cloud Platform, Microsoft Azure, Okta, Google Workspace, GitHub, Slack, Jira, Zoom, Datadog, and Salesforce. An API is also available for custom integrations.
Pros and Cons
Pros:
- Offers dedicated compliance managers
- Centralized dashboards for risk and compliance visibility
- Automated compliance evidence collection for audits
Cons:
- Reporting customization options are restrictive
- Policy template selection can feel limited
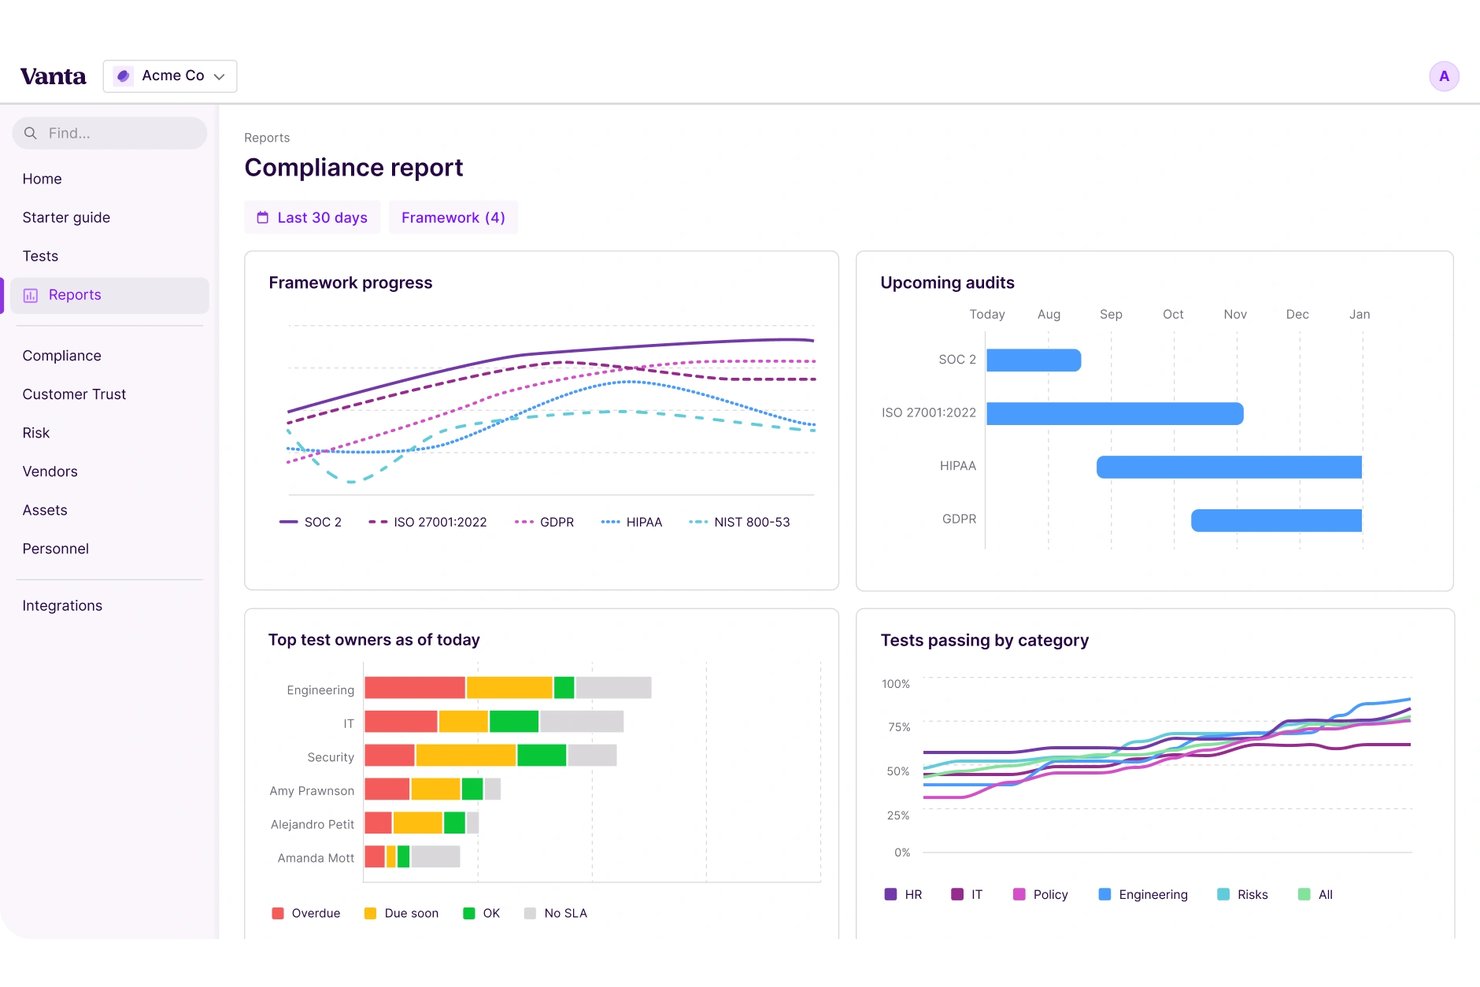
Vanta helps IT and security teams automate compliance, manage risk, and centralize evidence collection, making it easier for growing businesses and SaaS providers to simplify security reviews and stay audit-ready.
Who Is Vanta Best For?
Vanta is a good fit for IT and security teams at fast-growing SaaS companies that need to automate compliance and manage ongoing audit readiness.
Why Vanta Is a Good Drata Alternative
I picked Vanta for my shortlist because I rely on its automated evidence collection and continuous monitoring to simplify security reviews during sales cycles. I like how Vanta centralizes compliance status and streamlines audit preparation, which means I can respond quickly when prospects request new security documentation.
Vanta Key Features
- Automated risk assessments: Identify and prioritize risks continuously with built-in frameworks and customizable risk registers.
- Policy management tools: Create, edit, and distribute pre-built or custom security policies directly within the platform.
- Third-party vendor monitoring: Track and assess security postures and compliance of external vendors using integrated questionnaires and dashboards.
- Access control tracking: Monitor and verify user access levels, permissions, and account status across connected systems.
Vanta Integrations
Vanta offers native integrations with AWS, Google Cloud Platform, Microsoft Azure, Okta, Google Workspace, Slack, Jira, GitHub, GitLab, and Zoom. It also supports Zapier and an API for custom connections.
Pros and Cons
Pros:
- Third-party risk is tracked continuously
- Audit readiness status is always up to date
- Evidence collection is fully automated
Cons:
- Reporting options are less customizable
- Policy templates can feel inflexible
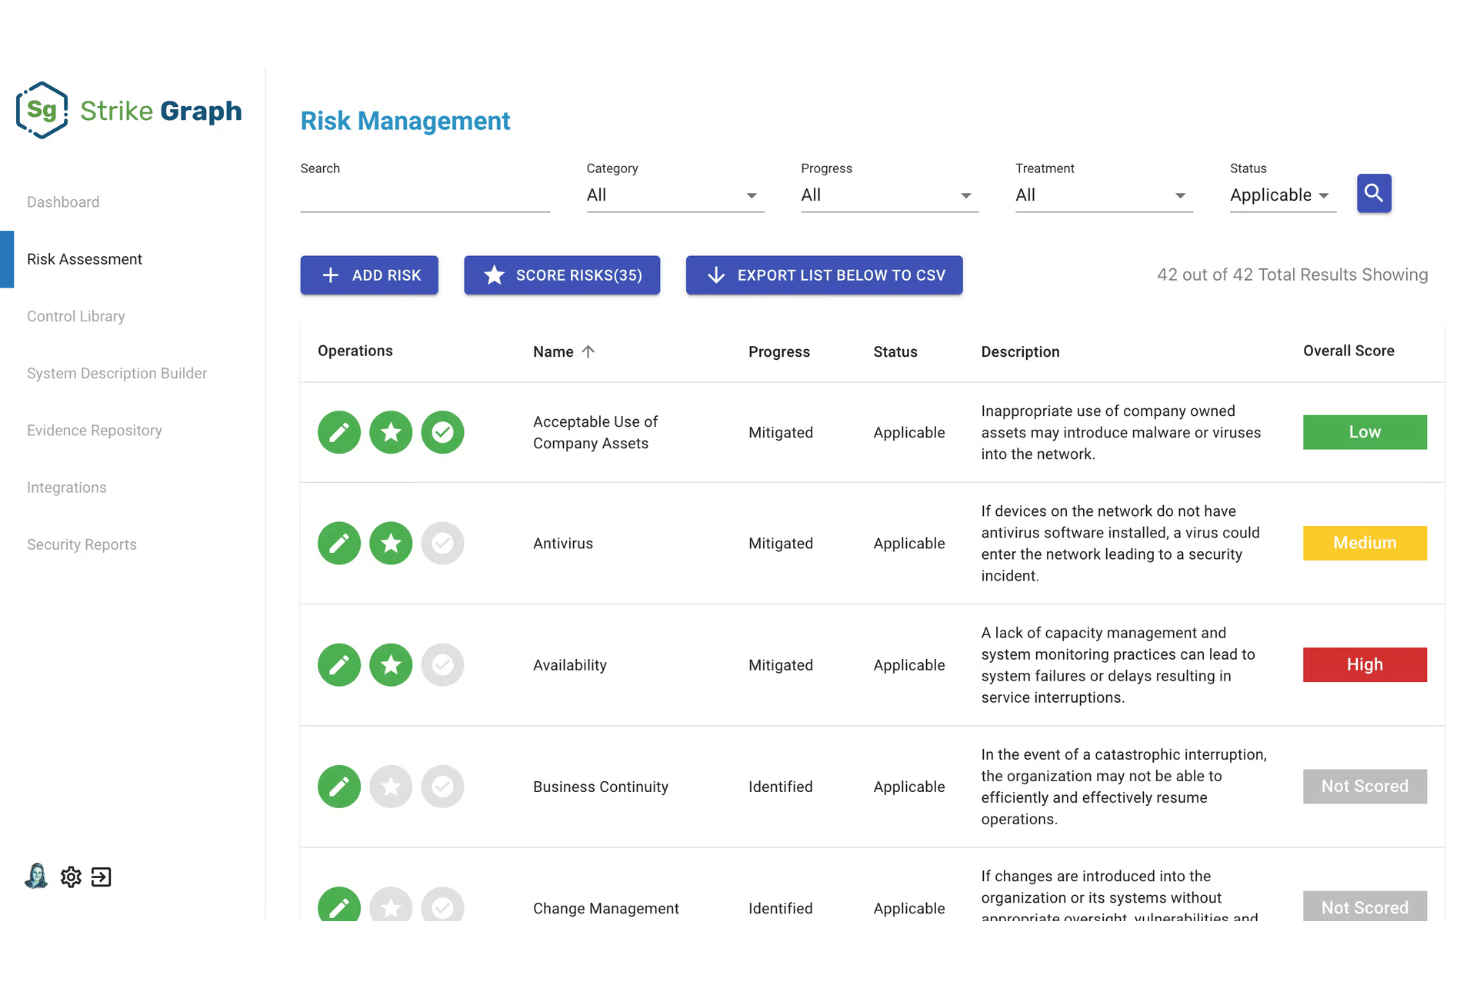
Strike Graph is an adaptable compliance automation platform designed to simplify audit preparation, control scoping, and continuous risk management for growing tech organizations.
Who Is Strike Graph Best For?
Strike Graph is ideal for small to midsize software companies and startups that want a flexible compliance platform to stay compliant as they grow.
Why Strike Graph Is a Good Drata Alternative
I picked Strike Graph for its AI-validated evidence collection that simplifies audit preparation in regulated industries. Its automated risk assessments and policy management handle complex compliance needs, while AI validation of audit evidence saves your team time and reduces manual errors during audits.
Strike Graph Key Features
- Automated control tracking: Monitor and update compliance controls through a centralized dashboard.
- Integrated audit management: Connects users directly with independent auditors through the platform to conduct end-to-end testing and issue official audit reports.
- Collaborative audit workspace: Assign tasks and share documentation with team members during the audit process.
- Integrated policy library: Access and deploy pre-built policy templates for faster compliance setup.
Strike Graph Integrations
Native integrations are not clearly documented. But it offers an API for custom integrations.
Pros and Cons
Pros:
- Customizable frameworks fit complex requirements
- Centralized dashboard tracks compliance controls
- AI validates audit evidence automatically
Cons:
- Pricing not disclosed upfront
- Integrations require custom API work
Anecdotes is an enterprise-grade GRC platform built for risk, compliance, and security leaders who need to orchestrate audit readiness, controls management, and evidence collection across multiple frameworks and business units.
Who Is Anecdotes Best For?
Anecdotes is an ideal solution for enterprise IT and security teams overseeing complex, data-intensive environments, especially when managing multiple compliance standards.
Why Anecdotes Is a Good Drata Alternative
I picked Anecdotes as one of the best alternatives because of its raw data-first approach to GRC. Rather than acting purely as a static compliance checklist, its platform normalizes granular system data into a centralized evidence pool, allowing security teams to run automated control testing and map live technical evidence across frameworks with unmatched accuracy.
Anecdotes Key Features
- Automated evidence mapping: Link collected evidence to controls and frameworks with rule-based mapping to cut down repetitive manual tasks.
- Dynamic workflow engine: Build and customize workflows to automate compliance, risk, and audit processes across distributed environments.
- Data-fabric evidence pool: Normalizes and stores technical evidence in a structured repository, ensuring tamper-proof artifact trails across all linked systems.
- Centralized policy manager: Create, update, and distribute company-wide policies and procedures from a single interface.
Anecdotes Integrations
Anecdotes provides over 230 native integrations, including AWS, Azure Active Directory, Okta, GitHub, Jira, Salesforce, and CrowdStrike. Its API, no-code Data Studio plugin builder, and MCP offer custom connectivity.
Pros and Cons
Pros:
- Customizes workflows for complex compliance needs
- Supports automation for evidence and audit tasks
- Centralizes control mapping across multiple frameworks
Cons:
- Requires enterprise resources for best adoption
- Setting up data pipeline connections requires more upfront effort
Other Drata Alternatives
Here are some additional alternatives to Drata that didn’t make it onto my shortlist, but are still worth checking out:
- TrustCloud
For SOC 2 and multi-framework GRC
- RegScale
For federal and enterprise-scale CCM
- LogicGate
For quantitative cyber risk in GRC programs
- Archer
For regulated-industry GRC at enterprise scale
- Thoropass
For audit delivery bundled with AI pre-screening
- Apptega
For MSSPs running multi-client GRC programs
- ServiceNow GRC
For GRC on an existing ServiceNow stack
- Hicomply
For UK/EU ISO 27001 compliance programs
- Comp AI
For open-source compliance verification
- Cypago
For agentic AI across multi-entity GRC


How I Evaluate Best Drata Alternatives
I split my evaluation into two layers: core functionality every platform must handle—automated evidence collection, multi-framework support, continuous control monitoring—and differentiators like trust centers, auditor networks, and vendor risk workflows that separate one option from another.
Core Functionality (Table Stakes for This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, and use that to help me assess its overall fit for the list.
- Multi-framework support: I check how many frameworks ship prebuilt and whether shared controls map across them, so a single control satisfies SOC 2 and ISO 27001 at once.
- Automated evidence collection: Each tool needs to pull evidence from cloud providers, identity systems, and HRIS platforms on a schedule.
- Continuous control monitoring: I look for real-time or near-real-time drift alerts with clear pass/fail status, not just periodic snapshots that go stale between audits.
- Integration ecosystem: The breadth of native connectors matters. I evaluate coverage across cloud, IdP, ticketing, and code repo categories plus API access for custom sources.
- Policy and risk management: I evaluate whether the tool ties policy lifecycle stages and risk register scores to controls and frameworks in one view.
- Auditor collaboration workflow: A dedicated auditor portal with evidence requests, comments, and approval tracking keeps the audit cycle inside the platform instead of in email threads.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
I look for AI-powered questionnaire automation that pulls from past answers and policy docs to pre-fill security reviews like SIG or CAIQ. This directly shortens sales cycles when prospects send custom RFPs. I also evaluate each platform's trust center—specifically whether it lets you publish live compliance status behind NDA gates, since a good one cuts inbound security review requests dramatically. Native vendor risk management is another separator I check. Platforms like Vanta and Sprinto bundle TPRM workflows with auto-scored vendor inventories, which saves you from buying a standalone tool.
Beyond Features
Pricing transparency matters a lot here. Some platforms charge per framework or lock TPRM behind add-ons, so I check whether the quoted price covers everything you'll actually use. Time-to-audit-readiness is another factor I evaluate—vendors like Sprinto and Secureframe offer guided onboarding with pre-built control libraries, while others expect your team to self-serve. I also look at each platform's auditor network, since pre-negotiated audit partnerships and in-platform collaboration can cut weeks off your first SOC 2 or ISO 27001 cycle.
Why Look For a Drata Alternative?
While Drata is a good choice for risk management, you might be looking for alternatives for the following reasons.
- You want a more flexible framework or control mapping
- You need broader integration options with third-party tools
- You require more transparent or predictable pricing
- You want faster time-to-audit readiness
- You seek enhanced vendor risk management workflows
- You need multi-entity or subsidiary support
Key Features of Drata
Here are some of Drata's key features to help you contrast and compare what alternatives offer:
- Multi-framework support: Connects compliance controls across frameworks like SOC 2, ISO 27001, and HIPAA so you can manage overlapping requirements within a single environment.
- Automated evidence collection: Gathers audit evidence from your cloud platforms, identity providers, HR systems, and other data sources on a recurring schedule to reduce manual review.
- Continuous control monitoring: Tracks changes and control drift in real time, alerting your team to any compliance gaps or failures so nothing gets missed between audits.
- Integration ecosystem: Offers native connectors for popular tools in cloud infrastructure, ticketing platforms, code repositories, HRIS, and more, plus an API for custom integration needs.
- Policy and risk management: Centralizes your policy documentation and risk registers, directly linking each policy or risk to related controls and regulatory frameworks for easy tracking.
- Auditor collaboration workflow: Provides a portal for auditors to access evidence, track requests, add comments, and approve responses, all within one secure platform.
- Automated security questionnaire response: Uses AI to auto-populate responses to security questionnaires such as SIG and CAIQ from your compliance documentation, saving time during vendor assessments.
- Trust center publishing: Lets you share real-time compliance status with prospects or customers through a customizable portal, reducing repetitive requests for security information.
- Vendor risk management: Maintains an inventory of third-party vendors, assesses their risk profiles, and connects their status directly to compliance controls within your environment.
- Guided onboarding and audit readiness: Includes step-by-step onboarding and access to templates or prebuilt control libraries to help teams prepare for audits with less guesswork.
Costs and Pricing of Drata Alternatives
Selecting the right software requires an understanding of the various pricing models and plans available. Costs vary based on features, team size, add-ons, and more. The table below summarizes common plans, their average prices, and typical features offered by alternative platforms:
Plan Comparison Table for Drata Alternatives
| Plan Type | Average Price | Common Features |
|---|---|---|
| Free Plan | $0-$20/user/month | Basic evidence collection, limited framework support, basic integrations, and simple reports. |
| Personal Plan | $25-$50/user/month | Multi-framework support, automated evidence collection, policy templates, and email-based support. |
| Business Plan | $55-$100/user/month | Continuous monitoring, advanced integrations, automated security questionnaires, and vendor risk tools. |
| Enterprise Plan | $110-$200+/user/month | Custom control mapping, auditor collaboration workflows, trust center publishing, and dedicated support. |