

10 Best Container Security Solutions You Need to Know

10 Best Container Security Solutions Shortlist


Managing container security can feel overwhelming. You're juggling compliance, data protection, and the ever-present threat of breaches. It's not easy, and I get it. That's why I've tested and reviewed the best container security solutions for you.
In my experience, the right tool can make a significant difference. These solutions help protect your infrastructure and give you peace of mind. I'll walk you through my top picks, focusing on their unique benefits and how they can fit your team's needs.
Expect a detailed, unbiased review that cuts through the noise. Let's find the tool that best addresses your challenges and supports your development goals.
Why Trust Our Software Recommendations
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Best Container Security Solutions Summary
This comparison chart summarizes pricing details for my top container security solutions selections to help you find the best one for your budget and business needs.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for auto-fixing container vulnerabilities | Free plan available | From $350/month | Website | |
| 2 | Best for Azure-native container attack path analysis | 30-day free trial | From $15/user/month (billed annually) | Website | |
| 3 | Best for full-stack container risk assessment | 14-day free trial | Pricing upon request | Website | |
| 4 | Best for vulnerability and compliance scanning | 7-day free trial | Pricing upon request. | Website | |
| 5 | Best for side-scanning container technology | Free trial available | Pricing upon request | Website | |
| 6 | Best for comprehensive cloud-native security | 30-day free trial | Pricing upon request | Website | |
| 7 | Best for runtime drift prevention in containers | Free trial available | Pricing upon request | Website | |
| 8 | Best for container visibility and forensics | Free demo available | Pricing upon request | Website | |
| 9 | Best for runtime-driven vulnerability prioritization | Free demo available | Pricing upon request | Website | |
| 10 | Best for Kubernetes-native supply chain security | 60-day free trial | Pricing upon request | Website |

Best Container Security Solution Reviews
Below are my detailed summaries of the best container security solutions that made it onto my shortlist. My reviews offer a detailed look at the key features, pros & cons, integrations, and ideal use cases of each tool to help you find the best one for you.

Best for auto-fixing container vulnerabilities
My Evaluation Score
- Runtime Threat Detection
- 1/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 2/5
- Configuration & Compliance Auditing
- 4/5
- Policy Enforcement & Admission Control
- 2/5
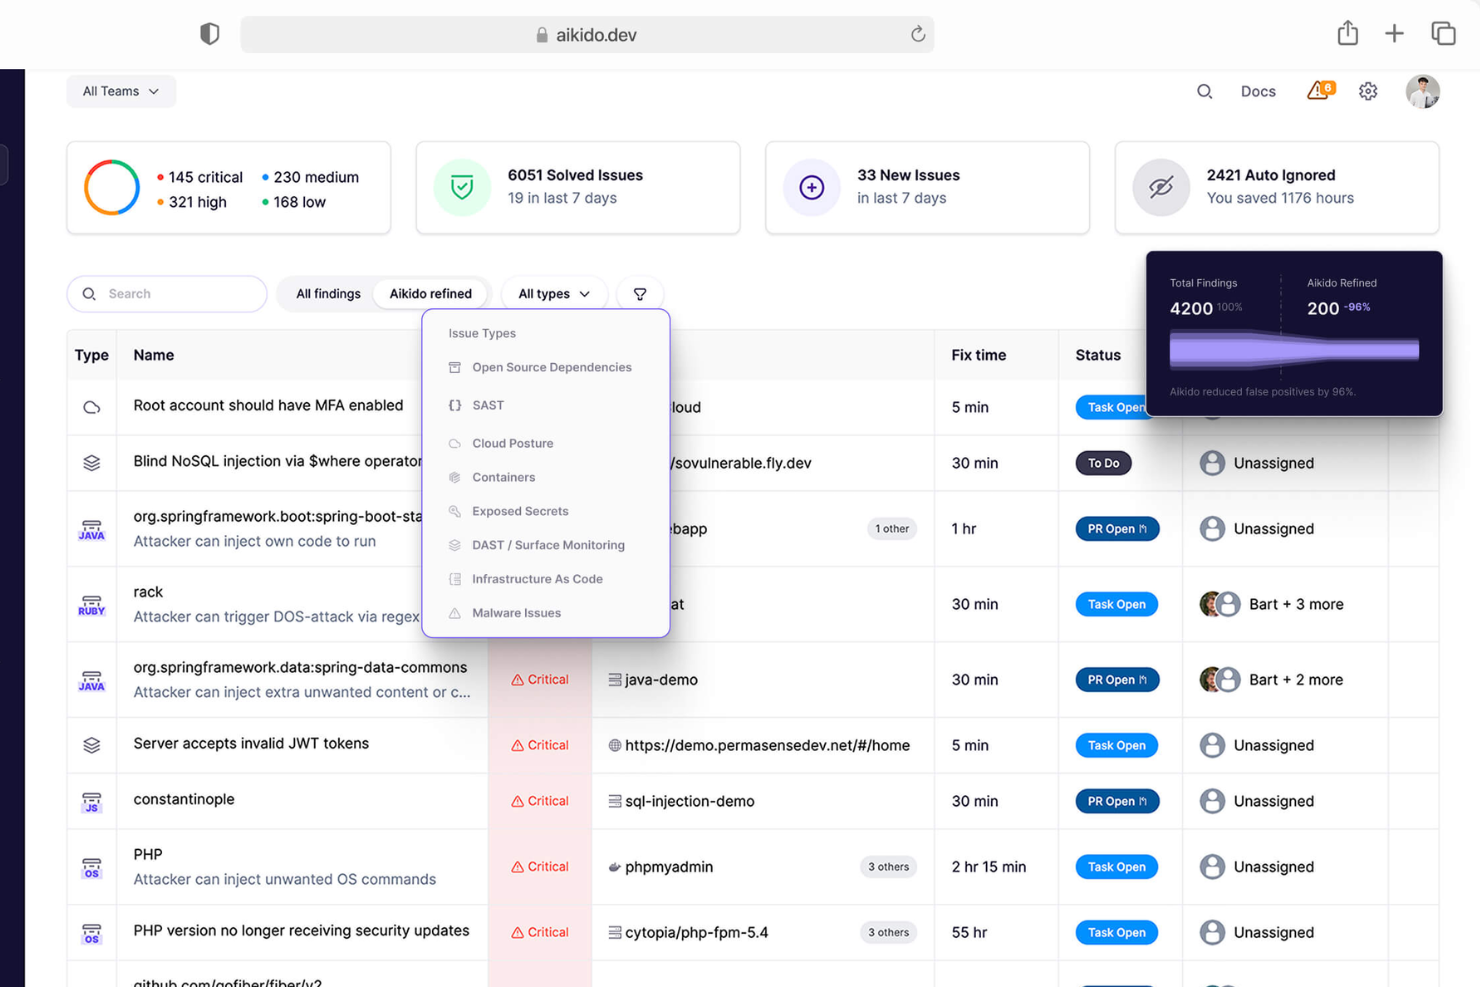
Aikido Security is a developer-native application security platform that combines container image scanning, SAST, SCA, secrets detection, CSPM, and in-app runtime protection across cloud and CI/CD environments.
Who Is Aikido Security Best For?
Aikido Security is a strong fit for DevSecOps teams that want to catch and fix container vulnerabilities before deployment, without adding agent overhead or complex tooling.
Why I Picked Aikido Security
I picked Aikido Security as one of the best because no other tool on this list handles base image vulnerability fixes the way it does. Instead of just flagging a vulnerable base image, it generates three to five ready-to-merge Dockerfile variants, each annotated with exactly which CVEs get fixed or introduced. Pair that with its library of 2,000+ zero-CVE hardened base images, and your team can swap out a risky base image without guessing at tradeoffs.
Aikido Security Key Features
- Reachability analysis: Confirms whether vulnerable functions in dependencies are actually called in your codebase, cutting false positives by up to 95%.
- SBOM generation: Exports software bills of materials in CycloneDX, SPDX, and CSV formats with VEX exploitability analysis, accessible via API for automated workflows.
- CI/CD pipeline gating: Blocks deployments based on configurable severity thresholds across GitHub Actions, GitLab CI/CD, Jenkins, Azure Pipelines, CircleCI, and Bitbucket Pipelines.
- Aikido Intel threat feed: A proprietary real-time feed that detects undisclosed vulnerabilities and malware in open-source ecosystems within 8 minutes of release.
Aikido Security Integrations
Aikido Security offers native integrations with GitHub, GitLab, Bitbucket, Azure Repos, six CI/CD platforms, and 12+ container registries, including Amazon ECR, Harbor, JFrog, and Docker Hub. It also connects with AWS, Azure, GCP, Jira, and Vanta, with API access for custom workflows.
Pros and Cons
Pros:
- Provides 2,000+ zero-CVE base images
- Reduces false positives with reachability analysis
- Auto-generates secure Dockerfile fixes for images
Cons:
- Lacks Kubernetes-native admission control integration
- No eBPF-based container runtime detection
New Product Updates from Aikido Security
Aikido Security Adds Pentest for AI Capabilities
Aikido Security adds Pentest for AI to test agents and LLM features against OWASP Agentic Top 10 risks. This helps teams identify AI-specific security weaknesses before they reach production. For more information, visit Aikido Security’s official site.


My Evaluation Score
- Runtime Threat Detection
- 4/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
Microsoft Defender for Cloud is a cloud-native application protection platform (CNAPP) that covers container image scanning, runtime threat detection, Kubernetes posture management, CI/CD pipeline security, and policy enforcement across Azure, AWS, and GCP environments.
Who Is Microsoft Defender for Cloud Best For?
It's a strong fit for Azure-native security teams that need to trace container attack paths across cloud resources without bolting on a separate CNAPP.
Why I Picked Microsoft Defender for Cloud
I picked Microsoft Defender for Cloud because its Cloud Security Graph does something I haven't seen matched in Azure-native environments: it traces exploitable attack paths from a publicly exposed container all the way through misconfigured RBAC, lateral network paths, and over-permissioned identities to critical cloud assets. That context-aware prioritization means I'm not chasing raw CVE counts but fixing the paths that are actually exploitable. I also like that Kubernetes Gated Deployment blocks non-compliant images at deploy time across AKS, EKS, and GKE, turning posture findings into enforced policy rather than just recommendations.
Microsoft Defender for Cloud Key Features
- Multi-registry image scanning: Agentless vulnerability assessment scans container images across ACR, ECR, GAR, GCR, Docker Hub, and JFrog Artifactory with daily rescans covering OS and language packages.
- MITRE ATT&CK-mapped threat detection: Over 60 built-in analytics tied to the MITRE ATT&CK for Containers framework detect suspicious activity at the cluster, node, and workload levels.
- Defender CLI CI/CD integration: A command-line tool embeds image scanning into 11+ CI/CD platforms, including GitHub Actions, Jenkins, and GitLab, with SARIF-based pass/fail gating.
- Reachability-based SCA via Endor Labs: An integration with Endor Labs identifies which vulnerabilities in container dependencies are actually reachable at runtime, reducing noise in remediation queues.
Microsoft Defender for Cloud Integrations
Microsoft Defender for Cloud offers native integrations with AKS, Amazon EKS, Google GKE, Azure Container Registry, Amazon ECR, GitHub Actions, Jenkins, GitLab, Microsoft Defender XDR, and Microsoft Sentinel. It supports 12 documented CI/CD integrations, plus GitHub Advanced Security, Endor Labs, and Azure Arc.
Pros and Cons
Pros:
- Kubernetes gated deployment for policy enforcement
- Agentless image scanning across major registries
- Attack path analysis from container to cloud
Cons:
- UI complexity reported by enterprise users
- Multi-cloud features lag behind Azure parity

My Evaluation Score
- Runtime Threat Detection
- 4/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
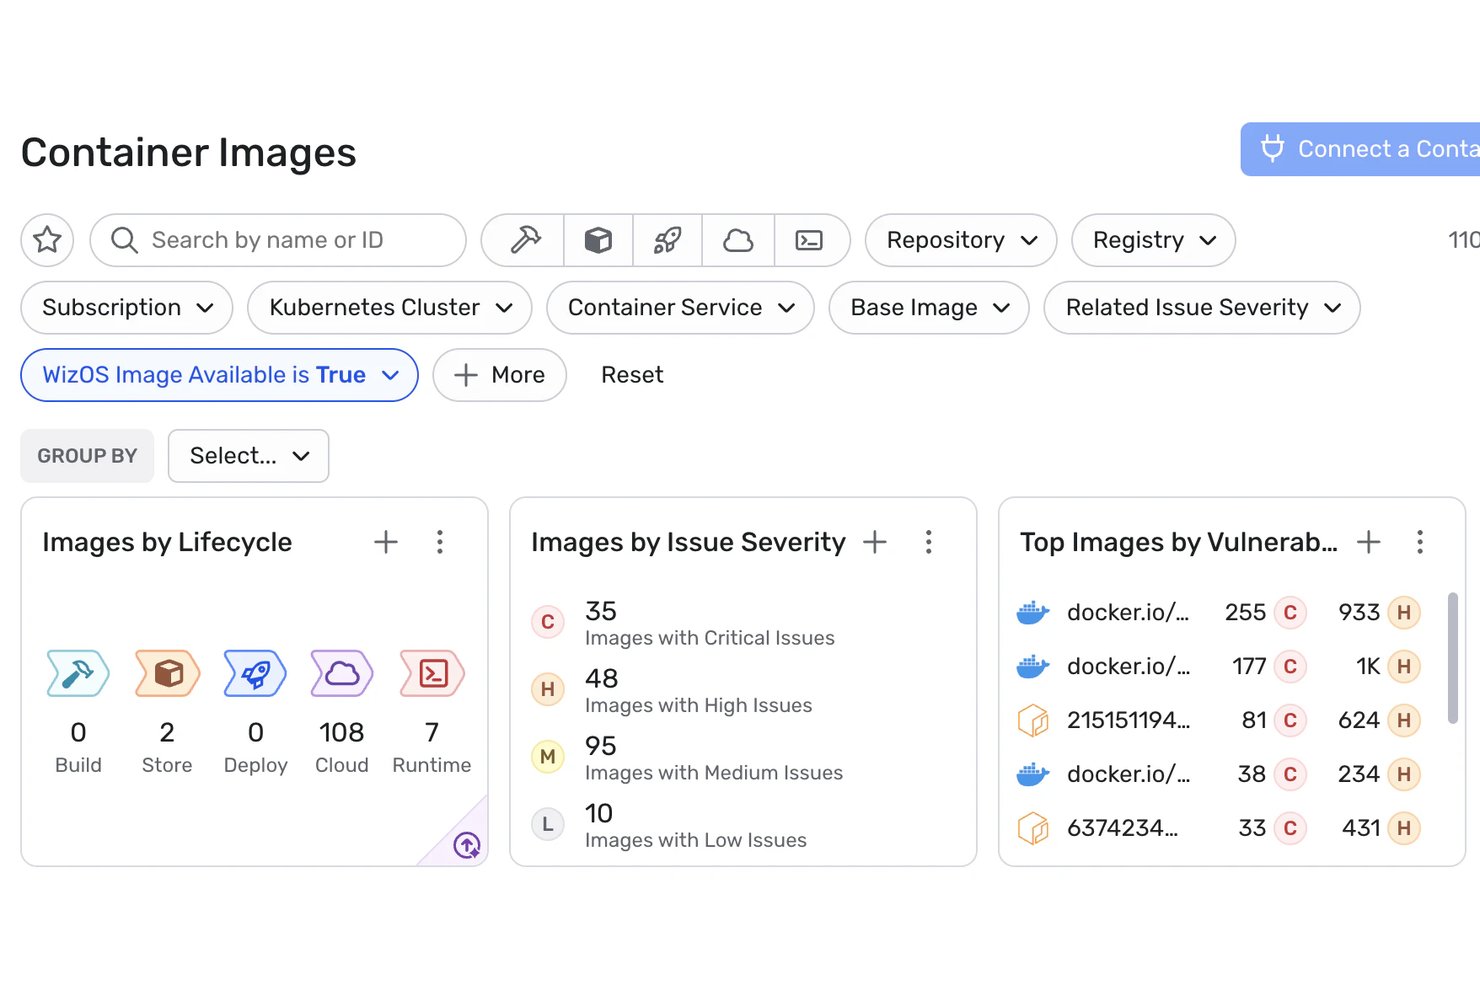
Wiz is a cloud-native application protection platform (CNAPP) that combines agentless image scanning, Kubernetes security posture management, runtime threat detection, CI/CD pipeline integration, and attack path analysis into a single unified platform.
Who Is Wiz Best For?
Wiz is a strong fit for enterprise security teams managing multi-cloud environments who need a single platform to assess and prioritize container risk across the full stack—from code to runtime.
Why I Picked Wiz
Wiz earns its spot on my shortlist because no other platform correlates container risk across the full stack the way its Security Graph does. Instead of surfacing thousands of raw CVEs, it maps relationships between vulnerabilities, misconfigurations, exposed secrets, and network exposure to identify genuinely exploitable attack paths. I also like how its KSPM covers EKS, AKS, and GKE with CIS-certified agentless assessments, tracing lateral movement from Kubernetes clusters into underlying cloud layers.
Wiz Key Features
- Wiz Defend runtime sensor: An eBPF-based sensor that monitors syscalls, process activity, and network flows across containerized workloads with under 2% CPU overhead.
- Wiz Admission Controller: A Kubernetes-native webhook that blocks non-compliant or unsigned container images from deploying based on centrally defined security policies.
- SBOM generation: Agentless, continuous software bill of materials creation across registries, CI/CD pipelines, and runtime environments with full package-level visibility.
- Wiz Workflows: Python-based custom playbooks that automate remediation actions such as revoking cloud roles, rotating credentials, and blocking storage bucket access.
Wiz Integrations
Wiz offers native integrations with GitHub Actions, Jenkins, GitLab CI/CD, Azure DevOps, Amazon ECR, Google Artifact Registry, Azure Container Registry, Docker Hub, Jira, and ServiceNow. It also connects with Splunk, Microsoft Sentinel, Cosign, and Notary.
Pros and Cons
Pros:
- CIS-certified posture for all major Kubernetes
- Security graph pinpoints true attack paths
- Agentless setup finds risks within hours
Cons:
- Some event search workflows feel clunky
- Runtime threat detection is relatively new

My Evaluation Score
- Runtime Threat Detection
- 5/5
- CI/CD & Registry Integration
- 4/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
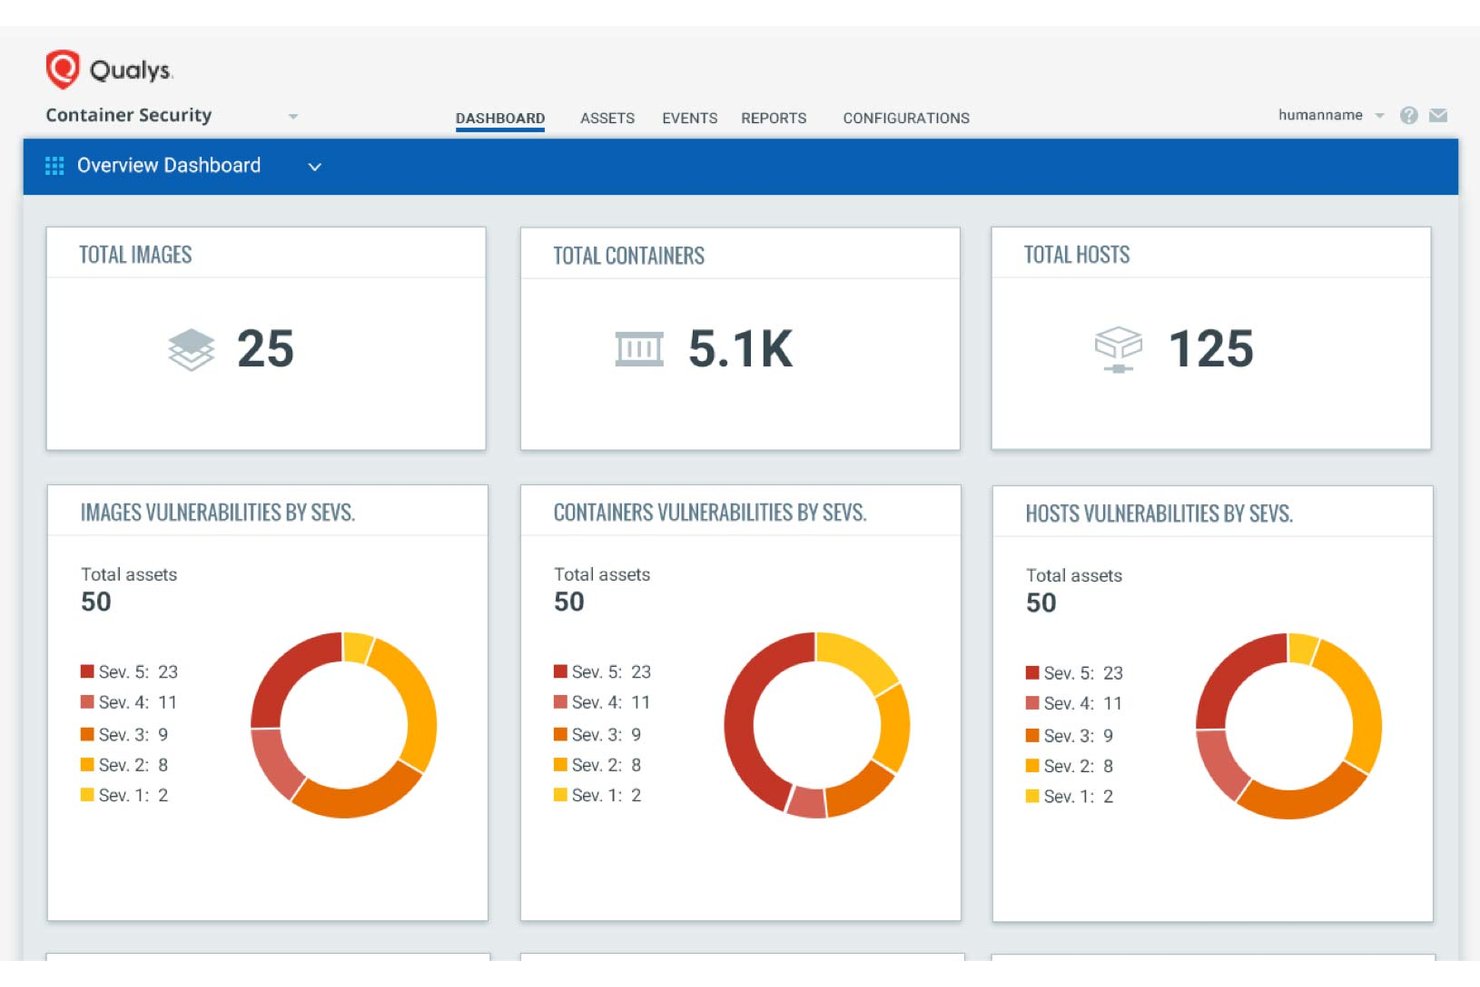
Qualys Container Security (CS) is a container security platform that covers image vulnerability scanning, runtime threat detection, Kubernetes security posture management, and compliance auditing across the full container lifecycle—from CI/CD pipelines to production.
Who Is Qualys Container Security (CS) Best For?
Qualys Container Security is a strong fit for security teams in regulated industries that need to consolidate vulnerability scanning, compliance auditing, and runtime threat detection under a single platform.
Why I Picked Qualys Container Security (CS)
I've included Qualys Container Security in my top picks because its TruRisk scoring goes beyond raw CVSS to factor in real-world exploitability signals like CISA KEV data and ransomware activity, so your team focuses on vulnerabilities that actually matter. The CIS Docker Benchmark v1.7.0 and Kubernetes compliance controls are continuously enforced, not just checked on demand. I also like that SBOM exports in SPDX and CycloneDX formats come built in, which matters when you need supply chain transparency fast.
Qualys Container Security (CS) Key Features
- Kubernetes Admission Controller: Intercepts Kubernetes API requests and evaluates organizational security policies before workloads are deployed to the cluster.
- QScanner CLI: A zero-install command-line tool that scans local and remote container images and outputs findings in JSON, SARIF, or SBOM formats for pipeline integration.
- eBPF-based Container Runtime Sensor: Monitors container processes, file activity, system calls, and network flows at the kernel level without requiring a sidecar or privileged container.
- Attack Path Analysis: Correlates container vulnerabilities, cloud misconfigurations, and excessive permissions to visualize exploitable paths across containers, nodes, and cloud resources.
Qualys Container Security (CS) Integrations
Qualys Container Security offers native integrations with GitLab CI/CD and Azure DevOps, plus Jenkins support and registry integrations for Amazon ECR, Azure Container Registry, GitHub Container Registry, JFrog Artifactory, and Harbor. QScanner and APIs support custom CI/CD workflows.
Pros and Cons
Pros:
- SBOM generation supports software supply chain transparency
- eBPF runtime protection covers kernel-level attacks
- TruRisk scoring highlights truly exploitable vulnerabilities
Cons:
- Remediation actions require manual team intervention
- Licensing model is complex to interpret

My Evaluation Score
- Runtime Threat Detection
- 4/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
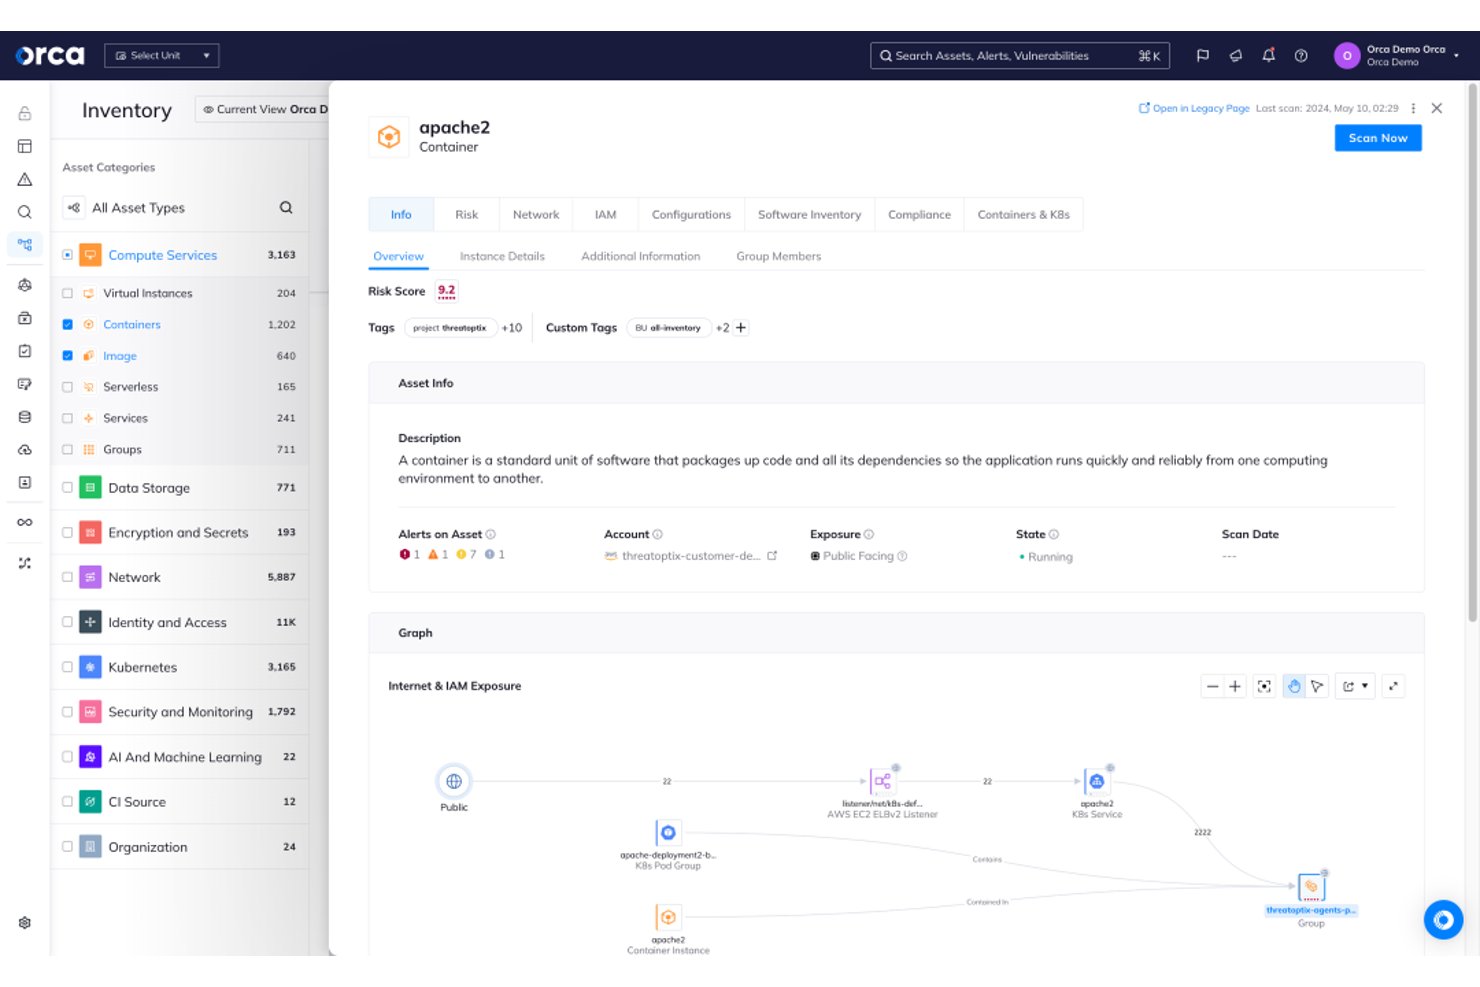
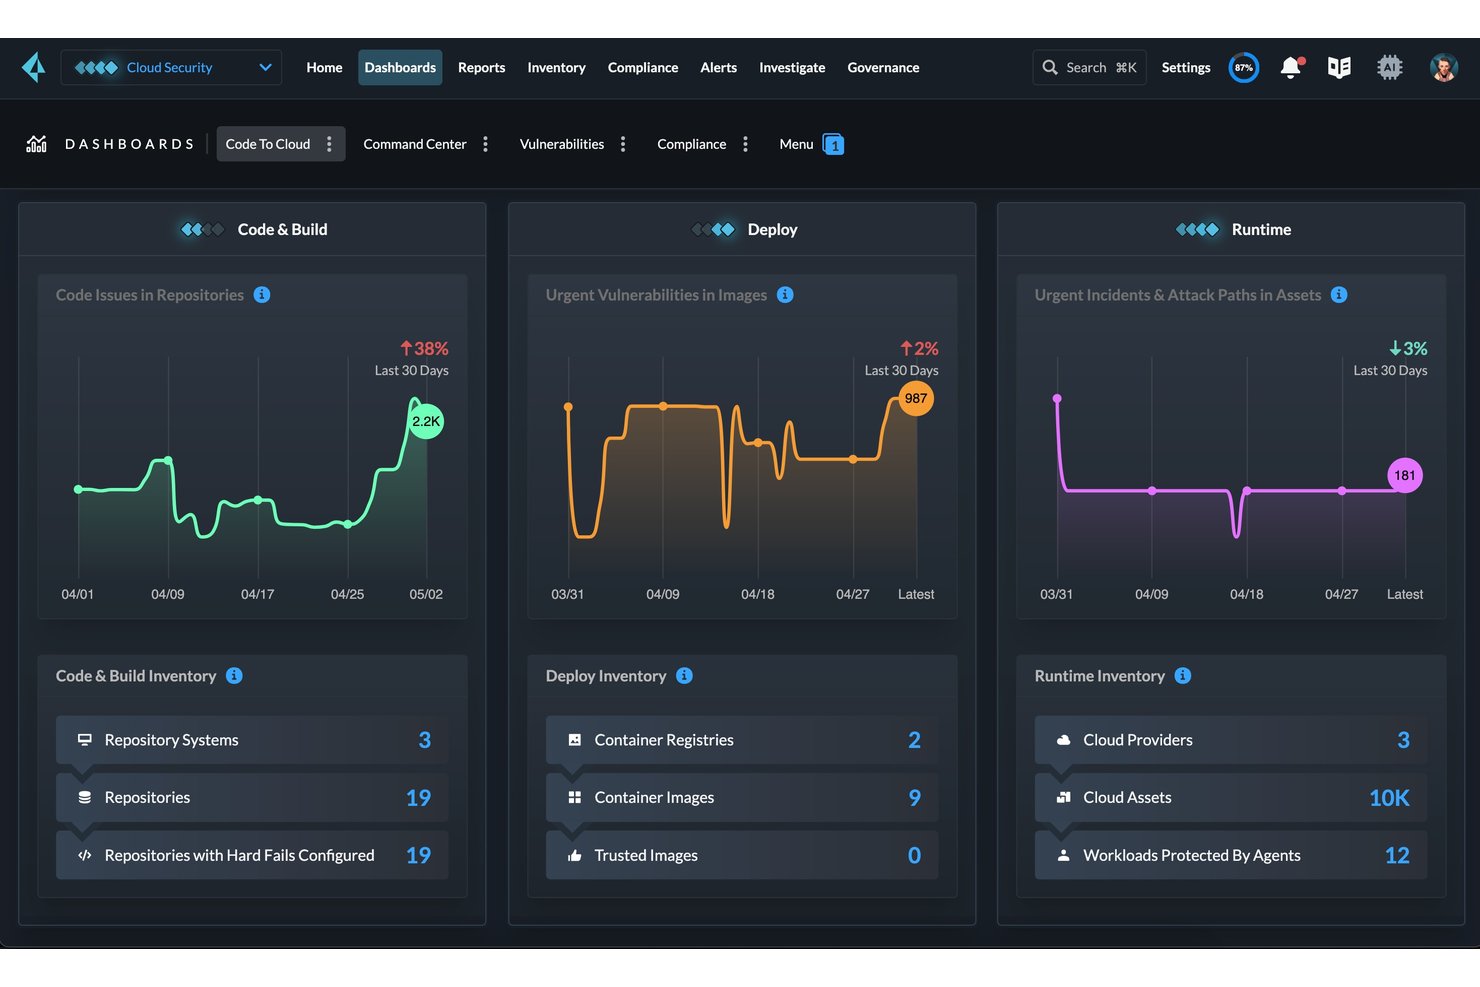
Orca Security is a cloud-native application protection platform (CNAPP) that combines agentless image scanning, Kubernetes security posture management, runtime threat detection, CI/CD integration, and compliance auditing across multi-cloud container environments.
Who Is Orca Security Best For?
Orca Security is a strong fit for cloud security teams managing large, multi-cloud container environments who need full-stack visibility without the overhead of deploying and maintaining agents across every workload.
Why I Picked Orca Security
Orca Security earns its spot on my list because its patented SideScanning™ technology reads workload block storage out-of-band through the shared virtualization layer, giving you full container visibility in under 30 minutes without deploying a single agent. I especially like how it scans images at all three lifecycle stages: build, registry, and runtime. Its context-aware prioritization layers in CVSS, EPSS, exploitability, and internet exposure, so you're not chasing vulnerabilities that can never actually be reached.
Orca Security Key Features
- Software Bill of Materials (SBOM) generation: Automatically produces a full SBOM, including transitive dependencies, across seven programming languages for every scanned container image.
- Kubernetes Admission Controller: A Helm-deployed, native admission controller that enforces block or warn policies on workload deployments directly from the Orca platform.
- Attack path analysis: Correlates vulnerabilities, misconfigurations, exposed secrets, and overprivileged identities into visualized attack paths targeting your most critical cloud assets.
- AI-generated fix pull requests: Automatically opens remediation PRs in GitHub, GitLab, or Azure DevOps when vulnerabilities or misconfigurations are detected in your code or container images.
Orca Security Integrations
Orca Security offers native integrations with Jenkins, GitHub Actions, GitLab CI/CD, Bitbucket, CircleCI, Travis CI, Harness, Jira, ServiceNow, Splunk, and Datadog for CI/CD, ticketing, SIEM, and observability workflows.
Pros and Cons
Pros:
- Deep compliance support with FedRAMP authorization
- Strong attack path and risk contextualization
- Agentless SideScanning gives instant full coverage
Cons:
- Dashboard customization options remain limited
- Runtime controls require optional sensor deployment

My Evaluation Score
- Runtime Threat Detection
- 5/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
Prisma Cloud is a cloud-native application protection platform (CNAPP) from Palo Alto Networks that combines container image scanning, runtime threat detection, Kubernetes security posture management, CI/CD pipeline integration, and compliance auditing across multi-cloud environments.
Who Is Prisma Cloud Best For?
Prisma Cloud is a strong fit for enterprise security teams managing multi-cloud environments who need a single platform to cover the full container lifecycle—from code to runtime.
Why I Picked Prisma Cloud
Prisma Cloud earns its spot on my shortlist because it covers more of the container security lifecycle in one platform than anything else I've evaluated. I particularly like the dual agentless and agent-based architecture: you can get immediate visibility across a multi-cloud environment without touching a single node, then layer in Defender agents for deep runtime enforcement where it counts. The attack path analysis is what really sets it apart, correlating CVEs, IAM misconfigurations, and network exposure into a visual graph so you're fixing the risks that are actually exploitable.
Prisma Cloud Key Features
- Image Analysis Sandbox: Dynamically executes container images in an isolated environment to detect malware or cryptominer activity before images reach production.
- Compliance framework coverage: Runs 400+ out-of-the-box checks against frameworks including CIS, NIST SP 800-190, PCI DSS, HIPAA, FedRAMP High, and DISA STIG.
- Software Bill of Materials generation: Automatically produces SBOMs as part of the supply chain security module to give teams full visibility into open source dependencies.
- Behavioral baselining: Profiles normal container process, filesystem, and network activity during an initial learning period, then flags or blocks deviations in real time.
Prisma Cloud Integrations
Prisma Cloud offers native integrations with Jenkins, GitHub Actions, CircleCI, AWS CodeBuild, Azure DevOps, Google Cloud Build, Docker Hub, Amazon ECR, Google Container Registry, and Azure Container Registry.
Pros and Cons
Pros:
- 400 plus compliance checks for regulations
- Dual agentless and agent-based deployment options
- Attack path analysis visualizes real exploit scenarios
Cons:
- Complex configuration for multi-cloud environments
- High alert volume can overwhelm small teams

My Evaluation Score
- Runtime Threat Detection
- 5/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
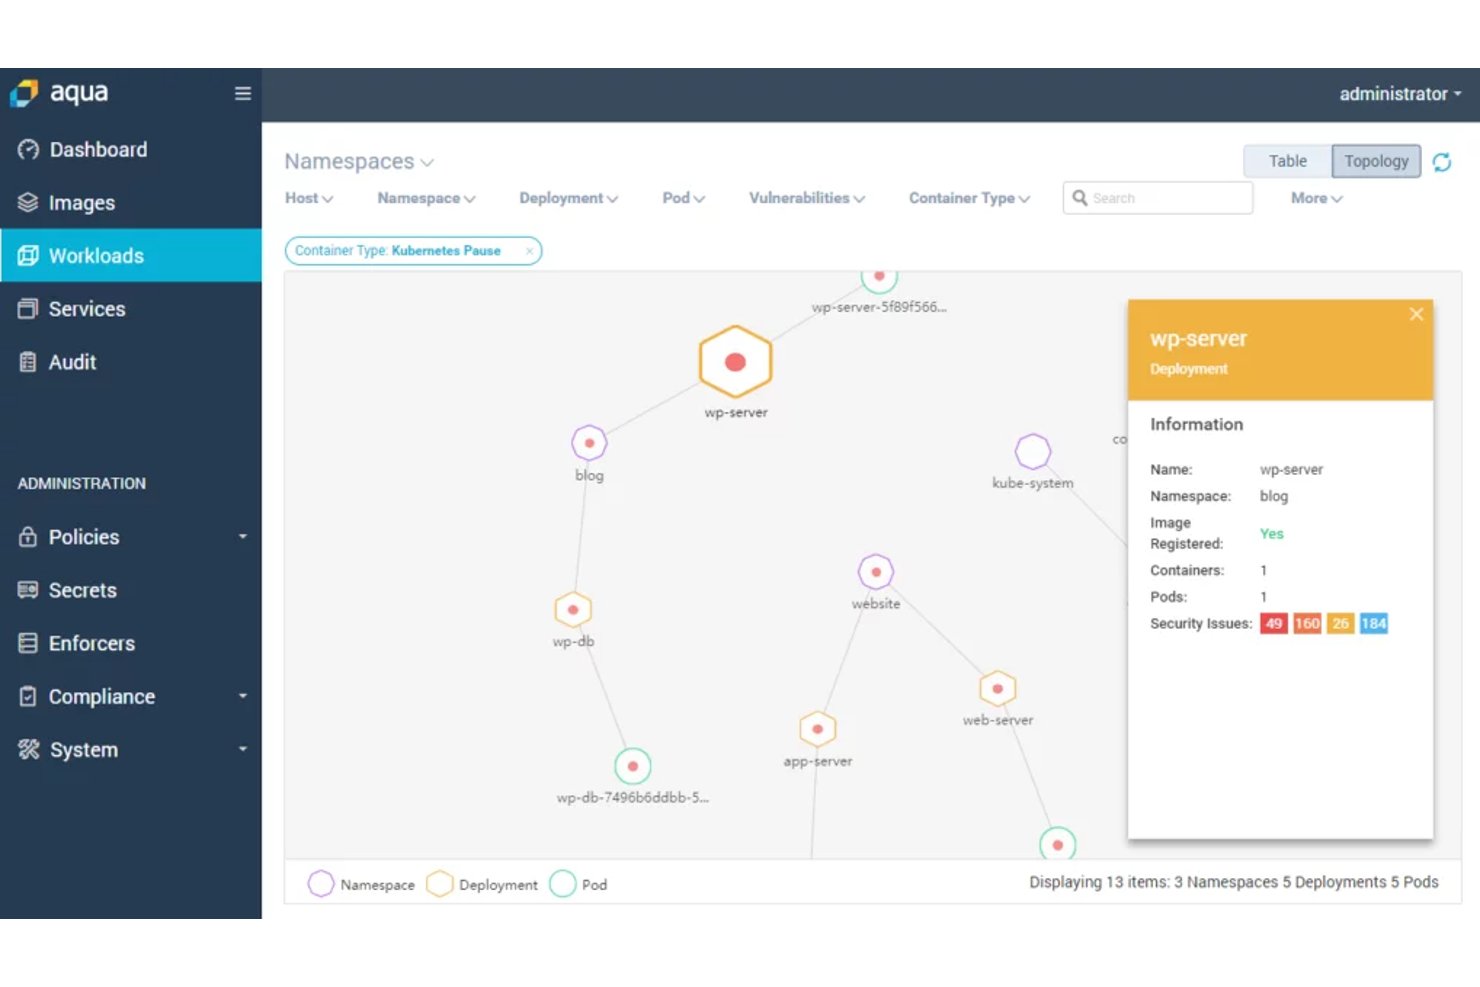
Aqua Security is a container security platform built around eBPF-based runtime protection, image vulnerability scanning, Kubernetes security posture management, and software supply chain security across multi-cloud and hybrid environments.
Who Is Aqua Security Best For?
Aqua Security is a strong fit for security and platform engineering teams running containerized workloads at scale who need runtime threat detection alongside supply chain security.
Why I Picked Aqua Security
Aqua Security earns its spot on my shortlist because its eBPF-based drift prevention is genuinely best-in-class: when a container deviates from its known-good state at runtime, Aqua blocks the unauthorized process or file change without terminating the workload. I also like the Dynamic Threat Analysis sandbox, which catches fileless malware and zero-day threats that static scanning misses entirely. Its patented vulnerability shielding blocks exploitation of unpatched components at runtime, buying your team time without requiring a code change.
Aqua Security Key Features
- Dynamic Threat Analysis sandbox: Runs container images in a secure virtual sandbox to detect fileless malware, zero-day attacks, and supply chain threats that static scanning misses.
- Kubernetes Risk Explorer: Provides an interactive, real-time map of running clusters that surfaces and rates security risks across namespaces, nodes, containers, and network connections.
- Software supply chain security module: Scans all source repositories for vulnerabilities, IaC misconfigurations, secrets, and license issues while generating digitally signed SBOMs at every stage of the build pipeline.
- CI/CD Assurance Policies: Enforces pass/fail security gates across Jenkins, GitHub Actions, GitLab CI, and other platforms to block non-compliant images from advancing to deployment.
Aqua Security Integrations
Aqua Security offers native integrations across 8+ CI/CD platforms and 10+ container registries, including Jenkins, GitLab CI, GitHub Actions, Azure DevOps, Amazon ECR, JFrog Artifactory, Harbor, Red Hat Quay, Docker Hub, and Sonatype Nexus Repository. It also supports Terraform and AWS CloudFormation.
Pros and Cons
Pros:
- Dynamic sandbox detects fileless container malware
- FedRAMP High approval supports regulated environments
- Drift prevention blocks unauthorized container changes
Cons:
- UI navigation frustrates new administrators
- Pricing not transparent without vendor contact

My Evaluation Score
- Runtime Threat Detection
- 5/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 4/5
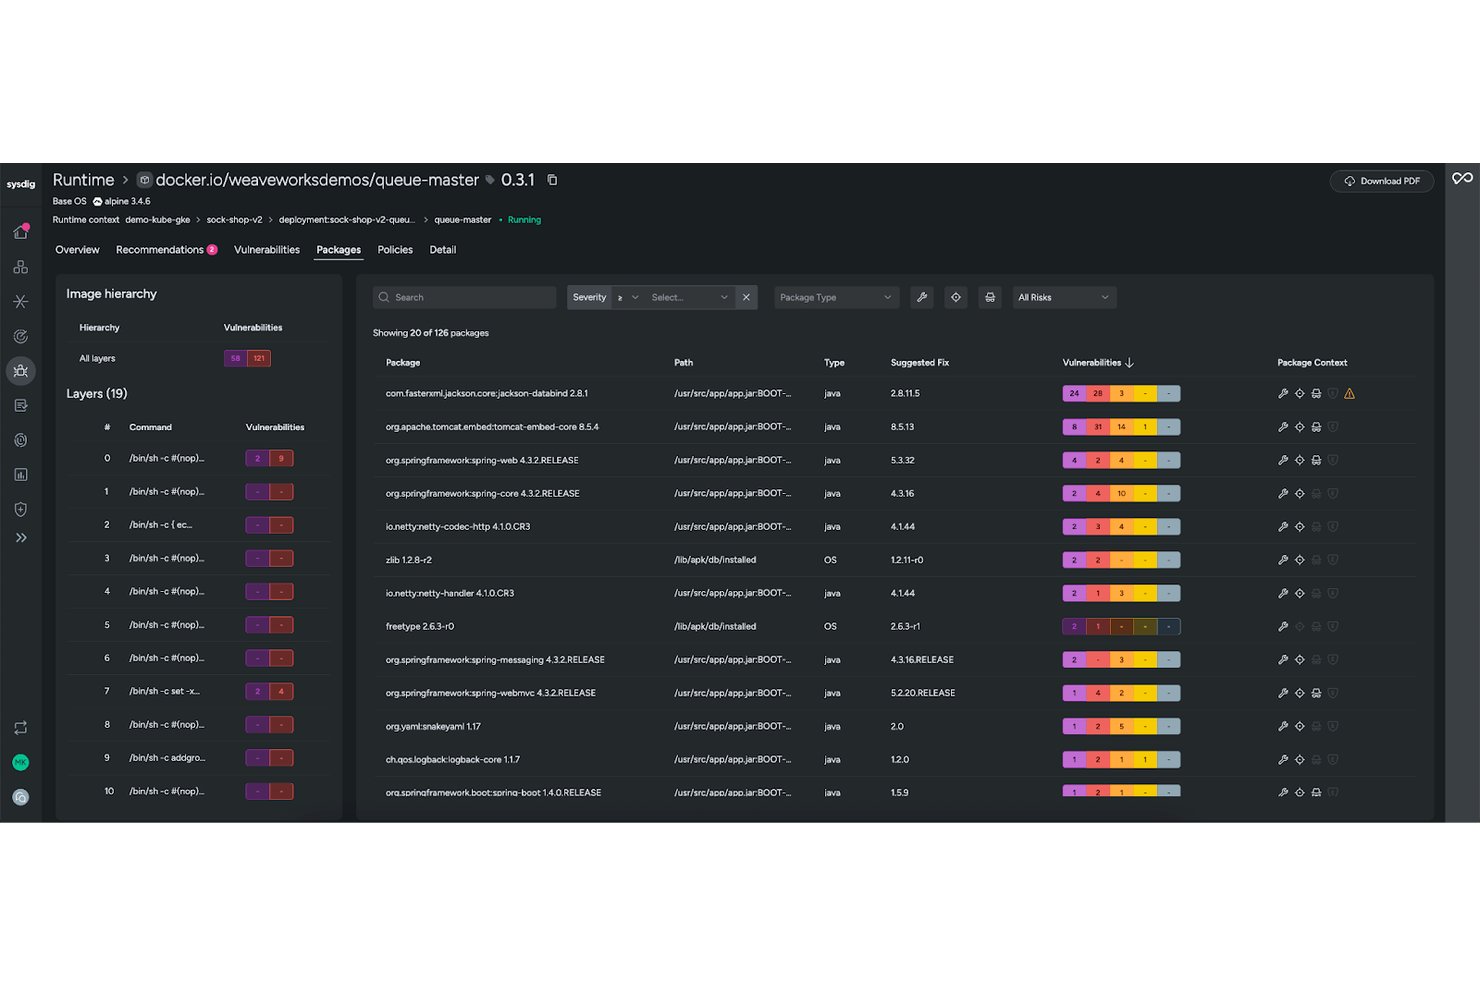
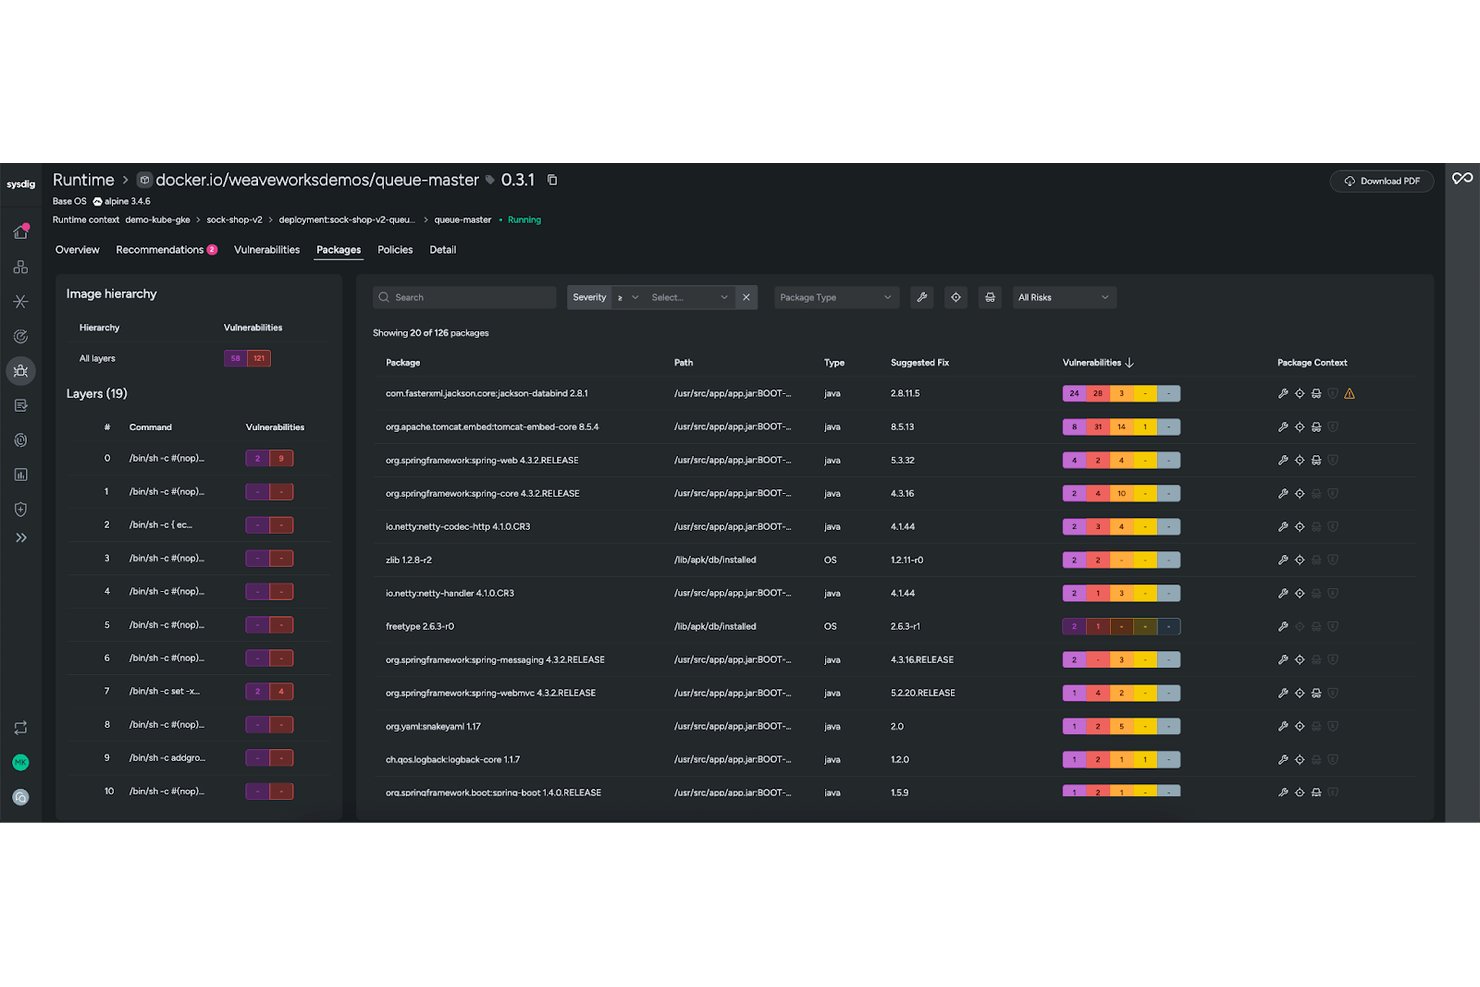
Sysdig is a cloud-native application protection platform (CNAPP) that combines runtime threat detection, image vulnerability scanning, Kubernetes security posture management, and forensic investigation capabilities built on the open-source Falco engine.
Who Is Sysdig Best For?
Sysdig is a strong fit for security and platform engineering teams running containerized workloads at scale who need deep runtime visibility and the ability to investigate incidents after they happen.
Why I Picked Sysdig
Sysdig earns its spot on my shortlist because it's the only vendor here that created Falco, the CNCF-graduated runtime detection engine now running inside 60% of Fortune 500 environments. That foundation gives it unmatched container visibility: eBPF-based syscall capture lets you see exactly which processes ran, which files were touched, and which connections were made inside a container, in real time. When an incident happens, Sysdig's forensic reconstruction lets you replay the full attack timeline rather than piecing it together from incomplete logs.
Sysdig Key Features
- Sysdig Sage: An AI assistant that answers security questions in plain language and auto-generates remediation tickets with full contextual detail.
- Cloud Attack Graph: Visualizes exploitable attack paths by correlating vulnerabilities, misconfigurations, exposed secrets, and excessive permissions across your environment.
- Software supply chain security: Validates image provenance and supports Sigstore/Cosign image signing verification to detect tampering across the build-to-deploy chain.
- Continuous compliance monitoring: Automatically checks your environment against frameworks like FedRAMP, PCI-DSS, HIPAA, and CIS Benchmarks, with on-demand audit-ready PDF reports.
Sysdig Integrations
Sysdig offers documented integrations with GitHub Actions, GitLab CI, Jenkins, CircleCI, Argo CD, AWS ECR, Google GCR, Azure ACR, Harbor, and JFrog Artifactory. It also connects with Splunk, Jira, ServiceNow, Slack, PagerDuty, and Open Policy Agent.
Pros and Cons
Pros:
- Real-time forensics with reconstructable attack timelines
- Correlates risk paths with Cloud Attack Graph
- Deepest runtime visibility with Falco syscall capture
Cons:
- No free trial for Sysdig Secure
- Initial setup and tuning is complex
My Evaluation Score
- Runtime Threat Detection
- 5/5
- CI/CD & Registry Integration
- 5/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 5/5
Sysdig Secure is a CNAPP and container security platform built on eBPF-based runtime detection that spans image vulnerability scanning, Kubernetes posture management, cloud detection and response, compliance auditing, and CI/CD pipeline security.
Who Is Sysdig Secure Best For?
Sysdig Secure is a strong fit for enterprise security and platform engineering teams running large-scale Kubernetes environments who need runtime context to cut through vulnerability noise.
Why I Picked Sysdig Secure
Sysdig Secure earns its spot on my shortlist because it's built on Falco, the CNCF-graduated runtime engine that detects threats at the kernel level using eBPF, giving it visibility that no static scanner can replicate. What I find most compelling is its in-use package prioritization: runtime context filters out vulnerabilities tied to packages not actually loaded in memory, cutting noise by up to 99.8% so your team works a real list, not a theoretical one. The CVE360 graph then layers in exploitability data and asset criticality to make prioritization genuinely actionable.
Sysdig Secure Key Features
- Falco-based runtime engine: Detects threats at the kernel level using eBPF instrumentation, capturing Linux syscalls across containers and hosts in real time.
- Cloud Attack Graph: Correlates vulnerabilities, misconfigurations, exposed secrets, and excessive permissions to map exploitable attack paths across your cloud environment.
- Sysdig Sage GenAI assistant: Answers security questions in plain language and walks your team through step-by-step remediation, including exact commands and base-image upgrade paths.
- Compliance module: Continuously audits Kubernetes and cloud configurations against frameworks like FedRAMP, PCI DSS 4.0, HIPAA, DISA STIGs, and CIS Benchmarks, with scheduled PDF and CSV report generation.
Sysdig Secure Integrations
Sysdig Secure offers native integrations with GitHub Actions, GitLab, Jenkins, Azure Pipelines, Amazon ECR, Azure Container Registry, Docker Hub, Quay, Splunk, and ServiceNow. It also supports Backstage and an API for custom security workflows.
Pros and Cons
Pros:
- Covers compliance for regulated industries
- Kernel-level detection with Falco eBPF engine
- Filters out vulnerabilities not in memory
Cons:
- Dashboard reporting features are limited
- Initial configuration is technically demanding
Best for Kubernetes-native supply chain security
My Evaluation Score
- Runtime Threat Detection
- 5/5
- CI/CD & Registry Integration
- 4/5
- Image Vulnerability Scanning
- 5/5
- Kubernetes/Orchestrator Security
- 5/5
- Configuration & Compliance Auditing
- 5/5
- Policy Enforcement & Admission Control
- 5/5
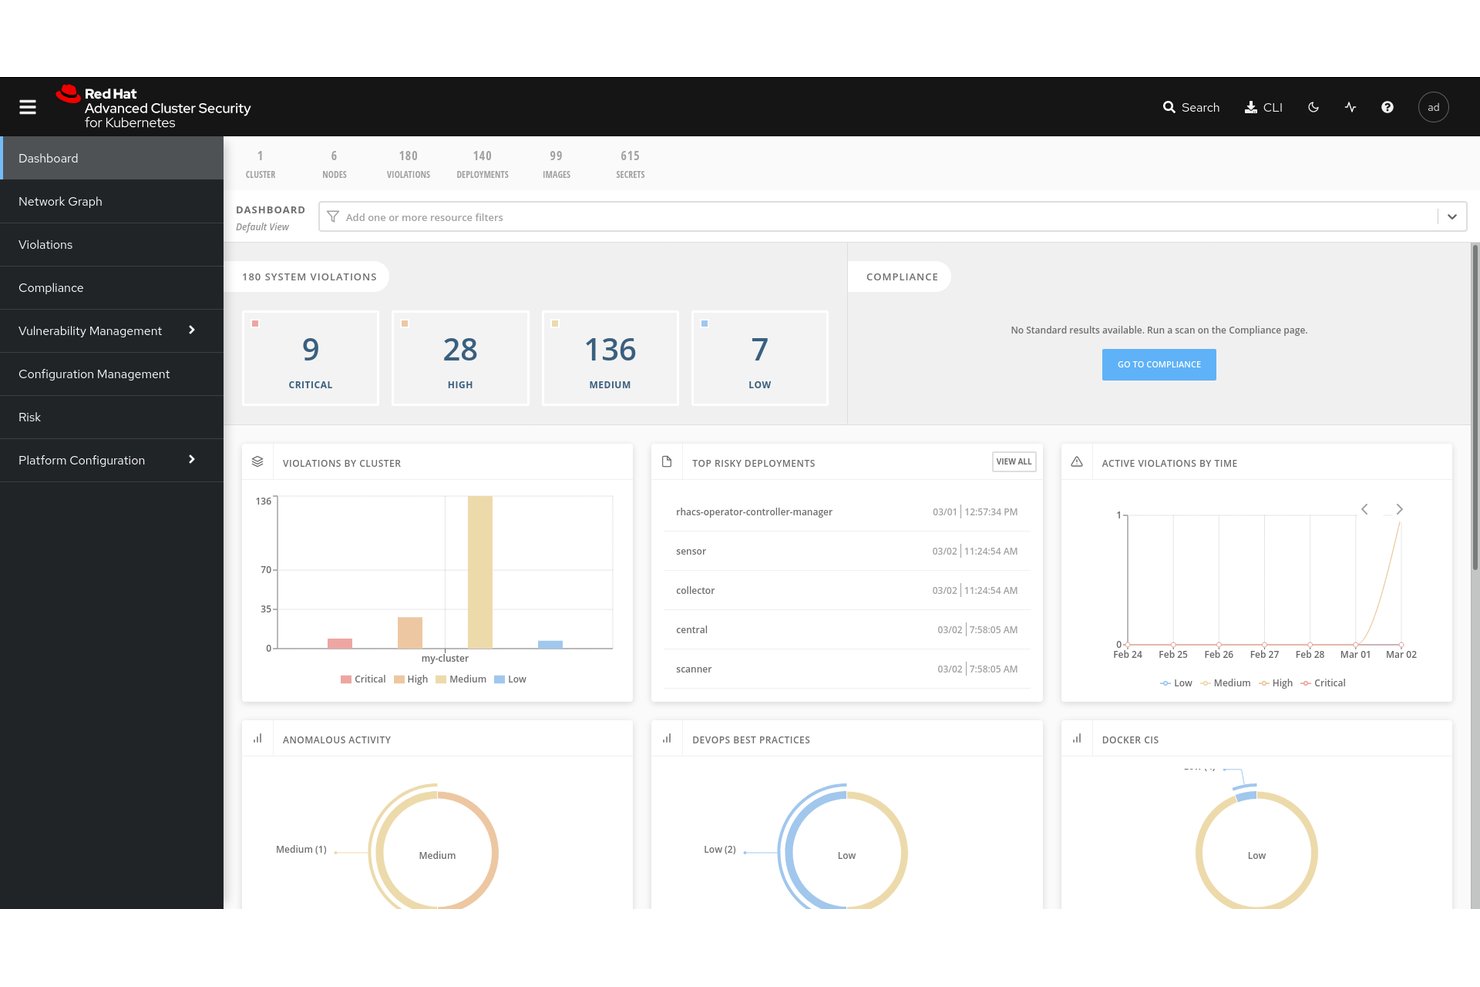
Red Hat Advanced Cluster Security for Kubernetes (RHACS) is a Kubernetes-native container security platform that covers image vulnerability scanning, runtime threat detection, policy enforcement, and compliance auditing across multi-cluster and multi-cloud environments.
Who Is Red Hat Advanced Cluster Security for Kubernetes Best For?
RHACS is a natural fit for platform and DevSecOps teams running workloads on Red Hat OpenShift or multi-cloud Kubernetes environments who need deep, native security coverage across the full container lifecycle.
Why I Picked Red Hat Advanced Cluster Security for Kubernetes
I picked RHACS as one of the best because it's purpose-built for Kubernetes from the ground up, which makes it uniquely suited for supply chain security at the orchestrator level. I particularly like how it combines Cosign/Sigstore image signature verification with SBOM generation in SPDX 2.3 format, letting teams enforce policies that block unsigned images before they ever reach the cluster. Its
roxctl
CLI integrates directly into Jenkins, GitHub Actions, and Tekton pipelines to gate builds on policy violations at configurable severity thresholds.
Red Hat Advanced Cluster Security for Kubernetes Key Features
- eBPF CO-RE runtime collection: Captures kernel-level syscall, process, file, and network telemetry from running containers without kernel modules or sidecar containers.
- Admission controller with configurable failure modes: Enforces deploy-time policies via a Kubernetes admission webhook, with Fail Open or Fail Close behavior to match your availability and security requirements.
- Automated compliance scanning: Runs scheduled checks against CIS, NIST, PCI DSS 4.0, HIPAA, and ISO 27001 frameworks, with one-click auditor-ready evidence export from a single dashboard.
- Multi-cluster discovery: Detects unprotected clusters across Amazon EKS, Google GKE, and Microsoft AKS via Paladin Cloud and Red Hat OpenShift Cluster Manager integration.
Red Hat Advanced Cluster Security for Kubernetes Integrations
Native integrations include Red Hat OpenShift, Amazon EKS, Google GKE, Microsoft AKS, Jenkins, GitHub Actions, Tekton, and Argo CD. RHACS also connects with Quay, Amazon ECR, and Prometheus through its metrics endpoint.
Pros and Cons
Pros:
- Deep compliance coverage across multiple frameworks
- eBPF runtime visibility with kernel-level detection
- Purpose-built for Kubernetes security controls
Cons:
- Some admin tasks require command line interface
- Richest features tied to OpenShift platform
Other Container Security Solutions
Here are some additional container security solutions options that didn’t make it onto my shortlist, but are still worth checking out:
- ARMO
For Kubernetes RBAC and runtime hardening
- CrowdStrike Falcon Cloud Security
For adversary-mapped container risk ranking
- Snyk
For container vulnerability management
- Check Point CloudGuard
For ThreatCloud AI-enriched runtime defense
- NeuVector
For open-source zero-trust container security
- PingSafe
For adaptive threat defense
- Trend Micro Cloud Security
For enterprise CNAPP with XDR correlation
- Tenable Container Security Scanner
For exposure-led container risk management


How I Evaluate Container Security Solutions
I evaluate container security tools in two layers: baseline capabilities like image scanning and runtime detection, then differentiators like Kubernetes hardening depth and CI/CD integration.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score into a percentage. Each tool needs to achieve a minimum total score of 65% to be considered for inclusion.
- Image Vulnerability Scanning: I check whether the tool scans container images across registries for CVEs, embedded secrets, and outdated packages—plus whether it generates SBOMs.
- Runtime Threat Detection: Real-time monitoring of running containers matters, so I evaluate how each tool detects anomalous processes, unexpected network calls, and container drift.
- Kubernetes Configuration Hardening: Each tool should assess K8s clusters against CIS benchmarks, flag risky RBAC permissions, and surface misconfigured admission controllers.
- CI/CD Pipeline Integration: I look at how each tool plugs into build pipelines to gate deployments—whether it supports policy checks in GitHub Actions, GitLab CI, or Jenkins.
- Compliance & Policy Enforcement: Pre-built policy templates for frameworks like PCI-DSS, HIPAA, and SOC 2 are a baseline; I also evaluate custom policy authoring and reporting depth.
- Network Segmentation Controls: Container-aware microsegmentation helps prevent lateral movement, so I look for L3–L7 policy enforcement and clear east-west traffic visibility.
Once I have a list of tools that meet this criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
AI-driven risk prioritization is a big differentiator—tools that correlate CVEs with runtime exposure and exploitability help teams cut through alert noise and focus on real threats. I also evaluate admission controller enforcement, which blocks non-compliant workloads from deploying into clusters before they cause issues. Unified CNAPP capabilities matter when teams want container security combined with CSPM, CWPP, and CIEM in one console, reducing tool sprawl across the cloud-native stack.
Beyond Features
Deployment model matters a lot here. I check whether a tool supports agent-based, agentless, or hybrid scanning—and whether it can run in air-gapped environments for regulated teams. Ecosystem integrations are equally important; a tool that connects to your SIEM, ticketing system, and registries like Harbor or Artifactory keeps security data flowing where your team already works. I also evaluate scalability, specifically how lightweight the runtime sensors are across clusters with thousands of nodes and whether multi-cloud visibility lives in a single console.
How to Choose a Container Security Solution
It’s easy to get bogged down in long feature lists and complex pricing structures. To help you stay focused as you work through your unique software selection process, here’s a checklist of factors to keep in mind:
| Factor | What to Consider |
|---|---|
| Scalability | Can the tool grow with your business? Consider if it handles increased workloads and users without needing constant upgrades. |
| Integrations | Does it work with your existing tools? Check for compatibility with CI/CD pipelines, cloud providers, and other essential software. |
| Customizability | Can you tailor it to your needs? Look for options to adjust settings, dashboards, and alerts to match your workflow. |
| Ease of use | Is it user-friendly? Ensure the interface is intuitive and requires minimal training for your team to get started. |
| Implementation and onboarding | How quickly can you start? Evaluate the setup time, availability of resources like training, and support during the initial stages. |
| Cost | Does it fit your budget? Compare pricing plans, watch for hidden fees, and consider the value provided for the price. |
| Security safeguards | Are there strong protections? Look for encryption, access controls, and compliance with industry standards to ensure data safety. |
| Compliance requirements | Does it meet regulations? Verify if the solution aligns with legal standards relevant to your industry, like GDPR or HIPAA. |
What Are Container Security Solutions?
Container security solutions are tools designed to protect containerized applications from vulnerabilities and threats. IT professionals, developers, and security teams generally use these tools to ensure applications run securely in various environments, whether they're using Docker alternatives or other container platforms. Vulnerability scanning, compliance checks, and runtime protection help with identifying risks, meeting regulations, and safeguarding operations. These tools provide essential security to keep your containerized applications safe and compliant.
Features
When selecting container security solutions, keep an eye out for the following key features:
- Vulnerability scanning: Identifies and alerts you to potential security risks within your container images and running applications.
- Compliance checks: Ensures that your containers meet industry standards and regulations like GDPR and HIPAA.
- Runtime protection: Monitors and defends against threats during the execution of containerized applications.
- Integration capabilities: Works seamlessly with your existing CI/CD pipelines and cloud providers to maintain security across development stages.
- Role-based access control: Allows you to set permissions and manage user access to sensitive information and actions.
- Automated remediation: Provides automatic fixes for identified vulnerabilities, reducing the need for manual intervention.
- Real-time alerting: Notifies your team immediately about security incidents, allowing for quick response.
- Customizable dashboards: Offers a tailored view of security metrics and alerts, making it easier to monitor what's important to you.
- Encryption: Ensures that data within containers is protected from unauthorized access.
- Machine learning-based threat detection: Uses advanced algorithms to identify and predict potential threats, enhancing overall security measures.
Benefits
Implementing container security solutions provides several benefits for your team and your business. Here are a few you can look forward to:
- Enhanced security: By using vulnerability scanning and runtime protection, you reduce the risk of breaches and protect sensitive data.
- Regulatory compliance: Compliance checks ensure your operations meet necessary legal standards, avoiding fines and legal issues.
- Time savings: Automated remediation and real-time alerting allow your team to respond quickly to threats without manual effort.
- Improved efficiency: Integration capabilities with existing tools streamline processes and maintain security throughout development.
- Access control: Role-based access control helps manage who can access what, reducing the chance of unauthorized actions.
- Informed decision-making: Customizable dashboards provide insights into security metrics, helping you make better-informed security decisions.
- Data protection: Encryption ensures data is safe from unauthorized access, maintaining confidentiality and integrity.
Costs & Pricing
Selecting container security solutions requires an understanding of the various pricing models and plans available. Costs vary based on features, team size, add-ons, and more. The table below summarizes common plans, their average prices, and typical features included in container security solutions:
Plan Comparison Table for Container Security Solutions
| Plan Type | Average Price | Common Features |
|---|---|---|
| Free Plan | $0 | Basic vulnerability scanning, limited compliance checks, and community support. |
| Personal Plan | $5-$25/user/month | Advanced scanning, basic runtime protection, and email support. |
| Business Plan | $30-$75/user/month | Full compliance checks, integration capabilities, and role-based access control. |
| Enterprise Plan | $100+/user/month | Customizable dashboards, machine learning threat detection, and dedicated support. |
Container Security Solutions FAQs
What trade-offs should you expect between open source and commercial container security tools?
With open source tools, you often get flexibility, customization, and no license fees—but you’ll usually shoulder more integration work, tuning, and support burden. Commercial solutions tend to bundle more out-of-the-box features (dashboards, alerts, policy engines), but you may be locked into vendor constraints or higher cost as you scale. You’ll want to weigh your team’s maturity, your environments’ complexity, and your willingness to build glue between tools.
What challenges arise when securing containers across multicloud or hybrid infrastructures?
In multicloud settings, you’ll face inconsistent APIs, differing identity models, and divergent network policies. A solution that works in AWS might not map cleanly to Azure or on-prem. You’ll need tooling that abstracts across these differences (or uses a central control plane) and enables security posture uniformity across clouds.
How can I resolve issues with containers exiting unexpectedly in AWS Fargate?
Unexpected container exits in AWS Fargate may be due to resource limitations or misconfigurations. Check the task definition for correct resource allocations and review logs for error messages. Adjusting memory or CPU settings might resolve the issue.
How do you manage false positives in vulnerability scans of container images?
False positives are common when scanners flag low-impact issues or dependencies your app doesn’t actually use. To reduce noise, tune your scanner thresholds, suppress alerts from low-risk findings, and correlate scan results over time to see persistent issues. You can also cross-validate findings with multiple tools or use a meta-framework (e.g. LUCID) to reduce inconsistencies across scanners.
What’s Next:
If you're in the process of researching container security solutions, connect with a SoftwareSelect advisor for free recommendations.
You fill out a form and have a quick chat where they get into the specifics of your needs. Then you'll get a shortlist of software to review. They'll even support you through the entire buying process, including price negotiations.