

10 Best AI Compliance Tools in 2026

Best AI Compliance Tools Shortlist


AI compliance tools help businesses monitor, document, and automate compliance with AI-related regulations, frameworks, and risk controls. With more regulators and customers demanding evidence that you’re governing AI deployments—across privacy, security, transparency, and evolving standards—you need systems built for cross-framework controls and real-time oversight.
In this guide, I’ll help you find options that fit modern IT workflows so you can address regulatory requirements, support enterprise growth, and prove business value.
Why Trust Our Software Recommendations
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
AI Compliance Tools Comparison Table
Compare pricing and specs, side by side, for the tools that made it onto my shortlist.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for governance across SOC 2 and AI frameworks | Free demo + free trial available | Pricing upon request | Website | |
| 2 | Best for unified privacy risk visibility | Free demo available | Pricing upon request | Website | |
| 3 | Best for enterprise GRC with control drift detection | Free demo available | Pricing upon request | Website | |
| 4 | Best for GRC mapped to quantitative financial risk | Free demo available | Pricing upon request | Website | |
| 5 | Best for closed-loop control monitoring | Free demo available | Pricing upon request | Website | |
| 6 | Best for AI governance mapped to ISO 42001 | Free demo available | Pricing upon request | Website | |
| 7 | Best for DevSecOps-native compliance automation | Free demo available | Pricing upon request | Website | |
| 8 | Best for AI governance across 35+ frameworks | Free demo available | Pricing upon request | Website | |
| 9 | Best for EU AI Act compliance | Free demo available | Pricing upon request | Website | |
| 10 | Best for GRC evidence tied to revenue impact | Free demo available | Pricing upon request | Website |
AI Compliance Tools Reviews
Below are detailed summaries of each platform on my shortlist, covering key features, pricing, and pros and cons to help you find the best one.
Best for governance across SOC 2 and AI frameworks
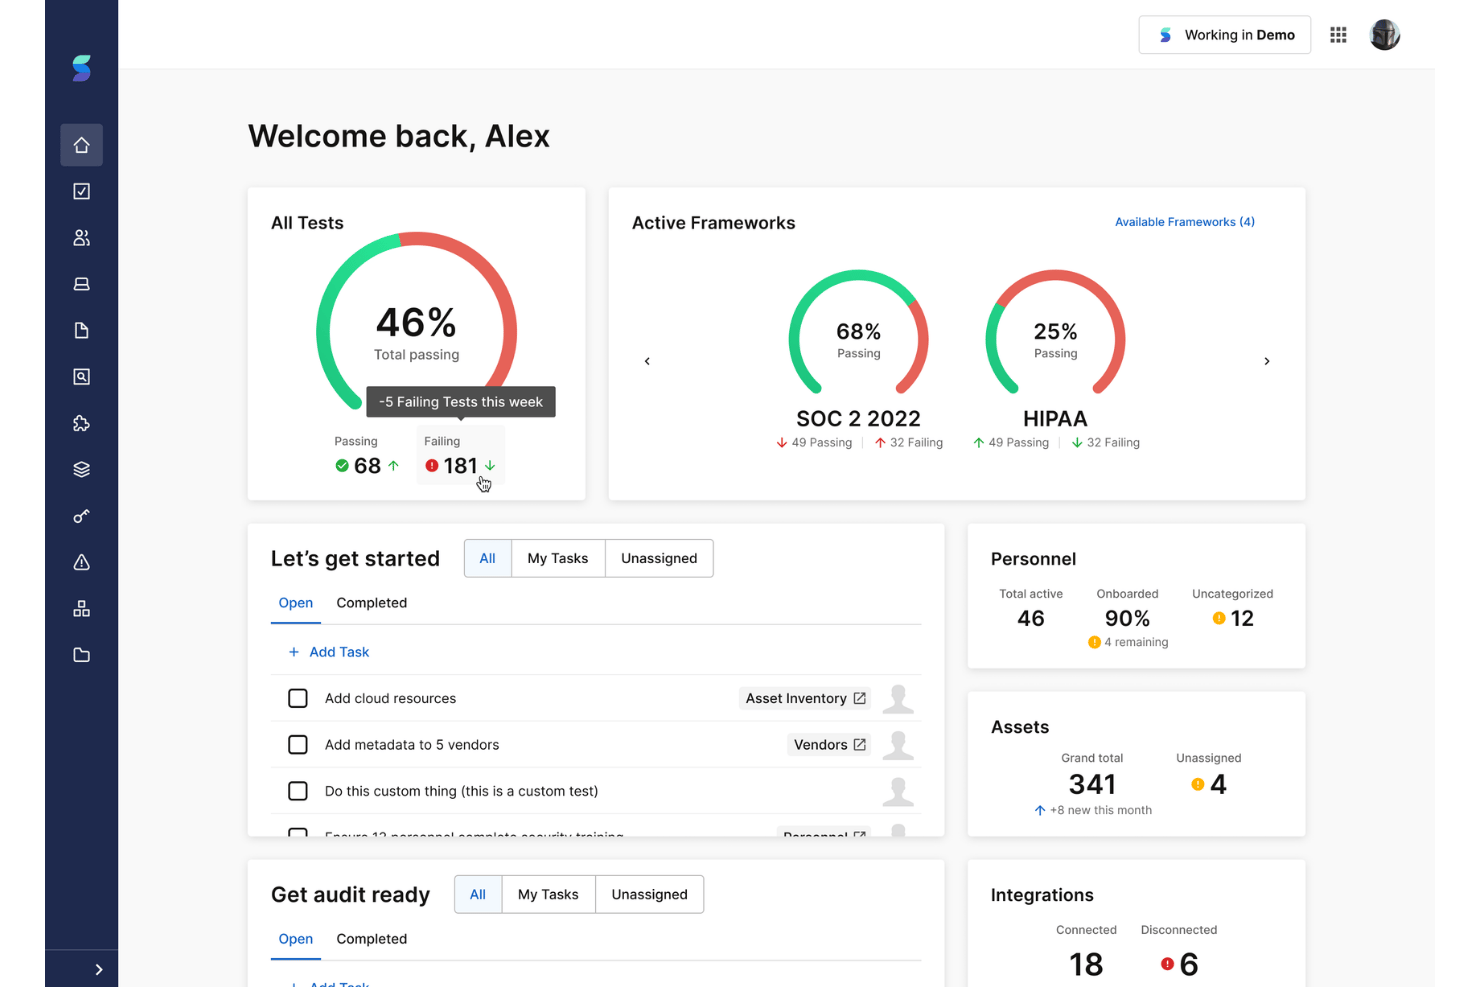
Secureframe is an AI compliance platform that automates evidence collection, control monitoring, risk assessment, and policy documentation across 35+ frameworks, including SOC 2, ISO 27001, HIPAA, NIST AI RMF, ISO 42001, and the EU AI Act.
Who Is Secureframe Best For?
Secureframe is a strong fit for security and compliance teams at growth-stage and mid-market companies that need to manage AI compliance obligations alongside traditional frameworks like SOC 2 and ISO 27001.
Why I Picked Secureframe
I picked Secureframe because it's one of the few platforms that treats AI governance as a first-class compliance obligation, not an afterthought. It natively supports NIST AI RMF, ISO 42001, and the EU AI Act alongside SOC 2, with prebuilt control mappings for all three. Comply AI for Control Mapping then cross-maps those AI-specific controls to your existing SOC 2 or ISO 27001 program, so you're not duplicating work across frameworks.
Secureframe Key Features
- Comply AI for policies: Uses generative AI to draft and refine security and compliance policies, with an AI-powered text editor for adjusting tone and specificity.
- Comply AI for risk: Accepts a risk description as input and automatically produces an inherent risk score, treatment plan, and residual risk score.
- Secureframe Agent: Collects device-level compliance evidence directly from endpoints for use in automated control tests and auditor review.
- Audit Partner Program: Connects customers with vetted CPA firms through a shared auditor console and data room for evidence review.
Secureframe Integrations
Secureframe offers 300+ native integrations, including AWS, Microsoft Teams, Google Cloud Platform, GitHub, Jira, Linear, Asana, and ClickUp. It also supports a REST API for custom integrations.
Pros and Cons
Pros:
- Integrates risk scoring and automated remediation
- AI-driven evidence validation for audits
- Supports EU AI Act and ISO 42001
Cons:
- Manual evidence uploads required for some controls
- Renewal pricing can escalate significantly
OneTrust
Best for unified privacy risk visibility
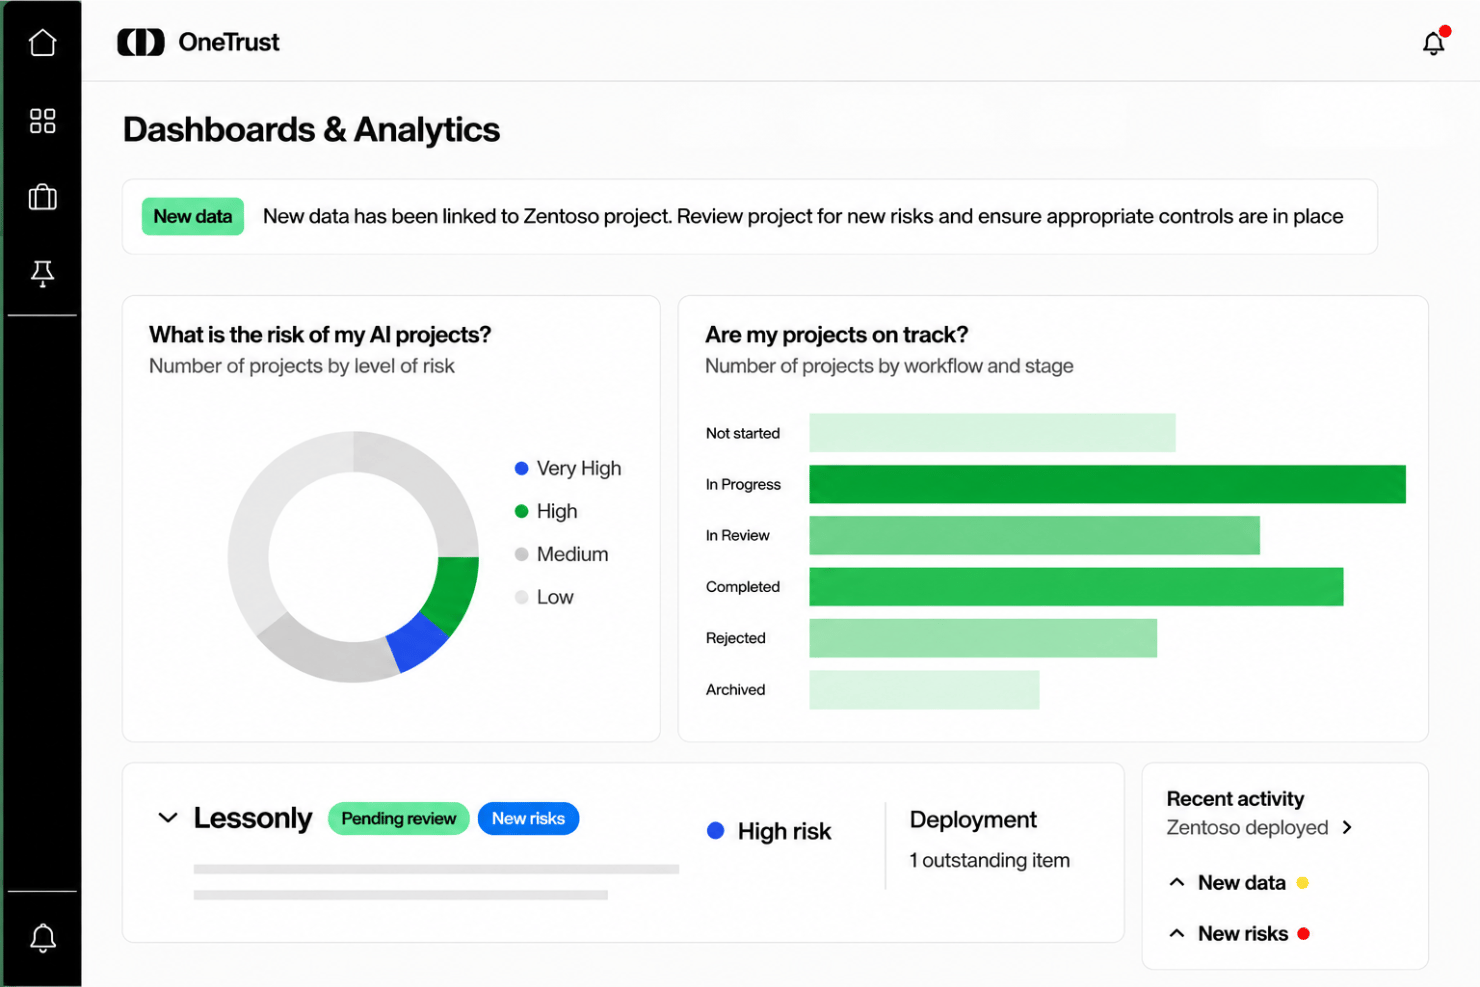
OneTrust is an AI governance and compliance platform that centralizes AI inventory management, multi-framework risk assessment, automated evidence collection, and regulatory change monitoring across privacy, tech risk, and third-party domains.
Who Is OneTrust Best For?
OneTrust is best suited to large enterprises that need a single platform to manage AI governance, privacy risk, and compliance across multiple regulatory frameworks simultaneously.
Why I Picked OneTrust
OneTrust earns its spot on my shortlist because no other platform connects AI risk, privacy exposure, and regulatory compliance into a single, unified view the way it does. I particularly like the AI Governance module's runtime monitoring across Amazon Bedrock, Azure AI Foundry, and Databricks, which surfaces model usage, safety signals, and guardrail violations in production rather than just at assessment time. Pair that with DataGuidance tracking AI regulations across 300+ jurisdictions daily, and you get a live picture of both your internal AI risk and the external regulatory landscape shifting around it.
OneTrust Key Features
- AI Policy Manager: Enforces prompt and output policies in real time across AI systems, with filtering, blocking, redacting, and escalation controls built in.
- Privacy Breach Response Agent: Automates breach investigation workflows, maps impacted jurisdictions, and pre-populates regulatory notification reports using agentic AI.
- Agent governance: Registers AI agents with defined purposes, audits Model Context Protocol environments, and governs multi-agent workflow permissions.
- DataGuidance Copilot: Translates daily regulatory updates across 300+ jurisdictions into actionable compliance workflows directly within the platform.
OneTrust Integrations
OneTrust offers 100+ pre-built connectors, including Adobe, Snowflake, Microsoft 365, Google Cloud, Asana, Kafka, Databricks, Okta, and RiskRecon. It also provides APIs and SDKs to support custom integrations.
Pros and Cons
Pros:
- Industry-leading regulatory intelligence and guidance
- Maps controls to 55+ global frameworks
- Monitors AI risk in production environments
Cons:
- Delayed support response reported by some users
- Complex configuration for cross-module workflows

Archer
Best for enterprise GRC with control drift detection
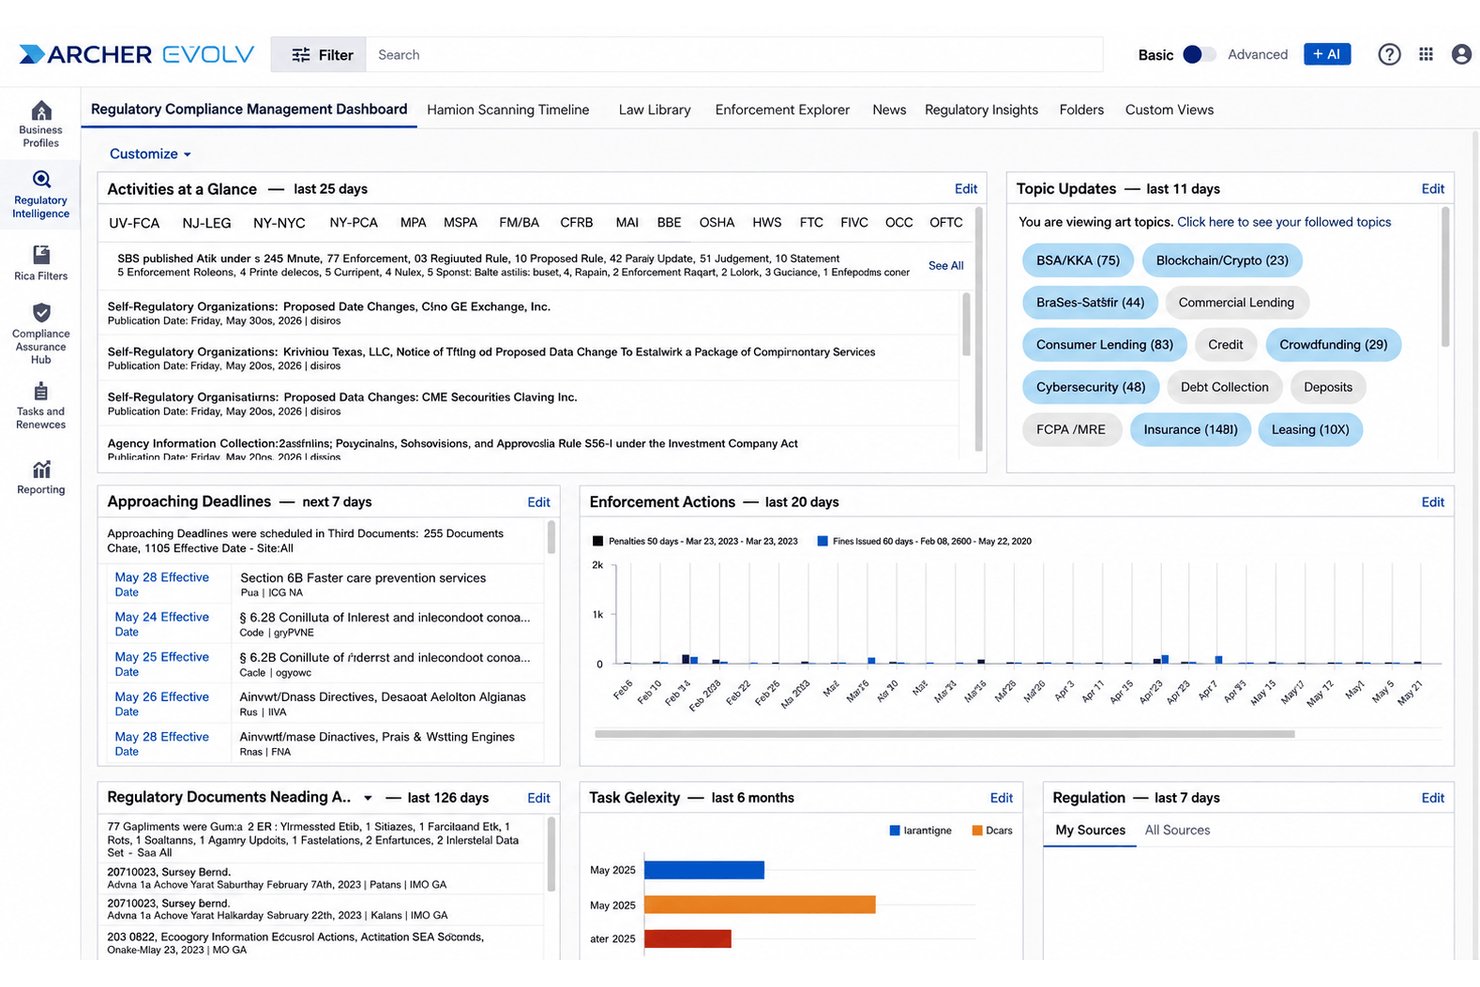
Archer is an enterprise GRC platform that combines continuous controls monitoring, automated evidence collection, multi-framework compliance mapping, AI-driven risk assessment, and a dedicated AI governance module for managing model inventories and regulatory obligations.
Who Is Archer Best For?
Archer is built for large enterprises and regulated industries—think financial services, healthcare, and public sector—where IT risk, compliance, and audit functions need to operate from a single, deeply integrated platform.
Why I Picked Archer
Archer earns its spot on my shortlist because of how it handles AI control drift detection inside a full enterprise GRC environment. Its Continuous Controls Monitoring module runs near real-time checks across cloud, identity, and IT systems, flagging the moment a control drifts out of alignment with frameworks like SOC 2, NIST CSF, or FedRAMP. I also like that its purpose-built GRC AI models automatically route remediation tasks when gaps surface, so nothing stalls waiting on manual triage.
Archer Key Features
- Obligation Extraction AI: Converts dense regulatory text into up to 10,000 structured, traceable obligations clustered for review.
- Predictive risk modeling: Archer Evolv Risk quantifies exposure across operational, IT, and third-party risk domains, prioritized by financial impact.
- Vendor lifecycle management: Manages third-party risk from intake and tiering through due diligence, continuous monitoring, and offboarding.
- Policy lifecycle management: Supports authoring, review, approval, and publishing of policies with exception tracking tied to expiry dates.
Archer Integrations
Archer offers integrations with AWS, Azure, Konexus, Trustero AI, Slack, and Microsoft OneDrive. An API for custom integrations is also available.
Pros and Cons
Pros:
- Cross-framework mapping reduces duplicate compliance work
- EU AI Act-aligned controls library included
- AI detects real-time compliance control drift
Cons:
- GenAI policy drafting lagging vs. competitors
- User interface is not intuitive
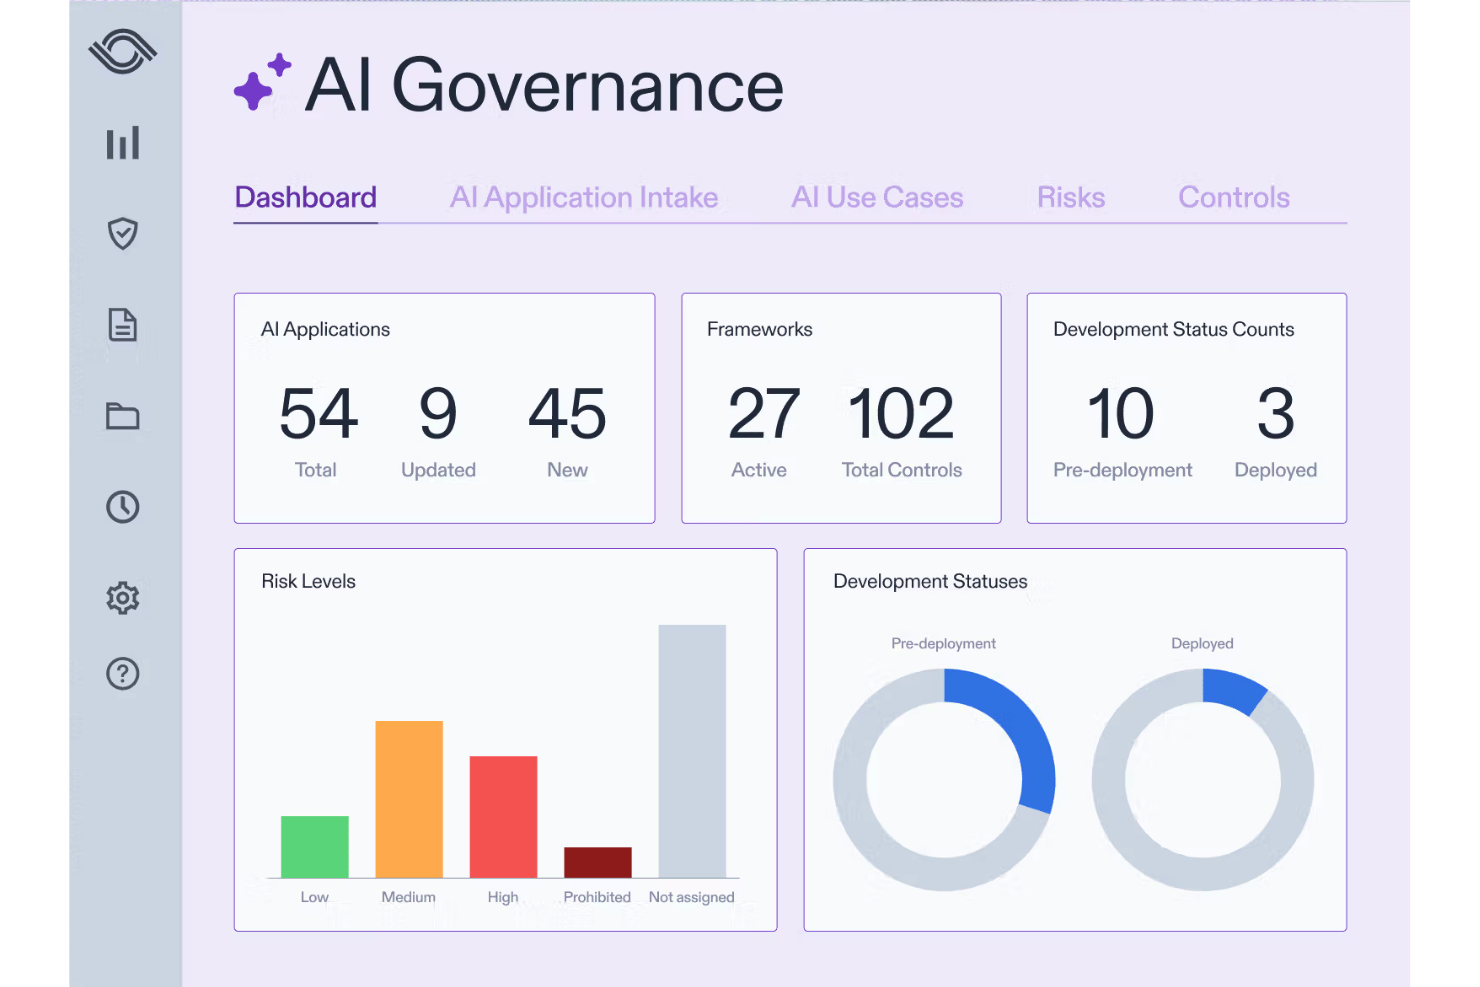
Optro is an AI-powered GRC platform that unifies compliance control monitoring, internal audit, quantitative risk analysis, and AI governance across 30+ prebuilt regulatory frameworks.
Who Is Optro Best For?
Optro fits enterprise compliance and risk teams that need to connect GRC controls directly to quantitative financial risk analysis—particularly where audit, risk, and AI governance need to live in one platform.
Why I Picked Optro
I picked Optro as one of the best because it's the only GRC platform I've seen that connects compliance controls directly to quantitative financial risk analysis using Monte Carlo simulations and Bowtie methodology. That means that when a vulnerability surfaces, Optro's AI generates a narrative explaining its financial impact, not just a technical severity score. Its Continuous Control Monitoring layer pairs with 30+ prebuilt frameworks, including the EU AI Act and ISO 42001, to flag control gaps in real time.
Optro Key Features
- GRC-trained AI drafting: Generates risk narratives, control descriptions, and audit test procedures using AI models trained on GRC-specific data.
- Unified Compliance Framework cross-mapping: Maps a single control across multiple frameworks simultaneously, covering SOC 2, ISO 27001, FedRAMP, DORA, and others.
- Real-time KRI monitoring: Tracks key risk indicators with automated alerts when thresholds are breached across the connected risk platform.
- Cyber risk narrative generation: Generates explanations of how specific vulnerabilities affect an organization's security posture and financial exposure.
Optro Integrations
Optro provides integrations with tools like AWS, Jira, ServiceNow, and Workday. For custom data workflows, it offers REST/SCIM APIs and an MCP server.
Pros and Cons
Pros:
- Real-time regulatory change impact mapping
- Covers multiple regulatory compliance frameworks
- Quantitative risk analysis tied to controls
Cons:
- Some evidence collection still requires manual input
- No built-in customer trust portal
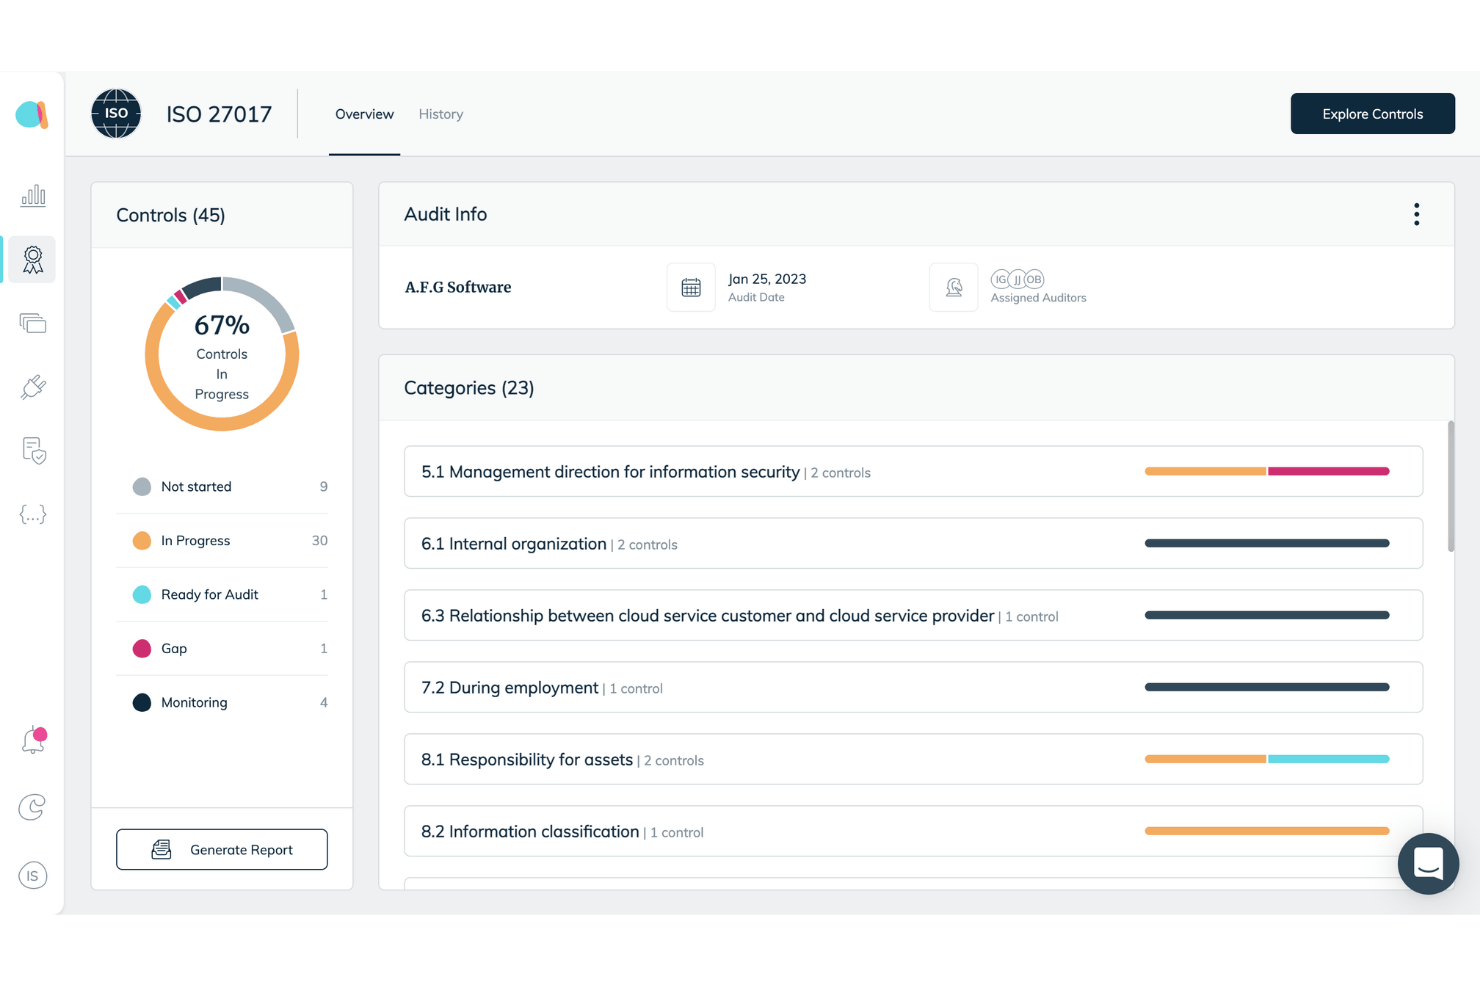
Anecdotes is an agentic GRC tool that handles continuous control monitoring, automated evidence collection, multi-framework compliance mapping, enterprise risk management, and third-party risk assessment.
Who Is Anecdotes Best For?
Anecdotes is a strong fit for mid-market and enterprise security and compliance teams managing regulatory frameworks across complex, multi-entity environments.
Why I Picked Anecdotes
Anecdotes earns its spot on my shortlist because its Agentic Continuous Control Monitoring (A-CCM) doesn't just flag control gaps—it closes them. When A-CCM detects something like MFA disabled in Azure AD, it auto-creates a Jira ticket, notifies the responsible owner via Slack, and re-verifies the fix before updating the risk register. I also rate the Policy Guardian module highly, as it continuously compares live policies against real evidence between review cycles, surfacing implementation gaps that periodic audits routinely miss.
Anecdotes Key Features
- Agentic Enterprise Risk Management (A-ERM): Automatically recalculates residual risk scores when connected controls change, with bi-directional risk-control mapping and customizable risk registers.
- Data Engine: Pulls structured evidence from connected systems, including metadata, timestamps, and source IDs, in a format accepted by Big Four audit firms.
- Agent Studio: Creates custom AI agents that respond to specific compliance scenarios beyond the out-of-the-box agent library.
- Trust Center: Reflects your certification and control status in real time, with DocuSign-powered NDA access and access controls.
Anecdotes Integrations
Anecdotes offers 230+ native integrations, including AWS, Microsoft Entra ID, Okta, GitHub, Jira, Salesforce, and CrowdStrike. It also offers an API and supports MCP for custom connectivity.
Pros and Cons
Pros:
- Risk analysis links evidence, controls, and frameworks
- Policy module checks live implementation, not just docs
- AI auto-remediates detected compliance gaps
Cons:
- Custom audit reports often need vendor support
- No automation for inbound security questionnaires

Sprinto
Best for AI governance mapped to ISO 42001
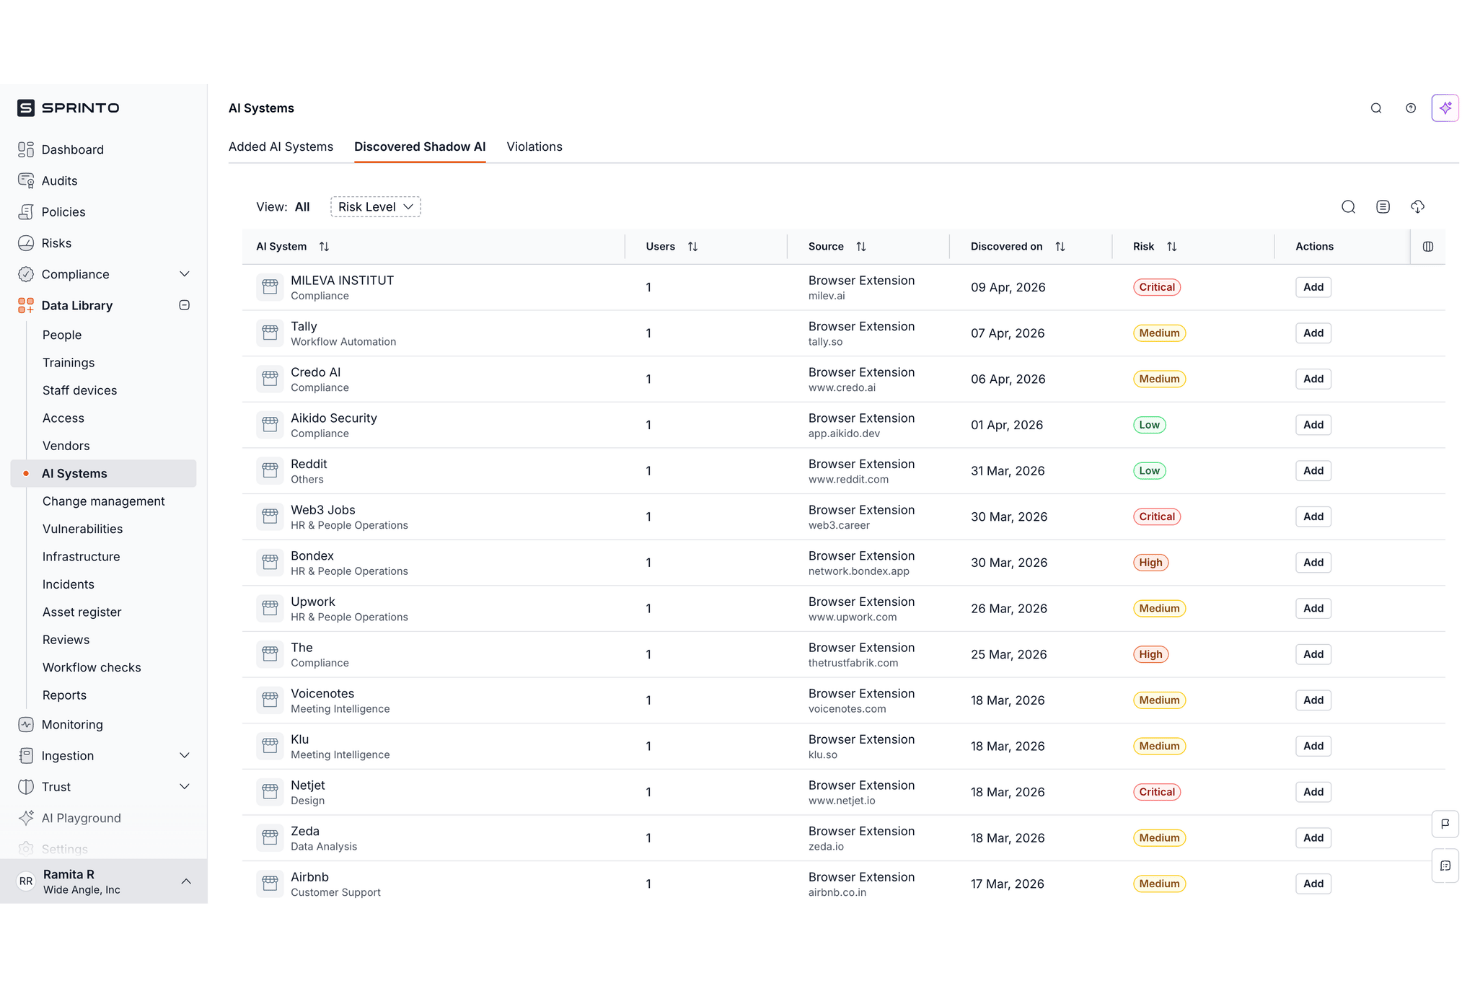
Sprinto is an AI-native GRC platform that automates evidence collection, control monitoring, risk scoring, and compliance documentation across 200+ frameworks, including AI-specific standards like ISO 42001 and the EU AI Act.
Who Is Sprinto Best For?
Sprinto is a strong fit for mid-market to enterprise security and compliance teams that need to govern internal AI systems alongside traditional GRC workflows.
Why I Picked Sprinto
Sprinto earns its spot on my shortlist because its dedicated AI Governance module does something few GRC platforms actually do: it maps your live AI system inventory directly to the EU AI Act and NIST AI RMF. I particularly like how it discovers shadow AI adoption across the organization and classifies each system by data risk level, so you're not manually cataloging tools. The Evidence Gap Detection Agent then proactively flags missing or stale evidence before an auditor ever sees it.
Sprinto Key Features
- AI security questionnaire automation: Pulls from past DDQs, policies, and audit evidence to auto-draft answers to inbound vendor questionnaires across formats like Excel, CSV, and browser-based portals.
- Auditor Portal: Allows external auditors to access evidence, review controls, and submit follow-up requests, eliminating spreadsheet-based back-and-forth.
- Unified Commitments module: Maps overlapping requirements across multiple regulatory frameworks to a single set of unified controls, reducing duplicate compliance work.
- Zones for multi-entity management: Run separate compliance programs for different business units, regions, or products under one dashboard without mixing their respective control environments.
Sprinto Integrations
Sprinto integrates with AWS, Adobe, Google Cloud Platform, Okta, GitHub, GitLab, Jira, Airtable, Rippling, and BambooHR. It also supports Zapier and an API for custom integrations.
Pros and Cons
Pros:
- Provides dedicated implementation managers
- Includes pre-built, audit-tested policy templates
- Maps compliance across multiple frameworks
Cons:
- Custom compliance workflows require Growth plan
- No instant platform access for new users

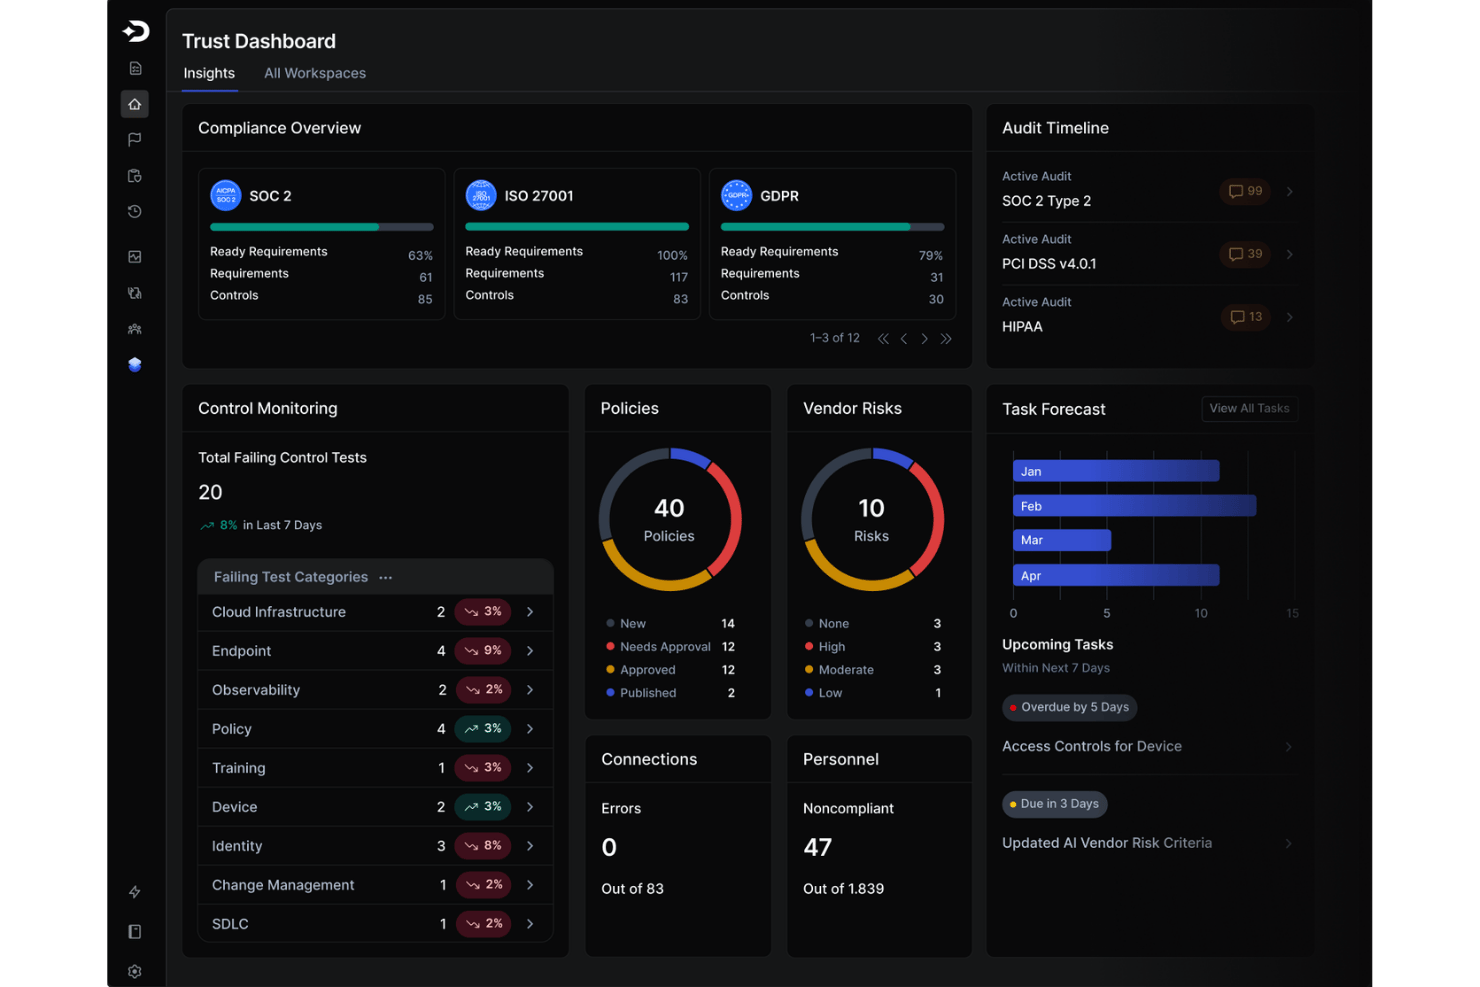
Drata is a compliance automation platform that offers control monitoring, automated evidence collection, AI-powered risk assessment, and multi-framework support across 30+ compliance standards.
Who Is Drata Best For?
Drata is a strong fit for engineering-led organizations where compliance needs to live inside the development workflow, not alongside it.
Why I Picked Drata
I picked Drata as one of the best because it's the only platform I've seen that treats compliance as an engineering problem from the ground up. Compliance as Code scans infrastructure-as-code in GitHub and Bitbucket during development, then auto-generates pull requests with the exact location and fix for each failure, catching gaps before they ever hit production. I also love the AI Agent Governance module, which discovers every AI agent running in your environment and enforces policies before agent actions execute, producing auditor-grade logs mapped to ISO 42001 and the EU AI Act.
Drata Key Features
- Audit Hub: Allows external auditors to review evidence, submit requests, and manage approvals without email or spreadsheet exchanges.
- AI questionnaire assistance: Drafts answers to security questionnaires (CAIQ, SIG, VSAQ, and custom DDQs) by pulling from your internal knowledge base and Trust Center.
- Trust Center portal: Publish your security posture and let prospects request documents under NDA without involving your team.
- Agentic TPRM assessment: Autonomously retrieves vendor documents, evaluates them against your criteria, generates follow-up questions, and produces risk-scored assessment outputs.
Drata Integrations
Drata offers 300+ native integrations, including AWS, Microsoft Azure, Google Cloud Platform, Okta, GitHub, 1Password, ADP, Atlassian, Slack, and Microsoft Teams. It also provides an API for custom connections.
Pros and Cons
Pros:
- Eliminates hours of manual evidence collection
- Offers real-time auditor collaboration
- Avoids duplicate effort by testing controls
Cons:
- Non-intuitive user interface
- AI Agent Governance not generally available
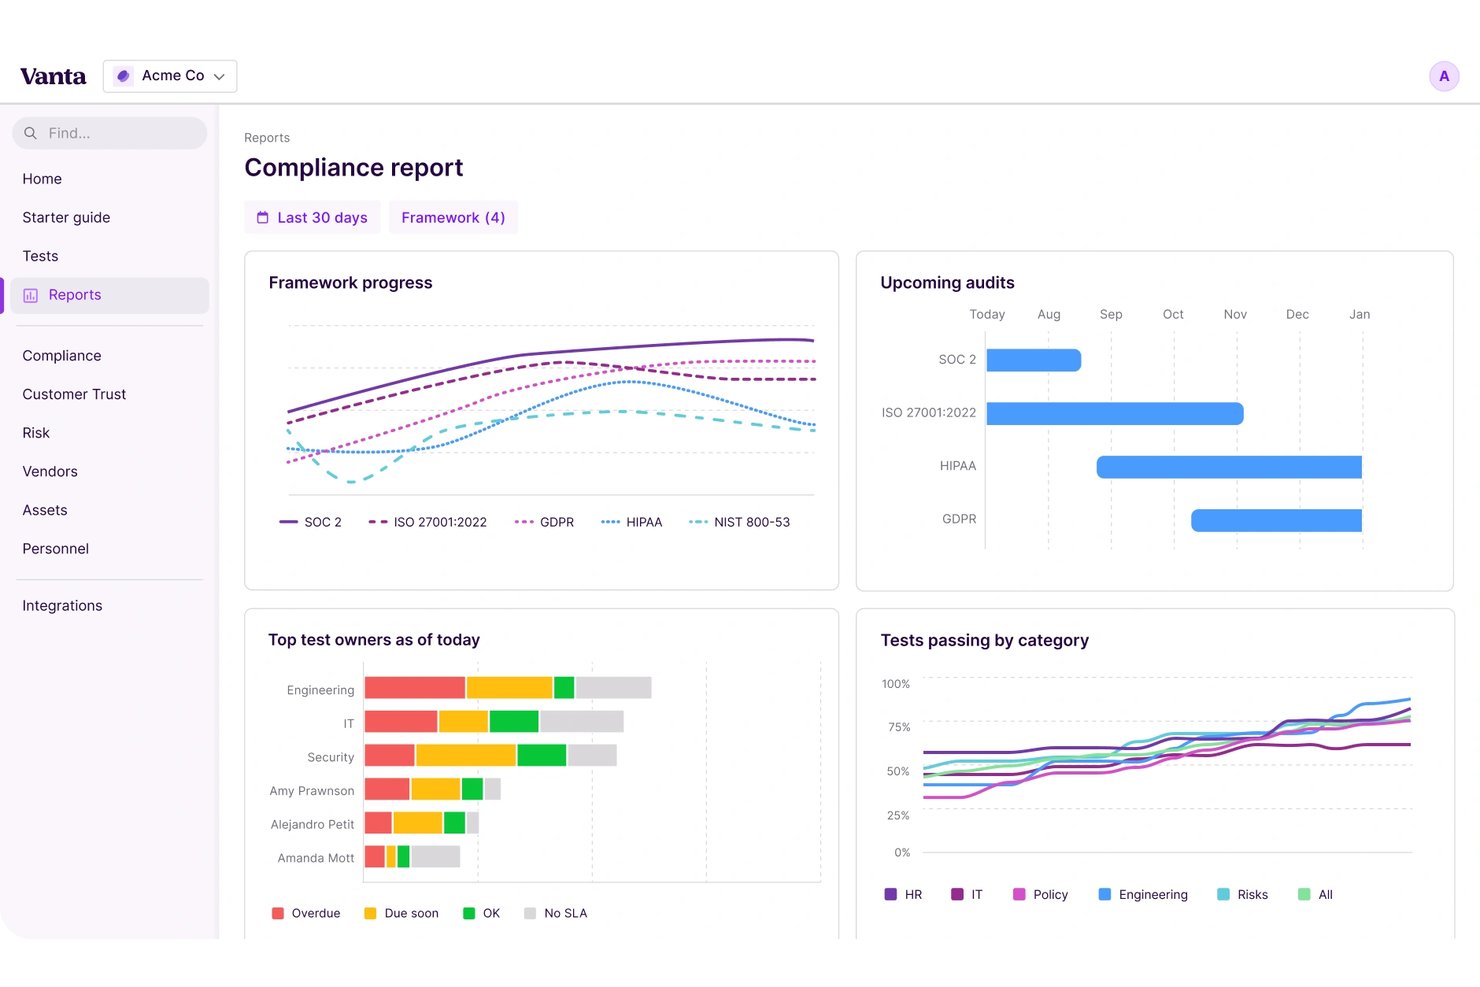
Vanta is an AI compliance platform that combines continuous control monitoring, automated evidence collection, multi-framework management, and a dedicated AI governance module covering standards like ISO 42001, EU AI Act, and NIST AI RMF.
Who Is Vanta Best For?
Vanta is a strong fit for security and compliance teams at mid-market to enterprise companies managing multiple regulatory frameworks.
Why I Picked Vanta
Vanta is one of my top picks because I love how the dedicated AI Governance module handles ISO 42001, EU AI Act, and NIST AI RMF alongside your existing SOC 2 or ISO 27001 program. The Framework Evidence Overlap Visualization shows exactly where evidence carries across frameworks, so your team isn't duplicating work. I also find the AI Security Assessment tool genuinely useful for evaluating risks tied to specific AI models, not just general security controls.
Vanta Key Features
- Continuous monitoring: Tracks real-time third- and fourth-party risks, including breaches, misconfigurations, and leaked credentials, with AI-powered scoring to filter noise.
- Trust Center portal: Continuously synced compliance page with an AI-powered chatbot that answers buyer questions and links activity to revenue attribution.
- Framework Version Manager: Highlights changes between framework versions, imports existing customizations, and enables side-by-side previews when transitioning standards.
- AI-generated policy drafting: Generates new policies from scratch or bulk-onboards existing ones, extracting titles, version history, and SLAs.
Vanta Integrations
Vanta integrates with AWS, Microsoft Azure, Google Cloud Platform, GitHub, GitLab, Okta, Google Workspace, Jira, Slack, and Salesforce. It also provides the Vanta API for custom integrations and developer workflows
Pros and Cons
Pros:
- GenAI drafts and updates compliance policies
- Risk Graph links controls, vendors, and systems
- AI automates evidence validation and remediation
Cons:
- Customer support quality varies by contract size
- Plan tiers cap questionnaire automation volume
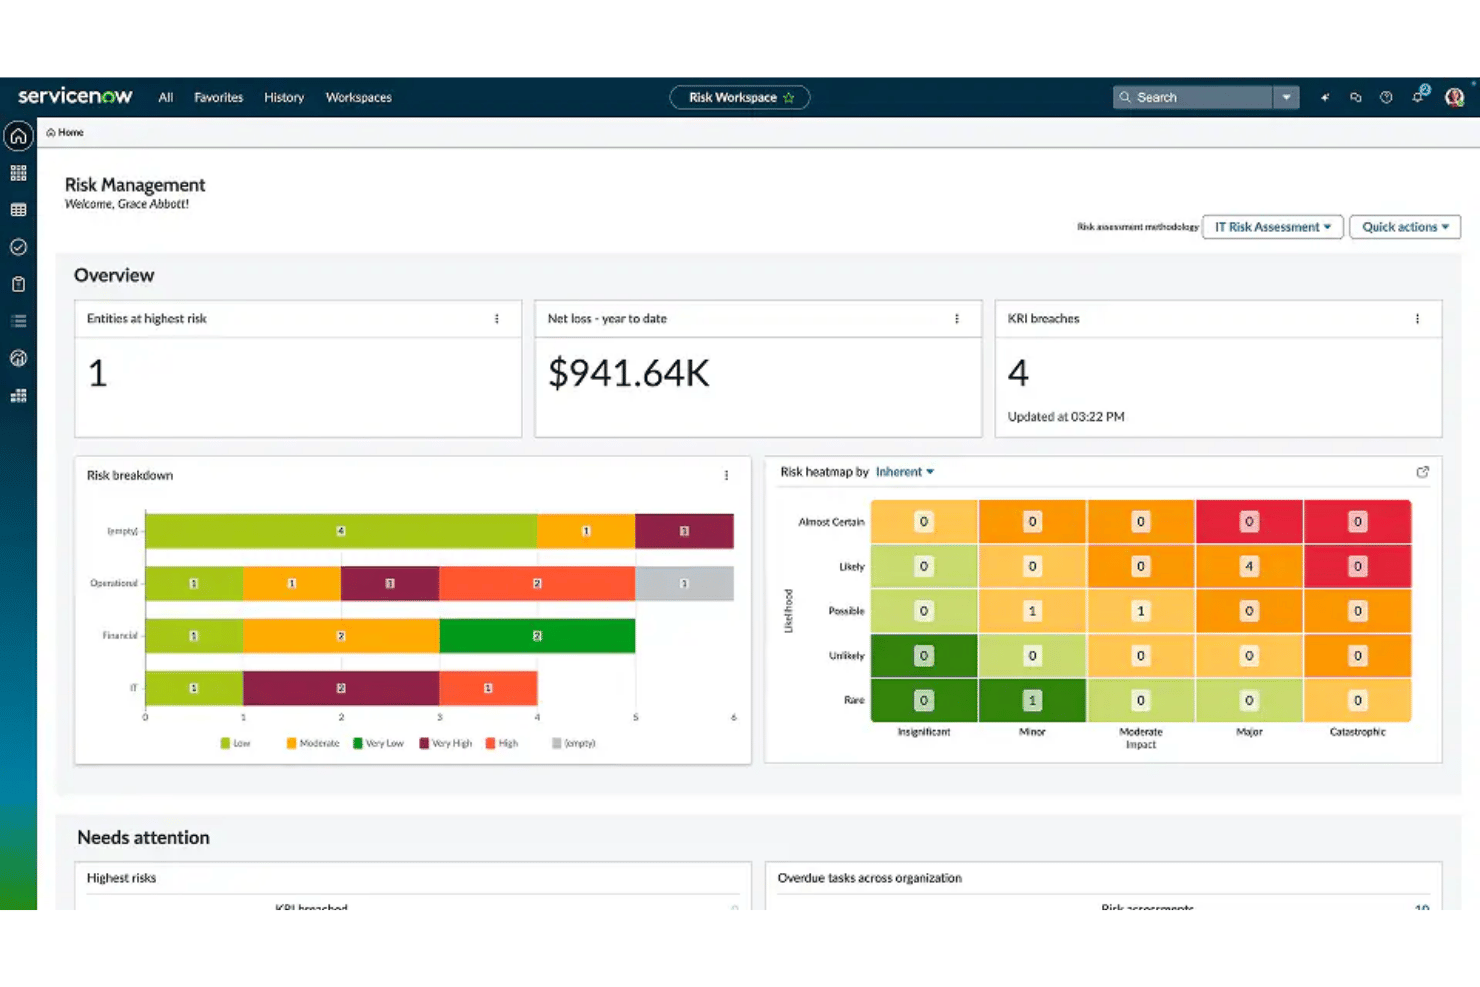
ServiceNow GRC is an enterprise governance, risk, and compliance platform that combines continuous control monitoring, AI-powered risk assessment, and multi-framework regulatory coverage.
Who Is ServiceNow GRC Best For?
ServiceNow GRC is ideal for large enterprises that already use ServiceNow and require a unified platform to manage both traditional IT risks and internal AI system governance.
Why I Picked ServiceNow GRC
I've included ServiceNow GRC in my top picks because its AI Control Tower is the only enterprise GRC offering I know of that tracks AI models and datasets as CMDB configuration items, then automatically classifies them against EU AI Act risk tiers. The AI Risk and Compliance Content Pack layers on pre-built control objectives and risk statements for NIST AI RMF and ISO/IEC 42001—covering key requirements like AI explainability, bias detection, and algorithmic governance—so your team isn't mapping those frameworks from scratch.
ServiceNow GRC Key Features
- GRC Continuous Monitoring: Automatically calculates control compliance on an ongoing basis from configuration scan results collected across connected systems.
- Third-Party Risk Management: Manages vendor portfolios with automated tiering, configurable risk scoring, and continuous vendor risk monitoring through a dedicated TPRM module.
- Regulatory Change Management: Pulls in regulatory alerts from external feeds and uses AI to analyze impact across your existing controls, policies, and processes.
- Continuous Authorization and Monitoring (CAM): Runs automated controls testing against FedRAMP-style authorization workflows, including OSCAL-compliant data export and proactive violation detection.
ServiceNow GRC Integrations
ServiceNow GRC integrates natively with ITSM, ITOM, ITAM, and SecOps, and external platforms like AWS, Microsoft Azure, Google Cloud, Jira, GitHub, and Veza. It also offers a REST API, webhooks, and Service Graph Connectors for custom integrations.
Pros and Cons
Pros:
- Automated risk tiering of internal AI systems
- Strong multi-framework compliance
- Unifies data across IT, Security, HR, and vendors
Cons:
- Non-IT users report challenging overall experience
- Implementation requires major configuration and services
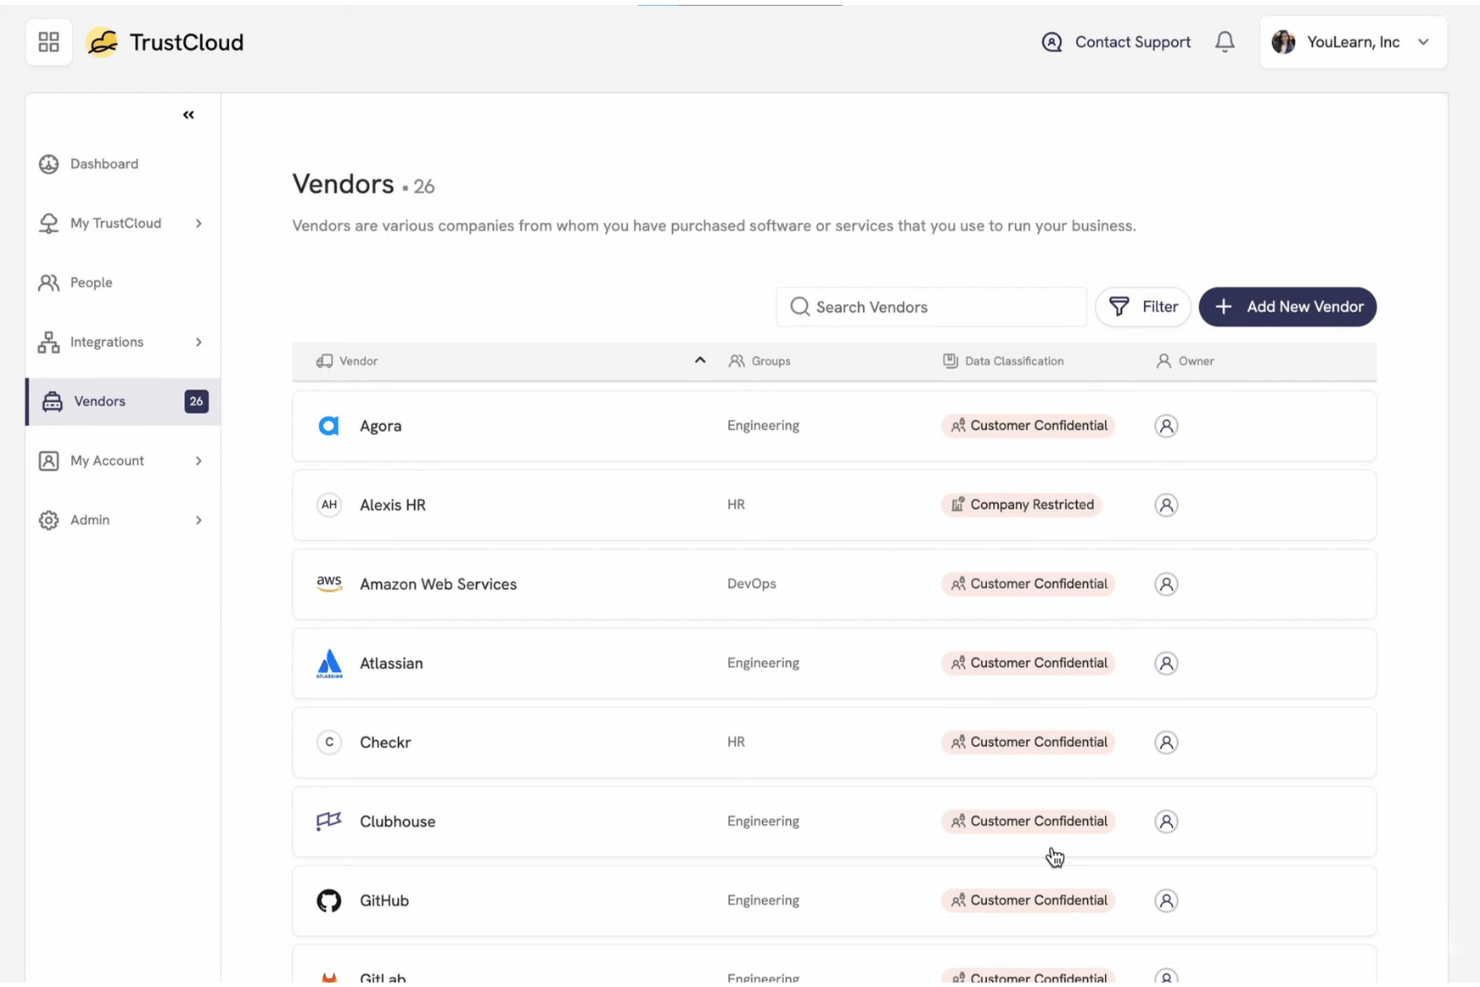
TrustCloud is a GRC platform that combines continuous control monitoring, automated evidence collection, multi-framework compliance, and AI-driven risk quantification across cloud and on-premises environments.
Who Is TrustCloud Best For?
TrustCloud is a strong fit for security and compliance teams at growth-stage and enterprise companies that need to connect GRC program performance to business outcomes like revenue.
Why I Picked TrustCloud
TrustCloud earns its spot on my shortlist because it's the only platform I've seen that connects control failures directly to dollar figures and pipeline. Its TrustShare portal tracks security reviews through to closed-won revenue, giving CISOs a concrete way to show GRC's business value. I also like that ConMon tests 10M+ records continuously using a deterministic rules engine, so every piece of evidence is citeable and auditor-ready, not a black-box output.
TrustCloud Key Features
- Common Control Framework: Maps controls across 18+ prebuilt frameworks so overlapping requirements in SOC 2, ISO 27001, GDPR, and others are populated automatically.
- AI Essentials module: Provides native ISO 42001 and NIST AI RMF support, including gap analysis and risk quantification for AI systems.
- GraphAI questionnaire automation: Pre-fills up to 85–90% of incoming security questionnaires using retrieval-augmented generation trained on GRC lexicons, with source citations on every answer.
- TrustHQ executive dashboard: Aggregates security posture, residual risk in dollar terms, and trend data across business units into board-ready reports tied to business goals.
TrustCloud Integrations
TrustCloud integrates with multiple platforms through its Hybrid Data Fabric, including AWS, Google Cloud Platform, Heroku, Okta, Deel, Workday, HiBob, GitHub, Jenkins, and Splunk. It also supports an open API for custom connections.
Pros and Cons
Pros:
- Native frameworks for AI system compliance
- Supports continuous monitoring of controls
- Maps evidence to dollar business impact
Cons:
- Smaller peer review volume than top rivals
- Complexity may slow onboarding for SMBs
Other AI Compliance Tools
Here are some additional platforms that didn’t make it onto my shortlist, but are still worth checking out:
- Hyperproof AI
For multi-framework governance readiness
- RegScale
For FedRAMP and CMMC compliance automation
- LogicGate
For GRC with built-in regulation mapping
- Thoropass
For audit-ready evidence with in-house auditors
- Securiti
For data risk mapped to 1,000+ systems
- Centraleyes
For governance with global regulatory crosswalk
- Strike Graph
For AI-validated evidence collection at scale
- Scytale
For human-expert and AI-backed audit prep
- Cypago
For cross-framework control monitoring


How I Evaluate AI Compliance Tools
To earn a spot on this list, a tool needs to deliver real, measurable value from AI—not just badge AI onto an existing GRC workflow. I split my evaluation into two layers: core functionality every tool must meet (like automated evidence collection and multi-framework control mapping) and differentiating factors that separate the best from the rest.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, and use that to help me assess its overall fit for the list.
- AI control monitoring: I evaluate whether the tool uses ML to detect drift and flag issues in real time, not just run scheduled rule-based checks.
- Automated evidence collection: Each tool should pull evidence directly from connected cloud and identity sources without manual screenshots or spreadsheet uploads.
- Multi-framework coverage: I look for prebuilt mappings across frameworks like SOC 2, ISO 27001, HIPAA, and GDPR, plus AI-specific standards such as ISO 42001 or NIST AI RMF.
- AI risk assessment: The platform should score and prioritize risks using AI, surfacing remediation guidance rather than relying on static risk registers alone.
- Generative AI documentation: I check whether the tool can draft policies, control narratives, or questionnaire responses with framework-aware context for human oversight.
- Integrations and continuous auditing: Native connectors to cloud providers, HRIS, ticketing, and identity systems matter—tools like Vanta and Drata connect to 100+ sources for ongoing audit coverage.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
I look for AI questionnaire automation that goes beyond template fill-ins—tools like Vanta and Drata use RAG engines to draft security questionnaire responses with source citations and confidence scores, which saves hours during prospect reviews. Regulatory change monitoring matters just as much: I check whether a platform can scan for new legislation and automatically map updates to affected controls, so your team isn't manually tracking framework changes. I also evaluate auditor collaboration hubs, where external auditors review and sign off on evidence in-platform instead of trading spreadsheets back and forth.
Beyond Features
I check whether vendors let you opt out of using your data to train shared AI models—tenant isolation and transparent LLM sourcing matter when audit artifacts contain sensitive infrastructure details. Integration depth is just as important: platforms like Drata and Vanta offer config-level reads into AWS, Azure, and Okta, not just surface-level API connections. I also evaluate time-to-value, looking for defined onboarding timelines with dedicated compliance advisors and pre-built framework templates that compress your path to audit readiness.
How to Choose AI Compliance Tools
Finding the best compliance platform means prioritizing controls and automation that match your risk profile, frameworks, and evidence requirements—not just ticking boxes for auditors.
| If your priority is... | Look for... |
|---|---|
| Fast onboarding and audit readiness | Prebuilt templates for SOC 2, ISO, and AI standards |
| Monitoring for control drift and real-time anomalies | ML-driven issue detection and alerting |
| Proving business value from GRC investments | Evidence mapping to revenue or risk impact |
| Managing changes to regulations across regions | Automated regulatory change monitoring |
| Deep integrations with cloud and identity systems | Native connectors with config-level access |
How to Vet Your Shortlist
- Request control mapping exports: Ask for an exported list of mapped controls for at least two frameworks (e.g., SOC 2, ISO 42001) to check coverage.
- Simulate a control drift event: Set up a test environment and trigger an access or configuration change—confirm the platform flags the drift in under 1 hour.
- Run a cloud integration trial: Connect a non-production AWS or Azure account and check what evidence is collected automatically within 24 hours.
- Ask for a data usage policy in writing: Ensure the vendor allows tenant data opt-out for AI model training, and get this as a contractual clause.
- Decide cloud-first vs. legacy GRC backbone: Weigh platforms purpose-built for cloud-native AI governance against GRC suites retrofitted with AI modules—choose based on how embedded cloud systems are in your environment.
What Is an AI Compliance Tool?
An AI compliance tool helps your business monitor, document, and automate adherence to AI regulations, frameworks, and risk controls. These tools support real-time oversight, track regulatory changes, and centralize required evidence for audits. They matter because they let IT specialists ensure AI systems meet security, privacy, and transparency standards while adapting to new requirements without disrupting everyday workflows.
Features of AI Compliance Tools
When selecting the right platform for your team, keep an eye out for the following key features:
- AI control monitoring: Uses AI to spot setting changes, broken rules, and policy breaks right away, replacing slow manual checks.
- Automated evidence collection: Pulls proof directly from cloud systems, login tools, and HR software, so you do not have to upload files or take screenshots by hand.
- Multi-framework mapping: Connects one set of rules to multiple standards like SOC 2, ISO 27001, and GDPR at the same time to save time and prevent missed requirements.
- AI risk assessment: Scores and ranks risks using live data, giving clear fix-it steps instead of static spreadsheets.
- Generative AI documentation: Writes policy drafts, rule descriptions, and survey answers automatically to speed up reports and keep documents current.
- Regulatory change monitoring: Tracks new laws automatically and updates your rules so you stay up-to-date without doing extra research.
- Integration with systems: Plugs straight into your cloud, helpdesk, and login tools to keep data moving without extra steps.
- Auditor collaboration portal: Gives outside auditors a single place to review and approve proof, cutting down on messy emails and spreadsheets.
- Tenant data isolation: Lets you block the system from using your data for AI training, keeping sensitive business information private.
- Continuous auditing capabilities: Runs checks and collects proof year-round so you are always ready for audits without last-minute stress.
Benefits of AI Compliance Tools
These platforms provide several benefits for your team and your business. Here are a few you can look forward to:
- Real-time control monitoring: Machine learning detects control drift and unauthorized changes as they happen, so you catch issues before they escalate.
- Automated evidence collection: The platform pulls audit evidence from cloud and identity systems without manual uploads, cutting down preparation time for audits.
- Multi-framework mapping: Prebuilt control mappings support multiple frameworks and AI standards in one place, reducing gaps and duplication of work.
- AI-driven risk assessment: Live scoring and prioritization of risks helps you focus resources where they’ll have the most impact, supporting remediation with actionable guidance.
- Generative policy documentation: Context-aware AI drafts policies and control narratives, helping you keep documentation aligned with regulatory changes.
- Continuous regulatory updates: The system monitors evolving laws and frameworks, automatically updating your controls so your compliance stays current.
- Tenant data isolation: You can opt out of sharing data for AI training, so sensitive information and audit artifacts stay protected.
Costs and Pricing of AI Compliance Tools
Selecting the right software for AI compliance requires an understanding of the various pricing models and plans available. Costs vary based on features, team size, add-ons, and more. The table below summarizes common plans, their average prices, and typical features included in these tools:
Plan Comparison Table for AI Compliance Tools
| Plan Type | Average Price | Common Features |
|---|---|---|
| Free Plan | $0 | Basic AI control monitoring, limited evidence collection, entry-level framework mapping, and email support. |
| Personal Plan | $30–$75/user/month | Advanced evidence collection, multi-framework mapping, AI risk assessment, generative documentation, and basic integrations. |
| Business Plan | $100–$250/user/month | Full framework mapping, ML-driven control monitoring, regulatory change alerts, cloud integrations, and policy automation. |
| Enterprise Plan | $300–$750/user/month | Custom integrations, auditor collaboration portal, tenant data isolation, continuous auditing, and dedicated onboarding. |
AI Compliance Tools FAQs
Here are some answers to common questions about AI compliance platforms:
How do AI compliance tools handle new and changing regulations?
These tools monitor relevant legislation and standards updates, often using automated feeds or integrated regulatory sources. When a regulation changes, these tools can update control mappings, notify users, and recommend or automate changes needed for compliance. This helps your team stay ahead of shifting regulations without manually tracking every change.
Can I use AI compliance tools with legacy on-premises infrastructure?
Yes, many tools support hybrid environments. While most focus on cloud-native integrations, vendors like Drata and Vanta also offer connectors or manual evidence collection options for on-premises systems. Check which specific integrations each vendor offers and whether manual evidence uploads are allowed for legacy components.
Are there risks with connecting sensitive systems to AI compliance tools?
Yes, connecting sensitive systems to any compliance tool brings risk, especially if those tools train AI models using your data. Look for vendors that offer tenant data isolation and explicit opt-outs from model training. Ask for data usage policies in writing and check their track record with security certifications like SOC 2 Type II or ISO 27001.
Do I need deep AI expertise to use these platforms effectively?
No, most tools are designed for IT professionals and compliance teams who aren’t AI experts. They provide guided workflows, dashboard status alerts, and simple explanations of risks, with optional human expert support for complex situations. Still, it helps if someone on your team can review AI-generated recommendations with a critical eye.
How do AI compliance tools support audit preparation and external auditor collaboration?
These tools let you automate evidence collection, map controls across multiple frameworks, and share artifacts directly with auditors through built-in portals. External auditors can often review, comment, and sign off on evidence within the platform, reducing the need to exchange spreadsheets or email attachments and lowering audit preparation workloads.