

10 Best Certificate Lifecycle Management Software in 2026

Best Certificate Lifecycle Management Software Shortlist


Certificate lifecycle management (CLM) tools track, secure, renew, and revoke digital certificates and keys across your infrastructure. The best platforms discover unmanaged certificates, monitor expiration risk, automate issuance and deployment, and support public and private certificate authorities.
I evaluated tools for hybrid environments, DevOps workflows, device authentication, PKI governance, HSM-backed key control, and Post-Quantum Cryptography (PQC) planning. Use this guide to compare options based on your certificate estate, infrastructure, compliance requirements, and team capacity.
Why Trust Our Software Recommendations
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Compare the Best Certificate Lifecycle Management Software
Compare pricing and specs, side by side, for the top software that made it onto my shortlist.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for managing SSL, SSH, and PGP in one place | Free plan + 30-day free trial available | Pricing upon request | Website | |
| 2 | Best for zero-touch PKI with PQC crypto-agility | Free demo available | Pricing upon request | Website | |
| 3 | Best for CBOM inventory | Free demo available | Pricing upon request | Website | |
| 4 | Best for DevOps-native PKI with multi-CA control | Free plan available | Pricing upon request | Website | |
| 5 | Best for post-quantum cert migration readiness | Free demo + 30-day free trial available | Pricing upon request | Website | |
| 6 | Best for native HSM key control | Free demo available | Pricing upon request | Website | |
| 7 | Best for certificate risk scoring and PQC readiness | Free demo available | Pricing upon request | Website | |
| 8 | Best for EU-regulated PKI environments | Free demo available | Pricing upon request | Website | |
| 9 | Best for F5-integrated zero-touch cert renewal | Free demo + 15-day free trial available | Pricing upon request | Website | |
| 10 | Best for DigiCert-native PQC at scale | Free demo available | Pricing upon request | Website |
Certificate Lifecycle Management Software Reviews
Below are the detailed summaries of the best software on my shortlist, covering key features, integrations, and pros and cons to help you find the right one for your needs.

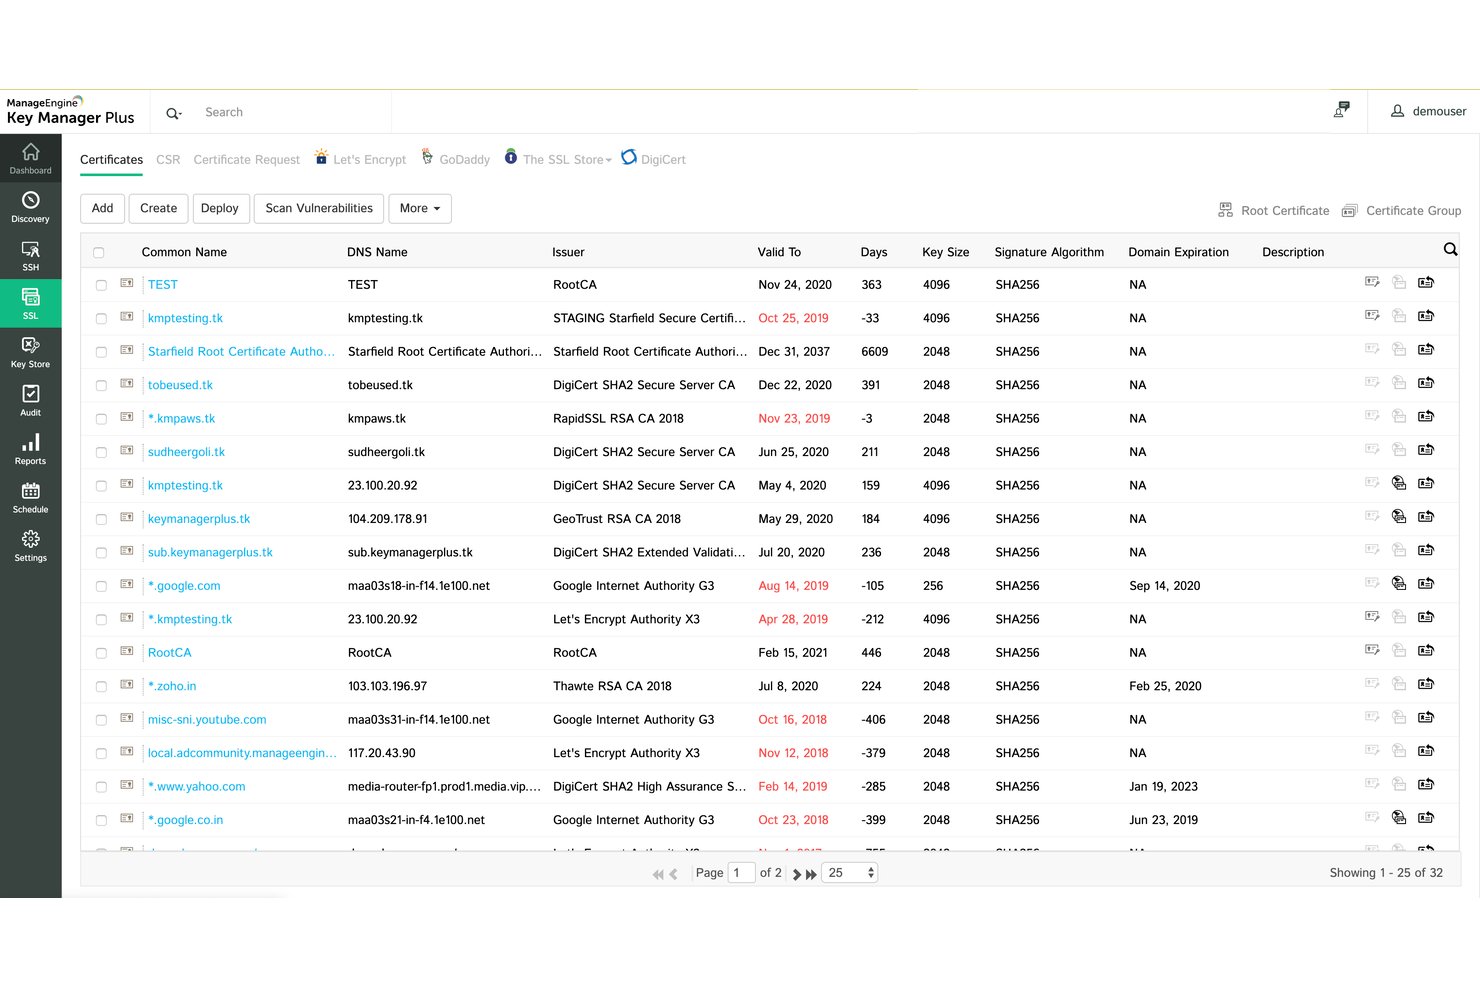
ManageEngine Key Manager Plus handles SSL/TLS certificates, SSH keys, and PGP keys from a single console, with multi-CA support, ACME-based automation, and built-in compliance reporting.
Who Is ManageEngine Key Manager Plus Best For?
ManageEngine Key Manager Plus is a strong fit for IT security and infrastructure teams managing mixed environments under a single compliance umbrella.
Why I Picked ManageEngine Key Manager Plus
ManageEngine Key Manager Plus earns its spot on my shortlist because it's one of the few CLM tools that consolidates SSL/TLS certificates, SSH keys, and PGP keys under a single management console without requiring separate products. I particularly like its ACME-based automation, which handles full certificate lifecycle cycles, including issuance, renewal, and redeployment, after a one-time configuration. The built-in compliance reporting against NIST, PCI-DSS, HIPAA, and SOX also means my team isn't assembling audit evidence from multiple sources.
ManageEngine Key Manager Plus Key Features
- Multi-CA certificate ordering: Request and issue certificates from 11+ public CAs, Microsoft AD CS, or any ACME-compliant CA directly from a single console.
- SSH key lifecycle management: Create, deploy, rotate, and recycle keys with real-time user-key mapping and full session audit logs.
- ITSM ticket creation on expiry events: Automatically generate tickets in ServiceDesk Plus or ServiceNow when certificates approach expiration or trigger vulnerability alerts.
- Kubernetes TLS secret rotation: Manage and rotate TLS secrets within Kubernetes clusters from the platform without manual intervention.
ManageEngine Key Manager Plus Integrations
Native integrations include Azure, Azure Key Vault, ServiceNow, Kubernetes, Jenkins, and ManageEngine ServiceDesk Plus. It also offers REST APIs to support custom connections.
Pros and Cons
Pros:
- Provides compliance reports and audit trails
- Supports broad multi-CA certificate coverage
- Unifies SSL, SSH, and PGP management
Cons:
- Lacks certificate dependency mapping
- Consumes substantial resources at scale
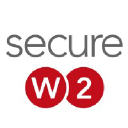
SecureW2 is a cloud-native PKI platform that handles certificate issuance, zero-touch enrollment, automated renewal, revocation, and post-issuance anomaly detection across managed devices, users, and machine identities.
Who Is SecureW2 Best For?
SecureW2 is a strong fit for security-focused IT teams managing large fleets of managed devices who need zero-touch certificate provisioning and post-quantum readiness built into their PKI.
Why I Picked SecureW2
SecureW2 earns its spot on my shortlist because its zero-touch PKI and post-quantum crypto-agility are genuinely production-ready. I picked it for its Dynamic SCEP and ACME-DA enrollment, which validate device posture and identity signals from your IdP or MDM before a certificate is ever issued. Layer in live support for ML-KEM and ML-DSA algorithms, and your PKI can issue quantum-resistant certificates today alongside classical ones without rebuilding your infrastructure.
SecureW2 Key Features
- CertIQ ML anomaly detection: Monitors post-issuance certificate activity and flags suspicious behavior like certificate duplication, spoofing, and lateral movement attempts.
- Adaptive Defense policy engine: Applies identity- and posture-aware policies that trigger real-time certificate suspension, reactivation, or revocation based on live signals from your IdP, MDM, or EDR.
- SPIRE/SPIFFE machine identity issuance: Issues short-lived SVIDs to AI agents, containers, and ephemeral workloads for mTLS authentication without API keys.
- FIPS 140-2/3 Level 3 HSM-backed CA keys: Stores CA private keys in hardware security modules with dual control and split knowledge for cryptographic key protection.
SecureW2 Integrations
SecureW2 integrates with Microsoft Intune, Jamf, Okta, Microsoft Entra ID, CrowdStrike, Cisco, Palo Alto Networks, and Fortinet. It also supports ACME, Dynamic SCEP, and REST APIs.
Pros and Cons
Pros:
- PQC crypto-agility supports ML-KEM and ML-DSA
- Identity-aware issuance validates device posture
- Zero-touch certificate lifecycle automation
Cons:
- Reporting metrics can be difficult to find
- Third-party certificate discovery remains limited
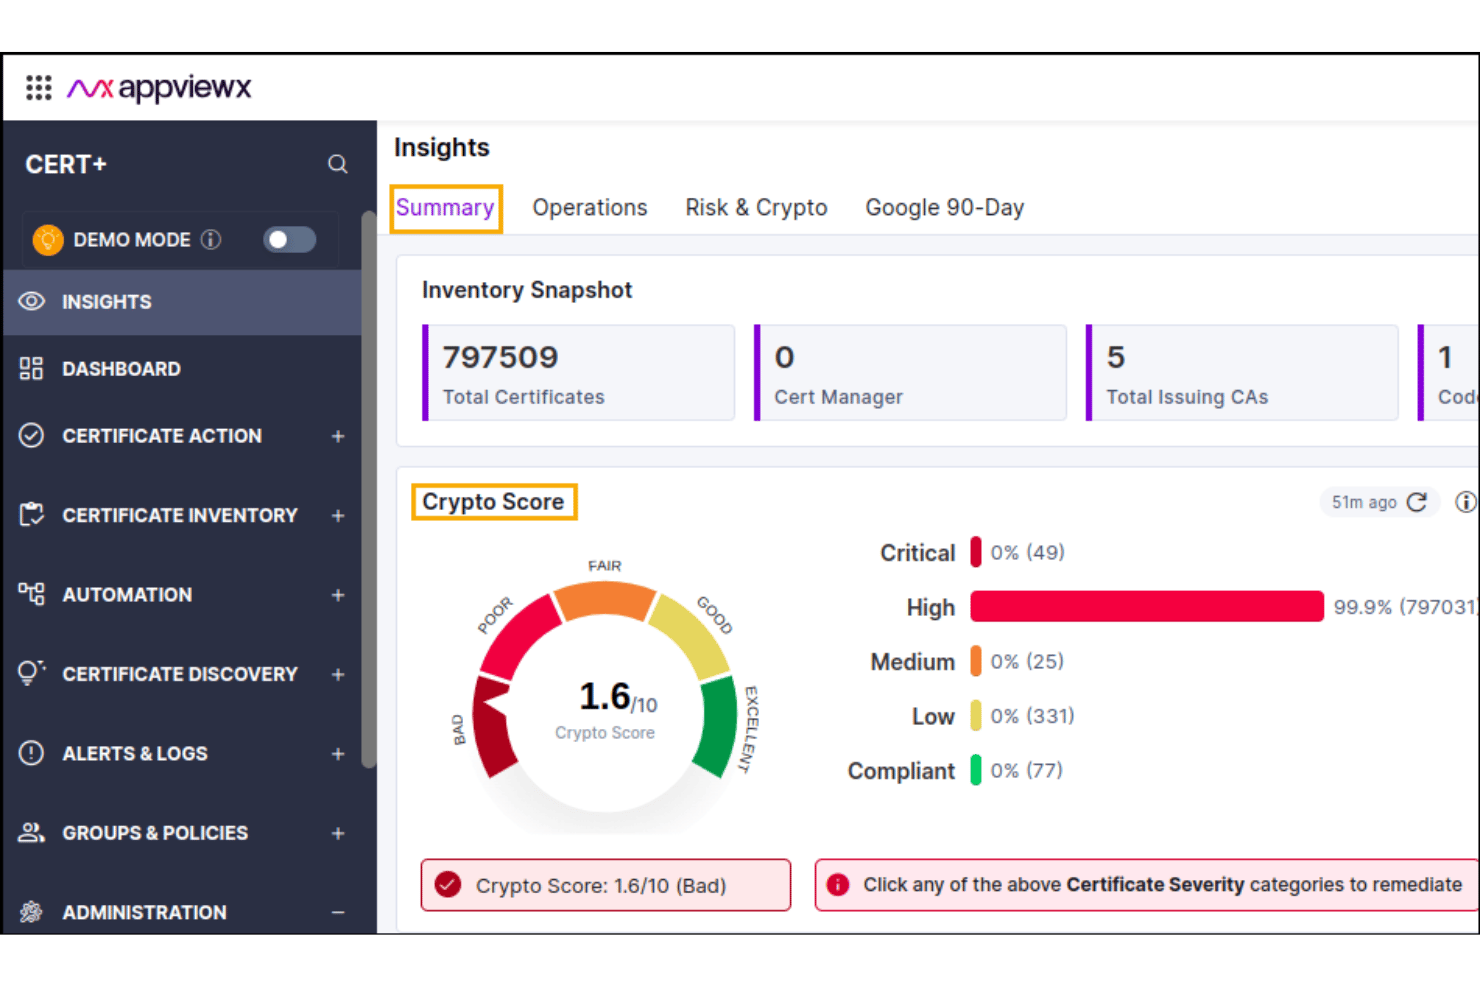
AppViewX is a certificate lifecycle management platform with Smart Discovery, closed-loop lifecycle automation, multi-CA orchestration, SSH key management, code signing, and post-quantum readiness tools across SaaS, hybrid, and on-premises deployments.
Who Is AppViewX Best For?
AppViewX is a strong fit for enterprise PKI and security teams in regulated industries that need post-quantum readiness.
Why I Picked AppViewX
AppViewX earns its spot on my shortlist because of how seriously it treats post-quantum readiness as a practical, operational concern rather than a future talking point. I love that it generates a Cryptographic Bill of Materials (CBOM), identifies every algorithm running across your environment, and maps a migration path aligned with NIST PQC guidance—all from a single platform. Its "Smart Discovery" also finds certificates across clouds, containers, Kubernetes clusters, and network devices, then ranks them by cryptographic risk so you know exactly where weak algorithms are hiding.
AppViewX Key Features
- Multi-CA orchestration: Connect to any public or private CA without being locked into a single provider.
- Closed-loop lifecycle automation: Automate certificate enrollment, renewal, deployment, key rotation, and revocation end-to-end, with policy-driven workflows and RBAC controls.
- InfinityAI anomaly detection: Monitors certificate health, flags anomalies, and surfaces recommended fixes across your environment.
- HSM-backed code signing: Store code signing keys in FIPS-certified HSMs from vendors including Thales, Entrust nShield, Utimaco, Fortanix, and Futurex.
AppViewX Integrations
AppViewX integrates with, including, AWS, F5 BIG-IP, CyberArk, Fortanix, Ansible, Terraform, Jenkins, and GitLab. It also offers an API to support custom automation.
Pros and Cons
Pros:
- Closed-loop automation covers certificate renewals
- Smart Discovery ranks cryptographic risks
- CBOM supports post-quantum migration planning
Cons:
- Compliance report templates remain unconfirmed
- Workflow setup can feel complex

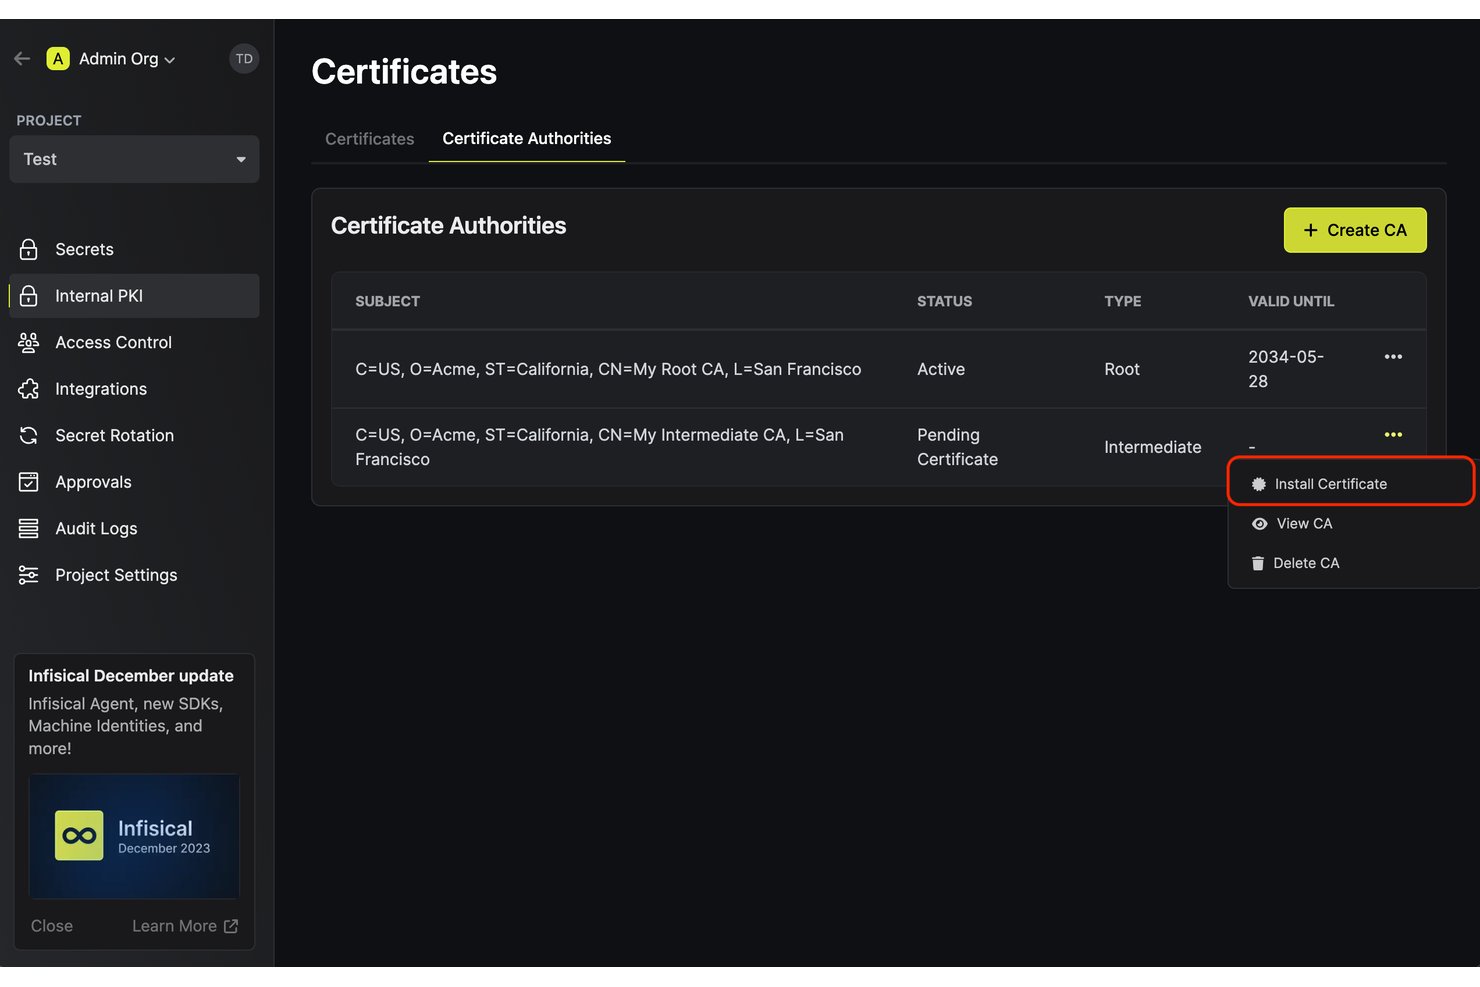
Infisical is a certificate lifecycle management platform that combines private CA hierarchy management, multi-CA integration, automated certificate issuance and renewal, and DevOps-native tooling including a native cert-manager issuer, Terraform provider, and ACME, EST, and SCEP protocol support.
Who Is Infisical Best For?
Infisical is a strong fit for DevOps and platform engineering teams that manage certificates across Kubernetes environments and multi-CA infrastructures.
Why I Picked Infisical
I picked Infisical as one of the best because it unifies private CA hierarchy management with external CA integrations (DigiCert, AWS Private CA, Microsoft AD CS, Venafi) under a single console. I love that the native cert-manager issuer handles Kubernetes certificate issuance with machine identity authentication and auto-renewal, no ACME domain-ownership challenges required. Certificate Profiles let security teams lock down algorithms, SANs, and validity periods while app teams self-serve through ACME or the API.
Infisical Key Features
- Server-driven renewal: Holds and rotates certificate keys, pushing renewed certificates automatically to connected sync destinations.
- Expiration status dashboard: Offers a centralized PKI view that surfaces certificates by status with configurable alert thresholds.
- SCEP enrollment: Supports SCEP-based certificate enrollment for network devices and MDM-managed endpoints including Jamf and Intune.
- Audit log retention: Records every certificate request, issuance, approval, and revocation event, with configurable retention periods up to custom durations.
Infisical Integrations
Infisical offers 90+ integrations, including 1Password, Ansible, AWS Amplify, Azure DevOps, Microsoft AD CS, Venafi, AWS Certificate Manager, Azure Key Vault, Cloudflare, and Windows Certificate Store. It also provides a Terraform provider and REST API for custom workflows.
Pros and Cons
Pros:
- Approval workflows support controlled self-service issuance
- Policy profiles enforce certificate request guardrails
- DevOps-native certificate issuance and renewal
Cons:
- Post-quantum support remains nascent
- Certificate discovery covers network endpoints only

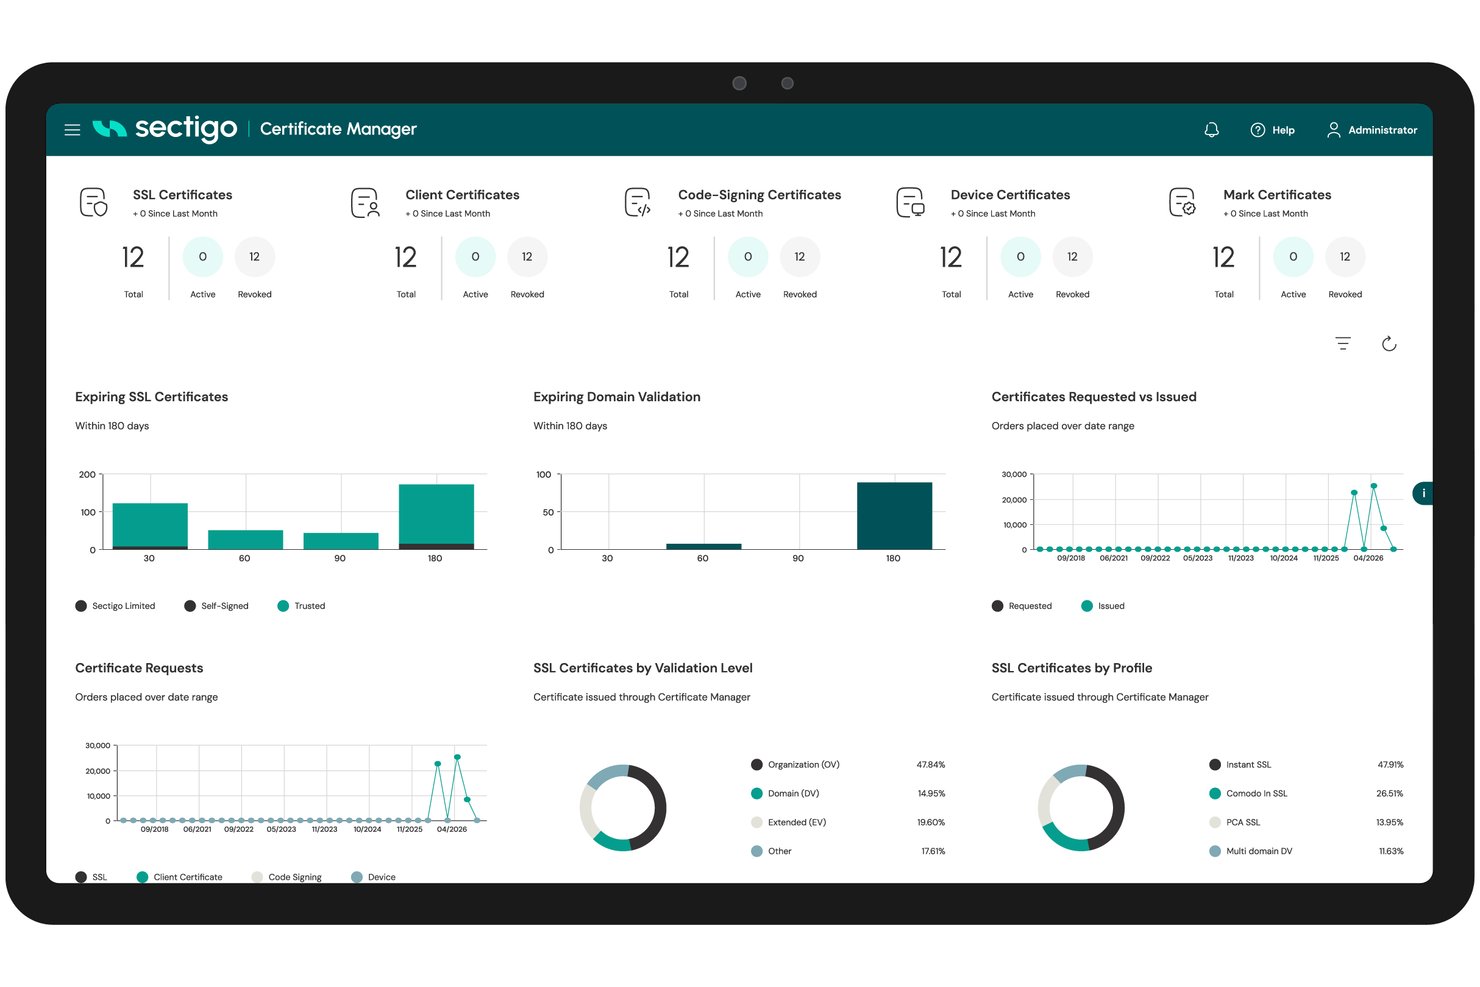
Sectigo Certificate Manager is a CA-agnostic CLM platform that handles certificate discovery, automated issuance, renewal, deployment, and revocation across public and private certificates, with built-in post-quantum cryptography testing tools.
Who Is Sectigo Best For?
Sectigo Certificate Manager is a strong fit for PKI administrators and infrastructure teams managing large, mixed-CA environments who need to start testing post-quantum certificate workflows now.
Why I Picked Sectigo
I picked Sectigo Certificate Manager as one of the best because it's the only CLM platform I've seen with a built-in post-quantum testing environment that works inside your actual certificate workflows. PQC Labs gives you a no-setup sandbox to test quantum-resistant certificates, and Private PQC in SCM lets you issue real ML-DSA certificates through Sectigo's private CA so you can validate your migration path before standards finalize. I also like that the Q.U.A.N.T. framework maps existing cryptographic dependencies and flags certs vulnerable to "harvest now, decrypt later" attacks.
Sectigo Key Features
- CA-agnostic multi-CA management: SCM consolidates public and private certificates from multiple CAs—including Microsoft AD CS, AWS, and Google Cloud—into a single dashboard.
- Automated certificate renewal and deployment: SCM handles end-to-end issuance, deployment, and renewal across load balancers, web servers, and firewalls without manual intervention.
- ITSM and SIEM integrations: SCM connects to ServiceNow, Jira, Splunk, and Microsoft Sentinel for certificate provisioning, monitoring, and expiry alerting within existing workflows.
- MCP server for AI-driven certificate management: An MCP server lets AI agents issue and manage certificates through natural-language commands.
Sectigo Integrations
Sectigo Certificate Manager offers 50+ integrations, including Microsoft CA (ADCS), AWS, Google Cloud, Kubernetes, Terraform, Jenkins, ServiceNow, Jira, Splunk, and Microsoft Sentinel. It also supports ACME, SCEP, EST, and REST API connectivity for certificate workflows and custom integrations.
Pros and Cons
Pros:
- Centralizes public and private certificate management
- Automates renewal and compromised-certificate replacement
- Built-in post-quantum certificate testing
Cons:
- Support responses can be slow
- Some screens feel dated to reviewers

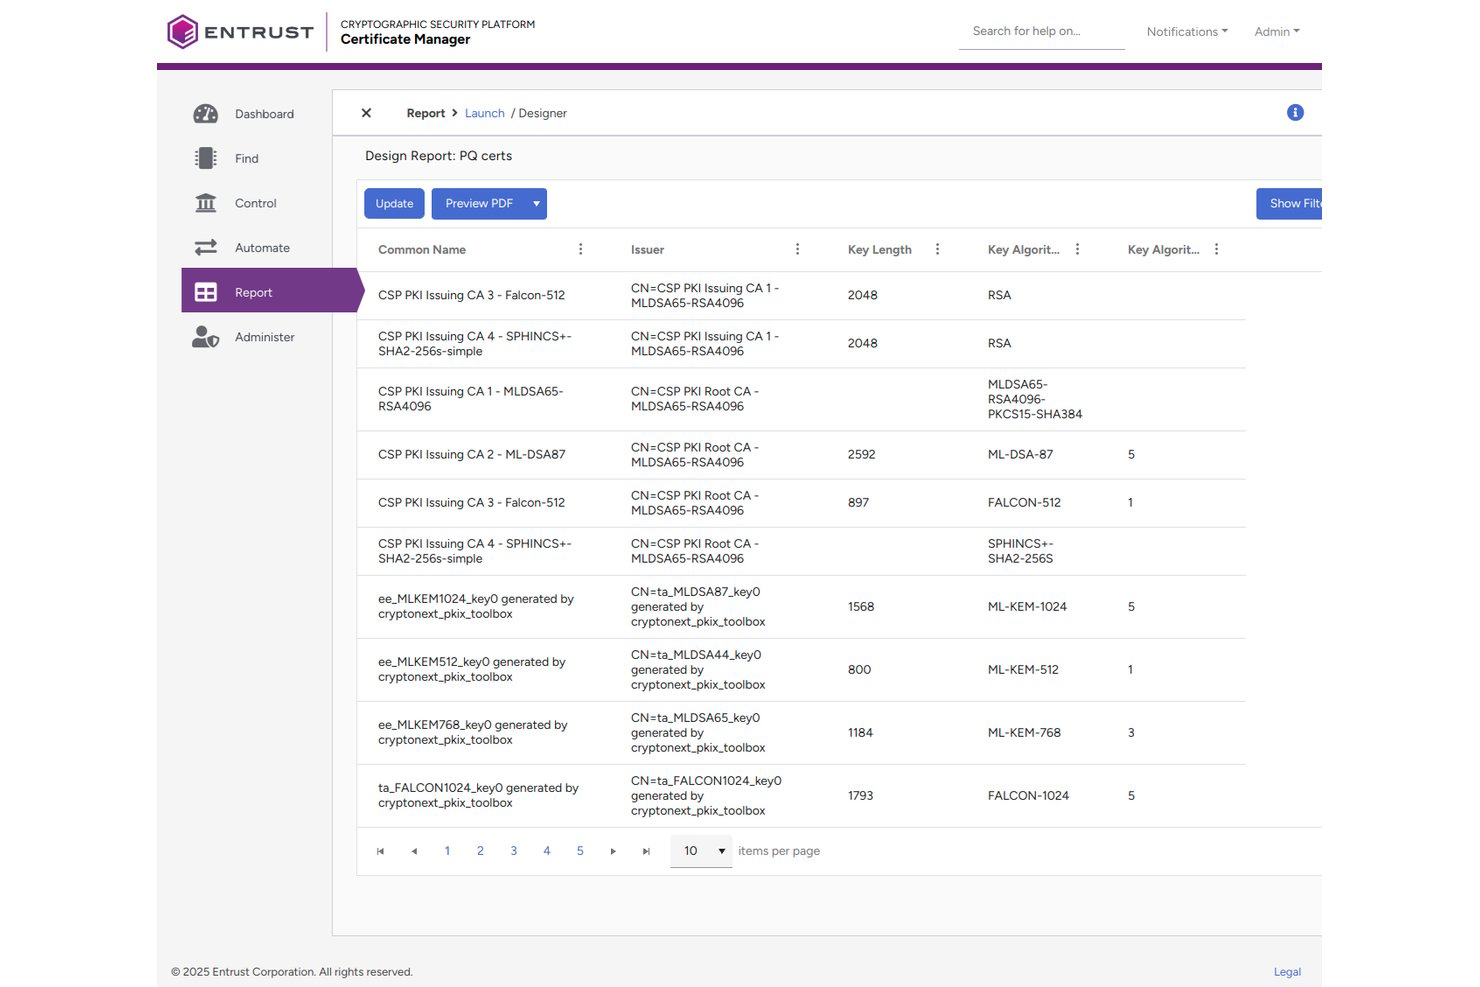
Entrust Certificate Manager is a PKI-based certificate lifecycle management platform that handles certificate discovery, automated enrollment and renewal, policy enforcement, and multi-CA orchestration across on-premises, cloud, hybrid, and IoT/OT environments.
Who Is Entrust Best For?
Entrust Certificate Manager is a strong fit for enterprise security and PKI teams in regulated industries that need private CA management backed by hardware-level key protection.
Why I Picked Entrust
Entrust earns its spot on my shortlist because it owns both ends of the key protection chain: the nShield HSM hardware and the PKI platform running on top of it. That native HSM integration means your private CA keys aren't just stored in a third-party appliance you've bolted on. I also like that the Certificate Manager handles automated enrollment via ACME and SCEP, which is essential now that 47-day TLS validity is the reality teams are managing against.
Entrust Key Features
- Post-quantum certificate inventory: Scans your environment to identify quantum-vulnerable certificates and supports composite and hybrid certificate issuance for PQC migration planning.
- Embedded OCSP service: Provides real-time monitoring and validation of certificate status within the platform, without relying on an external responder.
- CP/CPS authoring and key ceremony support: Includes built-in governance tooling for certificate policy documentation and formal key ceremony procedures, with immutable audit logs.
- Lightweight IoT endpoint agent: A small-footprint agent (~400–500 KB RAM) supports certificate discovery and enrollment on constrained OT and IoT devices, including ARM Cortex and TPM 2.0 environments.
Entrust Integrations
Entrust supports integrations with nShield HSM, Microsoft Intune, HashiCorp Vault, Ansible, Azure, and Nginx. A REST API for custom integrations is also available.
Pros and Cons
Pros:
- Lightweight IoT certificate management
- Post-quantum migration support
- Native HSM key control
Cons:
- Kubernetes-native depth remains limited
- Public TLS issuance ended
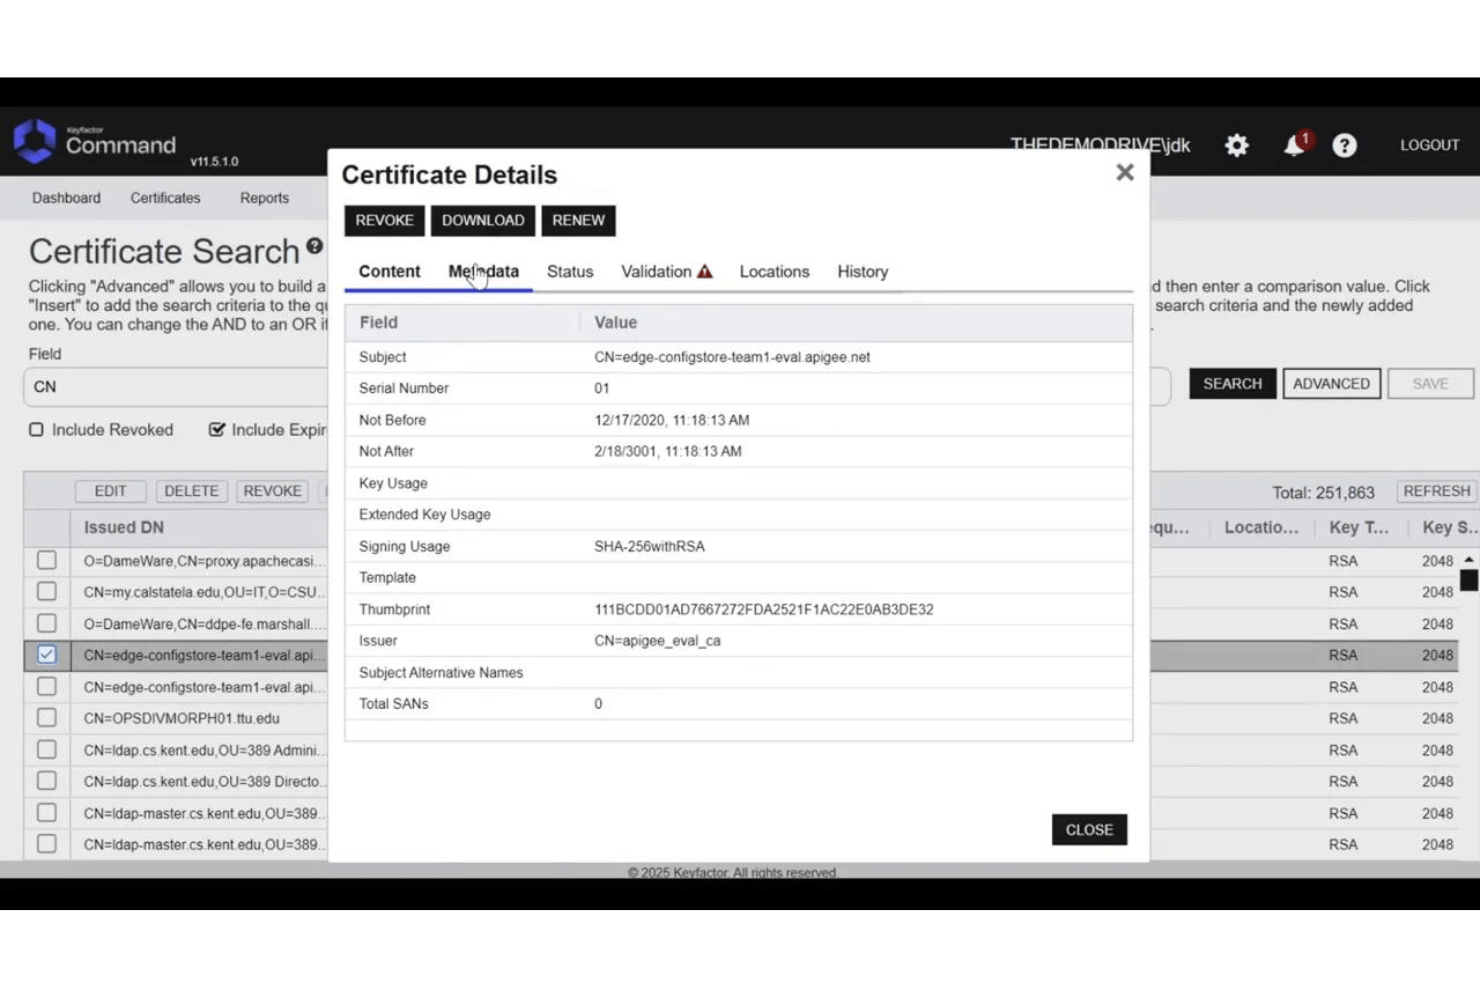
Keyfactor Command is an enterprise certificate lifecycle management platform covering automated discovery, multi-CA orchestration, zero-touch renewal, and post-quantum certificate support across on-premises, cloud, and hybrid environments.
Who Is Keyfactor Command Best For?
Keyfactor Command is well suited to regulated industries like finance, healthcare, and defense, where cryptographic compliance, audit trails, and quantum migration planning are non-negotiable.
Why I Picked Keyfactor Command
Keyfactor Command earns its spot on my shortlist because it's the only CLM platform I've seen that assigns a dynamic risk score to every certificate in your inventory. Command Risk Intelligence taps the world's largest Internet certificate database to surface certificates carrying real exposure, like long-lived certs or unsanctioned domain usage, and flags which ones are quantum-vulnerable ahead of NIST's 2030 algorithm deprecation deadline. ML-DSA and hybrid certificate support shipped in Command 25.2 make PQC readiness an active capability, not just a roadmap promise.
Keyfactor Command Key Features
- AnyCA Gateway: Manage certificate issuance across multiple public, private, and cloud CAs through a single control plane.
- Universal Orchestrator: Automatically deploy certificates across on-premises environments, cloud platforms, Kubernetes clusters, or integrated with a fully managed PKI framework.
- Enrollment Patterns: Define templates that enforce key size, algorithm, validity period, and wildcard restrictions across certificate requests without creating CA template sprawl.
- ACME protocol support: Issue and renew certificates automatically in Kubernetes environments via a native Helm chart deployment for ACME clients.
Keyfactor Command Integrations
Keyfactor Command integrates with Bosh, Cisco, AWS, Docker Enterprise, Fortinet, Okta, GoDaddy, HashiCorp, and Radware. Its REST API and OpenAPI documentation support custom integrations.
Pros and Cons
Pros:
- Handles massive certificate estates
- Native post-quantum readiness capabilities
- Dynamic certificate risk scoring
Cons:
- Older interface complicates endpoint management
- Implementation can take six months
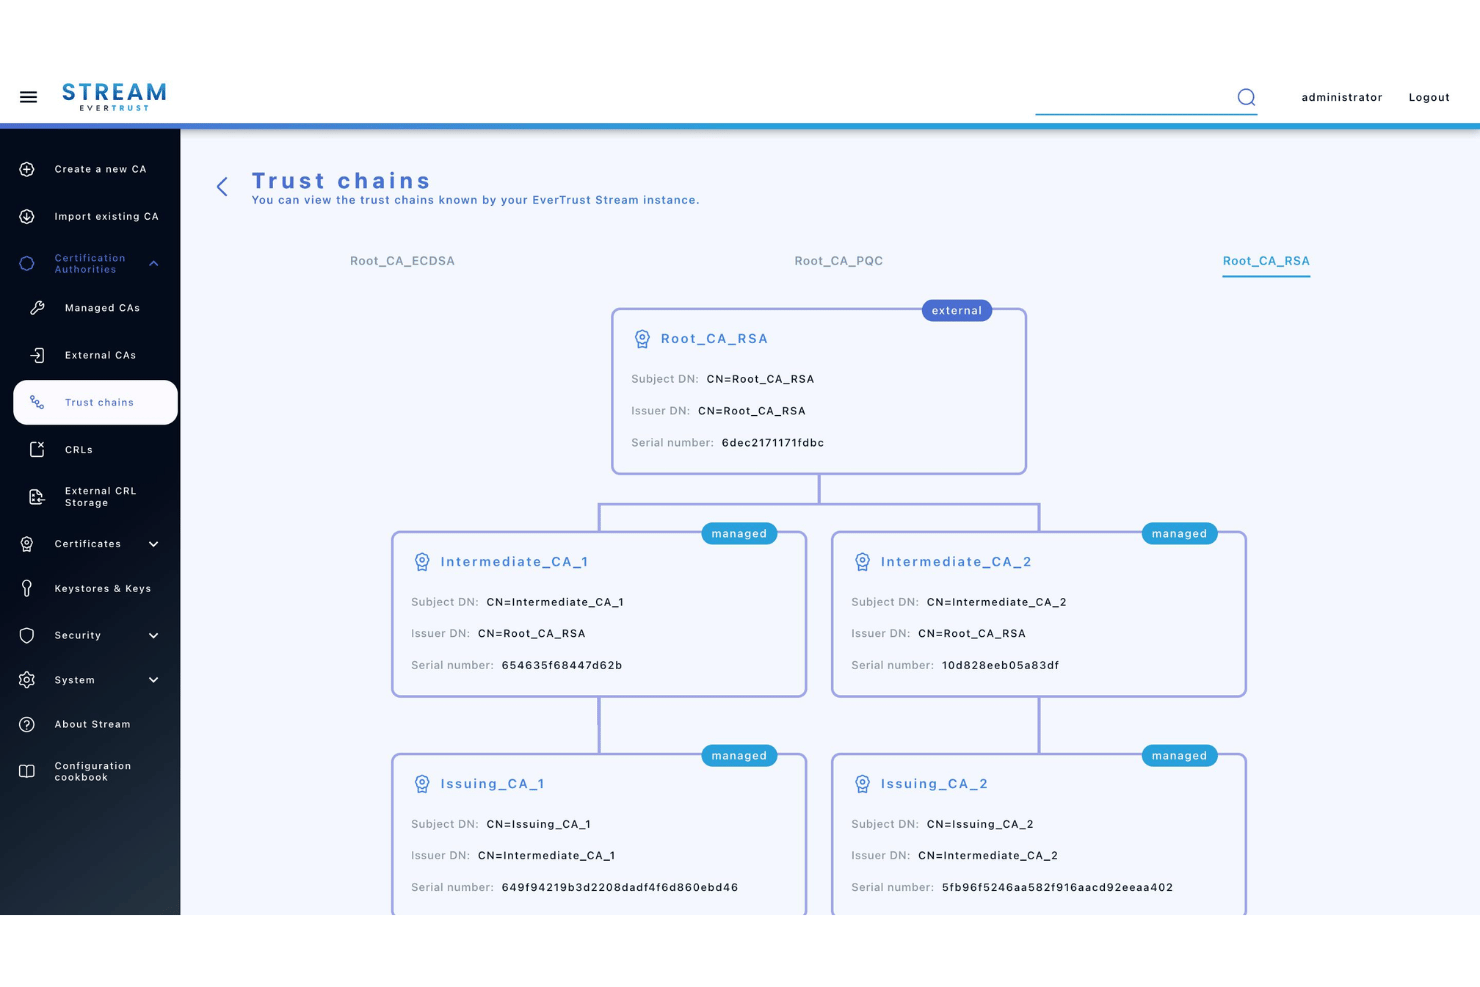
Evertrust CLM is a certificate lifecycle management software with built-in multi-CA orchestration, post-quantum certificate issuance, and HSM-backed key storage across SaaS, on-premises, and air-gapped deployments.
Who Is Evertrust CLM Best For?
Evertrust CLM is ideal for European enterprises, financial institutions, and public sector organizations that need to strictly comply with European Union digital resilience mandates like NIS2, DORA, and eIDAS 2.0.
Why I Picked Evertrust CLM
I chose Evertrust CLM because it delivers a level of native compliance enforcement rarely seen in non-EU platforms. Out of the box, it combines ANSSI CSPN certification with immutable audit logging and granular, CSR-level policy controls that map directly to strict European regulatory frameworks. Additionally, its deployment architecture allows organizations to keep keys, certificate data, and management pipelines entirely within localized, sovereign infrastructure.
Evertrust CLM Key Features
- Multi-CA orchestration: Centralize and manage certificate lifecycles across 20+ public and private Certificate Authorities from a single control plane.
- Crypto agility & post-quantum readiness: Audit your entire cryptographic standard for legacy algorithm vulnerabilities while automating migration.
- DevSecOps & native protocol automation: Provision and rotate certificates across containerized, cloud, and IaC pipelines using native protocols.
- Automated DCV & zero-touch renewals: Support short-lived TLS certificates with DNS-agnostic, automated Domain Control Validation and ITSM ticket routing via ServiceNow.
Evertrust CLM Integrations
Evertrust CLM supports 40+ connectors, including Let's Encrypt, AWS ACM PCA, AWS, Okta, Linux, EJBCA, Kubernetes, Terraform, Ansible, and Microsoft Intune. It also provides REST APIs for custom integrations.
Pros and Cons
Pros:
- Post-quantum certificate lifecycle support
- CSR-level cryptographic policy enforcement
- EU regulatory mapping and sovereignty
Cons:
- External agent needed for discovery
- Limited UI customization for environment segregation

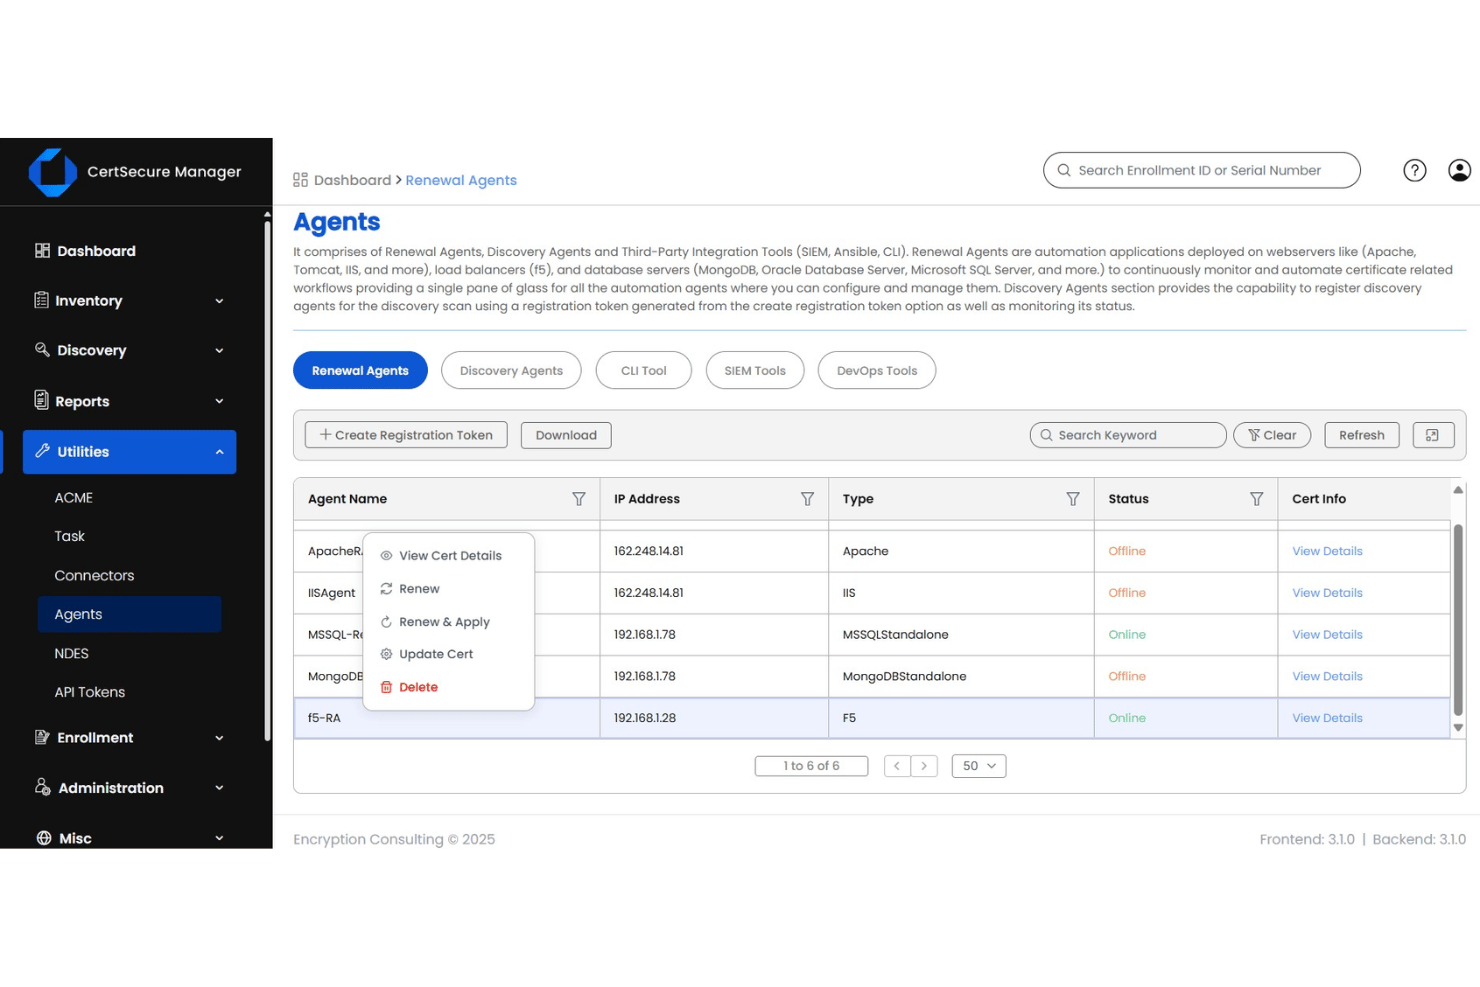
CertSecure Manager is a certificate lifecycle management platform that handles discovery, issuance, renewal, revocation, and policy enforcement across hybrid environments, multiple CAs, and enterprise infrastructure like load balancers, web servers, and databases.
Who Is CertSecure Manager Best For?
CertSecure Manager is a strong fit for enterprise PKI administrators and IT security managers who need multi-CA governance, cryptographic policy enforcement, and compliance reporting across regulated industries.
Why I Picked CertSecure Manager
I've included CertSecure Manager in my top picks because its formal F5 BIG-IP partnership delivers something I haven't seen done this cleanly elsewhere: zero-touch certificate renewal that handles enrollment, deployment, and binding on F5 infrastructure without manual steps. When you're staring down the CA/Browser Forum's 47-day validity mandate, that level of automation on load balancers is exactly what prevents 2 a.m. outage calls. I also like that it's purpose-built for unlimited-volume DevOps pipelines, so high-frequency rotation doesn't become a throughput bottleneck.
CertSecure Manager Key Features
- Certificate risk profile engine: Automatically classifies certificates by risk level based on key strength, algorithm type, and validity period, giving you a prioritized exposure view.
- M of N approval workflows: Enforces multi-party authorization policies for certificate issuance and renewal requests, adding a governance layer for high-sensitivity environments.
- Compliance reporting: Generates scheduled compliance reports for GDPR, HIPAA, PCI DSS, FIPS, and NIST automatically, delivered via email on a weekly or monthly basis.
- Multi-CA support with one-click switching: Manage certificates across 11 CAs, from a single console, with one-click migration between CAs.
CertSecure Manager Integrations
CertSecure Manager integrates with Ansible, Splunk, Apache, Microsoft AD CS, Nginx, IIS, Azure, and Java KeyStore. An API for custom integrations is also available.
Pros and Cons
Pros:
- Risk profiles prioritize weak cryptography
- One-click CA switching reduces vendor lock-in
- Zero-touch renewal
Cons:
- Kubernetes service mesh support is underdocumented
- Higher implementation effort for hybrid setups
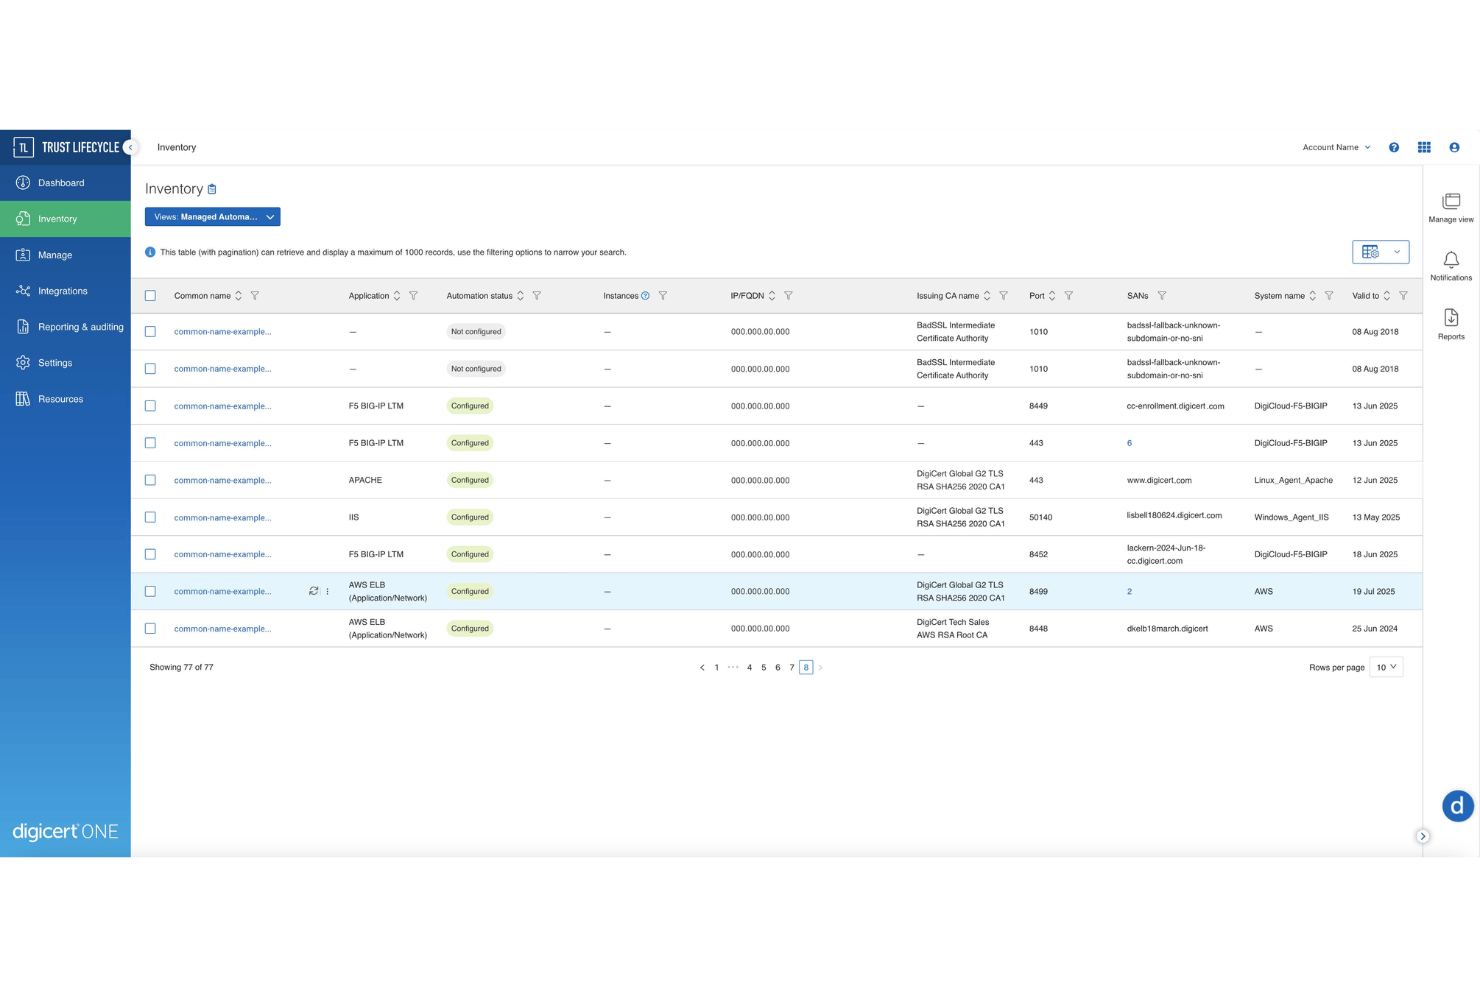
DigiCert Trust Lifecycle Manager is a certificate lifecycle management platform built on the DigiCert ONE architecture that handles certificate discovery, multi-CA issuance, lifecycle automation, policy enforcement, and post-quantum cryptography migration across cloud, on-premises, and air-gapped environments.
Who Is DigiCert Trust Lifecycle Manager Best For?
DigiCert Trust Lifecycle Manager is a strong fit for enterprise security and PKI teams managing large certificate volumes across hybrid, regulated, or air-gapped environments.
Why I Picked DigiCert Trust Lifecycle Manager
DigiCert Trust Lifecycle Manager earns its spot on my shortlist because it's the only CLM platform I've seen that combines native PQC certificate issuance with production-ready bulk replacement automation. I particularly like that it already issues ML-DSA and SLH-DSA certificates and can scan your network to find quantum-vulnerable certs, then replace them at scale without manual intervention. The built-in DigiCert Private CA with dedicated hierarchy options also means you're not stitching together a separate PKI infrastructure alongside your CLM.
DigiCert Trust Lifecycle Manager Key Features
- Multi-CA connector support: Connect to 10+ external certificate authorities—including AWS Private CA, Microsoft AD CS, Let's Encrypt, Sectigo, and Entrust—alongside the built-in DigiCert Private CA, all managed from a single console.
- Layered certificate discovery: Run CT log monitoring, cloud scans, network sensor scans, and agent-based system scans simultaneously to surface certificates across on-premises, cloud, and air-gapped environments.
- Policy-based compliance enforcement: Define certificate profiles that enforce key size, algorithm, validity period, and CA allowlists, with automated flagging and remediation of non-compliant certificates.
- Self-service enrollment portal: Give certificate requesters a role-scoped portal with SAML/OIDC SSO to enroll, request, and pick up certificates without involving PKI admins for every transaction.
DigiCert Trust Lifecycle Manager Integrations
DigiCert Trust Lifecycle Manager offers documented integrations with AWS Private CA, Microsoft AD CS, Sectigo, Entrust, ServiceNow, Jira, Kubernetes via cert-manager, Terraform, F5 BIG-IP, and SafeNet HSMs. It supports 150+ DNS providers plus REST API, ACME v2, SCEP, and EST.
Pros and Cons
Pros:
- Built-in Private CA supports dedicated hierarchies
- Eliminates certificate blind spots across cloud, network, and system
- Future-proofs PKI against quantum threats
Cons:
- Full discovery adds deployment friction
- Admin portal UI and navigation feel unintuitive
Other Certificate Lifecycle Management Software
Here are some additional tools that didn’t make it onto my shortlist, but might be a good fit for your needs:
- ServiceNow Certificate Management
For ServiceNow-native cert governance
- HID ACM
For managed PKI with retained HSM root key control
- CertKit
For appliance and server cert deployment
- Akeyless
For unified secrets and cert automation
- Segura Certificate Manager
For PAM-integrated cert lifecycle management
- Qualys CertView
For Qualys-native PQC readiness
- cert-manager
For open-source K8s cert automation
- Cloudflare Advanced Certificate Manager
For edge TLS on Cloudflare-proxied traffic
- GlobalSign Atlas
For GlobalSign-native PKI auto-enrollment


How I Evaluate Certificate Lifecycle Management Software
I split my evaluation into baseline criteria every tool must meet—discovery, automation, multi-CA support—and differentiators like PQC readiness, HSM integration, and DevOps-native workflows that separate the best from the rest.
Core Functionality (Table Stakes for This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, and use that to help me assess its overall fit for the list.
- Certificate discovery and inventory: I look for continuous scanning across cloud, on-prem, and DevOps environments so nothing hides in a forgotten subnet or container cluster.
- Lifecycle automation: I evaluate how much of enrollment, renewal, rotation, and revocation runs without manual steps—especially zero-touch renewal before expiration.
- Multi-CA support: I check whether a platform manages certificates from public CAs like DigiCert and Sectigo alongside private CAs like Microsoft AD CS from one console.
- Expiration monitoring and alerting: Configurable alert thresholds, escalation paths, and ITSM integration matter more to me than a simple expiration list view.
- Policy enforcement and compliance: I look for enforceable rules on key sizes, algorithms, and validity periods, plus audit-ready reports mapped to frameworks like PCI-DSS or NIST.
- Protocol and ecosystem integrations: Support for ACME, SCEP, EST, and REST APIs is the baseline; I also evaluate native ties to load balancers, Kubernetes, and HSMs.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
I evaluate post-quantum crypto-agility first—specifically whether a platform can inventory quantum-vulnerable certificates and orchestrate migration to PQC-ready algorithms like ML-KEM and ML-DSA. Certificate dependency mapping is equally important: I check whether the tool visualizes which services, load balancers, and endpoints rely on each certificate so you can gauge blast radius before a renewal or revocation. For teams running Kubernetes, I look at how deeply a vendor integrates with cert-manager and service meshes like Istio to rotate short-lived workload identities without developer friction.
Beyond Features
I evaluate deployment model first because it shapes everything from compliance to operational overhead. A platform offering air-gapped or on-prem options matters when you're managing PKI in regulated or sovereign environments where SaaS isn't viable. Scalability is equally important—I check whether a tool handles millions of certificates without performance drops, especially for IoT or short-lived workload scenarios where issuance rates spike. I also look at total cost of ownership, including hidden fees for CA connectors or onboarding services that inflate what looked like competitive pricing.
How to Choose the Right Certificate Lifecycle Management Software
Select the right platform based on the features that matter most to your team. Use the table below to match your priorities with the capabilities to look for.
| If your priority is | Look for |
|---|---|
| Finding unmanaged certificates | A discovery report covering cloud, on-premises, and container environments |
| Preventing expiration outages | A renewal workflow with documented ownership, escalation timing, and deployment records |
| Managing multiple certificate authorities | A written support matrix covering public CAs, Microsoft AD CS, and private PKI |
| Meeting audit requirements | Sample audit reports showing certificate history, policy changes, and administrator actions |
| Controlling regulated key material | Deployment documentation for on-premises, air-gapped, or HSM-connected environments |
How to Vet Your Shortlist
- Run a discovery trial: Ask the vendor to inventory a defined subnet, cloud account, and Kubernetes cluster within 14 days, then compare results against your known certificate register.
- Test renewal handling: Create a trial certificate that expires within 30 days and verify the documented process for approval, renewal, deployment, rollback, and revocation.
- Request the support matrix: Obtain a current document listing supported CAs, protocols, load balancers, certificate formats, and HSMs, including version limitations.
- Get commitments in writing: Ask for a sample audit report and a contract clause defining data retention, administrator access logs, and assistance during certificate incidents.
- Choose the operating tradeoff: Decide whether you need vendor-managed PKI with less internal administration or direct control over infrastructure, keys, and policy execution.
What Is Certificate Lifecycle Management Software?
Certificate lifecycle management software discovers, monitors, issues, renews, deploys, and revokes digital certificates and encryption keys. It gives IT and security teams a central inventory of certificates across cloud, on-premises, and DevOps environments.
These tools can automate renewal workflows, track expiration dates, enforce certificate policies, connect with certificate authorities, and provide audit records for compliance and incident response.
Features of Certificate Lifecycle Management Software
When selecting a certificate lifecycle management platform, keep an eye out for the following key features:
- Certificate discovery: Scans networks, cloud accounts, servers, containers, and endpoints to find certificates across your environment. It records certificate details, locations, owners, and expiration dates in a central inventory.
- Expiration monitoring: Tracks certificate validity periods and sends alerts before certificates expire. Configurable thresholds and escalation rules help teams assign ownership and address renewals before service interruptions occur.
- Lifecycle automation: Automates certificate requests, approvals, renewals, deployment, rotation, and revocation. Workflows reduce manual steps and create repeatable processes for certificates across servers, applications, and devices.
- Multi-CA management: Connects public and private certificate authorities through one interface. Teams can manage certificates from providers such as DigiCert, Sectigo, and Microsoft AD CS without maintaining separate inventories.
- Policy enforcement: Applies rules for key sizes, signature algorithms, certificate validity periods, and approved issuers. The platform can flag or block certificates that violate organizational or regulatory requirements.
- Certificate deployment: Installs renewed certificates on supported servers, load balancers, applications, and network devices. Deployment records show where each certificate was installed and help teams verify successful rotation.
- Integration support: Connects with protocols and systems such as ACME, SCEP, EST, REST APIs, IT service management platforms, Kubernetes, and hardware security modules. These integrations fit certificate operations into existing infrastructure and workflows.
- Audit reporting: Records certificate changes, approvals, renewals, revocations, administrator actions, and policy decisions. Reports give security and compliance teams evidence for audits, investigations, and internal reviews.
Common Certificate Lifecycle Management Software AI Features
Beyond the standard features listed above, many of these software now offer built-in AI features such as:
- Anomaly detection: AI examines certificate activity, issuance patterns, and system behavior to identify unusual changes. It can flag unexpected certificate creation, abnormal renewal activity, or suspicious usage for review.
- Risk scoring: Automatically assigns risk scores based on certificate attributes, exposure, configuration, usage, and operational history. Security teams can use these scores to prioritize certificates that require investigation or replacement.
- Predictive outage analysis: AI analyzes certificate dependencies, renewal history, and service relationships to estimate where a certificate issue could disrupt applications. Teams can investigate likely failure points before an outage occurs.
- Natural-language queries: AI lets administrators ask questions about certificate inventories in plain language. For example, you can request certificates expiring soon, certificates using deprecated algorithms, or certificates associated with a specific service.
- Intelligent incident triage: Groups related certificate alerts, removes duplicate notifications, and ranks incidents by urgency. This gives administrators a clearer starting point when several certificate events occur together.
- Remediation recommendations: AI reviews certificate findings and suggests corrective actions based on configuration, usage, and organizational rules. Recommendations can include replacing an algorithm, changing a validity period, or investigating an unapproved issuer.
Benefits of Certificate Lifecycle Management Software
The right certificate lifecycle management tool can offer several benefits to your team and your business. Here are a few you can look forward to:
- Certificate visibility: Discovery scans across cloud, on-premises, network, and DevOps environments create a central inventory of certificates, locations, owners, and expiration dates.
- Fewer expiration outages: Automated monitoring, configurable alerts, ownership assignments, and renewal workflows help your team address certificates before they expire.
- Consistent lifecycle operations: Workflows for enrollment, approval, renewal, deployment, rotation, and revocation replace inconsistent manual certificate handling.
- Multi-CA administration: A single interface manages certificates from public and private authorities, including providers such as DigiCert, Sectigo, and Microsoft AD CS.
- Policy and compliance control: Rules for key sizes, algorithms, validity periods, and approved issuers support consistent configurations and audit-ready records.
- Safer certificate changes: Dependency mapping shows which services, endpoints, load balancers, and applications rely on each certificate before renewal or revocation.
- Better infrastructure integration: Support for ACME, SCEP, EST, REST APIs, Kubernetes, IT service management platforms, and HSMs connects certificate operations with existing systems.
Costs and Pricing of Certificate Lifecycle Management Software
Selecting the best software requires an understanding of the pricing models and plans available. Costs vary based on features, team size, integrations, deployment options, and support requirements. The table below summarizes common plans, average prices, and typical features included in certificate lifecycle management platforms.
Plan Comparison Table for Certificate Lifecycle Management Software
| Plan Type | Average Price | Common Features |
|---|---|---|
| Free Plan | $0 | Basic certificate inventory, limited expiration alerts, manual certificate tracking, and community support. |
| Personal Plan | $10-$30/user/month | Certificate discovery, expiration monitoring, basic renewal reminders, limited integrations, and email support. |
| Business Plan | $30-$100/user/month | Automated renewals, multi-CA management, policy enforcement, deployment workflows, audit reports, and IT service management integrations. |
| Enterprise Plan | $100-$300+/user/month | Advanced discovery, unlimited or high-volume certificate management, HSM and Kubernetes integrations, custom workflows, dedicated support, and custom compliance reporting. |
Certificate Lifecycle Management Software FAQs
Here are some answers to common questions about certificate lifecycle management tools:
Can certificate lifecycle management software manage certificates from different authorities?
Yes, many platforms manage certificates from multiple public and private authorities. Support varies by product, so check the vendor’s current support matrix. Confirm compatibility with providers such as DigiCert, Sectigo, and Microsoft AD CS. Also verify support for your certificate formats, enrollment protocols, and private PKI systems. Ask whether each connector supports discovery, renewal, deployment, and revocation.
Does certificate lifecycle management software replace a certificate authority?
No, a certificate management platform usually manages certificate operations rather than replacing your certificate authority. It can connect to public and private CAs and internal PKI systems. The platform may handle discovery, requests, approvals, renewals, deployment, and revocation. Your existing CA still issues certificates according to its policies.
How should I test certificate lifecycle management software before buying it?
Test the platform with certificates and systems that reflect your production environment. Start by scanning a defined subnet, cloud account, and Kubernetes cluster. Compare the results with your known certificate register. Then create a test certificate that expires within 30 days. Verify approval, renewal, deployment, rollback, and revocation steps. Test alert routing and administrator permissions as well. Request written confirmation for unsupported certificate formats, integrations, retention periods, and air-gapped deployment requirements.