

In today's fast-paced tech environment, managing user access and security can be overwhelming. You're likely juggling multiple platforms, each with its own login credentials, making it challenging to keep everything secure and efficient. Cloud directory services can help solve these issues by centralizing user management, enhancing security, and saving you time.
I've independently reviewed top cloud directory services, drawing on my experience in the SaaS development industry. My goal is to provide you with unbiased insights into the best options available.
In this article, you'll find detailed reviews and comparisons of the leading cloud directory services. I'll highlight their features, pros, and cons, helping you make an informed decision for your team.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Best Cloud Directory Services Comparison Table
This comparison table summarizes pricing details for my top cloud directory services selections.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for automated provisioning of user accounts | 14-day free trial | From $8/user/month | Website | |
| 2 | Best for centralized identity management | 14-day free trial | From $2/device/month | Website | |
| 3 | Best for enterprise-wide zero-knowledge biometrics | 30-day free trial | From $3/user/month (billed annually) | Website | |
| 4 | Best for modular IAM with HR-driven provisioning | 30-day free trial | From $1.40/user/month | Website | |
| 5 | Best for Google Cloud-native identity federation | 14-day free trial | From $7.00/user/month | Website | |
| 6 | Best directory-as-a-service functions | 30-day free trial | From $9/user/month (billed annually) | Website | |
| 7 | Best for hybrid Microsoft 365 identity workflows | 30-day free trial | From $7.00/user/month | Website | |
| 8 | Best for efficient employee lifecycle management | 30-day free trial | From $6/user/month (billed annually) | Website | |
| 9 | Best for integrating on-premise and cloud directories | 30-day free trial | From $3/user/month | Website | |
| 10 | Best for SSO and MFA across 15+ auth methods | 30-day free trial | From $3/user/month | Website |


Best Cloud Directory Service Reviews
Below are my detailed summaries of the best cloud directory services that made it onto my shortlist. My reviews offer a detailed look at the key features, pros & cons, integrations, and ideal use cases of each tool to help you find the best one for you.
 Best for automated provisioning of user accounts
- 14-day free trial
- From $8/user/month
Visit WebsiteCustomer Rating:4.8/5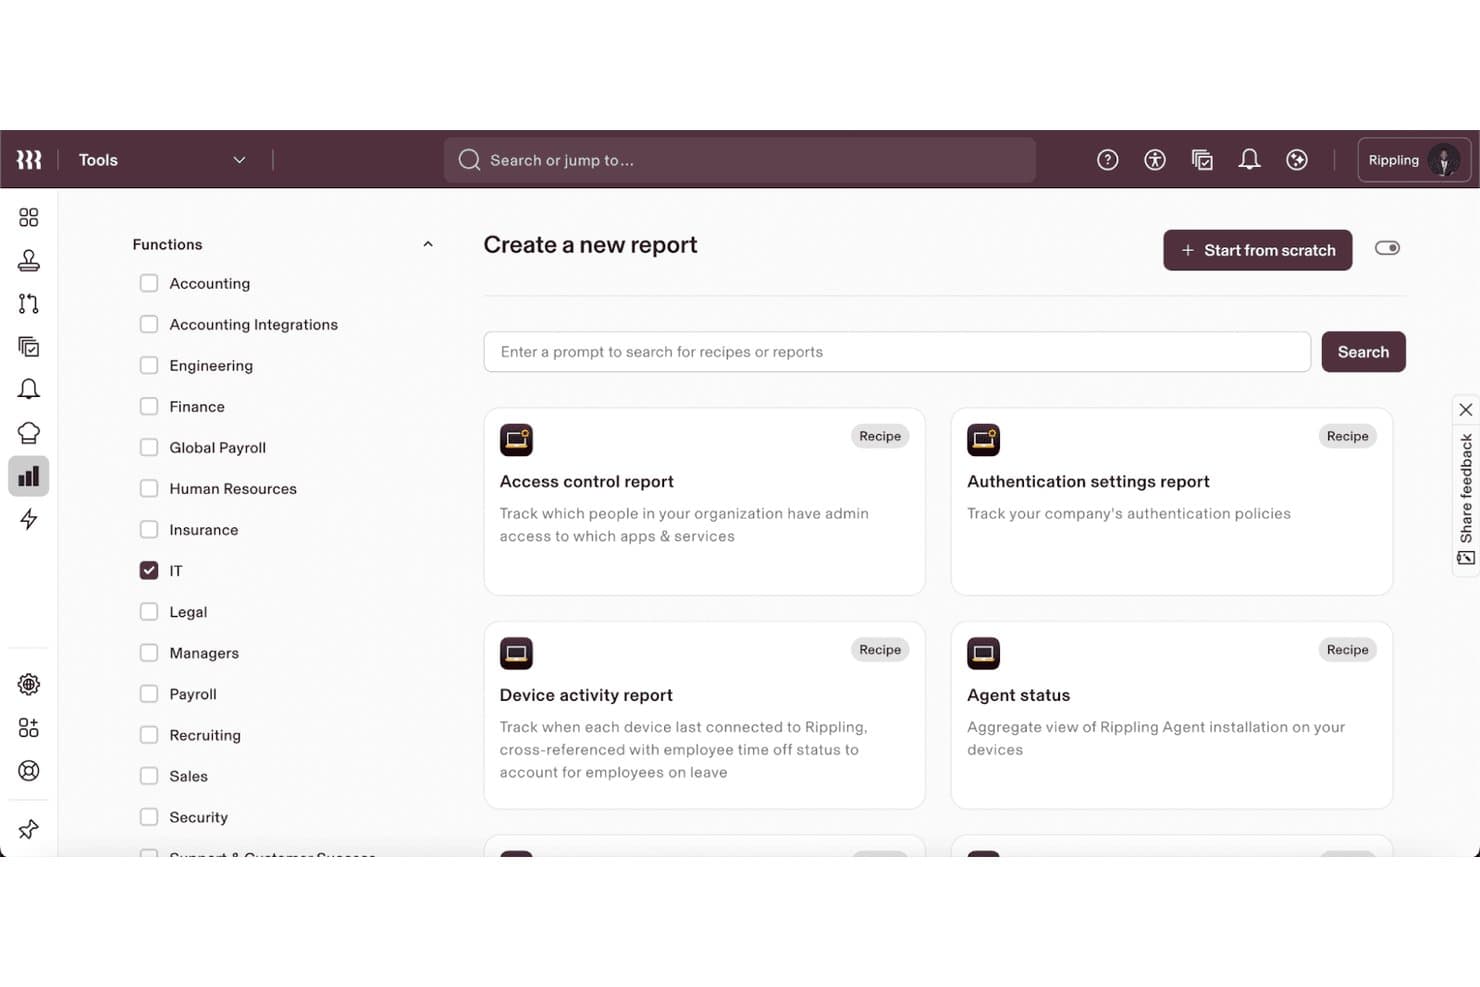
Rippling IT lets users build custom IT reports from prebuilt recipes. My Evaluation Score
- Device Management
- Adequate
- Directory Integration & Sync
- Minimal
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Strong
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Strong
Rippling IT is a cloud directory and IT management platform that combines identity and access management, SSO, automated user lifecycle management, MDM, and virtual LDAP and RADIUS directory services in a single system.
Who Is Rippling IT Best For?
Rippling IT is a strong fit for IT teams at growing companies that need access, devices, and app permissions to update automatically when employee roles change.
Why I Picked Rippling IT
I picked Rippling IT as one of the best because its provisioning is driven directly by employee records, not manual tickets. When someone's role changes in the HR system, their app accounts, group memberships, and device policies update automatically across 600+ connected tools. I also like that Supergroups tie access to live attributes like department or manager, so access stays accurate without any admin intervention.
Rippling IT Key Features
- Role-based MFA: Assign different authentication factors to different user groups, such as hardware keys for admins and TOTP codes for everyone else.
- Virtual LDAP directory: Expose Rippling user data over LDAP so legacy apps and network hardware like firewalls and NAS devices can authenticate against it.
- Cloud RADIUS: Let employees log into Wi-Fi and VPNs using their Rippling credentials, without managing a separate RADIUS server.
- Conditional access rules: Evaluate device trust, location, time, and risk profile at the moment of access to allow or block authentication in real time.
Rippling IT Integrations
Rippling IT offers 600+ integrations, including Microsoft Entra ID, on-premises Active Directory, Google Workspace, Okta, and Duo. It also supports custom SAML, SCIM, and REST API integrations with webhooks.
Pros and Cons
Pros:
- Virtual LDAP supports legacy systems
- Dynamic groups keep access aligned
- HR-driven provisioning follows employee changes
Cons:
- No Linux device management or ZTNA
- Directory synchronization remains mostly one-way
Learn more about Rippling IT: Best for centralized identity management
- 14-day free trial
- From $2/device/month
Visit WebsiteCustomer Rating:4.7/5
Scalefusion OneIdP guides users through directory setup in four steps. My Evaluation Score
- Device Management
- Adequate
- Directory Integration & Sync
- Strong
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Adequate
- Multi-Platform Application Support
- Minimal
- User Provisioning & Lifecycle Management
- Adequate
Scalefusion OneIdP is a cloud identity and access management platform that combines a built-in directory, SSO, MFA, conditional access, and device-based authentication into a single console.
Who Is Scalefusion OneIdP Best For?
Scalefusion OneIdP is a strong fit for IT teams already using or evaluating Scalefusion's device management stack who want identity and access control in the same console.
Why I Picked Scalefusion OneIdP
I picked Scalefusion OneIdP as one of the best because it puts identity and device context in the same place, which is something most cloud directories can't claim. I love that the free built-in directory lets you manage identities without needing Entra or Google Workspace licenses, and Extended Access Policies (XAP) check device compliance, location, and IP at every login. If a device falls out of compliance, access gets blocked before it becomes your problem.
Scalefusion OneIdP Key Features
- SCIM v2.0 inbound and outbound sync: Bidirectional SCIM keeps user and group records in sync between OneIdP and sources like Okta, Entra ID, and PingOne, with changes typically applying within about one minute.
- On-Prem Connector: A Windows Server agent connects to your on-prem AD or LDAP directory over a certificate-secured link, letting you map and sync custom attributes without moving everything to the cloud first.
- JIT admin elevation: Grants temporary local admin rights on Windows and macOS on demand, with controls over who can elevate and which apps can run with elevated privileges.
- Passkey support: Users can authenticate without a password using Windows Hello, a FIDO security key, or a phone-based QR code flow, reducing reliance on shared credentials.
Scalefusion OneIdP Integrations
Scalefusion OneIdP integrates with Google Workspace, Microsoft Entra ID, Okta, PingOne, OneLogin, and on-premises Active Directory or LDAP. It supports SAML 2.0 and OIDC apps, plus SCIM connections to AWS, Atlassian, Auth0, and Apple Business Manager.
Pros and Cons
Pros:
- Passkeys and device login reduce passwords
- JIT admin elevation limits local privilege
- Device compliance informs every login
Cons:
- Device-context controls require Scalefusion UEM
- No access certification workflows
Learn more about Scalefusion OneIdP: Best for enterprise-wide zero-knowledge biometrics
- 30-day free trial
- From $3/user/month (billed annually)
Visit WebsiteCustomer Rating:4.5/5
Ping Identity lets users inspect LDAP attribute type schema details. My Evaluation Score
- Device Management
- Limited
- Directory Integration & Sync
- Excels
- Authentication & Access Control
- Excels
- Centralized Identity Management
- Excels
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Strong
Ping Identity is a cloud directory and identity platform that combines centralized directory management, adaptive SSO and MFA, user lifecycle provisioning, and federation across hybrid and multi-cloud environments.
Who Is Ping Identity Best For?
Ping Identity is a strong fit for large enterprises managing complex hybrid environments where identity governance, adaptive authentication, and legacy directory coexistence are non-negotiable.
Why I Picked Ping Identity
Ping Identity earns its spot on my shortlist because of its zero-knowledge biometrics, powered by the Keyless acquisition, which lets frontline and shared-workstation users authenticate without storing biometric data anywhere. I also rely on PingOne Protect's risk scoring, which pulls in device trust signals, IP reputation, and geo-velocity to make adaptive access decisions in real time. Paired with PingDirectory's sub-millisecond reads across up to 100 million identities, it's built for enterprises running identity at serious scale.
Ping Identity Key Features
- PingDirectory high-performance directory: Handles up to 100 million identities with sub-millisecond read responses and 99.99% uptime across LDAPv3 and SCIM 2.0.
- LDAP gateway with bidirectional sync: Connects existing AD, Oracle, IBM, and any LDAPv3 directory to PingOne, supporting real-time two-way sync and phased app migration without rewrites.
- PingOne Privilege just-in-time access: Grants time-bound privileged access to AWS, Azure, GCP, Kubernetes, Snowflake, and PostgreSQL, with sessions bound to TPM hardware.
- Identity governance with micro-certifications: Runs focused access reviews, SoD policy checks, and AI-assisted approval recommendations across your full user lifecycle.
Ping Identity Integrations
Ping Identity documents 1,800+ integrations, including Microsoft 365, Active Directory, Microsoft Entra ID, Workday, Salesforce, Google Workspace, Slack, Zoom, Snowflake, and CrowdStrike. REST and SCIM APIs, webhooks, Terraform providers, and the DaVinci marketplace support custom connectivity.
Pros and Cons
Pros:
- Adaptive risk scoring strengthens access decisions
- Hybrid directory support earns reviewer praise
- Zero-knowledge biometrics protect shared workstations
Cons:
- Device management depends on external tools
- Directory administration requires substantial setup
Learn more about Ping Identity: Best for modular IAM with HR-driven provisioning
- 30-day free trial
- From $1.40/user/month
Visit WebsiteCustomer Rating:4.6/5
HelloID manages third-party app integrations via a centralized admin panel. My Evaluation Score
- Device Management
- Limited
- Directory Integration & Sync
- Adequate
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Strong
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Strong
HelloID is a modular, cloud-native IAM platform from Tools4ever that combines SSO, MFA, automated user provisioning, self-service access, and identity governance across cloud and on-premises environments.
Who Is HelloID Best For?
HelloID is a strong fit for IT administrators and identity managers in mid-sized organizations that need to automate user lifecycle management across HR systems, Active Directory, and cloud apps.
Why I Picked HelloID
I picked HelloID as one of the best because its HR-driven provisioning model is genuinely different from typical cloud directory tools. When an employee is hired or changes roles, HelloID pulls that data directly from source systems like SAP or ADP and automatically updates accounts across AD, Entra ID, and connected apps. I also like that the identity vault normalizes records from multiple HR and SIS sources, so your access rules are always working from clean, consistent data.
HelloID Key Features
- Modular SSO with multi-protocol support: HelloID supports SAML 2.0, OpenID Connect, and WS-Federation, plus browser extension-based access for apps without native SSO protocols.
- Contextual access rules: Admins can restrict or allow application access based on IP range, geolocation, date/time, and browser or OS version, with MFA enforcement tied to those rules.
- Self-service access with approval workflows: Employees and managers can request access through a self-service portal, with configurable approval chains and automatic access expiration.
- Governance and access reconciliation: The Governance module checks connected systems for orphaned or deviating accounts and runs periodic recertification reviews to keep access aligned with policy.
HelloID Integrations
HelloID offers 200+ ready-made connectors, including Microsoft Active Directory, Microsoft Entra ID, Google Workspace, SAP, ADP, AFAS, and Visma|Raet. PowerShell connectors and a REST API support custom integrations.
Pros and Cons
Pros:
- Governance reconciliation catches orphaned accounts
- Hybrid directory coexistence supports gradual migration
- HR-driven lifecycle automation reduces account drift
Cons:
- AD scenarios require an on-premises agent
- Device management capabilities are essentially absent
Learn more about HelloID: Best for Google Cloud-native identity federation
- 14-day free trial
- From $7.00/user/month

Google Cloud Identity supports multiple auth providers from one admin panel. My Evaluation Score
- Device Management
- Adequate
- Directory Integration & Sync
- Adequate
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Strong
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Minimal
Google Cloud Identity is Google's identity-as-a-service directory that handles centralized user and group management, SSO, MFA, device management, and Active Directory/LDAP sync across cloud and hybrid environments.
Who Is Google Cloud Identity Best For?
Google Cloud Identity fits IT teams already running Google Cloud or Google Workspace who need to centralize identity management, SSO, and access controls without adding a separate directory vendor.
Why I Picked Google Cloud Identity
Google Cloud Identity earns its spot on my shortlist because it's the most natural identity layer for teams already running workloads on Google Cloud or Google Workspace. I like that Context-Aware Access lets you enforce access policies based on user identity, device encryption status, and IP location at the same time, which is exactly what you need when your workforce is distributed across managed and unmanaged devices. GCDS and the newer cloud-based Directory Sync also give you real, workable paths to sync your existing Active Directory without rearchitecting your on-prem environment first.
Google Cloud Identity Key Features
- Pre-integrated SAML app catalog: Connects hundreds of third-party SaaS apps—including AWS, Salesforce, and RingCentral—using pre-built SAML configurations in both Free and Premium editions.
- Passkey and FIDO2 security key support: Lets admins enable passwordless sign-in via passkeys or restrict authentication to hardware security keys only.
- Dynamic groups: Automatically adds and removes group members based on user attribute queries, including custom attributes, without manual admin updates.
- Secure LDAP (Premium): Allows on-prem or cloud-hosted LDAP applications such as Jira, OpenVPN, and FreeRADIUS to authenticate against Cloud Directory.
Google Cloud Identity Integrations
Google Cloud Identity offers a pre-integrated SAML app catalog with hundreds of apps, including AWS, Salesforce, RingCentral, and Zoho CRM. It connects with Active Directory, OpenLDAP, and Microsoft Entra ID through sync or federation, supports Secure LDAP, and provides a REST API for custom integrations.
Pros and Cons
Pros:
- Passkeys and security keys support passwordless authentication
- Context-aware policies pair identity with device posture
- Google-native federation simplifies cloud access
Cons:
- macOS and Linux management remains limited
- Not a full Active Directory replacement
Learn more about Google Cloud Identity: Best directory-as-a-service functions
- 30-day free trial
- From $9/user/month (billed annually)
Visit WebsiteCustomer Rating:4.6/5
JumpCloud lets users manage and view all directory users in one place. My Evaluation Score
- Device Management
- Strong
- Directory Integration & Sync
- Strong
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Excels
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Strong
JumpCloud is a cloud directory platform that unifies identity management, SSO, MFA, device management, and access control for human, machine, and AI-agent identities across Windows, macOS, Linux, and mobile environments.
Who Is JumpCloud Best For?
JumpCloud fits IT teams managing mixed-OS environments who need identity, access, and device management in a single platform without relying on legacy on-premises infrastructure.
Why I Picked JumpCloud
JumpCloud earns its spot on my shortlist because it's one of the few platforms that delivers true directory-as-a-service without depending on any on-premises infrastructure. I love that its Open Cloud Directory treats Windows, macOS, and Linux devices as equal citizens, managing identities, SSO, MFA, and device compliance from one console. The Active Directory Integration's three sync modes (AD-authoritative, two-way, or JumpCloud-authoritative) let you migrate off legacy AD at your own pace rather than cutting over all at once.
JumpCloud Key Features
- Access Risk Detection: Flags unusual login behavior—like impossible travel or dormant accounts resuming activity—and triggers MFA challenges or alerts via email, Slack, or webhook.
- Cloud RADIUS: Provides built-in RADIUS authentication for Wi-Fi and VPN access, with all events logged in Directory Insights, no additional hardware required.
- HR-driven user lifecycle management: Connects to systems like Workday, BambooHR, and HiBob to automate account creation, staging, and deprovisioning across connected apps.
- Cross-platform patch management: Manages OS and application patches across Windows, macOS, and Linux from one console, with compliance dashboards and bulk remediation tools.
JumpCloud Integrations
JumpCloud offers native integrations with Active Directory, Microsoft 365, Entra ID, Google Workspace, BambooHR, Workday, Personio, Namely, HiBob, and People HR. It supports custom connections through SCIM, REST APIs, Cloud LDAP, and RADIUS, including Jira, Confluence, Jenkins, Kubernetes, and Docker.
Pros and Cons
Pros:
- Risk-aware conditional access policies
- Phased Active Directory migration support
- Cross-platform identity and device control
Cons:
- Android management can be less stable
- Broad coverage can sacrifice feature depth
Learn more about JumpCloud: Best for hybrid Microsoft 365 identity workflows
- 30-day free trial
- From $7.00/user/month

Microsoft Entra ID centralizes tenant, user, and app management in one dashboard. My Evaluation Score
- Device Management
- Adequate
- Directory Integration & Sync
- Strong
- Authentication & Access Control
- Excels
- Centralized Identity Management
- Excels
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Excels
Microsoft Entra ID is a cloud identity and access management service that handles user and group management, SSO, MFA, Conditional Access, device identity, and automated provisioning across cloud and hybrid environments.
Who Is Microsoft Entra ID Best For?
Microsoft Entra ID is a strong fit for organizations already running Microsoft 365 or Azure that need to manage identity across both cloud and on-premises Active Directory environments.
Why I Picked Microsoft Entra ID
Microsoft Entra ID earns its spot on my list because it's the identity backbone that organizations running Microsoft 365 and Azure already rely on, making it a natural fit for hybrid directory workflows. I particularly like how Conditional Access lets you enforce granular, context-aware policies across cloud and on-premises environments without needing a separate tool. Connect Sync and Cloud Sync both handle multi-forest AD environments, so teams managing disconnected forests after a merger can maintain directory continuity without a full cutover.
Microsoft Entra ID Key Features
- Privileged Identity Management: Assigns just-in-time, least-privilege admin roles so elevated access is granted only when needed and automatically expires.
- Passkey authentication: Supports device-bound and synced passkeys via Microsoft Authenticator, hardware security keys, Apple iCloud Keychain, and Google Password Manager.
- Automated user provisioning: Creates, updates, and removes accounts across connected apps using SCIM 2.0, LDAP, SQL, and custom ECMA connectors as user roles and statuses change.
- Lifecycle workflows: Automates joiner, mover, and leaver processes—including triggering tasks like account creation or access removal—based on HR data and user attributes.
Microsoft Entra ID Integrations
Microsoft Entra ID offers thousands of native app-gallery integrations, including ServiceNow, Workday, Salesforce, Slack, Snowflake, and Microsoft 365 and Azure services. Microsoft Graph, SCIM 2.0, and Application Proxy support custom and on-premises integrations.
Pros and Cons
Pros:
- Passwordless authentication reduces phishing exposure
- Context-aware policies strengthen distributed workforce access control
- Hybrid synchronization supports disconnected Active Directory forests
Cons:
- Device management depends on separate endpoint tooling
- Advanced governance requires multiple licensing tiers
Learn more about Microsoft Entra ID: Best for efficient employee lifecycle management
- 30-day free trial
- From $6/user/month (billed annually)

Okta Workforce Identity Cloud flags high-risk access with AI-driven revoke recommendations. My Evaluation Score
- Device Management
- Minimal
- Directory Integration & Sync
- Strong
- Authentication & Access Control
- Excels
- Centralized Identity Management
- Excels
- Multi-Platform Application Support
- Excels
- User Provisioning & Lifecycle Management
- Excels
Okta Workforce Identity Cloud is a cloud directory and identity platform that centralizes user, group, and device management across HR systems, Active Directory, LDAP, and thousands of SaaS and on-premises apps through SSO, adaptive MFA, lifecycle provisioning, and access governance.
Who Is Okta Workforce Identity Cloud Best For?
Okta Workforce Identity Cloud is a strong fit for mid-to-large enterprises with complex, multi-source identity environments where HR-driven provisioning and governance across thousands of apps are a priority.
Why I Picked Okta Workforce Identity Cloud
I picked Okta Workforce Identity Cloud as one of the best because its HR-driven lifecycle automation is genuinely hard to beat. When a new hire is added in Workday or BambooHR, Okta automatically provisions their accounts across hundreds of apps via SCIM, with no manual tickets required. I also like that offboarding is equally immediate: a single deactivation cuts access across every connected app at once, which also frees up licenses automatically.
Okta Workforce Identity Cloud Key Features
- Adaptive MFA: Enforces multi-factor authentication using context signals like device, location, network, and behavior to adjust access requirements in real time.
- Universal Directory: Acts as a central identity record, pulling users, groups, and custom attributes from AD, LDAP, and multiple HR systems simultaneously.
- Identity Threat Protection: Continuously scores session risk and can trigger Universal Logout across all connected apps when a threat is detected.
- Privileged Access: Provides SSO to Linux and Windows servers, records SSH and RDP sessions, and supports just-in-time access with multi-step approvals.
Okta Workforce Identity Cloud Integrations
Okta Workforce Identity Cloud offers 8,000+ pre-built integrations, including Active Directory, LDAP, Workday, BambooHR, SuccessFactors, Google Workspace, Salesforce, Slack, Microsoft Teams, and Jamf. REST APIs, event hooks, and Workflows support custom integrations.
Pros and Cons
Pros:
- Adapts authentication to identity risks
- Unifies HR, AD, and LDAP identities
- Automates employee onboarding and offboarding
Cons:
- Cannot fully replace GPO-heavy AD environments
- Doesn’t provide full device management
Learn more about Okta Workforce Identity Cloud: Best for integrating on-premise and cloud directories
- 30-day free trial
- From $3/user/month

OneLogin Advanced Directory lets users view and manage all user accounts centrally. My Evaluation Score
- Device Management
- Limited
- Directory Integration & Sync
- Strong
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Strong
- Multi-Platform Application Support
- Strong
- User Provisioning & Lifecycle Management
- Strong
OneLogin Advanced Directory is a cloud directory service that centralizes user identity management across Active Directory, LDAP, Google Workspace, and HR systems, with built-in SSO, MFA, adaptive authentication, and automated provisioning.
Who Is OneLogin Advanced Directory Best For?
OneLogin Advanced Directory is a strong fit for IT teams managing hybrid environments where Active Directory, cloud apps, and HR systems need to stay in sync without a dedicated IAM team.
Why I Picked OneLogin Advanced Directory
I picked OneLogin Advanced Directory because it handles real-time sync across Active Directory, LDAP, Google Workspace, and HR systems like Workday from a single connector. When an AD account closes, OneLogin cuts access across every connected app within seconds. I also like that its VLDAP and RADIUS bridges keep legacy infrastructure in the loop without forcing a rip-and-replace.
OneLogin Advanced Directory Key Features
- SmartFactor Authentication: Uses Vigilance AI to build a risk score from location, device, and behavior, then decides whether to allow, challenge, or deny a login.
- 6,000+ app catalog: Pre-integrated connectors for SSO and provisioning across cloud and on-premises applications, with new integrations added daily.
- Lifecycle automation with Workflows: A low-code automation layer that handles provisioning, deprovisioning, and custom identity tasks beyond standard create/update/delete operations.
- Compromised credential check: Validates new or changed passwords against a database of known stolen credentials before allowing them to be set.
OneLogin Advanced Directory Integrations
OneLogin Advanced Directory offers 6,000+ pre-integrated app connectors, including Active Directory, LDAP, Microsoft Entra ID, Google Workspace, Workday, UKG, BambooHR, and Jamf. REST APIs, SDKs, webhooks, and custom connectors support additional integrations.
Pros and Cons
Pros:
- Broad passwordless and MFA options
- Risk-based authentication adapts to behavior
- Real-time offboarding cuts access quickly
Cons:
- No built-in access certification campaigns
- No native device management
Learn more about OneLogin Advanced Directory: Best for SSO and MFA across 15+ auth methods
- 30-day free trial
- From $3/user/month
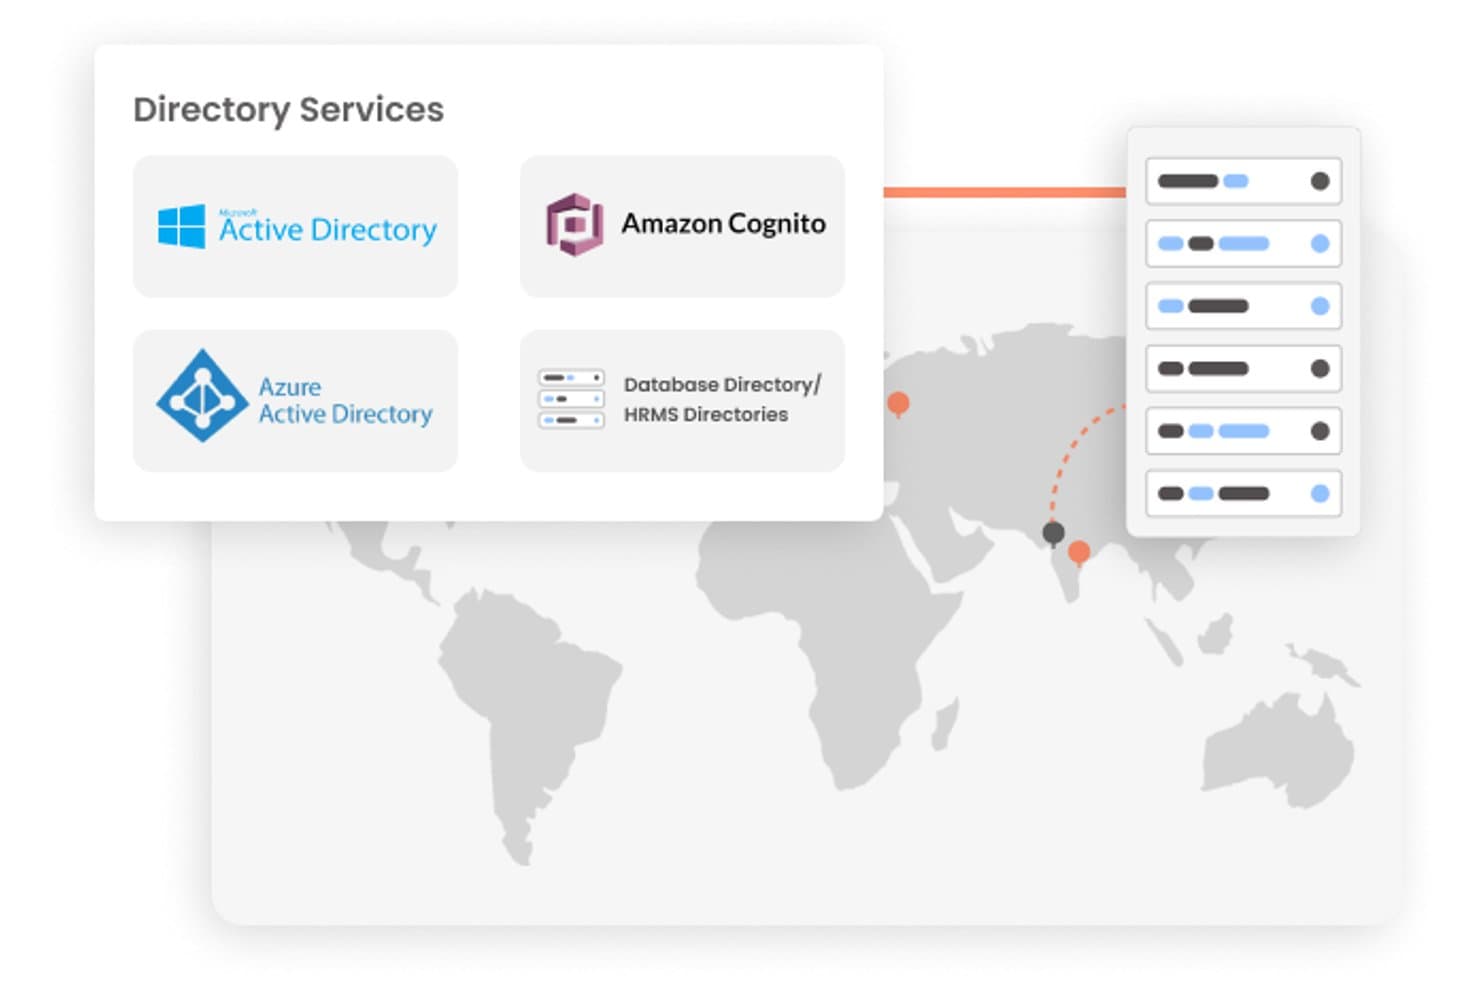
miniOrange supports Active Directory, Azure AD, Amazon Cognito, and HRMS directories. My Evaluation Score
- Device Management
- Adequate
- Directory Integration & Sync
- Strong
- Authentication & Access Control
- Strong
- Centralized Identity Management
- Strong
- Multi-Platform Application Support
- Excels
- User Provisioning & Lifecycle Management
- Strong
miniOrange is a cloud directory services platform that combines Directory as a Service (DaaS), SSO, MFA, adaptive access control, and user lifecycle management across cloud, on-premises, and hybrid environments.
Who Is miniOrange Best For?
miniOrange is a strong fit for IT and identity teams managing access across a mix of cloud apps, legacy systems, and on-premises directories who need broad MFA and SSO coverage without rebuilding their existing infrastructure.
Why I Picked miniOrange
I picked miniOrange as one of the best because its authentication breadth is genuinely hard to match at this price point: 15+ MFA methods, including FIDO2/passkeys, hardware tokens like YubiKey, and push notifications, plus SSO across SAML, OIDC, OAuth, and legacy apps via reverse proxy. I particularly like that it extends MFA down to Windows RDP, macOS, and Linux SSH logins, which closes a gap most directory platforms leave open. Adaptive, risk-based access rules layer on top, triggering step-up MFA based on IP, location, or device signals.
miniOrange Key Features
- Hybrid LDAP gateway: An on-premises LDAP Gateway lets you connect miniOrange to your existing AD or LDAP infrastructure without exposing it to the internet.
- Joiner-Mover-Leaver automation: HR-driven provisioning syncs with Workday, BambooHR, and SAP SuccessFactors to trigger role assignments and deprovisioning automatically.
- Legacy app access gateway: Header-based and reverse proxy login extends SSO to legacy and thick-client apps that don't support SAML or OAuth.
- RADIUS and TACACS+ server: Built-in AAA server authentication covers VPN, VDI, routers, and switches from the Premium tier up.
miniOrange Integrations
miniOrange offers 6,000+ integrations, including Microsoft 365, Google Workspace, Salesforce, AWS, Slack, Zoom, Workday, BambooHR, SAP SuccessFactors, Okta, and Fortinet. It supports SAML, OAuth, OIDC, SCIM, REST APIs, RADIUS, and TACACS+ for custom connectivity.
Pros and Cons
Pros:
- Legacy applications gain modern authentication controls
- Hybrid directory support eases phased migrations
- MFA spans cloud, desktop, and server logins
Cons:
- Directory configuration can challenge new administrators
- Advanced lifecycle controls require higher tiers
Learn more about miniOrange:
Other Cloud Directory Services
Here are some additional cloud directory services options that didn’t make it onto my shortlist, but are still worth checking out:
- 11ForgeRockBest for large-scale adaptive identity governance
- 12Zoho DirectoryBest for Zoho ecosystem identity and access control
- 13OneLoginBest for adaptive MFA with real-time AD sync
- 14SailPointBest for enterprise identity governance at scale
- 15VMware Workspace ONEBest for device-centric identity and access control
- 16IBM VerifyBest for adaptive risk-based access at enterprise scale
How I Evaluate Cloud Directory Services
I split my evaluation into three parts: core functionality (managing user identities centrally and enforcing authentication across apps) carries the most weight, followed by standout features like passwordless authentication, then factors like migration support and onboarding quality.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I score each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then convert the total into a percentage to help assess each tool's overall fit, with extra weight on any functionalities I've deemed essential.
- Identity Management (Essential): I evaluate how each tool stores and organizes user identities, looking at custom attributes, group nesting, and org hierarchy support.
- Authentication & Access Control (Essential): SSO breadth, MFA options, and conditional access policies are what I check—especially context-based rules tied to device or location.
- Directory Integration & Sync: I look at how well a platform syncs with existing directories like Active Directory or LDAP, including real-time updates and conflict handling.
- Device Management: Each tool's ability to enroll devices, push policies, and run compliance checks across Windows, macOS, and Linux factors into my scoring.
- User Provisioning & Lifecycle: Automated onboarding and offboarding across connected apps is what I evaluate, including role-based provisioning and scheduled access reviews.
- Multi-Platform App Support: I check the size and variety of each tool's app catalog, plus how flexible custom integrations are for apps without pre-built connectors.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Passwordless authentication is a big one for me. I check whether a platform supports FIDO2/WebAuthn and biometrics, since these methods cut credential-based attack risk and speed up logins across the org. Zero trust network access matters just as much—I look for built-in ZTNA that lets admins gate access to internal apps without relying on a traditional VPN. I also evaluate directory-as-a-service flexibility, specifically whether a tool can fully replace AD or coexist in hybrid mode during phased migrations.
Beyond Features
Migration support matters a lot—I check whether a platform offers automated attribute mapping and hybrid coexistence so you can phase out legacy AD without a hard cutover. I also evaluate compliance readiness, looking for built-in audit logs and access reviews aligned with frameworks like SOC 2 or ISO 27001, since manual audit prep burns time most IT teams don't have. Finally, I consider how well onboarding resources and documentation set admins up for self-sufficiency after deployment.
How To Choose a Cloud Directory Service
It’s easy to get bogged down in long feature lists and complex pricing structures. To help you stay focused as you work through your unique software selection process, here’s a checklist of factors to keep in mind:
| Factor | What to Consider |
|---|---|
| FactorScalability | What to ConsiderCan the service grow with your business? Consider user limits, data capacity, and long-term costs. Make sure the solution will accommodate growth without needing frequent upgrades. |
| FactorIntegrations | What to ConsiderDoes it work with your current systems? Check compatibility with existing software like HR systems, CRMs, and productivity tools. Avoid solutions that require extensive workarounds or third-party connectors. |
| FactorCustomizability | What to ConsiderCan you tailor it to fit your workflows? Look for flexible settings and options to adjust user roles, permissions, and interfaces to match your team's needs. |
| FactorEase of use | What to ConsiderIs it user-friendly for your team? Consider the learning curve and user interface. Avoid tools that require extensive training or have a cluttered interface that might slow down user adoption. |
| FactorImplementation and onboarding | What to ConsiderHow quickly can you get started? Evaluate the setup process, including data migration and user training. Look for vendors offering support during onboarding to minimize downtime and confusion. |
| FactorCost | What to ConsiderDoes it fit your budget? Compare pricing models, including subscription fees, potential add-ons, and long-term costs. Be wary of hidden fees or costs that can increase as your usage grows. |
| FactorSecurity safeguards | What to ConsiderAre your data and users protected? Check for encryption, authentication methods, and compliance with security standards. Ensure the service can meet your industry’s security requirements to avoid vulnerabilities. |
| FactorCompliance requirements | What to ConsiderDoes it meet industry standards? Verify that the service complies with regulations relevant to your business, such as GDPR or HIPAA. Non-compliance can lead to legal issues and fines. |
Trends in Cloud Directory Services For 2025
Reviewing product updates, press releases, and release logs from leading tools reveals key trends in cloud directory services that reflect the changing dynamics of cloud infrastructure access management.
Here's my overview of the current trends in 2025:
Trends in Cloud Directory Services
- Enhanced Security Features: A noticeable uptick in deploying advanced security features, such as adaptive multi-factor authentication (MFA) and machine learning-driven anomaly detection. These enhancements address the growing sophistication of cybersecurity threats and the need for more dynamic, context-aware security measures.
- Integration and Interoperability: An evident push towards greater integration and interoperability with other cloud services, user provisioning software, and legacy systems exists. This trend is driven by the need to create seamless user experiences and simplify the management of diverse IT environments, indicating a move towards more flexible and adaptable access management solutions.
- Scalability and Cloud-Native Features: The emphasis on scalability and cloud-native architectures highlights the industry's response to cloud environments' growing complexity and size. These features ensure that cloud directory services can efficiently manage access across extensive, distributed infrastructures, supporting organizational growth and cloud adoption strategies.
- Comprehensive Compliance Reporting: In response to tightening regulatory requirements, developing comprehensive compliance reporting tools has become a top priority. These tools help organizations navigate the complex landscape of data protection and privacy laws, underscoring the critical role of cloud directory services in ensuring legal compliance.
Features Becoming Less Important
- Traditional Password-Based Authentication: The shift away from conventional password-based authentication towards more secure and user-friendly alternatives, such as biometrics and single sign-on (SSO), indicates a decrease in the importance of passwords. This transition reflects the industry's recognition of password-based access controls' limitations and security risks.
By closely examining these trends, IT professionals can gain valuable insights into the future direction of cloud directory services and the evolving needs of cloud-based infrastructure management.
What Are Cloud Directory Services?
Cloud directory services are solutions that manage and organize user identities and access within an organization. IT professionals, security teams, and HR departments commonly use these tools to ensure secure and efficient access to resources. User management, single sign-on, and multi-factor authentication capabilities help with maintaining security and simplifying login processes. Overall, these tools provide centralized control over user access, enhancing operational efficiency.
Features
Here are the most important offerings to look for in cloud directory services:
- Single Sign-On (SSO): This feature allows users to access multiple applications with a single set of credentials. It significantly improves user experience by reducing password fatigue and simplifying user access management across various platforms.
- Multi-Factor Authentication (MFA): MFA adds an extra layer of security by requiring users to provide two or more verification factors to gain access to IT resources. This is crucial for preventing unauthorized access and safeguarding sensitive data.
- Unified Directory Services: This provides a centralized platform for managing access to all IT resources. It eliminates the need for multiple directories, streamlines administration, and ensures consistency in access control across the organization.
- Directory Integration: The ability to integrate with existing directories (like Active Directory or LDAP) ensures seamless synchronization and management of user accounts. This helps organizations leverage their existing infrastructure while transitioning to cloud-based services.
- Scalability: Cloud directory services must be able to scale with the organization's growth. This ensures that the directory service can handle the growth without performance degradation as the number of users, devices, and applications increases.
- Role-Based Access Control (RBAC): RBAC enables the assignment of access rights based on an organization's roles. This simplifies user permissions management, ensuring that individuals only have access to the information and resources necessary for their roles.
- Self-Service Password Reset: This feature allows users to reset passwords without IT intervention. It reduces the workload on IT departments and enhances user productivity by minimizing downtime.
- Audit and Reporting Capabilities: These features provide insights into user activities and access patterns. They are essential for compliance, security monitoring, and understanding how resources are used within the organization.
- Cloud-Native Architecture: A cloud-native directory service is designed to take full advantage of cloud computing frameworks. This ensures high availability, disaster recovery, and flexible deployment options, aligning with modern cloud strategies.
- API Access and Customization: The ability to customize and integrate the directory service with other applications via APIs is critical. It allows organizations to tailor the service to their needs and automate various processes, enhancing efficiency.
Cloud directory services streamline managing user access to IT resources and play a critical role in enhancing organizational security. By focusing on the features outlined above, organizations can ensure they have a robust foundation to support their evolving IT needs and protect their digital assets.
Benefits
Cloud directory services provide centralized management for user access to systems, applications, files, and networks, catering to the evolving needs of modern, cloud-based infrastructures. Below are five primary benefits of cloud directory services:
- Enhanced Security Protocols: Cloud directory services significantly reduce the risk of security breaches by centralizing user access control. They offer advanced security measures like multi-factor authentication and single sign-on, bolstering the organization's defense against unauthorized access and cyber threats.
- Scalability and Flexibility: Cloud directory services offer unparalleled scalability, easily accommodating an organization's growth. This flexibility allows businesses to add or remove users and manage access to resources efficiently without significant infrastructure changes.
- Cost Reduction and Efficiency: Cloud directory services can significantly lower operational costs by eliminating the need for on-premises hardware and reducing IT administrative tasks. They streamline access management processes, freeing up valuable IT resources and reducing overhead.
- Improved User Experience: With features like single sign-on and self-service password resets, these services offer a more streamlined and user-friendly access experience. Empowering users to manage their access improves productivity and reduces the workload on IT support teams.
- Compliance and Reporting: Cloud directory services simplify compliance with built-in reporting and audit tools. They help organizations adhere to regulatory requirements by providing detailed logs and reports on user activity and access changes.
Cloud directory services improve operational efficiency and security, making them an essential component of any cloud-based strategy. As businesses evolve and adopt cloud technologies, the importance of a scalable and secure directory service becomes increasingly evident.
Costs & Pricing
Cloud directory services offer a range of plans tailored to meet different organizational needs, from small businesses seeking essential access management to large enterprises requiring advanced security features and scalability.
The goal is to provide a secure, efficient, and flexible solution that grows with your business.
Plan Comparison Table for Cloud Directory Services
Below, I've outlined the standard plan options and their pricing to help simplify your decision-making process.
| Plan Type | Average Price | Common Features |
|---|---|---|
| Plan TypeFree | Average Price$0 | Common FeaturesBasic user and group management, Single Sign-On (SSO) for a limited number of applications |
| Plan TypeBasic | Average Price$1-3/user/month | Common FeaturesFull user and group management, SSO for all applications, basic MFA, basic reporting |
| Plan TypeProfessional | Average Price$4-8/user/month | Common FeaturesAdvanced user and group management, advanced MFA options, audit logs, API access, custom integrations |
| Plan TypeEnterprise | Average Price$9-15/user/month | Common FeaturesPremium support, unlimited SCIM provisioning, directory insights, identity governance, 24/7 support |
| Plan TypeCustom | Average PriceQuote-based | Common FeaturesTailored features to meet specific organizational needs, personalized support options |
Assessing your organization's current and potential future needs is essential when considering cloud directory services. Opt for a plan that offers the flexibility to scale and adapt to your changing business landscape.
Cloud Directory Services FAQ
Here are answers to some common questions regarding cloud directory services:
What are the main data security risks associated with cloud directory services?
Cloud directory services store sensitive identity information, making them attractive targets for cybercriminals. A breach could potentially compromise access across numerous applications. Additionally, organizations must carefully configure these services to maintain compliance with regulations like GDPR or HIPAA, which can be technically challenging.
What are the common synchronization issues with cloud directory services?
Synchronization issues include delays or inconsistencies in syncing user data between cloud and on-premises systems. These can cause frustration and access problems when updates in one system don’t immediately reflect in others, potentially leading to temporary security gaps and decreased productivity.
How can organizations mitigate the risks of using cloud directory services?
Organizations should implement multi-factor authentication, establish clear security policies, conduct regular security audits, maintain offline backups of critical directory data, develop contingency plans for service disruptions, and thoroughly evaluate providers’ security practices before implementation.
What compatibility challenges might organizations face with cloud directory services?
Organizations often encounter compatibility issues when integrating cloud directory services with various applications and on-premises systems. These integrations frequently require complex configurations, especially with legacy systems that use outdated authentication protocols. Without proper planning, these challenges can extend implementation timelines and increase costs.
How can organizations address compliance challenges with cloud directory services?
Organizations should implement strong audit logging capabilities, regularly review access controls, clearly define the shared responsibility model with their provider, encrypt sensitive data, maintain comprehensive documentation of security controls, and stay informed about changing regulatory requirements in all relevant jurisdictions.
What monitoring capabilities should organizations look for in cloud directory services?
Comprehensive monitoring should include real-time alerts for suspicious activities, detailed audit logs for compliance reporting, visibility into synchronization status and failures, performance metrics for authentication processes, and reporting tools that help identify potential security vulnerabilities
How do cloud directory services handle identity lifecycle management?
The effectiveness of automated provisioning and deprovisioning processes varies between providers. Organizations should evaluate how services handle temporary access requirements, attribute changes, role transitions, and account terminations to ensure security policies are consistently enforced throughout the identity lifecycle.
What should organizations consider when planning for cloud directory service scalability?
Organizations should assess how the service handles large numbers of users, groups, and authentication requests. They should understand performance implications during peak usage periods, test synchronization processes with realistic data volumes, and evaluate the cost implications of scaling up user licenses over time.
How do compatibility issues impact cloud directory service implementations?
Compatibility issues can force organizations to maintain multiple identity management systems simultaneously, creating administrative overhead. They may also result in inconsistent user experiences across platforms and compromise security if workarounds are implemented to address compatibility gaps.