

De beste kodeanalyseverktøyene hjelper utviklere med å oppdage feil tidlig, forbedre kodekvaliteten og håndheve kodestandarder automatisk, slik at problemer ikke når produksjonsmiljøet. Når du feilsøker uklare feil, leter etter skjulte mangler i store kodebaser eller håndterer uensartede kodestiler på tvers av team, blir det frustrerende og tidkrevende å opprettholde kvalitet i stor skala.
Den riktige kodeanalyseplattformen automatiserer kontroller, fremhever reelle problemer og lar teamene konsentrere seg om å skrive renere og mer pålitelig kode. Som teknologidirektør med over 20 års erfaring med å teste og vurdere utviklingsverktøy i aktive leveranseprosesser har jeg identifisert de beste løsningene som hjelper team med å jobbe raskere uten å ofre kvalitet. Hver anmeldelse dekker funksjoner, fordeler og ulemper samt de beste bruksområdene, slik at du kan velge det riktige verktøyet for arbeidsflyten din.
Hvorfor du kan stole på våre programvareanbefalinger
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Teamet vårt har testet og anmeldt programvare siden 2012. Vi er selv teknologiledere, så vi vet hvor vanskelig og hvor viktig det er å velge riktig programvare.
I denne guiden har vi vurdert verktøyene gjennom praktisk testing og uavhengig research og gitt dem poeng ut fra våre utvelgelseskriterier.
Anmeldelsene våre bygger på vår egen redaksjonelle vurdering. De er ikke et salgsargument.
Ekspertanmeldere:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Sammenligningstabell for kodeanalyseverktøy
Denne sammenligningstabellen oppsummerer prisinformasjonen for mine utvalgte kodeanalyseverktøy.
Sorted by: Default
| Tool | Starting Price | Website | |
|---|---|---|---|
Best for next-gen code reviews | 4.3 out of 5 | $350/month Free plan available | Book Demo |
Best for detecting supply chain threats | Not rated | $399/month 7-day free trial + free demo available | Website |
Best for AI-driven code analysis | 4.5 out of 5 | $200/month Free plan available | Book Demo |
Best for in-repo AI security remediation | 4.7 out of 5 | $1,000/dev/year Free demo available | Website |
Best for AI-driven vulnerability detection | Not rated | $34/developer/month Free plan available | Book Demo |
Best for security testing | 4.4 out of 5 | $25/contributor/month Free plan + free demo available | Website |
Best for technical debt management | 4.6 out of 5 | $21/month Enterprise | Website |
Best for advanced analysis | 4.4 out of 5 | $24/user/month 14-day free trial + free plan available | Website |
Best for CI/CD integrations | 4.5 out of 5 | $18/user/month 14-day free trial + free plan + free demo available | Website |
Best open-source code analyzer | Not rated | Open source project and available for free. Free | Website |


Anmeldelser av de beste kodeanalyseverktøyene
Nedenfor finner du mine detaljerte sammendrag av de beste kodeanalyseverktøyene som kom med på kortlisten. Anmeldelsene mine gir en grundig gjennomgang av de viktigste funksjonene, fordelene & ulempene, integrasjonene og de ideelle bruksområdene for hvert verktøy, slik at du kan finne det beste alternativet for deg.

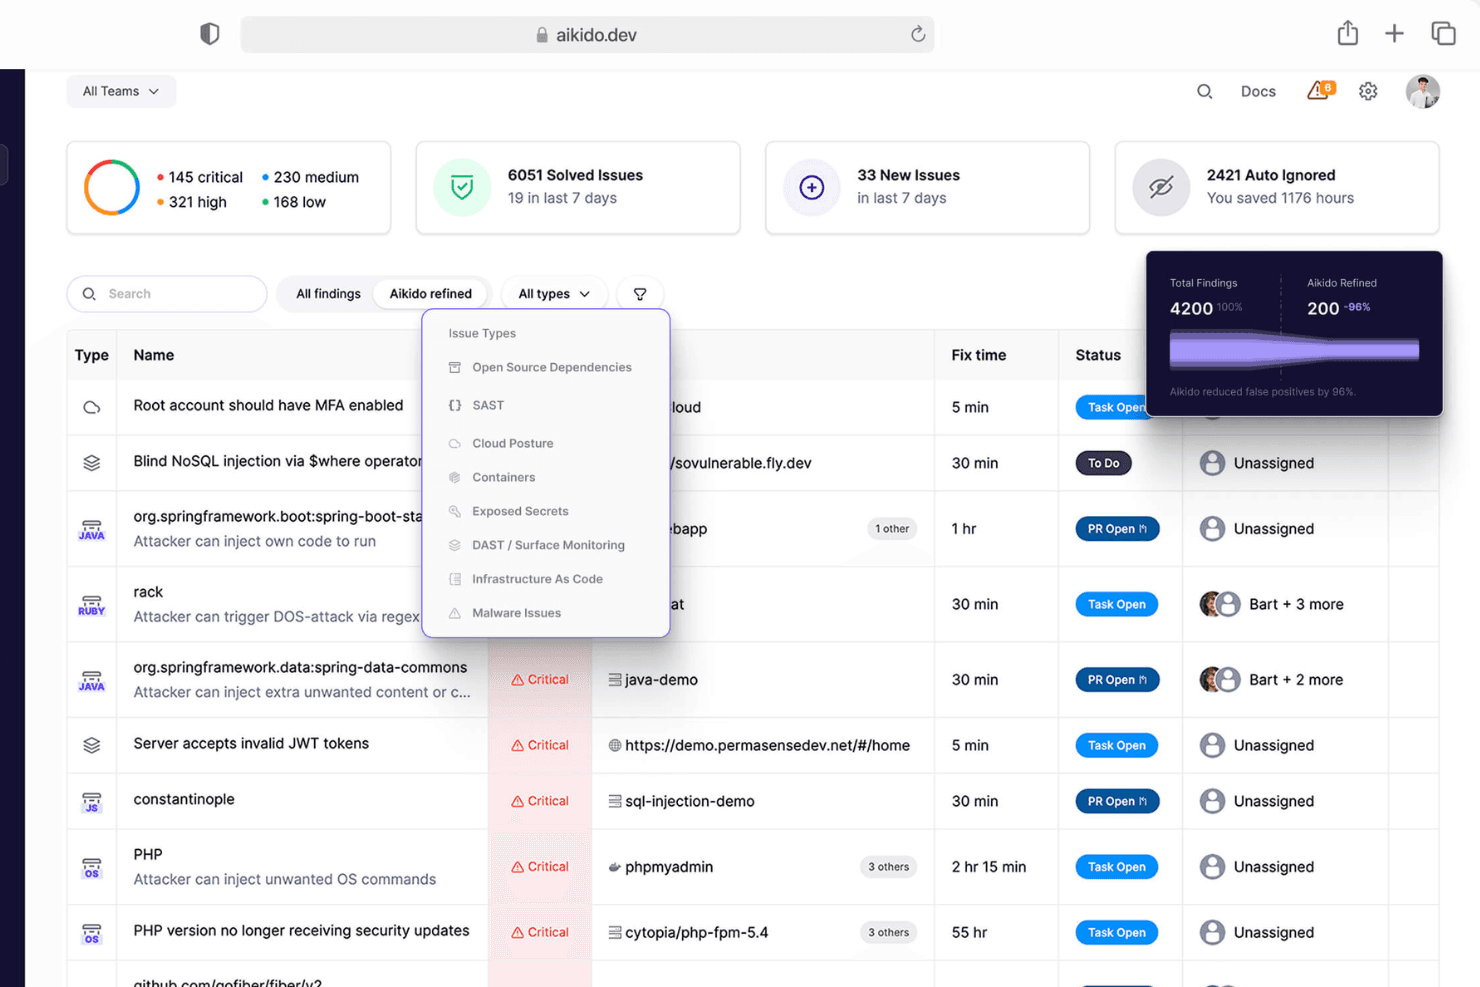
Aikido Security provides a unified dashboard to triage and filter issues by type, severity, and scan source. Aikido Security is a DevSecOps platform that provides comprehensive security solutions for both code and cloud environments.
Why I picked Aikido Security: Aikido combines next-gen code quality checks with static application security testing (SAST) in one platform, helping developers catch both bugs and vulnerabilities early. Its AI-powered reviews flag maintainability and code quality issues while detecting critical flaws like SQL injection, cross-site scripting (XSS), and buffer overflows. Powered by trusted open-source scanners like Bandit, Opengrep (replacing Semgrep), and Gosec, alongside Aikido’s proprietary AI-driven engines, the platform delivers deep, accurate, and actionable analysis.
Aikido Security Standout Features and Integrations:
Features that also make Aikido stand out are its cloud posture management (CSPM) capabilities that detect cloud infrastructure risks across major cloud providers and its secrets detection feature that prevents unauthorized access by checking your code for leaked and exposed API keys, passwords, certificates, and encryption keys.
Integrations include Amazon Web Services (AWS), Google Cloud, Microsoft Azure Cloud, Drata, Vanta, AWS Elastic Container Registry, Docker Hub, Jira, Asana, and GitHub.
Pros and Cons
Pros:
- Offers a comprehensive dashboard and customizable reports
- Provides actionable insights
- User-friendly interface
Cons:
- Custom SAST rules must be enabled by Aikido
- Unfixed CVEs excluded by default in ephemeral container scans
Learn more about Aikido Security: Best for detecting supply chain threats
- 7-day free trial + free demo available
- From $399/month (billed annually)

Xygeni dashboard showing prioritized application security risks across code, dependencies, CI/CD, secrets, and IaC. Xygeni is an AI-powered application security platform that combines SAST, software composition analysis (SCA), secrets detection, malicious code scanning, IaC analysis, CI/CD security, and supply chain risk monitoring. Code analysis is performed client-side, helping organizations keep source code within their own infrastructure.
Who Is Xygeni Best For?
Xygeni is a strong fit for security-focused engineering teams at mid-size to enterprise organizations that need unified visibility across application code, dependencies, and CI/CD pipelines.
Why I Picked Xygeni
I've included Xygeni in this list because it combines traditional application security testing with malicious code detection, software supply chain monitoring, and AI-assisted remediation workflows. In addition to identifying vulnerabilities in proprietary code and open-source dependencies, the platform helps teams prioritize findings through AI Triage and generate remediation suggestions using AI AutoFix. I also like that it combines reachability and exploitability analysis with broader application security visibility, helping teams focus on higher-priority risks.
Xygeni Key Features
- AI-powered SAST: Detects vulnerabilities including SQL injection, cross-site scripting (XSS), insecure authentication, authorization issues, and memory-related weaknesses.
- Malicious code detection: Identifies potentially malicious code patterns such as backdoors, trojans, reverse shells, obfuscated execution, masqueraded files, and registry tampering.
- AI Triage: Uses factors such as reachability, exploitability, internet exposure, and business impact to help prioritize security findings.
- AI AutoFix: Generates code-level remediation suggestions and supports pull-request-based workflows.
- Secrets and IaC scanning: Detects exposed credentials and analyzes infrastructure-as-code configurations across Terraform, CloudFormation, Kubernetes, and Helm environments.
- SBOM generation: Produces software bills of materials in SPDX and CycloneDX formats.
Xygeni Integrations
Xygeni integrates with GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, CircleCI, and other SCM and CI/CD platforms. It also supports Jira, GitHub Issues, and Slack for workflow management and notifications. IDE integrations are available for Visual Studio Code, Visual Studio, Eclipse, IntelliJ IDEA, Cursor, and Windsurf. The platform also provides REST API access and MCP server support for custom integrations and automation workflows.
Pros and Cons
Pros:
- Real-time malicious open-source package detection
- Covers code through container in one scan
- Filters noise to surface exploitable risks
Cons:
- Complex CI/CD setups need manual tuning
- Limited dashboard and report customization
Learn more about Xygeni: Best for AI-driven code analysis
- Free plan available
- From $200/month
Visit WebsiteCustomer Rating:4.5/5
Zeropath offers a comprehensive dashboard for monitoring code security. Zeropath is an AI-driven Static Application Security Testing (SAST) platform that appeals to businesses and professionals seeking to enhance code security and streamline their software development processes. With its ability to identify and automatically fix vulnerabilities, Zeropath is particularly suited for teams that prioritize security without compromising on speed. By minimizing false positives and integrating seamlessly with popular development platforms, it transforms security from a potential bottleneck into a catalyst for safer, faster code deployment.
Why I Picked Zeropath
I picked Zeropath because it stands out with its AI-driven approach to code analysis, offering unique capabilities that are crucial for modern development teams. The platform's rapid scanning capabilities, completing pull-request scans in under 60 seconds, ensure that your team receives timely feedback without disrupting the development workflow. Additionally, Zeropath's automated patch generation, refined through natural language prompts, addresses vulnerabilities efficiently, allowing your team to focus on innovation rather than manual fixes.
Zeropath Key Features
In addition to its standout capabilities, Zeropath offers several other features that make it a valuable tool for code analysis:
- Secrets Detection: Scans your repos for leaked tokens and keys.
- Comprehensive Language Support: Offers support for multiple programming languages, enhancing its versatility across different projects.
- Policy Enforcement: Allows you to write natural language rules and enforce them across your codebase.
- Integration with Version Control Systems: Seamlessly integrates with popular systems like GitHub and GitLab, providing real-time feedback during the development cycle.
Zeropath Integrations
Integrations include GitHub, GitLab, Bitbucket, Azure Pipelines, VS Code, CircleCI, and Docker.
Pros and Cons
Pros:
- Gives you clear fixes that speed up your security reviews.
- Cuts down noisy findings so your team can focus on real issues.
- It catches logic flaws and hidden risks you might miss in normal scans.
Cons:
- You may need time to adjust your workflow around its automation.
- Potential for missed vulnerabilities if AI is not configured correctly.
Learn more about Zeropath: Best for in-repo AI security remediation
- Free demo available
- Up to $1,000/dev/year (billed annually)
Visit WebsiteCustomer Rating:4.7/5
Mend.io dashboard showing a high-severity SQL injection (CWE-89) vulnerability with highlighted vulnerable code and remediation details. Mend.io is a code analysis platform that helps you catch security vulnerabilities and license issues in both proprietary and open-source code. It combines static application security testing (SAST) with software composition analysis (SCA) to give you visibility into your application risks as you build.
Why I picked Mend.io: I added Mend.io to this list because it tackles two pain points that many security teams struggle with—slow scans and noisy results. Its static analysis engine runs 10x faster than traditional SAST tools and focuses on surfacing new issues introduced since your last commit. That way, you can stay focused on fixing what matters instead of sorting through stale alerts. I also like its AI-powered remediation, which suggests fixes that you can apply with a single click to cut down mean time to resolution.
Mend.io Standout Features and Integrations:
Features include license compliance management for open-source packages, container image scanning, and risk analysis for AI-generated code components. It also offers role-based access controls, audit-ready reporting, and API access for custom integrations.
Integrations include Azure DevOps, Bitbucket Cloud, GitHub.com, GitHub Enterprise, GitLab, Mend for Azure Repos, Mend for Bitbucket Data Center, and Mend for GitLab.
Pros and Cons
Pros:
- Covers proprietary and open-source code
- AI-powered single-click remediation
- Faster scans than traditional SAST
Cons:
- Limited language and package support
- Setup may require configuration
Learn more about Mend.io: Best for AI-driven vulnerability detection
- Free plan available
- From $34/developer/month

Corgea flags a high-risk SQL injection issue and suggests a secure, parameterized code fix directly within a pull request. Corgea is built for developers and security professionals who want a smarter way to analyze code. It tackles the problem of finding and fixing vulnerabilities by bringing AI-driven analysis directly into your existing workflow. Because it understands the context of your code, Corgea cuts down on false positives and produces fixes you can actually use. That makes it a good fit for teams that want to improve security without dealing with the noise and inefficiencies common in traditional tools.
Why I Picked Corgea
I picked Corgea because it uses AI-native SAST to catch vulnerabilities that traditional tools often miss, including business logic flaws and more complex code issues. It relies on large language models to understand code context, which reduces false positives by a lot. On top of that, its automated triaging and context-aware detection don’t just flag issues; they provide actionable fixes. For teams focused on security, that makes Corgea a more efficient and practical option.
Corgea Key Features
In addition to its AI-native SAST capabilities, Corgea offers several other features that enhance its utility as a code analysis tool:
- Dependency Scanning: Automatically identifies vulnerabilities in third-party dependencies across 25+ programming languages.
- Infrastructure as Code (IaC) Scanning: Detects security misconfigurations and exposed secrets in infrastructure code before deployment.
- Secret Scanning: Finds hardcoded credentials and sensitive information using pattern matching and AI-powered contextual understanding.
- AI-Powered Remediation: Generates context-aware fixes for vulnerabilities by analyzing code patterns and security controls.
Corgea Integrations
Native integrations are not currently listed by Corgea.
Pros and Cons
Pros:
- Business logic flaw detection
- Automatic secure code fixes
- AI-driven vulnerability detection
Cons:
- AppSec-focused, not full stack
- No runtime protection features
Learn more about Corgea: Best for security testing
- Free plan + free demo available
- From $25/contributor/month
Visit WebsiteCustomer Rating:4.4/5
Snyk dashboard showing a summary of all coding issues. Snyk is a developer security platform that offers real-time scanning and analysis for your code. It also offers git repository integration, which allows you to prioritize issues across your projects.
Why I picked Snyk: I put Snyk on this list because it boasts impressive security features. The first is that its DeepCode AI tool pulls up a list of quick fixes as it identifies issues. You can review and implement these fixes from your integrated development environment (IDE). The second is that Snyk gives each issue a risk score, so you can prioritize issues and make your code more secure.
Snyk Standout Features and Integrations:
Features that make Snyk an excellent code analysis tool include container scanning that checks for vulnerabilities in container images and live code tracking that validates your code as you work. I liked that I could even check my code when I was away from my desk when I tested it.
Integrations are available natively for CI/CD tools like Jenkins, Azure Pipelines, and Bitbucket Pipelines. There are also plugins for IDE tools like Eclipse, PhpStorm, and Visual Studio.
Pros and Cons
Pros:
- User interface is easy to navigate
- Offers continuous integration, continuous delivery (CI/CD) pipeline integration
- Easy to integrate and setup
Cons:
- Free plan limited to 100 tests per month
- Slower scan times
Learn more about Snyk Code: Best for technical debt management
- Enterprise (Pricing Upon Request)
- $21/month
Visit WebsiteCustomer Rating:4.6/5
CodeScene analyzes code health trends, identifies hotspots, and provides actionable insights for improving code quality. CodeScene is a code analysis and visualization tool designed to help development teams identify technical debt, improve code quality, and enhance team productivity.
Why I picked CodeScene: I like its ability to identify hotspots within your codebase. These hotspots are areas that undergo frequent changes and may harbor hidden risks. By pinpointing these critical sections, CodeScene allows your team to focus maintenance efforts where they matter most. The tool also visualizes how individual authors and teams impact your code, from file ownership to output metrics. This insight helps you understand the human factors influencing code quality, facilitating better collaboration and knowledge sharing.
CodeScene Standout Features and Integrations:
Features include automated code reviews that integrate with your pull requests, providing real-time feedback on code quality issues. CodeScene's IDE extension offers instant code quality feedback within your development environment, helping you detect and fix issues early. Additionally, the tool provides code coverage analysis, combining coverage metrics to identify and mitigate high-risk areas in your codebase.
Integrations include Jira, Trello, Azure DevOps, GitHub Issues, GitLab, YouTrack, Slack, and REST API.
Pros and Cons
Pros:
- Offers visualizations that make complex data easy to understand
- Provides actionable insights into code quality and team dynamics
- Helps identify and prioritize technical debt effectively
Cons:
- Most integrations are only available on higher-tier plans
- Configuration can be complex for certain setups
Learn more about CodeScene: Best for advanced analysis
- 14-day free trial + free plan available
- From $24/user/month (billed annually)
Visit WebsiteCustomer Rating:4.4/5
CodeRabbit offers an AI-driven code review interface for analyzing TypeScript code. CodeRabbit is an AI-powered tool designed to enhance the code review process. By automating reviews and offering intelligent insights, it helps developers catch and fix issues more quickly and efficiently.
Why I picked CodeRabbit: I picked CodeRabbit because of its advanced analysis capabilities. The tool uses static analyzers and AI reasoning, which means it doesn't just find bugs but understands the code's structure. This results in a more thorough review with less noise, helping your team focus on what truly matters. Plus, its automated reporting feature generates useful release notes and daily reports, keeping everyone in the loop without extra effort.
CodeRabbit Standout Features and Integrations:
Features include agentic chat, which lets you interact and automate tasks like code generation and feedback resolution, making your workflow more cohesive. The tool also offers simple PR summaries that provide a concise overview of changed files and descriptions, helping you quickly grasp what's been modified. Additionally, CodeRabbit includes automated issue identification, ensuring that discrepancies are highlighted and addressed promptly.
Integrations include GitHub, GitLab, Azure DevOps, Jira, Linear, Mercury, Writer, Abnormal Security, Ashby, Chegg, Sisense, and Groupon.
Pros and Cons
Pros:
- Provides instant feedback on code, identifying hallucinations, logic gaps, vulnerabilities, and missing tests
- Users can review AI-generated code line by line before committing, ensuring thorough checks
- CodeRabbit CLI allows for AI code reviews directly in the terminal
Cons:
- May not fully grasp complex codebases, which might result in inaccuracies, affecting the reliability of feedback
- ome users may find the initial setup and integration process with repositories to be cumbersome
Learn more about CodeRabbit: Best for CI/CD integrations
- 14-day free trial + free plan + free demo available
- From $18/user/month (billed annually)
Visit WebsiteCustomer Rating:4.5/5
Codacy lets you view key code quality metrics from one location. Codacy is a code analysis tool that automates code reviews. It analyzes your source code and highlights issues as you work, allowing you to develop more efficient software. The platform supports over 40 programming languages and frameworks out of the box.
Why I picked Codacy: I selected Codacy because it integrates well with CI workflows—a DevOps practice of merging code changes into a repository. Integrating Codacy with GitHub allowed me to get instant feedback on my code, so I could quickly fix any issues. Another reason I picked Codacy is that it helps standardize code quality by automatically blocking pull requests that don’t meet certain standards.
Codacy Standout Features and Integrations:
Features that I liked about Codacy are the ability to set custom rule sets. Codacy has hundreds of rules available, but you can also upload your own configuration file. This makes it easy to apply specific conditions to a code base and maintain code quality across all teams.
Integrations are available natively with GitHub, GitLab, and Bitbucket. Native integrations are also available for Jira and Slack.
Pros and Cons
Pros:
- Adheres to SOC2 security standards
- Simple to integrate into coding workflows
- Provides helpful code quality reports
Cons:
- Not able to export code patterns
- Doesn’t integrate with Lombok, a Java library that reduces boilerplate code
Learn more about Codacy:

Using PMD to find duplicate code. PMD is an open-source tool that provides static analysis for programming languages like JavaScript, Apex, and XML. It’s available for Windows, macOS, and Linux.
Why I picked PMD: Most code analysis tools require a paid license or offer limited functionality on their free plans. But the reason I picked PMD is because it’s open-source software, which makes it a cost-effective alternative to paid options.
PMD Standout Features and Integrations:
Features that I liked when working with PMD include its built-in checks that allow you to configure rules for different languages to enforce coding standards. The tool also includes Copy/Paste Detector (CPD), which helps you identify duplicate code in your code base.
Integrations are available with popular IDEs like Eclipse, JDeveloper, and Gradle via plugins.
Pros and Cons
Pros:
- Free and open-source
- Able to deal with false positives well
- Can detect duplicate code in various programming languages
Cons:
- Coding feedback isn’t provided in real-time
- Configuring PMDs analysis rules can be complicated
Learn more about PMD:
Andre kodeanalyseverktøy
Det finnes noen andre kodeanalyseverktøy som ikke helt kom med på listen min, men som det er verdt å se nærmere på:
- 11QodanaBest for supporting many programming languages
- 12Synopsys CoverityBest for DevOps teams
- 13Fortify Static Code Analyzer (SCA)Best for enterprise security
- 14Veracode Static AnalysisBest for vulnerability scanning and coverage
- 15Code Climate QualityBest for GitHub users
- 16JSHintBest for managing code complexity
- 17SemgrepBest for accurate static analysis
- 18CAST HighlightBest for performing software assessments at scale
- 19InferBest for mobile developers
- 20PVS-StudioBest for game developers
- 21SourceryBest for real-time feedback in IDEs
- 22SentryBest for AI-driven debugging
- 23SonarQubeBest for code quality maintenance
- 24DerScannerBest for source code and binaries
- 25DeepSourceBest issue and security reporting features
- 26Helix QACBest for ensuring security compliance
- 27CodeSonarBest integration capabilities
- 28FindBugsBest for finding defects in Java code
- 29SemmleBest for securing Internet of Things (IoT) devices
Relaterte anmeldelser av IT-programvare
Hvis du fortsatt ikke har funnet det du leter etter her, kan du se nærmere på disse alternative verktøyene som vi har testet og vurdert.
- Programvare for nettverksovervåking
- Programvare for serverovervåking
- SD-Wan-løsninger
- Verktøy for infrastrukturovervåking
- Pakkeanalysator
- Verktøy for applikasjonsovervåking
How I Evaluate Code Analysis Tools
I split my evaluation into baseline criteria—like multi-language SAST and CI/CD integration—and differentiators like AI-powered fixes and SCA that separate the best tools from the rest.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score into a percentage. Each tool needs to achieve a minimum total score of 75% to be considered for inclusion.
- Static Code Analysis: I evaluate the depth of analysis each tool performs—whether it goes beyond basic linting to offer data-flow and control-flow analysis that catches real bugs before they hit production.
- Multi-Language Support: A polyglot codebase is the norm, so I check how many mainstream languages each tool covers and whether it handles frameworks like React, Spring, or .NET natively.
- Security Vulnerability Detection: I look for clear mapping to OWASP Top 10 and CWE entries with severity ratings, plus remediation guidance that helps developers fix issues rather than just flag them.
- CI/CD & IDE Integration: Each tool should plug into the platforms your team already uses—GitHub, GitLab, Jenkins, Azure DevOps—and ideally surface findings right inside VS Code or IntelliJ.
- Custom Rules & Policies: Teams have their own standards, so I evaluate whether you can create, modify, and share rule sets or quality gates tailored to your org's coding conventions.
- Reporting & Dashboards: I look for dashboards that track trends over time—defect density, remediation rates, hotspot files—so engineering leads and security teams can measure progress, not just find problems.
Once I have a list of tools that meet this criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Software composition analysis is a big one—I check whether a tool scans open-source dependencies for known CVEs alongside your first-party code, since most modern apps rely heavily on third-party libraries. AI-powered fix suggestions also matter, especially when a tool recommends specific remediation steps right inside a pull request. I also evaluate whether a tool catches hardcoded secrets and IaC misconfigurations in Terraform or Kubernetes files, which closes a gap that pure SAST tools often leave open.
Beyond Features
Developer experience is something I weigh heavily—tools with high false-positive rates erode trust fast, and teams end up ignoring findings altogether. I also look at deployment flexibility, since some organizations can't send source code to a SaaS platform and need self-hosted or air-gapped options. Pricing transparency matters too; I check whether a vendor charges per developer, per repo, or per line of code, because the wrong model can make costs unpredictable as your team scales.
Slik velger du kodeanalyseverktøy
Det er lett å gå seg vill i lange funksjonslister og kompliserte prismodeller. For å hjelpe deg med å holde fokus mens du arbeider deg gjennom den unike prosessen din for valg av programvare, har jeg laget en sjekkliste over faktorer du bør ha i bakhodet:
| Faktor | Hva bør vurderes |
|---|---|
| FaktorSkalerbarhet | Hva bør vurderesPass på at verktøyet kan håndtere store kodebaser og flere samtidige brukere uten å bremse analysen. |
| FaktorIntegrasjoner | Hva bør vurderesKontroller at verktøyet kan integreres med CI/CD-pipelinen, versjonskontrollsystemene og prosjektstyringsverktøyene dine. |
| FaktorTilpasningsmuligheter | Hva bør vurderesSe etter alternativer for å endre analyseregler, terskelverdier og rapportformater slik at de passer arbeidsflyten til teamet ditt. |
| FaktorBrukervennlighet | Hva bør vurderesVerktøy for kodevisualisering tilbyr grensesnitt som er enkle å navigere i, krever minimal opplæring og har raskt oppsett. |
| FaktorBudsjett | Hva bør vurderesVurder lisenskostnader, funksjonsnivåer og eventuelle ekstra gebyrer for premiumfunksjoner eller brukerstøtte. |
| FaktorSikkerhetstiltak | Hva bør vurderesKontroller kryptering, sikker håndtering av data og samsvar med sikkerhetsstandarder. |
| FaktorNøyaktighet | Hva bør vurderesVelg et verktøy med lav andel falske positiver og tydelige, handlingsrettede anbefalinger. |
| FaktorRapportering | Hva bør vurderesSe etter detaljerte rapporter med tydelig innsikt, historiske data og trendanalyse. |
Trender innen kodeanalyseverktøy
I undersøkelsen min samlet jeg inn utallige produktoppdateringer, pressemeldinger og lanseringslogger fra ulike leverandører av kodeanalyseverktøy. Her er noen av trendene som er i ferd med å vokse frem, og som jeg følger med på:
- KI-assistert analyse: Verktøy bruker i stadig større grad maskinlæring til å oppdage mønstre og foreslå løsninger, noe som forbedrer nøyaktigheten og reduserer antallet falske positiver.
- Sikkerhet tidligere i utviklingsprosessen: Flere plattformer legger inn sikkerhetskontroller tidligere i utviklingssyklusen for å oppdage sårbarheter før utrulling.
- Skybaserte løsninger: Skybasert kodeanalyse blir stadig mer populært på grunn av skalerbarheten og muligheten til å integreres med eksterne utviklingsmiljøer.
- Ytelsesprofilering: Nyere verktøy gir dypere innsikt i kodekjøring og ressursbruk for å bidra til bedre ytelse.
- Utvidet språkstøtte: Flere verktøy legger til støtte for nisjespråk og nye programmeringsspråk for å møte ulike utviklingsbehov.
Hva er kodeanalyseverktøy?
Kodeanalyseverktøy undersøker kildekode for å finne feil, sikkerhetsmangler og ytelsesproblemer før utrulling. Utviklere, QA-ingeniører og DevOps-fagfolk bruker disse verktøyene til å vedlikeholde renere og mer pålitelig kode og redusere tiden som brukes på manuelle gjennomganger.
Automatisert skanning, statisk og dynamisk analyse samt funksjoner for tilbakemelding i sanntid bidrar til å identifisere kodefeil, håndheve standarder og forbedre den generelle kodekvaliteten. Alt i alt gjør disse verktøyene det enklere for team å skrive bedre kode raskere og opprettholde langsiktig stabilitet på tvers av prosjekter.
Funksjoner i kodeanalyseverktøy
Når du velger kodeanalyseverktøy, bør du se etter følgende viktige funksjoner:
- Statisk kodeanalyse: Denne funksjonen skanner kildekoden uten å kjøre den, slik at du kan identifisere feil, tegn på dårlig kode og sårbarheter tidlig i utviklingsprosessen. Den er perfekt for å oppdage problemer før de i det hele tatt når produksjon.
- Integrasjon med utviklingsmiljøer: Med dette kan du arbeide der du skriver kode. Disse verktøyene integreres ofte sømløst i populære IDE-er, slik at du kan løse problemer og se forslag i sanntid uten å hoppe mellom programmer.
- Automatisert rapportering: Du får detaljerte oversikter over kodekvalitet, kompleksitet eller samsvar, levert direkte til innboksen eller kontrollpanelet ditt. Disse rapportene hjelper deg med å følge fremdriften, identifisere trender og holde teamet oppdatert.
- Kodemålinger og innsikt: Denne funksjonen kvantifiserer blant annet syklomatisk kompleksitet, kodeduplisering og vedlikeholdbarhet. Målingene gir et tydelig bilde av hvor problemer kan være i ferd med å oppstå, slik at du kan rette forbedringene mot de riktige områdene.
- Støtte for flere språk: Hvis du arbeider med mer enn ett programmeringsspråk, er denne funksjonen uvurderlig. Gode verktøy analyserer alt fra Java og Python til JavaScript, slik at du kan dekke hele kodebasen.
- Tilpassbare regelsett: Du kan tilpasse analysereglene slik at de passer teamets kodestandarder eller prosjektkrav. På denne måten er du ikke bundet til standardiserte råd, men får veiledning som passer de spesifikke målene dine.
- Oppdagelse av sikkerhetssårbarheter: Se etter verktøy som markerer kjente sikkerhetstrusler, for eksempel SQL-injeksjon eller bufferoverflyt, slik at du kan håndtere risikoer før de gjør appen sårbar.
- Integrasjon med versjonskontroll: Denne funksjonen lar kodeanalysen kjøre automatisk ved nye innsjekkinger eller forespørsler om å hente inn endringer, slik at bare ren og gjennomgått kode havner i de delte kodearkivene.
- Samarbeidsfunksjoner: Noen verktøy gjør det enkelt å tildele kodeproblemer, legge igjen kommentarer eller følge opp rettelser i teamet. Det handler om å holde arbeidet samordnet og sikre ansvarlighet.
Vanlige KI-funksjoner i kodeanalyseverktøy
Utover funksjonene i standardverktøy for kodeanalyse som er nevnt ovenfor, tar mange av disse løsningene i bruk KI med funksjoner som:
- Intelligent feilforutsigelse: Ved hjelp av historiske data forutsier KI hvor feil sannsynligvis vil oppstå, slik at du proaktivt kan rette tester og gjennomganger mot de mest risikofylte områdene.
- Automatiserte forslag til kodegjennomgang: KI analyserer koden din og gir umiddelbare, kontekstavhengige tilbakemeldinger og forbedringsforslag, slik at du kan forbedre kodebasen med mindre manuelt arbeid.
- Oppdagelse av sikkerhetstrusler: KI-drevne motorer oppdager subtile, nye sikkerhetstrusler ved å gjenkjenne mønstre både i koden din og i oppdaterte kilder med informasjon om trusler.
- Smarte anbefalinger for refaktorering: Få tilpassede forslag til omstrukturering av kode som forbedrer lesbarhet, vedlikeholdbarhet eller ytelse, alt foreslått av KI som lærer av dine unike kodevaner.
- Språkuavhengig analyse: KI utvider analysen til mindre utbredte eller uvanlige språk ved å tilpasse kontrollene sine, noe som reduserer blindsoner tradisjonelle verktøy kan overse.
Fordeler med kodeanalyseverktøy
Implementering av kodeanalyseverktøy gir flere fordeler for teamet og virksomheten din. Her er noen av fordelene du kan se frem til:
- Forbedret kodekvalitet: Identifiserer feil og ineffektivitet tidlig, slik at utviklere kan skrive renere og mer effektiv kode.
- Raskere feilsøking: Reduserer tiden som brukes på å identifisere og løse problemer ved å gi tydelig og handlingsrettet innsikt.
- Forbedret sikkerhet: Oppdager sårbarheter og sikkerhetsfeil tidlig, noe som minimerer risikoen for sikkerhetsbrudd.
- Bedre vedlikehold: Bidrar til å holde koden organisert og konsekvent, slik at fremtidige oppdateringer blir enklere og raskere.
- Økt produktivitet i teamet: Automatiserte kodegjennomgangsverktøy kan utføre repetitive kontroller og gi tilbakemeldinger, slik at utviklere kan konsentrere seg om oppgaver med høy verdi.
- Støtte for samsvar: Sikrer at koden oppfyller bransjestandarder og beste praksis ved å markere mulige brudd.
- Kostnadsbesparelser: Reduserer teknisk gjeld og kostbare rettelser etter lansering ved å forbedre kodekvaliteten fra starten av.
Kostnader og priser for kodeanalyseverktøy
Ved valg av kodeanalyseverktøy er det nødvendig å forstå de ulike prismodellene og abonnementene som er tilgjengelige. Kostnadene varierer basert på funksjoner, teamstørrelse, tillegg og mer. Tabellen nedenfor oppsummerer vanlige abonnementer, gjennomsnittsprisene deres og typiske funksjoner som er inkludert i kodeanalyseløsninger:
Sammenligningstabell for abonnementer for kodeanalyseverktøy
| Abonnementstype | Gjennomsnittspris | Vanlige funksjoner |
|---|---|---|
| AbonnementstypeGratisabonnement | Gjennomsnittspris$0/user/month | Vanlige funksjonerGrunnleggende kodeanalyse, begrenset språkstøtte og ingen avansert rapportering. |
| AbonnementstypePersonlig abonnement | Gjennomsnittspris$10–$30/user/month | Vanlige funksjonerUtvidet språkstøtte, egendefinerte regler og individuelle brukerinnstillinger. |
| AbonnementstypeBedriftsabonnement | Gjennomsnittspris$30–$100/user/month | Vanlige funksjonerTeamsamarbeid, CI/CD-integrasjon, tilbakemeldinger i sanntid og avansert rapportering. |
| AbonnementstypeVirksomhetsabonnement | Gjennomsnittspris$100+/user/month | Vanlige funksjonerSikkerhet på virksomhetsnivå, samsvarskontroller, ubegrenset antall brukere og dedikert kundestøtte. |
Vanlige spørsmål om kodeanalyseverktøy
\u003cspan class=\u0022relative -mx-px my-[-0.2rem] rounded px-px py-[0.2rem]\u0022\u003eHer er noen svar på vanlige spørsmål om kodeanalyseverktøy:\u003c/span\u003e