
Avis sur Veracode : avantages, inconvénients, fonctionnalités et tarifs expliqués
Get my no-nonsense take on Veracode: what it nails, where it misses, and whether its security tools actually deliver peace of mind for dev teams in 2026.

Nous évaluons les outils indépendamment ; les commissions aident à financer nos tests. Consultez notre politique de transparence et notre méthodologie.
Veracode is an application security software for development and security teams that need to scan code, open source dependencies, and running applications for vulnerabilities across the software development lifecycle. I'd reach for it when you want a unified platform that combines SAST, DAST, SCA, and container scanning under one policy engine, rather than stitching together point tools.
Compared to Checkmarx, which leans heavily on on-prem deployments and deeper tuning work, Veracode gives you a SaaS-first setup that gets your team scanning and triaging findings faster without standing up scan infrastructure yourself.
Veracode Evaluation Summary
3.8/5
- Pricing upon request
- Free demo available
Pourquoi faire confiance à nos recommandations de logiciels
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Notre équipe teste et évalue des logiciels depuis 2012. En tant que leaders technologiques nous-mêmes, nous savons à quel point il est difficile — et important — de choisir le bon logiciel.
Pour ce guide, nous avons évalué les outils grâce à des tests pratiques et une recherche indépendante, en notant les outils selon nos critères de sélection.
Nos avis reflètent notre jugement éditorial humain, et non un argumentaire de vente.
Réviseurs experts:
- Paulo Gardini MiguelDirecteur technique
 Tim FisherVP de l'IA
 Gabriel RosasTech Lead et architecte logiciel
 Christhian GruhnTech Lead et architecte plateforme

Veracode Overview
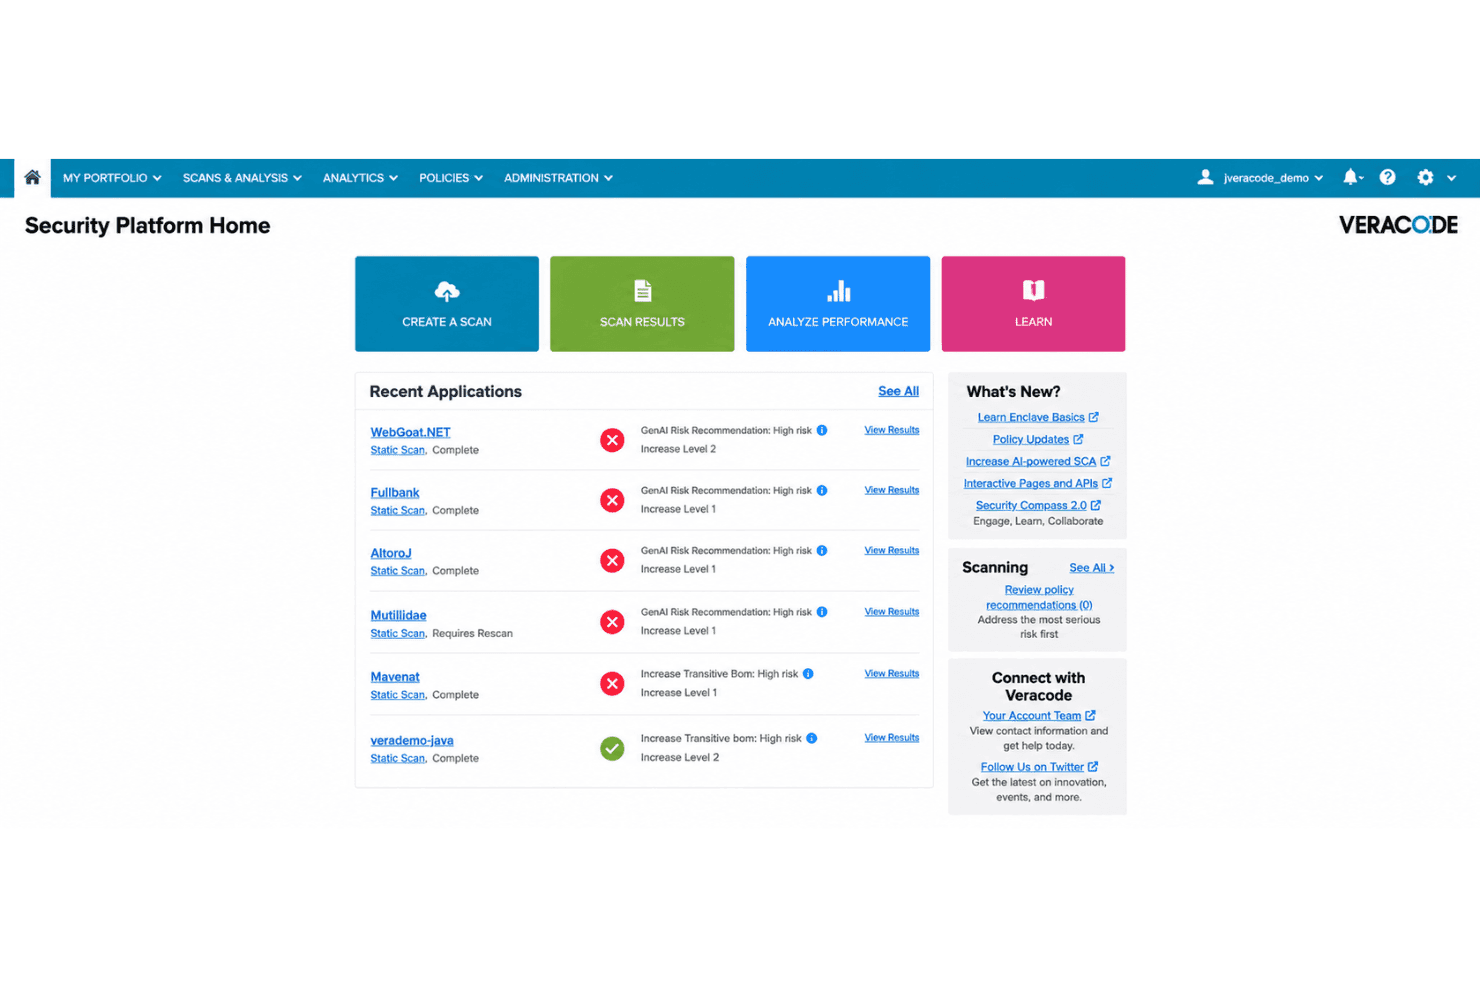
I think Veracode stands out for its SaaS-first approach, letting teams start scanning without heavy setup or infrastructure. Its all-in-one dashboard ties together static, dynamic, software composition, and container analysis, which saves time compared to juggling separate tools. I find the interface approachable, with policy management and triage features that suit larger DevSecOps and development teams. Pricing can be high for smaller teams, and limits on customization occasionally frustrate power users. Still, if you want fast onboarding, strong coverage across modern application stacks, and dependable support, Veracode should be at the top of your list for enterprise and mid-size environments.
Pros
- SaaS delivery skips on-prem setup and maintenance costs
- Unified dashboard covers SAST, DAST, SCA, and container scanning
- Policy management centralizes governance for large application portfolios
Cons
- Scan times can be lengthy for large codebases
- API coverage lags behind leading competitors
- False positives require extra manual triage effort
Is Veracode Right For Your Needs?
Who Would be a Good Fit for Veracode?
Veracode works best for mid to large businesses in regulated or security-driven sectors with complex development environments and clear compliance needs. Application security teams, DevOps-driven product companies, and organizations running critical cloud-native infrastructure will find real value because Veracode’s SaaS-based scanning, wide integration support, and built-in eLearning can handle compliance demands, varied tech stacks, and skills gaps. Regulated firms and those scaling app security across multiple business units get consistent policies, ASPM visibility, and audit trails. If your team needs less operational overhead and more out-of-the-box guidance, Veracode lines up well.
- Enterprise Software VendorsVeracode’s scalable scanning and API integrations help large software companies enforce security policies across many products and codebases.
- Finance and BankingBuilt-in compliance reporting, policy templates, and audit support make Veracode a solid option for banks needing to meet regulatory standards.
- SaaS ProvidersSaaS vendors who release frequently can run automated SAST, DAST, and container scans without on-premise overhead, speeding up release cycles.
- Healthcare IT TeamsHealthcare teams will find preconfigured compliance tools, transparent reporting, and eLearning useful for meeting HIPAA and similar requirements.
- DevOps OrganizationsDevOps teams cut down context-switching and manual steps thanks to Veracode’s integrations with GitHub and Jira.
- Global EnterprisesLarge organizations managing multiple app portfolios benefit from centralized dashboards, customizable policies, and multi-team onboarding.
Who Would be a Bad Fit for Veracode?
Veracode isn’t a great choice for small teams, legacy workloads, or companies with minimal regulatory or security demands. Early-stage startups, non-technical departments, and businesses working with closed-source or highly niche platforms won’t get full value—mainly because of pricing, the all-in focus on modern SDLC integration, and the way onboarding and learning programs assume some existing security maturity. Simple applications and teams who rarely update their codebase may find the feature set excessive for their needs and budget.
- Small Development TeamsEntry pricing and broad feature sets can be overkill for startups with only a single app and minimal formal security requirements.
- Legacy System OperatorsOrganizations focused on legacy platforms may struggle as Veracode’s integrations and policy workflows are built for modern frameworks and languages.
- Marketing AgenciesAgencies creating static sites or simple web apps won’t benefit from multi-layer scanning, policy controls, or deep SAST features.
- Academic InstitutionsUniversities and schools working on non-commercial apps or prototypes won’t use advanced scanning, compliance, or team management features.
- On-Premise-Only EnvironmentsCompanies who cannot use SaaS solutions due to data residency or regulatory constraints will hit a wall, since Veracode is delivered via the cloud.
- Freelance DevelopersSolo developers will find built-in eLearning and policy automation unnecessary, and the user minimums will put Veracode out of budget.
Notre méthodologie d'évaluation
Comment nous testons et notons les outils
Nous avons passé des années à développer, affiner et améliorer notre système de test et de notation des logiciels. Cette grille d’évaluation est conçue pour saisir les subtilités de la sélection des logiciels et ce qui rend un outil efficace, en se concentrant sur les aspects critiques du processus de décision.
Vous trouverez ci-dessous le détail de notre processus de test et de notation sur sept critères. Cela nous permet de fournir une évaluation impartiale du logiciel basée sur les fonctionnalités principales, les caractéristiques distinctives, la facilité d’utilisation, l’intégration, l’accompagnement lors de la prise en main, le support client, les avis utilisateurs et le rapport qualité-prix.
Fonctionnalité principale (25% de la note finale)
Le point de départ de notre évaluation est toujours la fonctionnalité principale de l’outil. Possède-t-il les fonctions de base auxquelles un utilisateur s’attend ? Certaines de ces fonctionnalités principales sont-elles limitées à des forfaits plus chers ? Nous attendons d’un outil qu’il soit au moins à la hauteur des capacités de base de ses concurrents.
Fonctionnalités remarquables (25% de la note finale)
Ensuite, nous évaluons les fonctionnalités exceptionnelles qui dépassent la fonctionnalité de base habituellement trouvée dans ce type d’outil. Un score élevé reflète des fonctionnalités spécialisées ou uniques rendant le produit plus rapide, plus efficace ou apportant une valeur ajoutée à l’utilisateur.
Nous évaluons aussi la facilité d’intégration avec d’autres outils courants dans la pile technologique pour élargir les fonctionnalités et l’utilité du logiciel. Les outils dotés de nombreuses intégrations natives, de connexions tierces et d’un accès API facilitant des intégrations personnalisées obtiennent les meilleurs scores.
Facilité d’utilisation (10% de la note finale)
Nous considérons la rapidité et la simplicité d’exécution des tâches principales avec l’outil. Les logiciels les mieux notés sont bien conçus, intuitifs, proposent des applications mobiles, offrent des modèles et rendent des tâches relativement complexes très simples.
Accompagnement lors de la prise en main (10% de la note finale)
Nous savons que l’adoption rapide d’une nouvelle plateforme au sein d’une équipe est cruciale. Nous évaluons donc la facilité avec laquelle un nouvel utilisateur peut apprendre et utiliser un outil avec un minimum de formation. Les meilleures solutions permettent une mise en route rapide, sans nécessité de support.
Support client (10% de la note finale)
Nous analysons la facilité et la rapidité avec lesquelles il est possible d’obtenir de l’aide par téléphone, chat en direct ou base de connaissances. Les outils et entreprises offrant une assistance en temps réel obtiennent les meilleurs scores, tandis que les chatbots sont moins bien notés.
Avis utilisateurs (10% de la note finale)
Au-delà de nos propres tests et évaluations, nous tenons compte du net promoter score des utilisateurs actuels et passés. Nous regardons la probabilité qu’ils choisiraient à nouveau l’outil pour ses fonctionnalités principales. Un logiciel bien noté reflète un net promoter score élevé.
Rapport qualité-prix (10% de la note finale)
Enfin, en tenant compte de tous les autres critères, nous examinons le prix moyen des forfaits d’entrée de gamme par rapport aux fonctionnalités principales et à la valeur des autres critères. Un logiciel offrant plus, pour moins cher, obtiendra un meilleur score.
Core Features
Static Application Security Testing (SAST)
Static analysis scans source code and compiled code for security flaws during development without running the application. This helps your team catch vulnerabilities and code quality issues early before code moves to production.
Dynamic Application Security Testing (DAST)
Dynamic analysis tests live, running applications for exploitable vulnerabilities from an attacker’s perspective. You can assess web apps for common issues like SQL injection or cross-site scripting in staging or production environments.
Software Composition Analysis (SCA)
Analyze open source components to identify outdated libraries, known vulnerabilities, and license compliance issues. This helps you manage risk from third-party dependencies automatically across your entire application portfolio.
Container Security Scanning
Scan container images for vulnerabilities, configuration risks, and policy violations before deployment. Teams get actionable feedback to secure containers integrated directly into CI/CD pipelines.
Centralized Policy Management
Define and enforce security policies across multiple projects and teams through one dashboard. You can set risk thresholds, remediation targets, and track your security posture for every application in your portfolio.
Triage and Remediation Guidance
Prioritize findings by risk and get specific remediation advice for developers right in the platform. This speeds up response times and helps your team focus on the most urgent vulnerabilities.
Ease of Use
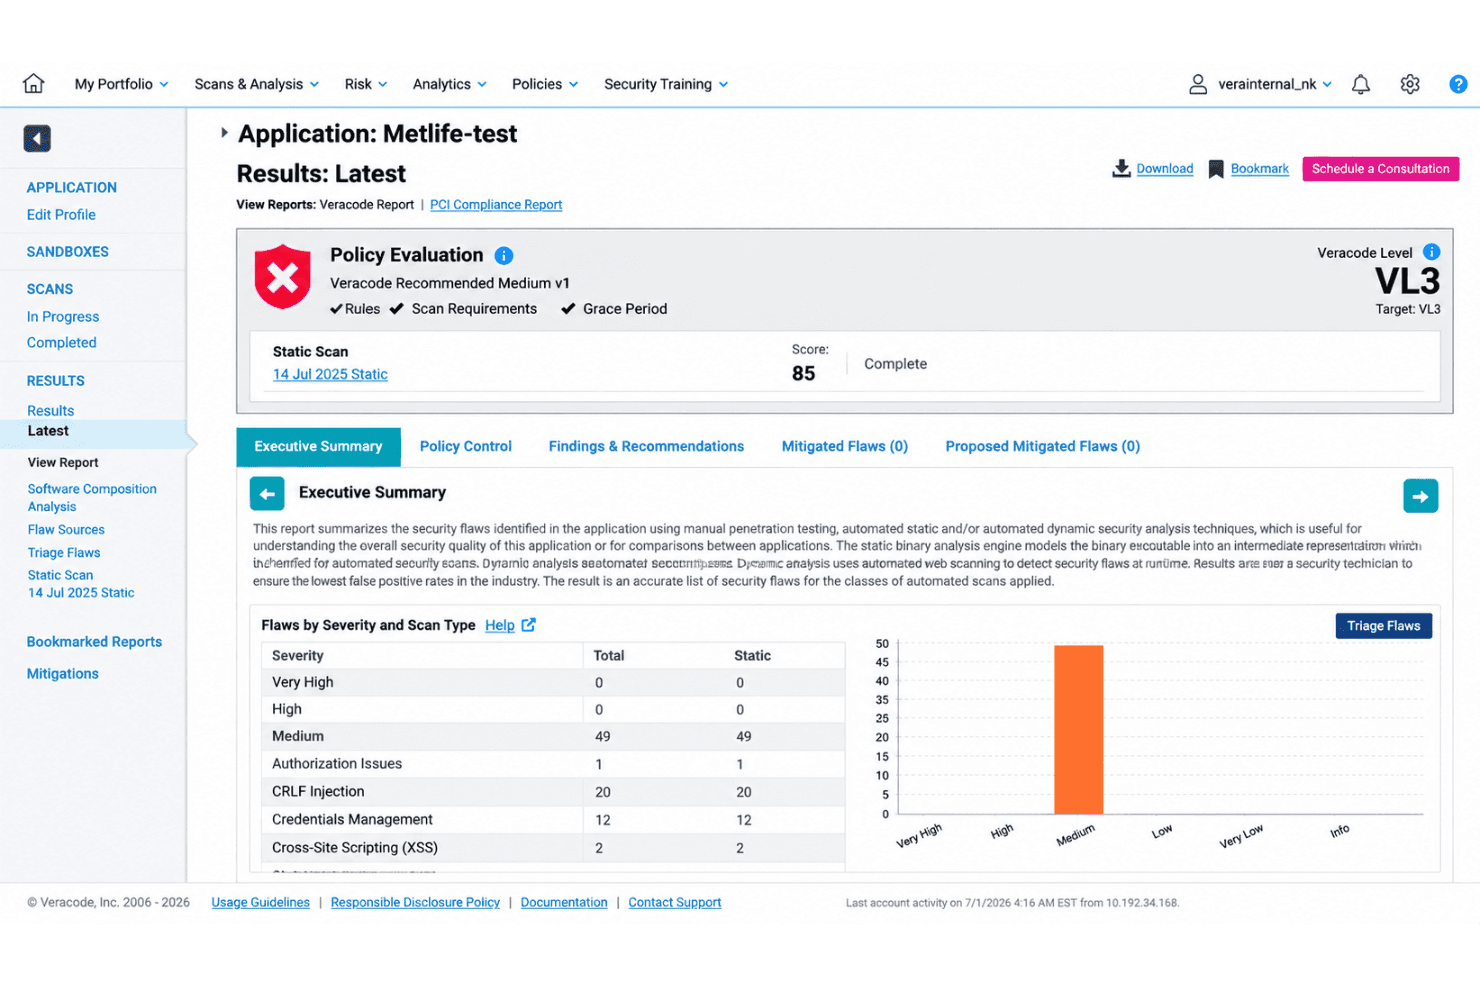
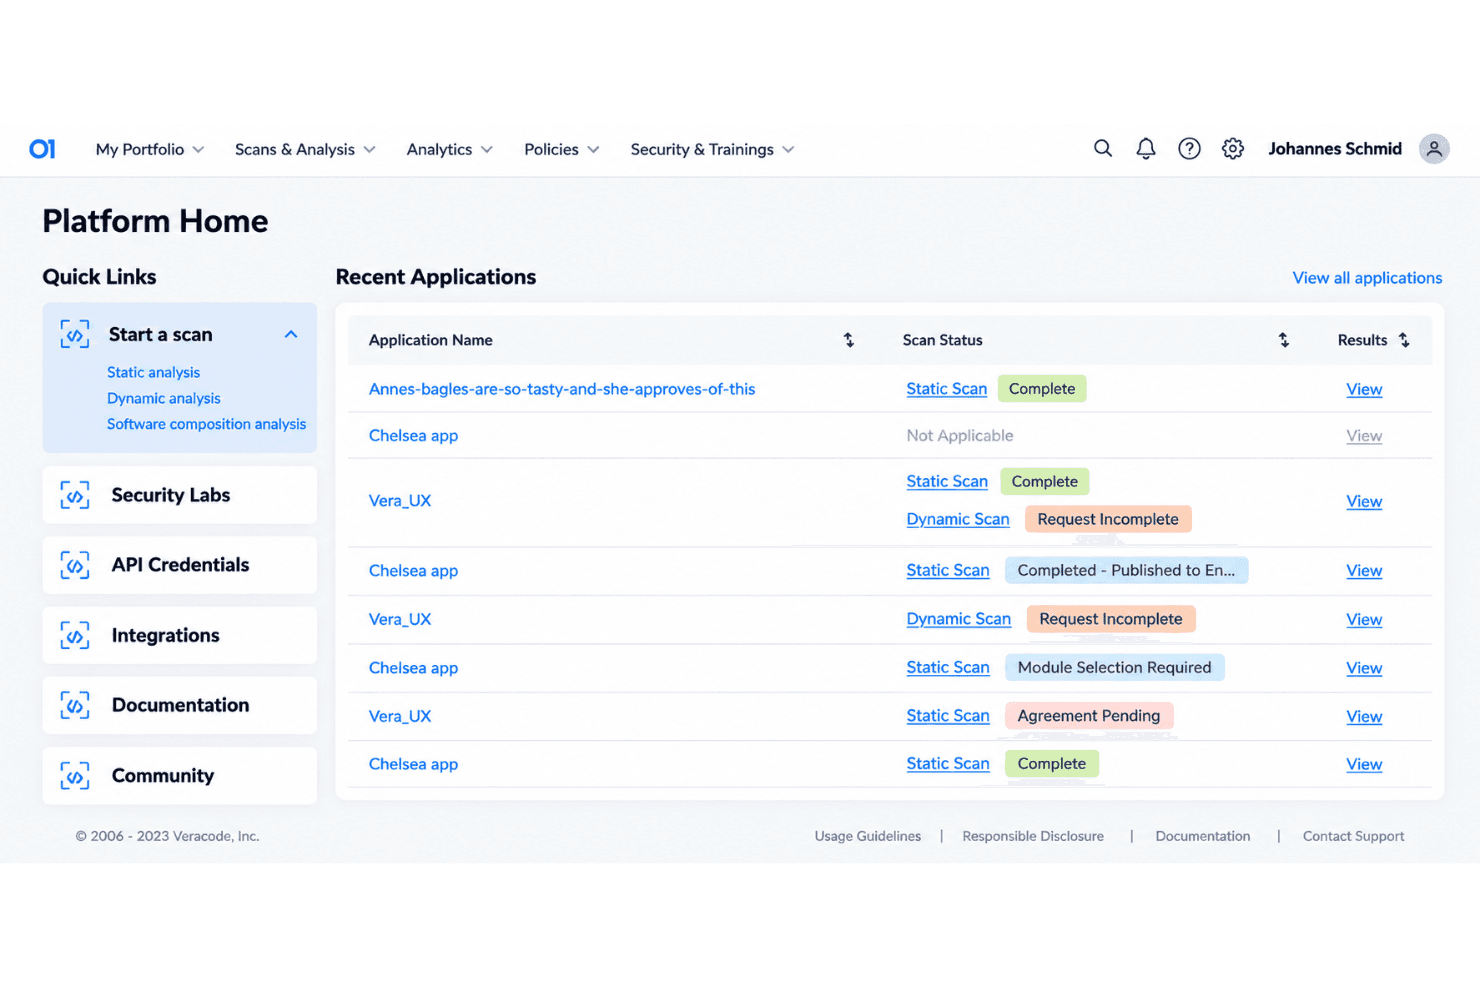
Veracode is easy to onboard for most teams, with a SaaS delivery model that skips manual setup or complex infrastructure. The dashboard brings SAST, DAST, SCA, and container scanning into one view, making it simple to manage policies and findings. Some users mention that large codebase scans take time and that false positives add extra triage, but the platform’s organized interface and clear workflows keep day-to-day usage straightforward.
Integrations
Veracode integrates with Jira, GitHub, GitLab, Azure DevOps, AWS, Bitbucket, ServiceNow, and Snyk, among others.
Veracode also provides both XML and REST API and supports integration with third-party tools for expanded connectivity.
Veracode Specs
- A/B Testing: Yes
- API: Yes
- Automated Testing: Yes
- Browser Compatibility Testing: Yes
- Bug Tracking: Yes
- Calendar Management: Yes
- CI/CD Integration: Yes
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- Data Visualization: Yes
- Developer Tools: Yes
- External Integrations: Yes
- History/Version Control: Yes
- Manual Testing: Yes
- Multi-User: Yes
- Notifications: Yes
- Performance Testing: Yes
- Regression Testing: Yes
- Scheduling: Yes
- Status Notifications: Yes
- Third-Party Plugins/Add-Ons: Yes


