

The best vulnerability management tools help teams identify exposures early, reduce security risks, and maintain safer, more compliant systems across their infrastructure. When weaknesses go undetected, when patching cycles rely on manual tasks, or when alerts generate more noise than useful insight, threats can grow quickly and create unnecessary gaps in security operations.
The right vulnerability management platform gives security and IT teams clear visibility, automated scanning, and accurate prioritization so they can understand which issues require immediate action and resolve them before they impact the business. As a Chief Technology Officer with over 20 years of experience testing and implementing security tools in real production environments, I’ve evaluated the top solutions based on detection accuracy, automation quality, and ease of use during ongoing security work.
Each review covers features, pros and cons, and ideal use cases to help your team choose the best vulnerability management tool for reliable, efficient risk reduction.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Vulnerability Management Tools Comparison Table
This comparison table summarizes pricing details for my top Vulnerability Management Tools selections.
Sorted by: Default
| Tool | Starting Price | Website | |
|---|---|---|---|
Best for real-time external threat monitoring | Not rated | Pricing upon request | Website |
Best for comprehensive code-to-cloud security | 4.3 out of 5 | $350/month Free plan available | Book Demo |
Best for third-party vendor risk assessments | 4.5 out of 5 | Pricing upon request Free demo available | Website |
Best for endpoint vulnerability & patch management | 4.5 out of 5 | Pricing upon request 30-day free trial + free demo available | Website |
Best for secure code analysis | 4.4 out of 5 | Pricing upon request Free trial available | Website |
Best for proactive network security monitoring | 4.7 out of 5 | Pricing upon request 14-day free trial + demo available | Website |
Best for UEM-native endpoint risk visibility | 4.7 out of 5 | $3/device/month 14-day free trial + free demo available | Website |
Best for automated patch management | Not rated | Pricing upon request Free trial + free demo available | Website |
Best for continuous vulnerability monitoring | 4.8 out of 5 | $119/month Free trial available | Website |
Best for comprehensive vulnerability scanning | 4.5 out of 5 | $69/month Free demo available | Website |


Best Vulnerability Management Tool Reviews
Below are my detailed summaries of the best Vulnerability Management Tools that made it onto my shortlist. My reviews offer a detailed look at the key features, pros & cons, integrations, and ideal use cases of each tool to help you find the best one for you.


NordStellar dashboard showing real-time data breach insights, including leaked data, risk levels, and key security metrics such as breaches, infections, and stolen credentials. NordStellar is a platform designed to help you manage vulnerabilities with a focus on external threat intelligence and security. It provides tools to identify and mitigate potential security threats in real-time, ensuring your organization stays protected from cyber threats.
Why I Picked NordStellar: I chose NordStellar for its real-time alerts, advanced threat detection, and automated attack surface management that keep you ahead of cyber risks. With instant data breach and dark web monitoring, it alerts your team to compromised data or emerging threats, enabling swift action. By centralizing intelligence from over 36,000 sources and prioritizing risks, NordStellar helps both executives and security teams maintain proactive, comprehensive protection.
Standout features & integrations:
Features include brand protection, which helps in detecting and preventing unauthorized use of your brand online. The platform also offers real-time monitoring, allowing you to keep a constant watch on security threats. Lastly, its integration capabilities with SIEM and SOAR platforms mean you can easily incorporate NordStellar into your existing security infrastructure, enhancing your overall security posture.
Integrations include Splunk, SIEM platforms, SOAR platforms, Email, Slack, Webhooks, and API.
Pros and Cons
Pros:
- Integrates with SIEM and SOAR
- Automated asset discovery and mapping
- Real-time alerts for cyber threats
Cons:
- Limited mobile application support
- Pricing not publicly disclosed
Learn more about NordStellar: Best for comprehensive code-to-cloud security
- Free plan available
- From $350/month
Visit WebsiteCustomer Rating:4.3/5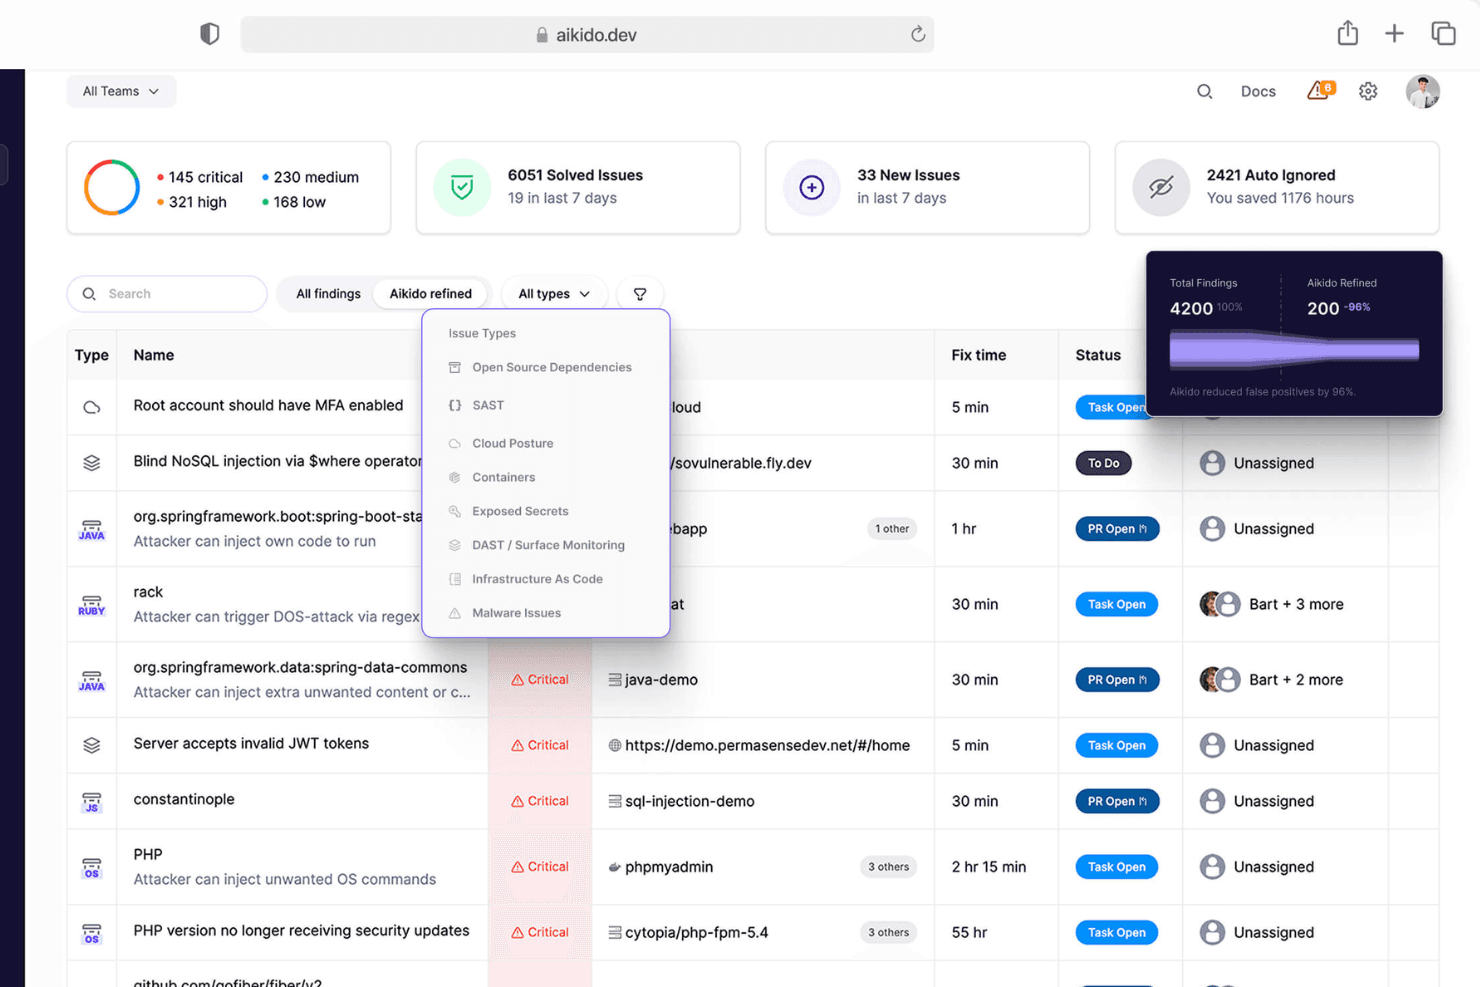
Aikido Security provides a unified dashboard to triage and filter issues by type, severity, and scan source. Aikido Security is an all-in-one platform that helps you identify and fix vulnerabilities in your code and cloud environments. It offers a range of tools to detect security risks, from static code analysis to cloud posture management.
Why I Picked Aikido Security: Aikido's static code analysis (SAST) scans your source code to spot vulnerabilities like SQL injection and cross-site scripting before they become issues. This proactive approach lets your team address potential threats early, enhancing your application's security. Additionally, Aikido's secret detection feature checks your code for exposed API keys, passwords, and other sensitive information, preventing accidental leaks that could be exploited.
Standout features & integrations:
Features include its cloud posture management (CSPM) capabilities that detect risks in your cloud infrastructure across major providers, helping you maintain a secure cloud environment. Aikido also offers infrastructure as code (IaC) scanning, open-source dependency scanning, container image scanning, surface monitoring, and malware detection in dependencies.
Integrations include Amazon Web Services (AWS), Google Cloud, Microsoft Azure Cloud, Drata, Vanta, AWS Elastic Container Registry, Docker Hub, Jira, Asana, and GitHub.
Pros and Cons
Pros:
- Scalable for growing teams
- Offers actionable insights
- Has a comprehensive dashboard and customizable reports
Cons:
- Custom SAST rules must be enabled by Aikido
- Unfixed CVEs excluded from ephemeral container scans by default
Learn more about Aikido Security: Best for third-party vendor risk assessments
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.5/5
Prevalent provides a centralized place to monitor vendor risks, including cyber vulnerabilities. Prevalent is a third-party risk management platform that helps organizations assess and monitor the risks associated with their vendors and suppliers. By automating the collection and analysis of vendor data, Prevalent enables you to focus on reducing risk and ensuring compliance throughout your vendor ecosystem.
Why I Picked Prevalent: As a vulnerability management tool, Prevalent offers cyber intelligence to help you identify and address potential security issues within your vendor network. It monitors over 550,000 companies for cyber incidents by tracking more than 1,500 criminal forums, numerous dark web pages, and various threat feeds. This extensive monitoring allows you to stay informed about vulnerabilities and take proactive measures to protect your organization.
Standout features & integrations:
Features include automated onboarding and offboarding processes, simplifying the management of vendor relationships. The platform also includes a vendor dashboard that centralizes security, performance, and compliance reporting, making it easier for your team to monitor and address risks. Furthermore, Prevalent provides built-in remediation guidance.
Integrations include Active Directory, BitSight, ServiceNow, SecZetta, and Source Defense.
Pros and Cons
Pros:
- Strong security protocols to protect data
- Users can tailor reports according to specific needs
- Extensive functionalities for managing vendor risk
Cons:
- Challenges in migrating data can complicate the initial setup
- The platform is complex and comes with a learning curve
Learn more about Prevalent: Best for endpoint vulnerability & patch management
- 30-day free trial + free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.5/5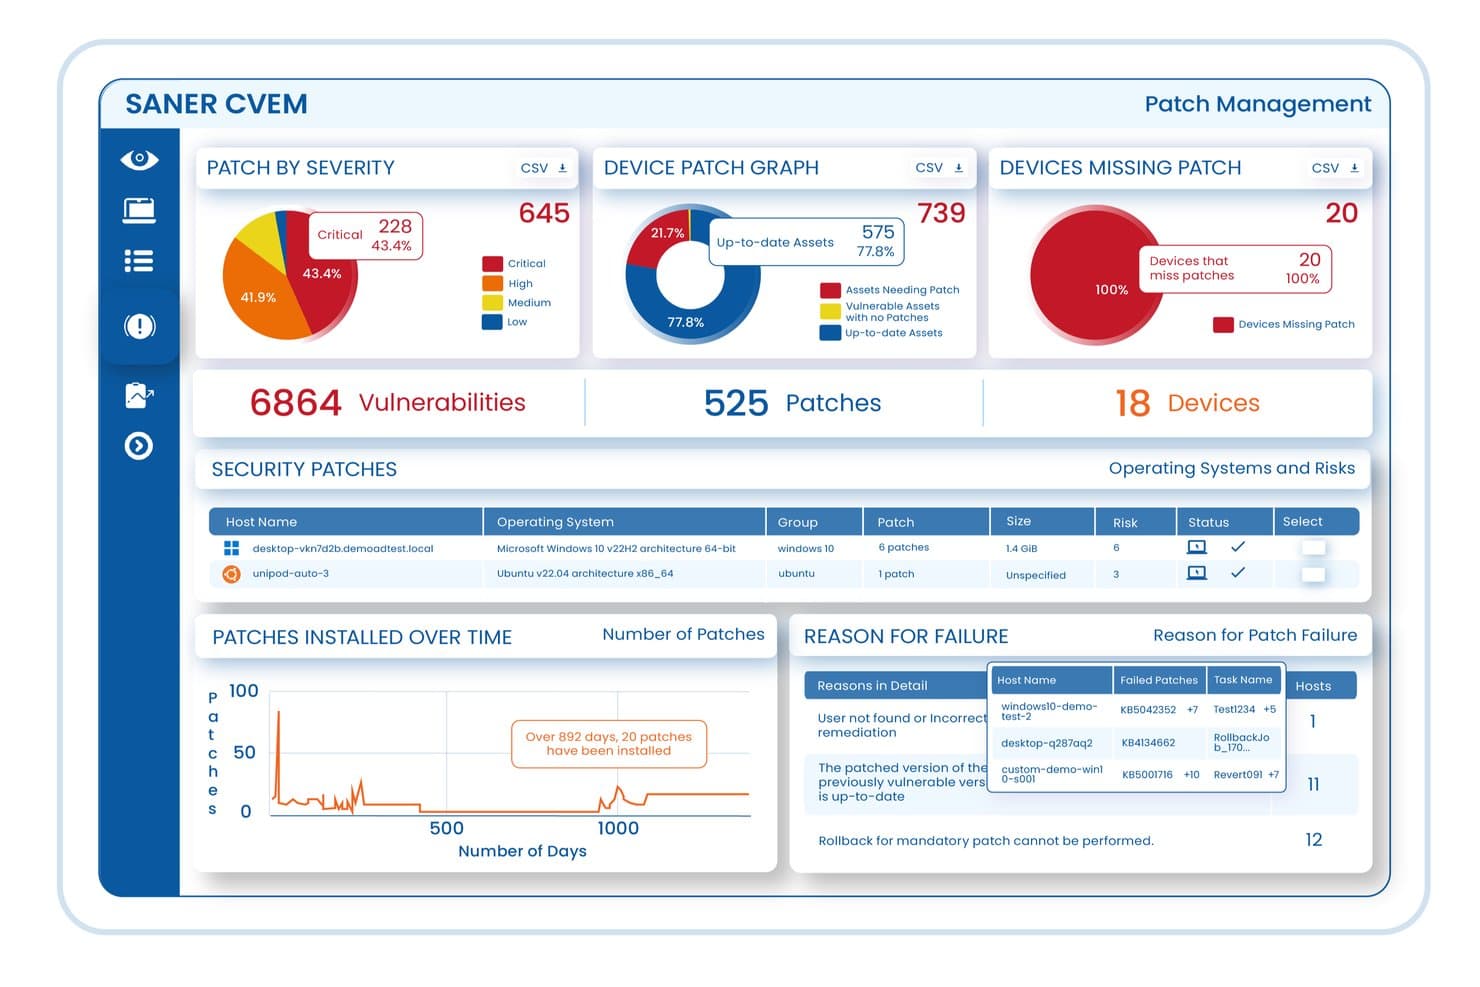
An interactive overview of the SecPod Saner Continuous Vulnerability and Exposure Management (CVEM) Platform, highlighting end-to-end vulnerability tracking, automated patch management, and risk prioritization across enterprise endpoints. SecPod (Saner Platform) is a continuous vulnerability and exposure management platform that combines endpoint scanning, risk-based prioritization, patch remediation, and compliance enforcement across enterprise IT environments in a single console.
Who Is SecPod (Saner Platform) Best For?
SecPod is a good fit for IT security teams in mid-to-large enterprises that need a single platform to manage vulnerability detection, patching, and compliance across distributed endpoint environments.
Why I Picked SecPod (Saner Platform)
I've included SecPod (Saner Platform) in my top picks because its automated endpoint detection goes well beyond basic CVE scanning. The platform runs continuous checks across Windows, macOS, Linux, and IBM AIX endpoints using a library of 160,000+ security checks, covering missing patches, misconfigurations, and exposed assets without requiring manual intervention. I also like that its AI-powered posture anomaly detection monitors 100+ device parameters using ML models, flagging behavioral deviations that signature-based scanners typically miss.
SecPod (Saner Platform) Key Features
- SSVC-based risk prioritization: Ranks vulnerabilities using EPSS exploit likelihood scores, CISA KEV status, and asset criticality to focus remediation on the highest-risk exposures first.
- Closed-loop patch remediation: Tracks vulnerabilities from initial detection through patching to verified resolution, all within the same platform.
- Compliance benchmark enforcement: Continuously audits endpoint configurations against CIS, NIST, HIPAA, PCI DSS, and STIG benchmarks.
- MITRE ATT&CK mapping: Tags vulnerability findings to MITRE ATT&CK techniques and CWE classifications for structured threat context.
SecPod (Saner Platform) Integrations
SecPod's Saner platform integrates with ServiceNow, ELK, IBM QRadar, Wazuh, and Jira, and also supports a native Freshservice integration. Its API-first architecture enables integration with SIEM, SOAR, ITSM, and DevOps pipelines, and a REST API is available for custom integrations.
Pros and Cons
Pros:
- Includes remediation, not just detection
- Lightweight agent with minimal resource consumption
- 200,000+ SCAP vulnerability checks built in
Cons:
- Initial agent setup requires significant configuration
- Reporting and dashboard customization options limited
Learn more about SecPod (Saner Platform): Best for secure code analysis
- Free trial available
- Pricing upon request
Visit WebsiteCustomer Rating:4.4/5
SonarQube shows project vulnerabilities, bugs, and quality gate status SonarQube helps development and security teams find vulnerabilities, code quality issues, secrets, and infrastructure-as-code misconfigurations before they reach production. It stands out for combining SAST, SCA, and AI code assurance across 40+ languages, making it a strong fit for teams managing application security within their DevSecOps workflows.
Who Is SonarQube Best For?
SonarQube is a strong choice for development teams and security engineers in organizations that need to manage code vulnerabilities across multiple languages and environments.
Why I Picked SonarQube
I picked SonarQube because it helps your team find and manage vulnerabilities directly in the codebase through static application security testing, secrets detection, and dependency analysis. Its secure code analysis fits well for development teams that need to catch issues during pull requests and CI/CD checks before they reach production. I also like that its quality gates can block risky code from moving forward until security and quality standards are met. For teams using AI-generated code, SonarQube can also review and suggest fixes for issues before that code is merged.
SonarQube Key Features
Some other features in SonarQube support secure development and vulnerability management workflows:
- Multi-language scanning: Scans codebases across 30+ programming languages to identify vulnerabilities, bugs, and security issues.
- Infrastructure-as-code analysis: Reviews Terraform, Kubernetes, and other IaC files for misconfigurations and security risks.
- Custom rule creation: Lets your team build and enforce security or compliance rules based on internal standards.
- Pull request decoration: Displays security findings in pull requests so teams can address issues before merging.
SonarQube Integrations
Integrations include GitHub, GitLab, Bitbucket, Azure DevOps, Atlassian Jira, and Slack.
Pros and Cons
Pros:
- Pull request feedback helps developers fix vulnerabilities earlier
- Quality gates help block risky code before production
- Scans code, secrets, dependencies, and IaC in one workflow
Cons:
- Advanced SCA capabilities require SonarQube Advanced Security add-on
- Requires self-hosting for advanced on-prem features
Learn more about SonarQube: Best for proactive network security monitoring
- 14-day free trial + demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.7/5
Auvik allows users to manage their networks with full visibility from anywhere. Auvik is a network management platform that helps you monitor, secure, and manage your network infrastructure through continuous monitoring, device tracking, and threat detection.
Why I Picked Auvik: I picked Auvik for its proactive network monitoring features that support vulnerability management through real-time visibility into device activity, potential threats, and compliance risks. Auvik’s automated network mapping and traffic analysis help identify unauthorized devices and unusual behaviors, providing the foundational insights needed to spot vulnerabilities early. The platform also includes features like configuration backups and automated alerts, enabling faster response times to potential risks. While not a full vulnerability management suite, Auvik’s security focus and integrations strengthen an organization’s overall security posture.
Standout features & integrations:
Features include real-time network monitoring, automated network mapping, traffic analysis, configuration management, compliance reporting, and alerts for potential threats. Auvik also provides encrypted communications and proactive monitoring tools that help MSPs and IT teams identify network vulnerabilities before they escalate.
Integrations include Microsoft Teams, Slack, ServiceNow, Cisco, Fortinet, Palo Alto Networks, Datto, Duo, IT Glue, Salesforce, Zendesk, and Zoom.
Pros and Cons
Pros:
- Detailed visual graphical representation of networks
- Single dashboard monitoring
- Quick and accurate alerting system
Cons:
- Customizing the platform can be time consuming
- Could use more integrations
Learn more about Auvik: Best for UEM-native endpoint risk visibility
- 14-day free trial + free demo available
- From $3/device/month (billed annually)
Visit WebsiteCustomer Rating:4.7/5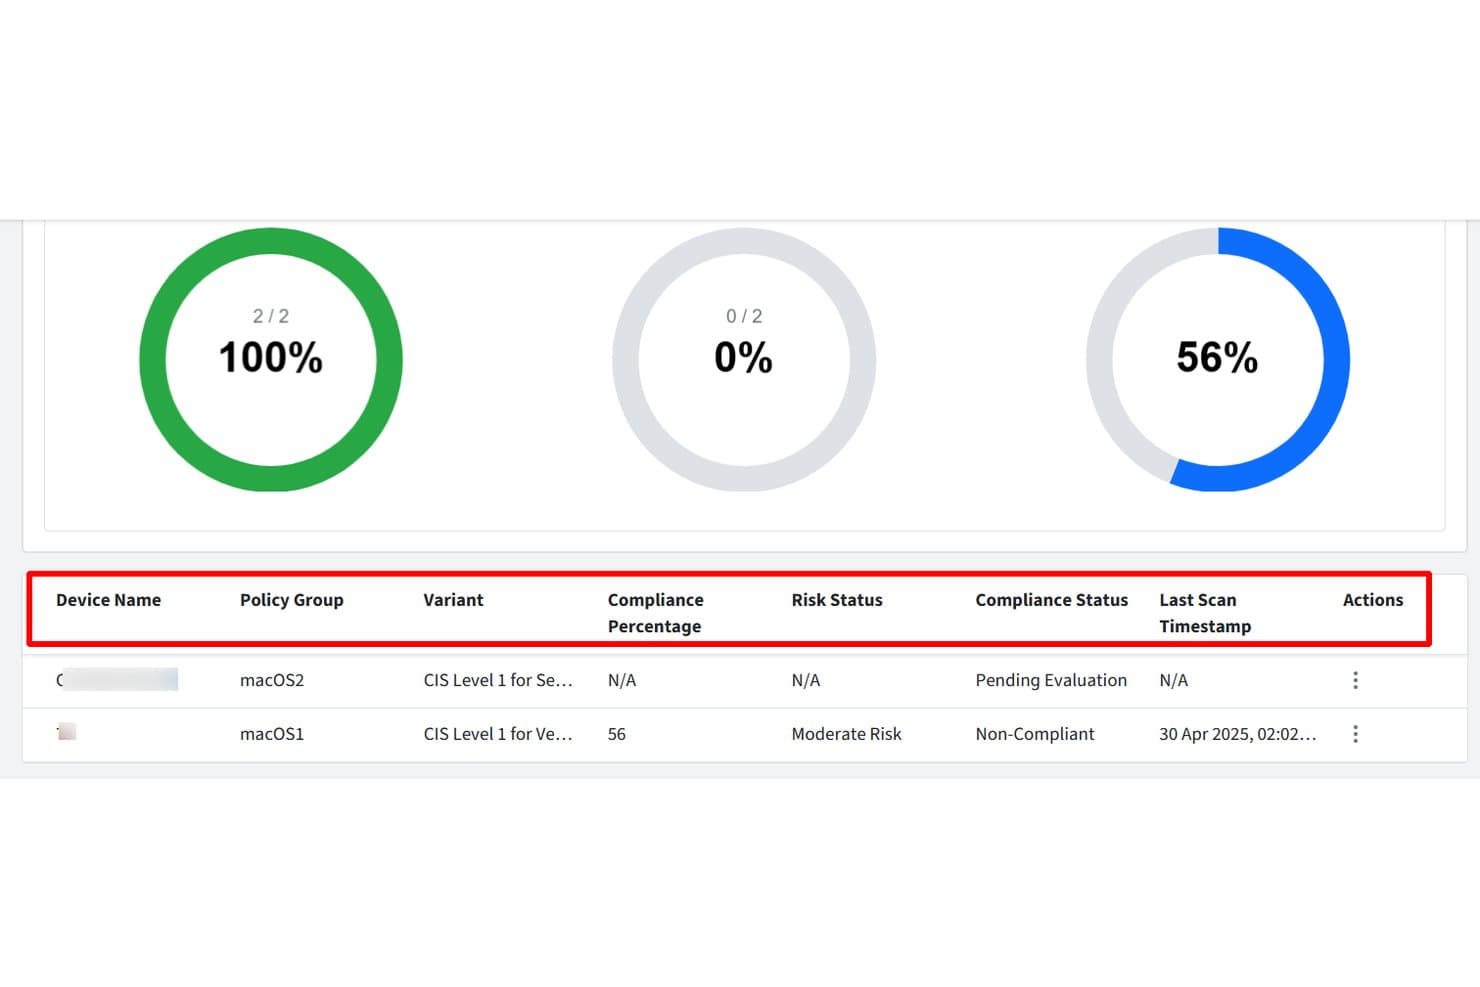
Scalefusion tracks device compliance status and risk levels at a glance. Veltar is an endpoint security product within the Scalefusion UEM platform that delivers continuous vulnerability scanning, risk-based prioritization, and asset inventory across managed Windows and macOS devices.
Who Is Scalefusion Best For?
Scalefusion is a strong fit for IT teams already managing Windows and macOS fleets through a UEM platform who want vulnerability visibility without deploying a separate scanning agent.
Why I Picked Scalefusion
Scalefusion's Veltar earns its spot on my shortlist because it closes the gap between UEM device management and vulnerability visibility without requiring a separate scanning agent. I particularly like how the risk score pulls together CVSS, EPSS, KEV status, and vulnerability age into a single composite indicator, so I can see at a glance which Windows or macOS endpoints carry the most exposure. The configurable SLA thresholds for Critical and High severity CVEs mean my team gets automatic breach flags before anything slips through unnoticed.
Scalefusion Key Features
- Continuous OS and application vulnerability scanning: Veltar identifies vulnerabilities across enrolled Windows and macOS endpoints by pulling CVE data hourly from NVD and MSRC.
- Configurable SLA thresholds: Administrators can set day-based SLA limits for Critical and High severity CVEs, with automatic breach flags surfaced in the Overview dashboard.
- CSV export for vulnerability and asset data: The Applications, Operating Systems, Devices, and Vulnerabilities views all support filtered CSV exports for sharing inventory and CVE data externally.
- UEM-integrated patch routing: When a fix is available, Veltar's "Patch Now" action routes administrators directly to the relevant Windows or macOS patching workflow inside the Scalefusion UEM console.
Scalefusion Integrations
Scalefusion integrates with Check Point Harmony and supports account controls for Google and Microsoft cloud apps. It also provides a Developer API and webhooks for custom integrations.
Pros and Cons
Pros:
- Centralized device views support practical endpoint triage
- Combines CVSS, EPSS, KEV, and vulnerability age
- Uses existing enrollment, no separate scanning agent
Cons:
- No ticketing, ownership, or fix-verification workflow
- Scans only managed Windows and macOS endpoints
Learn more about Scalefusion: Best for automated patch management
- Free trial + free demo available
- Pricing upon request

Heimdal offers a comprehensive dashboard for IT asset management. Heimdal offers a comprehensive solution for businesses seeking efficient vulnerability management software. Its platform is particularly appealing to industries that prioritize cybersecurity, such as finance, healthcare, and government sectors. By focusing on automated patch management and asset oversight, Heimdal addresses the critical need for timely vulnerability remediation, ensuring your systems remain secure against potential threats.
Why I Picked Heimdal
I picked Heimdal for its exceptional focus on automated patch management, a feature that directly addresses the need for timely vulnerability remediation. This ensures that your systems are consistently up-to-date, reducing the risk of exploitation. Additionally, Heimdal's asset management capabilities allow you to maintain a comprehensive view of your software inventory, aiding in the identification and prioritization of vulnerabilities. Its seamless integration with third-party tools further enhances its utility in diverse IT environments.
Heimdal Key Features
In addition to its core strengths, Heimdal offers several other valuable features:
- Threat Hunting: Enables proactive identification and mitigation of potential threats within your network.
- Unified Endpoint Management: Provides centralized control over all endpoints to enhance security and compliance.
- Compliance Reporting: Generates detailed reports to ensure adherence to industry standards and regulations.
- User-Friendly Interface: Offers an intuitive dashboard for easy navigation and policy management.
Heimdal Integrations
Native integrations are not currently listed by Heimdal; however, the platform supports API-based custom integrations.
Pros and Cons
Pros:
- Detailed asset and license visibility
- Strong vulnerability and threat detection
- Automates patching across endpoints
Cons:
- Interface requires onboarding time
- No native integrations available
Learn more about Heimdal: Best for continuous vulnerability monitoring
- Free trial available
- From $119/month
Visit WebsiteCustomer Rating:4.8/5
The attack surface view in Intruder helps identify and manage potential vulnerabilities in your network. Intruder is a cloud-based vulnerability management tool that helps you identify and address security weaknesses in your digital infrastructure.
Why I Picked Intruder: Intruder's continuous vulnerability management ensures your systems are regularly scanned for new threats. This feature automatically initiates scans when changes are detected, helping you stay ahead of potential security risks. Additionally, Intruder's attack surface management discovers unknown assets like subdomains and untracked APIs, providing a comprehensive view of your organization's exposure. It also offers exposure management, which combines multiple scanning engines to identify over a thousand attack surface issues that other scanners might miss.
Standout features & integrations:
Features include prioritization that leverages the latest threat intelligence, such as CISA's Known Exploited Vulnerabilities list and machine learning-driven exploitation predictions. It also offers private bug bounty access, allowing your team to collaborate with elite hackers to uncover vulnerabilities that automated scanners might overlook.
Integrations include AWS, Azure, Google Cloud, Drata, Jira, Azure DevOps, GitHub, GitLab, ServiceNow, Cloudflare, Microsoft Sentinel, and Okta.
Pros and Cons
Pros:
- Compliance reporting capabilities
- Automated scanning and monitoring
- Comprehensive vulnerability detection
Cons:
- Attack surface feature limited to premium plan
- Occasional false positives
Learn more about Intruder: Best for comprehensive vulnerability scanning
- Free demo available
- From $69/month
Visit WebsiteCustomer Rating:4.5/5
The main dashboard of Astra Pentest provides an overview of the security status and detected vulnerabilities. Astra Pentest is a comprehensive security tool designed to perform thorough penetration testing across various platforms, including web applications, cloud environments, mobile apps, APIs, networks, and blockchain systems. It helps users identify vulnerabilities using an intelligent scanner and a user-friendly dashboard, ensuring robust web application security.
Why I Picked Astra Pentest: One of its key features is the vulnerability scanner, which performs over 8000 tests, including checks for known CVEs, OWASP Top 10, and SANS 25. This scanner is designed to cover every possible loophole, ensuring thorough security assessments. Additionally, the scanner can analyze pages behind login screens using a browser extension, which simplifies the process of securing every part of an application.
Standout features & integrations:
Some key features of Astra Pentest include pentests for web apps, cloud security, mobile apps, API, network security, and blockchain. It also offers reporting, compliance, and publically verifiable security certificates.
Integrations include GitLab, GitHub, Bitbucket, Slack, Jira, Microsoft Azure, Jenkins, CircleCI.
Pros and Cons
Pros:
- User-friendly interface
- Comprehensive security checks for compliance
- Centralized dashboard for managing vulnerabilities
Cons:
- Limited customization options
- False positives are possible with the tool
Learn more about Astra Pentest:
Other Vulnerability Management Tools
Here are some additional vulnerability management tools options that didn’t make it onto my shortlist, but are still worth checking out:
- 11New RelicBest for zero-configuration security insights
- 12IBM Security QRadar EDRBest for comprehensive threat intelligence
- 13Cisco Vulnerability ManagementBest for extensive device and protocol coverage
- 14Microsoft Defender Vulnerability ManagementBest for integration with Microsoft ecosystem
- 15Tenable Vulnerability ManagementBest for active directory and infrastructure security
- 16Qualys VMDRBest for comprehensive IT asset management
- 17InsightVM (Nexpose)Best for real-time end-to-end visibility
- 18Wiz Vulnerability ManagementBest for multi-cloud environment security
- 19CyCognitoBest for attack surface management
- 20Arctic WolfBest for managed detection and response services
- 21Frontline Vulnerability ManagerBest for cloud and network security integration
- 22AdluminBest for financial sector-focused security
- 23NucleusBest for multi-framework compliance management
- 24Oligo SecurityBest for runtime open-source library protection
- 25CYRISMABest for intuitive user interface and automated patching
- 26NowSecureBest for mobile app security
- 27ResolverGood for integrating risk management across business operations
How I Evaluate Vulnerability Management Tools
I split evaluations into two layers: baseline requirements a SecOps team can't work without, and the differentiators—like exploit intelligence and attack path analysis—that set the best tools apart.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score into a percentage. Each tool needs to achieve a minimum total score of 65% to be considered for inclusion.
- Asset Discovery & Inventory: I check whether the tool can automatically map endpoints, cloud workloads, containers, and network devices—especially across hybrid environments where shadow IT tends to hide.
- Vulnerability Scanning: Scan coverage matters, so I evaluate support for authenticated and unauthenticated scans across operating systems, web apps, databases, and cloud configurations.
- Risk-Based Prioritization: Rather than just listing CVSS scores, the tool should layer in exploit availability, threat intelligence, and asset criticality to surface what actually needs attention first.
- Remediation Workflow & Tracking: I look for ticket assignment, SLA tracking, and two-way sync with tools like Jira or ServiceNow so findings don't sit in a dashboard while teams lose track of owners.
- Reporting & Compliance: Audit season reveals which tools pull their weight here—I evaluate built-in templates for PCI-DSS, HIPAA, ISO 27001, and NIST, plus the ability to customize reports for different stakeholders.
- Continuous Monitoring & Integrations: A single scan is a snapshot. I look for scheduled and real-time scanning paired with native connectors for SIEMs, EDR platforms, and CI/CD pipelines.
Once I have a list of tools that meet this criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Attack path analysis is a major differentiator—I look for tools that map how chained vulnerabilities and identity gaps could give an attacker lateral movement toward crown-jewel assets. EPSS and exploit intelligence also matter because a tool that incorporates real-world weaponization data helps teams move past theoretical risk scores. For DevSecOps teams, container and IaC scanning shifts detection into the build pipeline, catching misconfigurations in Terraform or Kubernetes manifests before they reach production.
Beyond Features
Licensing models vary widely in this space—some vendors charge per IP, others per asset or per user—so I evaluate whether the pricing structure aligns with how your environment will grow. Deployment flexibility also matters, especially for teams managing air-gapped networks or strict data residency requirements where a self-hosted option is essential. I also consider ecosystem fit, checking for native connectors to your existing SIEM, SOAR, and ITSM stack so findings flow into established workflows without custom scripting.
How to Choose a Vulnerability Management Tool
It’s easy to get bogged down in long feature lists and complex pricing structures. To help you stay focused as you work through your unique software selection process, here’s a checklist of factors to keep in mind:
| Factor | What to Consider |
| Scalability | Ensure the tool can grow with your business. Consider if it can handle increased data loads and more users without compromising performance. |
| Integrations | Check if the tool integrates with your existing software, such as SIEM systems, ticketing tools, and cloud services, to streamline workflows. |
| Customizability | Look for customization options that let you tailor dashboards, reports, and alerts to fit your team’s specific needs and preferences. |
| Ease of Use | Choose a tool with an intuitive interface and minimal learning curve to ensure quick adoption by your team. |
| Budget | Evaluate the cost against the features offered. Consider flexible pricing plans that fit your financial constraints and provide value for money. |
| Security Safeguards | Assess the tool's ability to protect sensitive data and comply with industry regulations, ensuring robust security measures are in place. |
| Vendor Support | Consider the vendor's reputation for customer support, including availability, response time, and the resources they provide for troubleshooting. |
| Reporting Features | Look for comprehensive reporting capabilities that provide insights into vulnerabilities and compliance, helping you make informed security decisions. |
Trends in Vulnerability Management Tool
In my research, I sourced countless product updates, press releases, and release logs from different Vulnerability Management Tools vendors. Here are some of the emerging trends I’m keeping an eye on:
- AI-Powered Threat Detection: Vendors are using artificial intelligence to enhance threat detection capabilities. AI can identify patterns and anomalies faster than traditional methods, helping teams respond to threats more quickly. Some tools are incorporating machine learning to predict potential vulnerabilities.
- Cloud-Native Security: As more businesses move to the cloud, tools are evolving to provide better cloud-native security features. This trend is crucial for companies relying heavily on cloud infrastructure, offering deeper insights into cloud-specific vulnerabilities.
- Zero Trust Security Models: More tools are adopting zero trust models, which require verification for every user and device. This approach enhances security by assuming threats could be internal or external. Vendors like Cisco are integrating zero trust principles into their platforms.
- Enhanced Reporting Capabilities: Detailed and customizable reporting is becoming more important. Users need insights into vulnerabilities and compliance status. Tools are offering more advanced reporting features to meet these demands, allowing for better risk management.
- User Behavior Analytics: Some vendors are incorporating user behavior analytics to monitor and identify unusual activities. This trend helps detect insider threats and compromised accounts, adding another layer of security for businesses.
What Are Vulnerability Management Tools?
Vulnerability management tools find, track, and help fix security weaknesses across an organization’s assets. They’re used by security teams, IT administrators, and operations staff who need to reduce risk and keep systems up to date without relying on manual checks.
Automated scanning, risk scoring, and reporting features help with spotting issues earlier, choosing what to fix first, and keeping teams informed. Overall, these tools help organizations maintain safer and more reliable systems with less manual effort.
Features of Vulnerability Management Tools
When selecting Vulnerability Management Tools, keep an eye out for the following key features:
- AI-powered threat detection: Uses artificial intelligence to quickly identify patterns and anomalies, helping teams respond to threats faster.
- Cloud-native security: Provides specialized security features for cloud environments, offering insights into cloud-specific vulnerabilities.
- Zero trust security models: Requires verification for every user and device, enhancing security by assuming all access could be a threat.
- Enhanced reporting capabilities: Offers customizable and detailed reports that provide insights into vulnerabilities and compliance status.
- User behavior analytics: Monitors and identifies unusual user activities to detect insider threats and compromised accounts.
- Risk prioritization: Helps teams focus on the most critical vulnerabilities by assessing and ranking potential threats.
- Automated patch management: Streamlines the process of applying security patches, reducing manual workload and minimizing vulnerabilities.
- Continuous monitoring: Provides ongoing assessment of the network to detect new vulnerabilities as they arise.
- Compliance reporting: Ensures that security measures meet industry standards and regulations, simplifying the compliance process.
- Customizable dashboards: Allows users to tailor their view of data and metrics to fit specific needs and preferences.
Benefits of Vulnerability Management Tools
Implementing Vulnerability Management Tools provides several benefits for your team and your business. Here are a few you can look forward to:
- Improved security posture: By identifying and managing vulnerabilities, these tools help protect your systems from potential threats and reduce security risks.
- Efficient risk management: Risk prioritization features allow your team to focus on the most critical vulnerabilities, ensuring resources are used effectively.
- Enhanced compliance: Compliance reporting helps you meet industry standards and regulations, simplifying audits and reducing compliance-related stress.
- Time savings: Automated patch management and continuous monitoring reduce manual tasks, freeing up your team to focus on other important activities.
- Informed decision-making: Detailed reporting and analytics provide insights that support better security decisions and strategies.
- Increased visibility: Features like cloud-native security and user behavior analytics give you a clearer view of your network and potential threats.
- Proactive threat detection: AI-powered threat detection enables faster identification and response to vulnerabilities, keeping your systems secure.
Costs and Pricing of Vulnerability Management Tools
Selecting Vulnerability Management Tools requires an understanding of the various pricing models and plans available. Costs vary based on features, team size, add-ons, and more. The table below summarizes common plans, their average prices, and typical features included in Vulnerability Management Tools solutions:
Plan Comparison Table for Vulnerability Management Tools
| Plan Type | Average Price | Common Features |
| Free Plan | $0 | Basic vulnerability scanning, limited reporting, and community support. |
| Personal Plan | $5-$25/user/month | Standard scanning capabilities, risk prioritization, and basic compliance checks. |
| Business Plan | $30-$60/ user/month | Advanced analytics, automated patch management, and customizable dashboards. |
| Enterprise Plan | $70-$150/ user/month | Comprehensive reporting, AI-powered threat detection, and dedicated support. |
Vulnerability Management Tools (FAQs)
Here are some answers to common questions about Vulnerability Management Tools:
How do vulnerability management tools work?
Vulnerability management tools assess your network using IP scanners, network and port scanners, and more. They prioritize issues to ensure the most critical weaknesses are fixed first and suggest practical remediation steps. This process helps secure your systems by addressing vulnerabilities promptly.
What is common with most vulnerability assessment tools?
A key feature of vulnerability assessment tools is their ability to scan your systems. They run automated scans across your network, analyzing every device, application, and system for potential vulnerabilities. This automation ensures comprehensive coverage and efficient vulnerability detection.
What are the typical pricing models for vulnerability management tools?
A key feature of vulnerability assessment tools is their ability to scan your systems. They run automated scans across your network, analyzing every device, application, and system for potential vulnerabilities. This automation ensures comprehensive coverage and efficient vulnerability detection.
What is the disadvantage of an automated vulnerability tool scan?
Automated vulnerability tool scans have some drawbacks. They might not detect newly discovered vulnerabilities or complex ones that are hard to automate. This limitation means you might need manual checks to ensure comprehensive security coverage.
How often should vulnerability scans be performed?
The frequency of vulnerability scans depends on your organization’s needs and risk tolerance. Generally, it’s best to perform scans regularly, such as weekly or monthly, to ensure continuous protection against emerging threats. Regular scans help maintain a strong security posture.
Can vulnerability management tools integrate with existing security systems?
Yes, many vulnerability management tools can integrate with existing security systems. This integration allows for seamless data sharing and improved threat management. By working with your current infrastructure, these tools enhance your overall security strategy.