

ThreatLocker vs. CrowdStrike: Confronto e Recensioni degli Esperti per il 2026
Il blocco zero trust di ThreatLocker contro l'EDR potenziato dall'IA di CrowdStrike: quale si adatta meglio al tuo stack di sicurezza? Copro prezzi, funzionalità vincenti e casi d’uso ideali.

Recensiamo gli strumenti in modo indipendente e le commissioni ci aiutano a finanziare i nostri test. Consulta la nostra politica sulla trasparenza, la nostra metodologia, oppure suggerisci uno strumento.
Le violazioni degli endpoint costeranno milioni alle aziende quest'anno, ma molte continuano a utilizzare strumenti che rilevano gli attacchi troppo tardi. Potresti essere in uno dei tanti team di sicurezza che stanno valutando tra l’approccio zero-trust di ThreatLocker e il rilevamento AI di CrowdStrike, e magari ti trovi in difficoltà nel decidere quale sia la soluzione migliore per prevenire violazioni senza compromettere la produttività o sforare il budget.
In questo articolo ti guiderò attraverso tutto ciò che devi sapere, dai prezzi alle funzionalità principali fino ai casi d’uso reali. Alla fine, saprai con certezza quale software di cybersecurity per endpoint risponde alle tue esigenze.
ThreatLocker


4.8/5
- 30-day free trial + free demo available
- Pricing upon request
CrowdStrike Falcon
4.6/5
- Free demo available
- Pricing upon request
Perché fidarsi dei nostri consigli sui software
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Il nostro team testa e recensisce software dal 2012. In quanto leader tecnologici noi stessi, sappiamo quanto sia difficile — e importante — scegliere il software giusto.
Per questa guida, abbiamo valutato gli strumenti attraverso test praticie ricerche indipendenti, assegnando un punteggio agli strumenti in base ai nostri criteri di selezione.
Le nostre recensioni riflettono il nostro giudizio editoriale umano, non un discorso di vendita.
Revisori esperti:
- Paulo Gardini MiguelDirettore tecnico
 Tim FisherVP dell'IA
 Gabriel RosasTech Lead e architetto software
 Christhian GruhnTech Lead e architetto della piattaforma

| ThreatLocker | CrowdStrike Falcon | |
|---|---|---|
| Free Trial | 30-day free trial + free demo available | Free demo available |
| Pricing | Pricing upon request | Pricing upon request |
ThreatLocker vs. CrowdStrike: Prezzi e Costi Nascosti
ThreatLocker utilizza una tariffazione personalizzata, basata su preventivo e adattata al tuo ambiente, considerando il numero di endpoint e i controlli richiesti. I costi vengono definiti fin dall’inizio in funzione delle tue necessità, puntando sulla prevedibilità invece che su fasce di prezzo fisse.
CrowdStrike propone abbonamenti trasparenti a dispositivo, suddivisi per livelli; le fasce superiori sbloccano funzionalità avanzate. Il prezzo dei pacchetti è chiaro, ma moduli opzionali, servizi premium e MDR vengono quotati separatamente dal reparto commerciale.
ThreatLocker si concentra sulla prevenzione deterministica, guidata da policy, con un modello zero-trust che nega tutto di default. L’allowlisting applicativo, il Ringfencing, il controllo delle elevazioni e le restrizioni su storage/rete garantiscono che possano essere eseguiti o spostarsi lateralmente solo software espressamente approvati, riducendo i falsi positivi e supportando esigenze di uptime e compliance rigorose.
CrowdStrike Falcon adotta un approccio basato sull’analisi, utilizzando AI e intelligence globale sulle minacce per monitorare i comportamenti in tempo reale e bloccare gli attacchi mentre si sviluppano. Combina antimalware di nuova generazione, rilevamento comportamentale, sicurezza d’identità e risposta automatizzata, offrendo ai team di sicurezza ampia visibilità, indagine rapida e contenimento scalabile senza dover pre-approvare ogni applicazione.
| ThreatLocker | CrowdStrike Falcon | |
|---|---|---|
| API | Yes | No |
| Data Export | No | Yes |
| Data Import | No | Yes |
| External Integrations | Yes | No |
| Multi-User | Yes | Yes |
| Notifications | Yes | No |
| Strumento | ThreatLocker | CrowdStrike |
| ConnectWise | ✅ | ✅ |
| N-able | ✅ | ✅ |
| Datto RMM | ✅ | ❌ |
| Kaseya | ✅ | ❌ |
| NinjaOne | ❌ | ✅ |
| Splunk | ✅ | ✅ |
| Elastic | ✅ | ✅ |
| ServiceNow | ✅ | ✅ |
| Okta | ✅ | ❌ |
| Zscaler | ❌ | ✅ |
| Palo Alto Networks | ❌ | ✅ |
| ThreatAware | ✅ | ❌ |
ThreatLocker concentra le sue integrazioni su flussi di lavoro orientati all’MSP, RMM, PSA e le principali piattaforme cloud, consentendo di distribuire agent, sincronizzare i clienti e automatizzare i ticket direttamente dagli strumenti già usati quotidianamente dal tuo team IT. Il marketplace di CrowdStrike, invece, è concepito per stack di sicurezza di grandi dimensioni, con connettori profondi e pronti all’uso verso SIEM, SOAR, fornitori cloud, piattaforme di identità e firewall, semplificando l’integrazione della telemetria di Falcon in ecosistemi SOC già esistenti.
| Fattore | ThreatLocker | CrowdStrike |
| Modello di Sicurezza Principale | Zero trust, allowlisting predefinito come negato e contenimento delle applicazioni focalizzato sulla prevenzione dell'esecuzione. | NGAV guidato dall'IA, EDR/XDR con telemetria continua, intelligence sulle minacce, e rilevamento e risposta automatizzati. |
| Conformità e Certificazioni | Pone l'accento sul supporto a framework come NIST, CIS, HIPAA, PCI tramite controlli di policy; le certificazioni formali sono limitate rispetto ai vendor più grandi. | Ampio profilo di conformità con SOC 2, ISO 27001, PCI, mappature HIPAA/HiTRUST e attestazioni di settore. |
| Gestione e Residenza dei Dati | Servizio gestito in cloud con opzioni di hosting regionale e controllo granulare su ciò che può essere eseguito, ma meno enfasi sulle sfumature della residenza dei dati nel marketing. | Architettura cloud globale con opzioni di residenza dei dati documentate e rigorosa segregazione dei dati nel suo trust center. |
| Controllo di Accesso e Identità | Accesso admin basato su ruoli all'interno della console; integra SSO/IdP, ma la protezione dell'identità non è una funzione principale. | Forte SSO/RBAC oltre a una protezione dedicata contro le minacce all'identità e integrazione con i principali IdP. |
| Affidabilità e Storico degli Incidenti | Implementazione rapida con supporto 24/7 “Cyber Hero” e attenzione all'uptime, ma meno SLA pubblici rispetto ai fornitori hyperscale. | SaaS distribuito su larga scala e a livello globale con documentata alta disponibilità, anche se il blackout del 2024 ha evidenziato la dipendenza da un singolo EDR vendor. |
Entrambi gli strumenti prendono la sicurezza molto seriamente ma pongono enfasi su filosofie diverse: ThreatLocker punta su una prevenzione rigorosa tramite policy Zero Trust e controllo granulare, che può ridurre notevolmente la superficie di attacco se le policy sono ben mantenute. CrowdStrike invece ottimizza per visibilità, analisi e conformità ampia, combinando forti certificazioni e affidabilità globale con funzionalità avanzate di rilevamento e risposta adatte a SOC maturi e aziende regolamentate.
| Fattore | ThreatLocker | CrowdStrike |
| Configurazione e Distribuzione Iniziale | Il deployment dell'agente è semplice, ma la creazione e l'ottimizzazione delle policy di allowlisting possono richiedere tempo e attenta pianificazione. | Il sensore leggero si distribuisce velocemente su larga scala tramite script e strumenti RMM/MDM, con minimo impatto sugli endpoint. |
| Curva di Apprendimento | Più ripida all'inizio poiché il deny-by-default richiede comprensione di app e workflow, anche se la modalità "learning" aiuta ad automatizzare la creazione delle policy. | Console e workflow risultano più familiari ai team SOC; gli utenti hanno accesso a funzionalità potenti, ma ci sono molte opzioni da padroneggiare. |
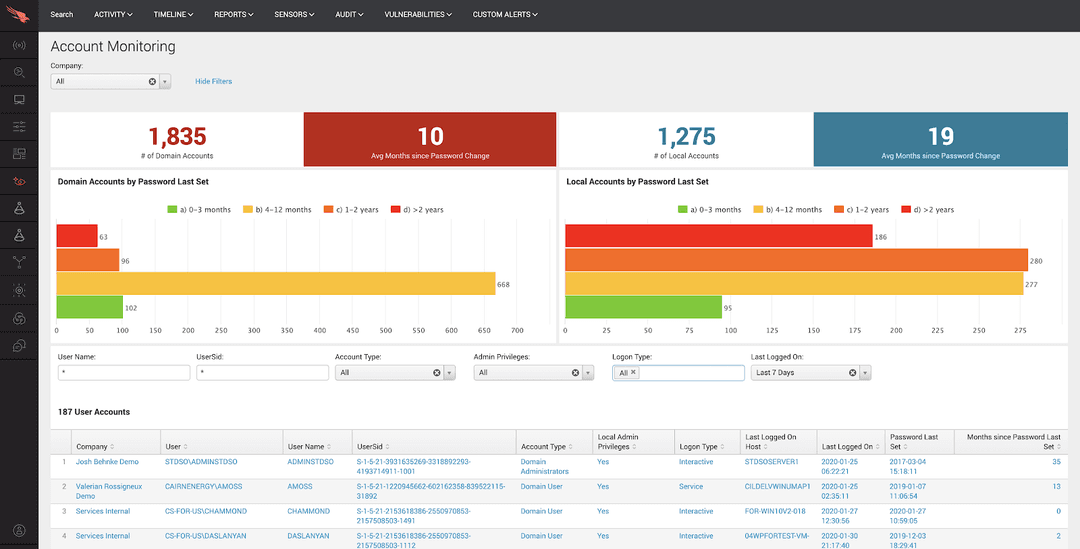
| Gestione Quotidiana | L'interfaccia centrata sulle policy rende semplice visualizzare e regolare cosa è consentito o bloccato, ma cambi frequenti nelle app possono implicare un aggiustamento continuo. | Dashboard centrale con ricerca avanzata, rilevamenti e dashboard che semplificano le indagini ma possono risultare caotiche per team più piccoli. |
| Onboarding e Formazione | Offre onboarding assistito con ingegneri ThreatLocker Cyber Hero e webinar per supportare la progettazione e la distribuzione delle policy. | Fornisce documentazione, formazione e supporto ai partner; i clienti più grandi spesso abbinano onboarding con integrazioni MDR o SIEM. |
| Esperienza di Supporto | Supporto “Cyber Hero” 24/7 reattivo e con aiuto pratico durante incidenti sulle policy. | Supporto di livello Enterprise con SLA e servizi gestiti opzionali; la qualità è alta ma può dipendere dal livello di servizio sottoscritto. |
ThreatLocker richiede generalmente un maggiore sforzo iniziale dato che sei tu a decidere esattamente cosa può essere eseguito, ma una volta stabilite le policy si riscontrano meno avvisi e comportamenti più prevedibili. CrowdStrike appare più immediato dal punto di vista del rilevamento, con interfaccia e processi in linea con quelli dei SOC, anche se la vastità delle opzioni può risultare impegnativa senza un team di sicurezza dedicato.
ThreatLocker
- Delivers strong prevention against ransomware and zero-days.
- Granular control over applications, storage, and network access.
- Detailed logging supports compliance, audits, and forensic investigations.
- Steep initial learning curve and tuning period, requires upfront policy work to avoid blocking legitimate apps.
- Not a set-and-forget security solution for most environments.
- End-user friction arises from strict controls that block routine software installs.
CrowdStrike Falcon
- Highly effective endpoint protection with features like device control and DLP options.
- Real-time threat detection.
- Cloud-native architecture provides scalable, efficient endpoint security.
- Customer support response times could be quicker.
- Onboarding might require more time and resources than expected.
- Interface can be complex and overwhelming at first.
ThreatLocker
- MSPs Managing Multiple ClientsCentralized cloud portal and RMM integrations let you deploy and tune policies across diverse environments without constant per-client tweaks.
- Healthcare OrganizationsGranular storage and elevation controls protect patient data on USBs, shares, and apps while meeting HIPAA compliance through audit trails.
- Educational InstitutionsLocks down student devices and servers against unauthorized software, reducing risks from unvetted apps in shared environments.
- Midmarket EnterprisesBalances strong prevention with learning modes to build allowlists quickly, minimizing disruption during rollout.
- High-Compliance IndustriesRingfencing and network controls limit lateral movement and data exfiltration, simplifying audits with detailed enforcement logs.
- Remote/Hybrid WorkforcesDynamic network ACLs secure traveling endpoints by whitelisting specific IPs or keywords without VPN overhead.
CrowdStrike Falcon
- Security TeamsFalcon's capabilities allow you to focus on advanced threat management and prevention.
- IT DepartmentsIt equips your team with tools to proactively manage and respond to security threats.
- Large EnterprisesFalcon's comprehensive features support your extensive IT security needs effectively.
- Retail ChainsFalcon's threat hunting tools help you identify vulnerabilities in your payment systems.
- Healthcare ProvidersIts endpoint protection ensures patient data is secure and compliant with regulations.
- Financial ServicesCrowdStrike Falcon provides real-time threat detection to protect your sensitive financial data.
Chi dovrebbe usare ThreatLocker e chi CrowdStrike
ThreatLocker è ideale per le organizzazioni che vogliono prevenire le minacce controllando rigorosamente cosa può essere eseguito nel proprio ambiente, in particolare in settori regolamentati o operativamente sensibili come sanità, manifatturiero, istruzione e PMI gestite da MSP. Il suo modello Zero Trust deny-by-default, i controlli granulari su applicazioni e storage, e ampia visibilità sugli audit risultano più efficaci per i team disposti a investire a monte nella progettazione delle policy per ridurre rischi a lungo termine, esposizione a ransomware e comportamenti imprevisti.
CrowdStrike è una scelta eccellente per le organizzazioni che necessitano di un'ampia visibilità e una rapida rilevazione all'interno di ambienti grandi e complessi, come ospedali, catene di vendita al dettaglio, aziende e agenzie governative. La piattaforma Falcon si concentra sulla rilevazione e la risposta tramite EDR/XDR, protezione dell'identità, sicurezza cloud e, opzionalmente, un monitoraggio 24/7 delle minacce gestito, rendendola particolarmente adatta ai team di sicurezza che danno priorità al monitoraggio in tempo reale, alla risposta agli incidenti e alla reportistica di conformità su larga scala.
| ThreatLocker | CrowdStrike Falcon | |
|---|---|---|
| Approach | ThreatLocker ThreatLocker is fundamentally a prevention platform built on zero-trust allowlisting and policy controls, stopping unapproved applications and scripts from executing in the first place. | CrowdStrike Falcon CrowdStrike is designed around AI-driven EDR and XDR that record activity, spot malicious behavior, and respond quickly once suspicious patterns appear, prioritizing detection and investigation. |
| Compliance | ThreatLocker Supports compliance by enforcing technical controls aligned with frameworks such as NIST, CIS, HIPAA, PCI-DSS, and CMMC, and provides SOC 2 Type II reports with security practices mapped to standards like ISO 27001, though it offers fewer formal certifications than some large legacy vendors. | CrowdStrike Falcon Maintains a broad compliance posture with SOC 2 Type II reports, ISO 27001 certification, PCI DSS assessments, and support for regulatory frameworks including HIPAA, NIST, and government standards like FedRAMP and IRAP, which can be valuable when auditors require named third-party attestations. |
| Control & Telemetry Breadth | ThreatLocker ThreatLocker gives you very granular control over what each app, script, user, and device can access, but collects comparatively limited behavioral telemetry. | CrowdStrike Falcon CrowsStrike captures rich endpoint and identity telemetry and correlates it with global threat intel, but it does not provide the same fine-grained, default-deny application allowlisting model that ThreatLocker offers. |
| Integrations | ThreatLocker ThreatLocker’s integrations are strongest in the MSP and IT operations ecosystem, with tight links into RMM, PSA, and endpoint tools to simplify multi-tenant management. | CrowdStrike Falcon CrowdStrike offers a far larger security ecosystem through its marketplace, including deep integrations with SIEM, SOAR, identity, cloud, and network security products—better suited if you want Falcon at the center of a broader detection and response stack. |
| Target Audience | ThreatLocker ThreatLocker tends to resonate with IT teams, MSPs, and mid-market enterprises that want to lock down known workflows and reduce alert fatigue without needing a fully staffed SOC. | CrowdStrike Falcon CrowdStrike is aimed more at enterprises and security-led organizations that have, or plan to have, a SOC, run SEIM or SOAR, and need threat hunting, incident response, and detailed forensics at scale. |
| Agent Architectures | Both ThreatLocker and CrowdStrike use small agents that live on your devices and connect to cloud consoles. This cloud approach lets you deploy quickly, push updates from one place, and protect remote workers without maintaining complex infrastructure yourself. |
|---|---|
| Breach Risk Reduction | Both platforms explicitly target modern ransomware, fileless attacks, and living-off-the-land techniques, going beyond legacy antivirus approaches. |
| Enterprise Readiness | ThreatLocker and CrowdStrike target the enterprise market. They’re built specifically for IT teams wrestling with complex networks, giving them what actually matters: centralized management, role-based access control, and support for complex, multi-site deployments. |
| Support | When security incidents hit, ThreatLocker’s Cyber Hero team is available 24/7 to help you adjust policies and coordinate your response. CrowdStrike matches this with always-on security operations via their support team and managed services options, with their Falcon Complete packages taking it further by handling monitoring and response duties for you. |
| Trial/Demo Availability | Both ThreatLocker and CrowdStrike let you test their platforms risk-free with a customized demo or a free trial, so you can deploy agents, build policies, or review detections, and assess fit for your specific environment before committing. |