

10 Best Authentication Software in 2026

10 Best Authentication Software Shortlist


Authentication software controls who gets into your systems, apps, and data by verifying user identities at every entry point. If you’re comparing the best authentication software, you’re probably working to secure complex environments, balance legacy tools with cloud services, and guard against rising threats like phishing and session hijacking.
The right authentication tool can help you manage risk, adapt security to changing conditions, and keep your teams productive without slowing them down. This guide will help you sort out what matters most—so you can pick a solution that fits your stack, supports your users, and gives you confidence in every login.
Why Trust Our Software Reviews
We’ve been testing and reviewing software since 2023. As tech leaders ourselves, we know how critical and difficult it is to make the right decision when selecting software.
We invest in deep research to help our audience make better software purchasing decisions. We’ve tested more than 2,000 tools for different tech use cases and written over 1,000 comprehensive software reviews. Learn how we stay transparent & our software review methodology.
Compare the Best Authentication Software
Compare pricing and specs, side by side, for the authentication software that made it onto my shortlist.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for heterogeneous IT and legacy app MFA | 30-day free trial | From $2/user/month | Website | |
| 2 | Best for phishing-resistant MFA at enterprise scale | Free plan available; 30-day free trial | From $3/user/month | Website | |
| 3 | Best for developer-driven identity integration | Free trial available | From $35/month | Website | |
| 4 | Best for Google-native workforce identity | 14-day free trial | From $7.00/user/month | Website | |
| 5 | Best for continuous post-login session risk scoring | 14-day free trial | Pricing upon request | Website | |
| 6 | Best for enterprise-wide identity at scale | 30-day free trial | From $6/user/month (billed annually) | Website | |
| 7 | Best for enterprise-grade hybrid and federal IAM | 30-day free trial | From $3/user/month (billed annually) | Website | |
| 8 | Best for ML-driven adaptive workforce auth | 30-day free trial available | From $3/user/month | Website | |
| 9 | Best for Microsoft 365-native identity security | 30-day free trial | From $7.00/user/month | Website | |
| 10 | Best for unified workforce and customer IAM | Free trial available | From $1.71/user/month (billed annually) | Website |
Authentication Software Reviews
Below are my detailed summaries of the best authentication software that made it onto my shortlist. My reviews offer a detailed look at the features, best use cases, and capabilities of each platform to help you find the best one for you.

Best for heterogeneous IT and legacy app MFA
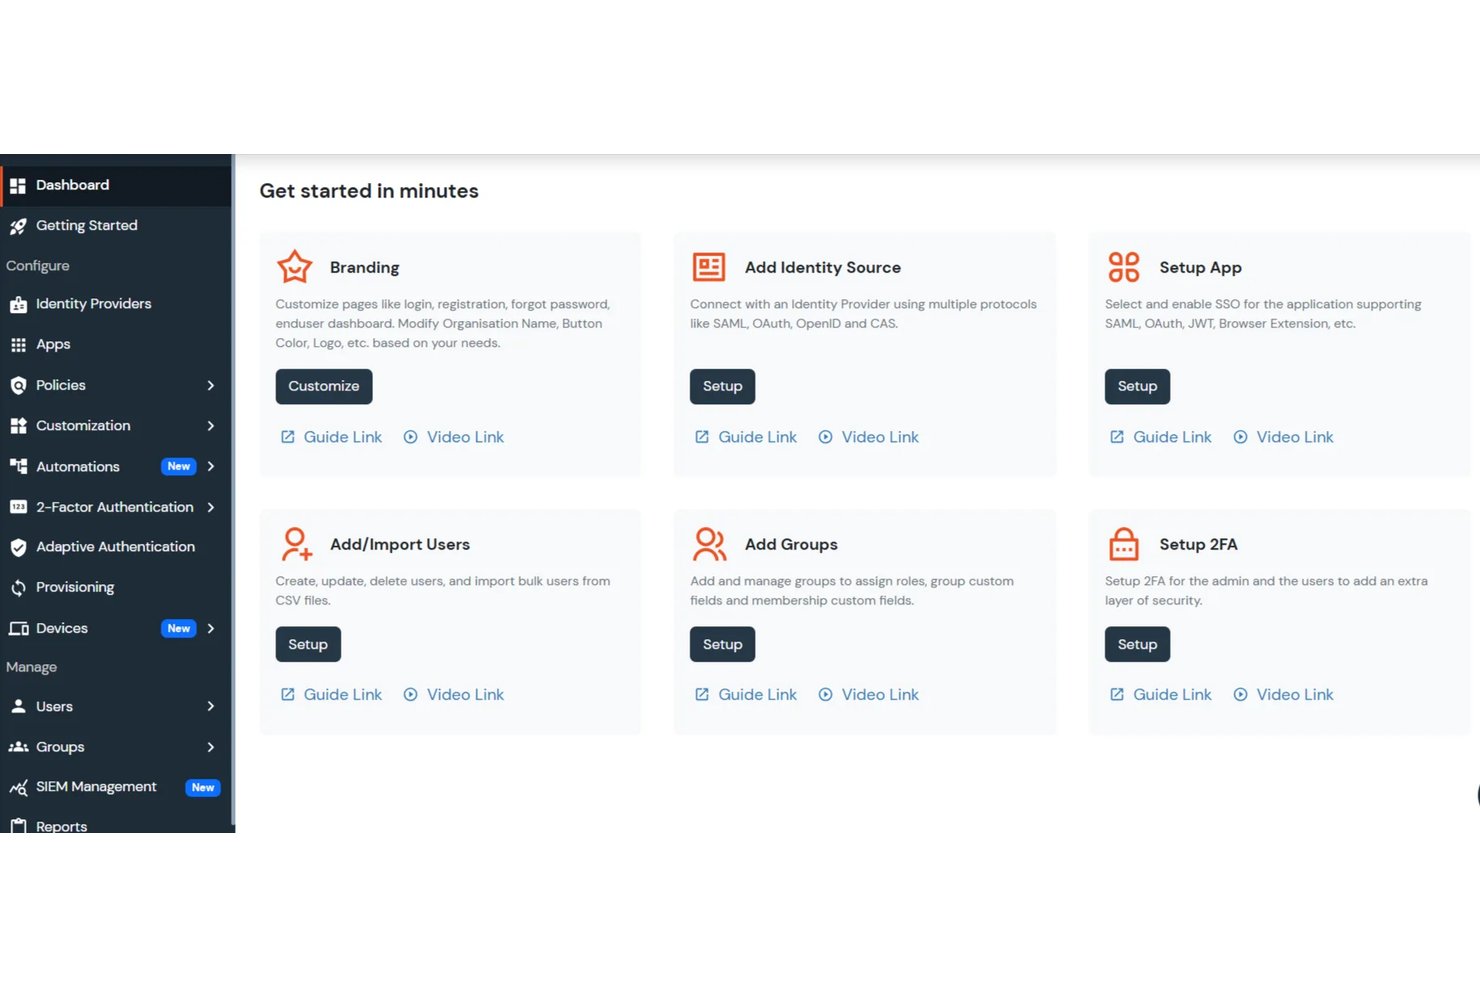
miniOrange is an identity and access management platform that covers MFA across VPNs, network devices, desktops, and legacy apps, alongside SSO, adaptive authentication, user provisioning, and CIAM.
Who Is miniOrange Best For?
miniOrange is a strong fit for IT teams managing mixed environments that include VPNs, network devices, legacy ERP systems, and modern SaaS apps side by side.
Why I Picked miniOrange
I picked miniOrange as one of the best because it's the only tool on my list that can put MFA in front of a Cisco AnyConnect VPN, a Windows RDP session, a PeopleSoft ERP login, and a SaaS app simultaneously, all from a single admin console. Most IAM vendors handle cloud apps well but fall apart when you introduce RADIUS-dependent network devices or header-based legacy apps. miniOrange handles both natively, using TACACS+ for network device authentication and reverse proxy for legacy apps that can't speak SAML or OIDC.
miniOrange Key Features
- SCIM-based user provisioning: Automatically provisions and deprovisions user accounts across 7,000+ applications using SCIM, with bidirectional sync and role-based attribute mapping.
- Adaptive risk-based access policies: Evaluates device posture, IP reputation, geolocation, and behavior patterns to dynamically allow, challenge, or block access attempts.
- FIDO2/WebAuthn passkey authentication: Supports phishing-resistant passwordless login via hardware security keys, biometrics, and device-bound passkeys on Premium plans and above.
- Self-service user enrollment portal: Lets users register their own MFA devices and authentication methods at first login, with optional admin-approval workflows.
miniOrange Integrations
miniOrange offers 6,000+ integrations, including Salesforce, Google Workspace, Microsoft 365, AWS, Slack, Zoom, SAP, Oracle EBS, PeopleSoft, and Active Directory. It supports custom connections through REST APIs, SAML, OAuth 2.0, OIDC, SCIM, LDAP, RADIUS, and TACACS+.
Pros and Cons
Pros:
- Adaptive authentication with risk-based policies
- Flexible deployment options including on-premise
- Supports legacy app and network device MFA
Cons:
- Integration with some apps can be complex
- Key features gated to higher plan tiers
Cisco
Best for phishing-resistant MFA at enterprise scale
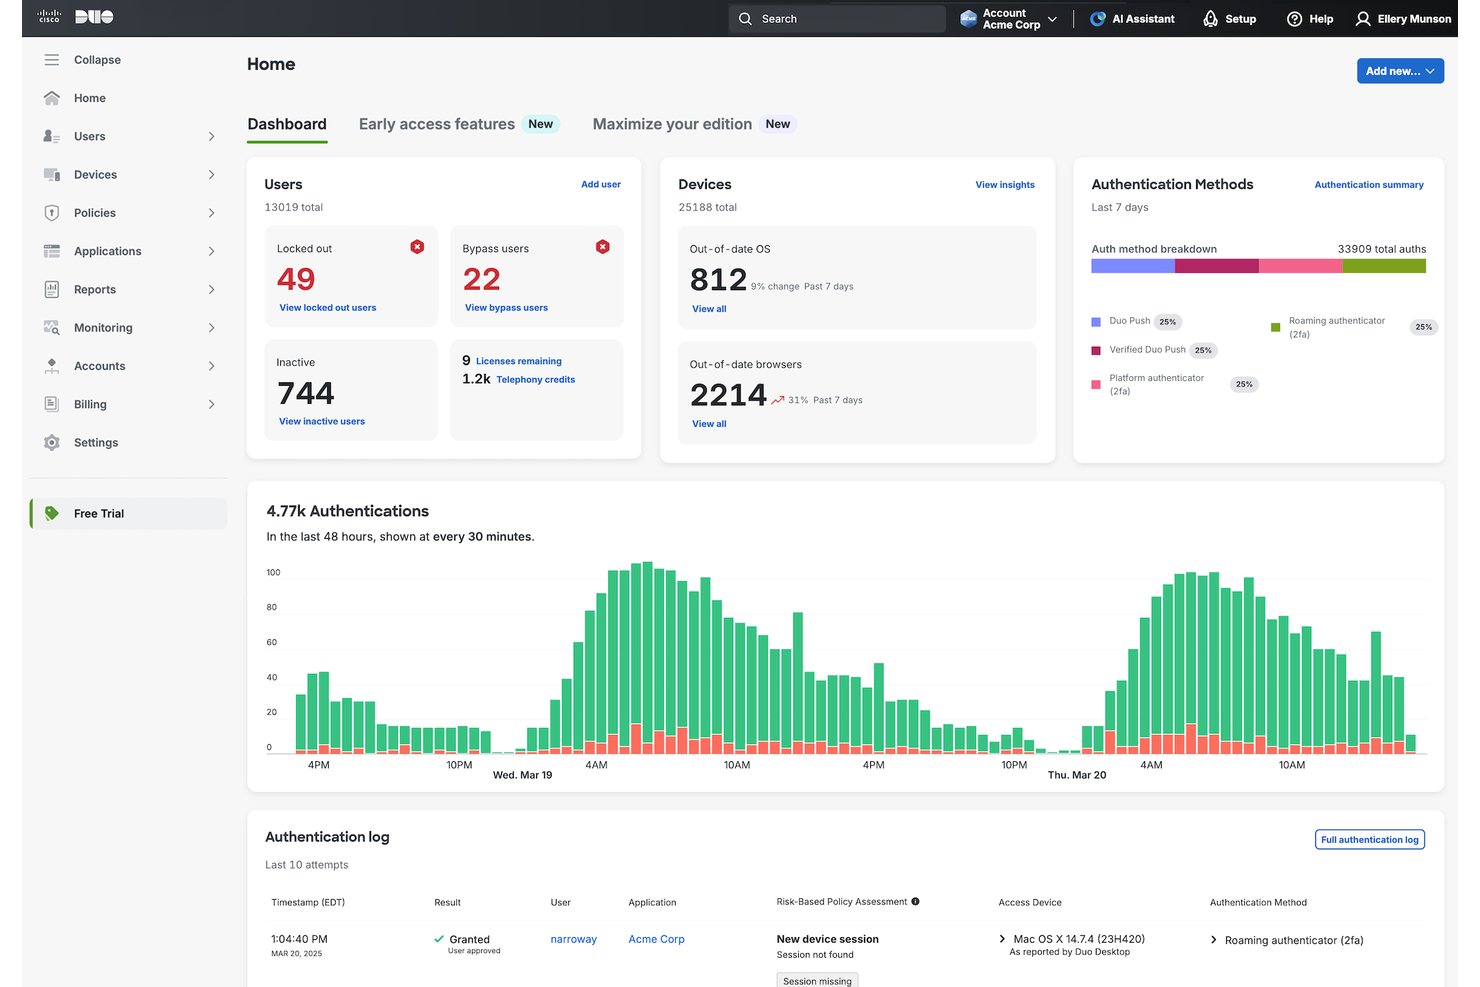
Cisco Duo is an MFA and identity security platform that covers phishing-resistant authentication, passwordless login, SSO, device trust, and adaptive access policies across cloud and on-premises environments.
Who Is Cisco Duo Best For?
Cisco Duo is the right call for enterprise IT and security teams that need to enforce phishing-resistant MFA across a large, distributed workforce without sacrificing compliance coverage.
Why I Picked Cisco Duo
Cisco Duo earns its spot on my shortlist because no other platform matches its depth of phishing-resistant MFA options at enterprise scale. I'm particularly impressed by Verified Duo Push, which forces users to enter a matching code at login, directly defeating push-bombing attacks. Combine that with FIDO2 passkey support and the BLE-based Proximity Verification, and you've got layered, hardware-grade authentication coverage that holds up across distributed workforces.
Cisco Duo Key Features
- Risk-based authentication: Dynamically adjusts authentication requirements based on real-time signals like device health, IP reputation, and user location.
- Duo Directory: A cloud-native user directory that lets you store and manage user identities, roles, and groups directly within Duo.
- Outbound SCIM provisioning: Automates user provisioning and deprovisioning to downstream apps like Microsoft 365, AWS IAM Identity Center, and Atlassian.
- Device trust enforcement: Checks endpoint security posture—including OS version, disk encryption, and antivirus status—before granting access to any connected app.
Cisco Duo Integrations
Cisco Duo offers 500+ pre-built application and infrastructure integrations, including Microsoft 365, Salesforce, AWS, Workday, Slack, Dropbox, Box, Zoom, and Atlassian. It also supports SAML, OIDC, RADIUS, LDAP, SCIM, and APIs for custom integrations.
Pros and Cons
Pros:
- FedRAMP and FIPS compliance for regulated sectors
- Device trust checks before granting access
- Verified Duo Push blocks push-bombing attacks
Cons:
- CIAM and social login features missing
- SSO app catalog smaller than Okta’s

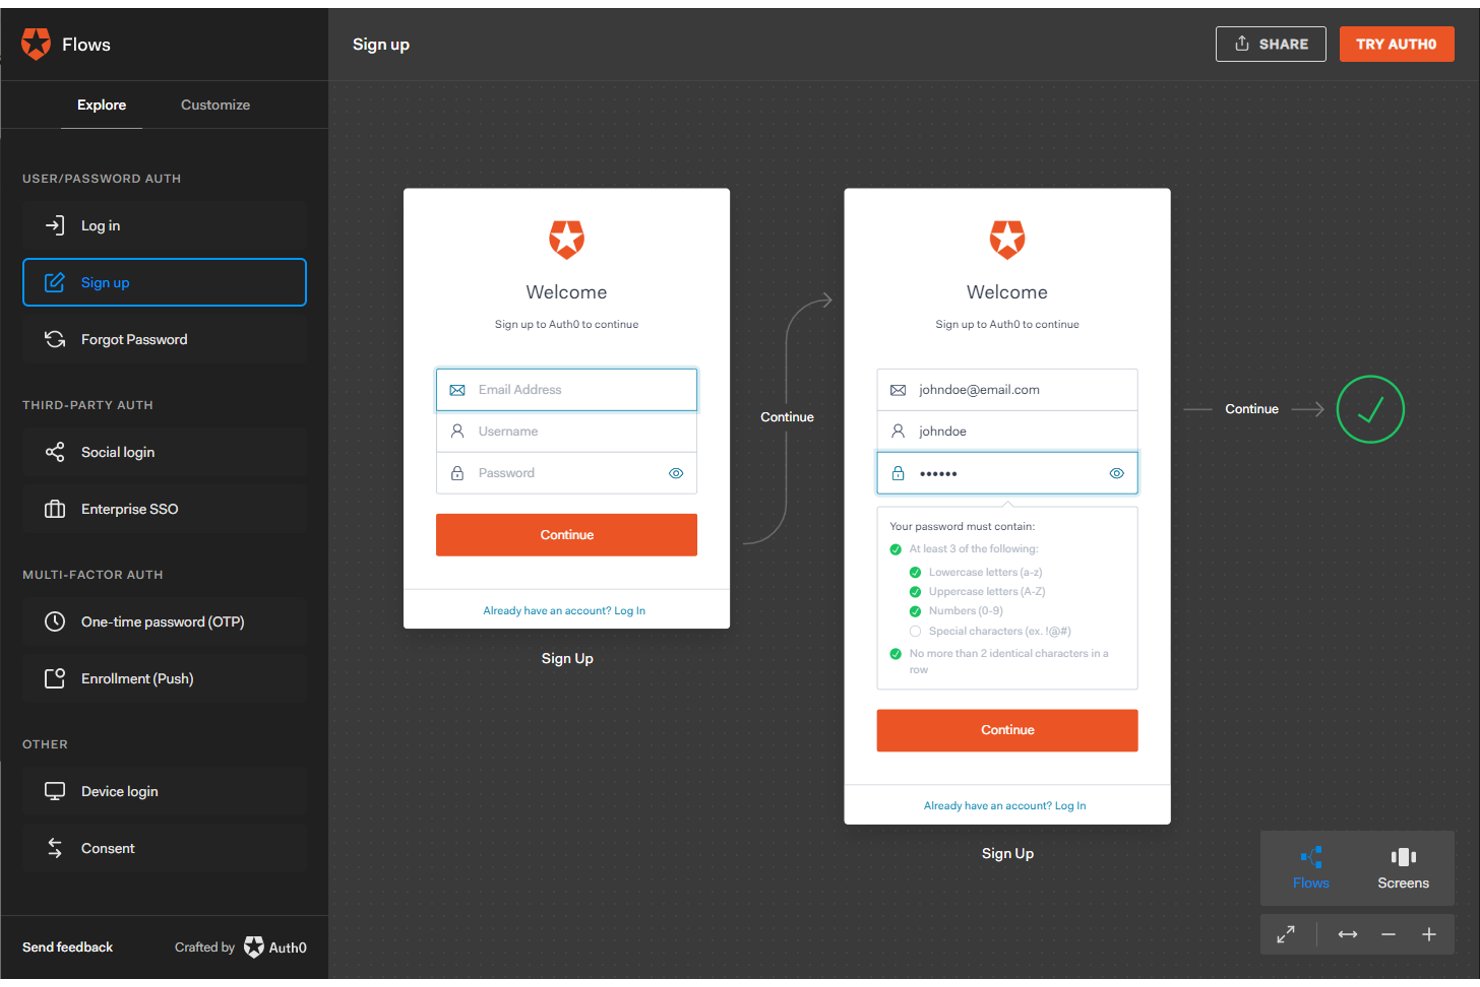
Auth0 is a developer-focused identity platform offering MFA, SSO, passwordless authentication, fine-grained authorization, and SCIM-based user lifecycle management across custom-built and enterprise applications.
Who Is Auth0 Best For?
Auth0 is a strong fit for engineering teams building authentication into custom applications and needing flexible, API-first identity infrastructure.
Why I Picked Auth0
Auth0 earns its spot on my shortlist because it's the most developer-native identity platform I've worked with, built from the ground up for teams embedding authentication directly into custom applications. I especially like its Auth0 Actions, which let you inject serverless logic into any point of the auth flow, like triggering Step-Up MFA only when a user accesses a sensitive API endpoint. Its Adaptive MFA engine uses ML-based risk scoring to challenge logins that show impossible travel or unrecognized devices, without adding friction to clean sessions.
Auth0 Key Features
- SCIM 2.0 inbound provisioning: Sync users and groups from upstream identity providers into Auth0 with full create, update, deactivate, and delete support, plus automatic session revocation on deprovisioning.
- Auth0 Organizations: Model multi-tenant B2B structures where each customer organization gets its own SSO configuration, directory sync, domain verification, and self-service admin portal.
- Fine-grained authorization (FGA): Define and evaluate complex relationship-based, role-based, and attribute-based access policies using an OpenFGA-powered engine that scales to billions of permission tuples.
- Log streaming: Export tenant audit logs in near-real time to SIEM platforms like Splunk, Datadog, and Amazon EventBridge, with event filtering and PII obfuscation controls built in.
Auth0 Integrations
Auth0 offers native integrations with Microsoft Entra ID, Active Directory, Google Workspace, Okta Workforce Identity, Datadog, Splunk, Amazon EventBridge, and Azure Event Hubs. It also supports marketplace integrations and custom connections through its REST Management API.
Pros and Cons
Pros:
- Multi-tenant B2B structures via Organizations feature
- Fine-grained authorization supports relationship-based policies
- Adaptive MFA challenges only risky login attempts
Cons:
- Advanced features often require plan upgrades
- Log retention is short on lower plans

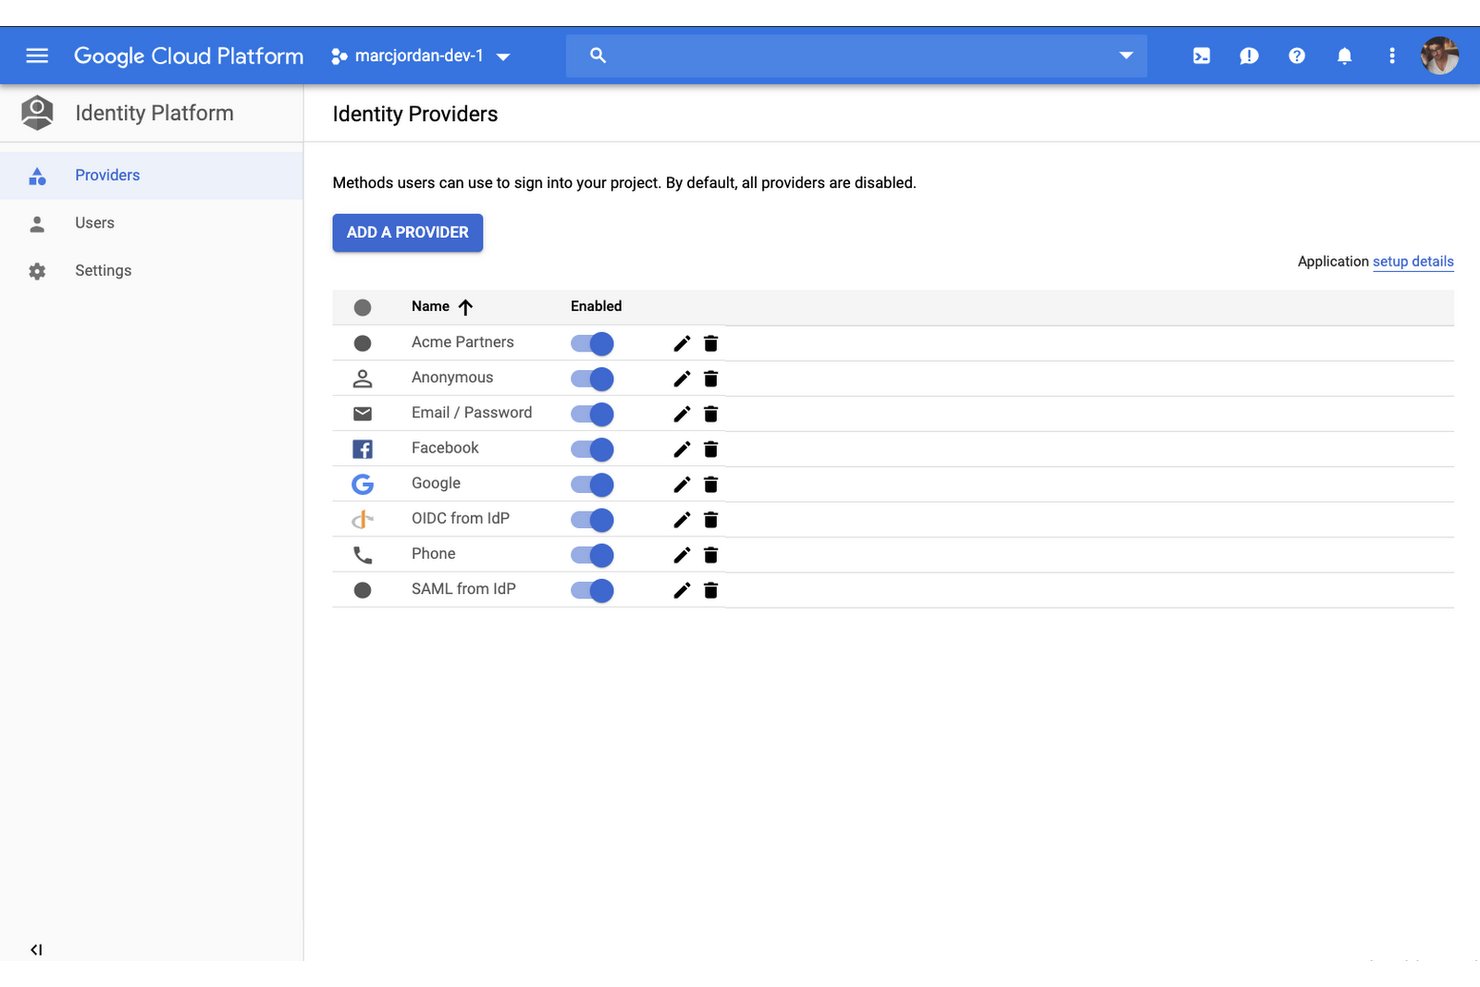
Google Cloud Identity is a workforce identity and access management platform that covers SSO, MFA, adaptive access policies, and a built-in cloud directory—with a developer-facing CIAM layer through Identity Platform for custom app authentication.
Who Is Google Cloud Identity Best For?
Google Cloud Identity is the right fit for IT and security teams running on Google Workspace or Google Cloud who need workforce identity management built directly into their existing environment.
Why I Picked Google Cloud Identity
I picked Google Cloud Identity because it's built directly into the Google ecosystem, which means if your workforce is already on Google Workspace or Google Cloud, identity management isn't something you bolt on. I especially like the Context-Aware Access policies, which evaluate device posture, location, and IP signals before granting access, and the mandatory passkey and FIDO2 rollout across all Google Cloud accounts, which gives you phishing-resistant authentication without requiring a separate vendor.
Google Cloud Identity Key Features
- Google Cloud Directory Sync (GCDS): Syncs users and groups from on-premises Active Directory or LDAP directories directly to Cloud Identity on a one-way basis.
- Workforce Identity Federation: Extends SSO to external IdPs without requiring user sync, covering more than 95% of Google Cloud products via attribute-based access.
- Identity-Aware Proxy (IAP): Enforces context-aware access policies on cloud apps and VMs based on device posture, network, and user identity signals—without a VPN.
- Identity Platform SDKs: Provides multi-language SDKs (JavaScript, iOS, Android, Node.js, Python, Go, Java, C++) for embedding authentication directly into custom-built applications.
Google Cloud Identity Integrations
Google Cloud Identity offers Marketplace integrations with Salesforce, Atlassian Jira, Confluence, and ServiceNow, plus native integrations across Google Workspace and Google Cloud. Admin SDK, Reports API, and Identity Platform REST APIs support custom integrations.
Pros and Cons
Pros:
- SDKs support custom app authentication workflows
- Context-aware access enforces granular zero trust
- Passkeys and FIDO2 required for all users
Cons:
- LDAP support limited to higher tiers
- Active Directory sync is one-way only

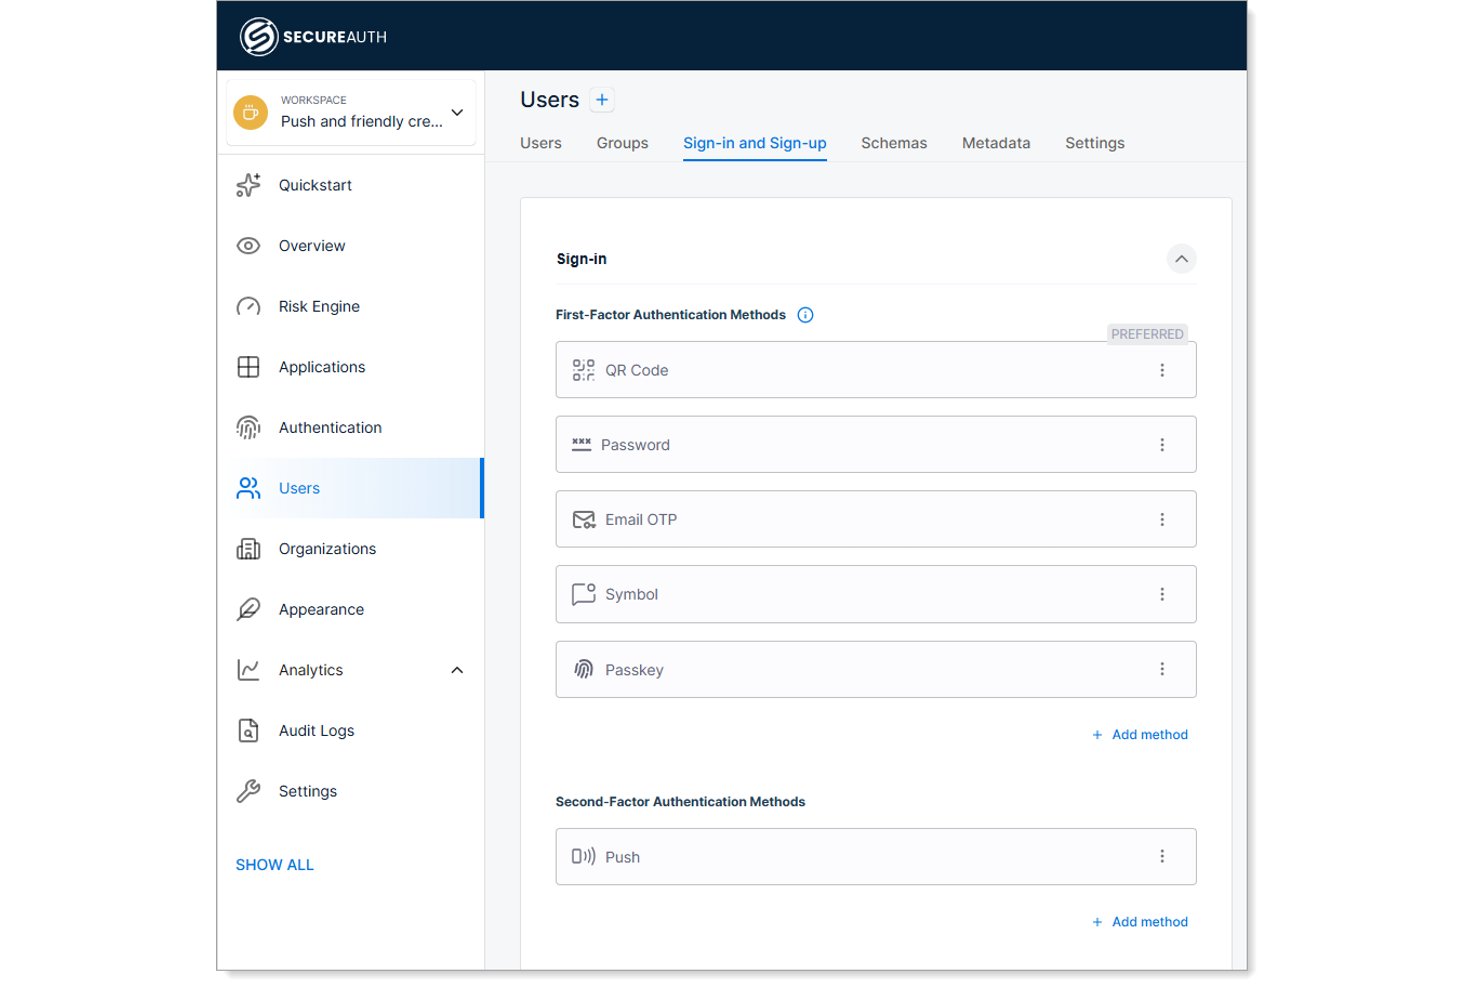
SecureAuth is an enterprise identity and access management platform built around continuous authentication, offering MFA, SSO, adaptive risk scoring, and session-level security across workforce, B2B, and consumer identity use cases.
Who Is SecureAuth Best For?
SecureAuth is a strong fit for security and IAM teams in regulated industries—think healthcare, finance, defense, and government—that need identity protection to extend beyond the login screen.
Why I Picked SecureAuth
SecureAuth earns its spot on my shortlist because of how it handles post-login risk, not just the login itself. Most IAM platforms stop scoring risk the moment a session opens, but SecureAuth's Assurance Authority continuously re-evaluates 100+ behavioral signals throughout the session, triggering step-up authentication or automatic termination when something looks off. I also like that Presence Authority goes further still, using facial recognition to confirm the right person stays at the screen.
SecureAuth Key Features
- Enterprise-issued FIDO2 passkeys: Organization-controlled passkeys that are hardware-enclave-bound and not tied to consumer platforms like Apple or Google, supporting full IT lifecycle management.
- B2B self-service SSO onboarding: A no-code wizard with 20+ pre-built IdP connectors lets partner organizations configure their own SSO in minutes without involving your team.
- RADIUS gateway for network MFA: A dedicated RADIUS gateway extends MFA enforcement to VPNs, firewalls, switches, and routers alongside standard application authentication.
- AI agent identity governance: Assigns a unique cryptographic identity to every AI agent, enforces scoped OAuth tokens per action, and maintains a tamper-proof audit trail of every agent action and delegation chain.
SecureAuth Integrations
SecureAuth documents 20+ pre-built B2B identity-provider connectors, including Okta, Microsoft Entra ID, Google Workspace, and OneLogin, plus Auth0, AWS Cognito, GitHub, and Google through OIDC and SAML. It also supports SCIM, LDAP, RADIUS, and APIs for custom connectivity.
Pros and Cons
Pros:
- Extensive authentication protocol and method support
- Physical presence verification during sessions
- Continuous post-login session risk evaluation
Cons:
- Monitoring dashboards are limited for daily use
- Admin console is complex and hard to navigate
Okta
Best for enterprise-wide identity at scale
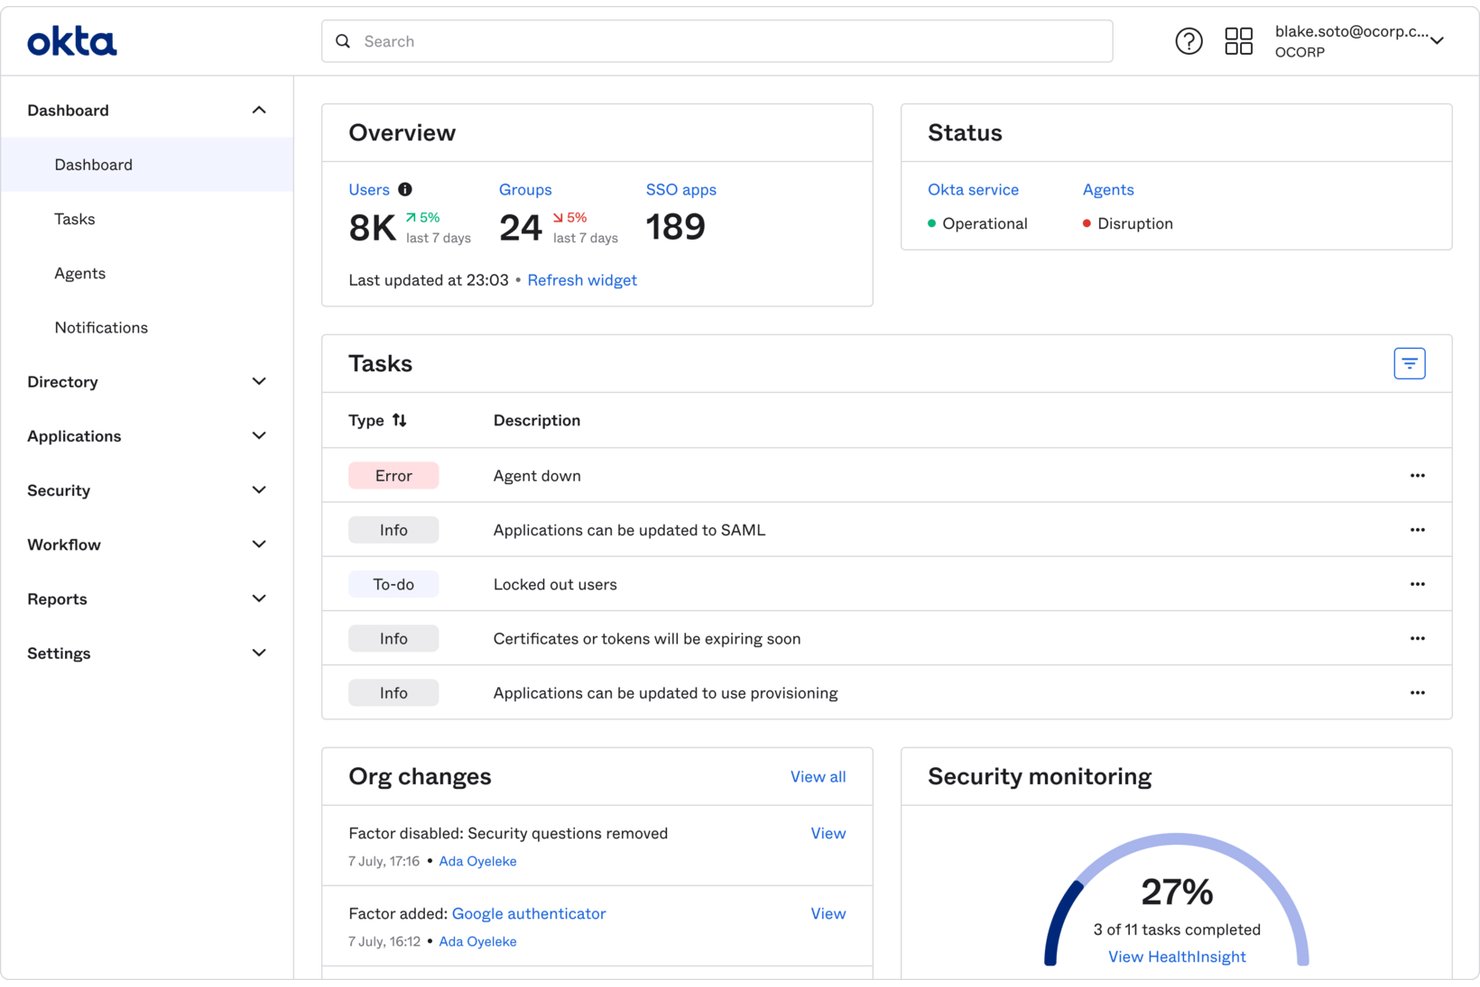
Okta is a workforce identity platform that covers SSO, adaptive MFA, lifecycle management, and identity governance across cloud, on-premises, and mobile environments.
Who Is Okta Best For?
Okta is a strong fit for enterprise IT and security teams managing identity at scale across complex, multi-app environments with strict compliance requirements.
Why I Picked Okta
Okta earns its spot on my shortlist because no other platform matches its scale for enterprise-wide identity management. I'm particularly impressed by Universal Directory, which aggregates identities from Active Directory, Workday, and LDAP into a single cloud control plane, and by Identity Threat Protection, which continuously scores session risk after login rather than just at authentication. With 8,000+ pre-built OIN integrations and adaptive MFA that triggers step-up challenges based on device posture and behavior signals, Okta handles identity at a scope few vendors come close to.
Okta Key Features
- Okta Workflows: A no-code automation platform for building Joiner-Mover-Leaver identity processes, with 50+ pre-built flows and integrations with Slack and Teams for self-service access requests.
- Identity Threat Protection: Continuously scores session risk after login using AI, triggering automated responses like Universal Logout or step-up MFA challenges when anomalous behavior is detected.
- Okta Integration Network (OIN): A catalog of 8,000+ pre-built, Okta-reviewed app integrations covering SSO, lifecycle management, identity governance, and centralized logging.
- Access certifications: Part of Okta Identity Governance, this feature lets you run periodic access reviews to confirm or revoke user entitlements across connected applications.
Okta Integrations
Okta offers 8,000+ Okta Integration Network integrations, including Microsoft 365, Salesforce, Workday, Slack, Splunk, CrowdStrike, and Google Workspace. It also provides REST APIs, SCIM, and Terraform providers for custom identity integrations.
Pros and Cons
Pros:
- Strong compliance for regulated industry requirements
- Adaptive MFA with continuous session risk scoring
- Massive pre-built SSO integrations catalog
Cons:
- Support responsiveness and documentation often criticized
- Initial configuration requires extensive IAM expertise

Best for enterprise-grade hybrid and federal IAM
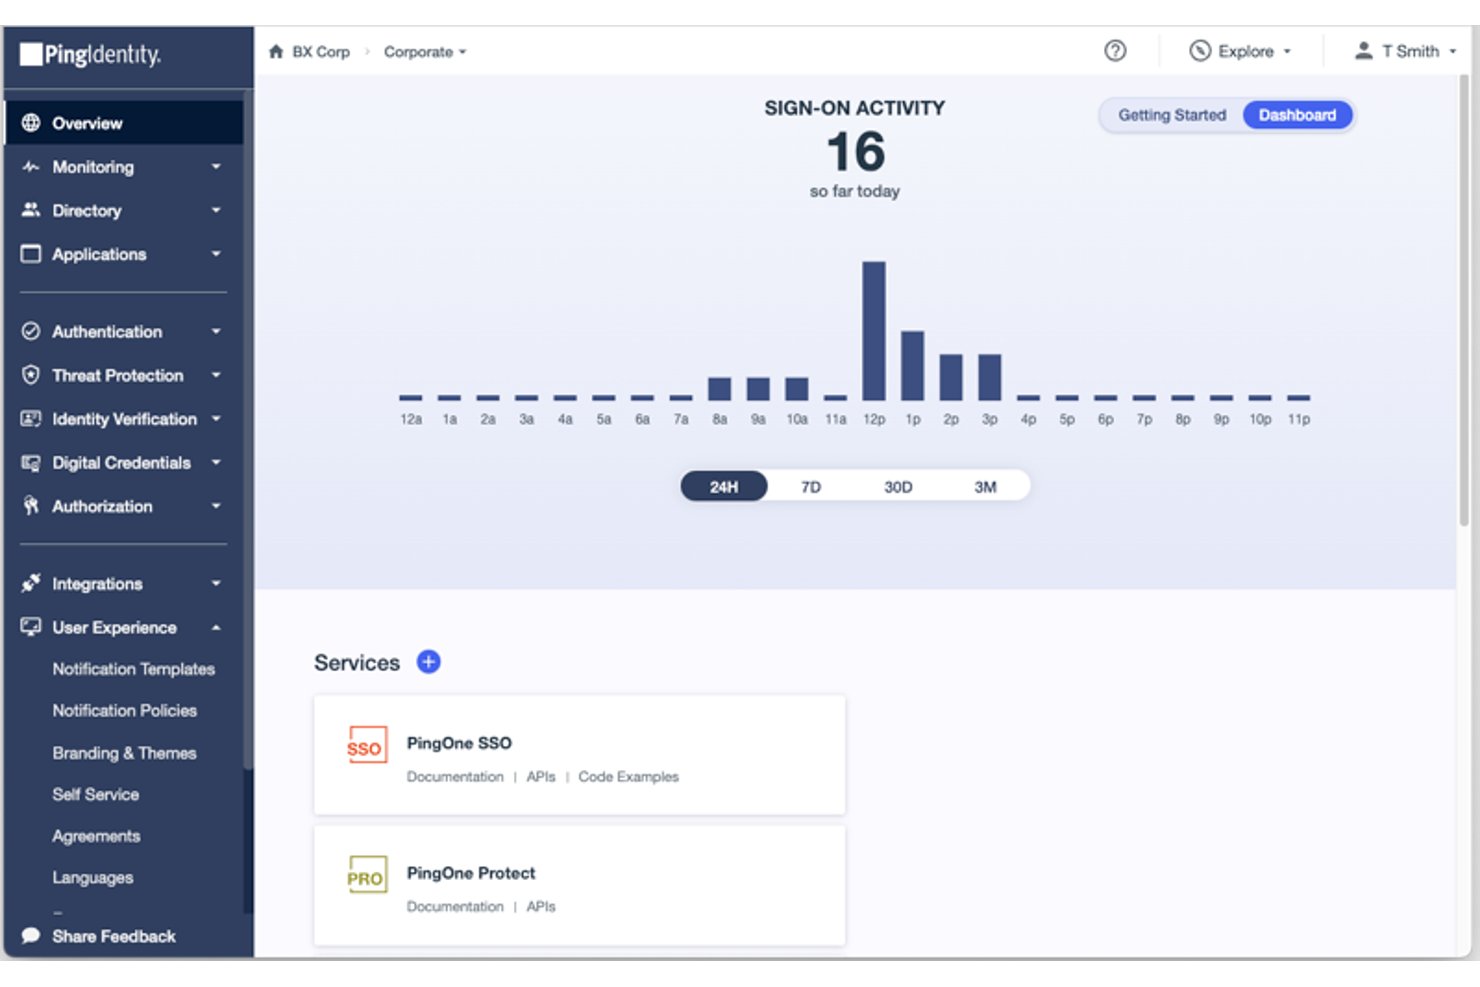
Ping Identity is an enterprise IAM platform covering SSO, MFA, adaptive authentication, fine-grained authorization, and identity orchestration across cloud, hybrid, and on-premises environments.
Who Is Ping Identity Best For?
Ping Identity is built for large enterprises and federal agencies that need to manage identity across hybrid, on-premises, and air-gapped environments with strict compliance requirements.
Why I Picked Ping Identity
Ping Identity earns its spot on my shortlist because it's the only IAM platform I've seen that delivers full feature parity across cloud, on-premises, air-gapped, and DDIL environments. I picked it specifically for teams in regulated industries or federal agencies where deploying to a FedRAMP High or DoD IL5-certified environment isn't optional. PingFederate handles SSO across legacy and modern apps without forcing a rip-and-replace, and PingOne Protect adds ML-driven risk scoring that triggers step-up MFA only when signals like geo-velocity anomalies or compromised credentials warrant it.
Ping Identity Key Features
- No-code identity orchestration: PingOne DaVinci provides a drag-and-drop canvas for building, testing, and deploying identity flows using hundreds of pre-built connectors.
- Fine-grained authorization: PingOne Authorize lets you define ABAC, RBAC, and ReBAC policies externally from application code using a visual policy decision tree.
- Offline MFA mode: PingOne MFA supports authentication without an active internet connection, covering access scenarios where connectivity isn't guaranteed.
- AI-agent identity management: A dedicated product registers and enforces runtime policies for non-human identities like AI agents, bots, and microservices.
Ping Identity Integrations
Ping Identity offers 350+ marketplace connectors, including integrations with Active Directory, Azure AD, Microsoft 365, Twilio, and ForgeRock. It also supports SAML, OAuth 2.0, OIDC, SCIM, LDAP, RADIUS, REST APIs, and native iOS and Android SDKs.
Pros and Cons
Pros:
- No-code orchestration platform for complex workflows
- Advanced adaptive risk-based authentication options
- Full protocol support for legacy and modern apps
Cons:
- Implementation often needs professional services
- Minimum 5,000-user commitment required

OneLogin
Best for ML-driven adaptive workforce auth
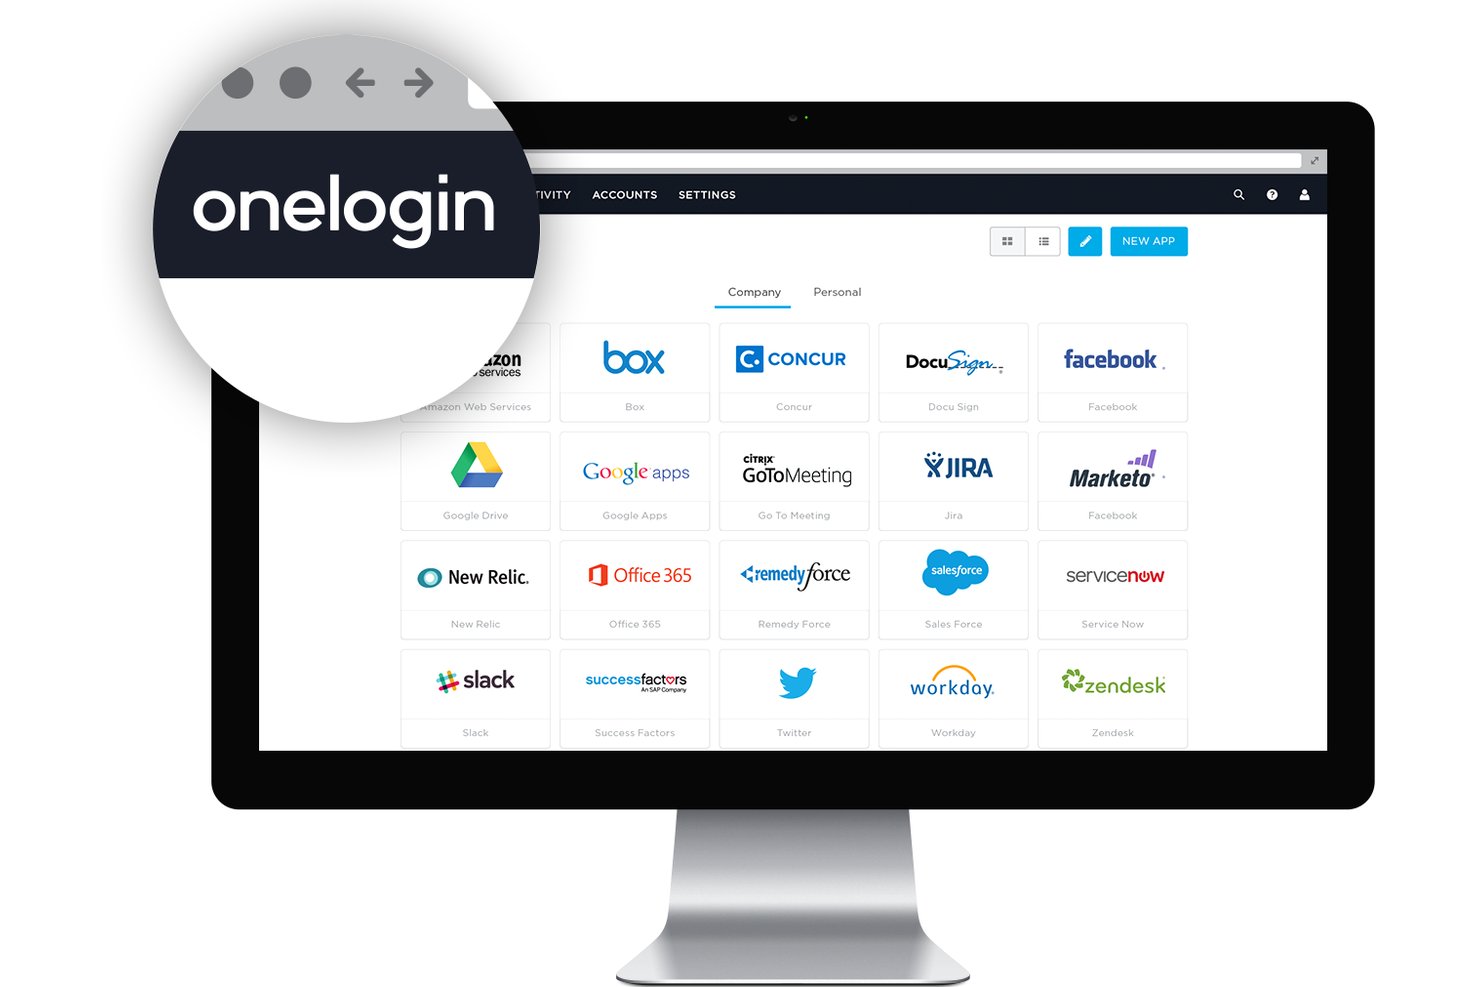
OneLogin is a workforce identity platform that combines SSO across 6,000+ apps, MFA with passkey and biometric support, adaptive authentication, and automated user lifecycle management.
Who Is OneLogin Best For?
OneLogin is a strong fit for mid-to-large enterprises that need a unified workforce IAM platform with ML-driven adaptive authentication across a complex, hybrid app environment.
Why I Picked OneLogin
OneLogin earns its spot on my shortlist because of how Vigilance AI handles adaptive authentication. Rather than applying static conditional access rules, it uses ML to calculate a risk score per login based on geolocation, IP reputation, device posture, and behavioral history, then adjusts factor requirements in real time. I've seen SmartFactor step up MFA automatically when a login comes from an unfamiliar country while letting low-risk sessions through with a single push approve.
OneLogin Key Features
- SmartFactor Authentication: ML-powered risk scoring that dynamically adjusts authentication factor requirements based on device posture, IP reputation, and geolocation signals.
- 6,000+ pre-built app connectors: A catalog of SAML, OIDC, and forms-based SSO integrations covering both cloud and on-premises applications.
- Compromised credential check: Automatically screens new and updated passwords against known breach databases and blocks reuse of stolen credentials.
- OneLogin Access: Extends SSO and MFA to on-premises and legacy applications without requiring protocol updates to the underlying apps.
OneLogin Integrations
OneLogin offers 6,000+ pre-built app connectors, including Workday, UKG, BambooHR, Namely, Microsoft Entra ID, Google Workspace, and Splunk. REST APIs and custom REST connectors support additional directory, provisioning, and application integrations.
Pros and Cons
Pros:
- Real-time compromised credential screening
- 6,000+ pre-built app SSO integrations
- SmartFactor adaptive authentication with Vigilance AI
Cons:
- API rate limits restrict advanced automations
- Service outages have disrupted access workflows

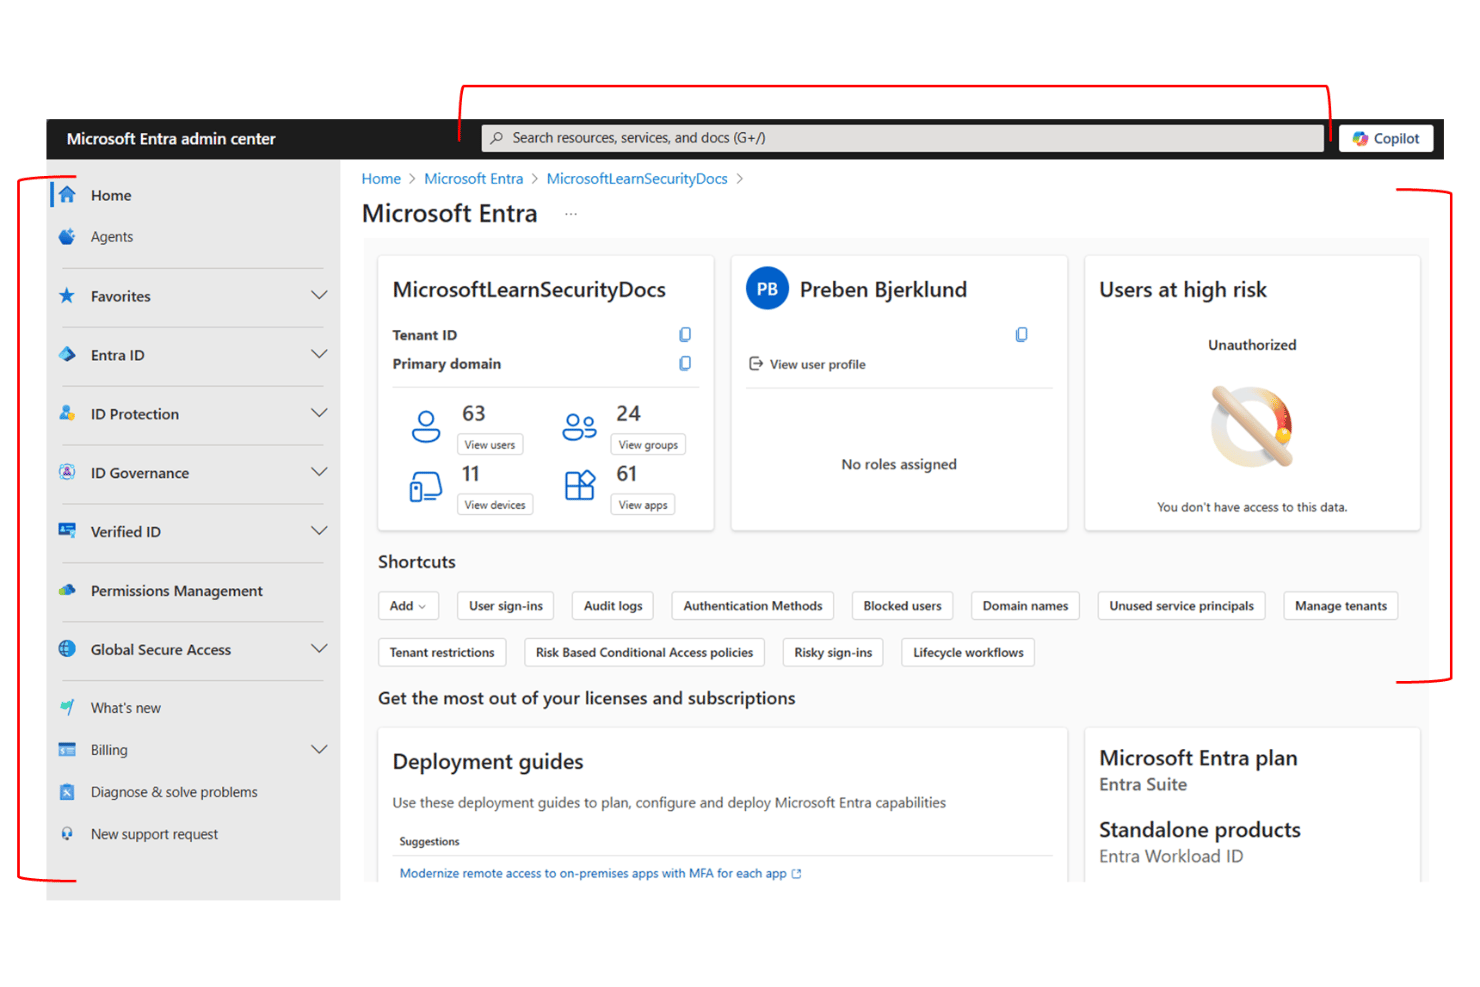
Microsoft Entra ID is a cloud-based identity and access management platform that covers MFA, SSO, adaptive authentication, user lifecycle management, and directory services across workforce and application environments.
Who Is Microsoft Entra ID Best For?
Microsoft Entra ID is the natural fit for IT and security teams already operating within the Microsoft 365 or Azure ecosystem who need centralized identity management across hybrid and cloud environments.
Why I Picked Microsoft Entra ID
Microsoft Entra ID earns its spot on my shortlist because, if your organization runs Microsoft 365 or Azure, identity is already baked into the infrastructure you're using every day. I particularly like how Conditional Access evaluates real-time signals, including device compliance via Intune, sign-in risk from Entra ID Protection, and location, to enforce step-up MFA only when the context actually warrants it. On top of that, phishing-resistant options like FIDO2 passkeys and Windows Hello for Business make passwordless authentication practical, not theoretical.
Microsoft Entra ID Key Features
- Privileged identity management (PIM): Grants time-bound, just-enough-access elevation for privileged roles, requiring justification and approval before access is activated.
- HR-driven provisioning: Connects to Workday and SAP SuccessFactors to automatically trigger joiner, mover, and leaver lifecycle events directly from your HR system.
- Entra ID Protection: Uses machine learning to score sign-in and user risk in real time, detecting signals like impossible travel, leaked credentials, and token anomalies.
- Microsoft Entra Application Proxy: Extends SSO to on-premises and legacy apps using header-based authentication, Kerberos, and integrated Windows authentication—no VPN required.
Microsoft Entra ID Integrations
Microsoft Entra ID offers thousands of app gallery integrations, including ServiceNow, Workday, Salesforce, AWS, Google Workspace, and Slack, plus native integrations across Microsoft 365 and Azure. Microsoft Graph API and SCIM 2.0 support custom application and provisioning connections.
Pros and Cons
Pros:
- Extensive support for hybrid identity scenarios
- Phishing-resistant MFA and passwordless options
- Granular conditional access policy engine
Cons:
- Complex, layered licensing for advanced features
- Cloud-only with no on-premises version
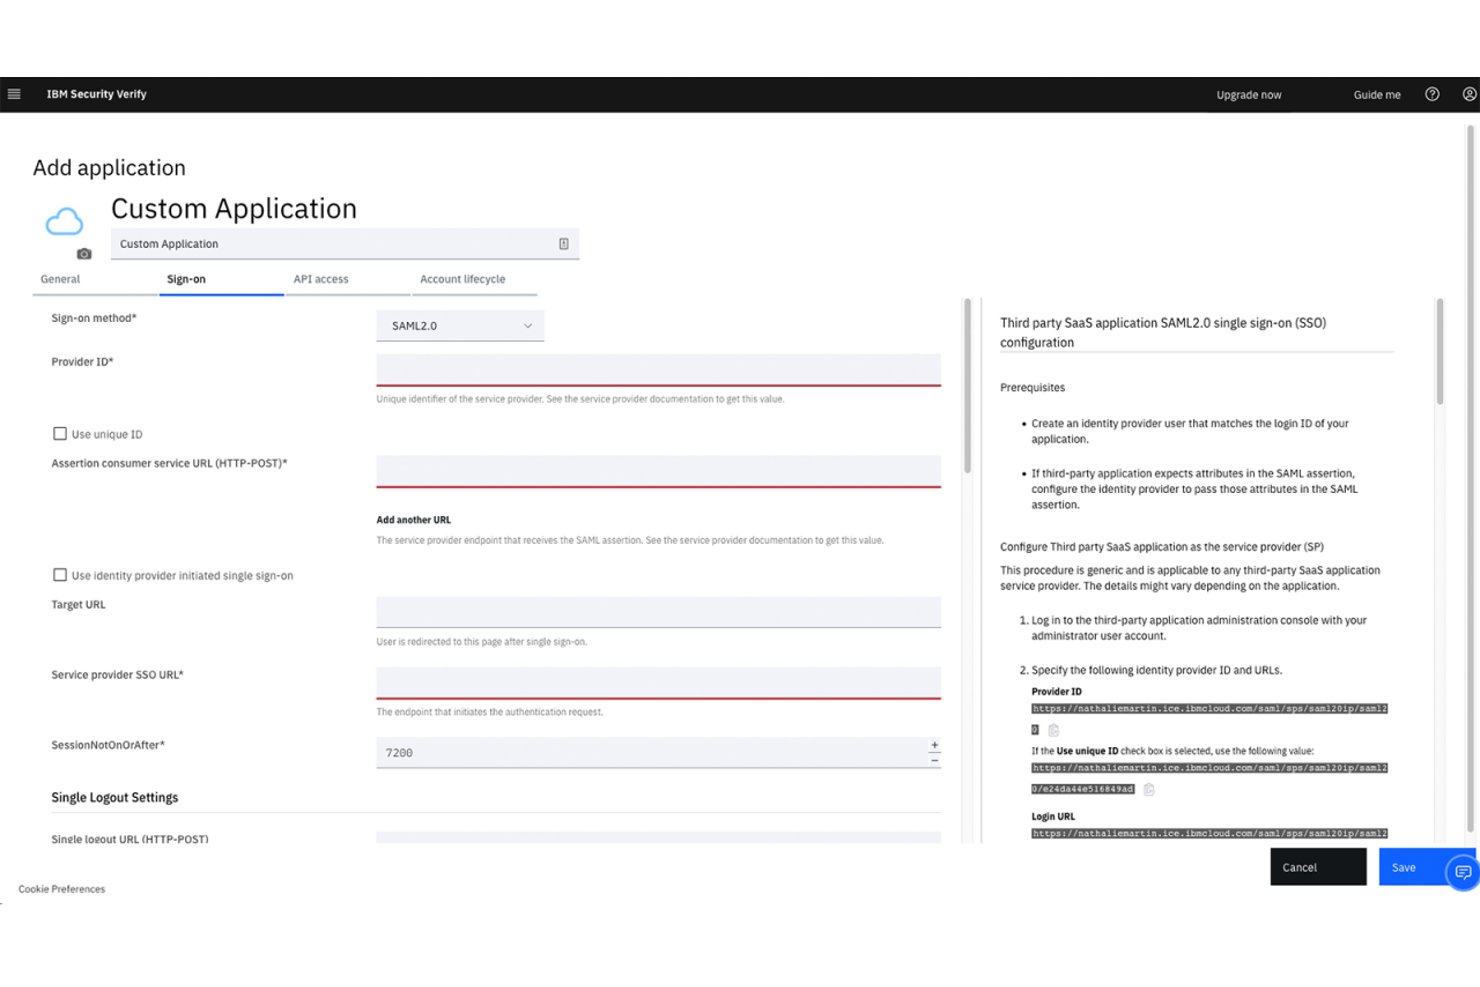
IBM Verify is an enterprise IAM platform that spans workforce and customer identity, covering MFA, SSO, adaptive access, identity governance, and privileged access management across cloud, on-premises, and hybrid environments.
Who Is IBM Verify Best For?
IBM Verify is a strong fit for large enterprises managing both employee and customer identities across cloud, on-premises, and hybrid environments.
Why I Picked IBM Verify
IBM Verify earns its spot on my shortlist because it's one of the few platforms that handles workforce IAM and customer identity in a single, unified system rather than stitching together separate products. I'm particularly drawn to its Trusteer-powered adaptive access engine, which scores authentication risk across device posture, behavior, and location simultaneously, then steps up MFA only when the risk score warrants it. Its native FIDO2 passkey and QR code login support means you can run fully passwordless flows for both employees and customers without a third-party add-on.
IBM Verify Key Features
- Identity governance: Run access certification campaigns, approval workflows, and automated provisioning and deprovisioning across SaaS and on-premises applications.
- IBM Application Gateway: Extend SSO and MFA to legacy on-premises web applications without modifying application code.
- Non-human identity management: Assign unique identities to AI agents and service accounts, with governed delegation and full audit trails.
- QRadar SIEM integration: Route authentication and access events natively into IBM QRadar for correlation, alerting, and security investigation.
IBM Verify Integrations
IBM Verify offers 100+ prebuilt application connectors, including Microsoft 365, Google Workspace, Salesforce, Slack, ServiceNow, Jira, GitHub Enterprise, and CyberArk. It supports custom integrations through SAML 2.0, OIDC, SCIM 2.0, REST APIs, and SDKs.
Pros and Cons
Pros:
- Supports on-premises, cloud, and hybrid setups
- Adaptive access engine uses real-time risk signals
- Passwordless authentication for employees and customers
Cons:
- Developer SDK options are limited
- Admin interface is dated and complex
Other Authentication Software
Here are some additional authentication software options that didn’t make it onto my shortlist, but are still worth checking out:
- RSA Security
For on-premises authentication
- Transmit Security
For AI-driven passkey and CIAM at scale
- LoginRadius
For customer identity at consumer scale
- JumpCloud
For unified identity and device access management
- FusionAuth
For developer-built customer identity
- HYPR
For phishing-resistant passwordless MFA
- Frontegg
For AI-driven risk-based auth in SaaS apps
- Rippling IT
For HR-driven identity and access control
- Beyond Identity
For phishing-resistant, passwordless MFA
- Descope
For no-code passwordless and passkey auth


How I Evaluate Authentication Software
I split my evaluation into baseline criteria every tool must meet—MFA, SSO, protocol support, directory integration, adaptive auth, and audit logging—and differentiating factors like passkey support, developer SDKs, and threat intelligence signals that separate good from great.
Core Functionality (Table Stakes for This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, using 75% as a benchmark to help assess its overall fit for the list.
- Multi-factor authentication: I evaluate the range of second-factor methods each tool supports, from basic TOTP, SMS, and push notifications to FIDO2 hardware keys, passkeys, and biometrics with per-app policy controls.
- Single sign-on: The breadth of the SSO app catalog matters, including whether it covers cloud, on-prem, and legacy apps through SAML, OIDC, or fallback methods like password vaulting.
- Standard protocol support: I check for SAML 2.0, OAuth 2.0, OpenID Connect, and SCIM at a minimum, plus protocols like LDAP and RADIUS that come up in hybrid environments.
- Directory and lifecycle management: Real-world identity sprawl means I look for automated provisioning and deprovisioning via SCIM, AD/LDAP sync, and JIT provisioning across multiple identity sources.
- Adaptive and risk-based auth: I look at how the platform handles contextual signals like device posture, location, and behavior patterns to trigger step-up MFA or block access dynamically.
- Audit logging and compliance: Detailed event logs with SIEM integration, exportable compliance reports for frameworks like SOC 2 and GDPR, and flexible retention options are what I evaluate here.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
I look for native FIDO2/WebAuthn passkey support and whether it covers both workforce and customer login flows—vendors like Okta and Microsoft Entra handle this differently depending on the SKU. Threat intelligence signals matter just as much: I check whether the platform detects breached credentials, impossible travel, and bot traffic to feed adaptive policies automatically. For SaaS teams, I evaluate B2B multi-tenant CIAM capabilities, including per-tenant SSO config and branded login experiences that let your customers manage their own users.
Beyond Features
I check whether a vendor offers cloud, private cloud, and self-hosted deployment options alongside regional data residency in the US, EU, and APAC—critical when you're navigating GDPR or sector-specific data sovereignty rules. Compliance certifications like SOC 2 Type II, ISO 27001, FedRAMP, and HIPAA BAA reduce due-diligence overhead significantly. I also evaluate total cost of ownership: how MFA and adaptive auth are gated across pricing tiers, migration tooling quality, and whether self-service password reset actually deflects help desk tickets at scale.
How to Choose Authentication Software
Which authentication platform meets your risk, integration, and compliance needs without introducing roadblocks for your users?
| If your priority is… | Look for… |
|---|---|
| Phishing-resistant MFA | FIDO2/WebAuthn biometrics and hardware keys coverage |
| Hybrid or legacy environments | Cross-protocol support (SAML, LDAP, RADIUS, OIDC) |
| Flexible user lifecycle control | Automated SCIM provisioning and multi-directory sync |
| Minimized help desk burden | Reliable self-service password reset and recovery |
| Meeting compliance requirements | Audit-ready event logs and certified data residency |
How to Vet Your Shortlist
- Run a 14-day live pilot: Deploy SSO and MFA to a small group and confirm all device types and protocols work as expected.
- Request a SIEM integration guide: Ask the vendor for current documentation to ingest logs into your existing SIEM and validate log formats.
- Perform forced deprovisioning: Remove a test user from your directory and verify—with logs—that deactivation flows to connected apps within one hour.
- Demand proof of compliance: Obtain up-to-date third-party audit reports (SOC 2 or ISO 27001) plus a written statement of regional data controls.
- Choose between platform breadth and specialty depth: Decide if you need extensive integration support for diverse environments or a narrower tool with deeper adaptive auth.
What Is Authentication Software?
Authentication software is technology that verifies the identity of users beyond a basic username and password when trying to access systems, applications, or data. It uses methods like passwords, multi-factor authentication, or biometrics like fingerprint scanning to ensure only authorized users get in. This software is an essential layer of security for IT environments, protecting sensitive resources against unauthorized access and reducing the risk of breaches from compromised credentials or malicious actors.
Features of Authentication Software
When selecting authentication software, keep an eye out for the following key features:
- Multi-factor authentication: Adds extra layers of verification beyond passwords, such as SMS OTP codes, authenticator apps, biometrics, or hardware tokens. This helps reduce unauthorized access caused by compromised credentials.
- Single sign-on: Lets users authenticate once to access many integrated apps, simplifying login experiences and streamlining password management across cloud and legacy systems.
- Standard protocol support: Integrates with common identity standards like SAML, OAuth, OpenID Connect, and SCIM. This ensures compatibility across different applications and environments, including hybrid IT setups.
- Directory and user lifecycle management: Syncs users with existing directories (Active Directory, LDAP) and automates provisioning and deprovisioning. This lets you control and audit who has access as people join, move, or leave the organization.
- Adaptive and risk-based authentication: Adjusts authentication requirements based on context like device type, user location, or login behavior. Suspicious activity can trigger step-up authentication or blocks, boosting security.
- Audit logging and reporting: Captures detailed records of authentication events, login attempts, and changes to access policies. These logs help with compliance, incident investigations, and integrating with SIEM systems.
- Self-service password reset: Allows users to securely reset forgotten passwords without involving IT support. This minimizes help desk tickets and reduces downtime for users.
- Integration with third-party applications: Supports pre-built and custom connectors to popular business apps, making it easier to extend secure authentication across your tech stack.
- Compliance and regulatory controls: Provides features and documentation to support regulatory requirements such as SOC 2, GDPR, HIPAA, and regional data residency.
- Customizable authentication policies: Enables you to set granular policies by app, group, or user. This lets you balance security and convenience according to your organization’s unique needs.
Common Authentication Software AI Features
Beyond the standard authentication software features listed above, many of these solutions are incorporating AI with features like:
- AI-driven anomaly detection: Uses machine learning to spot unusual login patterns, device changes, or access attempts that deviate from a user’s normal behavior. This helps your team catch suspicious activity early and trigger additional verification steps or alerts.
- Intelligent risk scoring: Continuously analyzes contextual signals—like location, device health, and user behavior—to assign a dynamic risk score to each authentication attempt. This lets you automate step-up authentication or block access based on real-time risk.
- Automated threat response: Leverages AI to correlate authentication events with known attack patterns and threat intelligence feeds. When a threat is detected, the system can automatically lock accounts, notify admins, or enforce stricter policies without manual intervention.
- Adaptive authentication policy tuning: Uses AI to learn from historical authentication data and recommend or automatically adjust policies. This helps you balance security and user experience by tightening controls where needed and reducing friction for low-risk users.
- Credential stuffing and bot attack prevention: Employs AI models to distinguish between legitimate users and automated bots attempting mass login attempts. The system can block or challenge suspicious traffic before it reaches your applications.
- Continuous authentication: Applies AI to monitor user behavior throughout a session—not just at login—to detect signs of account takeover or session hijacking. If risky behavior is detected, the system can prompt for re-authentication or terminate the session.
Benefits of Authentication Software
Implementing authentication software provides several benefits for your team and your business. Here are a few you can look forward to:
- Stronger access controls: Gain reliable protection against unauthorized access with features like multi-factor authentication, risk-based verification, and integration with user directories.
- Simplified user experience: Let users sign in to multiple systems with a single account using single sign-on and customizable login policies.
- Faster user onboarding and offboarding: Automate provisioning and deprovisioning, syncing with directories and apps through SCIM and JIT features to keep access current.
- Regulatory compliance support: Meet audit and compliance standards with detailed event logging, reporting, and regional data residency options.
- Reduced help desk workload: Enable users to reset passwords themselves, limiting password-related support tickets and keeping everyone productive.
- Adaptive security policies: Respond to changing threat levels in real time by using contextual risk signals and AI-driven anomaly detection.
- Integration with modern and legacy systems: Connect cloud, on-premises, and legacy applications through broad protocol support, making software fit complex IT environments.
Costs and Pricing of Authentication Software
Selecting authentication software requires an understanding of the various pricing models and plans available. Costs vary based on features, team size, add-ons, and more. The table below summarizes common plans, their average prices, and typical features included in authentication software solutions:
Plan Comparison Table for Authentication Software
| Plan Type | Average Price | Common Features |
|---|---|---|
| Free Plan | $0 | Basic multi-factor authentication, limited single sign-on, entry-level protocol support, and basic audit logs. |
| Personal Plan | $5-$10/user/month | Multi-factor authentication, single sign-on for select apps, basic protocol support, and limited user management. |
| Business Plan | $10-$25/user/month | Adaptive authentication, expanded protocol support, directory sync, better audit logging, and self-service password reset. |
| Enterprise Plan | $25-$40/user/month | Advanced user lifecycle management, risk-based authentication, SIEM integration, compliance tools, and premium support. |
Authentication Software FAQs
Here are some answers to common questions about authentication software:
How do I integrate authentication software with my existing directory services?
You usually integrate authentication software with directory services like Active Directory or LDAP using built-in connectors or sync tools. Most products support secure directory sync, automated provisioning, and real-time deprovisioning using SCIM or similar standards. Make sure the solution can handle nested groups, multiple forests, or hybrid environments if your setup is complex.
What steps can I take to ensure regulatory compliance using authentication software?
Choose software that provides audit-ready logging, compliance certifications (like SOC 2 or ISO 27001), and configurable data residency options. Regularly review authentication logs, set granular access policies, and ensure your MFA setup aligns with frameworks such as GDPR or HIPAA when needed. Request documentation and third-party audit reports during your vendor review.
Can authentication software help reduce help desk password reset tickets?
Yes, most authentication platforms offer self-service password reset features. When set up correctly, users can securely recover or reset their passwords without IT help. This minimizes downtime and frees up your help desk to focus on other priorities. Look for customizable policies and multi-factor verification during resets.
What should I test during a pilot deployment of new authentication software?
Start by rolling out single sign-on and multi-factor authentication to a small user group. Test across all device types, browsers, and supported apps. Check for protocol compatibility, directory sync, and user provisioning flows. Try forced deprovisioning and validate event logging and SIEM integration to confirm the solution meets your operational and compliance needs.
How can I balance security and user experience with adaptive authentication?
Use adaptive authentication policies that analyze risk factors like device health, geolocation, and behavior patterns. Set thresholds to trigger step-up MFA only for login attempts that look risky. This way, everyday logins remain easy for users while the software tightens controls in suspicious scenarios. Many vendors let you tune these settings for your risk appetite.