Veracode-beoordeling: voor- en nadelen, functies en prijzen uitgelegd


Veracode is an application security software for development and security teams that need to scan code, open source dependencies, and running applications for vulnerabilities across the software development lifecycle. I'd reach for it when you want a unified platform that combines SAST, DAST, SCA, and container scanning under one policy engine, rather than stitching together point tools.
Compared to Checkmarx, which leans heavily on on-prem deployments and deeper tuning work, Veracode gives you a SaaS-first setup that gets your team scanning and triaging findings faster without standing up scan infrastructure yourself.
Veracode Evaluation Summary
- Pricing upon request
- Free demo available
Waarom u onze softwareaanbevelingen kunt vertrouwen
Ons team test en beoordeelt software sinds 2012. Als technologieleiders weten we zelf hoe moeilijk — en belangrijk — het is om de juiste software te kiezen.
Voor deze gids hebben we tools geëvalueerd met behulp van praktijktests en onafhankelijk onderzoek, waarbij we tools beoordeeden aan de hand van onze selectiecriteria.
Onze reviews weerspiegelen ons menselijke redactionele oordeel, geen verkooppraatje.
Veracode Overview
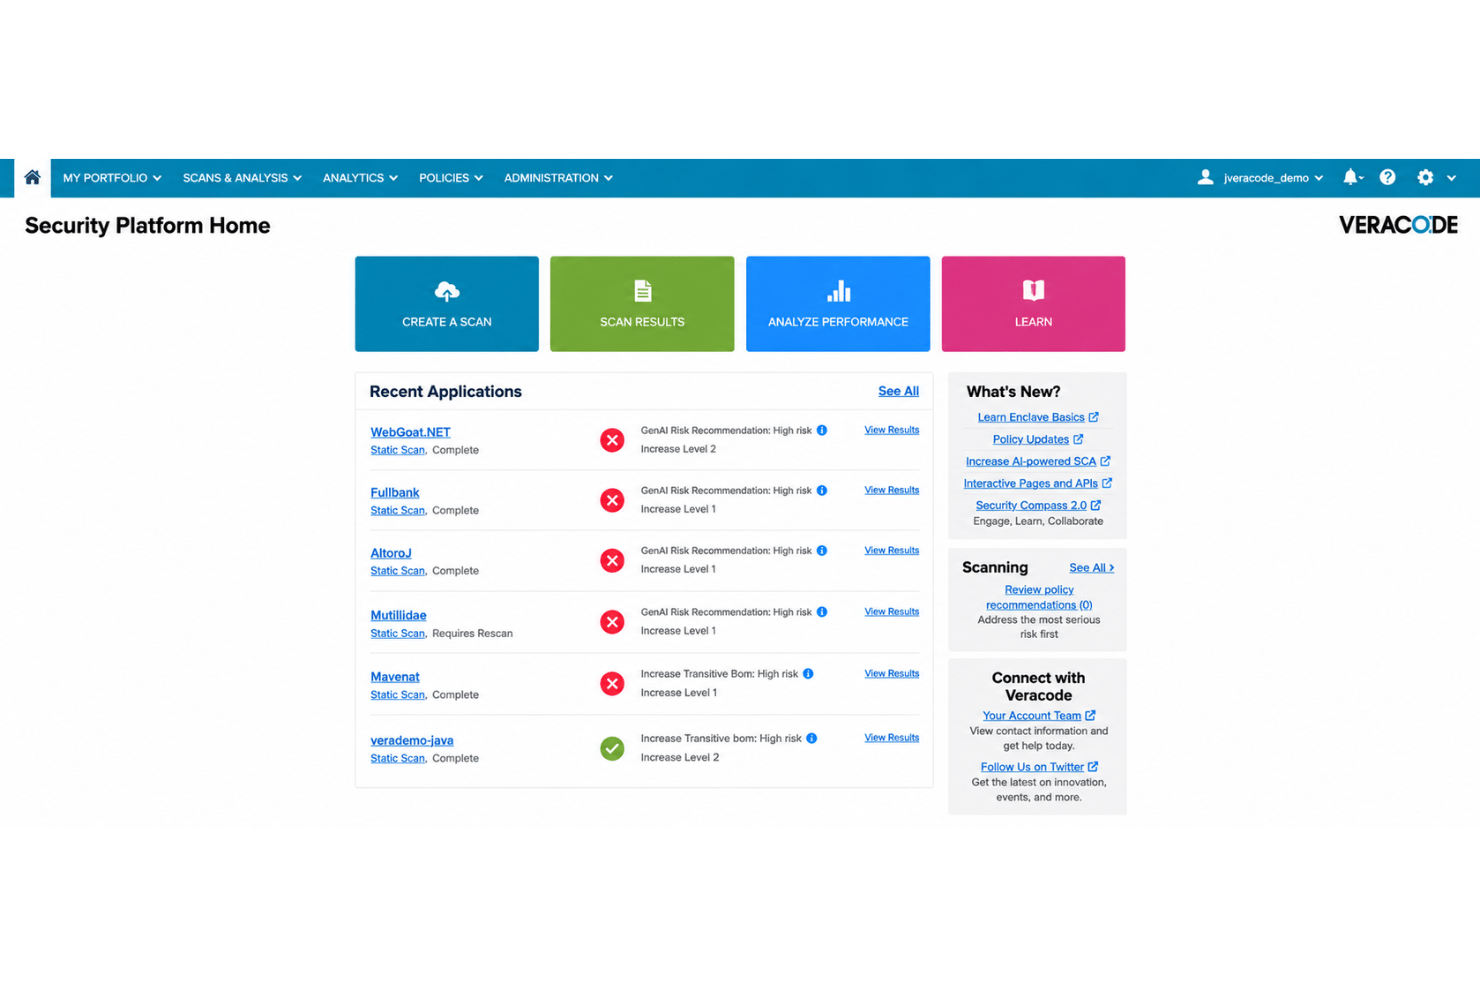
I think Veracode stands out for its SaaS-first approach, letting teams start scanning without heavy setup or infrastructure. Its all-in-one dashboard ties together static, dynamic, software composition, and container analysis, which saves time compared to juggling separate tools. I find the interface approachable, with policy management and triage features that suit larger DevSecOps and development teams. Pricing can be high for smaller teams, and limits on customization occasionally frustrate power users. Still, if you want fast onboarding, strong coverage across modern application stacks, and dependable support, Veracode should be at the top of your list for enterprise and mid-size environments.
pros
-
SaaS delivery skips on-prem setup and maintenance costs
-
Unified dashboard covers SAST, DAST, SCA, and container scanning
-
Policy management centralizes governance for large application portfolios
cons
-
Scan times can be lengthy for large codebases
-
API coverage lags behind leading competitors
-
False positives require extra manual triage effort



Our Review Methodology
How We Test & Score Tools
We’ve spent years building, refining, and improving our software testing and scoring system. The rubric is designed to capture the nuances of software selection and what makes a tool effective, focusing on critical aspects of the decision-making process.
Below, you can see exactly how our testing and scoring works across seven criteria. It allows us to provide an unbiased evaluation of the software based on core functionality, standout features, ease of use, onboarding, customer support, integrations, customer reviews, and value for money.
Core Functionality (25% of final scoring)
The starting point of our evaluation is always the core functionality of the tool. Does it have the basic features and functions that a user would expect to see? Are any of those core features locked to higher-tiered pricing plans? At its core, we expect a tool to stand up against the baseline capabilities of its competitors.
Standout Features (25% of final scoring)
Next, we evaluate uncommon standout features that go above and beyond the core functionality typically found in tools of its kind. A high score reflects specialized or unique features that make the product faster, more efficient, or offer additional value to the user.
We also evaluate how easy it is to integrate with other tools typically found in the tech stack to expand the functionality and utility of the software. Tools offering plentiful native integrations, 3rd party connections, and API access to build custom integrations score best.
Ease of Use (10% of final scoring)
We consider how quick and easy it is to execute the tasks defined in the core functionality using the tool. High scoring software is well designed, intuitive to use, offers mobile apps, provides templates, and makes relatively complex tasks seem simple.
Onboarding (10% of final scoring)
We know how important rapid team adoption is for a new platform, so we evaluate how easy it is to learn and use a tool with minimal training. We evaluate how quickly a team member can get set up and start using the tool with no experience. High scoring solutions indicate little or no support is required.
Customer Support (10% of final scoring)
We review how quick and easy it is to get unstuck and find help by phone, live chat, or knowledge base. Tools and companies that provide real-time support score best, while chatbots score worst.
Customer Reviews (10% of final scoring)
Beyond our own testing and evaluation, we consider the net promoter score from current and past customers. We review their likelihood, given the option, to choose the tool again for the core functionality. A high scoring software reflects a high net promoter score from current or past customers.
Value for Money (10% of final scoring)
Lastly, in consideration of all the other criteria, we review the average price of entry level plans against the core features and consider the value of the other evaluation criteria. Software that delivers more, for less, will score higher.
Core Features
Static Application Security Testing (SAST)
Static analysis scans source code and compiled code for security flaws during development without running the application. This helps your team catch vulnerabilities and code quality issues early before code moves to production.
Dynamic Application Security Testing (DAST)
Dynamic analysis tests live, running applications for exploitable vulnerabilities from an attacker’s perspective. You can assess web apps for common issues like SQL injection or cross-site scripting in staging or production environments.
Software Composition Analysis (SCA)
Analyze open source components to identify outdated libraries, known vulnerabilities, and license compliance issues. This helps you manage risk from third-party dependencies automatically across your entire application portfolio.
Container Security Scanning
Scan container images for vulnerabilities, configuration risks, and policy violations before deployment. Teams get actionable feedback to secure containers integrated directly into CI/CD pipelines.
Centralized Policy Management
Define and enforce security policies across multiple projects and teams through one dashboard. You can set risk thresholds, remediation targets, and track your security posture for every application in your portfolio.
Triage and Remediation Guidance
Prioritize findings by risk and get specific remediation advice for developers right in the platform. This speeds up response times and helps your team focus on the most urgent vulnerabilities.
Ease of Use
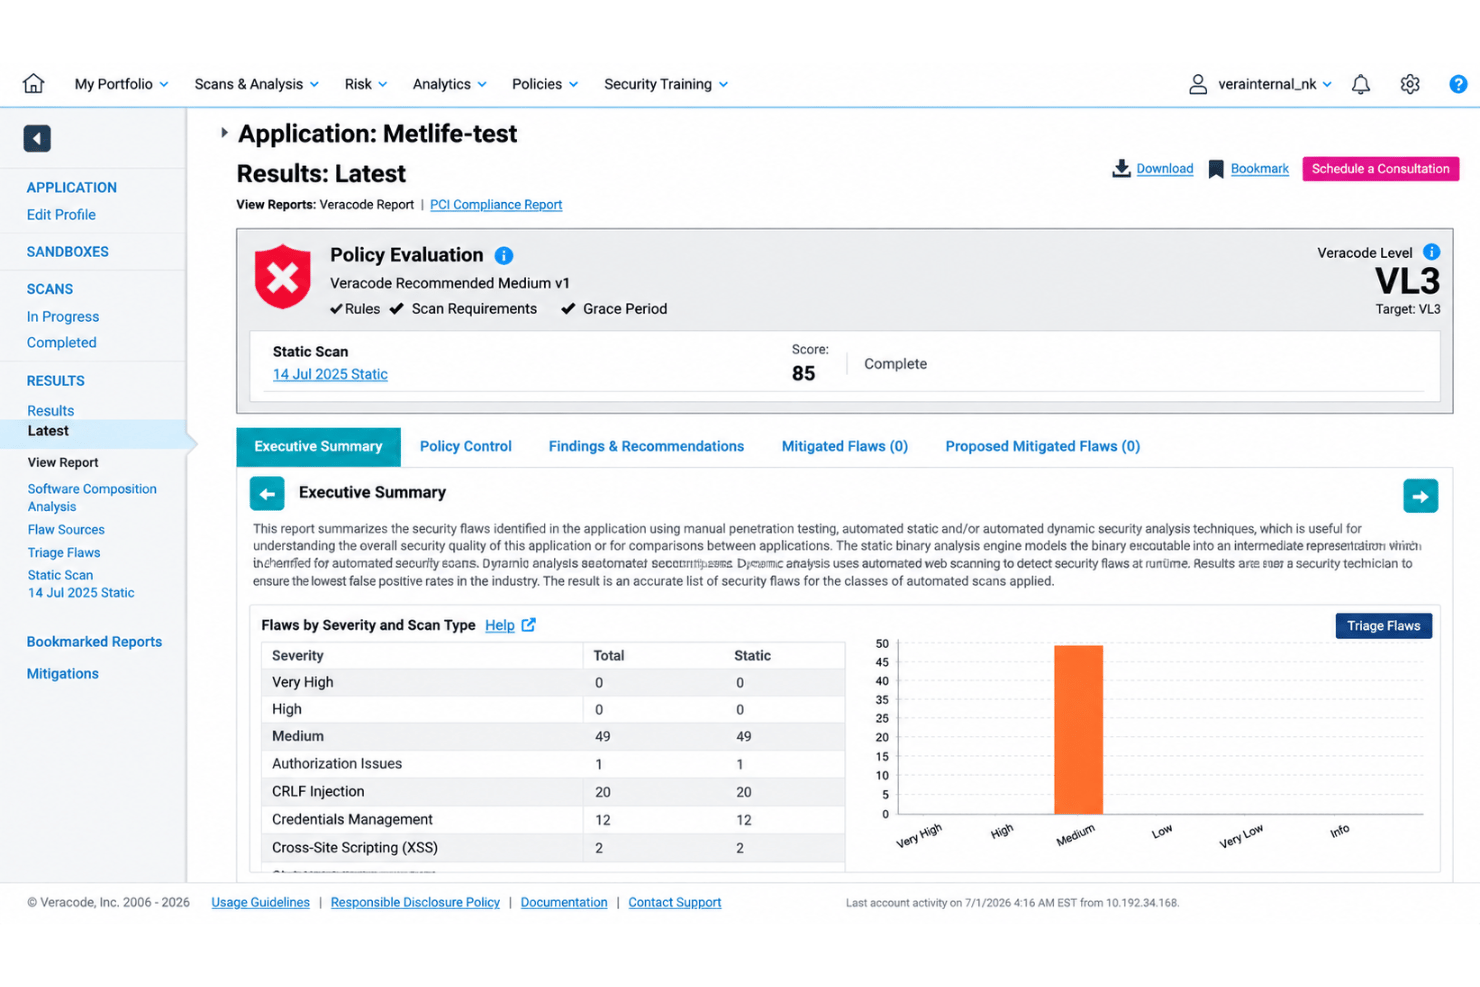
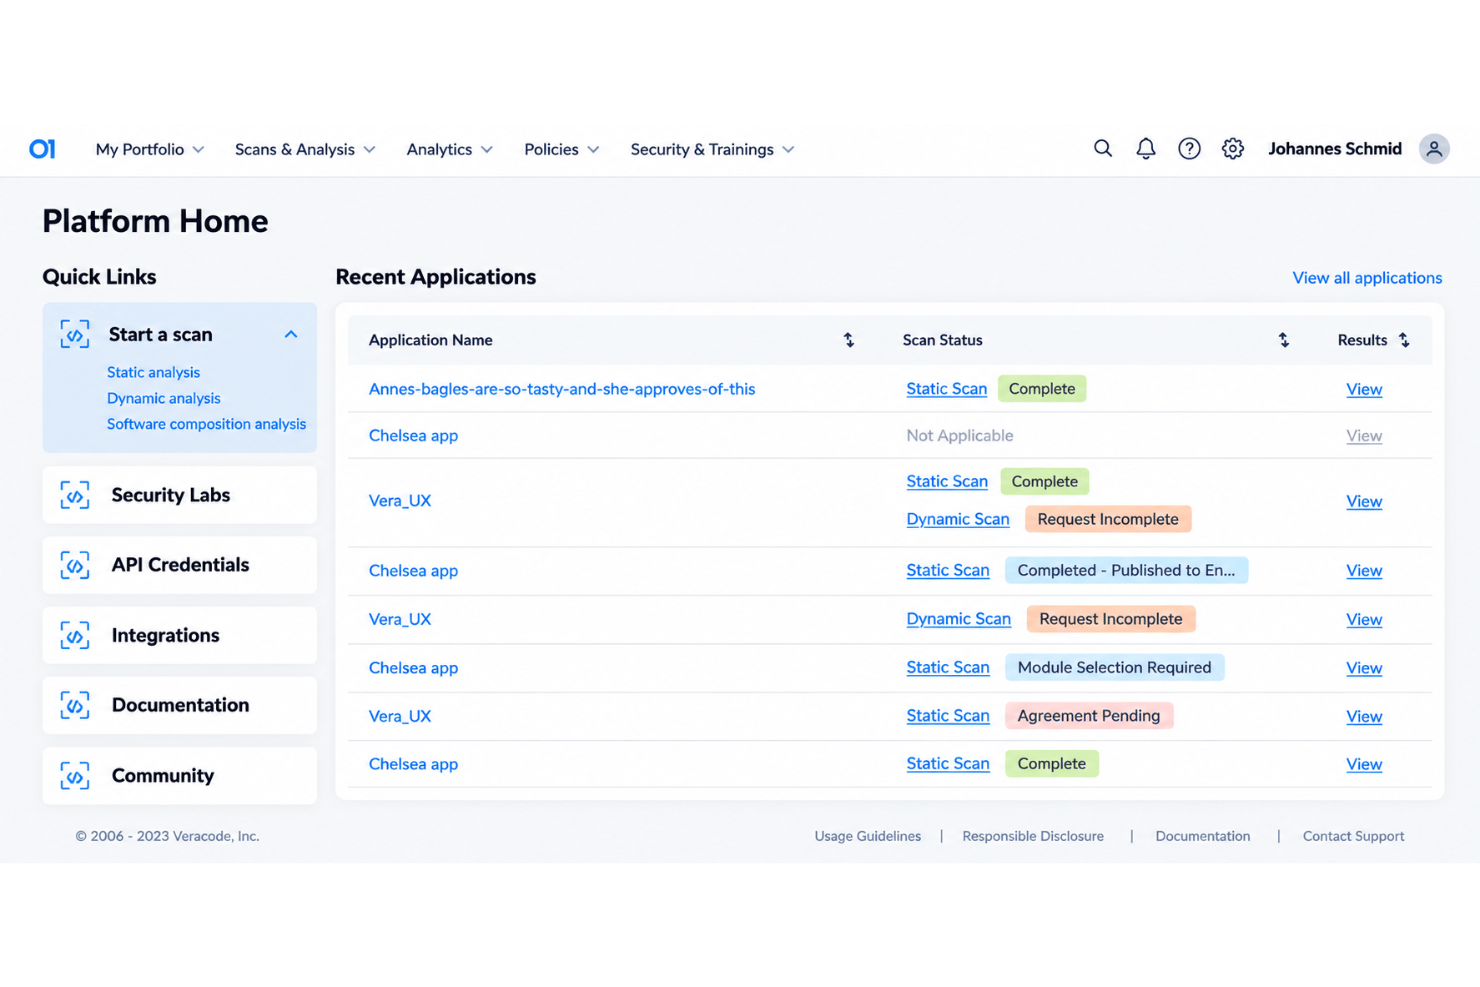
Veracode is easy to onboard for most teams, with a SaaS delivery model that skips manual setup or complex infrastructure. The dashboard brings SAST, DAST, SCA, and container scanning into one view, making it simple to manage policies and findings. Some users mention that large codebase scans take time and that false positives add extra triage, but the platform’s organized interface and clear workflows keep day-to-day usage straightforward.
Integrations
Veracode integrates with Jira, GitHub, GitLab, Azure DevOps, AWS, Bitbucket, ServiceNow, and Snyk, among others.
Veracode also provides both XML and REST API and supports integration with third-party tools for expanded connectivity.
Veracode Specs
- A/B Testing
- API
- Automated Testing
- Browser Compatibility Testing
- Bug Tracking
- Calendar Management
- CI/CD Integration
- Dashboard
- Data Export
- Data Import
- Data Visualization
- Developer Tools
- External Integrations
- History/Version Control
- Manual Testing
- Multi-User
- Notifications
- Performance Testing
- Regression Testing
- Scheduling
- Status Notifications
- Third-Party Plugins/Add-Ons