
Checkmarx-arvostelu: hyvät ja huonot puolet, ominaisuudet ja hinnoittelu
Checkmarx loistaa tietoturvaan keskittyvässä sovellustestauksessa ja tarjoaa vankkaa haavoittuvuuksien tunnistusta, joka erottaa sen kilpailijoista.

We review tools independently, and commissions help fund our testing. See our transparency policy, our methodology, or suggest a tool.
Checkmarx is an application monitoring software built around application security—covering static analysis, dynamic testing, software composition analysis, and API security across your development pipeline. I'd consider it if your team needs to identify and remediate vulnerabilities before code reaches production, not after. Compared to Veracode, Checkmarx gives security and development teams more flexibility in how they integrate scanning into existing CI/CD workflows, which makes it a more practical fit if you're working across a mix of languages, environments, and toolchains.
Checkmarx Evaluation Summary
4.2/5
- Pricing upon request
- Free demo available
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Checkmarx Overview
In my opinion, Checkmarx One is a solid choice for teams that require a cloud-native application security (AppSec) testing suite. It excels in vulnerability detection and offers strong integration capabilities. Compared to others, its interface is intuitive, but onboarding might take a bit longer for complex environments. The pricing is competitive, making it suitable for mid-sized to large enterprises. However, smaller teams with limited budgets might find it pricey. If security is your top priority, Checkmarx is worth considering.
Pros
- It offers excellent security vulnerability detection for your applications.
- The user interface is intuitive and easy for your team to navigate.
- It provides comprehensive security analysis to protect your code.
Cons
- Onboarding can take longer than expected for complex testing environments.
- Customer support response times might not meet your expectations.
- It may have a steeper learning curve for new users in your team.
Is Checkmarx Right For Your Needs?
Who Would be a Good Fit for Checkmarx?
Checkmarx One is a great fit for IT departments in industries like finance, healthcare, and technology, where application security is a top priority. If your team needs robust vulnerability detection and comprehensive security analysis, Checkmarx delivers. Its user-friendly dashboard helps development, security, and operations (DevSecOps)teams navigate efficiently. Both medium and large enterprises will find Checkmarx useful to enable security scanning throughout the software development lifecycle (SDLC).
- Finance SectorChief information security officers (CISOs) can benefit from its strong security features that protect sensitive financial data.
- Healthcare IndustryCheckmarx helps your team secure patient data with its rigorous vulnerability detection.
- Technology CompaniesSoftware development teams will appreciate Checkmarx’s comprehensive code security analysis and support for continuous integration and continuous deployment (CI/CD) workflow.
- Government AgenciesFor safeguarding confidential data, Checkmarx offers reliable security testing tools.
- Large EnterprisesIt provides extensive features that meet the security demands of large-scale software infrastructure and DevSecOps workflow.
- Security TeamsCheckmarx’s focus on application vulnerabilities makes it a valuable tool for security-focused teams.
Who Would be a Bad Fit for Checkmarx?
Checkmarx One might not be ideal for small businesses with limited budgets or resources. Its comprehensive security features and onboarding process can be overwhelming for teams without dedicated IT staff. If your team is looking for a simple, quick-to-implement solution, Checkmarx's depth might be more than you need. Additionally, startups or companies with minimal security concerns might find its extensive capabilities unnecessary.
- Small StartupsYour team might find Checkmarx too complex and costly for basic security needs.
- FreelancersIf you’re a solo developer, you’ll likely find Checkmarx’s features excessive.
- Non-Technical TeamsTeams without IT support might struggle with Checkmarx’s technical setup and use.
- Budget-Conscious CompaniesIf your company prioritizes cost over comprehensive security, Checkmarx may not fit your budget.
- Retail BusinessesSmall retailers with minimal cybersecurity needs may not need Checkmarx’s extensive features.
- Educational InstitutionsSchools or universities with basic security requirements might not benefit from Checkmarx’s advanced functionalities.
Our Review Methodology
How We Test & Score Tools
We’ve spent years building, refining, and improving our software testing and scoring system. The rubric is designed to capture the nuances of software selection and what makes a tool effective, focusing on critical aspects of the decision-making process.
Below, you can see exactly how our testing and scoring works across seven criteria. It allows us to provide an unbiased evaluation of the software based on core functionality, standout features, ease of use, onboarding, customer support, integrations, customer reviews, and value for money.
Core Functionality (25% of final scoring)
The starting point of our evaluation is always the core functionality of the tool. Does it have the basic features and functions that a user would expect to see? Are any of those core features locked to higher-tiered pricing plans? At its core, we expect a tool to stand up against the baseline capabilities of its competitors.
Standout Features (25% of final scoring)
Next, we evaluate uncommon standout features that go above and beyond the core functionality typically found in tools of its kind. A high score reflects specialized or unique features that make the product faster, more efficient, or offer additional value to the user.
We also evaluate how easy it is to integrate with other tools typically found in the tech stack to expand the functionality and utility of the software. Tools offering plentiful native integrations, 3rd party connections, and API access to build custom integrations score best.
Ease of Use (10% of final scoring)
We consider how quick and easy it is to execute the tasks defined in the core functionality using the tool. High scoring software is well designed, intuitive to use, offers mobile apps, provides templates, and makes relatively complex tasks seem simple.
Onboarding (10% of final scoring)
We know how important rapid team adoption is for a new platform, so we evaluate how easy it is to learn and use a tool with minimal training. We evaluate how quickly a team member can get set up and start using the tool with no experience. High scoring solutions indicate little or no support is required.
Customer Support (10% of final scoring)
We review how quick and easy it is to get unstuck and find help by phone, live chat, or knowledge base. Tools and companies that provide real-time support score best, while chatbots score worst.
Customer Reviews (10% of final scoring)
Beyond our own testing and evaluation, we consider the net promoter score from current and past customers. We review their likelihood, given the option, to choose the tool again for the core functionality. A high scoring software reflects a high net promoter score from current or past customers.
Value for Money (10% of final scoring)
Lastly, in consideration of all the other criteria, we review the average price of entry level plans against the core features and consider the value of the other evaluation criteria. Software that delivers more, for less, will score higher.
Core Features
Static Application Security Testing (SAST): Checkmarx SAST scans your codebases and binaries for vulnerabilities before deployment. It helps development and operation (DevOps) teams catch security issues early in the development process.
Software Composition Analysis (SCA): SCA identifies open-source components in your applications and checks for known vulnerabilities. Your team can manage and mitigate risks efficiently.
Interactive Application Security Testing (IAST): IAST tests your apps in real-time, identifying vulnerabilities during runtime. It provides your team with actionable insights for immediate fixes.
Dynamic Application Security Testing (DAST): Run scans to identify runtime vulnerabilities, enhancing application and API security.
Custom Policies: You can tailor security policies to fit your specific needs. This flexibility allows your team to focus on what's most important to your security strategy.
Detailed Reporting: Checkmarx provides comprehensive reports on vulnerabilities and their fixes. Your team gets clear visibility into security issues and solutions.
Ease of Use
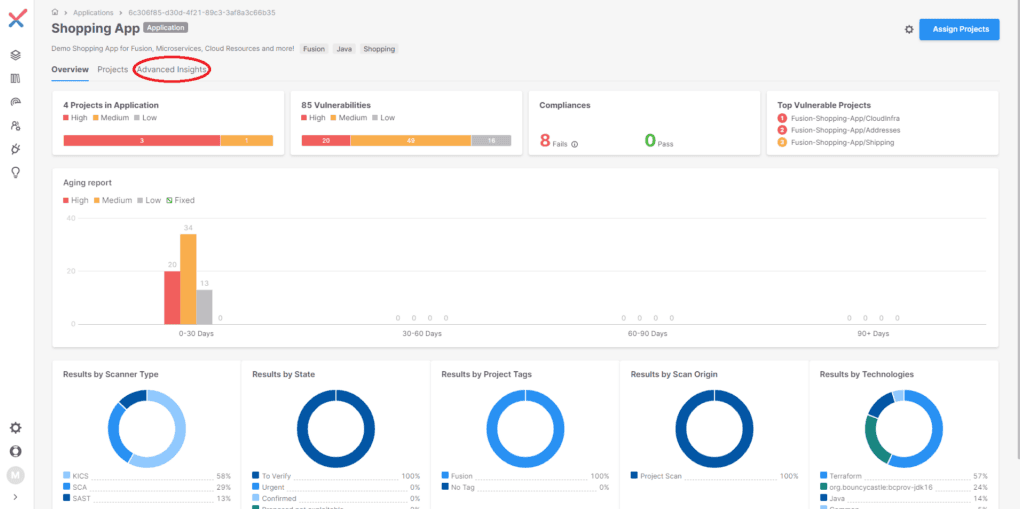
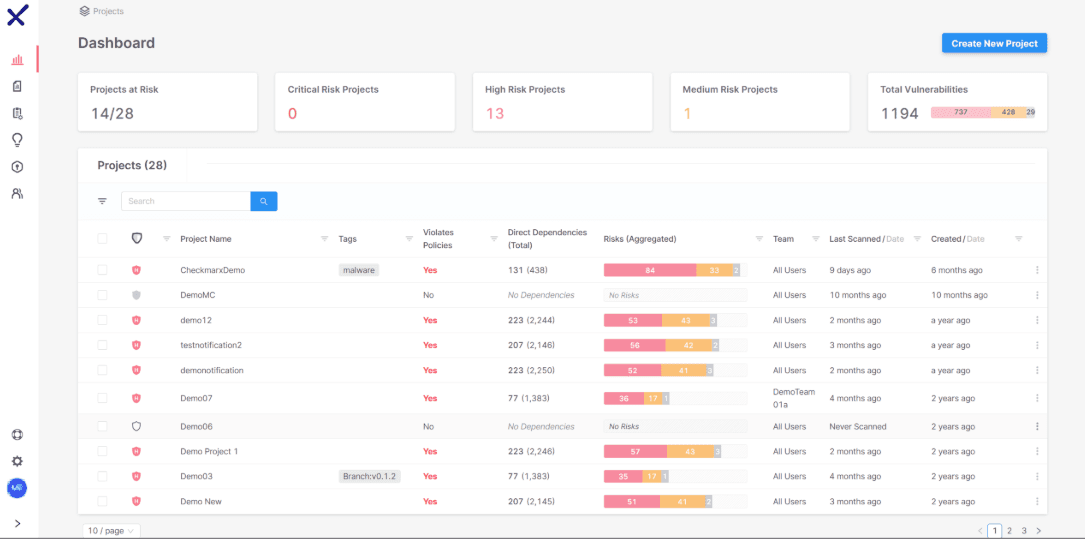
Checkmarx has an intuitive interface that makes it easier for your team to navigate compared to more complex solutions. While the setup might take some time, once you're up and running, the features are straightforward to use. The visual workflow builder simplifies process customization, allowing your team to adapt it to your needs quickly. User reviews highlight that the learning curve is manageable. However, there are incidents of false positives, which might complicate remediation efforts.
Integrations
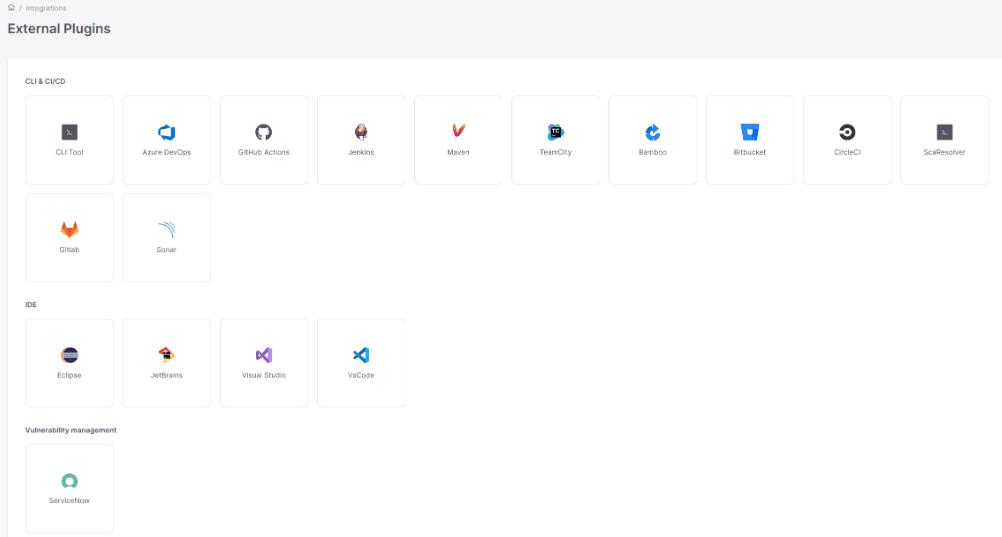
Checkmarx integrates with AWS, Azure, Sonarqube, GitHub, GitLab, Bitbucket, Jenkins, CircleCI, Jira, IntelliJ, and more.
Checkmarx also offers an application programming interface (API) and connects with third-party integration tools.
Checkmarx Specs
- A/B Testing: Yes
- API: Yes
- Automated Testing: Yes
- Browser Compatibility Testing: Yes
- Bug Tracking: Yes
- Calendar Management: No
- CI/CD Integration: Yes
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- Data Visualization: Yes
- Developer Tools: Yes
- External Integrations: Yes
- History/Version Control: Yes
- Manual Testing: Yes
- Multi-User: Yes
- Notifications: Yes
- Performance Testing: Yes
- Regression Testing: Yes
- Scheduling: No
- Status Notifications: Yes
- Third-Party Plugins/Add-Ons: No


