
SentinelOne Bewertung: Vorteile, Nachteile, Funktionen und Preise erklärt
SentinelOne überzeugt durch autonome Bedrohungserkennung und -abwehr und bietet einen robusten Schutz sowie einfache Bedienung, eignet sich jedoch am besten für Unternehmen, die Automatisierung gegenüber manueller Steuerung bevorzugen.

Wir bewerten Tools unabhängig; Provisionen helfen, unsere Tests zu finanzieren. Siehe unsere Transparenzrichtlinie und unsere Methodik.
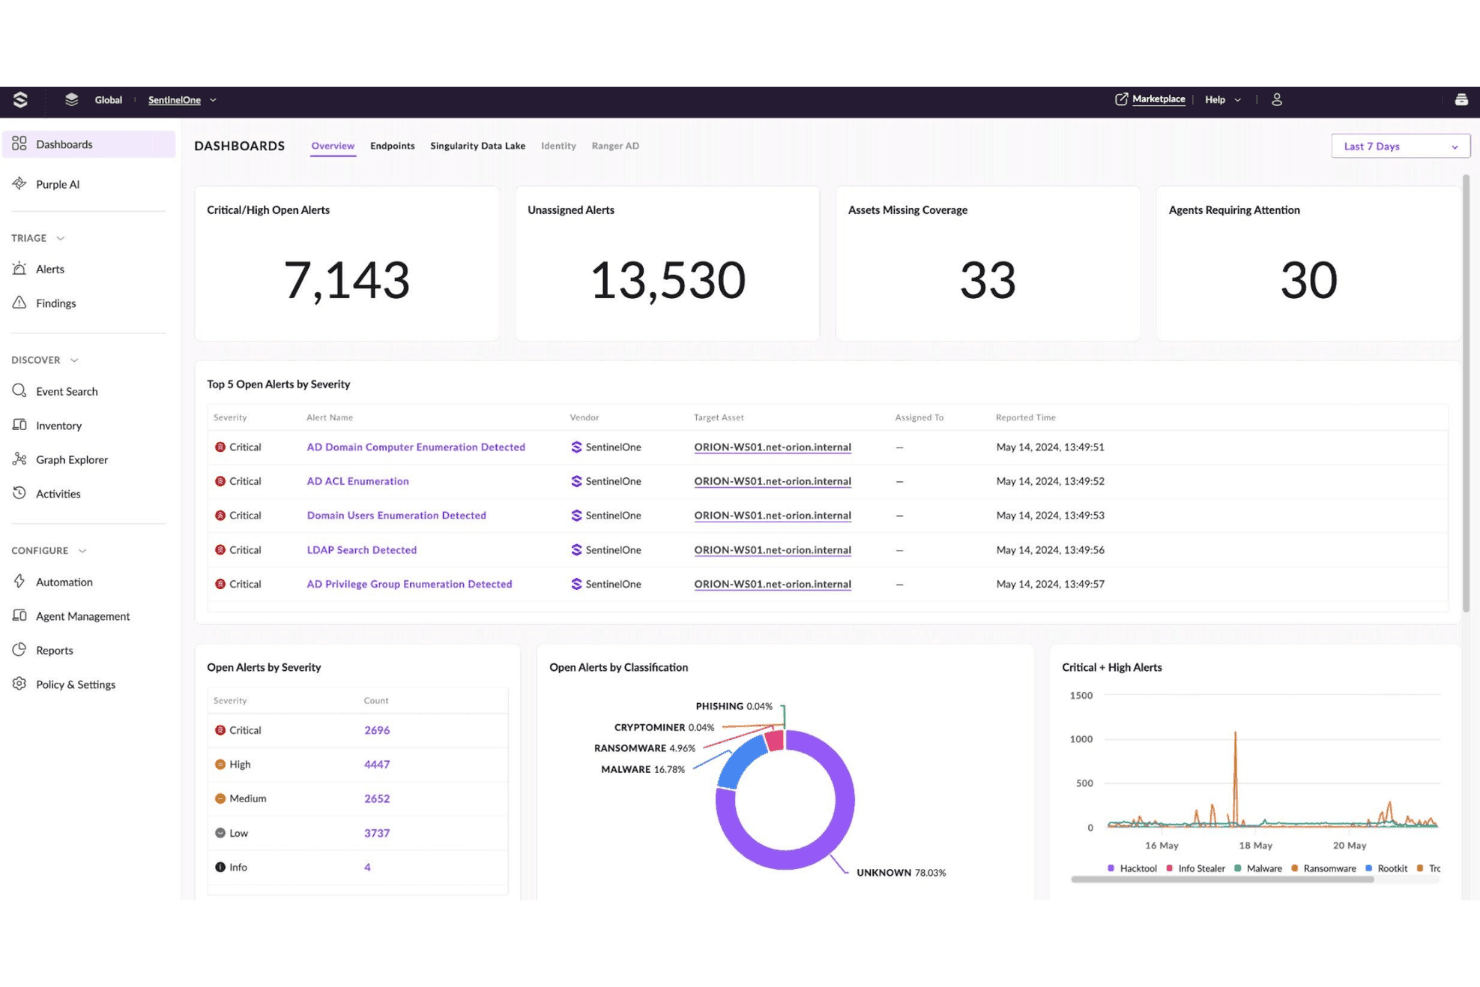
SentinelOne is a cybersecurity software built around autonomous AI-driven endpoint detection and response, covering endpoints, cloud workloads, identity, and network data from a single platform. I'd consider it if your team needs threat detection and automated remediation without depending heavily on analyst intervention at every step. If you're weighing it against CrowdStrike, SentinelOne tends to be the stronger pick when you want faster autonomous response with less reliance on cloud connectivity and human triage—particularly useful for teams running lean security operations.
SentinelOne Evaluation Summary
4.7/5
- From $179.99/endpoint (billed annually)
- Free demo available
Warum Sie unseren Software-Empfehlungen vertrauen können
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Unser Team testet und bewertet Software seit 2012. Als Tech-Führungskräfte wissen wir selbst, wie schwierig – und wichtig – es ist, die richtige Software auszuwählen.
Für diesen Leitfaden haben wir Tools mithilfe von praktischen Tests und unabhängiger Recherche bewertet und dabei unsere Bewertungskriterien angewendet.
Unsere Bewertungen spiegeln unser menschliches redaktionelles Urteilsvermögen wider, keine Verkaufsstrategie.
Expertenprüfer:
- Paulo Gardini MiguelTech-Direktor
 Tim FisherVP für KI
 Gabriel RosasTech Lead & Software-Architekt
 Christhian GruhnTech Lead & Plattform-Architekt

SentinelOne Overview
In my experience, SentinelOne delivers as an endpoint detection and response (EDR) solution, with a clean interface and robust functionality. Its AI-driven automation and broad integration options set it apart for teams seeking hands-off protection, though pricing can be higher than some alternatives and advanced manual controls are less granular. I think it's a strong choice for organizations prioritizing automation, endpoint security, and rapid incident response—especially in environments with limited security staff or high endpoint diversity. If you're judging by ease of use and automation, SentinelOne is tough to beat.
Pros
- AI-driven detection stops advanced threats quickly
- Automated rollback restores endpoints after ransomware attacks
- Minimal system impact on user devices
Cons
- Higher cost than many competitors
- Occasional false positives require manual review
- Console outages reported during updates
Is SentinelOne Right For Your Needs?
Who Would be a Good Fit for SentinelOne?
SentinelOne is a strong choice for organizations that need autonomous threat detection, rapid response, and scalable protection across diverse endpoints. I think it's especially well-suited for industries with strict compliance needs, companies with distributed workforces, and teams with limited security staff. SentinelOne's AI-driven automation, ransomware rollback, and minimal device impact make it a practical fit for environments where speed and reliability are essential. User reviews consistently highlight the platform's machine learning capabilities and response capabilities as key differentiators for mid-to-large security operations.
- Healthcare ProvidersSentinelOne's automated response and compliance features help protect sensitive patient data.
- Financial ServicesReal-time threat detection supports strict regulatory requirements and high-value assets.
- Remote WorkforcesCloud-based management and low device impact suit distributed teams.
- Education InstitutionsAutomated rollback and easy deployment help protect large, diverse device fleets.
- IT DepartmentsCentralized console and broad OS support simplify endpoint management.
- Mid-Size EnterprisesScalable licensing and automation reduce the need for large security teams.
Who Would be a Bad Fit for SentinelOne?
SentinelOne may not be the best fit for organizations with tight budgets, highly specialized manual security workflows, or those needing deep integration with legacy systems. If your team relies on granular manual controls or has minimal endpoints to protect, you might find SentinelOne's automation and pricing less appealing compared to other EDR solutions.
- Small NonprofitsHigher pricing and advanced features may exceed basic network security needs.
- Legacy System OperatorsLimited support for outdated OS versions can hinder deployment.
- Highly Regulated GovernmentSome agencies require on-premises solutions SentinelOne doesn't offer.
- Micro StartupsCost and feature set may be overkill for very small teams.
- Manual-First SOC TeamsAutomation focus limits deep manual investigation and tuning.
- Retail Chains With POSPOS-specific security needs may require more specialized solutions.
Unsere Bewertungsmethodik
Wie wir Werkzeuge testen & bewerten
Wir haben Jahre damit verbracht, unser System zur Softwareprüfung und -bewertung aufzubauen, zu verfeinern und zu verbessern. Das Bewertungsraster ist darauf ausgelegt, die Feinheiten der Softwareauswahl und Effektivität eines Tools einzufangen, wobei wir uns auf kritische Aspekte des Entscheidungsprozesses konzentrieren.
Nachfolgend sehen Sie genau, wie unser Test- und Bewertungssystem anhand von sieben Kriterien funktioniert. Es ermöglicht uns eine unparteiische Bewertung der Software basierend auf Grundfunktionalität, besonderen Funktionen, Benutzerfreundlichkeit, Onboarding, Kundensupport, Integrationen, Kundenbewertungen und Preis-Leistungs-Verhältnis.
Grundfunktionalität (25 % der Endbewertung)
Der Ausgangspunkt unserer Bewertung ist immer die Grundfunktionalität des Werkzeugs. Verfügt es über die grundlegenden Funktionen und Merkmale, die ein Benutzer erwarten würde? Sind grundlegende Funktionen auf höherpreisige Tarife beschränkt? Im Kern erwarten wir, dass ein Tool den Basisfähigkeiten seiner Konkurrenten standhält.
Besondere Features (25 % der Endbewertung)
Anschließend bewerten wir ungewöhnliche, herausragende Funktionen, die über die typische Grundfunktionalität von Tools dieser Art hinausgehen. Eine hohe Bewertung zeigt spezialisierte oder einzigartige Eigenschaften, die das Produkt schneller, effizienter oder für den Nutzer wertvoller machen.
Wir bewerten außerdem, wie einfach sich das Tool mit anderen üblichen Werkzeugen im Technologie-Stack integrieren lässt, um die Funktionalität und den Nutzen der Software zu erweitern. Tools mit vielen nativen Integrationen, Drittanbieter-Anbindungen und API-Zugang zur Erstellung kundenspezifischer Integrationen erhalten die besten Bewertungen.
Benutzerfreundlichkeit (10 % der Endbewertung)
Wir betrachten, wie schnell und einfach Aufgaben aus dem Bereich der Grundfunktionalität mit dem Tool erledigt werden können. Gut bewertete Software ist durchdacht gestaltet, intuitiv bedienbar, bietet mobile Apps, Vorlagen und lässt relativ komplexe Aufgaben einfach erscheinen.
Onboarding (10 % der Endbewertung)
Wir wissen, wie wichtig die schnelle Einführung eines neuen Tools für das Team ist, daher bewerten wir, wie leicht sich ein Werkzeug mit minimalem Training erlernen und nutzen lässt. Wir bewerten, wie schnell ein Teammitglied ohne Vorerfahrung anfangen kann. Hoch bewertete Lösungen benötigen wenig bis gar keine Unterstützung.
Kundensupport (10 % der Endbewertung)
Wir prüfen, wie schnell und einfach man bei Problemen Hilfe per Telefon, Live-Chat oder Wissensdatenbank erhält. Tools und Anbieter mit Echtzeit-Support werden besser bewertet, während Chatbots schlechter abschneiden.
Kundenbewertungen (10 % der Endbewertung)
Neben unserer eigenen Prüfung beziehen wir den Net Promoter Score aktueller und ehemaliger Kunden mit ein. Wir bewerten, wie wahrscheinlich es ist, dass sie sich erneut für das Werkzeug entscheiden würden. Hoch bewertete Software weist einen hohen Net Promoter Score auf.
Preis-Leistungs-Verhältnis (10 % der Endbewertung)
Abschließend vergleichen wir unter Berücksichtigung aller Kriterien den durchschnittlichen Preis der Einstiegspakete mit den Grundfunktionen und bewerten den Mehrwert aus den anderen Bewertungsbereichen. Software, die mehr fürs gleiche Geld bietet, schneidet besser ab.
Core Features
Autonomous Threat Detection
SentinelOne uses AI to identify and stop threats in real time without human intervention. This reduces response times and helps streamline vulnerability management.
Ransomware Rollback
The platform can automatically restore files and system states after a ransomware attack. This rollback feature minimizes downtime and data loss for affected endpoints.
Behavioral AI Engine
SentinelOne uses machine learning to analyze device and user behavior and spot suspicious activity. It adapts to new threats, catching malware that signature-based tools might miss.
Automated Remediation
When a threat is detected, SentinelOne can isolate, kill, and remove malicious files automatically. This limits the impact of attacks and reduces manual workload for IT teams.
Centralized Management Console
Admins manage all endpoints and policies from a single, cloud-based dashboard. This makes it easy to monitor, configure, and respond across large environments.
Device Control
SentinelOne lets you set policies for USB and peripheral device usage. This helps prevent data exfiltration and blocks unauthorized hardware access.
Ease of Use
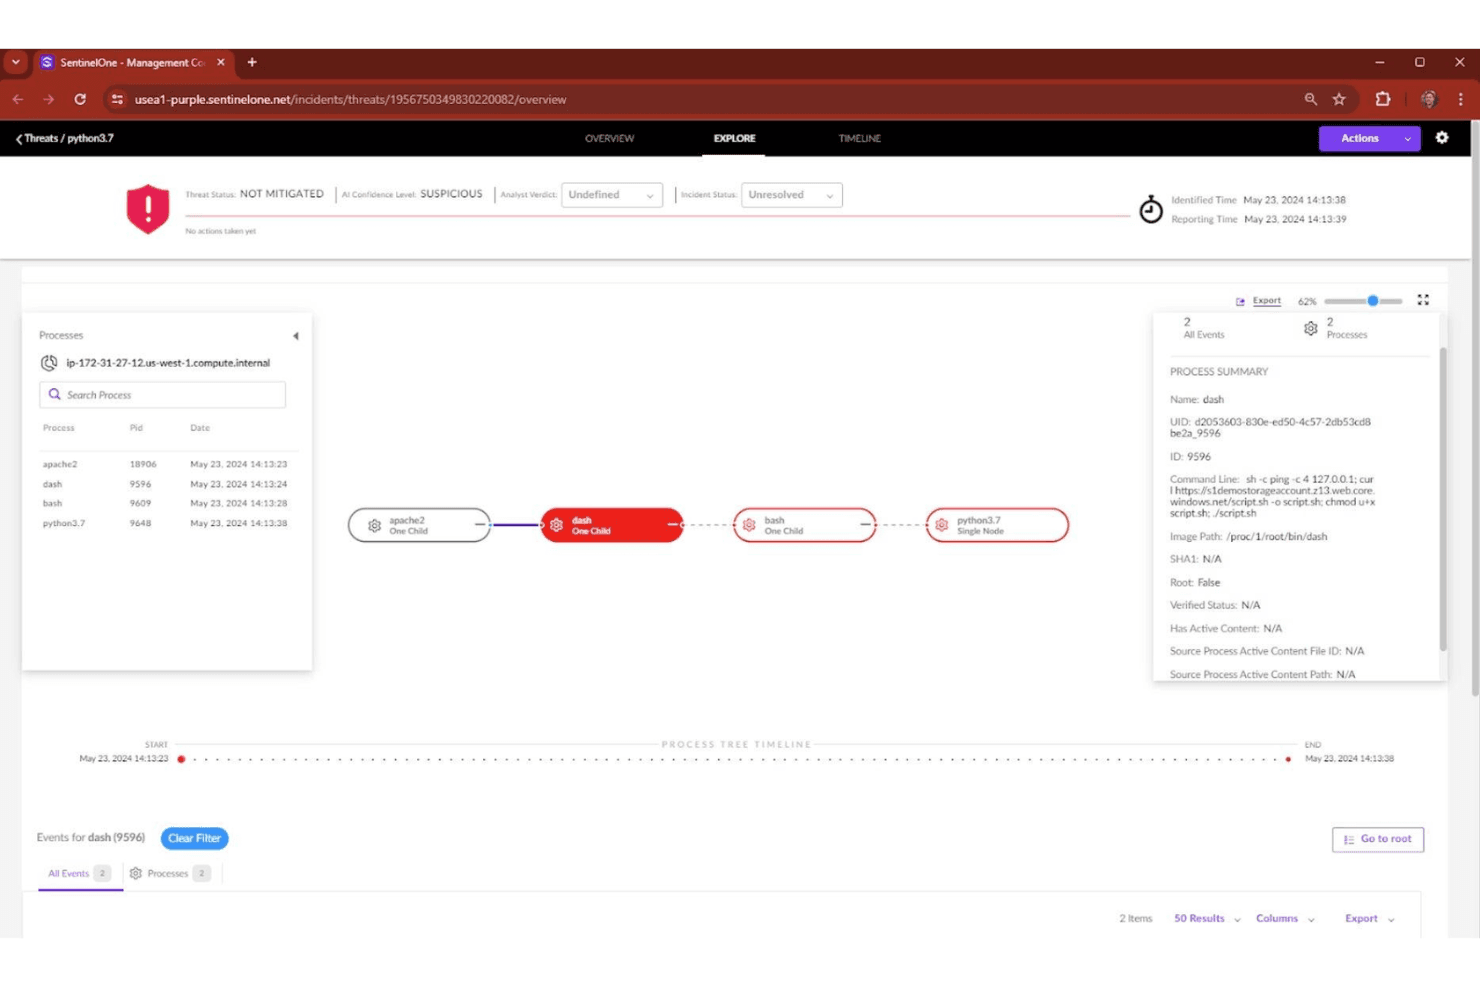
SentinelOne is widely praised for its intuitive interface and straightforward deployment, making it accessible even for teams without deep security expertise. The centralized console simplifies monitoring and policy management across many endpoints. Automated responses and clear visualizations reduce manual effort and speed up investigations. I think most users will find the platform easy to navigate, with helpful documentation and responsive support that further smooth out the onboarding process.
Integrations
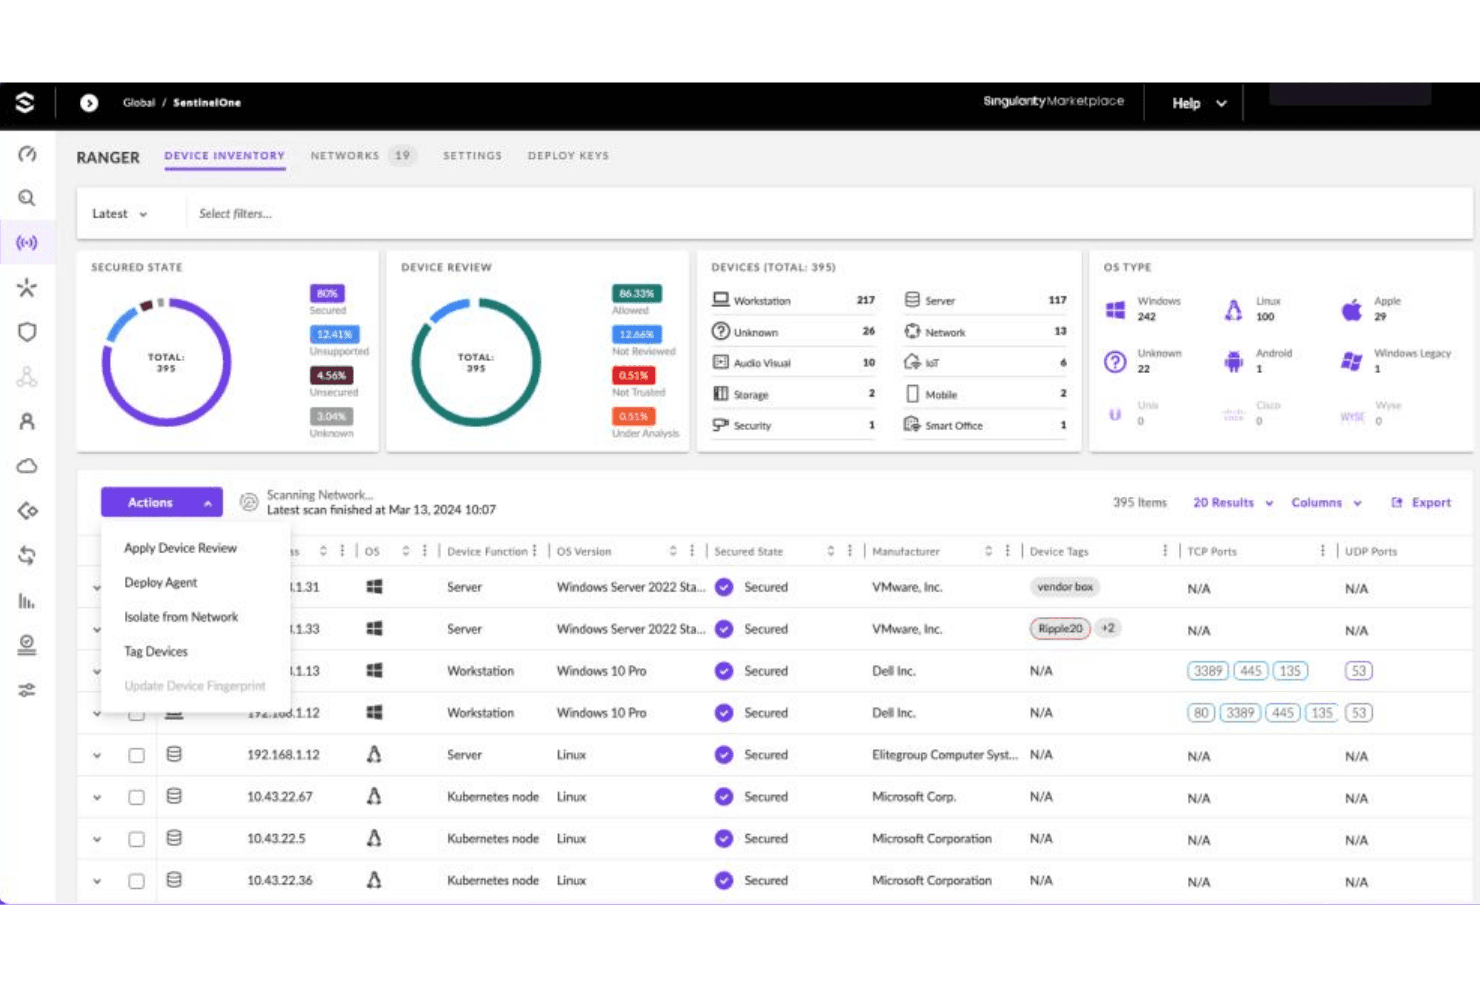
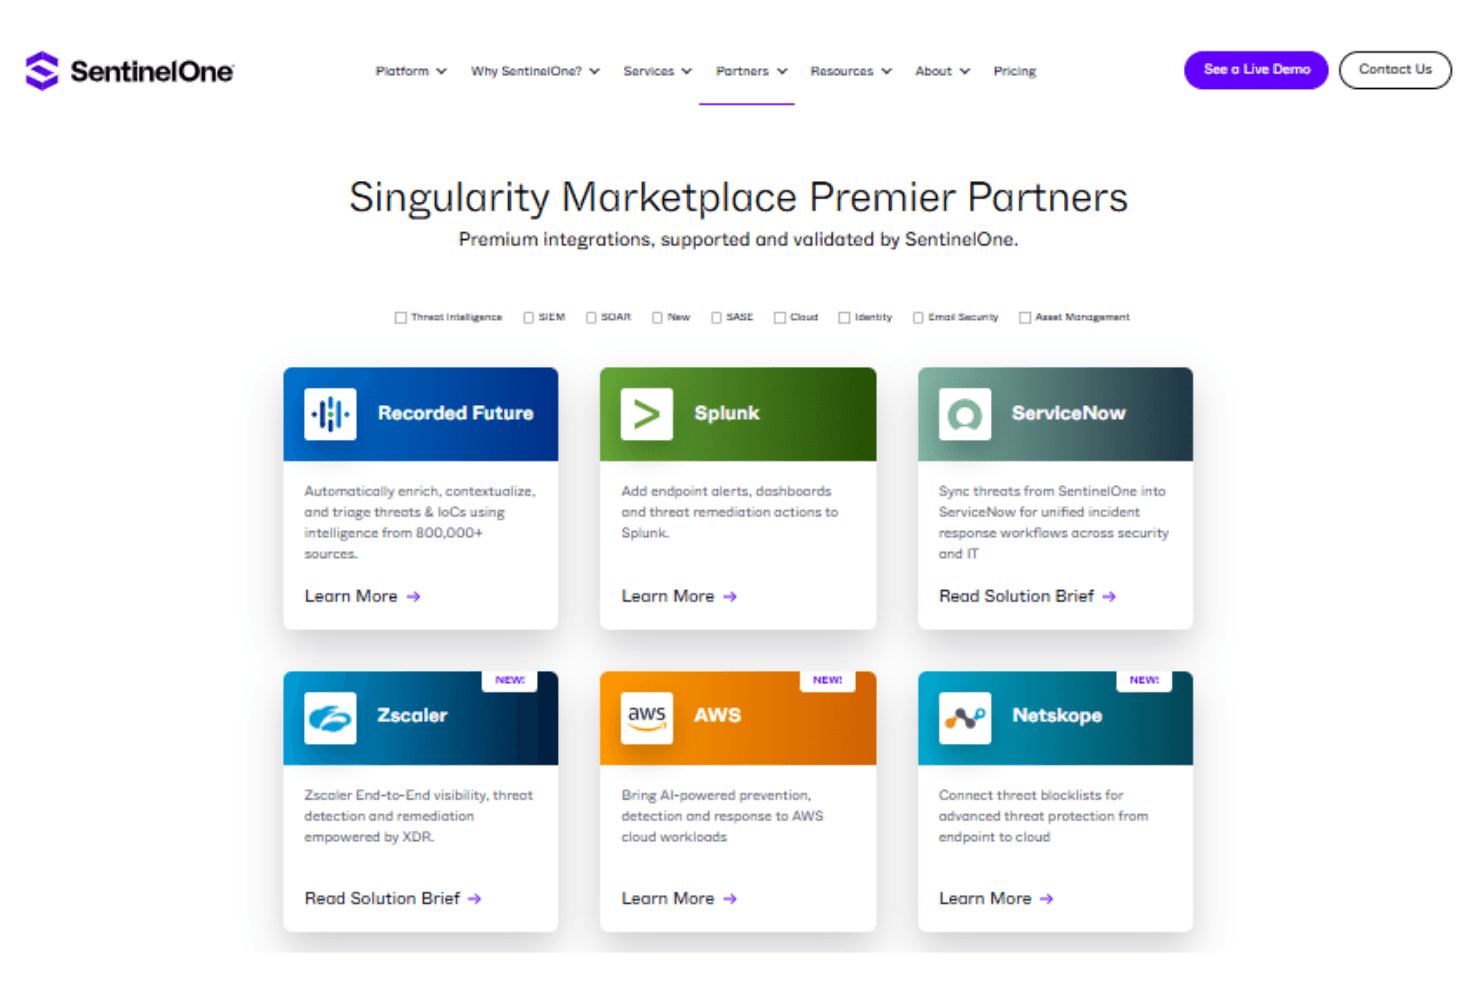
SentinelOne integrates with Splunk, Zscaler, AWS, Netskope, Okta, and IBM Security, among others.
SentinelOne also offers a robust API and connects with third-party integration tools through its Singularity Marketplace.
SentinelOne Specs
- 2-Factor Authentication: Yes
- Access Management: Yes
- Anti-Virus: Yes
- API: Yes
- Audit Management: Yes
- Audit Trail: Yes
- Batch Permissions & Access: Yes
- Compliance Tracking: Yes
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- DDoS Protection: Yes
- External Integrations: Yes
- File Sharing: Yes
- File Transfer: Yes
- Firewall: Yes
- Incident Management: Yes
- Malware Protection: Yes
- Multi-User: Yes
- Notifications: Yes
- Password & Access Management: Yes
- Policy Management: Yes
- Real-time Alerts: Yes
- Report & Compliance: Yes
- Risk Assessment: Yes
- Security Migration: Yes
- Threat Detection: Yes
- Workflow Management: Yes


