

Programvare for risikobasert sårbarhetshåndtering hjelper deg med å identifisere, prioritere og utbedre sikkerhetstrusler ved å fokusere på reell forretningsrisiko, ikke bare teknisk alvorlighetsgrad. Hvis du er lei av generiske sårbarhetslister og varselutmattelse, trenger du verktøy som fjerner støyen og viser deg hva du bør utbedre først.
I denne veiledningen finner du de beste løsningene for risikobasert sårbarhetshåndtering for 2026, valgt ut på grunn av deres evne til å hjelpe teamet ditt med å beskytte det som betyr noe, holde tritt med økende trusler og ta smartere beslutninger. Få praktisk innsikt i hvordan du velger riktig plattform for miljøet ditt, enten du administrerer en omfattende infrastruktur eller effektiviserer arbeidsflyter.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Sammenligningstabell for programvare for risikobasert sårbarhetshåndtering
Denne sammenligningstabellen oppsummerer prisdetaljer for mine beste utvalgte programmer for risikobasert sårbarhetshåndtering:
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best real-world exploit likelihood scoring | Free plan + free demo | From $29,000/year (billed annually) | Website | |
| 2 | Best for explainable AI in exposure management | Free demo | Pricing upon request | Website | |
| 3 | Best for machine-learning threat scoring | Free demo | Pricing upon request | Website | |
| 4 | Best for agentic workflow automation at scale | Free demo | Pricing upon request | Website | |
| 5 | Best for customizable enterprise integrations | Free demo | Pricing upon request | Website | |
| 6 | Best for threat intelligence-powered scoring | Free demo | Pricing upon request | Website | |
| 7 | Best for AI-driven exposure prioritization | Free demo | Pricing upon request | Website | |
| 8 | Best unified dashboard view across risk domains | Free trial + free demo | Pricing upon request | Website | |
| 9 | Best for built-in IT asset discovery | 30-day free trial | Pricing upon request | Website | |
| 10 | Best automation for multi-source risk data | Free demo | Pricing upon request | Website |


Anmeldelser av den beste programvaren for risikobasert sårbarhetshåndtering
Nedenfor finner du mine detaljerte sammendrag av den beste programvaren for risikobasert sårbarhetshåndtering som kom med på kortlisten min. Anmeldelsene mine gir et detaljert innblikk i funksjonene, integrasjonene og de beste bruksområdene for hver plattform, slik at du kan finne den beste løsningen for deg.
 Best real-world exploit likelihood scoring
- Free plan + free demo
- From $29,000/year (billed annually)
Visit WebsiteCustomer Rating:5/5
Strobes RBVM offers a centralized vulnerabilities dashboard displaying nearly 497K total findings with priority scores, SLA compliance, exploitability metrics, and detailed vulnerability listings. Strobes RBVM is a risk-based vulnerability management platform that aggregates findings from across your scanner stack, applies multi-factor risk scoring using EPSS and CISA KEV data, and orchestrates remediation workflows through integrations with your existing ITSM tools.
Who Is Strobes RBVM Best For?
Strobes RBVM is a strong fit for mid-size to enterprise SecOps teams managing vulnerability data across multiple scanners and cloud environments.
Why I Picked Strobes RBVM
I picked Strobes RBVM as one of the best because its risk-scoring engine goes beyond static CVSS by combining EPSS exploit probability with CISA KEV catalogue matching and asset criticality weighting. What I find especially useful is that scores update continuously as threat conditions and compensating controls change, so my team isn't chasing stale data. That means we can defensibly de-prioritize a high-CVSS CVE with no public exploit in favour of a lower-severity one that's actively being weaponized in the wild.
Strobes RBVM Key Features
- Integrated asset discovery: Automatically pulls in assets from cloud, code, and infrastructure sources for unified visibility.
- Deduplication across scanners: Aggregates and deduplicates findings from SAST, DAST, SCA, container, and infra scanners.
- Automated remediation ticketing: Routes prioritized vulnerability findings directly to ITSM tools like Jira and ServiceNow.
- Customizable executive dashboards: Provides real-time security metrics including backlog reduction, MTTR, and resolution trends.
Strobes RBVM Integrations
Strobes RBVM offers 120+ native integrations, including Jira, ServiceNow, AWS Inspector, Azure Defender, GCP Security Command Center, Qualys, Nessus, Snyk, Checkmarx, and Wiz. An API is available for custom integrations.
Pros and Cons
Pros:
- Executive dashboards tailored for security leadership
- Aggregates findings from cloud, app, and infra sources
- Dynamic risk scoring updates as threat context changes
Cons:
- No built-in risk quantification by financial impact
- Board-level PDF reports lack customization options
Learn more about Strobes RBVM:

Brinqa offers a Monitor dashboard displaying assets by status, risk rating, and type alongside critical, high, and medium vulnerability findings with SLA tracking metrics. Brinqa is a unified exposure management platform that ingests vulnerability and asset data from 260+ security tools, applies AI-driven risk scoring, and orchestrates remediation workflows across enterprise environments.
Who Is Brinqa Best For?
Brinqa is built for large enterprises running complex, multi-tool security environments where CISOs and security teams need unified visibility across thousands of assets.
Why I Picked Brinqa
I picked Brinqa as one of the best because its AI Deduplication Agent and AI Attribution Agent don't just score risk; they show exactly why a vulnerability is flagged, tracing each decision back to asset ownership and exploitability data. That explainability is what I need when justifying prioritization to stakeholders beyond raw CVSS scores. The human-in-the-loop confidence thresholds also let my team accept or override AI outputs case by case, keeping the risk model grounded.
Brinqa Key Features
- Unified Cyber Risk Graph: Maps exposures, assets, identities, and business context from all integrated sources into a single view.
- SmartFlows automation: Lets you build drag-and-drop workflows to automate remediation assignments and notifications.
- Connector library: Includes 260+ integrations with vulnerability scanners, ITSM tools, directories, CMDBs, and cloud services.
- Custom risk dashboards: Lets you create role-based, interactive dashboards to visualize risk posture and remediation progress.
Brinqa Integrations
Brinqa offers over 260 native integrations, including Qualys, Rapid7 InsightVM, Tenable, Microsoft Defender for Endpoint, CrowdStrike, Prisma Cloud, Jira, ServiceNow, BitSight, and GitHub. An API is available for custom integrations.
Pros and Cons
Pros:
- Correlates vulnerabilities with asset business context
- Workflow automation for remediation and notifications
- AI-driven risk scoring with transparent logic
Cons:
- Requires external agents for endpoint scanning
- Lacks out-of-the-box remediation tools
Learn more about Brinqa:
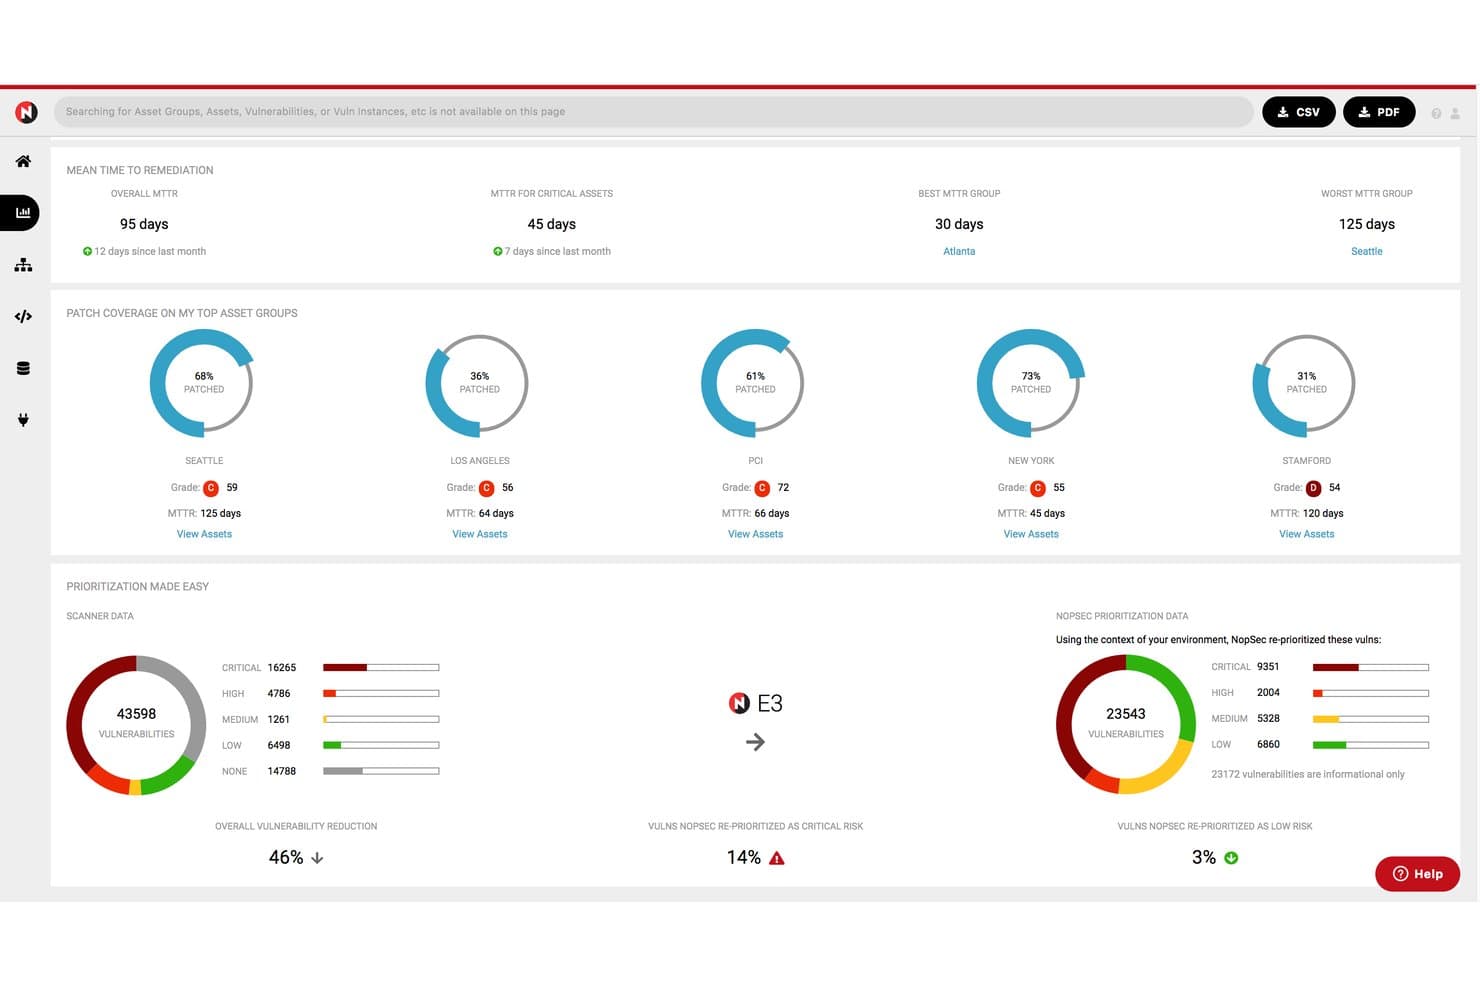
NopSec offers a unified vulnerability risk management dashboard displaying mean time to remediation, patch coverage by asset group, and prioritized vulnerability data with a 46% overall vulnerability reduction. NopSec is a risk-based vulnerability management platform that aggregates data from infrastructure, cloud, and application scanners, applies ML-driven threat scoring, and orchestrates remediation workflows through ITSM integrations and SLA tracking.
Who Is NopSec Best For?
NopSec is a strong fit for security teams at mid-market and enterprise organizations that are scaling a formal vulnerability management program and need ML-driven prioritization to cut through scanner noise.
Why I Picked NopSec
I picked NopSec as one of the best because its patented ML scoring engine goes beyond static CVSS weights to predict which vulnerabilities are most likely to be weaponized. I particularly like the Celebrity Vuln Hunt module, which delivers just-in-time alerts on zero-day and high-profile CVEs as active exploitation patterns emerge. The Risk Simulator also lets me model what-if scenarios to see how remediation decisions shift overall risk exposure before committing resources.
NopSec Key Features
- Attack Surface 360 external scanning: Continuously discovers and monitors internet-facing assets for unmanaged or new exposures.
- Collaborator ITSM integration: Sends vulnerability tickets directly into IT service management tools like Jira for workflow tracking.
- PowerIntel reporting suite: Delivers customizable executive dashboards and operational reports for vulnerability and remediation metrics.
- InControl compensating control validation: Verifies technical controls and tracks whether security measures are operating as intended.
NopSec Integrations
NopSec offers native integrations with vulnerability scanners like Tenable, Qualys, Rapid7, and CrowdStrike, as well as ServiceNow, Jira, and configuration management databases. An API is available for custom integrations.
Pros and Cons
Pros:
- Consolidates scanner, cloud, and CMDB data
- Customizable risk dashboards for executives and analysts
- ML threat scoring predicts weaponized vulnerabilities
Cons:
- Lacks native closed-loop patch automation
- Closed-loop patch automation not available
Learn more about NopSec: Best for agentic workflow automation at scale
- Free demo
- Pricing upon request

SAFE Security offers a Top Risks Dashboard with aggregate risk metrics including likelihood, loss magnitude, and annualized loss to support risk-based vulnerability management. SAFE Security is an agentic AI-driven cyber risk management platform that aggregates vulnerability and exposure data across 200+ integrations, applies business-context risk scoring, and orchestrates remediation through automated AI workflows.
Who Is SAFE Security Best For?
SAFE Security is a strong fit for enterprise security teams that already have vulnerability scanners in place and need a risk quantification and orchestration layer on top.
Why I Picked SAFE Security
I picked SAFE Security as one of the best because its agentic workflow engine genuinely changes how my team handles exposure response at scale. With 100+ prebuilt agentic workflow templates, I can automate ticket routing, ownership assignment, and exception management without building playbooks from scratch. The Agentic KEV Response feature also re-prioritizes exposures automatically the moment a new CISA KEV is published, so my team isn't scrambling manually when a zero-day drops.
SAFE Security Key Features
- Unified exposure inventory: Aggregates vulnerability and asset data from over 200 security and infrastructure integrations.
- Risk-based scoring engine: Applies dynamic risk scores using exploitability, real-time threat intel, and business context.
- Exposure validation: Simulates attack paths and validates which vulnerabilities are exploitable in your environment.
- Compliance-mapped dashboards: Delivers reporting mapped to NIST, ISO 27001, CIS, and PCI DSS standards.
SAFE Security Integrations
SAFE Security offers over 150 native integrations, including Tenable Vulnerability Management, Qualys VMDR, Rapid7 InsightVM, CrowdStrike Falcon, Wiz, ServiceNow, Jira, Okta, Microsoft Entra ID, and GitHub. An API is also available for custom integrations.
Pros and Cons
Pros:
- Custom risk scoring beyond CVSS or vendor defaults
- Financial risk quantification built on FAIR modelling
- Agentic workflows automate large-scale remediation tasks
Cons:
- Lacks built-in scanning capabilities
- Requires upstream scanners for vulnerability ingestion
Learn more about SAFE Security: Best for customizable enterprise integrations
- Free demo
- Pricing upon request

Nucleus Security offers customizable risk-based dashboards displaying total risk scores, asset counts, average vulnerability age, past due percentages, and SLA compliance metrics. Nucleus Security is a risk-based vulnerability management platform that aggregates findings from 176+ security tools, correlates them with threat intelligence and asset context, and prioritizes vulnerabilities for remediation.
Who Is Nucleus Security Best For?
Nucleus Security fits enterprise security teams managing complex, multi-scanner environments who need a centralized platform for vulnerability aggregation, prioritization, and remediation tracking.
Why I Picked Nucleus Security
I picked Nucleus Security because its FlexConnect framework lets my team pull in findings from virtually any custom data source, not just the 176+ named connectors already built into the platform. That matters when our environment includes legacy tools or homegrown scanners that most RBVM platforms simply won't touch. I also like that asset deduplication runs automatically across all those sources, so my risk scores aren't inflated by duplicate findings from overlapping scanners.
Nucleus Security Key Features
- Custom risk scoring: Create dynamic risk scores by integrating exploitability data, asset criticality, and business context.
- Threat intelligence feeds: Incorporate real-time exploit and threat feeds, including CISA KEV and EPSS, to inform prioritization.
- Remediation workflow automation: Assign, track, and manage remediation tickets through bi-directional Jira and ServiceNow integrations.
- POA&M compliance reporting: Generate executive, operational, and audit-ready reports focused on federal requirements and remediation SLAs.
Nucleus Security Integrations
Nucleus Security offers 176+ native integrations, including Tenable, Qualys, Rapid7, AWS Inspector, ServiceNow, Jira, Mandiant Advantage, Aqua, CrowdStrike, Microsoft Defender for Endpoint, and Splunk. An API is available for custom integrations.
Pros and Cons
Pros:
- Enables custom risk scoring formulas
- Supports granular asset and vulnerability deduplication
- Connects to over 170 security tools
Cons:
- Minimal patch validation automation built-in
- Reporting customization requires admin setup
Learn more about Nucleus Security: Best for threat intelligence-powered scoring
- Free demo
- Pricing upon request
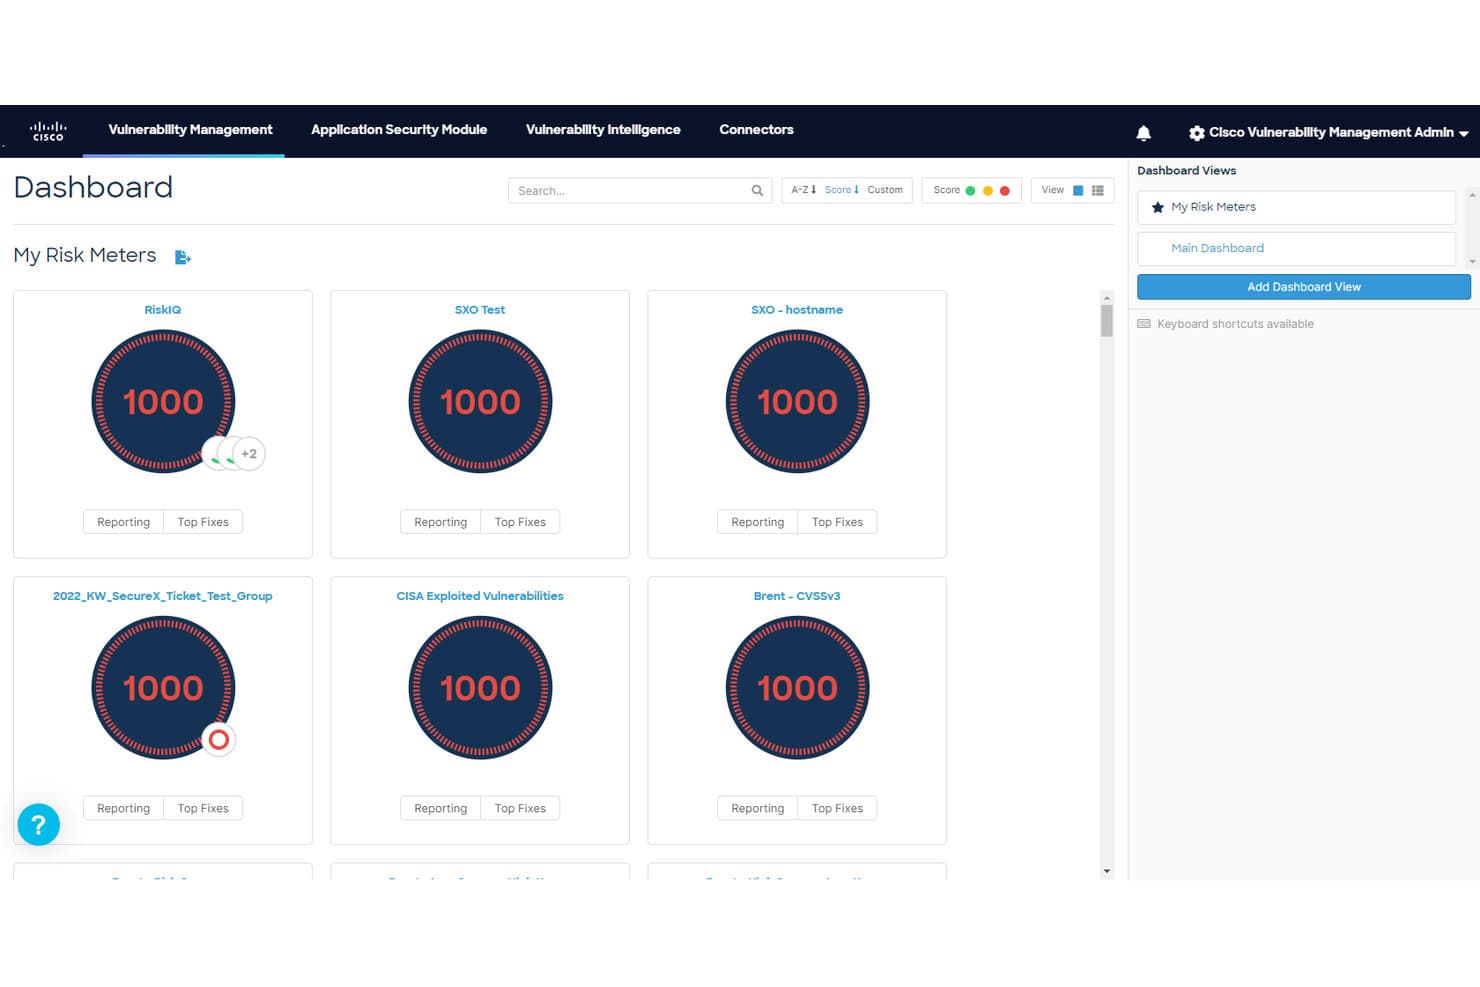
Cisco Vulnerability Management offers a risk meter dashboard displaying multiple asset groups each scored at 1000, with Reporting and Top Fixes actions available per group. Cisco Vulnerability Management is a SaaS-based vulnerability management platform that uses predictive data science and 19+ threat intelligence feeds to score and prioritize CVEs by real-world exploitability and asset criticality.
Who Is Cisco Vulnerability Management Best For?
It's a strong fit for enterprise security teams managing large, complex environments where Cisco infrastructure is already central to the stack.
Why I Picked Cisco Vulnerability Management
I picked Cisco Vulnerability Management because of how its scoring model forecasts vulnerability weaponization, not just flags it. By pulling from 19+ threat intelligence feeds and layering in Cisco Talos zero-day data, the platform predicts exploit likelihood with up to 94% accuracy. That means my team can act on what's most likely to be weaponized next, rather than defaulting to whatever scored highest on CVSS.
Cisco Vulnerability Management Key Features
- Risk Meters: Visualize vulnerability risk across different asset groups and environments with dynamic dashboards.
- Top Fix Groups: Identify prioritized sets of vulnerabilities to remediate for the greatest risk reduction.
- Bi-directional ticketing integration: Sync remediation tickets with ITSM tools to track progress and assignments.
- Peer benchmarking: Compare your risk scores against industry peers using built-in reporting tools.
Cisco Vulnerability Management Integrations
Cisco Vulnerability Management offers native integrations with Cisco Secure Endpoint, Cisco Talos, Cisco XDR, major vulnerability scanners like Tenable and Qualys, and leading ITSM tools including ServiceNow and Jira. An API is available for custom integrations.
Pros and Cons
Pros:
- Evidence-based SLAs for remediation tracking
- Predictive exploit scoring using real-world threat data
- Asset grouping with dynamic Risk Meter dashboards
Cons:
- Lacks custom vulnerability risk scoring
- Only supports CVE vulnerability findings
Learn more about Cisco Vulnerability Management: Best for AI-driven exposure prioritization
- Free demo
- Pricing upon request
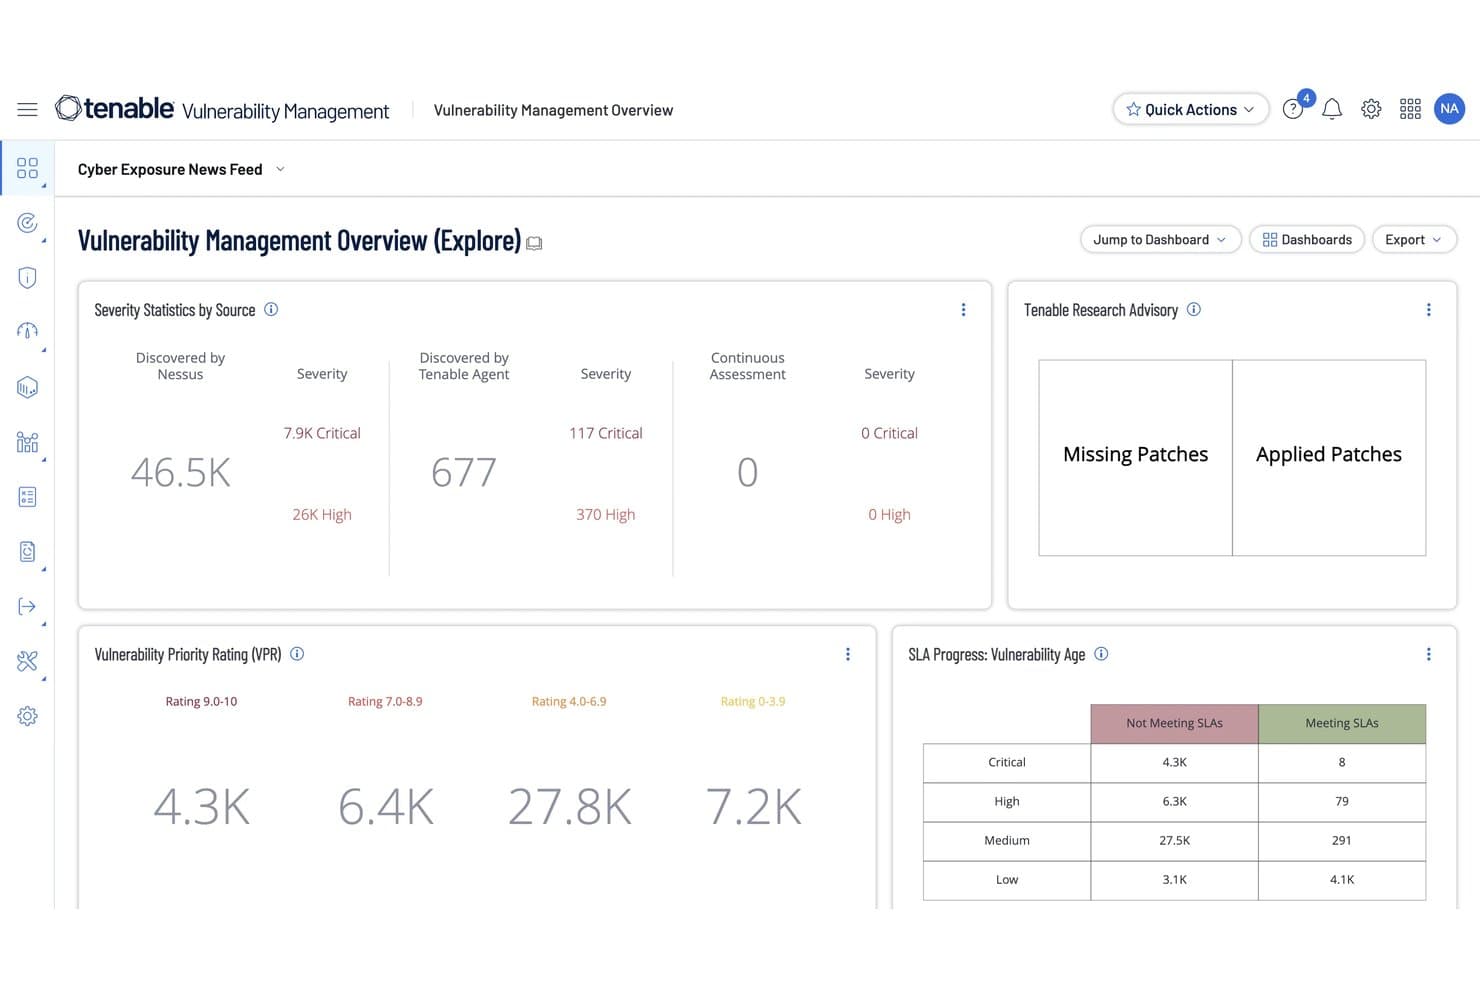
Tenable Vulnerability Management offers a risk-based overview dashboard displaying severity statistics, vulnerability priority ratings, SLA progress, and patch advisory data. Tenable Vulnerability Management is a cloud-based risk-based vulnerability management platform that combines continuous asset discovery, AI-driven vulnerability scoring, threat intelligence correlation, and remediation workflow orchestration across hybrid, cloud, and OT environments.
Who Is Tenable Vulnerability Management Best For?
It's a strong fit for enterprise security teams and SecOps leads managing large, complex environments across cloud, on-premises, and OT infrastructure.
Why I Picked Tenable Vulnerability Management
I picked Tenable Vulnerability Management as one of the best because its Vulnerability Priority Rating (VPR) fundamentally changes how my team triages CVEs. Unlike raw CVSS scores, VPR factors in active exploitation signals, ransomware associations, and asset criticality in real time, so my team isn't chasing theoretical risk. The Hexa AI agentic layer goes further still. It doesn't just surface exposure; it acts on it, executing remediation steps within guardrails my team sets.
Tenable Vulnerability Management Key Features
- Continuous asset discovery: Automatically identifies known and unknown assets across cloud, on-premises, and OT environments.
- Bi-directional ticketing: Integrates with ITSM tools like ServiceNow and Jira to sync and manage remediation tickets.
- PCI ASV integration: Supports PCI DSS scanning and attestation requirements as part of routine vulnerability management.
- Automated patch management add-on: Enables automated remediation workflows with configurable SLAs and safety guardrails.
Tenable Vulnerability Management Integrations
Tenable Vulnerability Management offers native integrations with ServiceNow, Splunk, and Jira. It natively connects with other Tenable solutions across cloud, web app, OT, and identity security. An API is available for custom integrations.
Pros and Cons
Pros:
- Automated remediation with closed-loop validation
- Continuous asset discovery across hybrid environments
- AI-driven Vulnerability Priority Rating scoring
Cons:
- Lacks agentless network scanning option
- Limited add-on for automated patching
Learn more about Tenable Vulnerability Management: Best unified dashboard view across risk domains
- Free trial + free demo
- Pricing upon request
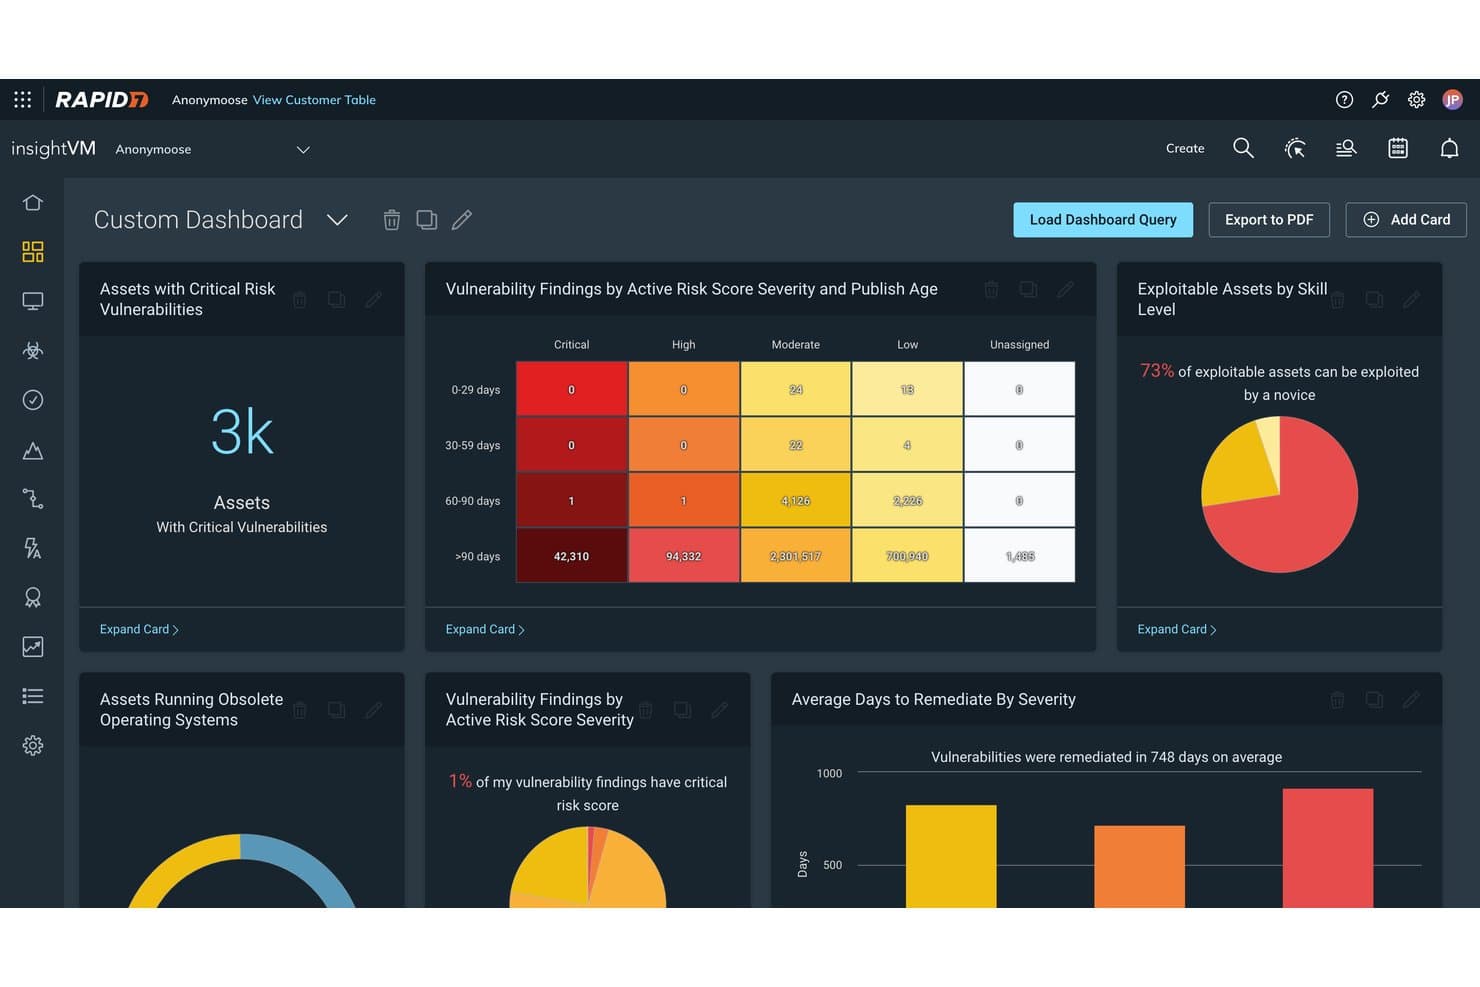
Rapid7 InsightVM offers a custom dashboard displaying critical vulnerability findings, exploitable assets by skill level, and average remediation days by severity. Rapid7 InsightVM is a risk-based vulnerability management platform that combines agent-based and network scanning, dynamic risk scoring, and remediation workflow orchestration across hybrid, cloud, and on-premises environments.
Who Is Rapid7 InsightVM Best For?
InsightVM is a strong fit for enterprise security teams managing complex hybrid environments who need to coordinate vulnerability remediation across both security and IT functions.
Why I Picked Rapid7 InsightVM
I picked Rapid7 InsightVM as one of the best because the live dashboard genuinely delivers on the promise of a unified view, pulling vulnerability data, asset criticality, and Active Risk Scores into a single pane across on-premises, cloud, and container environments. What I especially like is the Executive Risk View, which surfaces risk posture and SLA progress in a format that's usable in a board-level conversation without any extra prep work. Add the Goals and SLAs tracking layer, and I can monitor remediation commitments without switching contexts or tools.
Rapid7 InsightVM Key Features
- Remediation workflow automation: Create, assign, and track vulnerability remediation tasks integrated with Jira and ServiceNow.
- Dynamic asset tagging: Automatically group and prioritize assets based on criticality, environment, or ownership.
- Agent-based and network scanning: Scan both on-premises and cloud environments using lightweight agents or network-based methods.
- Threat intelligence integration: Incorporate real-time exploit and malware data to inform vulnerability prioritization.
Rapid7 InsightVM Integrations
Rapid7 InsightVM offers native integrations with Jira, ServiceNow, Microsoft SCCM, Ivanti, and integrates natively with Rapid7 products like InsightConnect and InsightIDR. An API is available for custom integrations.
Pros and Cons
Pros:
- Remediation projects with SLA tracking
- Dynamic asset tagging and prioritization
- Executive Risk View for board-level reporting
Cons:
- Lacks native cloud security posture tracking
- Limited third-party scanner data aggregation
Learn more about Rapid7 InsightVM:
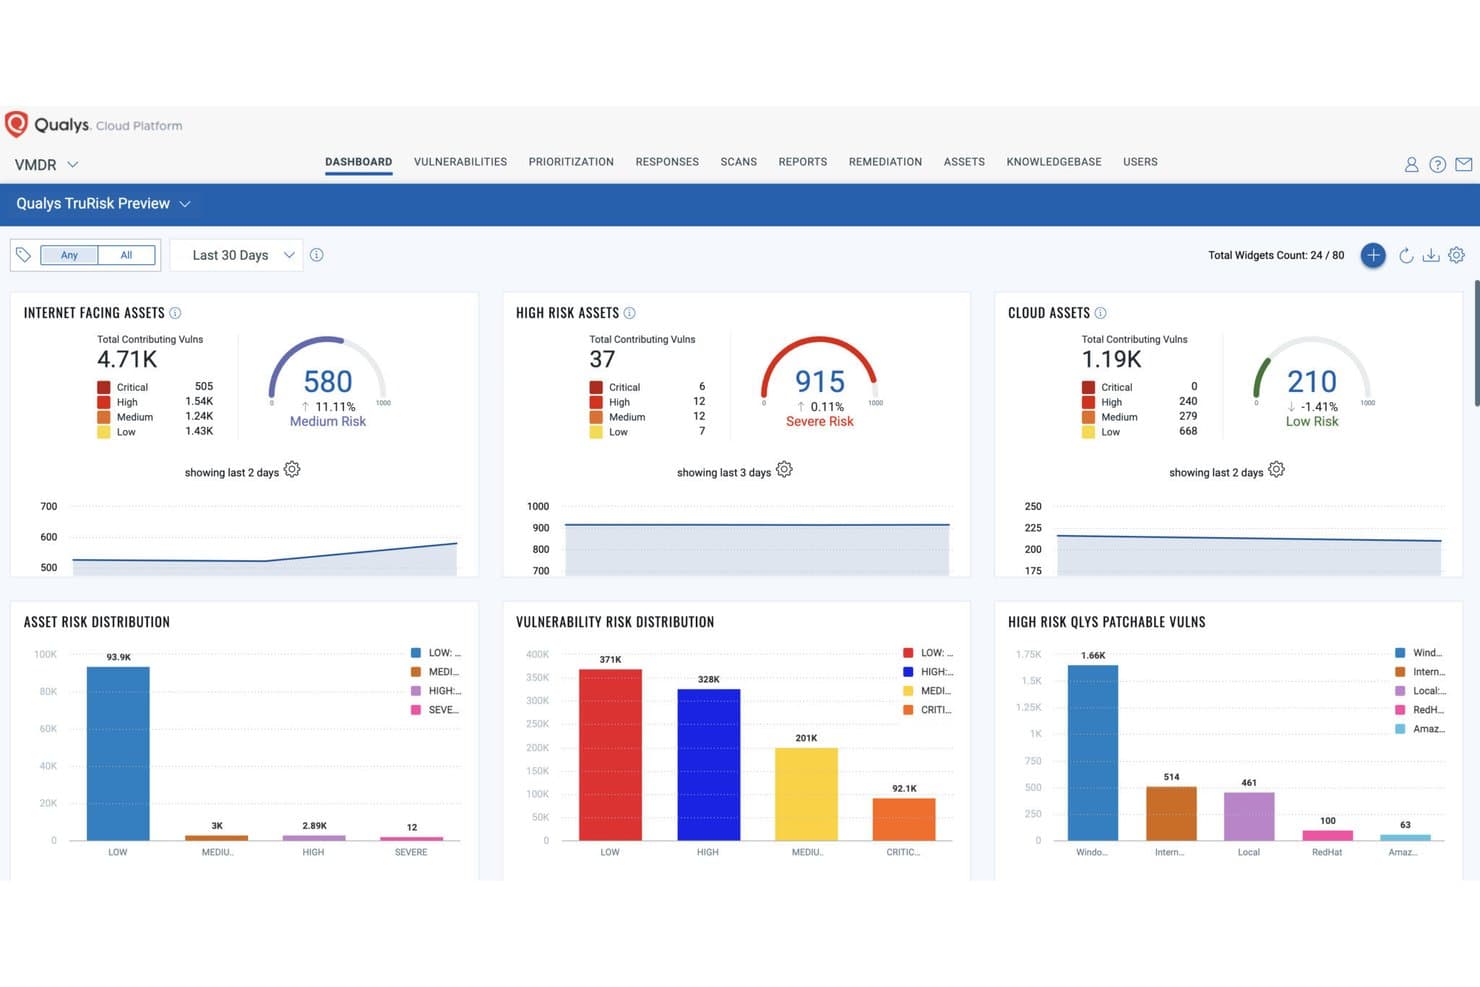
Qualys VMDR offers a TruRisk dashboard displaying risk-based vulnerability metrics across internet-facing, high-risk, and cloud assets with distribution charts. Qualys VMDR is a cloud-based vulnerability management platform that consolidates asset discovery, risk-based prioritization via TruRisk scoring, threat intelligence correlation, and patch remediation orchestration into a single agent-driven solution.
Who Is Qualys VMDR Best For?
Qualys VMDR is a strong fit for enterprise security teams managing large, complex hybrid environments across cloud, on-premises, and OT/IoT infrastructure.
Why I Picked Qualys VMDR
I picked Qualys VMDR as one of the best because its built-in asset discovery goes beyond scheduled scans. Passive Scanning Sensors detect unknown assets the moment they connect to the network, and Cloud Agents provide 2-second visibility across on-premises, cloud, OT, and IoT devices without requiring network access. That real-time inventory feeds directly into TruRisk scoring, so every asset entering my environment is immediately assessed for risk rather than waiting for the next scan cycle.
Qualys VMDR Key Features
- TruRisk scoring: Assigns dynamic, contextual risk scores that reflect exploitability, threat intelligence, and asset criticality.
- MITRE ATT&CK mapping: Aligns vulnerabilities to attacker techniques and tactics using the MITRE ATT&CK framework.
- Integrated patch management: Enables targeted remediation actions directly from risk dashboards with Qualys Patch Management.
- Bi-directional ITSM integration: Connects with ServiceNow and Jira for automated ticketing and remediation workflow tracking.
Qualys VMDR Integrations
Qualys VMDR offers native integrations with ServiceNow, Jira (Cloud and on-premises), and AWS EC2. An API is available for custom integrations.
Pros and Cons
Pros:
- Integrated patch remediation from risk dashboard
- Dynamic TruRisk scoring for every vulnerability
- Real-time asset discovery with passive sensors
Cons:
- Requires dedicated agent deployment
- Lacks built-in code scanner integration
Learn more about Qualys VMDR: Best automation for multi-source risk data
- Free demo
- Pricing upon request
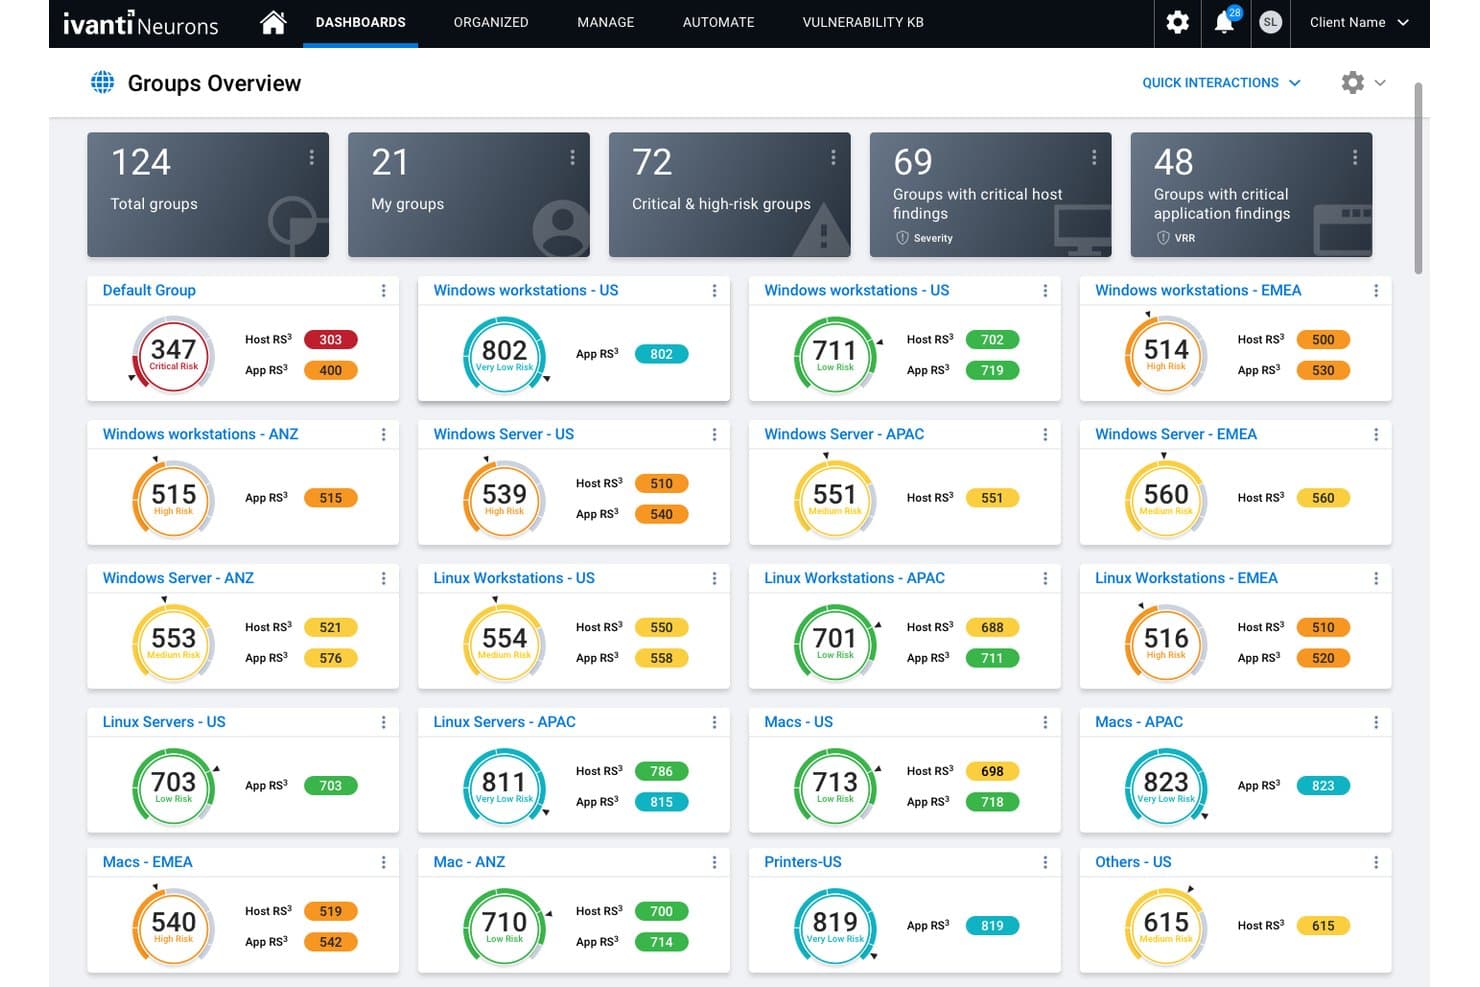
Ivanti Neurons for RBVM offers a Groups Overview dashboard displaying risk scores, host findings, and application findings across 124 device groups worldwide. Ivanti Neurons for RBVM is a SaaS-based risk-based vulnerability management platform that ingests vulnerability data from 100+ sources, applies proprietary risk scoring, and orchestrates remediation workflows across ITSM and patch management tools.
Who Is Ivanti Neurons for RBVM Best For?
It's a strong fit for large enterprise security teams managing vulnerability data across complex, multi-scanner environments who need centralized risk prioritization and remediation tracking.
Why I Picked Ivanti Neurons for RBVM
I've included Ivanti Neurons for RBVM in my top picks because of how it pulls in data from 100+ vulnerability sources and automatically correlates findings against threat intelligence, asset criticality, and exploit availability. That correlation powers the Vulnerability Risk Rating (VRR), a proprietary score that replaces raw CVSS with context tied to ransomware and active exploits. Playbook automation then handles SLA assignment and remediation alerts without manual triage.
Ivanti Neurons for RBVM Key Features
- RS³ organizational risk scoring: Quantifies and visualizes risk posture across the entire organization so you can track risk levels over time.
- Role-based access controls: Lets you define user roles for granular access to risk data, dashboards, and workflows.
- Threat-based system views: Surfaces critical exposures connected to high-priority threats like ransomware or known exploits.
- Executive and ransomware dashboards: Delivers prebuilt dashboards tailored for executive visibility and focused reporting on ransomware exposure.
Ivanti Neurons for RBVM Integrations
Ivanti Neurons for RBVM offers native integrations with Ivanti Neurons for ITSM, Ivanti Neurons for Patch Management, and Snyk, and supports ingestion from over 100 vulnerability data sources via API, flat file, or XML. An API is available for custom integrations.
Pros and Cons
Pros:
- Automated SLA assignment and workflow routing
- Includes ransomware-focused threat mapping
- Correlates vulnerabilities from 100+ data sources
Cons:
- Requires manual setup for custom playbooks
- Lacks built-in automated patch validation
Learn more about Ivanti Neurons for RBVM:
Annen programvare for risikobasert sårbarhetshåndtering
Her er noen flere alternativer for risikobasert sårbarhetshåndtering som ikke kom med på kortlisten min, men som likevel er verdt å se nærmere på:
- 11SeemplicityBest for AI-powered remediation task routing
- 12HackuityBest for consolidating vulnerability tools
- 13Tripwire IP360Best network-based vulnerability discovery
- 14EdgescanBest coverage of external and internal assets
- 15CrowdStrike Falcon Exposure ManagementBest for threat detection suite integration
- 16Hive ProBest predictive attack path visualization
- 17Arctic Wolf Aurora Exposure ManagementBest for managed proactive risk reduction
- 18ArmorCodeBest for unified security posture monitoring
How I Evaluate Risk-Based Vulnerability Management Software
I split my evaluation into baseline requirements—like context-aware risk scoring and ITSM ticket routing—and the differentiators that separate good tools from truly useful ones.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score as a percentage. Each tool needs to achieve a minimum total score of 65% to be considered for inclusion.
- Risk-Based Prioritization: I evaluate whether the tool scores vulnerabilities using exploitability, threat intel, and asset value rather than just raw CVSS numbers.
- Vulnerability Data Aggregation: The platform should ingest findings from multiple scanners like Tenable, Qualys, or Rapid7 and normalize them into one view.
- Asset Context Enrichment: I look for CMDB integration and business-context tagging so risk scores reflect asset ownership, data sensitivity, and criticality.
- Threat Intelligence Integration: Real-time feeds like EPSS, CISA KEV, and ransomware associations should actively shape how vulnerabilities get scored and surfaced.
- Remediation Workflow Orchestration: I check for bi-directional sync with tools like Jira or ServiceNow, plus SLA tracking and automated ticket assignment.
- Risk Reporting & Dashboards: Dashboards should offer role-based views so analysts see operational detail and CISOs see risk trends and remediation progress.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Attack path analysis is a real differentiator. I look for tools that map how vulnerabilities chain across assets to reach key systems. That helps you fix choke points instead of chasing isolated CVEs. Business context weighting matters just as much. Tagging assets by data sensitivity or compliance scope ensures risk scores reflect real organizational impact. I also evaluate executive risk reporting, where platforms translate technical findings into financial terms a CISO can bring to the board.
Beyond Features
Scanner and data source integrations are a big deal. I check whether a platform works with your existing scanners and pushes tickets into tools like Jira or ServiceNow without forcing you to rip and replace. Risk scoring transparency also matters. I look for audit trails that explain why a CVE was prioritized, so you can defend your patching decisions during audits. Deployment model is worth evaluating too, especially if you operate in regulated industries where cloud-only SaaS won't fly.
Slik velger du programvare for risikobasert sårbarhetshåndtering
Det er lett å gå seg vill i lange funksjonslister og kompliserte prisstrukturer. For å hjelpe deg med å holde fokus mens du går gjennom den unike prosessen din for valg av programvare, får du her en sjekkliste over faktorer du bør ha i bakhodet:
| Faktor | Hva du bør vurdere |
|---|---|
| FaktorSkalerbarhet | Hva du bør vurdereKan plattformen støtte mengden ressurser du har i dag og etter hvert som du vokser? Vurder global ekspansjon eller scenarier med fusjoner og oppkjøp. |
| FaktorIntegrasjoner | Hva du bør vurdereHenter den inn data fra skannerne, skyleverandørene og ITSM-verktøyene dine uten omfattende omveier? |
| FaktorTilpasningsmuligheter | Hva du bør vurdereKan du justere risikopoeng, dashbord eller arbeidsflyter slik at de passer med virksomhetens retningslinjer eller rapporteringsstrukturer? |
| FaktorBrukervennlighet | Hva du bør vurdereEr brukergrensesnittet intuitivt for både praktikere og ledere? Vil teamet ditt faktisk ta det i bruk raskt? |
| FaktorImplementering og innføring | Hva du bør vurdereHvor lang tid tar det vanligvis før du får verdi? Spør om distribusjonsmodeller, tidslinjer for innføring og støtte ved migrering. |
| FaktorKostnad | Hva du bør vurdereHvordan samsvarer prisen med det forventede antallet brukere og ressursomfanget ditt? Finn ut hva som utløser lisensiering. |
| FaktorSikkerhetstiltak | Hva du bør vurdereOppfyller leverandøren standardene dine for databeskyttelse av sensitive sårbarhets- og ressursdata? |
| FaktorOverholdelseskrav | Hva du bør vurdereKan løsningen støtte revisjoner og bidra til å dokumentere etterlevelse av rammeverk som PCI DSS, HIPAA eller NIST? |
Hva er programvare for risikobasert sårbarhetshåndtering?
Programvare for risikobasert sårbarhetshåndtering er en sikkerhetsplattform som prioriterer sårbarheter basert på reell risiko, ikke bare teknisk alvorlighetsgrad. Den kombinerer data fra flere skannere, kontekst om ressurser og trusselintelligens for å fremheve hvilke problemer som bør håndteres først, slik at sikkerhetsteam kan fokusere på det som er viktigst for organisasjonens risikoprofil.
Funksjoner i programvare for risikobasert sårbarhetshåndtering
Når du velger risikobasert programvare for sårbarhetshåndtering, bør du se etter følgende nøkkelfunksjoner:
- Risikobasert prioritering: Bruker utnyttbarhet, forretningspåvirkning og trusseldata fra virkeligheten til å rangere sårbarheter etter organisasjonens faktiske risiko – ikke bare alvorlighetsgrader.
- Aggregasjon av sårbarhetsdata: Samler funn fra ulike skannere og skyverktøy i en samlet oversikt, slik at du får et fullstendig og nøyaktig bilde av risikoen.
- Berikelse av aktivakontekst: Kobler sårbarheter til eierskap, kritikalitet og forretningsfunksjon for aktiva, slik at teamene forstår konsekvensene av hvert funn.
- Integrasjon med trusselintelligens: Inkluderer oppdaterte kilder til informasjon om utnyttelser, skadevarekampanjer og andre trusselintelligenskilder for å informere risikoberegninger og varsle om problemer som aktivt utnyttes.
- Arbeidsflyter for utbedringsbilletter: Tildeler, sporer og administrerer oppgaver for feilretting gjennom integrasjon med ITSM-verktøy, slik at sårbarheter utbedres og verifiseres innen definerte SLA-er.
- Tilpassbare dashbord: Presenterer risiko- og utbedringsdata visuelt og tilpasser visningene for analytikere, ledere og toppledere, med detaljvisning og trendanalyse.
- Rapportering for revisjon og samsvar: Genererer rapporter i tråd med bransjerammeverk – som PCI DSS eller NIST – for forberedelse til revisjoner og løpende oppfølging av samsvar.
- Verifisering med lukket sløyfe: Skanner aktiva på nytt automatisk for å bekrefte at utbedringen er fullført, noe som reduserer behovet for manuell oppfølging og risikoen for at feilrettinger overses.
- Støtte for API-er og integrasjoner: Tilbyr detaljerte API-er og koblinger for synkronisering med aktivabeholdninger, konfigurasjonsstyring og eksterne rapporteringssystemer.
Fordeler med risikobasert programvare for sårbarhetshåndtering
Implementering av risikobasert programvare for sårbarhetshåndtering gir flere fordeler for teamet og virksomheten din. Her er noen av fordelene du kan se frem til:
- Fokusert utbedring: Prioriter sårbarheter som utgjør en reell risiko for organisasjonen, slik at teamet først løser det som virkelig betyr noe.
- Samlet risikobilde: Samler funn fra flere skannere og kilder i ett enkelt, standardisert dashbord for sårbarhetshåndtering.
- Bedre beslutningsgrunnlag: Aktivakontekst, forretningspåvirkning og integrasjon med trusselintelligens hjelper interessenter med å forstå risiko i forretningsmessige termer, ikke bare teknisk sjargong.
- Forbedret samsvar: Automatisert revisjonsrapportering i tråd med rammeverk gjør det enklere å samle inn og spore dokumentasjon for bransjereguleringer og standarder.
- Automatisering av arbeidsflyter: Integrert billettsystem for utbedring og verifisering med lukket sløyfe sørger for effektiv og ansvarlig oppdatering på tvers av IT- og sikkerhetsteam.
- Rapportering til ledelsen: Tilpassede dashbord og verktøy for kvantifisering av risiko gjør det enklere å kommunisere cyberrisiko og fremdrift i utbedringsarbeidet til ledere og styrer.
- Redusert etterslep av utbedringer: Ved å filtrere bort trusler med liten påvirkning bruker teamene mindre tid på å følge opp mindre problemer, slik at de samlede køene for oppdateringer blir kortere.
Kostnader og priser for risikobasert programvare for sårbarhetshåndtering
Valg av risikobasert programvare for sårbarhetshåndtering krever en forståelse av de ulike prismodellene og abonnementene som er tilgjengelige. Kostnadene varierer basert på funksjoner, teamstørrelse, tillegg og mer. Tabellen nedenfor oppsummerer vanlige abonnementer, gjennomsnittsprisene deres og typiske funksjoner som inngår i løsninger for risikobasert sårbarhetshåndtering:
Sammenligningstabell for abonnementer for risikobasert programvare for sårbarhetshåndtering
| Abonnementstype | Gjennomsnittspris | Vanlige funksjoner |
|---|---|---|
| AbonnementstypeGratisabonnement | Gjennomsnittspris$0 | Vanlige funksjonerBegrenset støtte for aktiva, grunnleggende risikoskåring, manuell rapportering og ingen integrasjoner. |
| AbonnementstypePersonlig abonnement | Gjennomsnittspris$50-$200/måned | Vanlige funksjonerTilgang for én bruker, standard risikoskåring, dataaggregering og enkle dashbord. |
| AbonnementstypeForretningsabonnement | Gjennomsnittspris$500-$2,000/måned | Vanlige funksjonerStøtte for flere brukere, tilpasset risikovekting, integrasjoner med skannere og ITSM, samsvarsrapporter og SLA-er. |
| AbonnementstypeVirksomhetsabonnement | Gjennomsnittspris$2,000-$10,000/måned | Vanlige funksjonerAktivaskala for virksomheter, avansert analyse, kilder til trusselintelligens, analyse av angrepsbaner, API-tilgang og prioritert brukerstøtte. |
Vanlige spørsmål om risikobasert programvare for sårbarhetshåndtering
Her er noen svar på vanlige spørsmål om risikobasert programvare for sårbarhetshåndtering:
Hvordan skiller risikobasert sårbarhetshåndtering seg fra tradisjonell sårbarhetshåndtering?
Risikobasert sårbarhetshåndtering prioriterer problemer basert på konteksten til ressurser og trusler i den virkelige verden, ikke bare tekniske alvorlighetsgrader eller grunnleggende sårbarhetsskanning. I motsetning til tradisjonell sårbarhetshåndtering vurderer den virksomhetskritikalitet, trusselaktører og sannsynligheten for utnyttelse for å forhindre datainnbrudd og optimalisere den overordnede livssyklusen for sårbarhetshåndtering.
Hvilke typer ressurser kan risikobasert programvare for sårbarhetshåndtering dekke?
Du kan forvente dekning for lokale systemer, skyarbeidsbelastninger, containere, endepunkter og IoT-ressurser. Noen plattformer forbedrer nettverks- og applikasjonssikkerheten ved å integrere resultater fra penetrasjonstesting og verktøy for sårbarhetsvurdering, noe som gir fullstendig oversikt over angrepsflaten på tvers av nettapplikasjoner, mobile enheter og eksterne inngangspunkter.
Integreres risikobasert programvare for sårbarhetshåndtering med de eksisterende verktøyene våre?
Ja, de fleste løsninger integreres med vanlige skannere, ITSM-plattformer som Jira eller ServiceNow og ressursbeholdninger. Kontroller at de spesifikke verktøyene organisasjonen bruker, støttes for direkte dataflyt og automatisering av arbeidsflyter.
Kan det bidra til å oppfylle samsvarskrav?
Ja, mange plattformer genererer revisjonsklare rapporter og sporer avtaler om tidsfrister for utbedring i samsvar med rammeverk som PCI DSS, HIPAA, NIST eller ISO 27001. Dette støtter innsamling av dokumentasjon og bidrar til å demonstrere risikobasert beslutningstaking under vurderinger.
Hvor lang tid tar det å implementere risikobasert programvare for sårbarhetshåndtering?
Implementeringen kan ta fra noen dager til flere uker, avhengig av omfanget av ressursene, integrasjonsbehovene og organisasjonens kompleksitet. Det er lurt å spørre leverandørene om støtte ved oppstart, tilgjengelige veiledninger og opplæringsressurser for teamet.