

En plattform for endepunktbeskyttelse er en sentralisert sikkerhetsløsning for å oppdage, forhindre og håndtere trusler rettet mot enheter på tvers av nettverket ditt. Hvis du leter etter den beste plattformen for endepunktbeskyttelse for organisasjonen din, prøver du sannsynligvis å balansere eldre teknologi, innføring av skyen og kontinuerlig hendelseshåndtering. Når angripere beveger seg raskt og regelverket er i stadig utvikling, kan mangler i dekningen eller trege svar føre til tapt produktivitet – eller noe verre.
Denne veiledningen sammenligner plattformer med høy ytelse som kombinerer avansert gjenkjenning, tilbakerulling etter løsepengevirusangrep og integrasjon med det øvrige sikkerhetsøkosystemet ditt. Få innsikten du trenger for å velge verktøy som faktisk samsvarer med risikoene, infrastrukturen og den globale tilstedeværelsen din.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Sammenligningstabell for plattformer for endepunktbeskyttelse
Tabellen nedenfor sammenligner prisopplysninger for mine beste utvalgte plattformer for endepunktbeskyttelse.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for enterprise-grade threat hunting at scale | Free demo available | Pricing upon request | Website | |
| 2 | Best for multi-layered behavioral analysis | Free demo available | Pricing upon request | Website | |
| 3 | Best for ransomware rollback after an active attack | Free trial available | Pricing upon request | Website | |
| 4 | Best for AI-driven XDR across enterprise endpoints | Free demo available | Pricing upon request | Website | |
| 5 | Best for MSP-ready endpoint security with bundled MDR | Free demo available | Pricing upon request | Website | |
| 6 | Best for multi-layered ransomware rollback and MDR | Free demo available | Pricing upon request | Website | |
| 7 | Best for AI-native autonomous endpoint defense | Free demo available | Pricing upon request | Website | |
| 8 | Best for legacy enterprise endpoints | Free demo available | Pricing upon request | Website | |
| 9 | Best for Microsoft 365-based orgs | Not available | Pricing upon request | Website | |
| 10 | Best for defense with identity context | Free demo available | Pricing upon request | Website |


Anmeldelser av plattformer for endepunktbeskyttelse
Nedenfor finner du mine detaljerte sammendrag av de beste plattformene for endepunktbeskyttelse som kom med på kortlisten min. Anmeldelsene mine gir en detaljert gjennomgang av funksjonene, de beste bruksområdene og funksjonaliteten til hver plattform, slik at du kan finne den beste løsningen for deg.
 Best for enterprise-grade threat hunting at scale
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.6/5
CrowdStrike Falcon tracks CVE vulnerabilities across endpoints by host and severity. CrowdStrike Falcon is a cloud-native endpoint protection platform that combines next-gen antivirus, EDR, threat intelligence, device control, firewall management, and AI-powered threat hunting across enterprise endpoints.
Who Is CrowdStrike Falcon Best For?
CrowdStrike Falcon is a strong fit for large enterprises and security operations teams managing thousands of endpoints across distributed environments.
Why I Picked CrowdStrike Falcon
CrowdStrike Falcon earns its spot on my shortlist because of Falcon Adversary OverWatch, a managed threat hunting layer that analyzes trillions of events continuously to catch what automated detections miss. I like that OverWatch pairs human hunters with AI-driven detection, so your SOC gets actionable findings rather than raw alerts to sort through. The EDR telemetry feeding into that process gives hunters deep visibility across every endpoint at scale.
CrowdStrike Falcon Key Features
- Falcon Prevent: An AI-powered next-gen antivirus that blocks malware, fileless attacks, and zero-day exploits using machine learning and behavioral analysis—even when endpoints are offline.
- Falcon Insight XDR: Extended detection and response that correlates endpoint telemetry with data from cloud environments, identity systems, and third-party security tools for cross-domain visibility.
- Falcon Firewall Management: Centralized firewall policy enforcement across Windows and macOS devices, with pre-built policies, reusable rules, and role-based access controls.
- Adversary intelligence profiles: Built-in threat intelligence covering 245+ tracked adversary groups, giving your security team context on attacker tactics, techniques, and procedures during investigations.
CrowdStrike Falcon Integrations
CrowdStrike Falcon connects with a large partner ecosystem through the CrowdStrike Marketplace, with documented integrations including AWS, Microsoft Azure, Microsoft Sentinel, ServiceNow, Splunk, Zscaler, Okta, Nutanix, Darktrace, and NinjaOne. Falcon also provides public APIs for custom integrations and SIEM, SOAR, and threat intelligence data connectors.
Pros and Cons
Pros:
- Managed threat hunting operates 24/7
- Endpoint telemetry gives deep investigation visibility
- Human threat hunters analyze live attacks
Cons:
- Advanced settings require skilled security staff
- Requires strong network connectivity for full value
Learn more about CrowdStrike Falcon: Best for multi-layered behavioral analysis
- Free demo available
- Pricing upon request

Symantec Endpoint Protection alerts users to threats via real-time notifications. Symantec Endpoint Protection is an endpoint protection platform that combines malware detection, behavioral analysis, attack surface reduction, endpoint detection and response (EDR), and threat hunting across Windows, Mac, Linux, mobile, and virtual environments.
Who Is Symantec Endpoint Protection Best For?
It's a strong fit for enterprise security teams managing large, mixed-OS environments that need layered threat detection across physical, virtual, and mobile endpoints.
Why I Picked Symantec Endpoint Protection
Symantec Endpoint Protection earns its spot on my shortlist because its SONAR behavioral analysis engine layers heuristics, machine learning, and reputation data together to catch threats that signature-based detection misses entirely. I find the depth here genuinely impressive: it monitors process behavior in real time and cross-references the Global Intelligence Network to flag zero-day activity before it executes. That combination makes it one of the few platforms I trust for environments where unknown and living-off-the-land attacks are a real concern.
Symantec Endpoint Protection Key Features
- Active Directory defense: Monitors and protects Active Directory from credential theft and reconnaissance attacks that precede lateral movement.
- Attack surface reduction: Applies application control, device control, and exploit mitigation to shrink the number of entry points available to attackers.
- AI-guided policy management: Uses AI to recommend and automate policy adjustments, reducing manual configuration burden on security operations teams.
- Single-agent, multi-deployment architecture: Runs one agent across cloud, on-premises, and hybrid environments, managed through a single cloud console.
Symantec Endpoint Protection Integrations
Symantec Endpoint Protection offers native integrations with Symantec Endpoint Protection Manager, Microsoft Active Directory, Microsoft Entra ID, Symantec CloudSOC, Symantec Secure Web Gateway, Symantec Content Analysis, and unified endpoint management providers, plus event streaming to SIEM tools like Splunk and FortiSIEM. It also provides REST APIs through the Broadcom Enterprise Security Group for custom integrations.
Pros and Cons
Pros:
- AI-driven automated policy recommendations
- Active Directory protections built into core agent
- Real-time behavioral monitoring against advanced threats
Cons:
- Policy updates can be slow to sync
- High system resource usage during scans
Learn more about Symantec Endpoint Protection: Best for ransomware rollback after an active attack
- Free trial available
- Pricing upon request

Sophos dashboard gives admins a full view of device compliance. Sophos Endpoint is an endpoint protection platform that combines AI-driven threat detection, behavioral analysis, anti-ransomware technology, and centralized device management across Windows, macOS, and Linux environments.
Who Is Sophos Endpoint Best For?
Sophos Endpoint is a strong fit for IT security teams in mid-to-large organizations that need active ransomware defense with the ability to roll back encrypted files after an attack.
Why I Picked Sophos Endpoint
Sophos Endpoint earns its spot because of CryptoGuard, its behavioral ransomware detection layer that doesn't just block an attack—it rolls back encrypted files to their pre-attack state after the fact. If ransomware slips past earlier defenses and starts encrypting files, CryptoGuard detects the unauthorized encryption in real time and automatically restores affected data. I also like the kernel-level tamper protection, which blocks attackers from killing the endpoint agent before the rollback can trigger.
Sophos Endpoint Key Features
- Deep learning malware prevention: Multiple AI models scan files before execution to detect known malware and zero-day variants, including AI-generated mutations.
- Anti-exploitation controls: Over 60 built-in exploit mitigations block attacker techniques across the attack chain with no per-application configuration needed.
- Peripheral device control: Monitors and blocks access to removable media, Bluetooth devices, and mobile hardware to prevent unauthorized data transfer or malware entry.
- Malicious traffic detection: Analyzes outbound non-browser network traffic to identify communication with attacker command-and-control servers in real time.
Sophos Endpoint Integrations
Sophos Endpoint offers native integrations with Splunk, Microsoft Sentinel, ServiceNow, Jira, PagerDuty, Slack, Microsoft Teams, Okta, Amazon Web Services, and Google Cloud, plus native integrations across the Microsoft ecosystem, including Microsoft 365 and Entra ID. Sophos Central also provides an API for custom integrations and connects with a range of RMM and PSA tools like ConnectWise, Datto, and Kaseya.
Pros and Cons
Pros:
- Blocks over sixty attacker exploit techniques
- Kernel-level tamper protection prevents agent disabling
- Ransomware rollback restores encrypted files fast
Cons:
- Occasional false positives trigger unwanted remediation
- Rollback feature available only on Windows
Learn more about Sophos Endpoint: Best for AI-driven XDR across enterprise endpoints
- Free demo available
- Pricing upon request

Cortex XDR's AI assistant summarizes cases and identifies compromised users instantly. Cortex XDR is an AI-driven extended detection and response (XDR) platform from Palo Alto Networks that covers endpoint protection, threat detection, investigation, and response across endpoints, network, cloud, identity, and email from a single agent and unified data lake.
Who Is Cortex XDR Best For?
Cortex XDR is a strong fit for large enterprises that need unified threat detection and response across endpoints, cloud, network, and identity from a single platform.
Why I Picked Cortex XDR
I've included Cortex XDR in my top picks because its AI-driven detection goes beyond signature-based methods, using behavioral analytics across endpoint, network, cloud, and identity data simultaneously to surface threats that siloed tools would miss. I'm particularly impressed by its Cortex AgentiX AI agents, which automate root cause analysis and can contain an active attack within minutes without manual intervention. The single-agent architecture also handles NG-SIEM, endpoint data loss prevention, and exposure management in one deployment, which cuts the complexity of running separate tools across a large environment.
Cortex XDR Key Features
- Zero-day and fileless malware prevention: Dedicated prevention modules block zero-day exploits, fileless malware, and process-hijacking attacks before they execute on endpoints.
- Managed detection and response: Unit 42 MDR operates directly inside your Cortex XDR tenant to handle proactive threat hunting, monitoring, and remediation on your behalf.
- Managed threat hunting: Unit 42 analysts combine their threat intelligence with Cortex XDR's AI analytics to validate and surface threats earlier than automated detection alone.
- Alert triage and noise reduction: Cortex XDR correlates alerts across data sources and groups related events into incidents, cutting alert volume so your team works fewer, higher-quality cases.
Cortex XDR Integrations
Cortex XDR offers native integrations with Palo Alto Networks Next-Generation Firewalls, Prisma Cloud, Active Directory, AWS, Microsoft Azure, Google Cloud Platform, Okta, Microsoft 365, and ingests data from third-party firewalls like Cisco and Fortinet. It connects to Cortex XSOAR for automated response playbooks and provides a REST API for custom integrations with tools like Splunk, ServiceNow, and Rapid7 InsightIDR.
Pros and Cons
Pros:
- Unit 42 MDR handles proactive threat response
- Behavioral analytics catch fileless and zero-day threats
- AI-driven threat hunting covers endpoints and cloud
Cons:
- High alert volume may still overwhelm small teams
- Incident investigation tools sometimes feel complex
Learn more about Cortex XDR: Best for MSP-ready endpoint security with bundled MDR
- Free demo available
- Pricing upon request

Cynet centralizes threat detection, automation, and remediation in one dashboard. Cynet is an AI-powered endpoint protection platform that unifies EPP, EDR, XDR, identity security, network detection, email security, cloud and SaaS security, and built-in SOAR under a single agent and console.
Who Is Cynet Best For?
Cynet is a strong fit for managed service providers that need a single platform to protect multiple client environments without building out a dedicated security operations team.
Why I Picked Cynet
Cynet earns its spot on my shortlist because the bundled CyOps MDR service is included with the platform, not sold as an add-on, which means MSPs get 24/7 analyst coverage without negotiating a separate contract. I like that a single agent covers EPP, EDR, identity threat detection, network detection, and email security across all client tenants from one console. The one-click CyOps engagement from the dashboard lets MSP analysts escalate to Cynet's SOC in seconds, and automated remediation playbooks handle containment before a human even reviews the alert.
Cynet Key Features
- Cloud and SaaS security posture management: Cynet scans cloud and SaaS environments like AWS, Azure, and Microsoft 365 for misconfigurations, risky permissions, and compliance gaps across NIST, PCI DSS, and HIPAA frameworks.
- Mobile threat defense: The platform detects and blocks device, network, and phishing threats on iOS, Android, and ChromeOS, with on-device automated remediation and MDM/EMM integration.
- CyAI threat prediction engine: Cynet's AI engine continuously learns from real-world attack data to predict and block threats before execution, reducing alert noise for your team.
- RMM and PSA integrations: Cynet connects to 80+ tools including RMM and PSA platforms, letting MSPs pull Cynet data directly into their existing workflows without switching consoles.
Cynet Integrations
Cynet offers 80+ built-in integrations across 50+ ecosystem partners, including ConnectWise RMM, ConnectWise PSA, HaloPSA, Autotask, NinjaOne, Microsoft 365, Google Workspace, AWS, and Azure, with 30+ threat intelligence feeds also supported. Open APIs are available for custom integrations, and the platform ingests telemetry from 50+ sources to feed SOAR playbooks across RMM, PSA, SIEM, and identity tools.
Pros and Cons
Pros:
- Automated playbooks accelerate alert response
- Single agent simplifies multi-tenant deployments
- CyOps MDR service included for all clients
Cons:
- Mobile device management features are fairly basic
- Reporting dashboards have limited customization options
Learn more about Cynet: Best for multi-layered ransomware rollback and MDR
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.2/5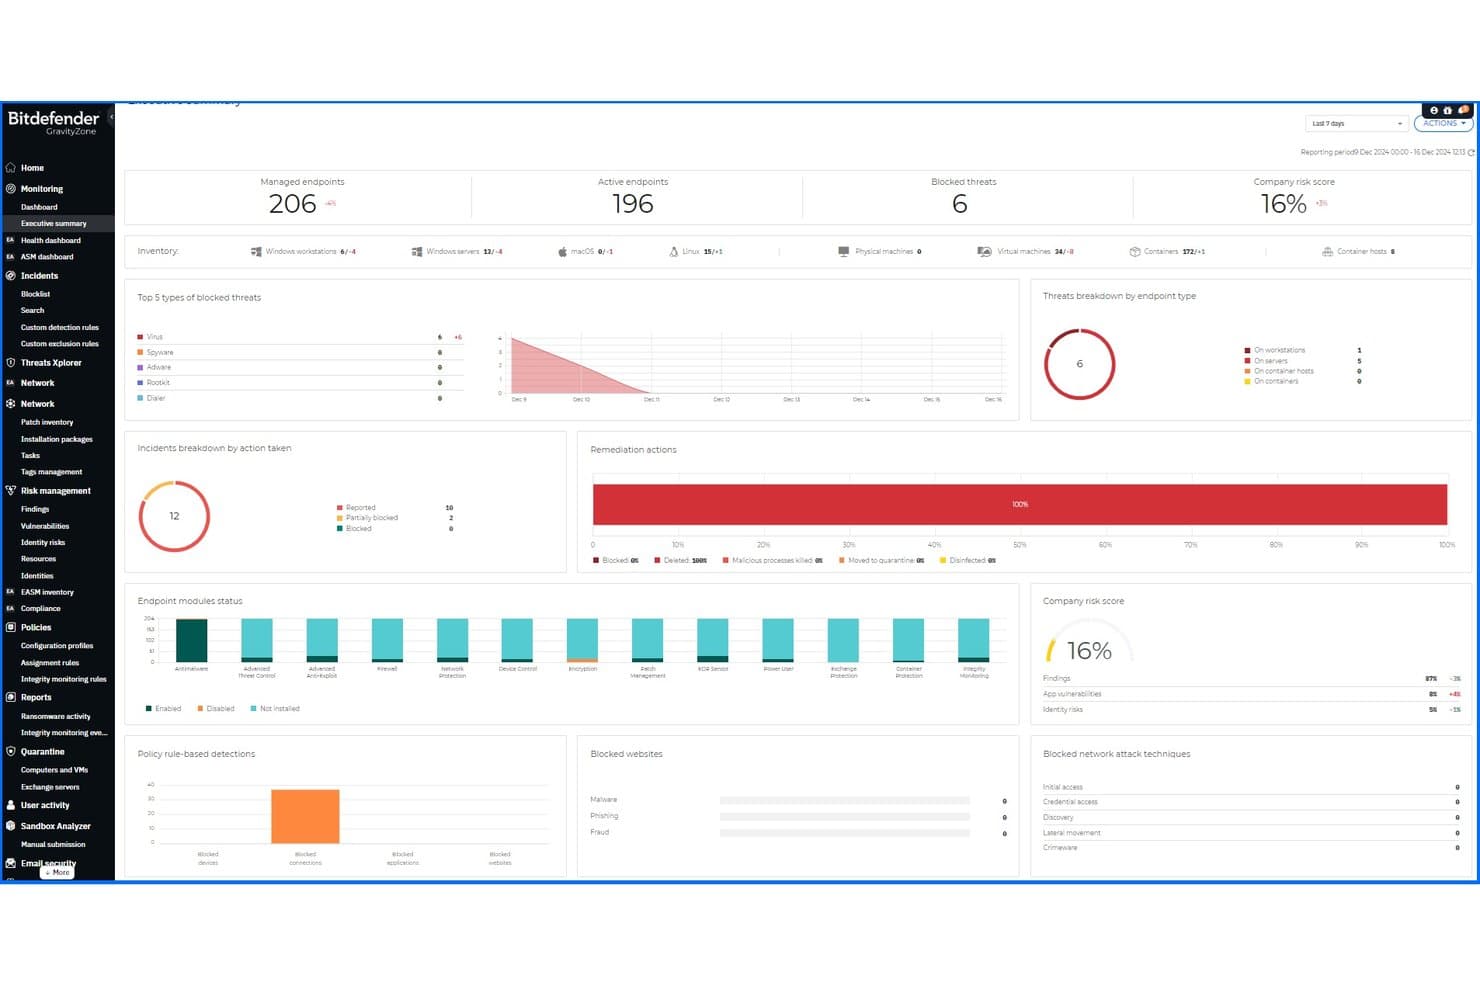
Bitdefender GravityZone provides a unified executive summary dashboard for endpoint security. Bitdefender GravityZone is an endpoint protection platform that combines machine learning, behavioral analysis, network attack defense, risk management, and web content control into a single cloud or on-premise management console for small and medium-sized businesses.
Who Is Bitdefender GravityZone Best For?
GravityZone is a strong fit for SMBs that need enterprise-grade threat detection without a large in-house security team.
Why I Picked Bitdefender GravityZone
I picked Bitdefender GravityZone as one of the best because its ransomware mitigation goes beyond detection. When GravityZone spots abnormal encryption activity, it blocks the process and automatically recovers affected files from backup copies, restoring them to their pre-attack state. Layer that with Bitdefender MDR, which provides 24/7 analyst-led threat monitoring with pre-approved response actions, and you get a platform that can contain active threats without waiting on customer approval.
Bitdefender GravityZone Key Features
- Patch management: Automatically keeps Windows OS and third-party applications up to date across managed endpoints to reduce exposure to known vulnerabilities.
- Email security: Scans and filters inbound and outbound email threats across Microsoft 365, Gmail, and Exchange to block phishing, malware, and spam before they reach users.
- Full disk encryption: Enforces encryption on endpoint storage using native OS tools, ensuring data on lost or stolen devices stays protected.
- Mobile device security: Extends endpoint protection to iOS, Android, and ChromeOS devices, applying threat detection and policy enforcement to mobile endpoints alongside desktops and servers.
Bitdefender GravityZone Integrations
Bitdefender GravityZone offers native integrations with VMware vCenter, Microsoft Active Directory, Microsoft Exchange, Veeam Backup & Replication, Splunk, ConnectWise PSA, HaloPSA, Okta, Jira, and Slack, plus XDR sensor integrations across the Microsoft ecosystem (Microsoft 365, Azure, Azure AD, Intune, Defender), AWS, and Google Workspace. An API is available for custom integrations, and it supports SIEM forwarding via syslog and webhook.
Pros and Cons
Pros:
- Extensive endpoint and mobile device coverage
- 24/7 managed detection and response available
- Automatic ransomware rollback and file recovery
Cons:
- Policy configuration options may overwhelm new admins
- Forensic analysis features can feel basic
Learn more about Bitdefender GravityZone: Best for AI-native autonomous endpoint defense
- Free demo available
- Pricing upon request
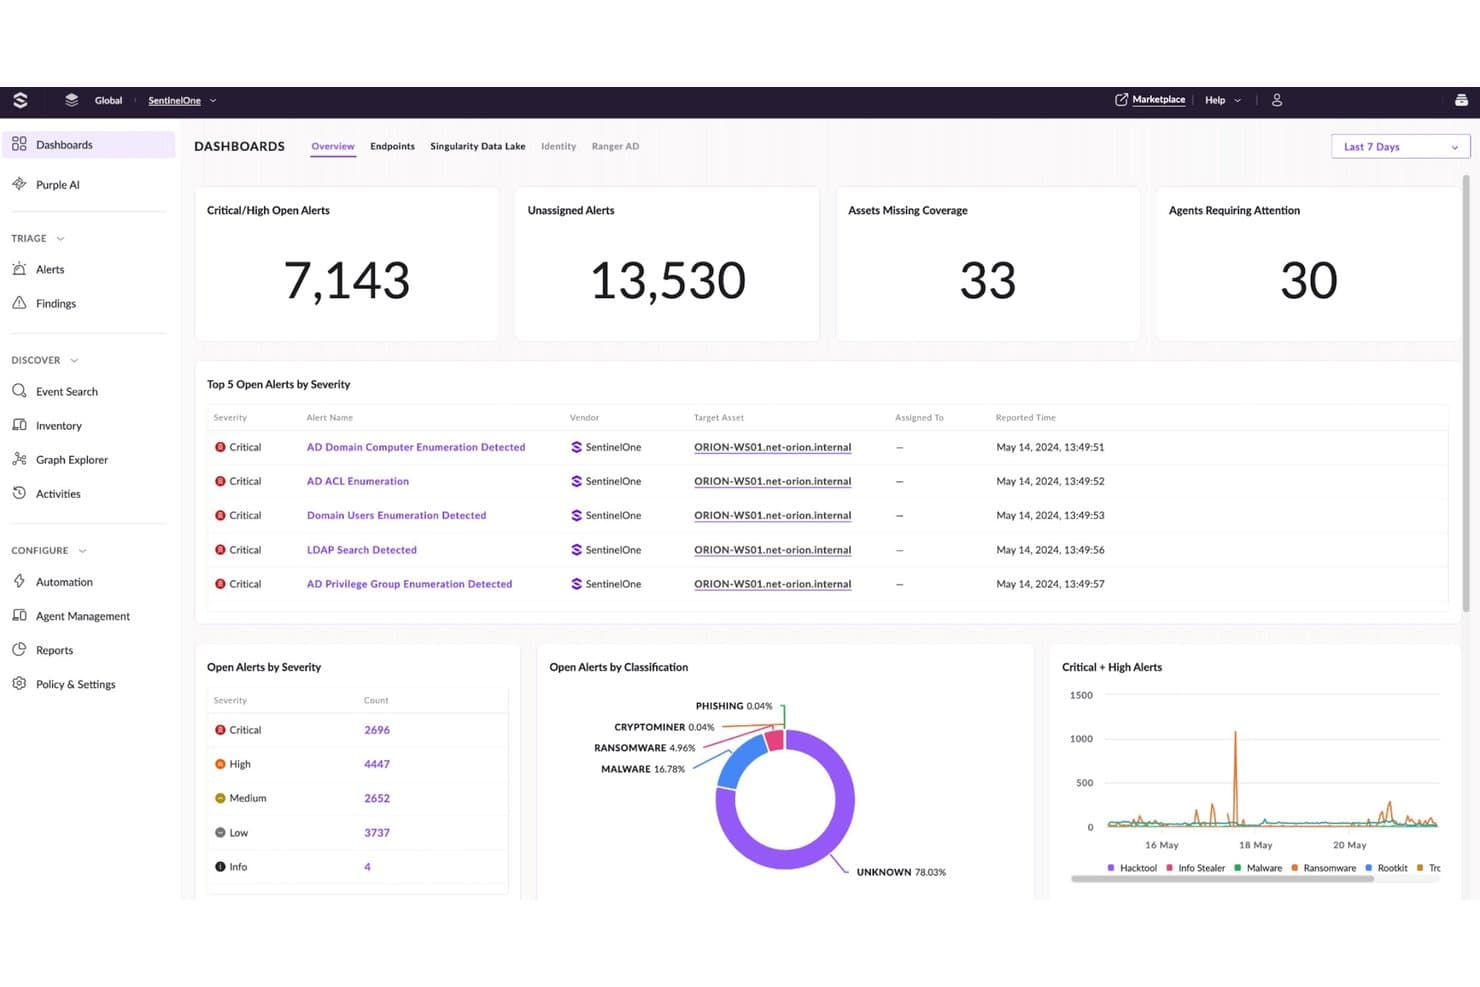
SentinelOne Singularity centralizes critical threat alerts and endpoint coverage metrics. SentinelOne Singularity is an AI-native endpoint protection platform that unifies endpoint, identity, cloud, and mobile security under a single console, with autonomous threat detection and response across ransomware, zero-days, fileless malware, and supply chain attacks.
Who Is SentinelOne Singularity Best For?
SentinelOne Singularity is a strong fit for security operations teams at mid-to-large enterprises that need autonomous threat response across endpoints, cloud workloads, and identity without relying on manual analyst intervention.
Why I Picked SentinelOne Singularity
SentinelOne Singularity earns its spot on my shortlist because its AI-driven Storyline technology automatically correlates related events across endpoints into a single attack narrative, so analysts aren't manually stitching together alerts after the fact. I also like that its ActiveEDR can roll back malicious changes autonomously without waiting for human approval, which is rare at this level of fidelity. The Singularity platform covers endpoints, cloud workloads, and identity under one console, making it a genuinely unified surface for detection and response.
SentinelOne Singularity Key Features
- Purple AI: An agentic AI analyst built into the platform that automates triage, threat hunting, and investigation using natural language queries.
- Singularity Hyperautomation: A no-code interface for building and executing automated response workflows directly inside the Singularity Platform.
- AI SIEM: Ingests and normalizes third-party and native telemetry into a single data layer for unified detection, investigation, and response.
- Singularity Mobile: Extends real-time endpoint protection to mobile devices, blocking phishing, malware, and zero-day exploits on iOS and Android.
SentinelOne Singularity Integrations
SentinelOne Singularity offers one-click integrations through its Singularity Marketplace, including Splunk, IBM QRadar, ServiceNow, Okta, Zscaler, Netskope, Recorded Future, Swimlane, AWS, and Mimecast. An API is also available for custom integrations and automation workflows.
Pros and Cons
Pros:
- ActiveEDR can autonomously roll back ransomware attacks
- Purple AI automates incident triage and hunting
- Storyline technology reconstructs full attack narratives
Cons:
- Some advanced features only in premium tiers
- Requires tuning to reduce initial alert volume
Learn more about SentinelOne Singularity: Best for legacy enterprise endpoints
- Free demo available
- Pricing upon request
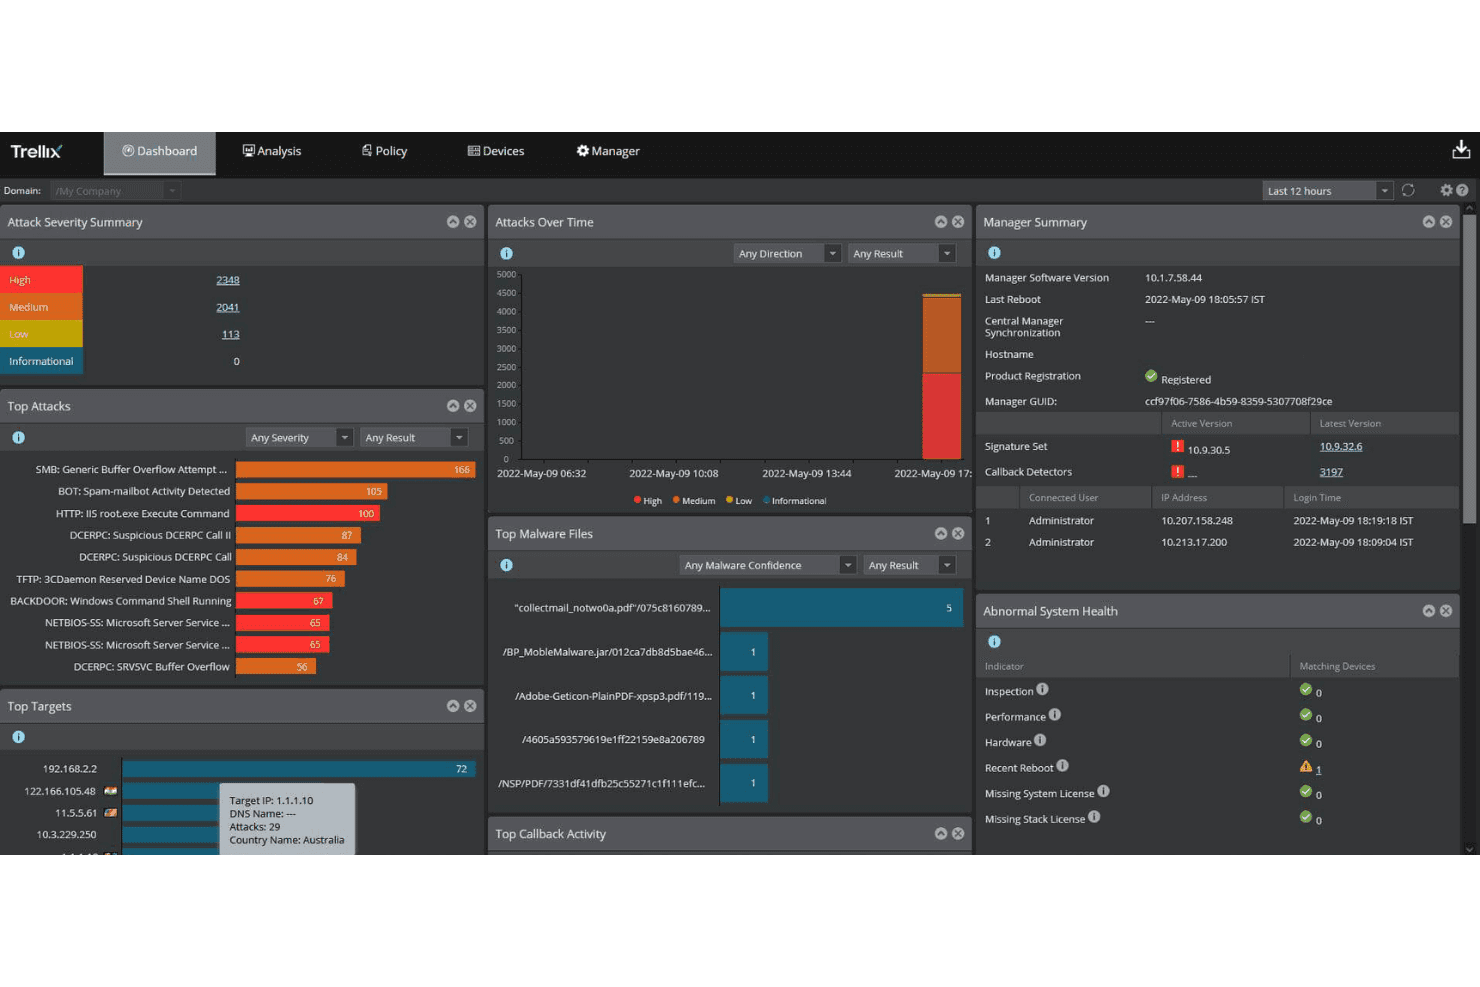
Trellix centralizes threat monitoring across severity, targets, and malware activity. Trellix Endpoint Security is an AI-powered endpoint protection platform that combines threat detection, application control, and cloud workload security across physical, virtual, and hybrid environments using a single agent.
Who Is Trellix Endpoint Security Best For?
Trellix Endpoint Security is a strong fit for large enterprises managing mixed environments that include older operating systems and legacy infrastructure alongside modern endpoints.
Why I Picked Trellix Endpoint Security
Trellix Endpoint Security earns its spot on my list because of how seriously it takes legacy infrastructure, something most modern EPP vendors quietly avoid. Trellix extends support for Windows XP-based systems through December 2028, which is a real differentiator if your environment includes older OT devices, industrial systems, or endpoints that simply can't be upgraded. I also like its Application and Change Control feature, which locks down servers and workstations by allowing only trusted applications to run, a key control for environments where patch cycles are irregular. The single-agent architecture covers on-premises, cloud, and air-gapped deployments without requiring separate tooling.
Trellix Endpoint Security Key Features
- Adaptive threat protection: Uses machine learning and behavioral analysis to detect and block file-based, fileless, and script-based threats in real time.
- Trellix ePolicy Orchestrator (ePO): A centralized management console for configuring, enforcing, and auditing endpoint security policies across on-premises, IaaS, and SaaS deployments.
- Threat Intelligence Exchange (TIE): Shares real-time threat intelligence across endpoints, email gateways, and network sensors so detections on one system inform protection across your entire environment.
- Trellix Wise: An AI-powered investigation engine that correlates alerts across endpoint, email, network, and cloud sources, then generates investigation summaries with containment and remediation recommendations.
Trellix Endpoint Security Integrations
Trellix Endpoint Security connects through Trellix ePolicy Orchestrator (ePO), which integrates with 150+ third-party security and IT tools, including ServiceNow, Splunk, Swimlane, BeyondTrust, MobileIron, IBM Resilient, AWS, and Microsoft Azure, plus Trellix products like EDR, DLP, and Email Security. An API is available for custom integrations, and the Trellix Marketplace hosts additional partner apps for SIEM, SOAR, and threat intelligence workflows.
Pros and Cons
Pros:
- Application and change control for legacy systems
- Single agent covers mixed physical and virtual endpoints
- Extends support for Windows XP environments
Cons:
- Policy configuration complexity frustrates new admins
- Interface feels dated compared to competitors
Learn more about Trellix Endpoint Security: Best for Microsoft 365-based orgs
- Not available
- Pricing upon request
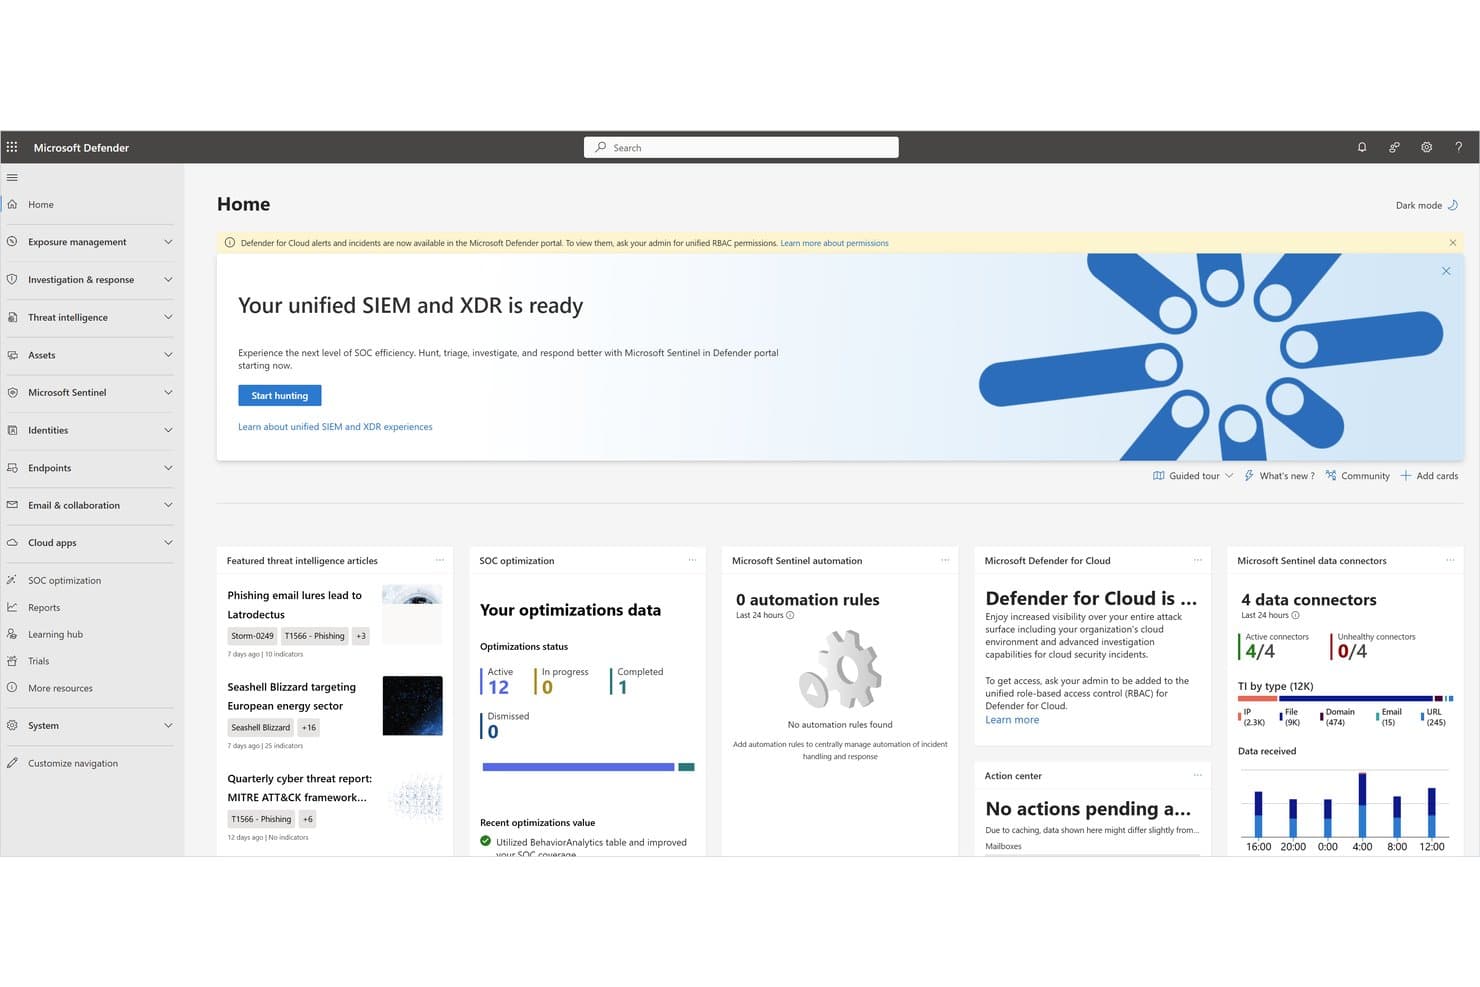
Microsoft Defender for Endpoint unifies SIEM and XDR for streamlined SOC operations. Microsoft Defender for Endpoint is a cloud-native endpoint protection platform that combines threat detection, vulnerability management, attack surface reduction, and extended detection and response (XDR) capabilities across Windows, macOS, Linux, iOS, and Android devices.
Who Is Microsoft Defender for Endpoint Best For?
It's a natural fit for organizations already running Microsoft 365 or Azure, where native integration with the Microsoft security stack removes the need for third-party endpoint agents.
Why I Picked Microsoft Defender for Endpoint
Microsoft Defender for Endpoint earns its spot on my shortlist because it's built directly into the Microsoft ecosystem, which means if your org runs Microsoft 365, you're getting XDR coverage without bolting on a separate agent. I particularly like how its attack surface reduction rules let you lock down specific behaviors, like blocking Office applications from spawning child processes, across your entire device fleet from a single policy. The integration with Microsoft Sentinel also means threat signals from endpoints feed directly into your SIEM without manual connector configuration.
Microsoft Defender for Endpoint Key Features
- Threat and vulnerability management: Continuously scans enrolled endpoint devices to surface misconfigurations, missing patches, and software vulnerabilities ranked by exposure risk.
- Automated investigation and remediation: Automatically triages alerts, traces attack chains, and resolves threats on affected endpoints without requiring manual analyst intervention.
- Live response: Opens a remote shell session to an endpoint so you can collect forensic artifacts, run scripts, and isolate or remediate a device in real time.
- Behavioral blocking and containment: Detects and stops suspicious in-memory and process behaviors on-device, even when malware attempts to evade signature-based detection.
Microsoft Defender for Endpoint Integrations
Microsoft Defender for Endpoint has native integrations across the Microsoft ecosystem, including Microsoft Sentinel, Microsoft Intune, Microsoft Entra ID, Microsoft Defender for Cloud, Microsoft Defender for Identity, Microsoft Purview, and Azure. It also connects with third-party tools like ServiceNow, Splunk, and Jamf Pro, and provides APIs for custom integrations and SIEM connectors.
Pros and Cons
Pros:
- Automated triage reduces manual incident response
- Attack surface reduction applies to entire fleet
- Native integration with Microsoft security stack
Cons:
- Limited support for non-Microsoft environments
- No trial option for hands-on evaluation
Learn more about Microsoft Defender for Endpoint: Best for defense with identity context
- Free demo available
- Pricing upon request
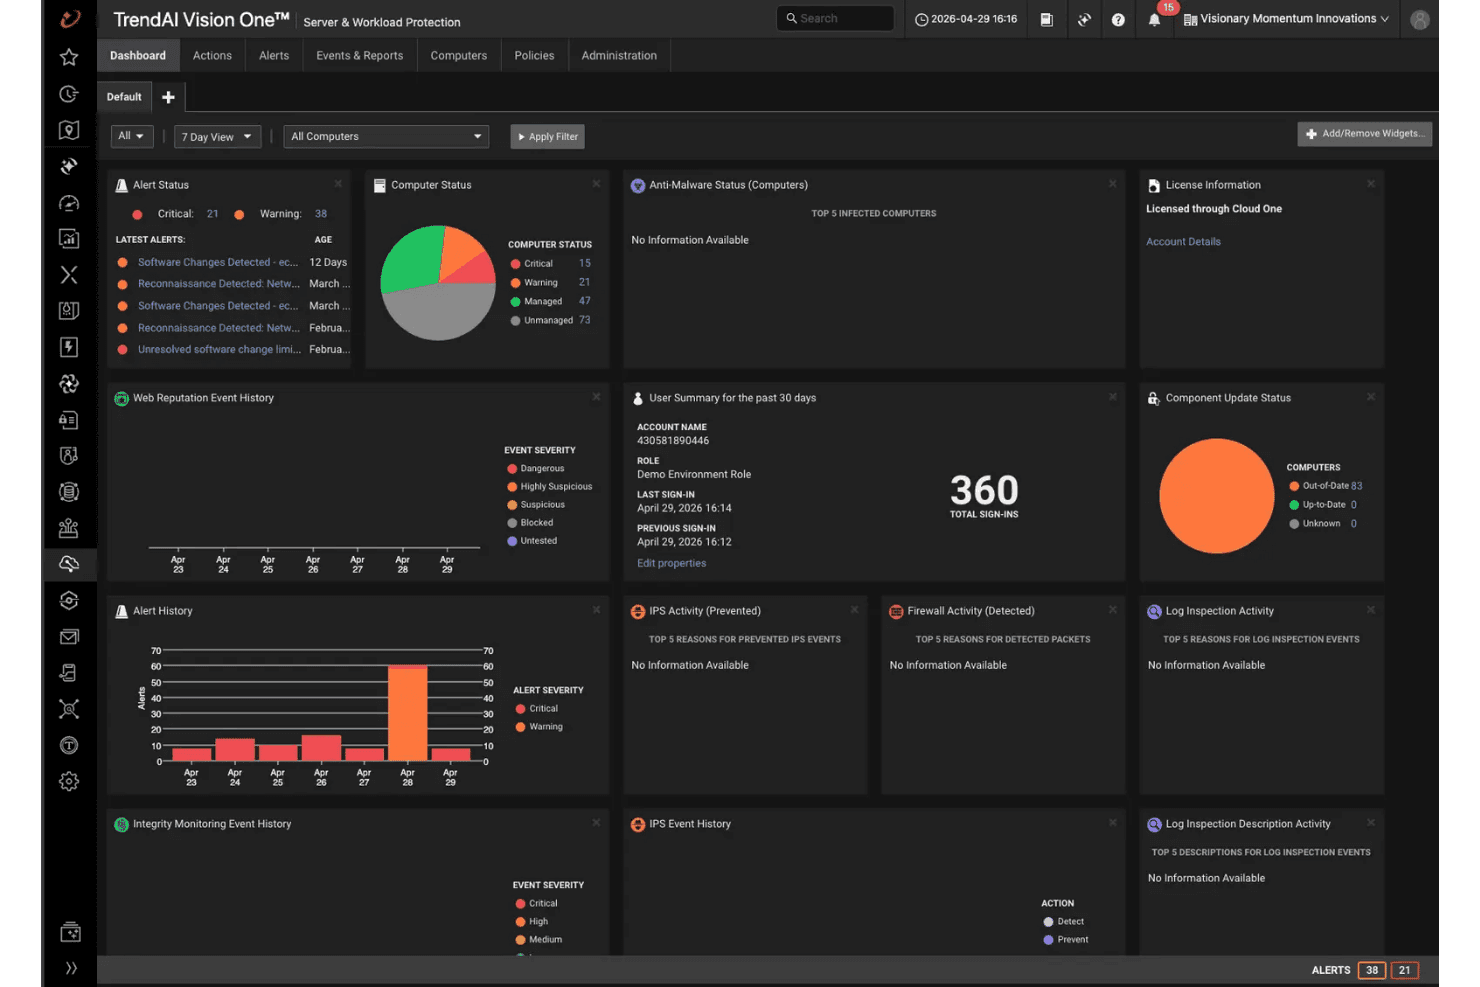
TrendAI Vision One offers security alerts and computer status at a glance. TrendAI Vision One is an AI-powered endpoint protection platform that combines EDR, XDR, automated incident response, and attack surface risk management across endpoints, servers, cloud workloads, and IoT environments from a single console.
Who Is TrendAI Vision One Best For?
TrendAI Vision One is a strong fit for enterprise security teams managing hybrid environments who need endpoint, identity, and XDR threat detection unified in a single console.
Why I Picked TrendAI Vision One
TrendAI Vision One earns its spot on my list because of how it ties identity signals directly into endpoint defense. When an alert fires, the platform automatically enriches it with identity context, asset risk, and exposure data, so analysts aren't chasing answers across disconnected tools. I also like that it accounts for Microsoft Entra ID security defaults when evaluating identity risk, which adds a layer of precision to prioritization. That combination of native XDR telemetry and identity-aware detection is what makes it genuinely useful when investigating lateral movement or compromised credentials.
TrendAI Vision One Key Features
- Virtual patching: Applies protection rules for known vulnerabilities at the network layer before a formal patch is deployed, reducing exposure on unpatched endpoints and servers.
- Behavioral analysis: Monitors process activity and execution patterns in real time to detect ransomware and exploit techniques that signature-based detection alone would miss.
- Automated security playbooks: Lets you configure predefined response actions that trigger automatically when specific threat conditions are met, reducing manual triage time.
- Attack surface risk management: Continuously inventories devices, accounts, and vulnerabilities across your environment and assigns risk scores to help you prioritize remediation.
TrendAI Vision One Integrations
TrendAI Vision One supports native integrations with Active Directory, Microsoft Entra ID, Google Cloud Identity, Okta, Splunk, Azure Sentinel, ServiceNow, AWS S3, QRadar, and Palo Alto Panorama, along with connectors for Cortex XSOAR, Chronicle SOAR, FortiGate, Check Point, Rapid7 Nexpose, Nessus, MISP, and VirusTotal. An API is available for custom integrations, and syslog and TAXII feeds are supported for extending data sharing across your security stack.
Pros and Cons
Pros:
- Automated security playbooks for fast incident response
- Virtual patching protects unpatched endpoints and servers
- Identity context enriches every security alert
Cons:
- Asset inventory can miss some IoT devices
- Advanced features may require additional training
Learn more about TrendAI Vision One :
Andre plattformer for endepunktbeskyttelse
Her er noen flere alternativer for plattformer for endepunktbeskyttelse som ikke kom med på kortlisten min, men som likevel er verdt å se nærmere på:
- 11FortiClientBest for Fortinet Security Fabric ecosystem protection
- 12Kaspersky NextBest for enterprises outside US-aligned markets
- 13Acronis Cyber Protect CloudBest for backup-native endpoint security built for MSPs
- 14N-ableBest for MSP-native endpoint defense with built-in RMM
- 15Elastic Security Best for unified SIEM, XDR, and endpoint defense
- 16Cybereason EDRBest for operation-centric attack correlation
- 17VMware Carbon Black EndpointBest for deep EDR telemetry in complex enterprise SOCs
- 18Cisco Secure EndpointBest for Cisco-native security ecosystem
- 19WatchGuard EPDRBest for MSPs managing endpoint security at scale
- 20ESET Protect EliteBest for built-in patch management
How I Evaluate Endpoint Protection Platforms
When a ransomware strain bypasses prevention and starts encrypting files, I want to know exactly which tools can stop it, roll it back, and tell me how it got in—so I split my evaluation into baseline criteria every tool must meet and differentiators that separate the best from the rest.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, using 75% as a benchmark to help assess its overall fit for the list.
- Threat prevention: I evaluate how many detection layers a platform stacks—signatures, behavioral analysis, ML models, and exploit blocking—and whether it holds up against fileless attacks, not just commodity malware.
- Endpoint detection and response: Deep telemetry, root cause analysis, and MITRE ATT&CK mapping matter here. I look for tools that let analysts hunt threats and trace lateral movement across endpoints without jumping between consoles.
- Centralized management console: I check for multi-tenant support, role-based access controls, and real-time visibility across distributed fleets. Platforms like CrowdStrike Falcon and Microsoft Defender for Endpoint both offer cloud-native consoles, but the depth of policy granularity and API access varies.
- Multi-OS endpoint support: Coverage across Windows, macOS, and Linux desktops and servers is baseline. I also evaluate whether mobile and cloud workload agents maintain feature parity with desktop counterparts.
- Automated response and remediation: Playbook-driven containment—endpoint isolation, process kills, file quarantine, and rollback of malicious changes—reduces mean time to respond. I look at how much of that workflow runs without manual intervention.
- Threat intelligence integration: Real-time feeds with contextual enrichment and adversary attribution give SOC teams an edge. I evaluate whether the platform supports third-party feed ingestion alongside its own proprietary intelligence network.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Ransomware rollback is the first thing I check beyond baseline detection. I want to know if a platform can revert encrypted files to a pre-infection state automatically—without depending on external backups. Identity threat protection is equally high on my list. Platforms that tie into Active Directory or Okta to flag credential misuse and privilege escalation give SOC teams visibility that standalone EDR misses. I also evaluate XDR data fabric capabilities, since correlating endpoint, cloud, and email telemetry in one query layer cuts investigation time dramatically during cross-domain incidents.
Beyond Features
I check whether a platform offers open API access and pre-built SIEM connectors—tools like Splunk or Microsoft Sentinel need clean telemetry feeds, and gaps here create blind spots in your SOC workflows. Licensing transparency matters just as much: I evaluate whether EPP, EDR, XDR, and MDR tiers are clearly separated so you're not hit with surprise upsells when you need ransomware rollback or managed hunting. For teams serving regulated industries, I look at compliance-ready reporting for frameworks like HIPAA, PCI-DSS, and NIST 800-171, plus data residency options that support regional obligations.
Slik velger du en plattform for endepunktbeskyttelse
Når sikkerhetsstakken din er selve grunnlaget for virksomhetens kontinuitet, hvordan kan du være sikker på at plattformen for endepunktbeskyttelse du velger, faktisk oppfyller de viktigste kravene til gjenkjenning, respons og operasjonell tilpasning?
| Hvis prioriteten din er … | Se etter … |
|---|---|
| Hvis prioriteten din er …Rask tilbakerulling etter løsepengevirus | Se etter …Innebygd, agentbasert filgjenoppretting uten avhengighet av ekstern sikkerhetskopiering |
| Hvis prioriteten din er …Støtte for hybride eller eldre miljøer | Se etter …Dokumenterte distribusjonsveiledninger og støttede agenter for alle nødvendige operativsystemer og all nødvendig maskinvare |
| Hvis prioriteten din er …Integrasjon med XDR og SIEM | Se etter …Åpen API-tilgang og ferdigbygde datakoblinger for stakken din |
| Hvis prioriteten din er …Overholdelse av krav i flere regioner | Se etter …Leverandørdokumentasjon om datalagring i riktig region og revisjonslogger for tilsynsmyndigheter |
| Hvis prioriteten din er …Minimalt behov for interne sikkerhetsressurser | Se etter …Inkluderte alternativer for administrert gjenkjenning og respons, ikke bare EDR |
Slik vurderer du kortlisten din
- Kjør en kontrollert løsepengevaresimulering: Krev full tilbakeføring av minst 5 krypterte filer i laboratorienettverket ditt.
- Test dekningen for OS-agenter: Distribuer til 2 eller flere eldre eller nisjepregede endepunkter, og bekreft at alle kjernefunksjoner fungerer uten manuell justering.
- Be om integrasjonsdokumentasjon: Be om skjemaveiledninger eller dokumentasjon for oppsett av SIEM-koblinger som er spesifikk for plattformene du trenger.
- Gjennomgå koblingen til samsvar: Skaff en skriftlig erklæring eller et brev fra en revisor som viser kontroller for regional datalagring.
- Avklar avveiningen mellom operasjonell kontroll: Bestem om du ønsker innsyn internt med verktøybasert EDR, eller foretrekker en håndfri tjeneste for administrert deteksjon og respons – et viktig filter når du snevrer inn alternativene.
Hva er plattformer for endepunktbeskyttelse?
Plattformer for endepunktbeskyttelse er sentraliserte sikkerhetsløsninger som oppdager, forhindrer og håndterer trusler mot enheter i nettverket ditt. Disse plattformene overvåker stasjonære datamaskiner, bærbare datamaskiner, servere og mobile enheter for å blokkere skadevare, løsepengevirus og uautorisert tilgang. Ved å gi innsyn i sanntid, koordinerte verktøy for håndtering og integrasjon med bredere sikkerhetssystemer hjelper plattformer for endepunktbeskyttelse IT-team med å redusere risiko, begrense hendelser og opprettholde samsvar i komplekse miljøer.
Funksjoner
Når du velger plattformer for endepunktbeskyttelse, bør du se etter følgende viktige funksjoner:
- Trusselforebygging: Identifiserer og blokkerer kjent og ukjent skadevare, løsepengevirus og utnyttelser ved hjelp av signaturbasert og atferdsbasert analyse før truslene kan kjøres på endepunkter.
- Deteksjon og respons for endepunkter: Overvåker kontinuerlig endepunkter, registrerer systemaktiviteter og gjør det mulig for hendelsesresponsteam å undersøke trusler, spore angrepets opphav og kartlegge omfanget av hendelser.
- Sentralisert administrasjonskonsoll: Gir et samlet nettbasert dashbord for å distribuere agenter, administrere sikkerhetspolicyer, se varsler og generere rapporter for alle endepunkter fra ett sted.
- Støtte for flere operativsystemer: Gir beskyttelse for enheter som kjører ulike operativsystemer, for eksempel Windows, macOS og Linux – og dekker stasjonære datamaskiner, bærbare datamaskiner, servere og noen ganger mobile enheter.
- Automatisert respons og utbedring: Isolerer automatisk kompromitterte endepunkter, avslutter ondsinnede prosesser, setter infiserte filer i karantene og tilbakefører endringer fra angrep for å redusere tiden det tar å håndtere hendelser.
- Integrasjon med trusselintelligens: Henter inn sanntidsstrømmer og indikatorer på kompromittering fra globale kilder for å ligge i forkant av nye trusler og forbedre deteksjonen med kontekstbasert innsikt.
- Rollebasert tilgangskontroll: Lar organisasjoner tildele tillatelser og roller til brukere og administratorer, slik at bare autorisert personale kan administrere endepunkter, justere policyer eller få tilgang til sensitiv sikkerhetsinformasjon.
- Samsvarsrapportering: Genererer forhåndsbygde og tilpassbare rapporter tilpasset regelverksrammeverk, noe som gjør det enklere for sikkerhets- og samsvarsteam å dokumentere at de følger nødvendige standarder.
- Distribusjonsalternativer i skyen og lokalt: Støtter både skybaserte og lokale implementeringer, slik at organisasjoner kan velge modellen som passer infrastrukturen og regelverkskravene deres.
- Patchadministrasjon og sårbarhetsskanning: Overvåker endepunkter for manglende oppdateringer, søker etter sårbarheter og hjelper IT-team med å prioritere og distribuere oppdateringer for å redusere sikkerhetsrisiko.
Vanlige AI-funksjoner
I tillegg til standardfunksjonene for plattformer for endepunktbeskyttelse som er nevnt ovenfor, tar mange av disse løsningene i bruk AI med funksjoner som:
- AI-drevet trusseljakt: Bruker maskinlæring til automatisk å analysere telemetri fra endepunkter, identifisere mistenkelige mønstre og avdekke potensielle trusler som menneskelige analytikere kan overse. Dette hjelper teamet ditt med å oppdage avanserte angrep proaktivt før de eskalerer.
- Automatisert atferdsanalyse: Overvåker kontinuerlig bruker- og prosessatferd på endepunkter og bruker kunstig intelligens til å markere avvik som kan indikere interne trusler, misbruk av legitimasjon eller nulldagssårbarheter. Dette reduserer antallet falske positiver og hjelper med å prioritere reelle risikoer.
- Prediktiv skadevareoppdagelse: Benytter KI-modeller som er trent på omfattende datasett, til å identifisere og blokkere skadevare som aldri er sett før, basert på kodeegenskaper og kjøringsmønstre – ikke bare kjente signaturer.
- Adaptiv beskyttelse mot phishing: Bruker KI til å analysere e-postinnhold, nettadresser og brukerinteraksjoner i sanntid, og blokkerer phishingforsøk og angrep som forsøker å stjele påloggingsinformasjon etter hvert som de utvikler seg.
- KI-drevet hendelsessortering: Korrelaterer automatisk varsler, tildeler risikopoeng og anbefaler responshandlinger, slik at teamet ditt kan konsentrere seg om de mest presserende truslene og redusere tiden som brukes på undersøkelser.
- Trusselrapportering på naturlig språk: Genererer sammendrag av hendelser og angrepskjeder på dagligspråk ved hjelp av KI, noe som gjør det enklere for IT- og sikkerhetsteam å kommunisere funn til interessenter og dokumentere responshandlinger.
Fordeler
Implementering av plattformer for endepunktbeskyttelse gir flere fordeler for teamet ditt og virksomheten din. Her er noen av fordelene du kan se frem til:
- Trusselforebygging på tvers av enheter: Blokker skadevare, løsepengevirus og utnyttelsesangrep med signaturbasert og atferdsbasert deteksjon på tvers av stasjonære og bærbare datamaskiner, servere og mobile enheter.
- Sentralisert oversikt og kontroll: Bruk en samlet administrasjonskonsoll til å overvåke sikkerhetspolicyer, varsler og samsvarsstatus for hvert endepunkt i miljøet ditt.
- Automatisert respons og rask utbedring: Begrens trusler raskt ved hjelp av handlinger styrt av responsplaner, som isolering av endepunkter, avslutning av prosesser, filkarantene og tilbakerulling av uautoriserte endringer.
- Støtte for flere operativsystemer og hybride miljøer: Beskytt blandede enhetsparker, inkludert Windows, macOS, Linux og noen ganger mobile enheter eller skyarbeidsbelastninger, uten manuell finjustering eller bytte av agenter.
- Integrert trusselintelligens: Utnytt sanntidsbaserte og kontekstrike trusselfeeder samt innsikt i trusselaktører for å forbedre arbeidsflyter for deteksjon og undersøkelser.
- Rapportering for overholdelse av regelverk: Generer innebygde eller tilpassbare rapporter som er knyttet til rammeverk som HIPAA, PCI-DSS og NIST 800-171, slik at du kan dokumentere kontroll overfor revisorer og interessenter.
- Tilgang til åpne API-er og SIEM-koblinger: Send rene telemetridata til SIEM-plattformer og automatiser arbeidsflyter ved å koble sømløst til verktøy for sikkerhetsoperasjoner og overvåking.
Kostnader og priser
Ved valg av plattformer for endepunktbeskyttelse må du forstå de ulike prismodellene og abonnementene som er tilgjengelige. Kostnadene varierer basert på funksjoner, teamstørrelse, tillegg og mer. Tabellen nedenfor oppsummerer vanlige abonnementer, gjennomsnittsprisene deres og typiske funksjoner som inngår i løsninger for plattformer for endepunktbeskyttelse:
Sammenligningstabell for abonnementer
| Abonnementstype | Gjennomsnittspris | Vanlige funksjoner |
|---|---|---|
| AbonnementstypeGratisabonnement | Gjennomsnittspris$0 | Vanlige funksjonerGrunnleggende skadevareoppdagelse, begrenset enhetsstøtte og minimal rapportering. |
| AbonnementstypePersonlig abonnement | Gjennomsnittspris$3-$10/bruker/måned | Vanlige funksjonerGrunnleggende trusselforebygging, sanntidsbeskyttelse, støtte for flere enheter og grunnleggende sentralisert administrasjon. |
| AbonnementstypeForretningsabonnement | Gjennomsnittspris$15-$35/bruker/måned | Vanlige funksjonerAvansert endepunktdeteksjon og -respons, policyadministrasjon, rollebasert tilgangskontroll, automatisert utbedring og samsvarsrapportering. |
| AbonnementstypeStorbedriftsabonnement | Gjennomsnittspris$40-$75/bruker/måned | Vanlige funksjonerStøtte for flere operativsystemer, integrasjon med avansert trusselintelligens, API- og SIEM-koblinger, tilbakerulling etter løsepengevirusangrep og førsteklasses kundestøtte. |
Vanlige spørsmål om plattformer for endepunktbeskyttelse
Her er noen svar på vanlige spørsmål om plattformer for endepunktbeskyttelse:
Hvordan håndterer plattformer for endepunktbeskyttelse nulldagstrusler?
De fleste plattformer for endepunktbeskyttelse bruker en kombinasjon av AI-drevet atferdsanalyse og trusselintelligens i sanntid for å oppdage og blokkere nulldagstrusler. I stedet for å basere seg utelukkende på kjente skadevaresignaturer overvåker disse plattformene prosessatferd, nettverkstilkoblinger og mistenkelige filer for tegn på nye eller ukjente angrep. Du kan forvente at verktøyene isolerer eller ruller tilbake systemer hvis en nulldagssårbarhet blir oppdaget, slik at mulig skade reduseres selv før en oppdatering er tilgjengelig.
Kan plattformer for endepunktbeskyttelse støtte eksterne og hybride arbeidsmiljøer?
Ja, de fleste moderne plattformer for endepunktbeskyttelse er utviklet for å støtte eksterne og hybride arbeidsmodeller. Se etter skybaserte administrasjonskonsoller og agenter som ikke trenger tilkobling til lokale systemer for å oppdatere retningslinjer og overvåke enheter kontinuerlig. Dette betyr at du kan opprettholde oversikt og kontroll over stasjonære datamaskiner, bærbare datamaskiner og mobile endepunkter, uansett hvor brukerne dine arbeider fra.
Hva er forskjellen mellom EDR og XDR i plattformer for endepunktbeskyttelse?
Endepunktdeteksjon og -respons (EDR) fokuserer på å overvåke aktivitet og reagere på trusler direkte på enheter som bærbare datamaskiner og servere. Utvidet deteksjon og respons (XDR) går et skritt videre ved å integrere telemetri fra flere kilder – som endepunkter, skytjenester, e-post og identitetssystemer. Med XDR kan teamet ditt avdekke angrepsmønstre som krysser plattformer eller verktøygrenser, noe som gjør det enklere å undersøke og begrense trusler på flere nivåer.
Hvordan vet jeg om en plattform for endepunktbeskyttelse oppfyller samsvarskravene?
Sjekk leverandørens dokumentasjon for ferdig utarbeidede samsvarsrapporter, revisjonserklæringer eller sertifiseringer knyttet til standarder som HIPAA, PCI-DSS og NIST 800-171. De fleste plattformer tilbyr rapporteringsverktøy som kobler direkte til regulatoriske rammeverk. Det er lurt å be om informasjon om datalagring i riktig region hvis virksomheten din opererer i flere land eller må følge strenge lokale datalover.
Påvirker plattformer for endepunktbeskyttelse enhetens ytelse?
De fleste plattformer for endepunktbeskyttelse forsøker å minimere ressursbruken, men noen kan gjøre eldre enheter tregere under skanning eller omfattende analyse. Du bør teste agenter i miljøet ditt for å se hvordan de påvirker oppstartstider, CPU, minne og brukernes arbeidsflyter. Se etter verktøy med ressursbesparende agenter eller konfigurerbare skanneplaner hvis ytelse er en viktig bekymring for teamet ditt.
Kan plattformer for endepunktbeskyttelse integreres med SIEM- eller IT-administrasjonsverktøyene mine?
Ja, mange plattformer for endepunktbeskyttelse tilbyr åpne API-er og innebygde koblinger for populære SIEM- og IT-administrasjonsverktøy som Splunk, Microsoft Sentinel og ServiceNow. Du bør gjennomgå API-dokumentasjonen og tilgjengelige integrasjonsveiledninger tidlig – gode integrasjoner hjelper deg med å automatisere arbeidsflyter, samle varsler og redusere risikoen for å gå glipp av viktige hendelser.