
Reseña de IBM QRadar 2026: Características clave, ventajas, desventajas y precios
IBM QRadar destaca por su sólida detección de amenazas y escalabilidad, aunque puede estar mejor orientado a organizaciones grandes que busquen análisis profundos por encima de la facilidad de uso o un despliegue rápido.

Revisamos herramientas de forma independiente y las comisiones ayudan a financiar nuestras pruebas. Consulta nuestra política de transparencia, nuestra metodología o sugiere una herramienta.
IBM Security QRadar SIEM is a SIEM tool built for security operations teams managing threat detection, log correlation, and incident investigation across large, distributed environments. It's worth considering if your team handles high volumes of network flow and event data and needs built-in correlation rules, threat intelligence, and behavioral analytics without building that capability from scratch. I'd choose it over Splunk when your primary focus is security operations specifically—QRadar is purpose-built for that use case, while Splunk demands significantly more customization to deliver the same depth of security-focused detection out of the box.
IBM Security QRadar SIEM Evaluation Summary

4.5/5
- Pricing upon request
- Free demo available
Por qué confiar en nuestras recomendaciones de software
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Nuestro equipo lleva probando y evaluando software desde 2012. Como líderes tecnológicos, sabemos lo difícil —y lo importante— que es elegir el software adecuado.
Para esta guía, evaluamos las herramientas mediante pruebas prácticas e investigación independiente, puntuando las herramientas según nuestros criterios de selección.
Nuestras reseñas reflejan nuestro criterio editorial humano, no un discurso de ventas.
Revisores expertos:
- Paulo Gardini MiguelDirector técnico
 Tim FisherVP de IA
 Gabriel RosasTech Lead y arquitecto de software
 Christhian GruhnTech Lead y arquitecto de plataforma

IBM Security QRadar SIEM Overview
When judging IBM QRadar as a SIEM Tool, its advanced analytics, broad integration options, and strong threat detection set it apart for organizations with complex security needs. The interface can feel dated, and onboarding may require more time than some competitors, but its depth of functionality and responsive support make it a top choice for enterprises prioritizing thorough investigation and compliance.
Pricing is on the higher end, yet justified for those needing scalable, customizable deployments. If you’re selecting a SIEM for a large, regulated environment, QRadar’s capabilities often outweigh its steeper learning curve.
Pros
- Streamlines compliance reporting for regulated industries
- Strong user and network behavior analytics capabilities
- Advanced threat detection with real-time analytics
Cons
- Pricing is higher than many mid-market SIEM solutions
- Initial setup and tuning require significant time investment
- Interface can feel outdated compared to newer tools
Is IBM Security QRadar SIEM Right For Your Needs?
Who Would be a Good Fit for IBM Security QRadar SIEM?
IBM QRadar is best suited for organizations with complex security requirements, high compliance demands, and large-scale environments. Its advanced analytics, automated threat detection, and strong compliance reporting make it a strong choice for industries where security and regulatory oversight are top priorities.
Teams with dedicated security staff and the resources to manage a sophisticated SIEM will benefit most from QRadar’s depth and scalability.
- Managed Security ProvidersMulti-tenant capabilities allow service providers to monitor multiple clients.
- Government AgenciesSupports FISMA and other government compliance requirements.
- Security Operations CentersCentralized threat detection and investigation tools fit SOC workflows.
- Healthcare OrganizationsQRadar’s HIPAA-ready tools help protect sensitive patient data.
- Financial ServicesIts compliance reporting and fraud detection features support strict regulatory needs.
- Large EnterprisesQRadar handles high event volumes and complex infrastructure with ease.
Who Would be a Bad Fit for IBM Security QRadar SIEM?
IBM QRadar is less suitable for smaller businesses, teams with limited IT resources, or organizations seeking a lightweight, low-maintenance SIEM. Its higher cost, complex setup, and resource requirements can outweigh the benefits for those with simpler security needs or limited budgets. Companies prioritizing rapid deployment or minimal ongoing management may find QRadar unnecessarily complex.
- Temporary ProjectTeams Long setup and tuning times don’t fit short-term projects.
- Remote-Only TeamsOn-premises or hybrid deployments may not suit fully remote operations.
- Retail ChainsMay be overkill for environments with basic compliance needs.
- Non-Technical DepartmentsRequires security expertise for configuration and ongoing management.
- StartupsResource requirements and setup time are not startup-friendly.
- Small BusinessesThe cost and complexity exceed what most small teams need.
Nuestra metodología de revisión
Cómo probamos y puntuamos las herramientas
Hemos invertido años construyendo, refinando y mejorando nuestro sistema de pruebas y puntuación de software. La rúbrica está diseñada para captar los matices de la selección de software y lo que hace a una herramienta efectiva, enfocándose en aspectos críticos del proceso de toma de decisiones.
A continuación, puedes ver exactamente cómo nuestro sistema de prueba y puntuación funciona a través de siete criterios. Esto nos permite ofrecer una evaluación imparcial del software basada en funcionalidad central, características destacadas, facilidad de uso, incorporación, soporte al cliente, integraciones, reseñas de clientes y relación calidad-precio.
Funcionalidad principal (25% de la puntuación final)
El punto de partida de nuestra evaluación siempre es la funcionalidad central de la herramienta. ¿Tiene las características y funciones básicas que un usuario esperaría encontrar? ¿Alguna de esas funciones principales está limitada a planes de precios superiores? Esperamos que una herramienta esté a la altura de las capacidades básicas de sus competidores.
Características destacadas (25% de la puntuación final)
Luego, evaluamos las características poco comunes y sobresalientes que van más allá de la funcionalidad principal que normalmente se encuentra en herramientas de su tipo. Una puntuación alta refleja características especializadas o únicas que hacen el producto más rápido, eficiente o que ofrecen valor adicional al usuario.
También evaluamos qué tan fácil es integrar con otras herramientas que normalmente forman parte del ecosistema tecnológico para expandir la funcionalidad y utilidad del software. Las herramientas que ofrecen abundantes integraciones nativas, conexiones de terceros y acceso API para crear integraciones personalizadas obtienen la mejor puntuación.
Facilidad de uso (10% de la puntuación final)
Consideramos cuán rápido y sencillo es ejecutar las tareas definidas por la funcionalidad principal usando la herramienta. El software con mejor puntuación está bien diseñado, es intuitivo, ofrece aplicaciones móviles, proporciona plantillas y hace que tareas relativamente complejas parezcan sencillas.
Incorporación (10% de la puntuación final)
Sabemos lo importante que es la adopción rápida por parte del equipo para una nueva plataforma, por lo que evaluamos cuán fácil es aprender y usar una herramienta con entrenamiento mínimo. Evaluamos cuán rápido un miembro del equipo puede configurarla y comenzar a utilizarla sin experiencia previa. Las soluciones con mayor puntuación requieren poco o ningún soporte.
Soporte al cliente (10% de la puntuación final)
Revisamos qué tan rápido y sencillo es resolver dudas y encontrar ayuda por teléfono, chat en vivo o base de conocimientos. Las herramientas y compañías que proporcionan soporte en tiempo real obtienen la mejor puntuación, mientras que los chatbots obtienen la peor.
Reseñas de clientes (10% de la puntuación final)
Además de nuestras pruebas y evaluaciones, consideramos la puntuación neta de promotores por parte de clientes actuales y anteriores. Revisamos la probabilidad de que elijan la herramienta de nuevo para la funcionalidad principal. Una puntuación alta refleja una alta puntuación neta de promotores actuales o pasados.
Relación calidad-precio (10% de la puntuación final)
Por último, considerando todos los demás criterios, revisamos el precio promedio de los planes de nivel básico comparado con las funciones principales y consideramos el valor de los demás criterios de evaluación. El software que ofrezca más, por menos, obtendrá una puntuación mayor.
Core Features
User Behavior Analytics
Detects insider threats by analyzing user actions and highlighting risky behavior. Helps uncover anomalous activity with clear, actionable insights.
Network Threat Analytics
Monitors network traffic in real time to identify suspicious patterns. Provides deep visibility into lateral movement and advanced attacks.
Sigma Community Rules
Supports thousands of open source Sigma rules for flexible, up-to-date threat detection. Lets analysts quickly import new detection logic as threats evolve.
Advanced Threat Detection
Correlates data from multiple sources to spot sophisticated attacks. Automates alerting and prioritization to reduce manual investigation time.
Threat Hunting
Enables analysts to search across datasets for hidden threats. Turns disparate security data into actionable intelligence for proactive defense.
Compliance Reporting
Generates audit-ready reports for regulations like HIPAA and FISMA. Streamlines evidence collection and documentation for internal and external audits.

Ease of Use
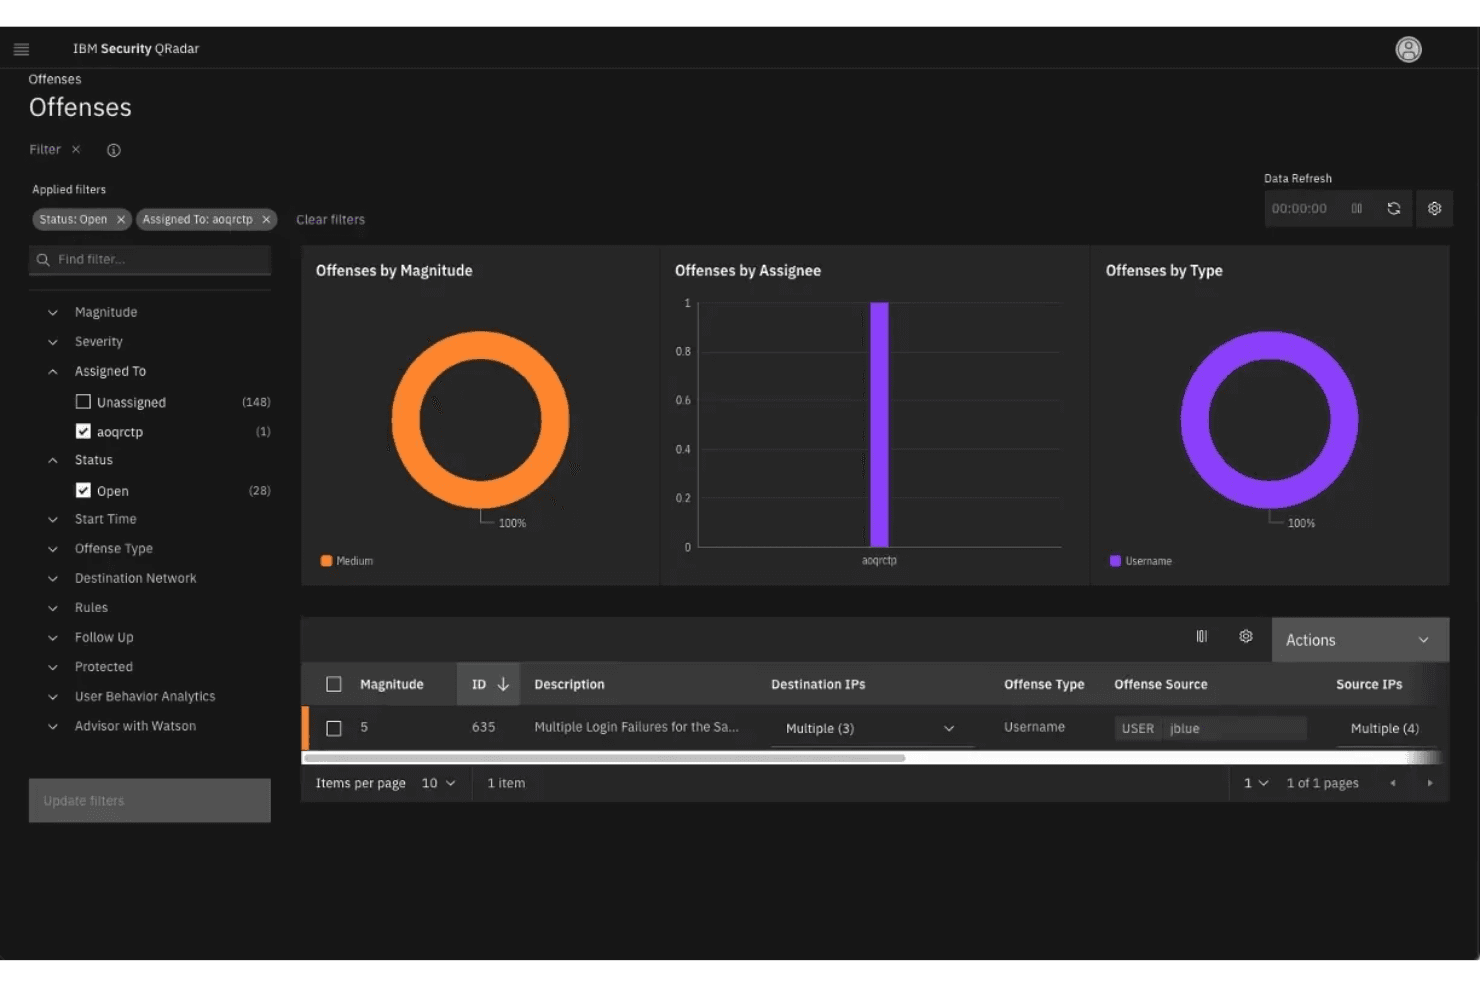
IBM QRadar offers deep functionality but can feel complex and overwhelming, especially during initial setup and tuning. Many users report that the interface is less intuitive than newer SIEM tools, requiring more training and expertise to navigate.
However, once configured, its dashboards and automated workflows provide clear visibility and efficient investigation paths for experienced security teams. The learning curve is offset by the platform’s powerful analytics and customization options.
Integrations
IBM QRadar integrates with AWS, Microsoft, Google Cloud, Palo Alto Networks, CrowdStrike, Trend Micro, Cisco, Splunk, Tenable, and Mimecast, among others.
IBM QRadar also offers a robust API and supports custom integrations, allowing connections with a wide range of third-party tools and platforms.

IBM Security QRadar SIEM Specs
- 2-Factor Authentication: Yes
- Anti-Virus: No
- API: Yes
- Bug Tracking: No
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- Data Visualization: Yes
- Email Integration: No
- External Integrations: Yes
- Firewall: No
- Google Apps Integration: No
- Malware Protection: No
- Multi-User: Yes
- Network Traffic Monitoring: Yes
- Network Visualization: Yes
- Notifications: Yes
- Third-Party Plugins/Add-Ons: Yes

