

O software de inventário de redes monitoriza, organiza e ajuda a gerir todos os ativos ligados à sua rede. Quando gere ambientes de TI, TO ou IoT, estas ferramentas oferecem visibilidade em tempo real, permitindo minimizar os riscos e acompanhar requisitos em constante mudança.
Se precisa de auditar, controlar ou automatizar a gestão dos seus ativos, está no sítio certo. Abaixo, encontrará o melhor software de inventário de redes para 2026, com opções que vão desde a descoberta em ambientes de nuvem híbrida até à documentação orientada para a conformidade.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Tabela comparativa de software de inventário de redes
Esta tabela comparativa resume os detalhes de preços das minhas principais seleções de software de inventário de redes:
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for AI-driven inventory and compliance audits | Free demo + 30-day free trial available | From $1,499/year | Website | |
| 2 | Best for hybrid network visibility | Free demo + 14-day free trial available | Not available | Website | |
| 3 | Best for automation-driven asset inventory | Free demo + 30-day free trial available | Pricing upon request | Website | |
| 4 | Best for agentless asset discovery | Free plan + 21-day free trial available | From $5,000/year | Website | |
| 5 | Best for auto-updating IT docs and compliance audits | 30-day free trial | From €465.00/year | Website | |
| 6 | Best for hybrid IT environments | Free trial + free demo available | Pricing upon request | Website | |
| 7 | Best for IT, OT, and IoT asset discovery in one view | Free demo + 14-day free trial available | From $239/month (billed annually) | Website | |
| 8 | Best for DC asset lifecycle and CMDB sync | Free demo available | Pricing upon request | Website | |
| 9 | Best for CMDB-connected asset discovery at scale | Free demo available | Pricing upon request | Website | |
| 10 | Best for enterprise-wide asset discovery sync | Free demo available | Pricing upon request | Website |


Análises de software de inventário de redes
Estas são as minhas principais escolhas de software. Resumi as principais funcionalidades, os casos de utilização e as integrações de cada opção, para que possa encontrar a solução mais adequada.
 Best for AI-driven inventory and compliance audits
- Free demo + 30-day free trial available
- From $1,499/year
Visit WebsiteCustomer Rating:4.6/5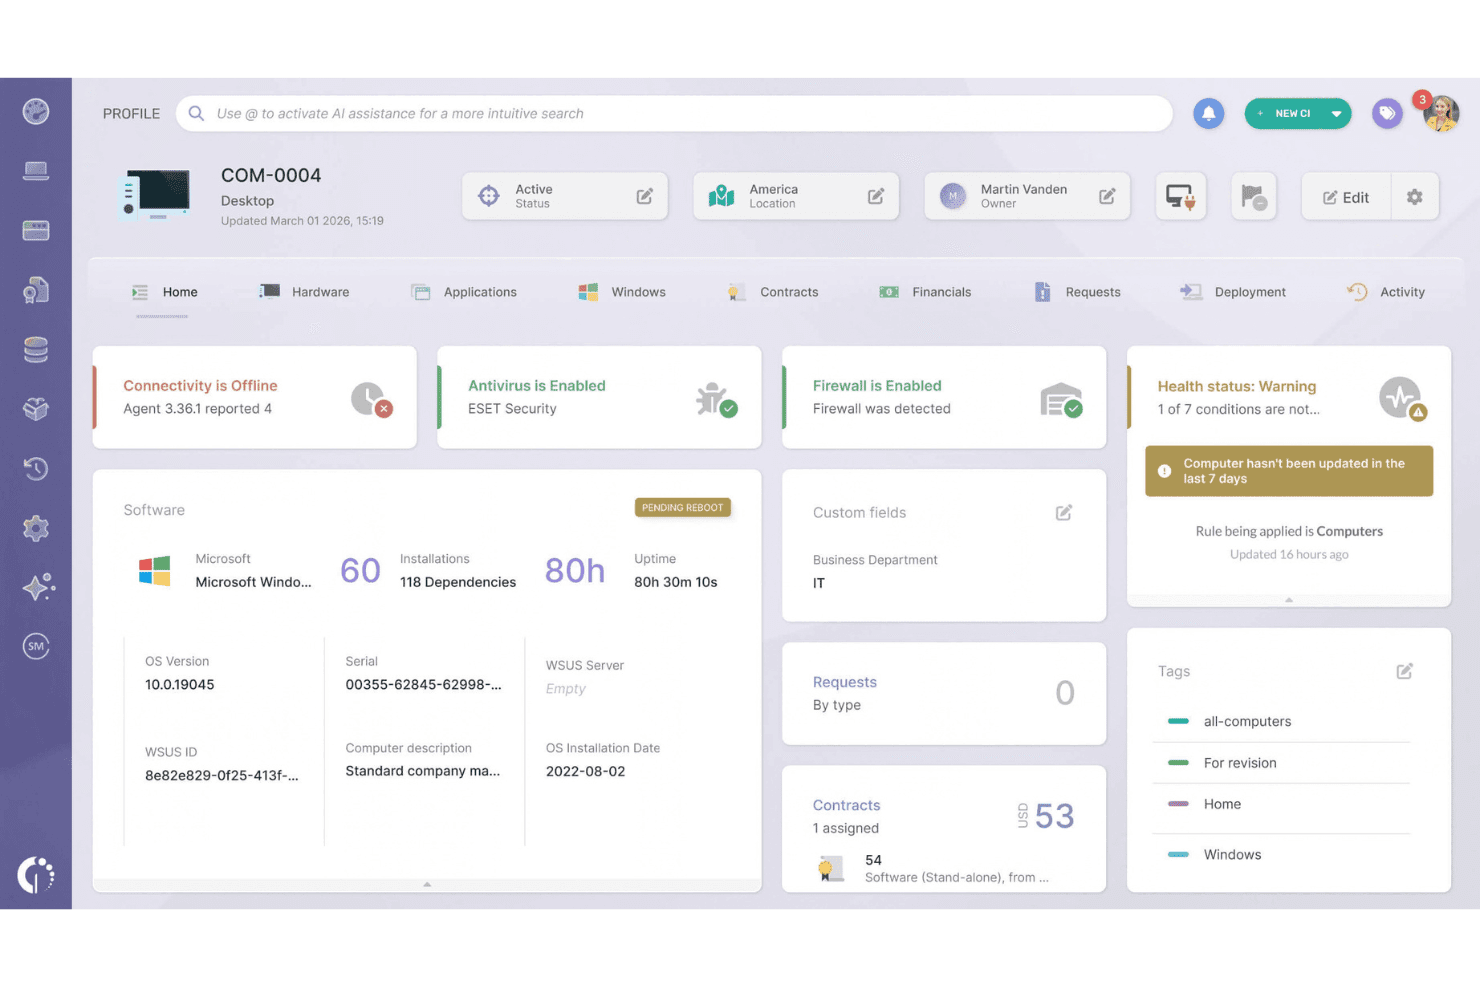
InvGate Asset Management displays full device health, software, and contract details. InvGate Asset Management is an IT asset management platform that combines agent-based and agentless network discovery, centralized hardware and software inventory, CMDB mapping, and compliance reporting across cloud, virtual, and on-premises environments.
Who Is InvGate Asset Management Best For?
InvGate Asset Management is a strong fit for IT teams in mid-to-large enterprises that need audit-ready inventory with built-in compliance reporting across GDPR, HIPAA, and PCI-DSS frameworks.
Why I Picked InvGate Asset Management
I picked InvGate Asset Management because its AI Hub genuinely changes how compliance audits work in practice. Instead of manually hunting for outdated or non-compliant assets, Smart Recommendations surfaces them automatically, with specific guidance on whether to update, replace, or reassign. The Atlas database layers in real end-of-life and end-of-support dates for hardware and software, so pre-built GDPR, HIPAA, and PCI-DSS compliance reports are grounded in accurate, current data.
InvGate Asset Management Key Features
- Agent-based endpoint inventory: A lightweight agent for Windows, macOS, Linux, and Android collects detailed hardware specs, installed software, and usage data daily, even when devices are off-network.
- Proxy-based agentless network scanning: Lightweight Discovery Proxies scan user-defined IP ranges using SNMP, WMI, and SSH to fingerprint servers, printers, routers, and switches without deploying agents.
- Automated CMDB with dependency mapping: The built-in CMDB maps relationships between assets, applications, users, and locations, with AI-assisted suggestions to keep dependency data current as your environment changes.
- Automated warranty tracking: Native API integrations with Dell and Lenovo auto-populate warranty expiration dates at the asset level, with Smart Tag automation and email alerts for upcoming expirations.
InvGate Asset Management Integrations
InvGate Asset Management offers native integrations across the Microsoft ecosystem, AWS, Google Cloud Platform, Jamf, VMware vCenter, Jira, and Zendesk. Its REST API supports custom integrations.
Pros and Cons
Pros:
- Built-in compliance dashboards and audit tools
- AI-powered recommendations for risky assets
- Dual agent-based and agentless device discovery
Cons:
- Automatic warranty sync limited to Dell and Lenovo
- No real-time network topology mapping
Learn more about InvGate Asset Management: Best for hybrid network visibility
- Free demo + 14-day free trial available
- Not available
Visit WebsiteCustomer Rating:4.5/5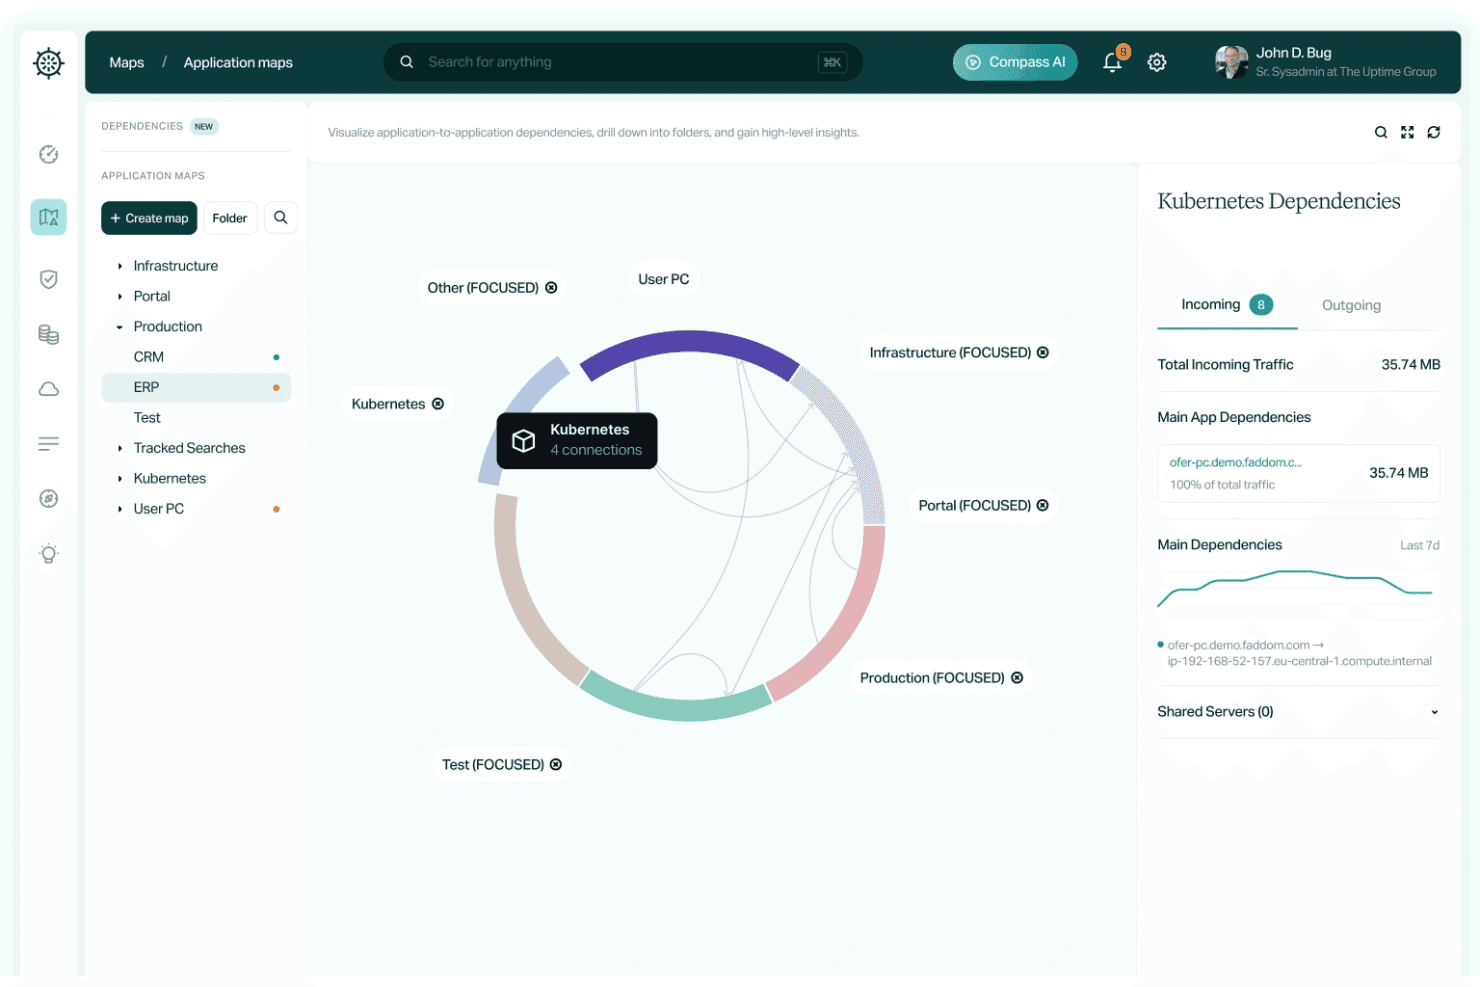
Faddom maps application dependencies with traffic insights. Faddom is an agentless network inventory and topology mapping tool that discovers servers, VMs, cloud instances, and application dependencies across on-premises and cloud environments using passive traffic analysis and protocols like NetFlow, SNMP, and sFlow.
Who Is Faddom Best For?
Faddom is a strong fit for enterprise IT and infrastructure teams managing hybrid environments who need real-time topology visibility without the overhead of agent deployment.
Why I Picked Faddom
I picked Faddom as one of the best because it gives you a complete, real-time topology map of your hybrid environment in under 60 minutes, with no agents and no credentials required by default. What I find impressive is how it handles both on-premises infrastructure and multi-cloud environments (AWS, Azure, GCP) within a single unified map, using passive traffic analysis via NetFlow, sFlow, and SNMP. Its Lighthouse AI continuously flags behavioral anomalies like rogue logins and DNS spikes, so your inventory isn't just a snapshot—it's a live, security-aware view of your network.
Faddom Key Features
- CVE vulnerability enrichment: Links discovered software and version data to known CVEs, giving you a real-time view of vulnerable assets across your environment.
- Cloud rightsizing and migration planning: Built-in recommendations surface idle or oversized cloud instances with cost data across AWS, Azure, and GCP to support migration wave planning.
- Compass AI natural language querying: Ask plain-language questions about your infrastructure topology and get direct answers without manually digging through maps or reports.
- SSL certificate tracking: Monitors SSL certificates across discovered services, flagging expiring or misconfigured certificates before they become an incident.
Faddom Integrations
Faddom offers integrations with ServiceNow, Jira, Zabbix, Nagios, Microsoft AD, and AWS.
Pros and Cons
Pros:
- Flags shadow IT and CVE vulnerabilities automatically
- No endpoint agents or server credentials required
- Generates real-time topology maps in under an hour
Cons:
- Does not support SaaS application discovery
- No native CMDB or bidirectional data sync
Learn more about Faddom: Best for automation-driven asset inventory
- Free demo + 30-day free trial available
- Pricing upon request
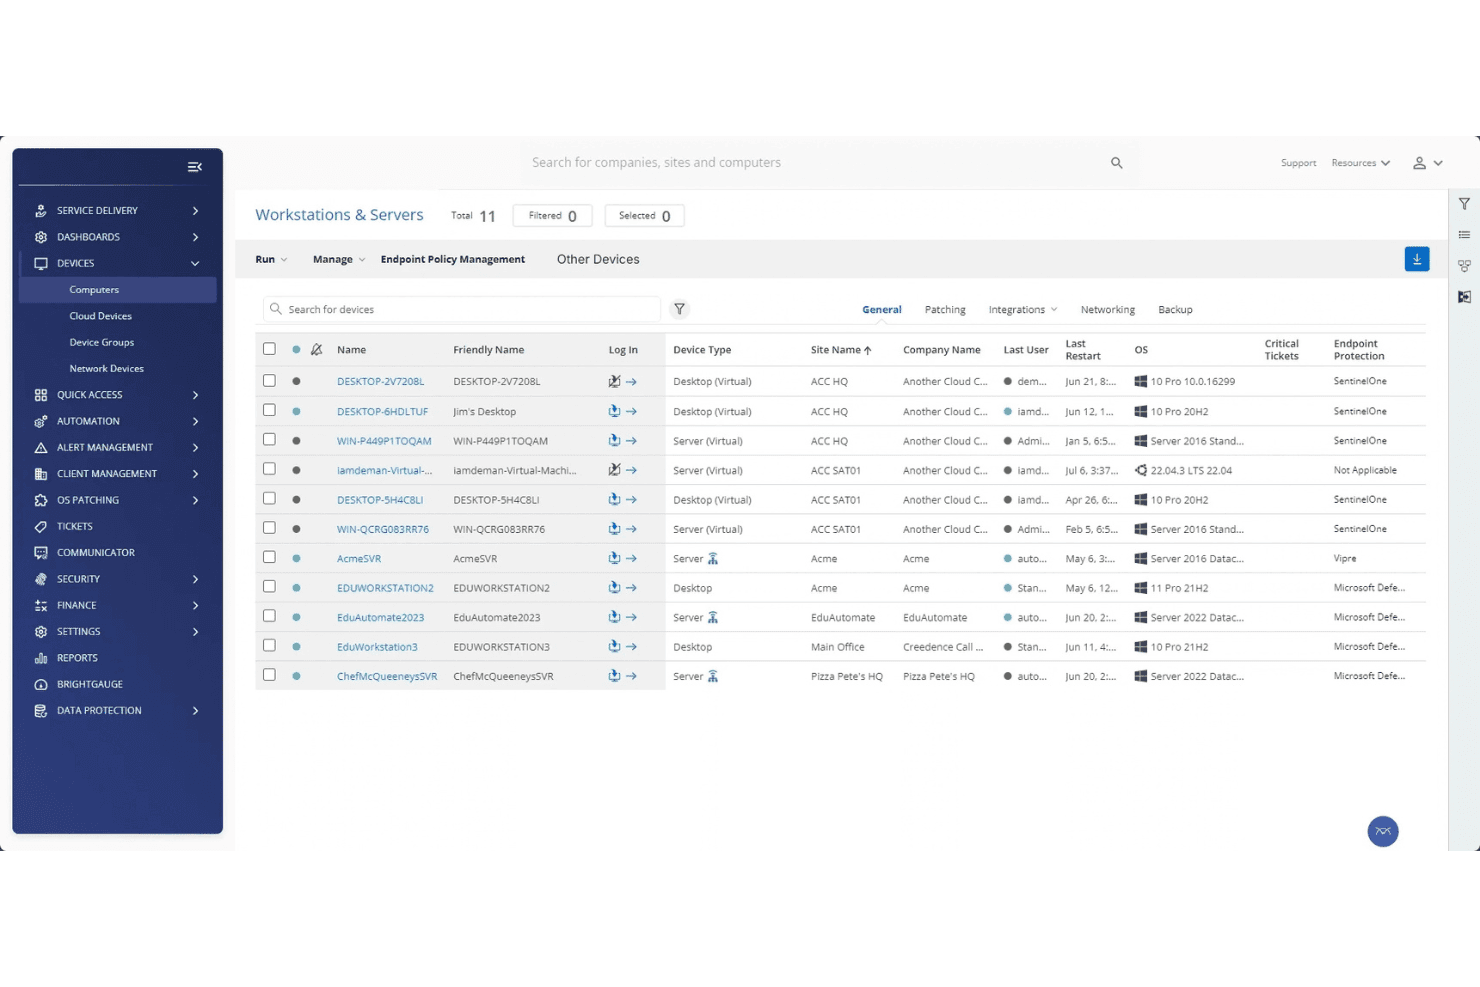
ConnectWise RMM centralizes device management across all client workstations and servers. ConnectWise RMM is an agent-based and agentless remote monitoring and management platform that combines automated network discovery, multi-protocol device scanning, asset cataloging, change tracking, and scripted automation across multi-site IT environments.
Who Is ConnectWise RMM Best For?
ConnectWise RMM is purpose-built for MSP technicians managing multiple client networks from a single console.
Why I Picked ConnectWise RMM
ConnectWise RMM earns its spot on my shortlist because its Network Probe technology turns any Windows agent into a discovery engine, automatically scanning IP ranges, creating device records, and querying devices via Detection Templates across multi-site environments. I particularly like how the platform pairs agent-based cataloging (hardware specs, installed software, patch status) with agentless SNMP, WMI, and LLDP scanning, so even unmanaged switches and printers get captured. The ~400 prebuilt automation scripts then let you act on that inventory data without writing everything from scratch.
ConnectWise RMM Key Features
- Asset change tracking: Logs hardware, software, and ownership changes over time to support audits and lifecycle management.
- Dataviews reporting: Provides 100+ interactive query views for searching, filtering, and exporting asset data.
- Multi-tenant console: Manages multiple client networks from one interface with per-client site structures and segmented reporting.
- Deployment flexibility: Supports on-premises and cloud (SaaS) hosting based on your data residency or network segmentation needs.
ConnectWise RMM Integrations
ConnectWise RMM connects with ConnectWise PSA, Autotask, Auvik, ServiceNow, and Aportio. It also integrates with Zapier and provides a REST API for custom connections.
Pros and Cons
Pros:
- Multi-tenant console for MSP client management
- Deep change tracking for asset lifecycles
- Hybrid agent and agentless device discovery
Cons:
- Monitoring for non-Windows devices is limited
- Advanced topology mapping requires Auvik add-on
Learn more about ConnectWise RMM: Best for agentless asset discovery
- Free plan + 21-day free trial available
- From $5,000/year
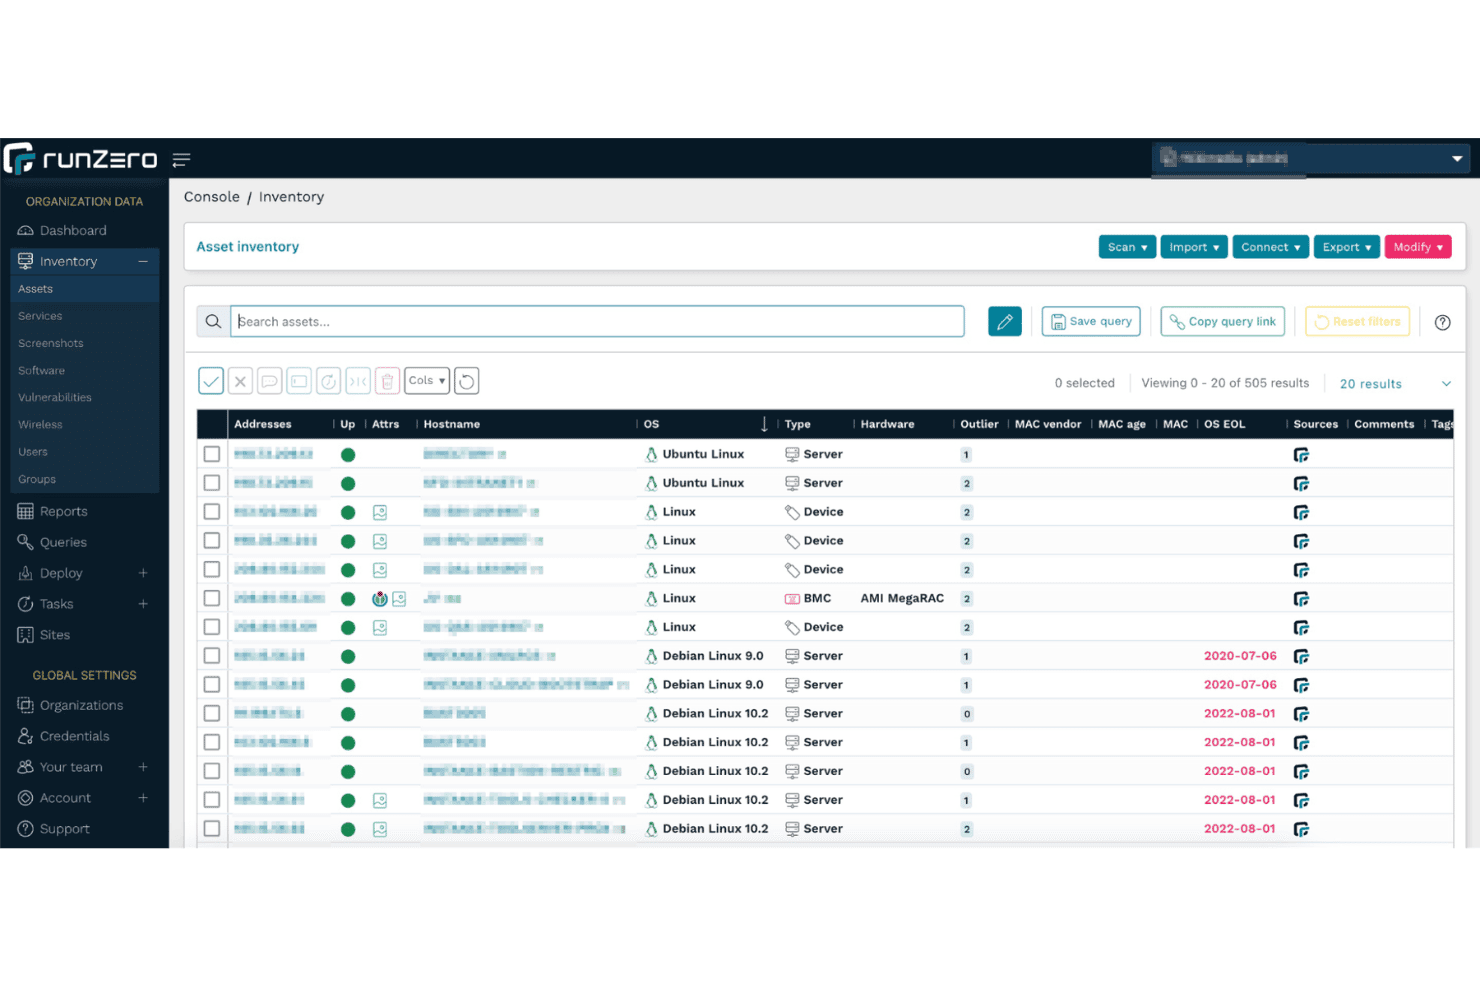
runZero displays a full asset inventory across 505 discovered network devices. runZero is a network inventory and cyber asset attack surface management (CAASM) platform that discovers and catalogs IT, OT, IoT, and cloud assets using a combination of active scanning, passive traffic sampling, and API-based integrations.
Who Is runZero Best For?
runZero is a strong fit for security and network teams managing mixed IT, OT, and IoT environments where deploying agents or gathering credentials isn't practical.
Why I Picked runZero
I picked runZero as one of the best because its agentless discovery model sets it apart. It fingerprints IoT, OT, and shadow IT devices without credentials, agents, or appliances. I've run it against environments where deploying agents wasn't an option, and it still surfaces open ports, running services, SSL certificates, and even screenshots of web interfaces. The passive OT traffic sampling is particularly valuable for fragile ICS environments where active scanning carries real operational risk.
runZero Key Features
- Compliance dashboards: Pre-built dashboards mapped to frameworks including NIST CSF, PCI DSS, DORA, NIS2, and NYDFS for audit-ready reporting.
- Multi-tenant MSSP console: Supports per-customer accounts or a global account with per-organization RBAC, scoped credentials, and parent-child org relationships.
- SSL/TLS certificate tracking: Discovers and catalogs all certificates across the network, including expired and expiring-soon certs with full issuer and chain metadata.
- Attack path mapping: Visualizes lateral movement paths from internet-facing entry points through the network, identifying segmentation gaps and choke points.
runZero Integrations
runZero offers 30+ documented integrations, including Jira Service Management, NetBox, AWS, Microsoft Intune, Google Cloud Platform, CrowdStrike, Splunk, and Qualys. It also provides an API for custom integrations.
Pros and Cons
Pros:
- Screenshots web services for faster device validation
- Visualizes network topology with 2D and 3D maps
- Agentless discovery finds unmanaged and shadow IT
Cons:
- Native change tracking requires external SIEM export
- Hardware detail is limited without credentials
Learn more about runZero: Best for auto-updating IT docs and compliance audits
- 30-day free trial
- From €465.00/year
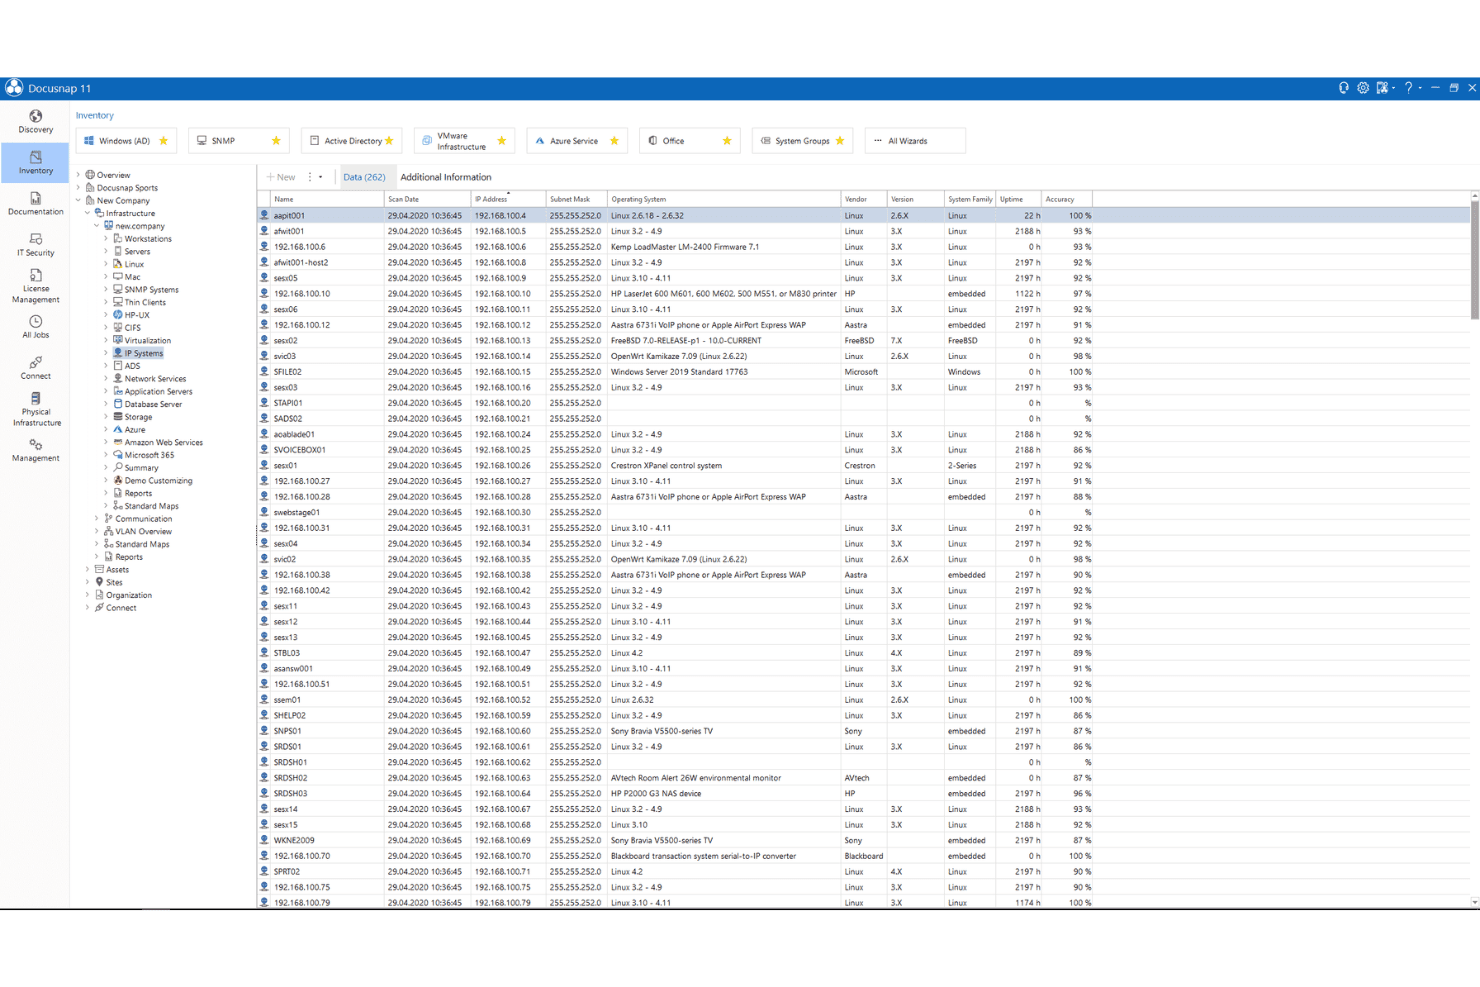
Docusnap displays a full SNMP device inventory with OS and network details. Docusnap is an agentless network inventory and IT documentation tool that combines automated device discovery, an ITIL-compliant CMDB, license management, network topology mapping, and compliance-ready reporting across on-premises and cloud environments.
Who Is Docusnap Best For?
Docusnap is a strong fit for IT teams in regulated industries that need audit-ready documentation and license compliance tracking across hybrid on-premises and cloud environments.
Why I Picked Docusnap
Docusnap earns its spot on my shortlist because of how it handles documentation that actually stays current. Every scheduled inventory cycle automatically refreshes network maps, IT concept documents, and compliance reports without anyone touching them manually. I particularly like its 200+ pre-built audit reports mapped to frameworks like ISO 27001, NIS-2, GDPR, and DORA, which means your documentation is audit-ready by default, not scrambled together before an inspection. The agentless discovery across Windows, Linux, macOS, and cloud platforms like Azure and AWS keeps the CMDB accurate across hybrid environments without deployment overhead.
Docusnap Key Features
- Multi-protocol agentless scanning: Scans devices using WMI, SSH, SNMP, and REST APIs without installing agents on any endpoint.
- ITIL-compliant CMDB: Stores all inventoried assets in a structured, dependency-aware configuration database.
- Multi-tenancy for MSPs: Built-in client separation with per-tenant scanning credentials, role-based access control, and custom branding for each managed organization.
- Permission analysis: Audits access rights across Windows file systems, Active Directory, SharePoint, Exchange, and CIFS/SMB-compatible storage.
Docusnap Integrations
Docusnap offers native integrations with Microsoft 365, Azure Services, Amazon Web Services, and Cisco Meraki. It also provides a REST API and Zapier for custom connections.
Pros and Cons
Pros:
- Multi-tenancy with per-client data segregation
- ITIL-compliant CMDB with dependency mapping
- Auto-updating IT documentation after each scan
Cons:
- Limited report customization options
- No real-time rogue device alerting
Learn more about Docusnap: Best for hybrid IT environments
- Free trial + free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.8/5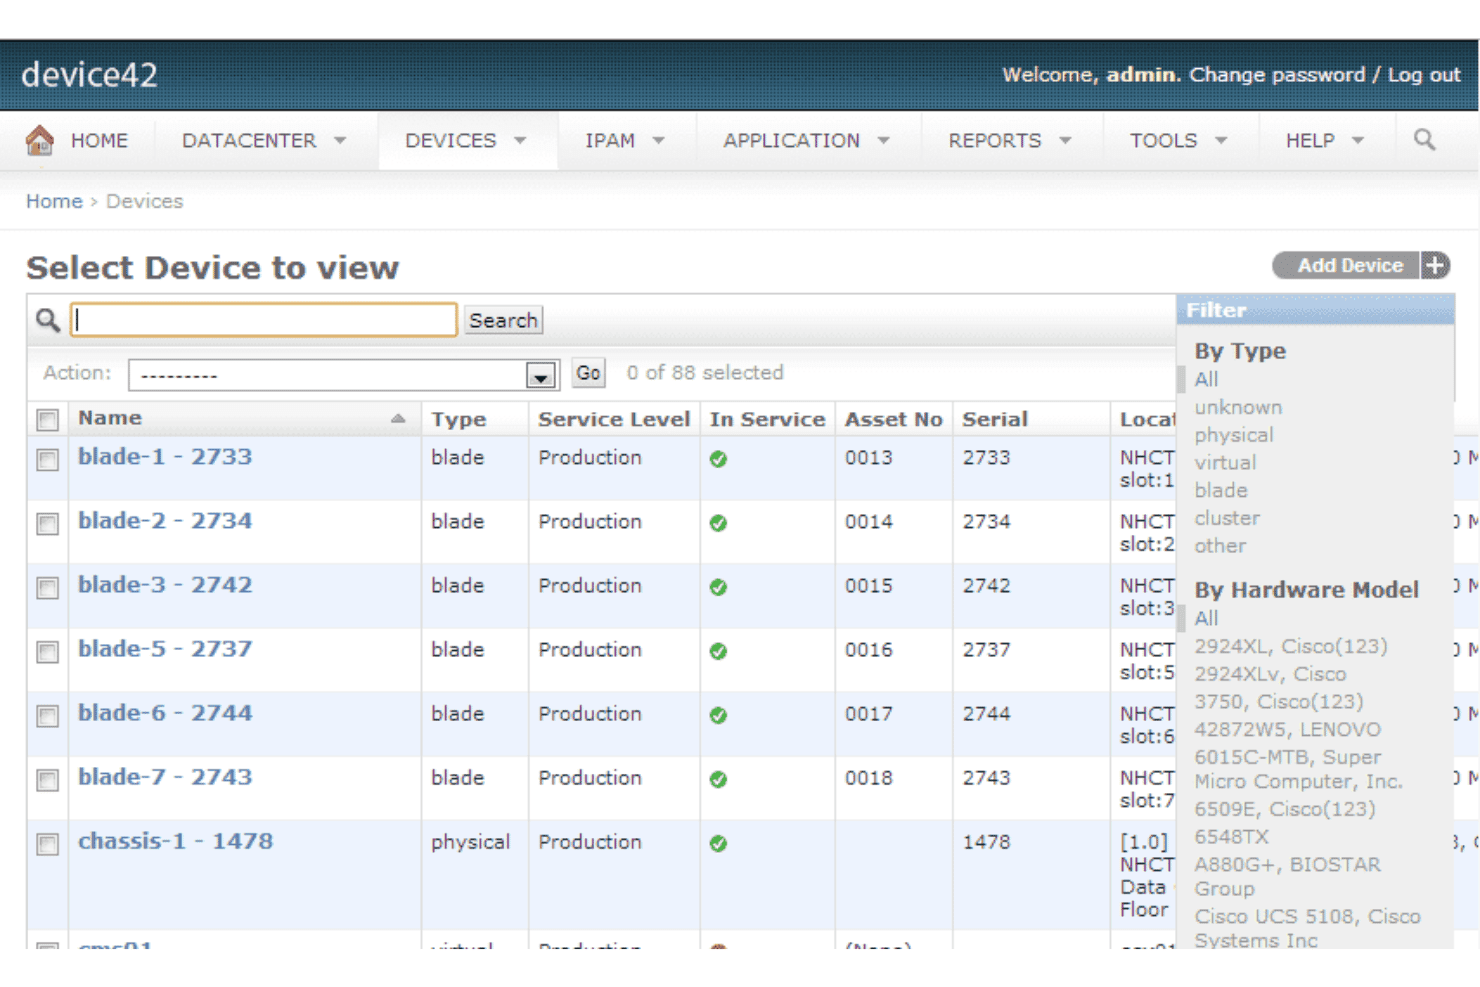
Device42 lets users filter and manage all devices by type and hardware model. Device42 is a network inventory management platform that combines agentless auto-discovery, a unified CMDB, IPAM, DCIM, and application dependency mapping across physical, virtual, cloud, and containerized environments.
Who Is Device42 Best For?
Device42 is a strong fit for mid-to-large IT teams managing mixed environments that span on-premises hardware, virtual infrastructure, and cloud resources under one inventory system.
Why I Picked Device42
I've included Device42 in my top picks because it's one of the few network inventory management tools that genuinely handles physical, virtual, cloud, and containerized assets under a single CMDB without requiring agents on most devices. I particularly like how Remote Collectors extend agentless discovery into segmented subnets and remote offices, covering protocols like SNMP, WMI, SSH, and even Modbus for OT/IoT devices. Its Application Dependency Mapping automatically visualizes service-to-server relationships, which is invaluable when you need to assess the impact of a planned change across a hybrid environment.
Device42 Key Features
- Software license tracking: Monitor purchased, installed, and actively used software licenses in a single view, with flags for prohibited software and upcoming expirations.
- EnrichAI data normalization: Automatically deduplicates and enriches discovered asset records with manufacturer warranty, EOL, and EOS data on every discovery cycle.
- SSL certificate management: Auto-discovers certificates across your environment, tracks expiration dates, and surfaces cipher suite details for audit and compliance review.
- IPAM with DNS and NAT tracking: Manages IPv6/IPv4 subnets, VLANs, and IP assignments alongside DNS record types and NAT rules through firewalls and load balancers.
Device42 Integrations
Device42 offers native integrations with ServiceNow, Freshservice, Jira Service Management, Splunk, Power BI, and CyberArk. An API is also available for custom connections.
Pros and Cons
Pros:
- Warranty and EOL data auto-enriched every cycle
- Topology and impact charts auto-generate from scans
- Agentless discovery spans cloud, on-prem, and IoT
Cons:
- Advanced reporting requires DOQL query language
- Hardware subcomponent change tracking is limited
Learn more about Device42: Best for IT, OT, and IoT asset discovery in one view
- Free demo + 14-day free trial available
- From $239/month (billed annually)
Visit WebsiteCustomer Rating:4.3/5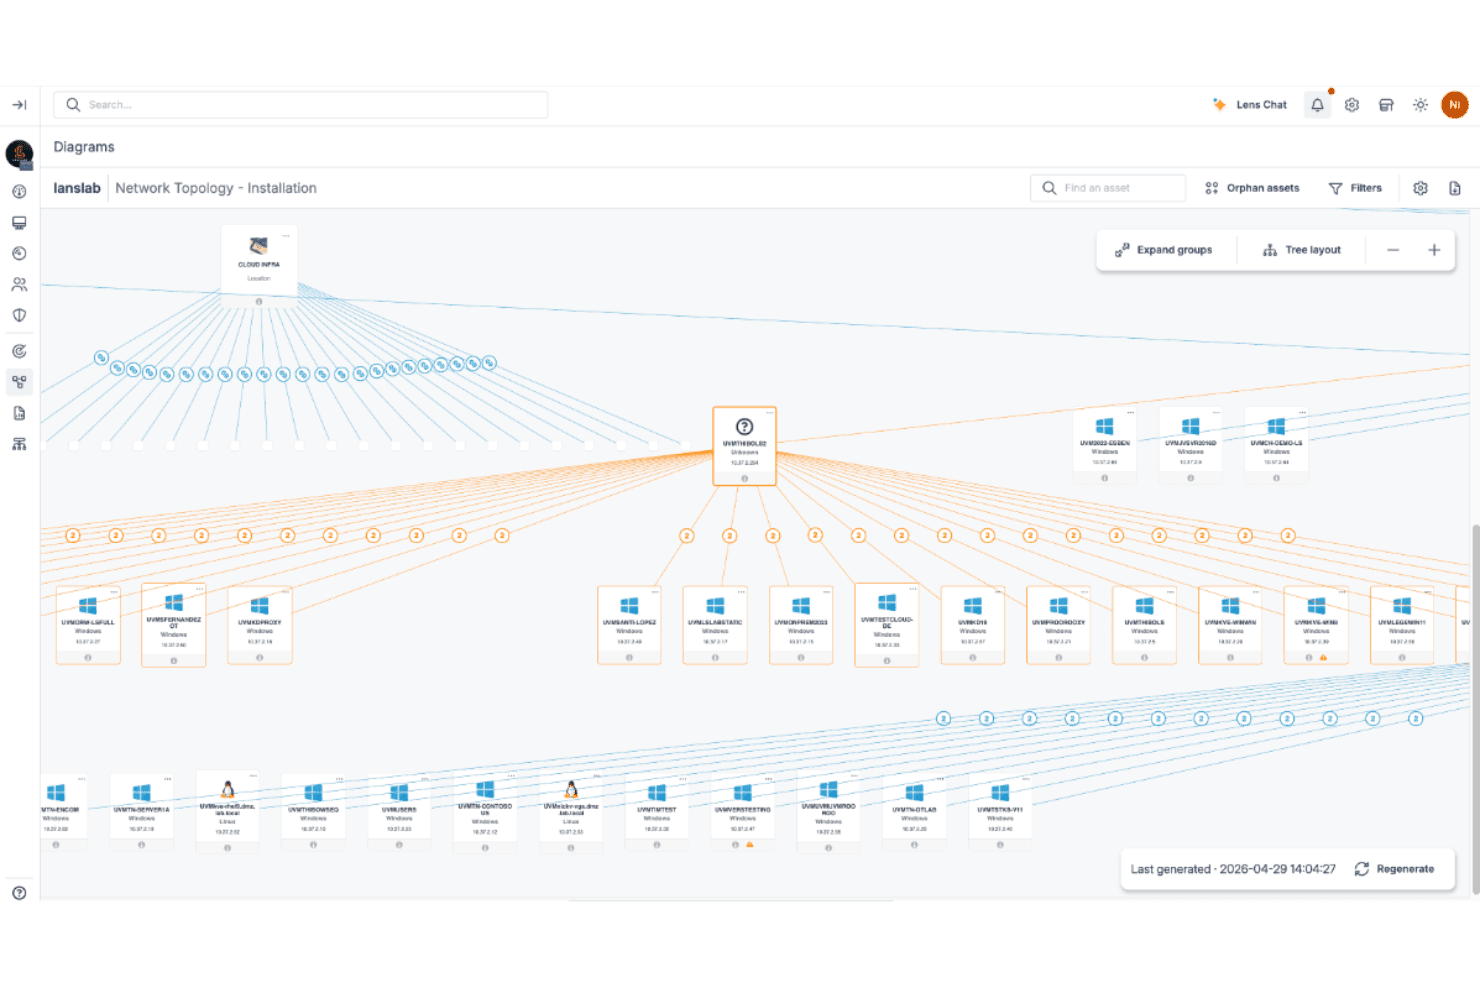
Lansweeper maps your full network topology across all assets. Lansweeper is a network inventory management system that combines agentless active scanning, passive device sensing, agent-based tracking, and cloud connectors to discover and catalog IT, OT, and IoT assets across hybrid environments.
Who Is Lansweeper Best For?
Lansweeper is a strong fit for IT teams managing mixed environments where IT, OT, and IoT devices coexist and need to be tracked in a single, unified inventory.
Why I Picked Lansweeper
I picked Lansweeper as one of the best because no other tool I've used collapses IT, OT, and IoT discovery into a single, normalized inventory as naturally as this one does. Its Asset Radar layer passively fingerprints devices using credential-free packet sensing, surfacing unmanaged IoT hardware and rogue endpoints that credentialed scans routinely miss. I also rely on its built-in vulnerability cross-referencing, which maps discovered assets directly to CVE feeds so I can see which specific devices are exposed without switching tools.
Lansweeper Key Features
- Warranty tracking: Automatically pulls warranty status from Dell, HP, Lenovo, and other major vendors, with configurable expiration alerts at 30, 60, and 90 days.
- Multi-tenant MSP portal: A dedicated management console lets MSPs view, report on, and manage asset inventories across all client sites from a single interface.
- Compliance reporting templates: Pre-built report templates mapped to frameworks including NIST, HIPAA, PCI-DSS, ISO 27001, and CIS Controls support audit preparation directly from inventory data.
- GraphQL API and webhooks: Available on Pro and Enterprise tiers, these let your team push asset data into external tools or trigger automated workflows based on inventory changes.
Lansweeper Integrations
Lansweeper integrates with Datadog, Jira Service Management, Brinqa, Halo, Happyfox, Microsoft Sentinel, Splunk, and Armis. GraphQL and REST APIs, webhooks, and an MCP Server support custom connectivity.
Pros and Cons
Pros:
- Maps vulnerabilities directly to discovered assets
- Agentless scanning uncovers hard-to-reach assets
- Finds unmanaged and rogue IoT/OT devices
Cons:
- SNMPv3 context field not supported
- No built-in patch deployment feature
Learn more about Lansweeper: Best for DC asset lifecycle and CMDB sync
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.4/5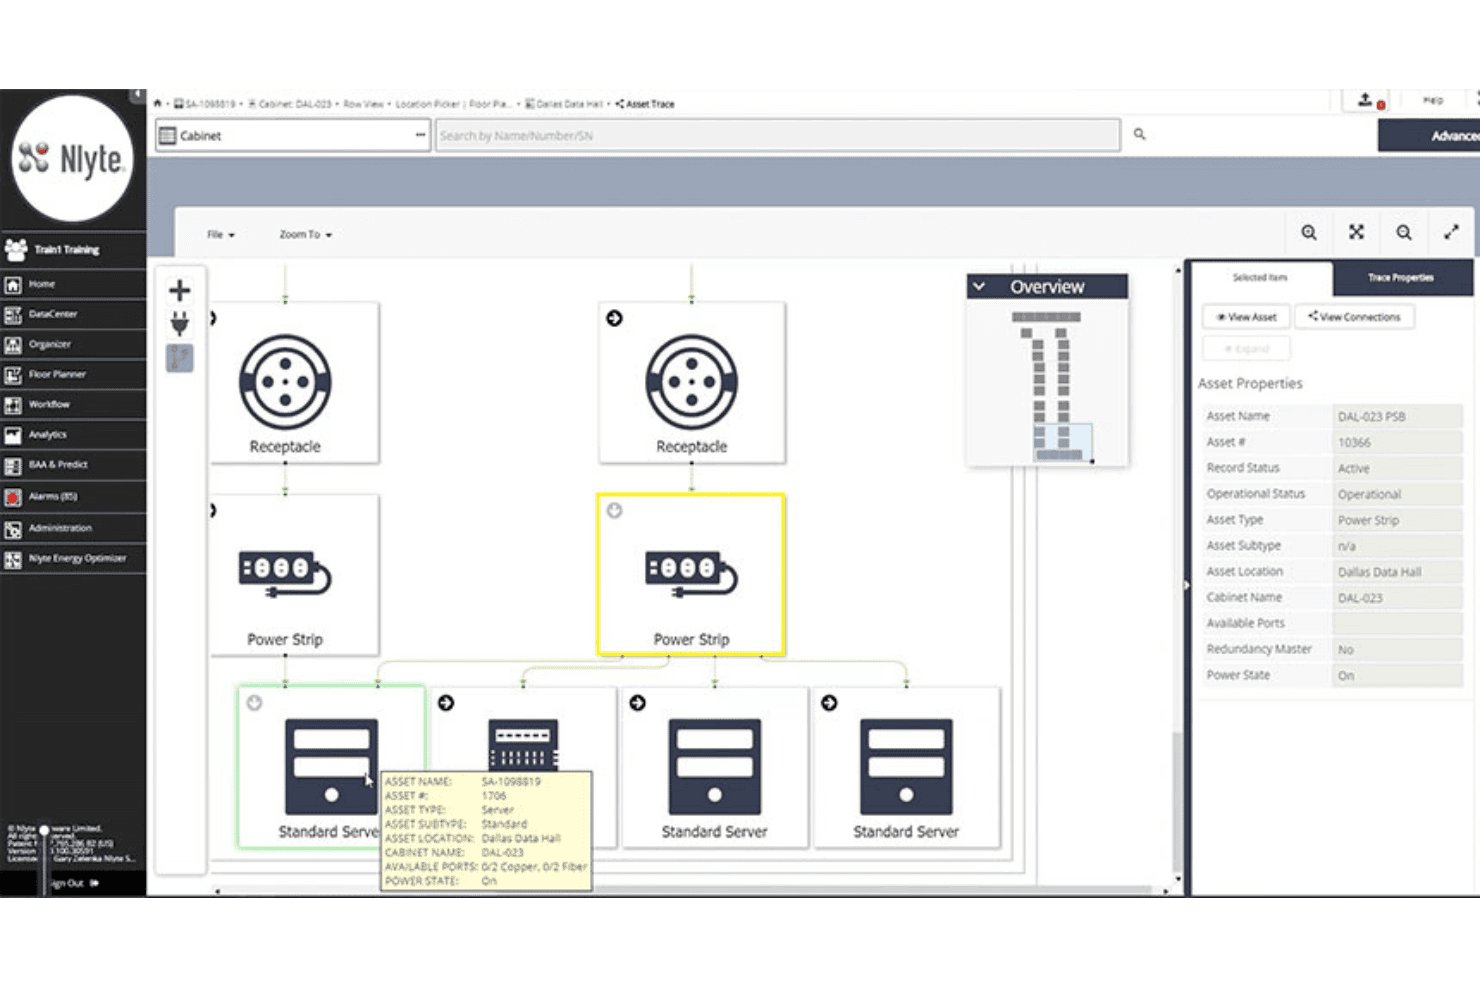
Nlyte DCIM visualizes power chain connections across cabinet assets. Nlyte DCIM is a data center infrastructure management platform that combines automated asset discovery, full lifecycle asset cataloging, change tracking, multi-protocol scanning, and CMDB integration across physical DC environments.
Who Is Nlyte DCIM Best For?
Nlyte DCIM is a strong fit for enterprise IT teams managing large physical data center footprints who need end-to-end asset lifecycle tracking and tight CMDB integration.
Why I Picked Nlyte DCIM
Nlyte DCIM earns its spot on my shortlist because of how it handles the full asset lifecycle alongside live CMDB synchronization, which is genuinely rare at this depth. The Asset Optimizer tracks every device from procurement to decommissioning, capturing serial numbers, RFID tags, rack position, and custom fields like PO numbers. Its bi-directional ServiceNow sync means a physical rack change in Nlyte automatically updates the logical CMDB record, keeping both systems accurate without manual reconciliation.
Nlyte DCIM Key Features
- Nlyte Discovery module: Automatically scans networks across all major protocols and operating systems to detect connected devices, capture firmware data, and flag unknown or zombie assets.
- Asset Integrity Monitoring: Baselines all assets, power systems, and processes with chain-of-custody tracking to surface unauthorized changes and support Zero Trust security postures.
- Operational AI suite: Includes conversational natural language querying of asset and infrastructure data, AI-driven workload placement, and anomaly detection with root cause analysis.
- Multi-tenant cabinet views: Provides secure, isolated per-tenant visibility into cabinet data, supporting colocation providers managing infrastructure across multiple customers.
Nlyte DCIM Integrations
Nlyte DCIM integrates with leading ITSM, CMDBs, and BMSs. A REST API is also available for custom connections.
Pros and Cons
Pros:
- Supports broad protocols including BACnet and MODBUS
- Bi-directional sync with ServiceNow CMDB
- Excels at tracking the full asset lifecycle
Cons:
- Interface design frequently called outdated
- Oriented around physical data center assets
Learn more about Nlyte DCIM: Best for CMDB-connected asset discovery at scale
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4/5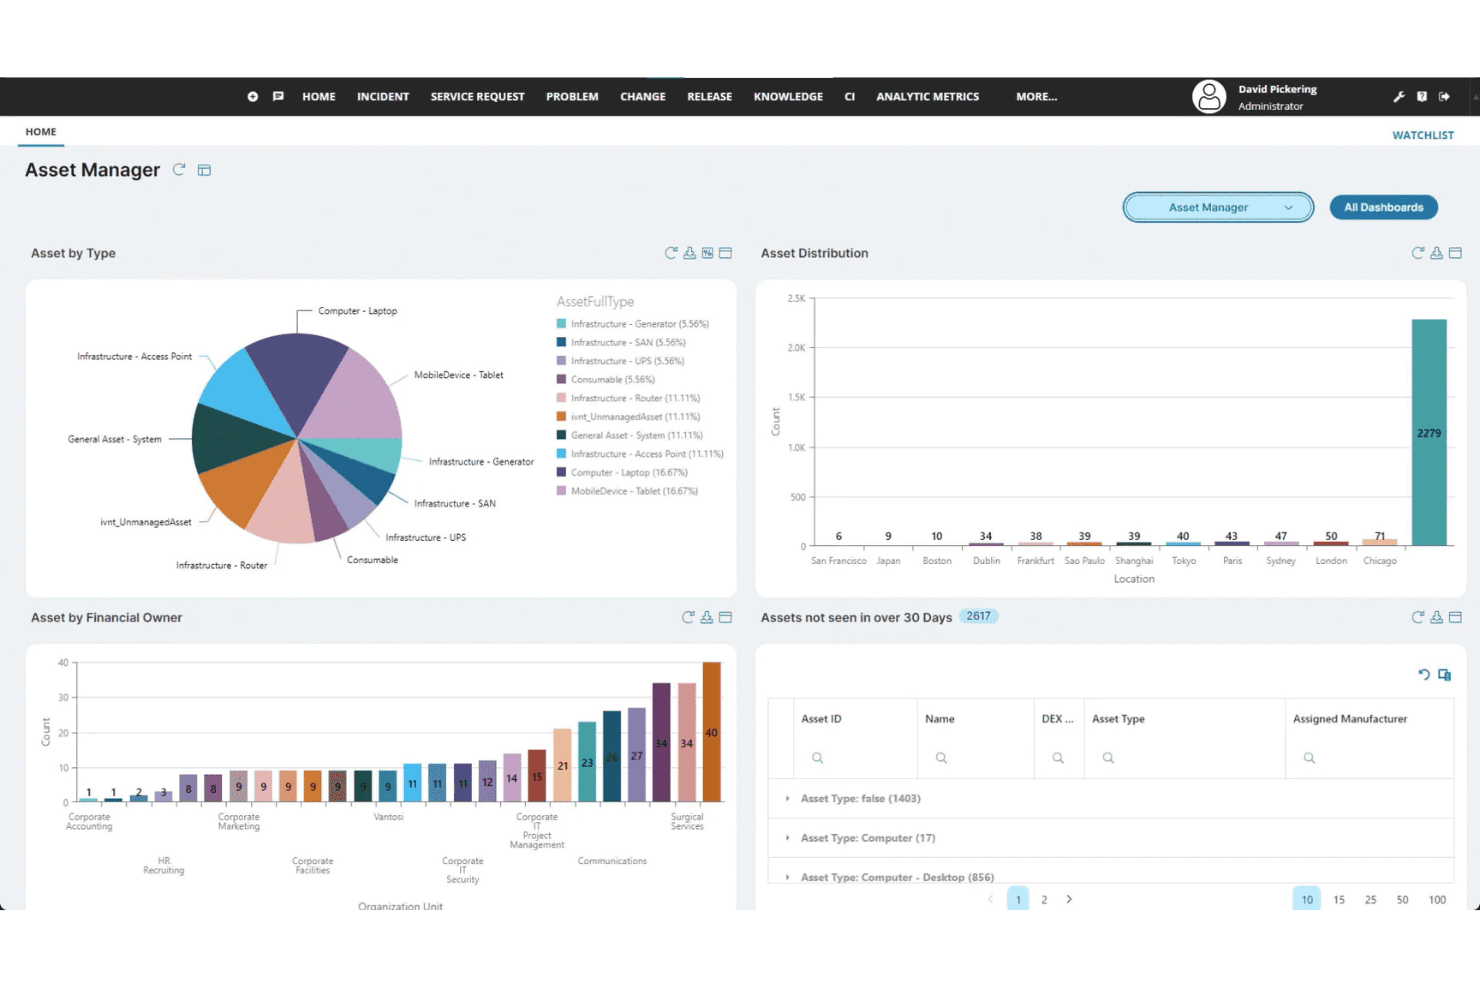
Ivanti Neurons centralizes asset tracking across type, location, and owner. Ivanti Neurons is a network inventory platform that combines active scanning, passive discovery, and agent-based telemetry to build a unified, deduplicated asset catalog across managed, unmanaged, IoT, OT, and cloud environments.
Who Is Ivanti Neurons Best For?
Ivanti Neurons is a strong fit for enterprise IT teams that need a single, authoritative asset record feeding directly into an existing CMDB or ITSM platform.
Why I Picked Ivanti Neurons
I picked Ivanti Neurons because its CMDB sync is genuinely one of the best I've seen in this category. Discovery data flows directly into ServiceNow, Freshservice, Jira, and others, keeping configuration items current without manual intervention. What makes it stand out at scale is the combination of always-on passive discovery and a self-organizing scanner election, so even intermittent or transient devices don't slip through.
Ivanti Neurons Key Features
- Rogue device detection: Continuously scans every subnet to flag unauthorized devices and rogue wireless access points against your known asset baseline.
- Multi-source data normalization: Ingests discovery data from active scans, passive listening, agent telemetry, and third-party connectors, then deduplicates it into a single asset record.
- Warranty and lifecycle enrichment: Automatically augments asset records with warranty status, contract data, and end-of-life dates pulled from vendor data connectors.
- AI-driven automation via Neurons Bots: Uses embedded AI to power automation workflows that act on discovery data, including vulnerability prioritization and self-healing endpoint tasks.
Ivanti Neurons Integrations
Ivanti Neurons integrates with ServiceNow CMDB, Ivanti Neurons for ITSM, Jira, Halo, Microsoft Azure DevOps, and AWS Amazon Inspector. Open REST APIs support custom integrations.
Pros and Cons
Pros:
- Direct CMDB sync maintains real-time asset accuracy
- Agentless scanning covers IoT and OT devices
- Continuous always-on asset and change discovery
Cons:
- Initial setup needs advanced technical expertise
- Full topology maps require separate purchase
Learn more about Ivanti Neurons: Best for enterprise-wide asset discovery sync
- Free demo available
- Pricing upon request
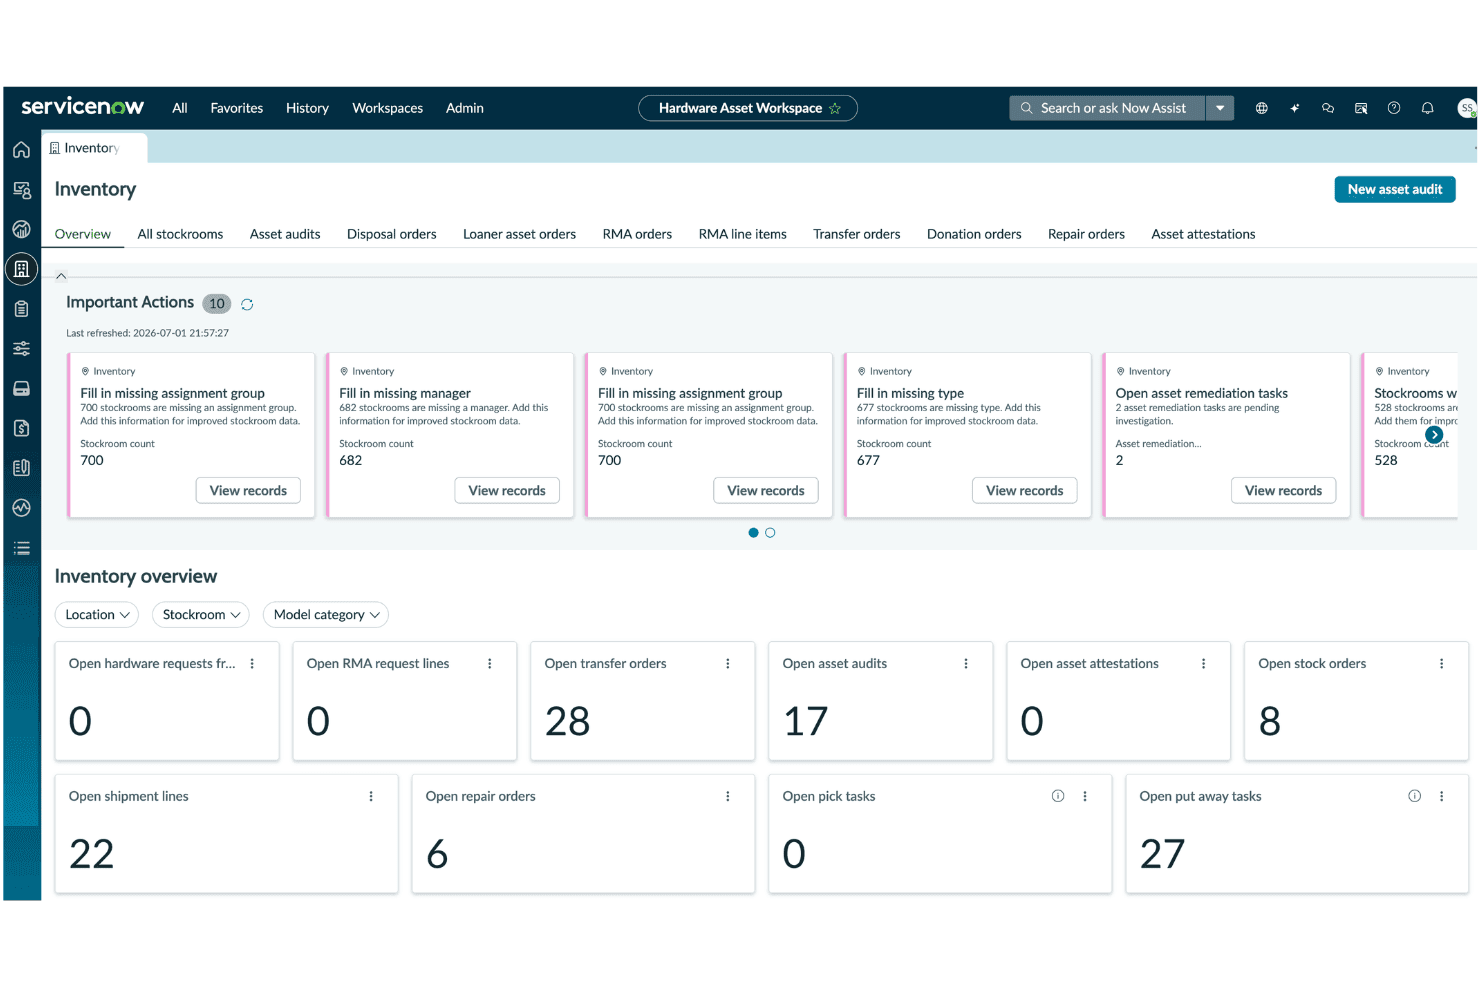
ServiceNow ITAM centralizes inventory oversight with real-time asset action alerts. ServiceNow ITAM is an enterprise IT asset management platform that combines automated network discovery, CMDB-backed device and software cataloging, multi-protocol scanning, and license compliance tracking across on-premises, cloud, and hybrid environments.
Who Is ServiceNow ITAM Best For?
ServiceNow ITAM is a strong fit for large enterprises that already run ServiceNow for ITSM and want asset discovery, CMDB records, and license compliance managed on the same platform.
Why I Picked ServiceNow ITAM
ServiceNow ITAM earns its spot on my shortlist because the CMDB is the actual system of record, not a secondary sync target. I love how Discovery auto-populates CI records across WMI, SSH, and SNMP in a single scheduled scan, then keeps those records current as configurations shift. What makes this genuinely useful for large shops is that the same asset data feeds directly into incident, change, and vulnerability workflows without any custom plumbing.
ServiceNow ITAM Key Features
- Software asset management (SAM): Tracks software license entitlements, monitors usage, detects compliance violations, and flags corrective actions automatically.
- Application dependency mapping: Visualizes relationships between applications and underlying network infrastructure CIs to support impact analysis during incidents or changes.
- Cloud resource discovery: Automatically discovers and catalogs assets across AWS, Azure, and GCP environments, including serverless functions like AWS Lambda and Azure Functions.
- GRC integration: Feeds asset and compliance data directly into ServiceNow's Governance, Risk, and Compliance module for audit management and policy enforcement.
ServiceNow ITAM Integrations
ServiceNow ITAM has native integrations across ServiceNow ITSM, ITOM, SecOps, IntegronQ, Splunk, QRadar, and Microsoft Entra ID. REST API is also available for custom connections
Pros and Cons
Pros:
- Cloud and serverless discovery feature included
- Multi-protocol scanning supports enterprise-scale networks
- Directly updates CMDB as system of record
Cons:
- Setup requires significant platform expertise
- Discovery misses devices on unknown subnets
Learn more about ServiceNow ITAM:
Outro software de inventário de redes
Estas são algumas opções adicionais que não foram incluídas na minha lista principal, mas que podem ser relevantes para as suas necessidades.
- 11N-able N-centralBest for MSP-scale network topology mapping
- 12AuvikBest for multi-tenant network discovery
- 13FreshserviceBest for ITSM-linked network asset discovery
- 14DomotzBest for rogue device detection
- 15PRTG Network MonitorBest for sensor-based network mapping
- 16ManageEngine AssetExplorerBest for end-to-end ITAM with license compliance
- 17AxoniusBest for cyber-physical asset visibility
- 18WhatsUp Gold 360Best for distributed multi-site network inventory
- 19JDisc DiscoveryBest for one-time network assessment projects
- 20AlloyScanBest for cloud-native agent and agentless inventory
Related Reviews
How I Evaluate Network Inventory Software
I split my evaluation into baseline requirements every tool must meet—like agentless discovery and multi-protocol scanning—and the differentiators that separate a solid tool from the right one for your environment.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, and use that to help me assess its overall fit for the list.
- Automated network discovery: I evaluate whether the tool can scan distributed or hybrid environments on a recurring schedule without manual input for each subnet.
- Device and asset cataloging: A solid catalog goes beyond IP and hostname lists. I look for rich asset records that include OS, manufacturer, installed software, and location data.
- Multi-protocol scanning: I check for support across SNMP, WMI, SSH, and ICMP at minimum, plus agent and agentless options that cover a range of device types including IoT.
- Change and configuration tracking: Tools that log config changes with timestamps, and comparison views help teams catch drift before it causes outages or compliance gaps.
- Reporting and export: I look for customizable reports, scheduled delivery, and export formats that feed into ITSM or CMDB workflows rather than just static CSV dumps.
- Network mapping and topology: Interactive topology maps with drill-down capability matter more than static diagrams, especially when you're troubleshooting across multiple sites.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Agentless deep discovery matters most when your environment includes unmanaged IoT, OT, or BYOD devices you can't install agents on. I check whether a tool can fingerprint those endpoints using both credentialed and credential-less scans. Rogue device detection builds on that by alerting you when unknown MAC addresses appear against an approved baseline—critical for catching shadow IT before it becomes a security gap. I also evaluate CMDB and ITSM sync depth, looking for bidirectional connectors with platforms like ServiceNow or Jira that keep asset data authoritative across your operations stack without manual re-entry.
Beyond Features
Pricing model matters a lot here. Per-device licensing can spiral fast when you're scanning dynamic environments where device counts fluctuate weekly, so I check whether a vendor offers per-subnet or flat-tier options that keep costs predictable. I also evaluate the integration ecosystem beyond ITSM—tools like Auvik and ConnectWise RMM offer prebuilt connectors into RMM, SIEM, and patch management platforms, while others rely on REST APIs you'll need to build around. Security posture is another factor: I look for SOC 2 or ISO 27001 certifications and confirm that scan credentials stored for WMI or SSH are encrypted at rest, not just in transit.
Como escolher um software de inventário de redes
Para encontrar o software adequado, utilize esta tabela para fazer corresponder as suas prioridades aos principais critérios de seleção:
| Se a sua prioridade for... | Procure... |
|---|---|
| Se a sua prioridade for...Reduzir o acompanhamento manual dos ativos | Procure...Descoberta de redes automatizada e sem agentes |
| Se a sua prioridade for...Gerir ambientes diversificados | Procure...Suporte para vários protocolos e ambientes híbridos (TI/TO/IoT) |
| Se a sua prioridade for...Integrar com ITSM ou CMDB | Procure...Conectores pré-configurados e sincronização bidirecional |
| Se a sua prioridade for...Auditar para garantir a conformidade | Procure...Documentação atualizada automaticamente e registos de configuração |
| Se a sua prioridade for...Deteção de dispositivos não autorizados ou ocultos | Procure...Alertas em tempo real sobre dispositivos desconhecidos e ferramentas de referência |
Como avaliar a sua lista restrita
- Teste a cobertura da descoberta de ativos: Execute uma demonstração ou período de teste e analise dois segmentos de rede diferentes (com e sem fios) para confirmar a abrangência da deteção de dispositivos.
- Verifique a profundidade da integração: Solicite uma demonstração ou uma apresentação da documentação que mostre como os dados dos ativos são sincronizados bidirecionalmente com a CMDB ou ferramenta ITSM escolhida.
- Analise os fluxos de trabalho de relatórios/exportação: Peça ao fornecedor para gerar uma exportação agendada dos relatórios de alterações dos ativos e fornecer exemplos dos formatos de saída.
- Confirme a postura de segurança: Solicite provas da encriptação das credenciais (em repouso e em trânsito), sob a forma de um documento de segurança ou resumo de auditoria.
- Decida entre flexibilidade em tempo real e rigor da documentação: Escolha entre ferramentas otimizadas para análise em tempo real e sem agentes e ferramentas centradas em relatórios robustos e adequados para auditorias — selecione uma abordagem com base nas exigências do seu ambiente.
O que é o software de inventário de rede?
O software de inventário de rede é uma ferramenta que deteta, cataloga e monitoriza automaticamente todos os dispositivos ligados à sua rede. Estas plataformas fornecem informações detalhadas sobre o hardware, o software e as configurações dos dispositivos. Pode utilizar software de inventário de rede para monitorizar alterações, auditar ativos, gerar relatórios e apoiar a conformidade. Ajudam as equipas de infraestrutura e segurança a manter a organização, reduzir o acompanhamento manual de ativos e responder rapidamente à evolução dos ambientes de rede.
Funcionalidades do software de inventário de rede
Ao avaliar plataformas de inventário de rede, procure estas funcionalidades essenciais:
- Descoberta automatizada da rede: Deteta e cataloga todos os dispositivos em ambientes com e sem fios, na nuvem e virtuais, para manter uma lista de ativos em tempo real e eliminar lacunas de visibilidade.
- Catalogação de dispositivos e ativos: Recolhe detalhes granulares — incluindo especificações de hardware, sistema operativo, endereços IP, software instalado e localização — para acelerar a resolução de problemas e a gestão do ciclo de vida.
- Análise através de vários protocolos: Utiliza SNMP, WMI, SSH e ICMP para extrair dados de hardware diversificado, garantindo a compatibilidade em ambientes mistos.
- Monitorização de configurações e alterações: Regista definições dos dispositivos, atualizações de firmware e alterações às políticas para simplificar auditorias, permitir reversões rápidas e detetar configurações incorretas numa fase inicial.
- Mapeamento interativo da rede: Gera mapas da topologia em tempo real para visualizar as ligações entre dispositivos, localizar falhas e identificar estrangulamentos rapidamente.
- Relatórios personalizáveis: Disponibiliza relatórios agendados ou a pedido em vários formatos de exportação para satisfazer as necessidades de conformidade e apoiar a partilha de dados entre ferramentas de TI.
- Integração com ferramentas de gestão de TI: Sincroniza diretamente os dados dos ativos com plataformas ITSM, CMDB e de gestão de pedidos, eliminando a introdução manual e apoiando uma resposta eficiente a incidentes.
- Controlo de acesso baseado em funções: Restringe o acesso, a edição e a exportação de dados com base nas permissões dos utilizadores, protegendo informações sensíveis dos ativos.
- Alertas e notificações: Aciona alertas instantâneos quando dispositivos não autorizados se ligam à rede ou ocorrem alterações de configuração não autorizadas, acelerando a resposta a ameaças.
- Suporte à conformidade e auditoria: Conserva registos históricos dos ativos, do estado e das alterações para garantir a preparação para auditorias regulamentares e de políticas internas.
Funcionalidades de IA do software de inventário de rede
Para além das funcionalidades padrão listadas acima, muitas destas soluções estão a integrar IA com funcionalidades como:
- Deteção de anomalias baseada em IA: Utiliza aprendizagem automática para identificar padrões invulgares no tráfego da rede ou no comportamento dos dispositivos, alertando-o para potenciais ameaças ou configurações incorretas antes de estas se agravarem.
- Análise preditiva de falhas dos dispositivos: Analisa o desempenho histórico dos dispositivos e os dados ambientais para prever quais os componentes de hardware com maior probabilidade de falhar, ajudando-o a planear uma manutenção proativa e a reduzir o tempo de inatividade.
- Análise automatizada da causa principal: Aplica algoritmos de IA para correlacionar alertas, registos e alterações de configuração, identificando mais rapidamente a causa subjacente dos incidentes de rede do que uma investigação manual.
- Classificação inteligente de ativos: Utiliza IA para categorizar dispositivos novos ou desconhecidos com base em padrões de tráfego, protocolos de comunicação e assinaturas comportamentais, reduzindo a etiquetagem manual e melhorando a precisão do inventário.
- Recomendações inteligentes de correção: Fornece sugestões geradas por IA para resolver problemas detetados, como alterações de configuração ou atualizações de firmware, com base em boas práticas e nos resultados de incidentes anteriores.
Vantagens do software de inventário de rede
A implementação de ferramentas de inventário de rede proporciona várias vantagens para a sua equipa e para a sua empresa. Eis algumas das que pode esperar:
- Descoberta automática de dispositivos: Analisa a sua rede para criar automaticamente uma lista completa e atualizada de dispositivos, eliminando pontos cegos.
- Rastreio preciso de ativos: Armazena os principais detalhes de cada dispositivo — como hardware, software e localização — para facilitar a gestão.
- Compatibilidade com vários protocolos: Utiliza regras padrão, como SNMP, WMI, SSH e ICMP, para encontrar e monitorizar todos os tipos de equipamento.
- Registo de alterações e configurações: Regista as alterações às definições ao longo do tempo, para que possa detetar antecipadamente erros ou atualizações não intencionais.
- Mapeamento interativo da rede: Cria mapas em tempo real da configuração da sua rede para o ajudar a identificar e resolver problemas rapidamente.
- Integração com sistemas de gestão de TI: Partilha dados diretamente com as suas ferramentas de gestão de pedidos e rastreio, mantendo todos os sistemas atualizados.
- Alertas em tempo real e apoio à conformidade: Avisa-o sobre dispositivos desconhecidos ou alterações inseguras, mantendo simultaneamente registos históricos preparados para auditorias.
Custos e preços do software de inventário de rede
A seleção da ferramenta adequada exige uma compreensão dos vários modelos de preços e planos disponíveis. Os custos variam consoante as funcionalidades, a dimensão da equipa, os complementos e outros fatores. A tabela abaixo resume os planos comuns, os respetivos preços médios e as funcionalidades normalmente incluídas no software de inventário de rede:
Tabela de comparação de planos de software de inventário de rede
| Tipo de plano | Preço médio | Funcionalidades comuns |
|---|---|---|
| Tipo de planoPlano gratuito | Preço médio$0-$0 | Funcionalidades comunsDescoberta básica da rede, inventário limitado de dispositivos, análises manuais e apoio da comunidade. |
| Tipo de planoPlano pessoal | Preço médio$15-$40 por utilizador/mês | Funcionalidades comunsApoio a um único utilizador, análise agendada de dispositivos, relatórios padrão e integração básica com ferramentas de TI. |
| Tipo de planoPlano empresarial | Preço médio$40-$100 por utilizador/mês | Funcionalidades comunsAcesso para vários utilizadores, descoberta automática da rede, relatórios avançados, integrações com ITSM e controlo de acesso baseado em funções. |
| Tipo de planoPlano empresarial de grande escala | Preço médio$100-$250 por utilizador/mês | Funcionalidades comunsUtilizadores ilimitados, apoio a ambientes híbridos na nuvem e locais, integrações personalizadas, registos de auditoria e acesso à API. |
Perguntas frequentes sobre software de inventário de rede
Eis algumas respostas a perguntas comuns que poderá encontrar ao selecionar a ferramenta de inventário de rede adequada:
Como posso saber se o software de inventário de rede é compatível com ambientes híbridos ou na nuvem?
Deve verificar se existem funcionalidades de análise multiprotocolo e descoberta na nuvem. Procure suporte para SNMP, WMI, SSH e APIs para plataformas como AWS, Azure e Google Cloud. Muitas das principais ferramentas indicam a compatibilidade com ambientes híbridos nas respetivas páginas de funcionalidades ou na documentação.
O software de inventário de rede consegue detetar e classificar dispositivos IoT e não geridos?
Sim, a maioria das plataformas modernas de inventário de rede consegue identificar dispositivos IoT e BYOD, especialmente as que oferecem descoberta aprofundada sem agentes. Utilizam análises com e sem credenciais para identificar os tipos de dispositivos, mesmo quando não é possível instalar agentes. A precisão da classificação dos dispositivos varia, pelo que deve validar sempre os resultados com uma análise-piloto.
Que integrações devo priorizar para fluxos de trabalho de ITSM e CMDB?
Dê prioridade a software com conectores bidirecionais pré-configurados para as ferramentas de ITSM e CMDB que a sua equipa já utiliza. ServiceNow, Jira Service Management e BMC Remedy são destinos de integração comuns. Os conectores nativos poupam tempo e reduzem os problemas de sincronização dos registos de ativos entre sistemas.
É possível monitorizar alterações na rede em tempo real com estas ferramentas?
Sim, algumas ferramentas de inventário de rede oferecem deteção de alterações em tempo real ou quase em tempo real. Monitorizam alterações de configuração em todos os dispositivos, alertam-no para novos terminais ou terminais não autorizados e disponibilizam frequentemente registos de auditoria com marcas temporais e opções de reversão. Tenha apenas em atenção que a frequência das atualizações e os atrasos nas notificações variam consoante o fornecedor.
Como posso validar a postura de segurança de um fornecedor, especialmente no que diz respeito ao armazenamento de credenciais?
Peça aos fornecedores provas de encriptação dos dados em repouso e em trânsito e verifique a conformidade com referenciais como SOC 2 ou ISO 27001. Solicite um resumo de uma auditoria de segurança recente e analise a forma como a plataforma armazena e trata credenciais de análise sensíveis, especialmente para SNMP, WMI ou SSH.
A maioria das soluções requer agentes ou tudo pode ser feito sem agentes?
A maioria das ferramentas de inventário de rede oferece descoberta sem agentes por predefinição, mas algumas disponibilizam agentes opcionais para uma recolha de dados mais aprofundada ou para locais remotos. Em ambientes onde não é possível instalar agentes, como redes IoT ou de convidados, as ferramentas sem agentes que utilizam SNMP, análises de rede e ARP são as mais adequadas.
Qual é a melhor forma de experimentar ou testar o software de inventário de rede antes de o comprar?
Comece por uma demonstração ou avaliação gratuita e analise dois segmentos diferentes: com e sem fios, ou na nuvem e no local. Reveja os dispositivos descobertos, o nível de detalhe dos registos de ativos e teste os fluxos de trabalho de exportação e integração. Aproveite este período prático para verificar a cobertura e a facilidade de utilização.