

Uma plataforma de proteção de terminais é uma solução de segurança centralizada para detetar, impedir e responder a ameaças direcionadas aos dispositivos da sua rede. Se está à procura da melhor plataforma de proteção de terminais para a sua organização, é provável que esteja a equilibrar tecnologia antiga, adoção da nuvem e uma resposta contínua a incidentes. Com os atacantes a agir rapidamente e os regulamentos em constante evolução, lacunas na cobertura ou respostas lentas podem significar perda de produtividade — ou pior.
Este guia compara plataformas de elevado desempenho que combinam deteção avançada, reversão de ataques de ransomware e integração com o seu ecossistema de segurança mais abrangente. Obtenha as informações necessárias para selecionar ferramentas que estejam verdadeiramente alinhadas com os seus riscos, a sua infraestrutura e a sua presença global.
Why Trust Our Software Recommendations
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Our team has been testing and reviewing software since 2012. As tech leaders ourselves, we know how difficult—and important—it is to choose the right software.
For this guide, we evaluated tools using hands-on testing and independent research, scoring tools using our selection criteria.
Our reviews reflect our human editorial judgment, not a sales pitch.
Expert reviewers:
- Paulo Gardini MiguelTech Director
 Tim FisherVP of AI
 Gabriel RosasTech Lead & Software Architect
 Christhian GruhnTech Lead & Platform Architect

Tabela de comparação de plataformas de proteção de terminais
A tabela abaixo compara os detalhes de preços das minhas principais escolhas de plataformas de proteção de terminais.
Score legend (out of 5)
- Excellent4.5–5
- Good4–4.4
- Average3–3.9
- Below average2–2.9
- Poor1–1.9
Sorted by: Default
| Tool | Starting Price | Website | ||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
Best for adding security controls to Scalefusion | Not rated | 3 | Not rated | 3 | 4 | 3 | Not rated | Not rated | Not rated | Not rated | Not rated | Not rated | $2/device/month 14-day free trial + free demo available | Website |
Best for enterprise-grade threat hunting at scale | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | $7.99/device/month 15-day free trial available | Website |
Best for multi-layered behavioral analysis | Not rated | Not rated | Not rated | 4 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | Pricing upon request Free demo available | Website |
Best for ransomware rollback after an active attack | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 4 | 5 | 5 | 5 | Pricing upon request Free trial available | Website |
Best for AI-driven XDR across enterprise endpoints | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 4 | 5 | 5 | 5 | Pricing upon request Free demo available | Website |
Best for multi-layered ransomware rollback and MDR | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | Pricing upon request Free demo available | Website |
Best for AI-native autonomous endpoint defense | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | Pricing upon request Free demo available | Website |
Best for legacy enterprise endpoints | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | Pricing upon request Free demo available | Website |
Best for Microsoft 365-based orgs | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | Pricing upon request Not available | Website |
Best for defense with identity context | Not rated | Not rated | Not rated | 5 | Not rated | Not rated | Not rated | 5 | 5 | 5 | 5 | 5 | Pricing upon request Free demo available | Website |


Avaliações de plataformas de proteção de terminais
Seguem-se os meus resumos detalhados das melhores plataformas de proteção de terminais que entraram na minha seleção. As minhas avaliações oferecem uma análise detalhada das funcionalidades, dos melhores casos de utilização e das capacidades de cada plataforma, para o ajudar a encontrar a melhor opção para si.
 Best for adding security controls to Scalefusion
- 14-day free trial + free demo available
- From $2/device/month (billed annually)
Visit WebsiteCustomer Rating:4.8/5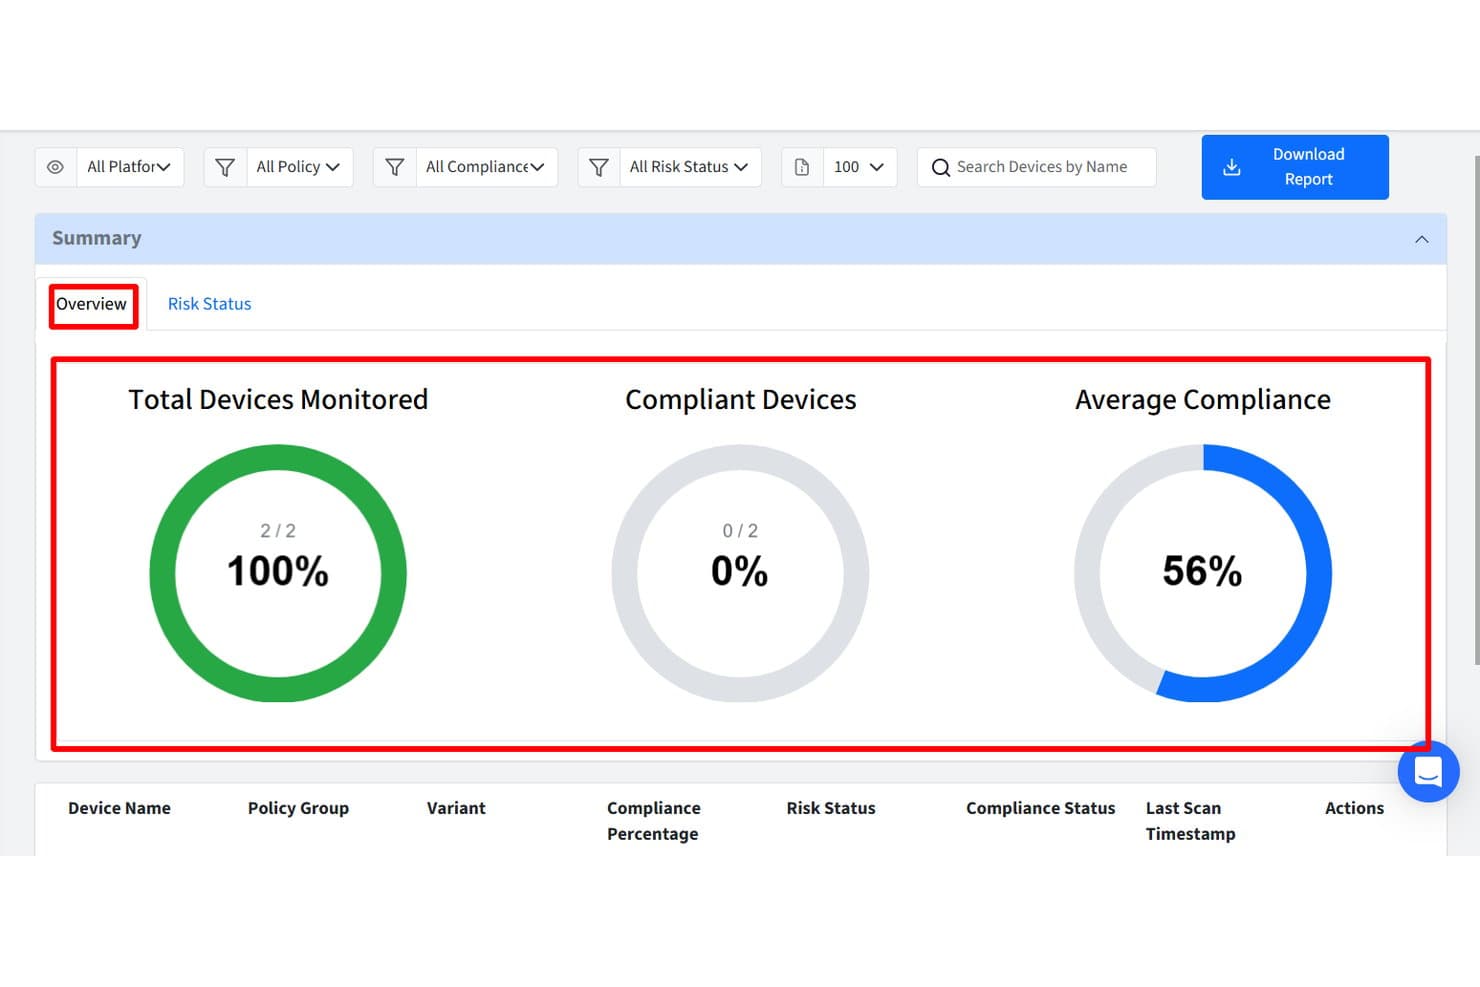
Veltar's compliance summary dashboard tracks monitored devices, compliant devices, and average compliance across the fleet. Scalefusion Veltar is a UEM-integrated endpoint security add-on that bundles DLP, secure web gateway, vulnerability management, compliance automation, and business VPN into a single lightweight agent.
Who Is Scalefusion Veltar Best For?
Veltar is a strong fit for IT administrators who already use Scalefusion UEM and need to layer DLP, compliance automation, and secure web access onto their existing device fleet.
Why I Picked Scalefusion Veltar
I've included Scalefusion Veltar in my top picks because it's the most direct way to add layered security controls to an existing Scalefusion UEM deployment without introducing a separate agent or console. I like how it bundles DLP, secure web gateway, and automated CIS Benchmark enforcement into the same platform your team already uses to manage devices. In practice, that means you can block USB data transfers and restrict cloud app logins to corporate domains from the same dashboard where you're already pushing policies.
Scalefusion Veltar Key Features
- Business VPN with split tunneling: Routes critical traffic through an encrypted tunnel while letting other data use a separate path, so you can enforce policies without slowing everything down.
- Vulnerability detection and remediation: Scans endpoints for vulnerabilities, prioritizes them by risk, and lets you push fixes through UEM-driven actions from the same console.
- CIS Benchmark automation: Automatically tracks and enforces CIS Level 1 and Level 2 controls across your device fleet to keep compliance status current.
- Audit logging for VPN changes: Records all configuration changes made in the network environment so you have a clear trail for compliance reviews.
Scalefusion Veltar Integrations
Scalefusion Veltar has native integrations with Scalefusion UEM and OneIdP. It also supports custom OIDC authentication for VPN access.
Pros and Cons
Pros:
- Endpoint DLP and web access controls
- Automated CIS Benchmark enforcement
- Centralized visibility across managed devices
Cons:
- No incident investigation or response workflows
- No documented malware or ransomware detection
Learn more about Scalefusion Veltar: Best for enterprise-grade threat hunting at scale
- 15-day free trial available
- From $7.99/device/month
Visit WebsiteCustomer Rating:4.6/5
CrowdStrike Falcon tracks CVE vulnerabilities across endpoints by host and severity. CrowdStrike Falcon is a cloud-native endpoint protection platform that combines next-gen antivirus, EDR, threat intelligence, device control, firewall management, and AI-powered threat hunting across enterprise endpoints.
Who Is CrowdStrike Falcon Best For?
CrowdStrike Falcon is a strong fit for large enterprises and security operations teams managing thousands of endpoints across distributed environments.
Why I Picked CrowdStrike Falcon
CrowdStrike Falcon earns its spot on my shortlist because of Falcon Adversary OverWatch, a managed threat hunting layer that analyzes trillions of events continuously to catch what automated detections miss. I like that OverWatch pairs human hunters with AI-driven detection, so your SOC gets actionable findings rather than raw alerts to sort through. The EDR telemetry feeding into that process gives hunters deep visibility across every endpoint at scale.
CrowdStrike Falcon Key Features
- Falcon Prevent: An AI-powered next-gen antivirus that blocks malware, fileless attacks, and zero-day exploits using machine learning and behavioral analysis—even when endpoints are offline.
- Falcon Insight XDR: Extended detection and response that correlates endpoint telemetry with data from cloud environments, identity systems, and third-party security tools for cross-domain visibility.
- Falcon Firewall Management: Centralized firewall policy enforcement across Windows and macOS devices, with pre-built policies, reusable rules, and role-based access controls.
- Adversary intelligence profiles: Built-in threat intelligence covering 245+ tracked adversary groups, giving your security team context on attacker tactics, techniques, and procedures during investigations.
CrowdStrike Falcon Integrations
CrowdStrike Falcon connects with a large partner ecosystem through the CrowdStrike Marketplace, with documented integrations including AWS, Microsoft Azure, Microsoft Sentinel, ServiceNow, Splunk, Zscaler, Okta, Nutanix, Darktrace, and NinjaOne. Falcon also provides public APIs for custom integrations and SIEM, SOAR, and threat intelligence data connectors.
Pros and Cons
Pros:
- Managed threat hunting operates 24/7
- Endpoint telemetry gives deep investigation visibility
- Human threat hunters analyze live attacks
Cons:
- Advanced settings require skilled security staff
- Requires strong network connectivity for full value
Learn more about CrowdStrike Falcon: Best for multi-layered behavioral analysis
- Free demo available
- Pricing upon request

Symantec Endpoint Protection alerts users to threats via real-time notifications. Symantec Endpoint Protection is an endpoint protection platform that combines malware detection, behavioral analysis, attack surface reduction, endpoint detection and response (EDR), and threat hunting across Windows, Mac, Linux, mobile, and virtual environments.
Who Is Symantec Endpoint Protection Best For?
It's a strong fit for enterprise security teams managing large, mixed-OS environments that need layered threat detection across physical, virtual, and mobile endpoints.
Why I Picked Symantec Endpoint Protection
Symantec Endpoint Protection earns its spot on my shortlist because its SONAR behavioral analysis engine layers heuristics, machine learning, and reputation data together to catch threats that signature-based detection misses entirely. I find the depth here genuinely impressive: it monitors process behavior in real time and cross-references the Global Intelligence Network to flag zero-day activity before it executes. That combination makes it one of the few platforms I trust for environments where unknown and living-off-the-land attacks are a real concern.
Symantec Endpoint Protection Key Features
- Active Directory defense: Monitors and protects Active Directory from credential theft and reconnaissance attacks that precede lateral movement.
- Attack surface reduction: Applies application control, device control, and exploit mitigation to shrink the number of entry points available to attackers.
- AI-guided policy management: Uses AI to recommend and automate policy adjustments, reducing manual configuration burden on security operations teams.
- Single-agent, multi-deployment architecture: Runs one agent across cloud, on-premises, and hybrid environments, managed through a single cloud console.
Symantec Endpoint Protection Integrations
Symantec Endpoint Protection offers native integrations with Symantec Endpoint Protection Manager, Microsoft Active Directory, Microsoft Entra ID, Symantec CloudSOC, Symantec Secure Web Gateway, Symantec Content Analysis, and unified endpoint management providers, plus event streaming to SIEM tools like Splunk and FortiSIEM. It also provides REST APIs through the Broadcom Enterprise Security Group for custom integrations.
Pros and Cons
Pros:
- AI-driven automated policy recommendations
- Active Directory protections built into core agent
- Real-time behavioral monitoring against advanced threats
Cons:
- Policy updates can be slow to sync
- High system resource usage during scans
Learn more about Symantec Endpoint Protection: Best for ransomware rollback after an active attack
- Free trial available
- Pricing upon request

Sophos dashboard gives admins a full view of device compliance. Sophos Endpoint is an endpoint protection platform that combines AI-driven threat detection, behavioral analysis, anti-ransomware technology, and centralized device management across Windows, macOS, and Linux environments.
Who Is Sophos Endpoint Best For?
Sophos Endpoint is a strong fit for IT security teams in mid-to-large organizations that need active ransomware defense with the ability to roll back encrypted files after an attack.
Why I Picked Sophos Endpoint
Sophos Endpoint earns its spot because of CryptoGuard, its behavioral ransomware detection layer that doesn't just block an attack—it rolls back encrypted files to their pre-attack state after the fact. If ransomware slips past earlier defenses and starts encrypting files, CryptoGuard detects the unauthorized encryption in real time and automatically restores affected data. I also like the kernel-level tamper protection, which blocks attackers from killing the endpoint agent before the rollback can trigger.
Sophos Endpoint Key Features
- Deep learning malware prevention: Multiple AI models scan files before execution to detect known malware and zero-day variants, including AI-generated mutations.
- Anti-exploitation controls: Over 60 built-in exploit mitigations block attacker techniques across the attack chain with no per-application configuration needed.
- Peripheral device control: Monitors and blocks access to removable media, Bluetooth devices, and mobile hardware to prevent unauthorized data transfer or malware entry.
- Malicious traffic detection: Analyzes outbound non-browser network traffic to identify communication with attacker command-and-control servers in real time.
Sophos Endpoint Integrations
Sophos Endpoint offers native integrations with Splunk, Microsoft Sentinel, ServiceNow, Jira, PagerDuty, Slack, Microsoft Teams, Okta, Amazon Web Services, and Google Cloud, plus native integrations across the Microsoft ecosystem, including Microsoft 365 and Entra ID. Sophos Central also provides an API for custom integrations and connects with a range of RMM and PSA tools like ConnectWise, Datto, and Kaseya.
Pros and Cons
Pros:
- Blocks over sixty attacker exploit techniques
- Kernel-level tamper protection prevents agent disabling
- Ransomware rollback restores encrypted files fast
Cons:
- Occasional false positives trigger unwanted remediation
- Rollback feature available only on Windows
Learn more about Sophos Endpoint: Best for AI-driven XDR across enterprise endpoints
- Free demo available
- Pricing upon request

Cortex XDR's AI assistant summarizes cases and identifies compromised users instantly. Cortex XDR is an AI-driven extended detection and response (XDR) platform from Palo Alto Networks that covers endpoint protection, threat detection, investigation, and response across endpoints, network, cloud, identity, and email from a single agent and unified data lake.
Who Is Cortex XDR Best For?
Cortex XDR is a strong fit for large enterprises that need unified threat detection and response across endpoints, cloud, network, and identity from a single platform.
Why I Picked Cortex XDR
I've included Cortex XDR in my top picks because its AI-driven detection goes beyond signature-based methods, using behavioral analytics across endpoint, network, cloud, and identity data simultaneously to surface threats that siloed tools would miss. I'm particularly impressed by its Cortex AgentiX AI agents, which automate root cause analysis and can contain an active attack within minutes without manual intervention. The single-agent architecture also handles NG-SIEM, endpoint data loss prevention, and exposure management in one deployment, which cuts the complexity of running separate tools across a large environment.
Cortex XDR Key Features
- Zero-day and fileless malware prevention: Dedicated prevention modules block zero-day exploits, fileless malware, and process-hijacking attacks before they execute on endpoints.
- Managed detection and response: Unit 42 MDR operates directly inside your Cortex XDR tenant to handle proactive threat hunting, monitoring, and remediation on your behalf.
- Managed threat hunting: Unit 42 analysts combine their threat intelligence with Cortex XDR's AI analytics to validate and surface threats earlier than automated detection alone.
- Alert triage and noise reduction: Cortex XDR correlates alerts across data sources and groups related events into incidents, cutting alert volume so your team works fewer, higher-quality cases.
Cortex XDR Integrations
Cortex XDR offers native integrations with Palo Alto Networks Next-Generation Firewalls, Prisma Cloud, Active Directory, AWS, Microsoft Azure, Google Cloud Platform, Okta, Microsoft 365, and ingests data from third-party firewalls like Cisco and Fortinet. It connects to Cortex XSOAR for automated response playbooks and provides a REST API for custom integrations with tools like Splunk, ServiceNow, and Rapid7 InsightIDR.
Pros and Cons
Pros:
- Unit 42 MDR handles proactive threat response
- Behavioral analytics catch fileless and zero-day threats
- AI-driven threat hunting covers endpoints and cloud
Cons:
- High alert volume may still overwhelm small teams
- Incident investigation tools sometimes feel complex
Learn more about Cortex XDR: Best for multi-layered ransomware rollback and MDR
- Free demo available
- Pricing upon request
Visit WebsiteCustomer Rating:4.2/5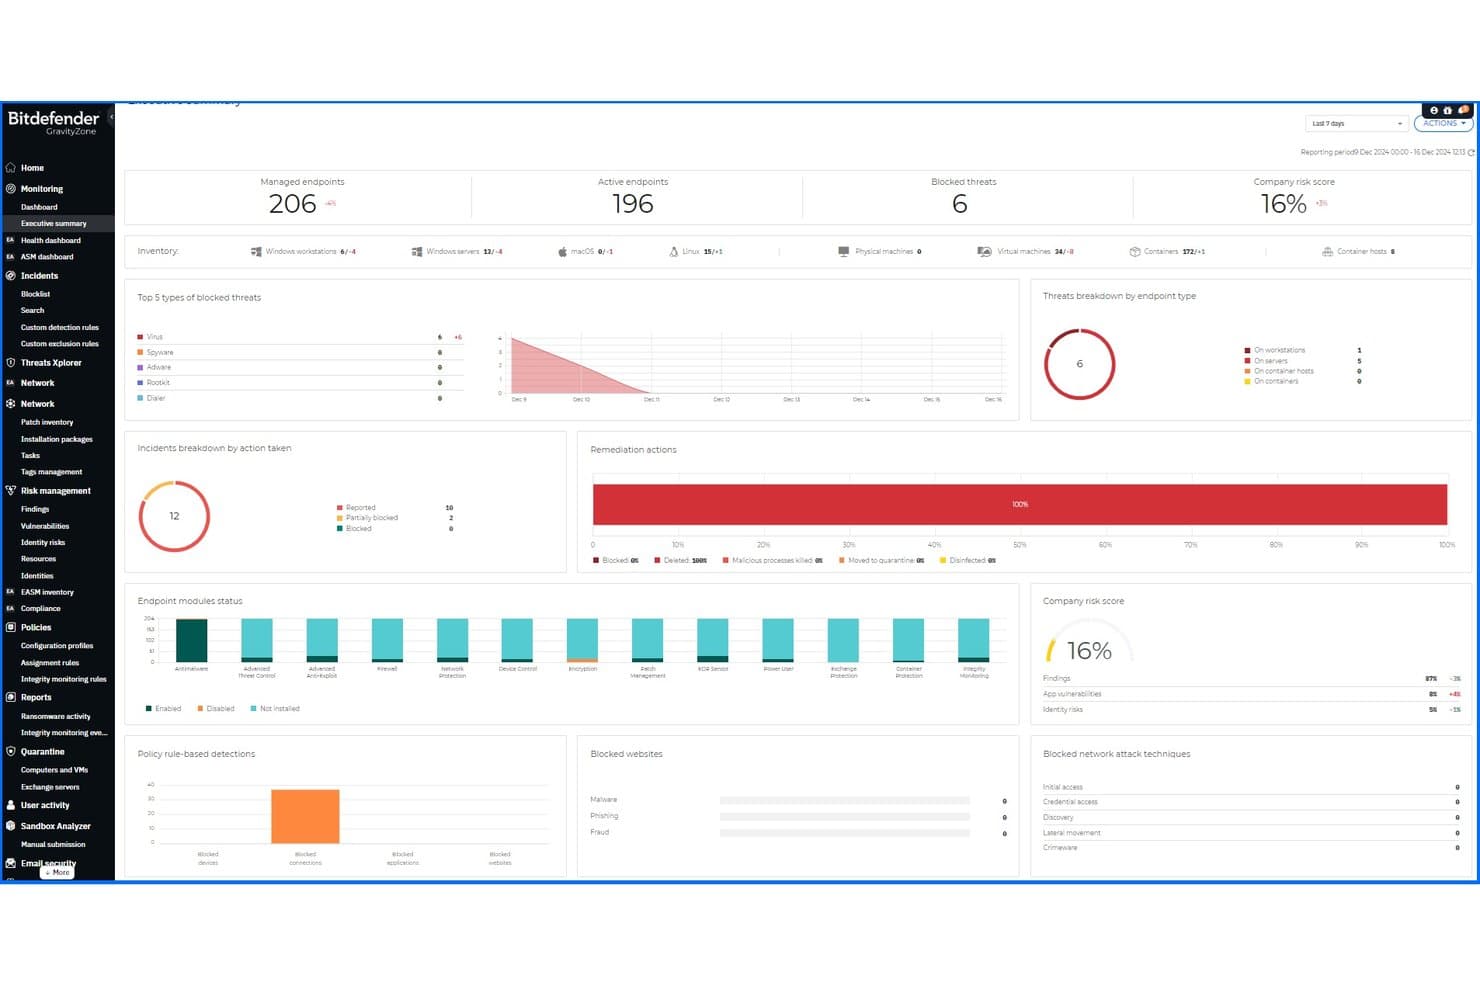
Bitdefender GravityZone provides a unified executive summary dashboard for endpoint security. Bitdefender GravityZone is an endpoint protection platform that combines machine learning, behavioral analysis, network attack defense, risk management, and web content control into a single cloud or on-premise management console for small and medium-sized businesses.
Who Is Bitdefender GravityZone Best For?
GravityZone is a strong fit for SMBs that need enterprise-grade threat detection without a large in-house security team.
Why I Picked Bitdefender GravityZone
I picked Bitdefender GravityZone as one of the best because its ransomware mitigation goes beyond detection. When GravityZone spots abnormal encryption activity, it blocks the process and automatically recovers affected files from backup copies, restoring them to their pre-attack state. Layer that with Bitdefender MDR, which provides 24/7 analyst-led threat monitoring with pre-approved response actions, and you get a platform that can contain active threats without waiting on customer approval.
Bitdefender GravityZone Key Features
- Patch management: Automatically keeps Windows OS and third-party applications up to date across managed endpoints to reduce exposure to known vulnerabilities.
- Email security: Scans and filters inbound and outbound email threats across Microsoft 365, Gmail, and Exchange to block phishing, malware, and spam before they reach users.
- Full disk encryption: Enforces encryption on endpoint storage using native OS tools, ensuring data on lost or stolen devices stays protected.
- Mobile device security: Extends endpoint protection to iOS, Android, and ChromeOS devices, applying threat detection and policy enforcement to mobile endpoints alongside desktops and servers.
Bitdefender GravityZone Integrations
Bitdefender GravityZone offers native integrations with VMware vCenter, Microsoft Active Directory, Microsoft Exchange, Veeam Backup & Replication, Splunk, ConnectWise PSA, HaloPSA, Okta, Jira, and Slack, plus XDR sensor integrations across the Microsoft ecosystem (Microsoft 365, Azure, Azure AD, Intune, Defender), AWS, and Google Workspace. An API is available for custom integrations, and it supports SIEM forwarding via syslog and webhook.
Pros and Cons
Pros:
- Extensive endpoint and mobile device coverage
- 24/7 managed detection and response available
- Automatic ransomware rollback and file recovery
Cons:
- Policy configuration options may overwhelm new admins
- Forensic analysis features can feel basic
Learn more about Bitdefender GravityZone: Best for AI-native autonomous endpoint defense
- Free demo available
- Pricing upon request
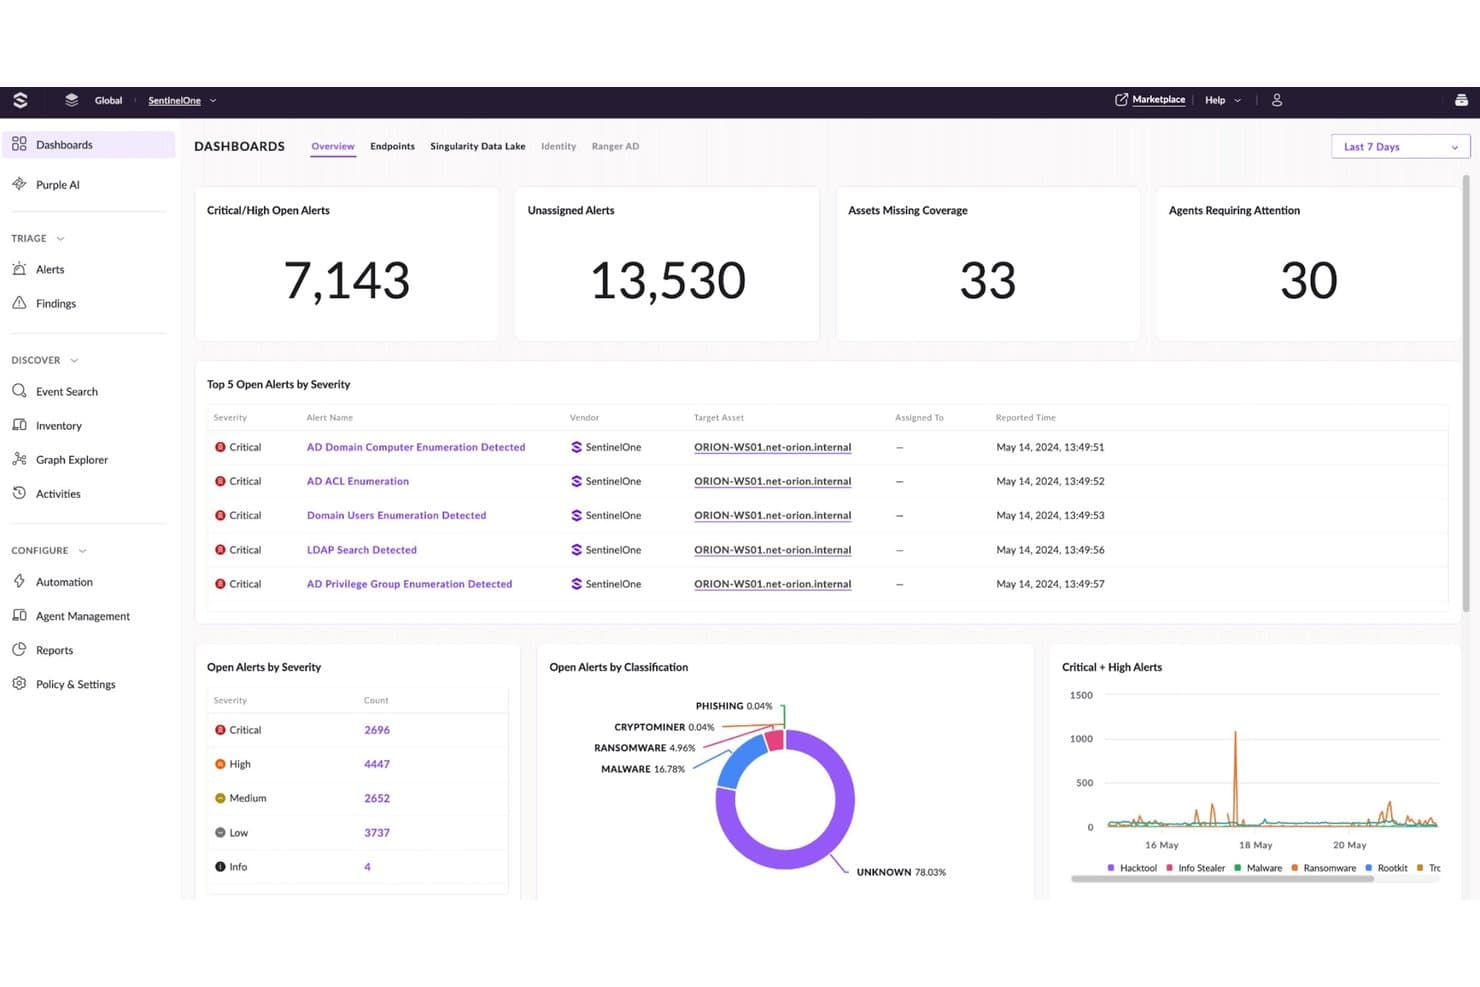
SentinelOne Singularity centralizes critical threat alerts and endpoint coverage metrics. SentinelOne Singularity is an AI-native endpoint protection platform that unifies endpoint, identity, cloud, and mobile security under a single console, with autonomous threat detection and response across ransomware, zero-days, fileless malware, and supply chain attacks.
Who Is SentinelOne Singularity Best For?
SentinelOne Singularity is a strong fit for security operations teams at mid-to-large enterprises that need autonomous threat response across endpoints, cloud workloads, and identity without relying on manual analyst intervention.
Why I Picked SentinelOne Singularity
SentinelOne Singularity earns its spot on my shortlist because its AI-driven Storyline technology automatically correlates related events across endpoints into a single attack narrative, so analysts aren't manually stitching together alerts after the fact. I also like that its ActiveEDR can roll back malicious changes autonomously without waiting for human approval, which is rare at this level of fidelity. The Singularity platform covers endpoints, cloud workloads, and identity under one console, making it a genuinely unified surface for detection and response.
SentinelOne Singularity Key Features
- Purple AI: An agentic AI analyst built into the platform that automates triage, threat hunting, and investigation using natural language queries.
- Singularity Hyperautomation: A no-code interface for building and executing automated response workflows directly inside the Singularity Platform.
- AI SIEM: Ingests and normalizes third-party and native telemetry into a single data layer for unified detection, investigation, and response.
- Singularity Mobile: Extends real-time endpoint protection to mobile devices, blocking phishing, malware, and zero-day exploits on iOS and Android.
SentinelOne Singularity Integrations
SentinelOne Singularity offers one-click integrations through its Singularity Marketplace, including Splunk, IBM QRadar, ServiceNow, Okta, Zscaler, Netskope, Recorded Future, Swimlane, AWS, and Mimecast. An API is also available for custom integrations and automation workflows.
Pros and Cons
Pros:
- ActiveEDR can autonomously roll back ransomware attacks
- Purple AI automates incident triage and hunting
- Storyline technology reconstructs full attack narratives
Cons:
- Some advanced features only in premium tiers
- Requires tuning to reduce initial alert volume
Learn more about SentinelOne Singularity: Best for legacy enterprise endpoints
- Free demo available
- Pricing upon request
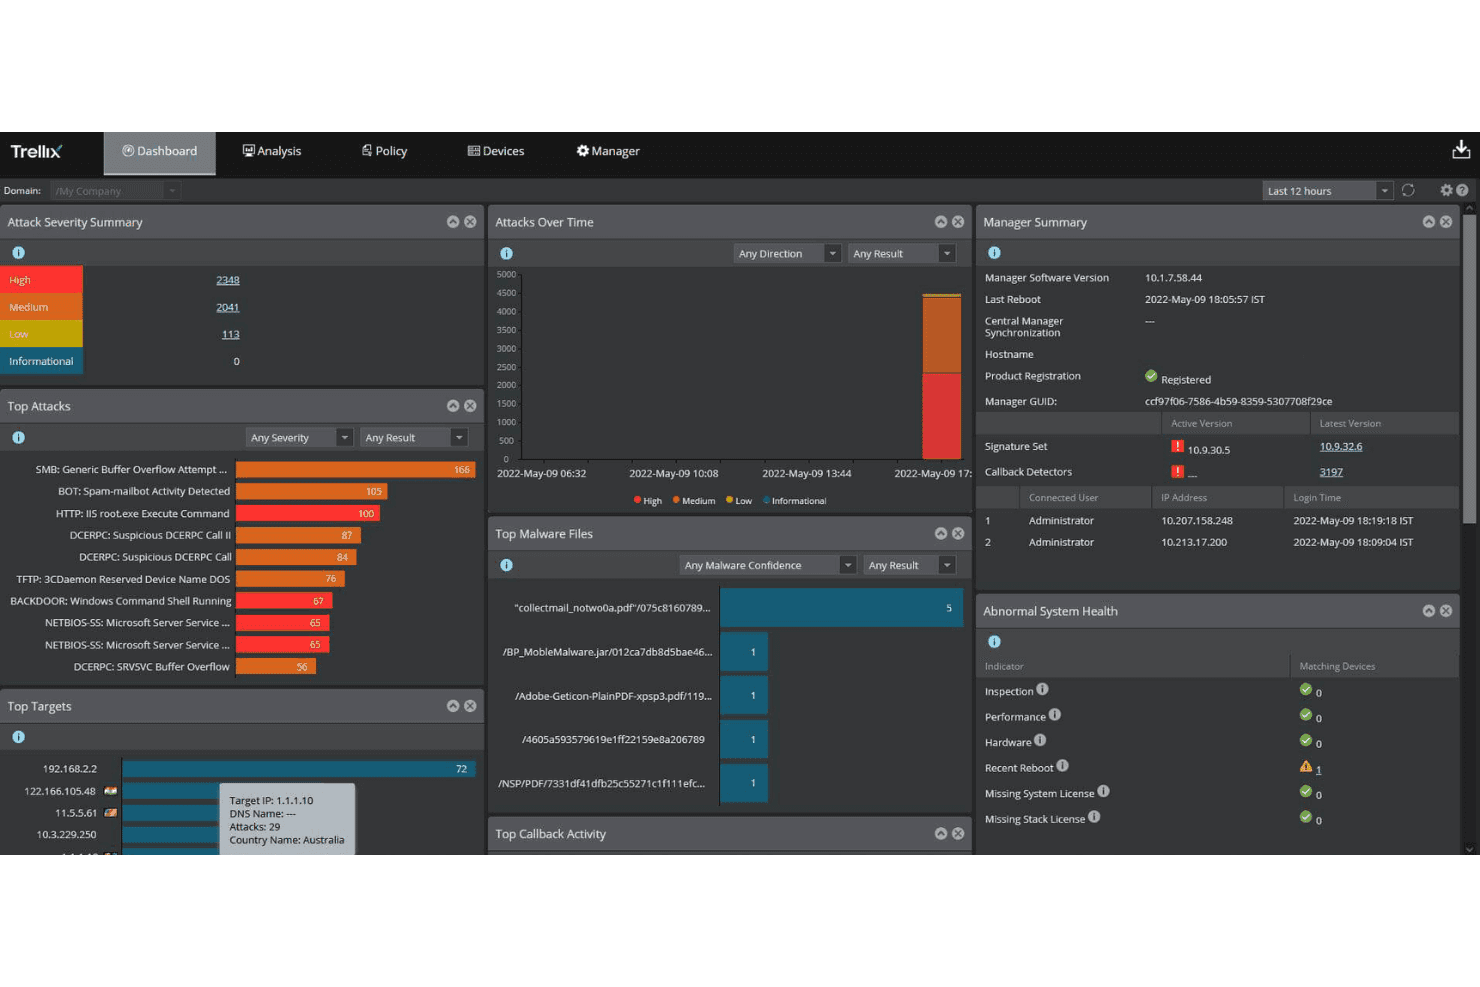
Trellix centralizes threat monitoring across severity, targets, and malware activity. Trellix Endpoint Security is an AI-powered endpoint protection platform that combines threat detection, application control, and cloud workload security across physical, virtual, and hybrid environments using a single agent.
Who Is Trellix Endpoint Security Best For?
Trellix Endpoint Security is a strong fit for large enterprises managing mixed environments that include older operating systems and legacy infrastructure alongside modern endpoints.
Why I Picked Trellix Endpoint Security
Trellix Endpoint Security earns its spot on my list because of how seriously it takes legacy infrastructure, something most modern EPP vendors quietly avoid. Trellix extends support for Windows XP-based systems through December 2028, which is a real differentiator if your environment includes older OT devices, industrial systems, or endpoints that simply can't be upgraded. I also like its Application and Change Control feature, which locks down servers and workstations by allowing only trusted applications to run, a key control for environments where patch cycles are irregular. The single-agent architecture covers on-premises, cloud, and air-gapped deployments without requiring separate tooling.
Trellix Endpoint Security Key Features
- Adaptive threat protection: Uses machine learning and behavioral analysis to detect and block file-based, fileless, and script-based threats in real time.
- Trellix ePolicy Orchestrator (ePO): A centralized management console for configuring, enforcing, and auditing endpoint security policies across on-premises, IaaS, and SaaS deployments.
- Threat Intelligence Exchange (TIE): Shares real-time threat intelligence across endpoints, email gateways, and network sensors so detections on one system inform protection across your entire environment.
- Trellix Wise: An AI-powered investigation engine that correlates alerts across endpoint, email, network, and cloud sources, then generates investigation summaries with containment and remediation recommendations.
Trellix Endpoint Security Integrations
Trellix Endpoint Security connects through Trellix ePolicy Orchestrator (ePO), which integrates with 150+ third-party security and IT tools, including ServiceNow, Splunk, Swimlane, BeyondTrust, MobileIron, IBM Resilient, AWS, and Microsoft Azure, plus Trellix products like EDR, DLP, and Email Security. An API is available for custom integrations, and the Trellix Marketplace hosts additional partner apps for SIEM, SOAR, and threat intelligence workflows.
Pros and Cons
Pros:
- Application and change control for legacy systems
- Single agent covers mixed physical and virtual endpoints
- Extends support for Windows XP environments
Cons:
- Policy configuration complexity frustrates new admins
- Interface feels dated compared to competitors
Learn more about Trellix Endpoint Security: Best for Microsoft 365-based orgs
- Not available
- Pricing upon request
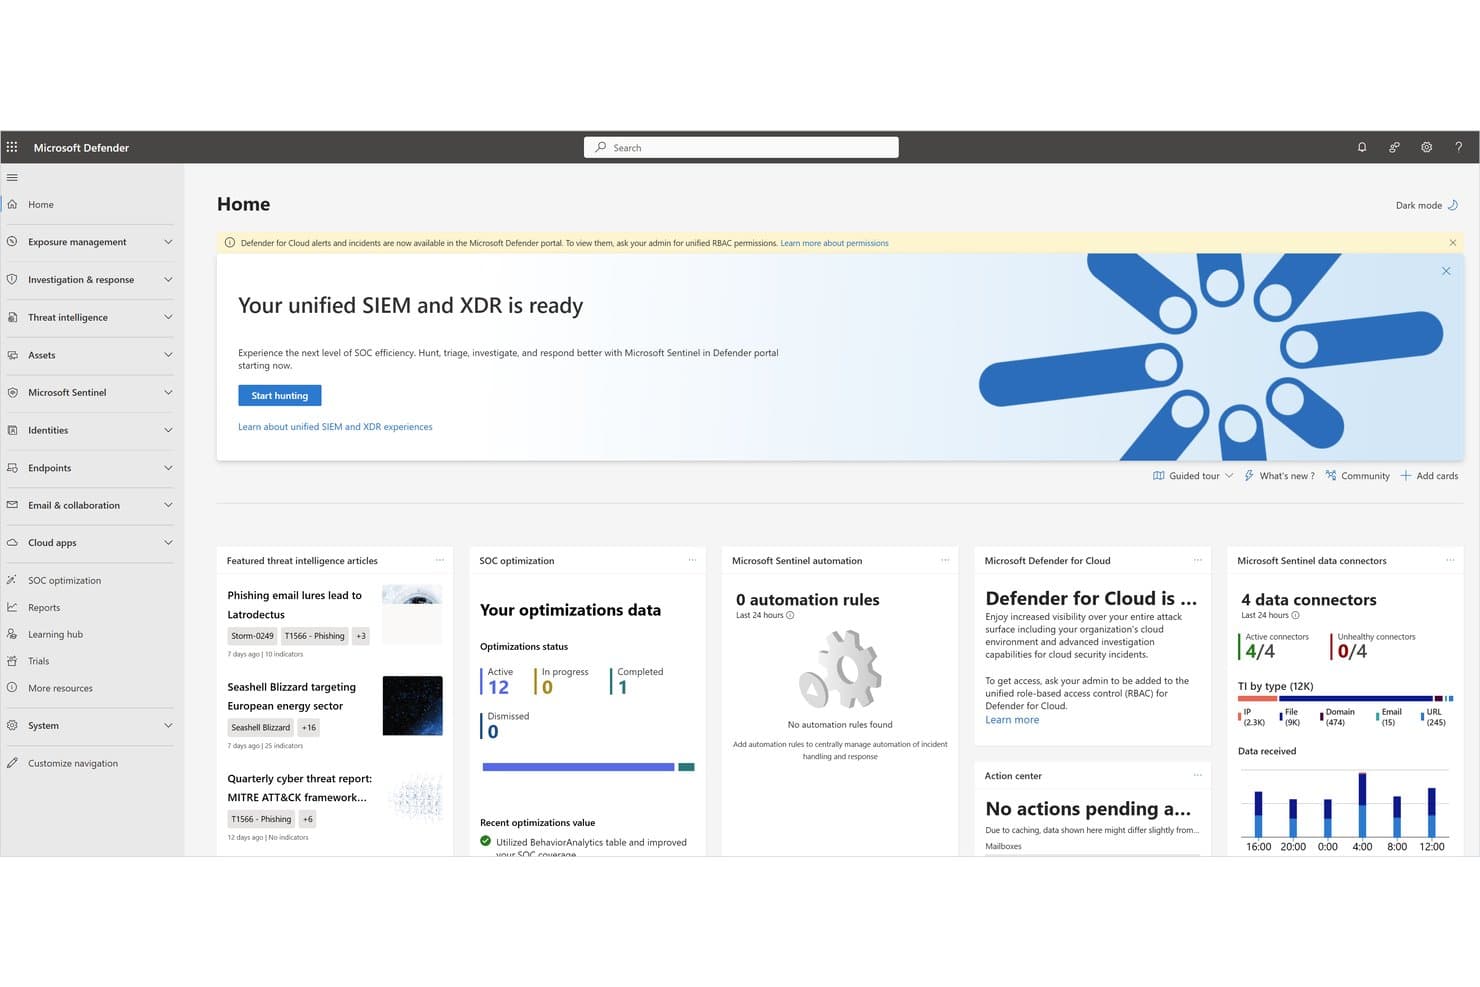
Microsoft Defender for Endpoint unifies SIEM and XDR for streamlined SOC operations. Microsoft Defender for Endpoint is a cloud-native endpoint protection platform that combines threat detection, vulnerability management, attack surface reduction, and extended detection and response (XDR) capabilities across Windows, macOS, Linux, iOS, and Android devices.
Who Is Microsoft Defender for Endpoint Best For?
It's a natural fit for organizations already running Microsoft 365 or Azure, where native integration with the Microsoft security stack removes the need for third-party endpoint agents.
Why I Picked Microsoft Defender for Endpoint
Microsoft Defender for Endpoint earns its spot on my shortlist because it's built directly into the Microsoft ecosystem, which means if your org runs Microsoft 365, you're getting XDR coverage without bolting on a separate agent. I particularly like how its attack surface reduction rules let you lock down specific behaviors, like blocking Office applications from spawning child processes, across your entire device fleet from a single policy. The integration with Microsoft Sentinel also means threat signals from endpoints feed directly into your SIEM without manual connector configuration.
Microsoft Defender for Endpoint Key Features
- Threat and vulnerability management: Continuously scans enrolled endpoint devices to surface misconfigurations, missing patches, and software vulnerabilities ranked by exposure risk.
- Automated investigation and remediation: Automatically triages alerts, traces attack chains, and resolves threats on affected endpoints without requiring manual analyst intervention.
- Live response: Opens a remote shell session to an endpoint so you can collect forensic artifacts, run scripts, and isolate or remediate a device in real time.
- Behavioral blocking and containment: Detects and stops suspicious in-memory and process behaviors on-device, even when malware attempts to evade signature-based detection.
Microsoft Defender for Endpoint Integrations
Microsoft Defender for Endpoint has native integrations across the Microsoft ecosystem, including Microsoft Sentinel, Microsoft Intune, Microsoft Entra ID, Microsoft Defender for Cloud, Microsoft Defender for Identity, Microsoft Purview, and Azure. It also connects with third-party tools like ServiceNow, Splunk, and Jamf Pro, and provides APIs for custom integrations and SIEM connectors.
Pros and Cons
Pros:
- Automated triage reduces manual incident response
- Attack surface reduction applies to entire fleet
- Native integration with Microsoft security stack
Cons:
- Limited support for non-Microsoft environments
- No trial option for hands-on evaluation
Learn more about Microsoft Defender for Endpoint: Best for defense with identity context
- Free demo available
- Pricing upon request
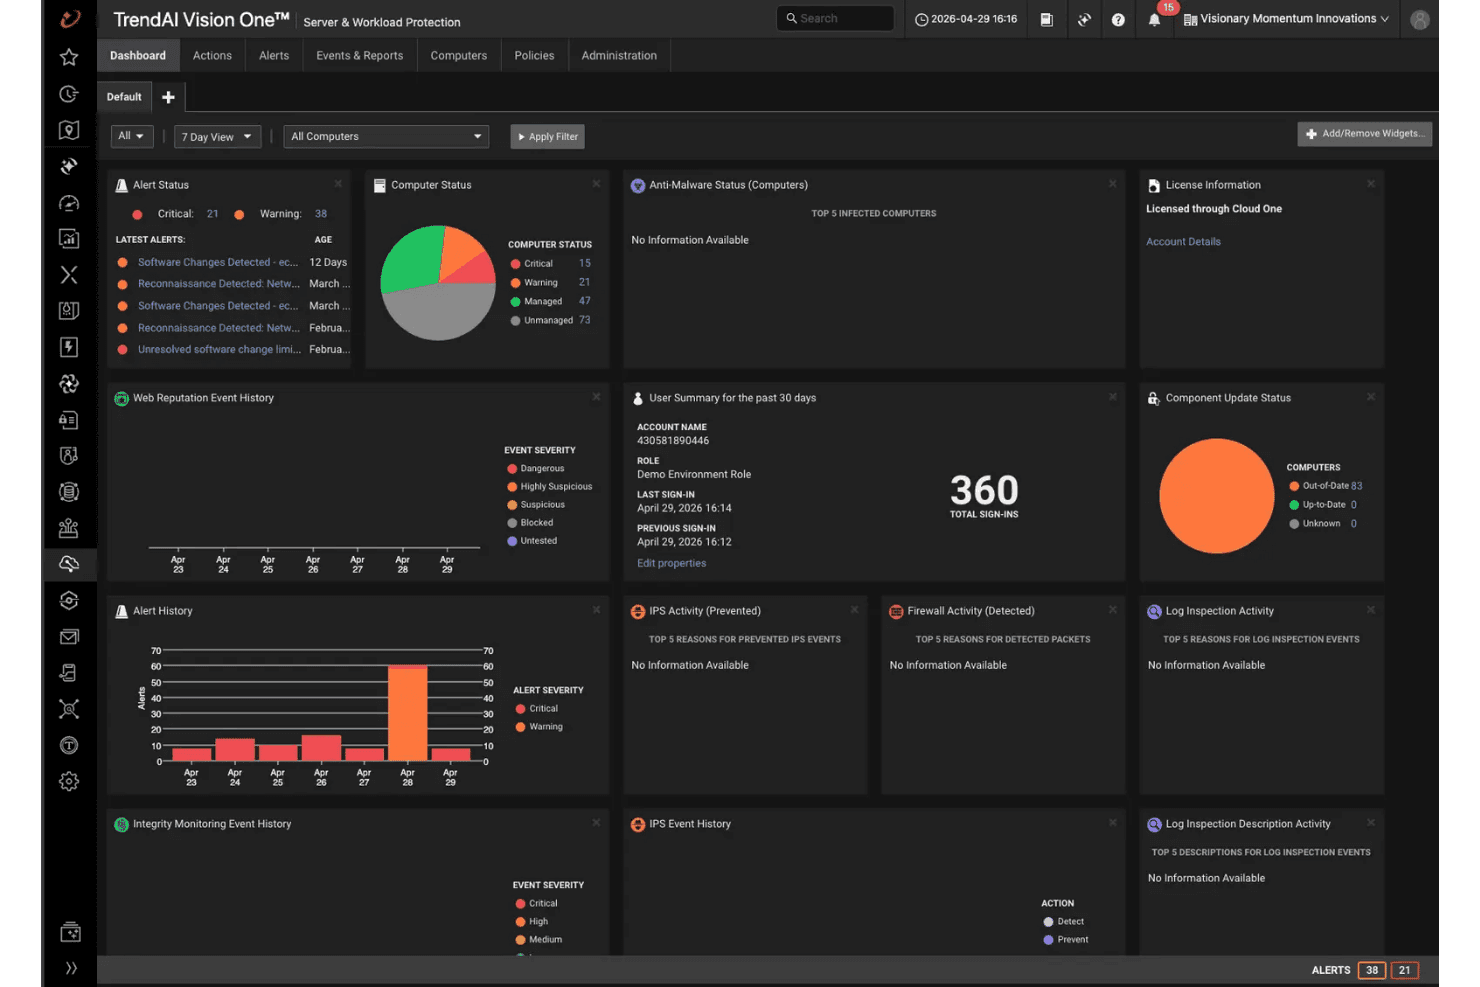
TrendAI Vision One offers security alerts and computer status at a glance. TrendAI Vision One is an AI-powered endpoint protection platform that combines EDR, XDR, automated incident response, and attack surface risk management across endpoints, servers, cloud workloads, and IoT environments from a single console.
Who Is TrendAI Vision One Best For?
TrendAI Vision One is a strong fit for enterprise security teams managing hybrid environments who need endpoint, identity, and XDR threat detection unified in a single console.
Why I Picked TrendAI Vision One
TrendAI Vision One earns its spot on my list because of how it ties identity signals directly into endpoint defense. When an alert fires, the platform automatically enriches it with identity context, asset risk, and exposure data, so analysts aren't chasing answers across disconnected tools. I also like that it accounts for Microsoft Entra ID security defaults when evaluating identity risk, which adds a layer of precision to prioritization. That combination of native XDR telemetry and identity-aware detection is what makes it genuinely useful when investigating lateral movement or compromised credentials.
TrendAI Vision One Key Features
- Virtual patching: Applies protection rules for known vulnerabilities at the network layer before a formal patch is deployed, reducing exposure on unpatched endpoints and servers.
- Behavioral analysis: Monitors process activity and execution patterns in real time to detect ransomware and exploit techniques that signature-based detection alone would miss.
- Automated security playbooks: Lets you configure predefined response actions that trigger automatically when specific threat conditions are met, reducing manual triage time.
- Attack surface risk management: Continuously inventories devices, accounts, and vulnerabilities across your environment and assigns risk scores to help you prioritize remediation.
TrendAI Vision One Integrations
TrendAI Vision One supports native integrations with Active Directory, Microsoft Entra ID, Google Cloud Identity, Okta, Splunk, Azure Sentinel, ServiceNow, AWS S3, QRadar, and Palo Alto Panorama, along with connectors for Cortex XSOAR, Chronicle SOAR, FortiGate, Check Point, Rapid7 Nexpose, Nessus, MISP, and VirusTotal. An API is available for custom integrations, and syslog and TAXII feeds are supported for extending data sharing across your security stack.
Pros and Cons
Pros:
- Automated security playbooks for fast incident response
- Virtual patching protects unpatched endpoints and servers
- Identity context enriches every security alert
Cons:
- Asset inventory can miss some IoT devices
- Advanced features may require additional training
Learn more about TrendAI Vision One :
Outras plataformas de proteção de terminais
Eis algumas opções adicionais de plataformas de proteção de terminais que não entraram na minha seleção, mas que ainda vale a pena conhecer:
- 11CynetBest for MSP-ready endpoint security with bundled MDR
- 12FortiClientBest for Fortinet Security Fabric ecosystem protection
- 13Kaspersky NextBest for enterprises outside US-aligned markets
- 14Acronis Cyber Protect CloudBest for backup-native endpoint security built for MSPs
- 15N-ableBest for MSP-native endpoint defense with built-in RMM
- 16Elastic Security Best for unified SIEM, XDR, and endpoint defense
- 17Cybereason EDRBest for operation-centric attack correlation
- 18VMware Carbon Black EndpointBest for deep EDR telemetry in complex enterprise SOCs
- 19Cisco Secure EndpointBest for Cisco-native security ecosystem
- 20WatchGuard EPDRBest for MSPs managing endpoint security at scale
How I Evaluate Endpoint Protection Platforms
When a ransomware strain bypasses prevention and starts encrypting files, I want to know exactly which tools can stop it, roll it back, and tell me how it got in—so I split my evaluation into baseline criteria every tool must meet and differentiators that separate the best from the rest.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. I then calculate the tool's total score into a percentage, using 75% as a benchmark to help assess its overall fit for the list.
- Threat prevention: I evaluate how many detection layers a platform stacks—signatures, behavioral analysis, ML models, and exploit blocking—and whether it holds up against fileless attacks, not just commodity malware.
- Endpoint detection and response: Deep telemetry, root cause analysis, and MITRE ATT&CK mapping matter here. I look for tools that let analysts hunt threats and trace lateral movement across endpoints without jumping between consoles.
- Centralized management console: I check for multi-tenant support, role-based access controls, and real-time visibility across distributed fleets. Platforms like CrowdStrike Falcon and Microsoft Defender for Endpoint both offer cloud-native consoles, but the depth of policy granularity and API access varies.
- Multi-OS endpoint support: Coverage across Windows, macOS, and Linux desktops and servers is baseline. I also evaluate whether mobile and cloud workload agents maintain feature parity with desktop counterparts.
- Automated response and remediation: Playbook-driven containment—endpoint isolation, process kills, file quarantine, and rollback of malicious changes—reduces mean time to respond. I look at how much of that workflow runs without manual intervention.
- Threat intelligence integration: Real-time feeds with contextual enrichment and adversary attribution give SOC teams an edge. I evaluate whether the platform supports third-party feed ingestion alongside its own proprietary intelligence network.
Once I have a list of tools that meet the criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Ransomware rollback is the first thing I check beyond baseline detection. I want to know if a platform can revert encrypted files to a pre-infection state automatically—without depending on external backups. Identity threat protection is equally high on my list. Platforms that tie into Active Directory or Okta to flag credential misuse and privilege escalation give SOC teams visibility that standalone EDR misses. I also evaluate XDR data fabric capabilities, since correlating endpoint, cloud, and email telemetry in one query layer cuts investigation time dramatically during cross-domain incidents.
Beyond Features
I check whether a platform offers open API access and pre-built SIEM connectors—tools like Splunk or Microsoft Sentinel need clean telemetry feeds, and gaps here create blind spots in your SOC workflows. Licensing transparency matters just as much: I evaluate whether EPP, EDR, XDR, and MDR tiers are clearly separated so you're not hit with surprise upsells when you need ransomware rollback or managed hunting. For teams serving regulated industries, I look at compliance-ready reporting for frameworks like HIPAA, PCI-DSS, and NIST 800-171, plus data residency options that support regional obligations.
Como escolher uma plataforma de proteção de terminais
Quando a sua estrutura de segurança é a base da continuidade do negócio, como pode garantir que a plataforma de proteção de terminais que escolher consegue realmente cumprir os principais requisitos de deteção, resposta e adequação operacional?
| Se a sua prioridade for... | Procure... |
|---|---|
| Se a sua prioridade for...Reversão rápida após um ataque de ransomware | Procure...Restauro de ficheiros integrado e orientado por agentes, sem dependência de cópias de segurança externas |
| Se a sua prioridade for...Compatibilidade com ambientes híbridos ou antigos | Procure...Guias de implementação comprovados e agentes compatíveis com todos os sistemas operativos e equipamentos necessários |
| Se a sua prioridade for...Integração com XDR e SIEM | Procure...Acesso a API aberta e conectores de dados pré-criados para a sua estrutura |
| Se a sua prioridade for...Requisitos de conformidade em várias regiões | Procure...Documentação do fornecedor relativa ao alojamento de dados na região e a registos de auditoria dos reguladores |
| Se a sua prioridade for...Encargos mínimos para a equipa interna de segurança | Procure...Opções integradas de deteção e resposta geridas, não apenas EDR |
Como avaliar a sua seleção
- Execute uma simulação controlada de ransomware: Exija a reversão completa de pelo menos 5 ficheiros encriptados na sua rede de laboratório.
- Teste a cobertura do agente do SO: Faça a implementação em mais de 2 terminais antigos ou específicos e verifique se todas as funcionalidades essenciais funcionam sem ajustes manuais.
- Solicite documentação de integração: Peça guias de esquemas ou documentação de configuração do conector SIEM específica para as plataformas necessárias.
- Analise a ligação à conformidade: Obtenha uma declaração escrita ou uma carta do auditor que demonstre os controlos regionais de residência dos dados.
- Esclareça o compromisso relativo ao controlo operacional: Decida se pretende visibilidade interna com uma solução EDR baseada em ferramentas ou se prefere deteção e resposta geridas sem intervenção — um filtro essencial ao reduzir o número de opções.
O que são as plataformas de proteção de terminais?
As plataformas de proteção de terminais são soluções de segurança centralizadas que detetam, impedem e respondem a ameaças direcionadas aos dispositivos da sua rede. Estas plataformas monitorizam computadores de secretária, computadores portáteis, servidores e dispositivos móveis para bloquear malware, ransomware e acessos não autorizados. Ao fornecerem visibilidade em tempo real, ferramentas de resposta coordenada e integração com sistemas de segurança mais abrangentes, as plataformas de proteção de terminais ajudam as equipas de TI a reduzir riscos, conter incidentes e manter a conformidade em ambientes complexos.
Funcionalidades
Ao selecionar plataformas de proteção de terminais, procure as seguintes funcionalidades essenciais:
- Prevenção de ameaças: Identifica e bloqueia malware, ransomware e explorações conhecidas e desconhecidas, utilizando análise baseada em assinaturas e comportamental antes que as ameaças possam ser executadas nos terminais.
- Deteção e resposta em terminais: Monitoriza continuamente os terminais, regista as atividades do sistema e permite que as equipas de resposta a incidentes investiguem ameaças, rastreiem as origens dos ataques e determinem o alcance do impacto dos incidentes.
- Consola de gestão centralizada: Fornece um painel unificado baseado na Web para implementar agentes, gerir políticas de segurança, consultar alertas e gerar relatórios sobre todos os terminais a partir de um único local.
- Suporte para vários SO: Permite proteger dispositivos com diferentes sistemas operativos, como Windows, macOS e Linux, abrangendo computadores de secretária, computadores portáteis, servidores e, por vezes, dispositivos móveis.
- Resposta e correção automatizadas: Isola automaticamente os terminais comprometidos, termina processos maliciosos, coloca ficheiros infetados em quarentena e reverte alterações resultantes de ataques para reduzir o tempo de resposta a incidentes.
- Integração de informações sobre ameaças: Obtém feeds em tempo real e indicadores de comprometimento de fontes globais para se antecipar às ameaças emergentes e melhorar a deteção com informações contextuais.
- Controlo de acesso baseado em funções: Permite às organizações atribuir permissões e funções a utilizadores e administradores, garantindo que apenas o pessoal autorizado pode gerir terminais, ajustar políticas ou aceder a informações de segurança sensíveis.
- Relatórios de conformidade: Gera relatórios pré-configurados e personalizáveis adaptados aos quadros regulamentares, facilitando a demonstração, por parte das equipas de segurança e conformidade, do cumprimento das normas exigidas.
- Opções de implementação na nuvem e no local: Suporta implementações alojadas na nuvem e no local, oferecendo às organizações a flexibilidade para adotarem o modelo que melhor se adapta à sua infraestrutura e aos seus requisitos regulamentares.
- Gestão de correções e análise de vulnerabilidades: Monitoriza os terminais à procura de correções em falta, verifica a existência de vulnerabilidades e ajuda as equipas de TI a dar prioridade às atualizações e a implementá-las para reduzir os riscos de segurança.
Funcionalidades comuns de IA
Para além das funcionalidades padrão das plataformas de proteção de terminais indicadas acima, muitas destas soluções estão a incorporar IA com funcionalidades como:
- Caça às ameaças orientada por IA: Utiliza aprendizagem automática para analisar automaticamente a telemetria dos dispositivos terminais, identificar padrões suspeitos e detetar potenciais ameaças que os analistas humanos poderão não detetar. Isto ajuda a sua equipa a detetar proativamente ataques avançados antes que estes se agravem.
- Análise comportamental automatizada: Monitoriza continuamente o comportamento dos utilizadores e dos processos nos dispositivos terminais, utilizando IA para assinalar anomalias que poderão indicar ameaças internas, utilização indevida de credenciais ou explorações de vulnerabilidades de dia zero. Isto reduz os falsos positivos e ajuda a dar prioridade aos riscos reais.
- Deteção preditiva de malware: Utiliza modelos de IA treinados com vastos conjuntos de dados para identificar e bloquear malware nunca antes detetado, com base nas características do código e nos padrões de execução, e não apenas em assinaturas conhecidas.
- Proteção adaptativa contra phishing: Utiliza IA para analisar conteúdo de correio eletrónico, URLs e interações dos utilizadores em tempo real, bloqueando tentativas de phishing e ataques de recolha de credenciais à medida que evoluem.
- Triagem de incidentes com tecnologia de IA: Correlaciona automaticamente alertas, atribui níveis de risco e recomenda ações de resposta, ajudando a sua equipa a concentrar-se nas ameaças mais urgentes e a reduzir o tempo de investigação.
- Relatórios de ameaças em linguagem natural: Gera resumos dos incidentes e das cadeias de ataque em linguagem simples, utilizando IA, facilitando a comunicação das conclusões às partes interessadas pelas equipas de TI e de segurança, bem como a documentação das ações de resposta.
Vantagens
A implementação de plataformas de proteção de dispositivos terminais proporciona várias vantagens à sua equipa e à sua empresa. Eis algumas das vantagens que poderá esperar:
- Prevenção de ameaças em todos os dispositivos: Bloqueie malware, ransomware e ataques de exploração de vulnerabilidades com deteção baseada em assinaturas e em comportamentos, abrangendo computadores de secretária, portáteis, servidores e dispositivos móveis.
- Visibilidade e controlo centralizados: Utilize uma consola de gestão unificada para supervisionar políticas de segurança, alertas e o estado de conformidade de todos os dispositivos terminais do seu ambiente.
- Resposta automatizada e remediação rápida: Contenha rapidamente as ameaças utilizando ações orientadas por manuais de procedimentos, como o isolamento de dispositivos terminais, a terminação de processos, a colocação de ficheiros em quarentena e a reversão de alterações não autorizadas.
- Suporte para vários sistemas operativos e ambientes híbridos: Proteja conjuntos diversificados de dispositivos, incluindo Windows, macOS, Linux e, por vezes, cargas de trabalho móveis ou na nuvem, sem afinação manual nem substituição de agentes.
- Informações integradas sobre ameaças: Tire partido de feeds de ameaças em tempo real e ricos em contexto, bem como de informações sobre adversários, para melhorar os fluxos de trabalho de deteção e investigação.
- Relatórios de conformidade regulamentar: Gere relatórios incorporados ou personalizáveis, associados a estruturas como HIPAA, PCI-DSS e NIST 800-171, ajudando a demonstrar os controlos aos auditores e às partes interessadas.
- Acesso a API aberta e a conectores SIEM: Envie telemetria limpa para plataformas SIEM e automatize fluxos de trabalho, estabelecendo uma ligação simples com ferramentas de operações de segurança e monitorização.
Custos e preços
A seleção de plataformas de proteção de dispositivos terminais exige uma compreensão dos vários modelos de preços e planos disponíveis. Os custos variam consoante as funcionalidades, o tamanho da equipa, os extras e outros fatores. A tabela abaixo resume os planos comuns, os respetivos preços médios e as funcionalidades normalmente incluídas nas soluções de plataformas de proteção de dispositivos terminais:
Tabela de comparação de planos
| Tipo de plano | Preço médio | Funcionalidades comuns |
|---|---|---|
| Tipo de planoPlano gratuito | Preço médio$0 | Funcionalidades comunsDeteção básica de malware, suporte limitado para dispositivos e relatórios mínimos. |
| Tipo de planoPlano pessoal | Preço médio$3-$10/utilizador/mês | Funcionalidades comunsPrevenção essencial de ameaças, proteção em tempo real, suporte para vários dispositivos e gestão centralizada básica. |
| Tipo de planoPlano empresarial | Preço médio$15-$35/utilizador/mês | Funcionalidades comunsDeteção e resposta avançadas para dispositivos terminais, gestão de políticas, controlo de acesso baseado em funções, remediação automatizada e relatórios de conformidade. |
| Tipo de planoPlano empresarial avançado | Preço médio$40-$75/utilizador/mês | Funcionalidades comunsSuporte para vários sistemas operativos, integração avançada de informações sobre ameaças, conectores API e SIEM, reversão de ransomware e serviços de suporte premium. |
Perguntas frequentes sobre plataformas de proteção de dispositivos terminais
Eis algumas respostas a perguntas comuns sobre plataformas de proteção de dispositivos terminais:
Como lidam as plataformas de proteção de dispositivos terminais com ameaças de dia zero?
A maioria das plataformas de proteção de dispositivos terminais utiliza uma combinação de análise comportamental baseada em IA e informações sobre ameaças em tempo real para detetar e bloquear ameaças de dia zero. Em vez de dependerem apenas de assinaturas de malware conhecidas, estas plataformas monitorizam o comportamento dos processos, as ligações de rede e os ficheiros suspeitos em busca de sinais de ataques novos ou desconhecidos. Pode esperar que as ferramentas isolem ou revertam os sistemas se for detetada uma exploração de dia zero, reduzindo os potenciais danos mesmo antes de estar disponível uma correção.
As plataformas de proteção de dispositivos terminais podem suportar ambientes de trabalho remoto e híbrido?
Sim, a maioria das plataformas modernas de proteção de dispositivos terminais foi concebida para suportar modelos de trabalho remoto e híbrido. Procure consolas de gestão baseadas na nuvem e agentes que não necessitem de conectividade no local para atualizar continuamente as políticas e monitorizar os dispositivos. Isto significa que pode manter a visibilidade e o controlo sobre computadores de secretária, portáteis e dispositivos terminais móveis, independentemente do local a partir do qual os seus utilizadores trabalham.
Qual é a diferença entre EDR e XDR nas plataformas de proteção de dispositivos terminais?
A deteção e resposta em dispositivos terminais (EDR) centra-se na monitorização da atividade e na resposta a ameaças diretamente em dispositivos como portáteis e servidores. A deteção e resposta alargadas (XDR) vai mais longe, integrando telemetria de várias fontes, como dispositivos terminais, serviços na nuvem, correio eletrónico e sistemas de identidade. Com o XDR, a sua equipa pode descobrir padrões de ataque que atravessam plataformas ou os limites das ferramentas, facilitando a investigação e a contenção de ameaças multicamada.
Como posso saber se uma plataforma de proteção de dispositivos terminais cumpre os requisitos de conformidade?
Consulte a documentação do fornecedor para verificar a existência de relatórios de conformidade pré-criados, declarações de auditores ou certificações associadas a normas como HIPAA, PCI-DSS e NIST 800-171. A maioria das plataformas disponibiliza ferramentas de elaboração de relatórios que fazem a correspondência direta com os quadros regulamentares. É aconselhável solicitar informações sobre a residência dos dados na região relevante se a sua empresa operar em vários países ou tiver de cumprir leis locais rigorosas relativas aos dados.
As plataformas de proteção de dispositivos terminais afetam o desempenho dos dispositivos?
A maioria das plataformas de proteção de dispositivos terminais procura minimizar a utilização de recursos, mas algumas podem tornar mais lentos os dispositivos antigos durante a análise ou verificações intensivas. Deve testar os agentes no seu ambiente para perceber como afetam os tempos de arranque, o CPU, a memória e os fluxos de trabalho dos utilizadores. Se o desempenho for uma preocupação prioritária para a sua equipa, procure ferramentas com agentes leves ou agendas de verificação configuráveis.
As plataformas de proteção de dispositivos terminais podem integrar-se com o meu SIEM ou com as minhas ferramentas de gestão de TI?
Sim, muitas plataformas de proteção de dispositivos terminais disponibilizam APIs abertas e conectores integrados para ferramentas populares de SIEM e gestão de TI, como o Splunk, o Microsoft Sentinel e o ServiceNow. Convém analisar antecipadamente a documentação das APIs e os guias de integração disponíveis: integrações sólidas ajudam a automatizar fluxos de trabalho, consolidar alertas e reduzir o risco de não detetar incidentes importantes.