
Recensione SentinelOne: Pro, Contro, Caratteristiche e Prezzi Spiegati
SentinelOne si distingue per il rilevamento e la risposta automatizzati alle minacce, offrendo una protezione solida e facilità d’uso, ma potrebbe essere più adatto per le organizzazioni che danno priorità all’automazione rispetto al controllo manuale.

Recensiamo gli strumenti in modo indipendente e le commissioni ci aiutano a finanziare i nostri test. Consulta la nostra politica sulla trasparenza, la nostra metodologia, oppure suggerisci uno strumento.
SentinelOne is a cybersecurity software built around autonomous AI-driven endpoint detection and response, covering endpoints, cloud workloads, identity, and network data from a single platform. I'd consider it if your team needs threat detection and automated remediation without depending heavily on analyst intervention at every step. If you're weighing it against CrowdStrike, SentinelOne tends to be the stronger pick when you want faster autonomous response with less reliance on cloud connectivity and human triage—particularly useful for teams running lean security operations.
SentinelOne Evaluation Summary
4.7/5
- From $179.99/endpoint (billed annually)
- Free demo available
Perché fidarsi dei nostri consigli sui software
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Il nostro team testa e recensisce software dal 2012. In quanto leader tecnologici noi stessi, sappiamo quanto sia difficile — e importante — scegliere il software giusto.
Per questa guida, abbiamo valutato gli strumenti attraverso test praticie ricerche indipendenti, assegnando un punteggio agli strumenti in base ai nostri criteri di selezione.
Le nostre recensioni riflettono il nostro giudizio editoriale umano, non un discorso di vendita.
Revisori esperti:
- Paulo Gardini MiguelDirettore tecnico
 Tim FisherVP dell'IA
 Gabriel RosasTech Lead e architetto software
 Christhian GruhnTech Lead e architetto della piattaforma

SentinelOne Overview
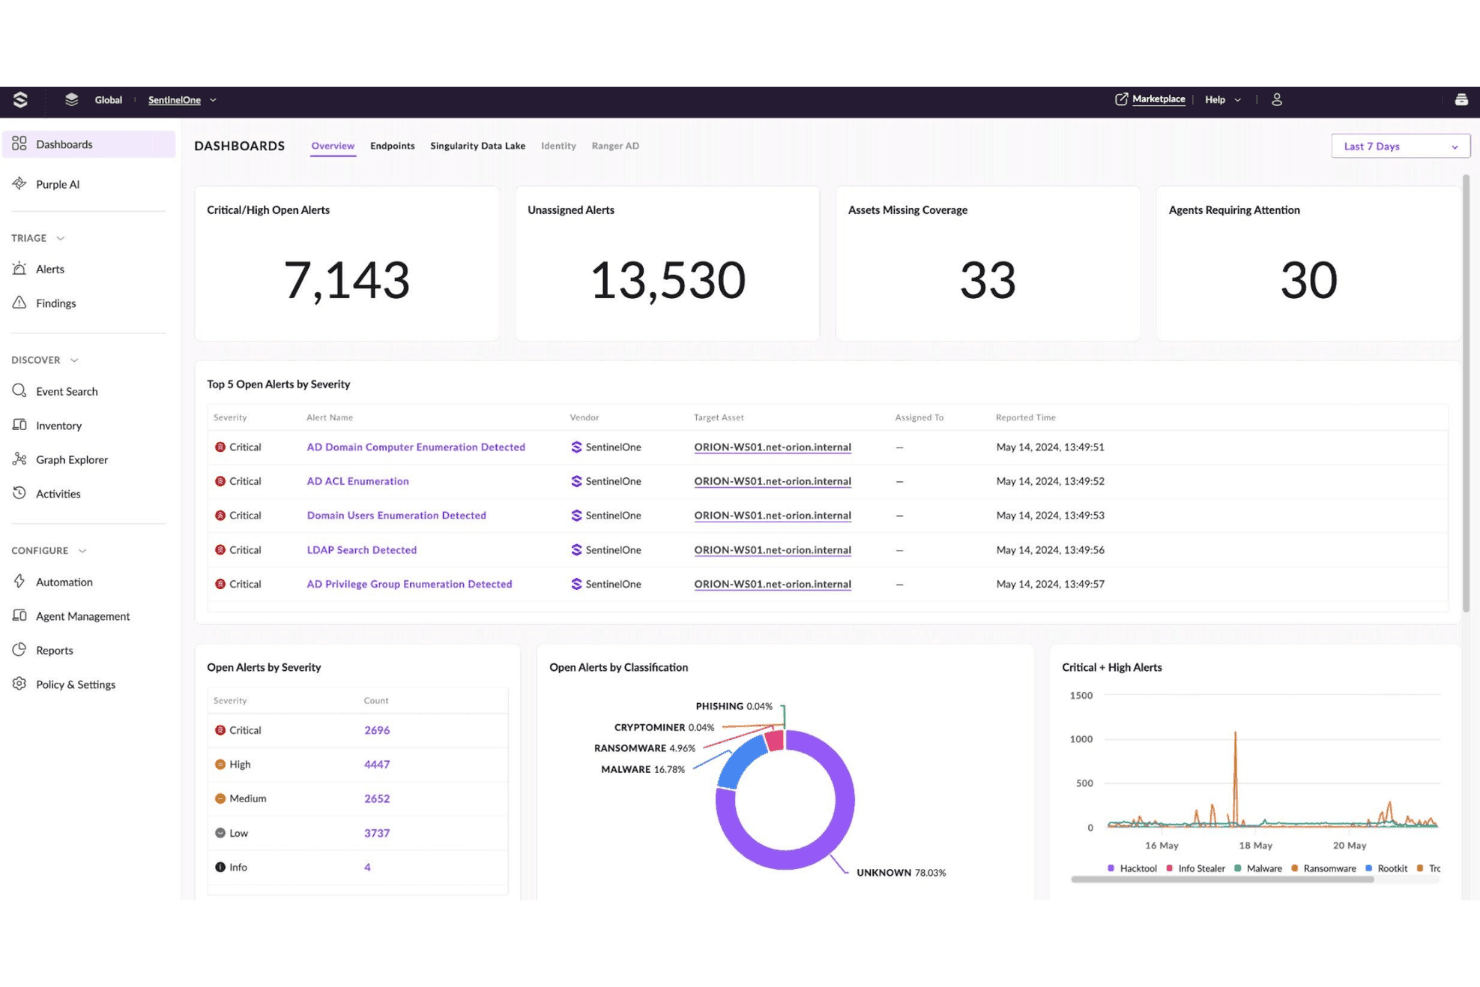
In my experience, SentinelOne delivers as an endpoint detection and response (EDR) solution, with a clean interface and robust functionality. Its AI-driven automation and broad integration options set it apart for teams seeking hands-off protection, though pricing can be higher than some alternatives and advanced manual controls are less granular. I think it's a strong choice for organizations prioritizing automation, endpoint security, and rapid incident response—especially in environments with limited security staff or high endpoint diversity. If you're judging by ease of use and automation, SentinelOne is tough to beat.
Pros
- AI-driven detection stops advanced threats quickly
- Automated rollback restores endpoints after ransomware attacks
- Minimal system impact on user devices
Cons
- Higher cost than many competitors
- Occasional false positives require manual review
- Console outages reported during updates
Is SentinelOne Right For Your Needs?
Who Would be a Good Fit for SentinelOne?
SentinelOne is a strong choice for organizations that need autonomous threat detection, rapid response, and scalable protection across diverse endpoints. I think it's especially well-suited for industries with strict compliance needs, companies with distributed workforces, and teams with limited security staff. SentinelOne's AI-driven automation, ransomware rollback, and minimal device impact make it a practical fit for environments where speed and reliability are essential. User reviews consistently highlight the platform's machine learning capabilities and response capabilities as key differentiators for mid-to-large security operations.
- Healthcare ProvidersSentinelOne's automated response and compliance features help protect sensitive patient data.
- Financial ServicesReal-time threat detection supports strict regulatory requirements and high-value assets.
- Remote WorkforcesCloud-based management and low device impact suit distributed teams.
- Education InstitutionsAutomated rollback and easy deployment help protect large, diverse device fleets.
- IT DepartmentsCentralized console and broad OS support simplify endpoint management.
- Mid-Size EnterprisesScalable licensing and automation reduce the need for large security teams.
Who Would be a Bad Fit for SentinelOne?
SentinelOne may not be the best fit for organizations with tight budgets, highly specialized manual security workflows, or those needing deep integration with legacy systems. If your team relies on granular manual controls or has minimal endpoints to protect, you might find SentinelOne's automation and pricing less appealing compared to other EDR solutions.
- Small NonprofitsHigher pricing and advanced features may exceed basic network security needs.
- Legacy System OperatorsLimited support for outdated OS versions can hinder deployment.
- Highly Regulated GovernmentSome agencies require on-premises solutions SentinelOne doesn't offer.
- Micro StartupsCost and feature set may be overkill for very small teams.
- Manual-First SOC TeamsAutomation focus limits deep manual investigation and tuning.
- Retail Chains With POSPOS-specific security needs may require more specialized solutions.
La Nostra Metodologia di Recensione
Come Testiamo e Valutiamo gli Strumenti
Abbiamo trascorso anni a costruire, perfezionare e migliorare il nostro sistema di testing e valutazione del software. Il nostro schema è progettato per cogliere le sfumature della selezione software e cosa rende efficace uno strumento, focalizzandosi sugli aspetti critici del processo decisionale.
Di seguito, puoi vedere esattamente come funziona il nostro testing e punteggio su sette criteri. Ci permette di offrire una valutazione imparziale del software basata su funzionalità principali, caratteristiche distintive, facilità d’uso, onboarding, assistenza clienti, integrazioni, recensioni dei clienti e rapporto qualità-prezzo.
Funzionalità Principali (25% del punteggio finale)
Il punto di partenza della nostra valutazione è sempre la funzionalità principale dello strumento. Ha le funzioni e caratteristiche base che ci si aspetta? Alcune di queste caratteristiche sono limitate ai piani tariffari superiori? Fondamentalmente, ci aspettiamo che uno strumento regga il confronto rispetto alle capacità di base dei concorrenti.
Caratteristiche Distintive (25% del punteggio finale)
Successivamente, valutiamo le caratteristiche distintive e non comuni che vanno oltre la funzionalità base tipicamente trovata negli strumenti di questa categoria. Un punteggio alto riflette funzionalità specializzate o uniche che rendono il prodotto più veloce, efficiente o offrono ulteriore valore all’utente.
Valutiamo inoltre quanto sia semplice integrare altri strumenti tipicamente utilizzati nell’infrastruttura tecnologica per espandere la funzionalità e l’utilità del software. Gli strumenti che offrono numerose integrazioni native, connessioni di terze parti e accesso API per creare integrazioni personalizzate ottengono i punteggi migliori.
Facilità d’Uso (10% del punteggio finale)
Consideriamo quanto sia rapido e semplice svolgere i compiti definiti nella funzionalità principale utilizzando lo strumento. Il software con punteggio alto è ben progettato, intuitivo da usare, offre app mobili, fornisce modelli e rende semplici attività relativamente complesse.
Onboarding (10% del punteggio finale)
Sappiamo quanto sia importante l’adozione rapida da parte del team per una nuova piattaforma, quindi valutiamo quanto sia facile imparare e utilizzare uno strumento con formazione minima. Valutiamo quanto velocemente un membro del team possa iniziare a usare lo strumento anche senza esperienza. Soluzioni con punteggio alto indicano che sono richiesti pochi o nessun supporto.
Assistenza Clienti (10% del punteggio finale)
Esaminiamo quanto sia veloce e facile ricevere assistenza e risolvere problemi tramite telefono, live chat o knowledge base. Gli strumenti e le aziende che garantiscono supporto in tempo reale ottengono il miglior punteggio, mentre i chatbot ottengono il peggiore.
Recensioni dei Clienti (10% del punteggio finale)
Oltre ai nostri test e valutazioni, prendiamo in considerazione il net promoter score dei clienti attuali e passati. Valutiamo la probabilità che, data la scelta, selezionerebbero nuovamente lo strumento per la funzionalità principale. Un software con punteggio alto riflette un alto net promoter score da parte dei clienti attuali o passati.
Rapporto Qualità-Prezzo (10% del punteggio finale)
Infine, considerando tutti gli altri criteri, analizziamo il prezzo medio dei piani base rispetto alle funzionalità principali e consideriamo il valore degli altri criteri di valutazione. Il software che offre di più a meno otterrà un punteggio più alto.
Core Features
Autonomous Threat Detection
SentinelOne uses AI to identify and stop threats in real time without human intervention. This reduces response times and helps streamline vulnerability management.
Ransomware Rollback
The platform can automatically restore files and system states after a ransomware attack. This rollback feature minimizes downtime and data loss for affected endpoints.
Behavioral AI Engine
SentinelOne uses machine learning to analyze device and user behavior and spot suspicious activity. It adapts to new threats, catching malware that signature-based tools might miss.
Automated Remediation
When a threat is detected, SentinelOne can isolate, kill, and remove malicious files automatically. This limits the impact of attacks and reduces manual workload for IT teams.
Centralized Management Console
Admins manage all endpoints and policies from a single, cloud-based dashboard. This makes it easy to monitor, configure, and respond across large environments.
Device Control
SentinelOne lets you set policies for USB and peripheral device usage. This helps prevent data exfiltration and blocks unauthorized hardware access.
Ease of Use
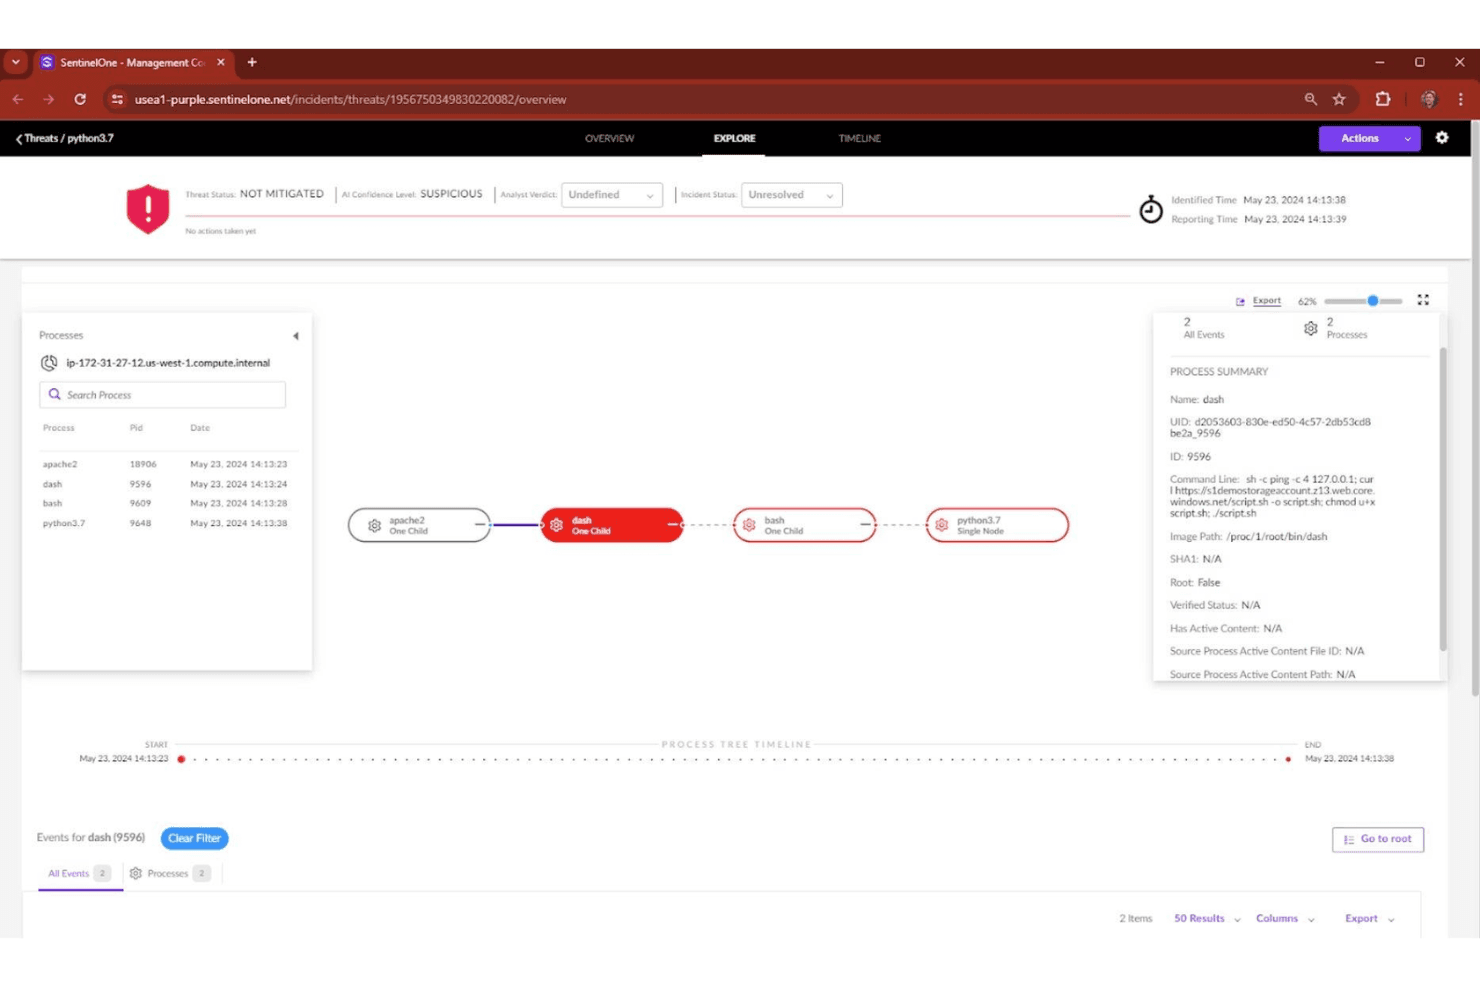
SentinelOne is widely praised for its intuitive interface and straightforward deployment, making it accessible even for teams without deep security expertise. The centralized console simplifies monitoring and policy management across many endpoints. Automated responses and clear visualizations reduce manual effort and speed up investigations. I think most users will find the platform easy to navigate, with helpful documentation and responsive support that further smooth out the onboarding process.
Integrations
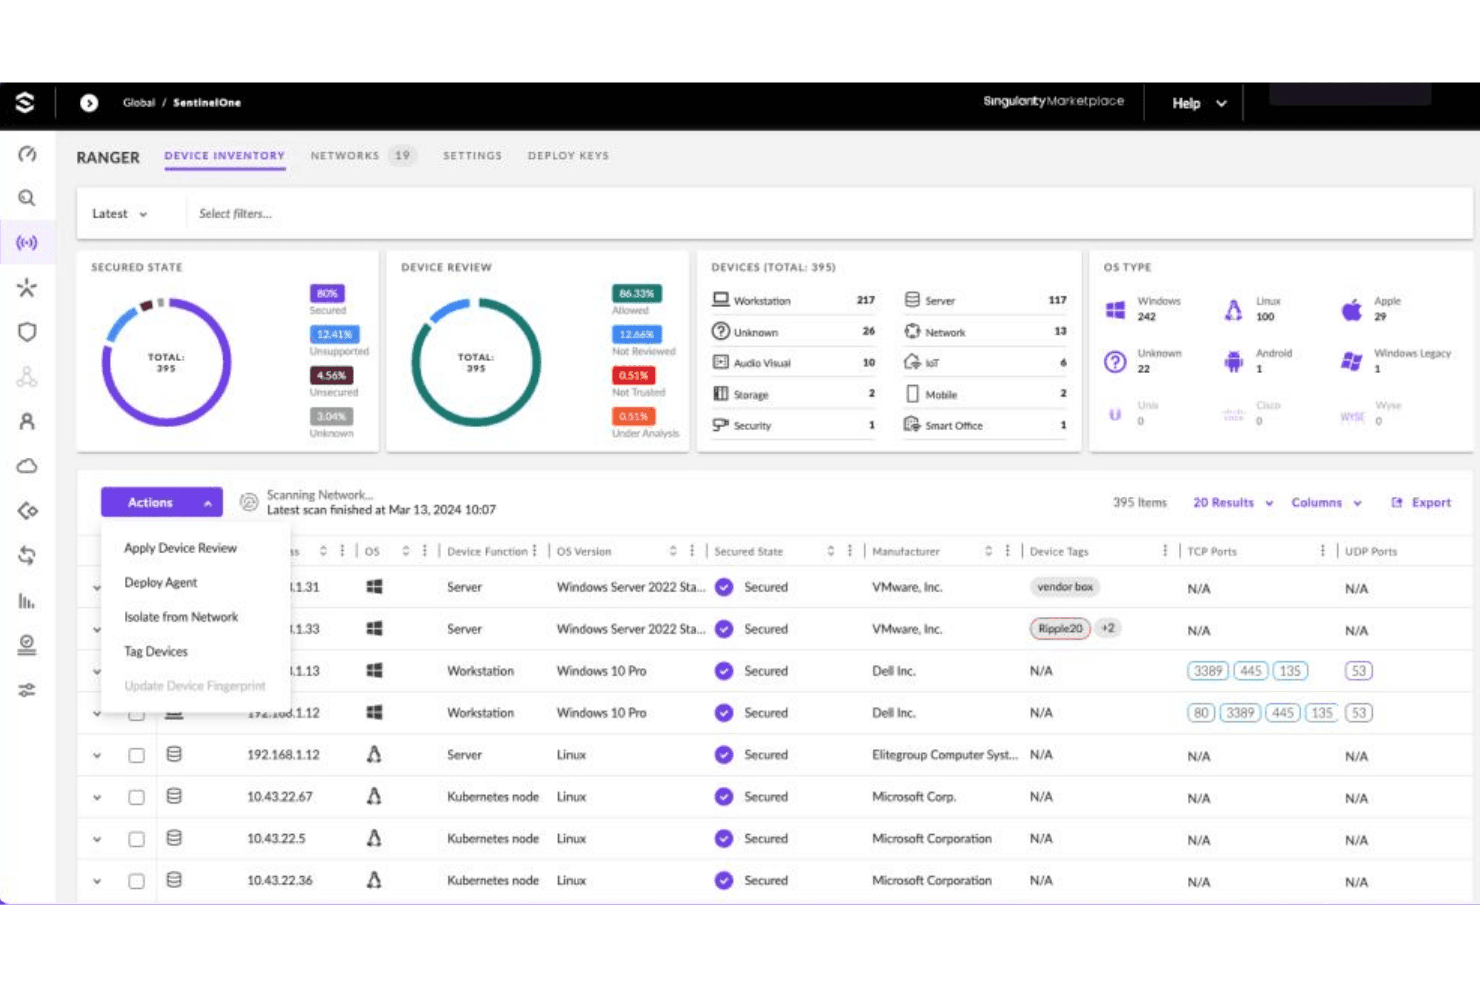
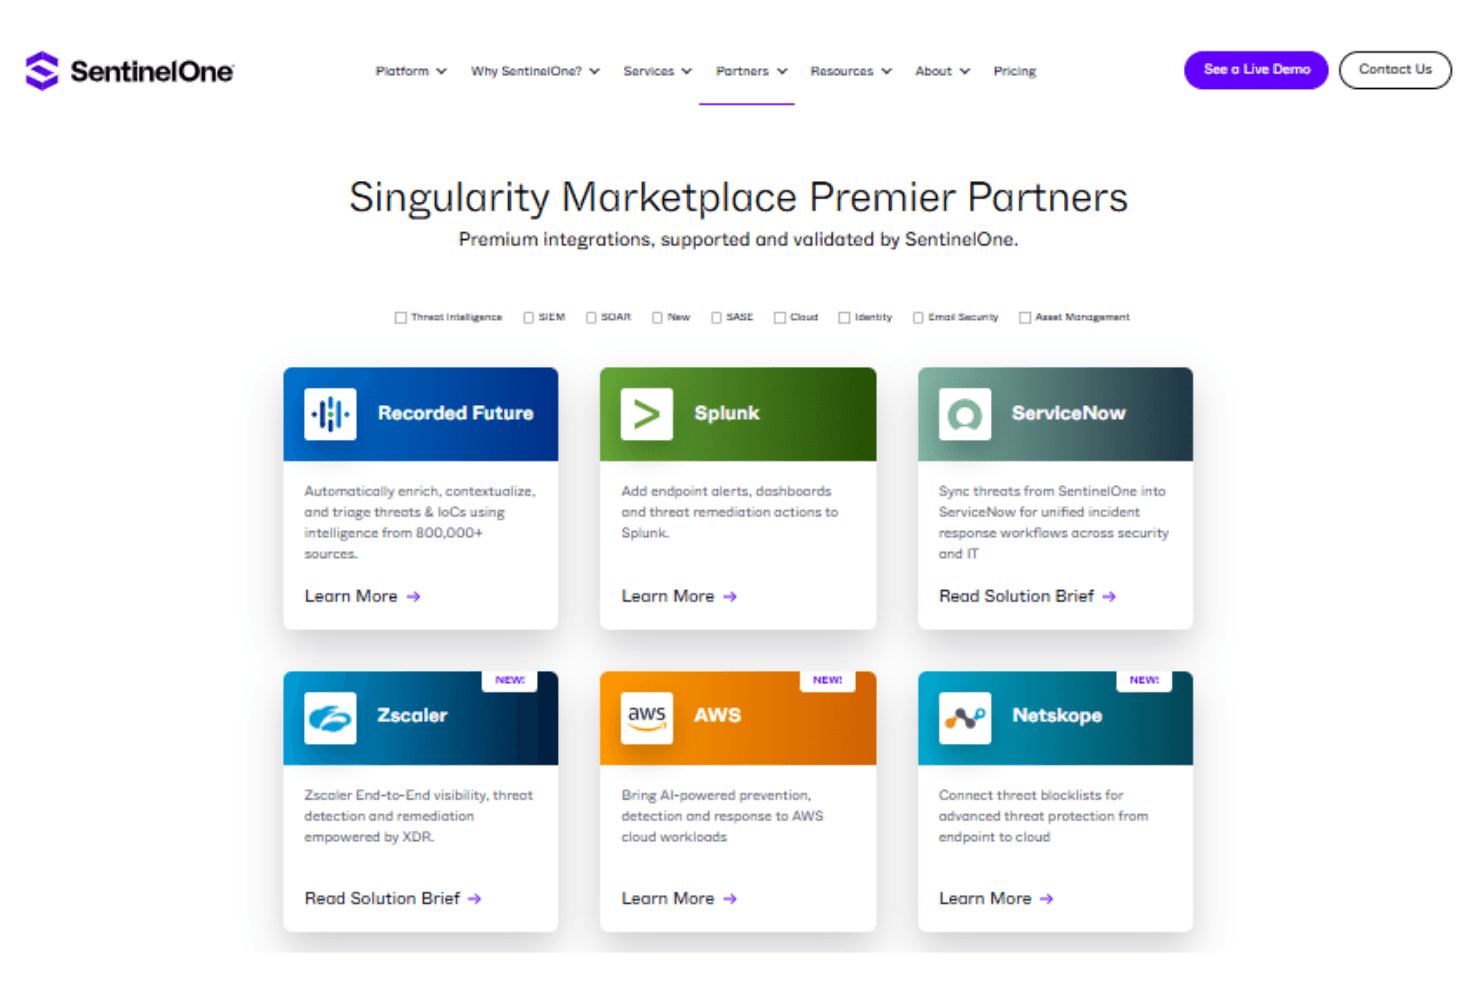
SentinelOne integrates with Splunk, Zscaler, AWS, Netskope, Okta, and IBM Security, among others.
SentinelOne also offers a robust API and connects with third-party integration tools through its Singularity Marketplace.
SentinelOne Specs
- 2-Factor Authentication: Yes
- Access Management: Yes
- Anti-Virus: Yes
- API: Yes
- Audit Management: Yes
- Audit Trail: Yes
- Batch Permissions & Access: Yes
- Compliance Tracking: Yes
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- DDoS Protection: Yes
- External Integrations: Yes
- File Sharing: Yes
- File Transfer: Yes
- Firewall: Yes
- Incident Management: Yes
- Malware Protection: Yes
- Multi-User: Yes
- Notifications: Yes
- Password & Access Management: Yes
- Policy Management: Yes
- Real-time Alerts: Yes
- Report & Compliance: Yes
- Risk Assessment: Yes
- Security Migration: Yes
- Threat Detection: Yes
- Workflow Management: Yes


