The cybersecurity experts you follow shape how you think about threats, defenses, and risk. With so much noise online, finding voices that offer real, actionable insight matters. I've put together this list to help you cut through the clutter and connect with practitioners who actually move the needle on security strategy.
Top 17 Cybersecurity Experts
Below are the profiles of the top cybersecurity experts, covering who they are and the impact they've made in this space.
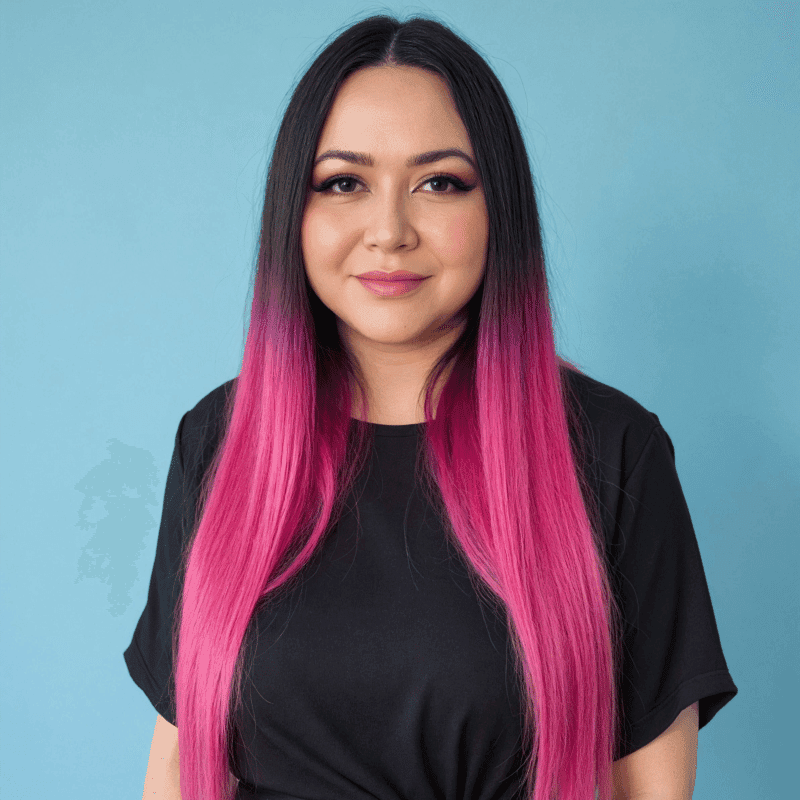
Katie Moussouris
Founder & CEO at Luta Security
Kirkland, United States
Focus area:
#Vulnerability disclosure#Bug bounty programs#Security policy#AI security
Katie Moussouris is founder and CEO of Luta Security, a cybersecurity firm focused on vulnerability disclosure, bug bounty strategy, and coordinated programs for organizations worldwide.
Moussouris helped develop modern vulnerability disclosure and bug bounty programs through her work at Microsoft, HackerOne, and public-sector initiatives such as Hack the Pentagon. Her work links vulnerability management with incentives, policy, and security costs.
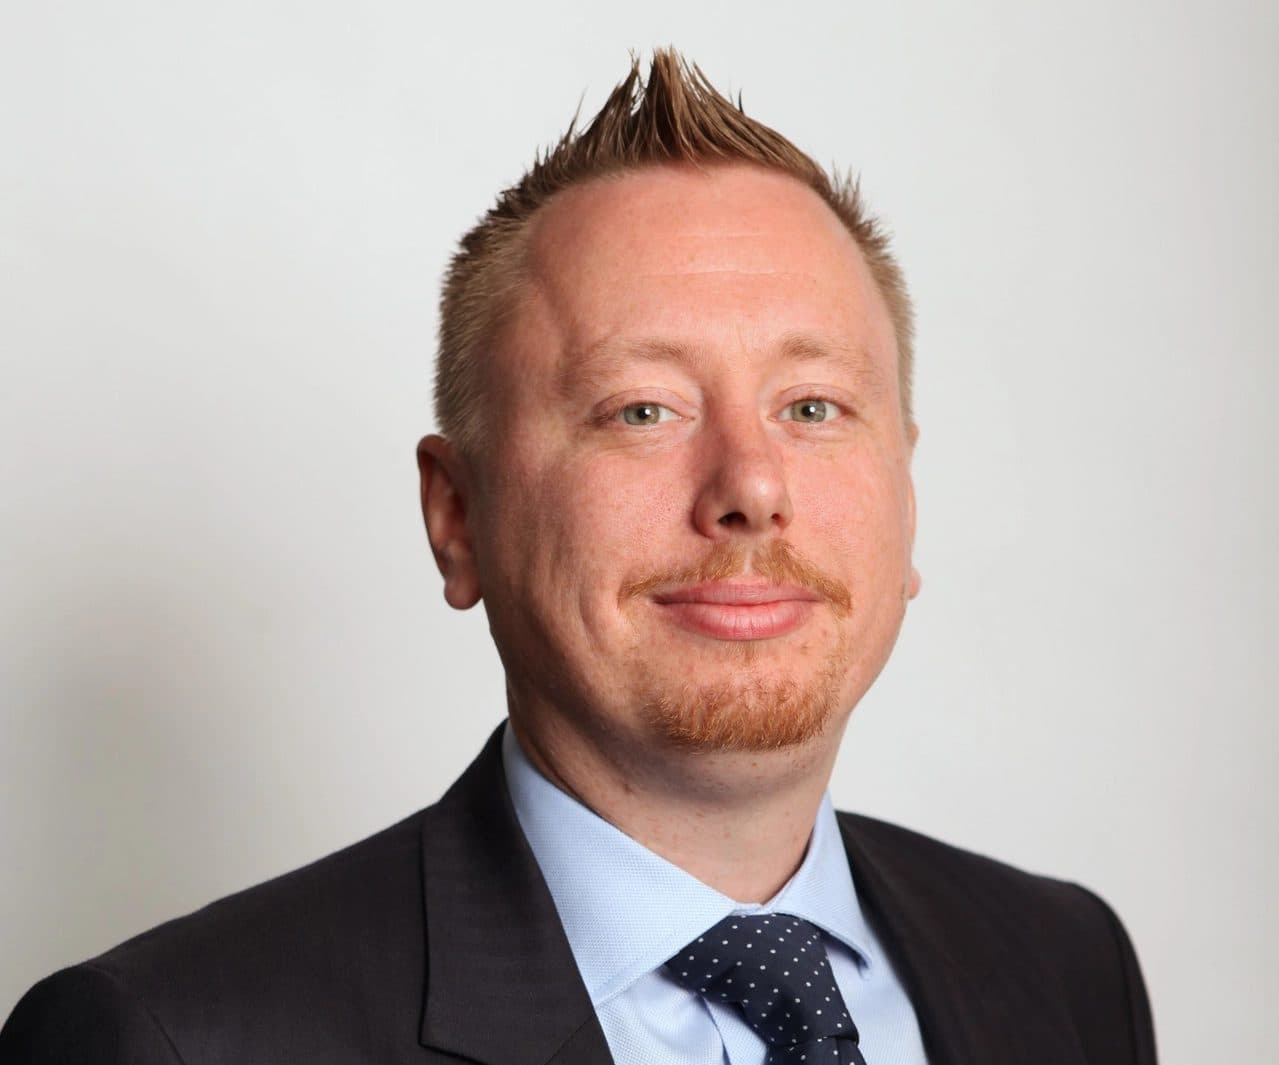
Ollie Whitehouse
CTO at National Cyber Security Centre
United Kingdom
Focus area:
#National cybersecurity#Security technology#Cyber resilience#Emerging threats
Ollie Whitehouse is Chief Technology Officer of the UK National Cyber Security Centre, following more than 27 years across cybersecurity research, advisory work, and private-sector leadership.
At the NCSC, Whitehouse helps maintain the organization’s role as the UK’s National Technical Authority for cybersecurity. His remit spans national resilience, emerging technologies, security research, and developing the technical capabilities needed to address future threats.
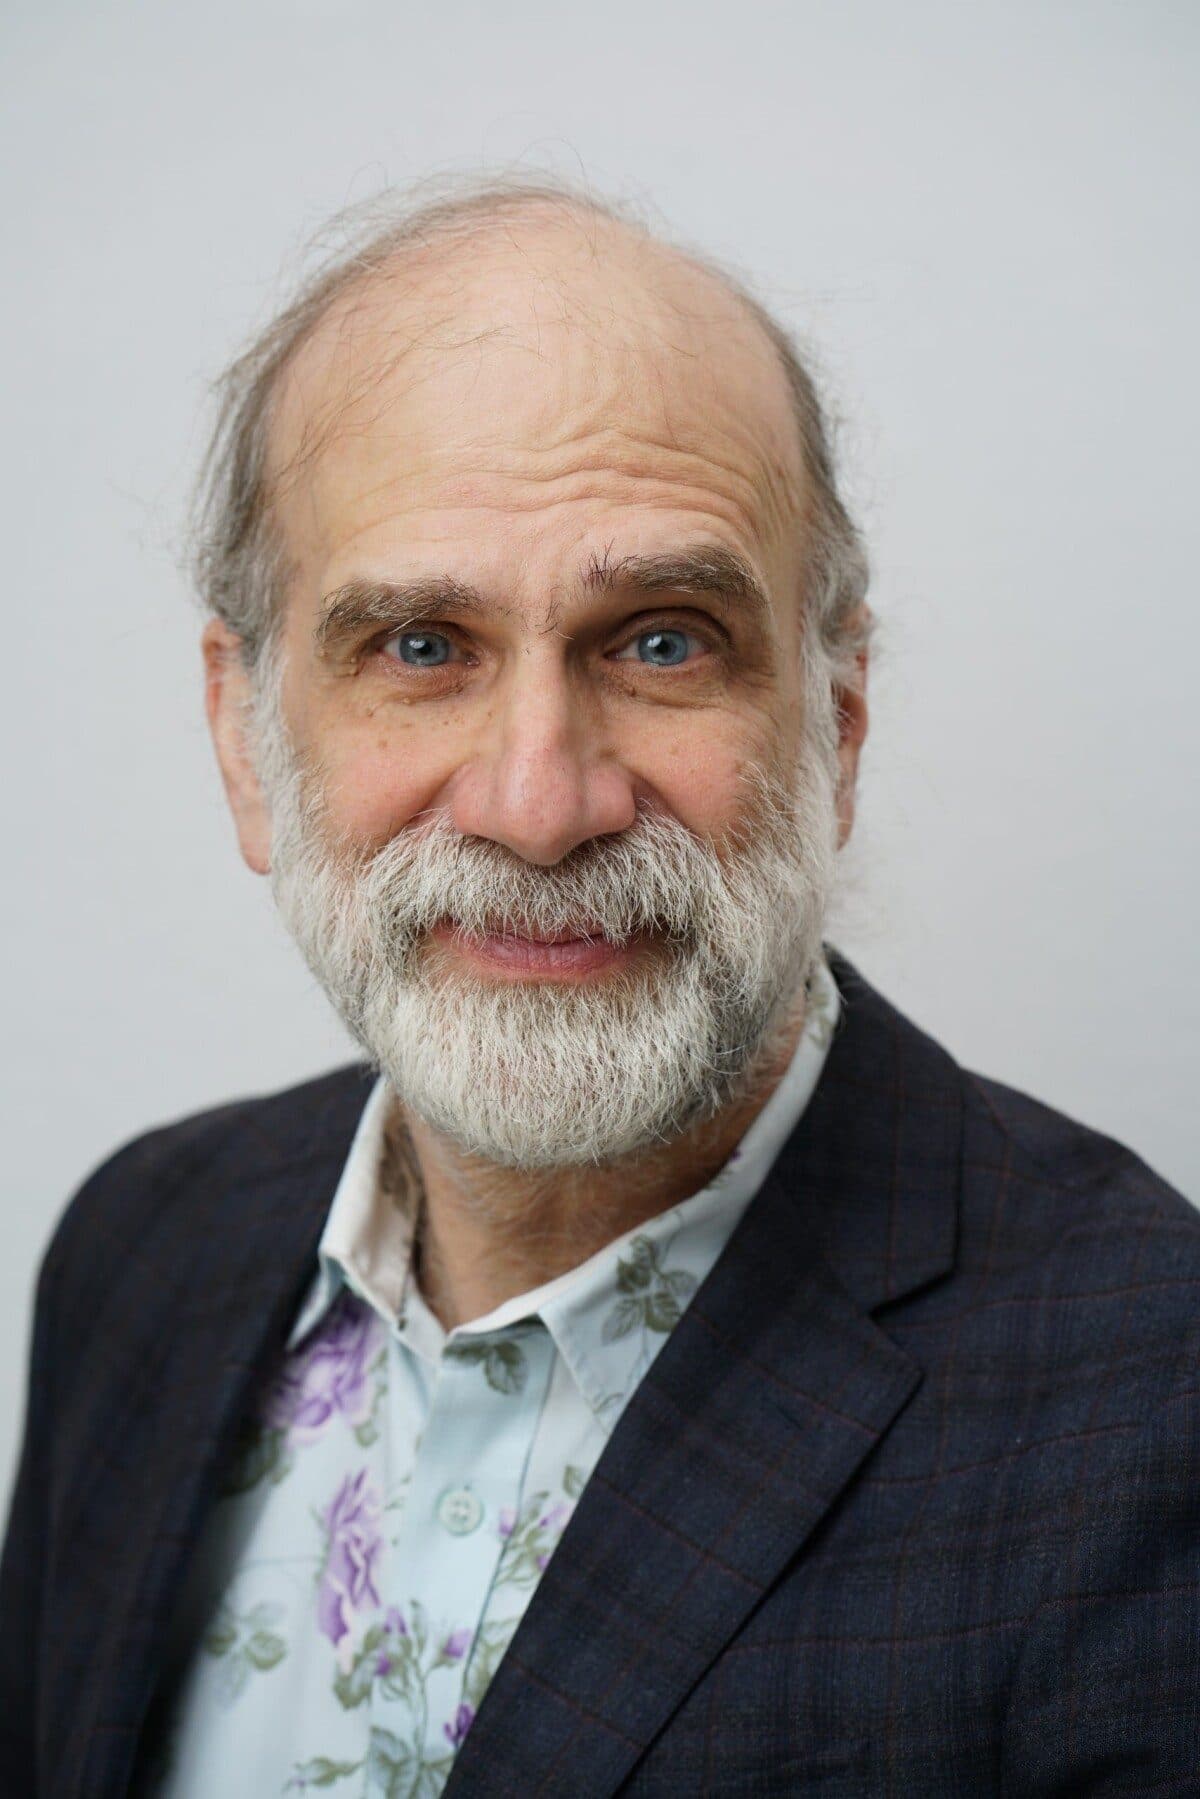
Bruce Schneier
Security Technologist & Author
Focus area:
#Security engineering#Security policy#Cryptography#AI security#Public-interest technology
Connect with Bruce:
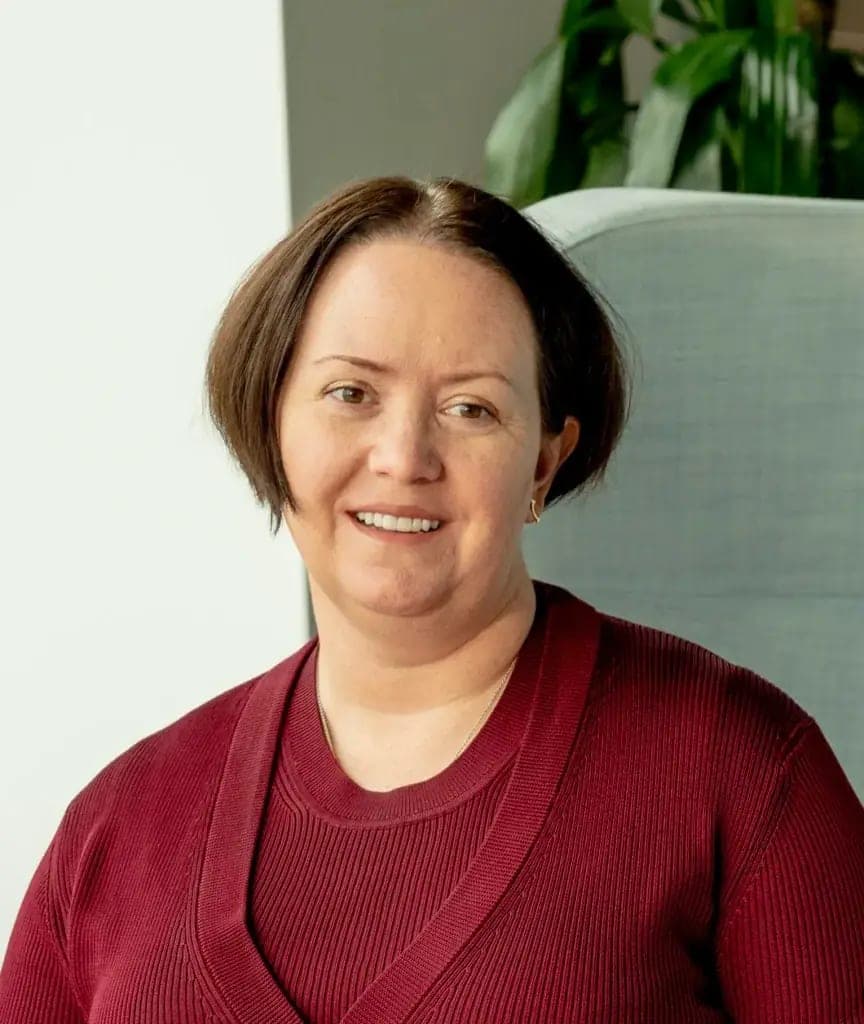
Heather Adkins
VP, Security Engineering at Google
San Francisco, United States
Focus area:
#Security engineering#Incident response#Cyber resilience#Secure systems
Connect with Heather:
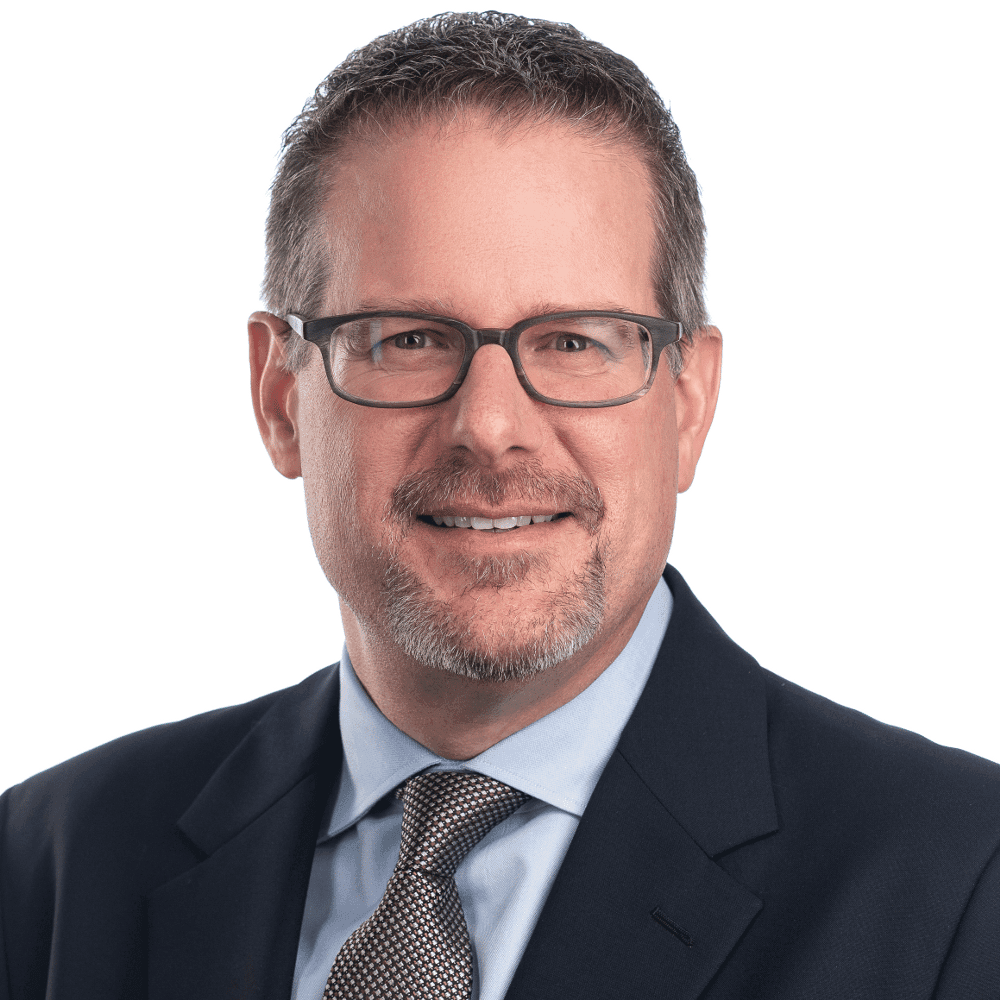
Chris Wysopal
Founder & Chief Security Evangelist at Veracode
Massachusetts, United States
Focus area:
#Application security#Software security#Vulnerability research#Responsible disclosure
Chris Wysopal is a Veracode founder and Chief Security Evangelist who began as a L0pht vulnerability researcher and has spent decades advancing software security and vulnerability disclosure.
From exposing insecure software at L0pht to co-founding Veracode, Wysopal has pushed application security toward measurable engineering practice. His work includes responsible disclosure, security testing, vulnerability research, and advocating for stronger software throughout the development lifecycle.
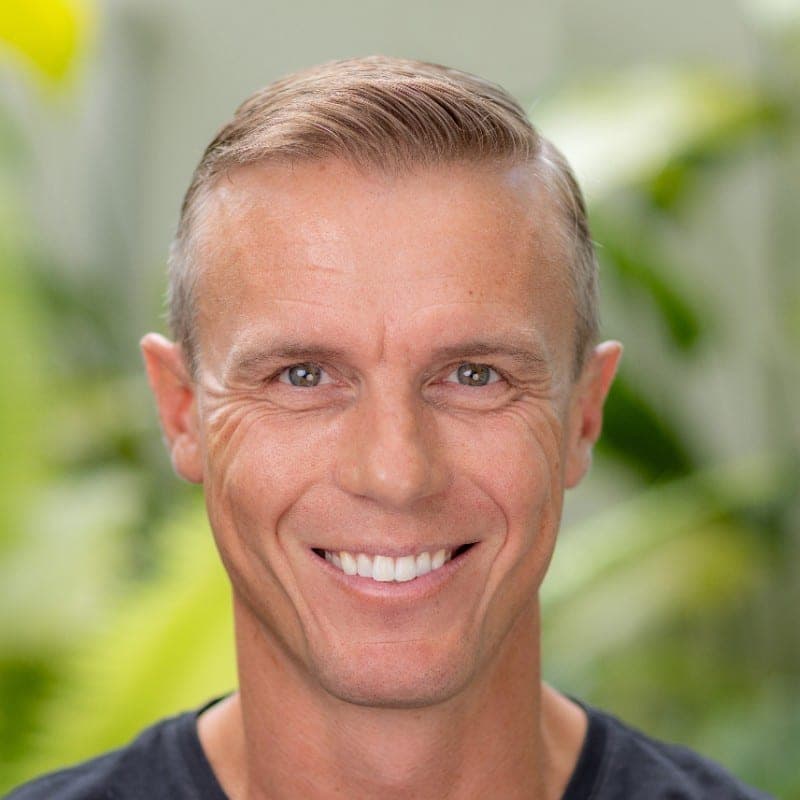
Troy Hunt
Founder & CEO of Have I Been Pwned
Gold Coast, Australia
Focus area:
#Data breaches#Web security#Security education#Identity security
Troy Hunt is the founder and CEO of Have I Been Pwned, a widely used breach-notification service, and a security educator, author, Microsoft Regional Director, and MVP based in Australia.
Through Have I Been Pwned, Hunt turns breach data into a practical resource for individuals and security teams. His writing and teaching also cover web security, authentication, privacy, data exposure, and the lessons organizations can draw from real-world compromises.
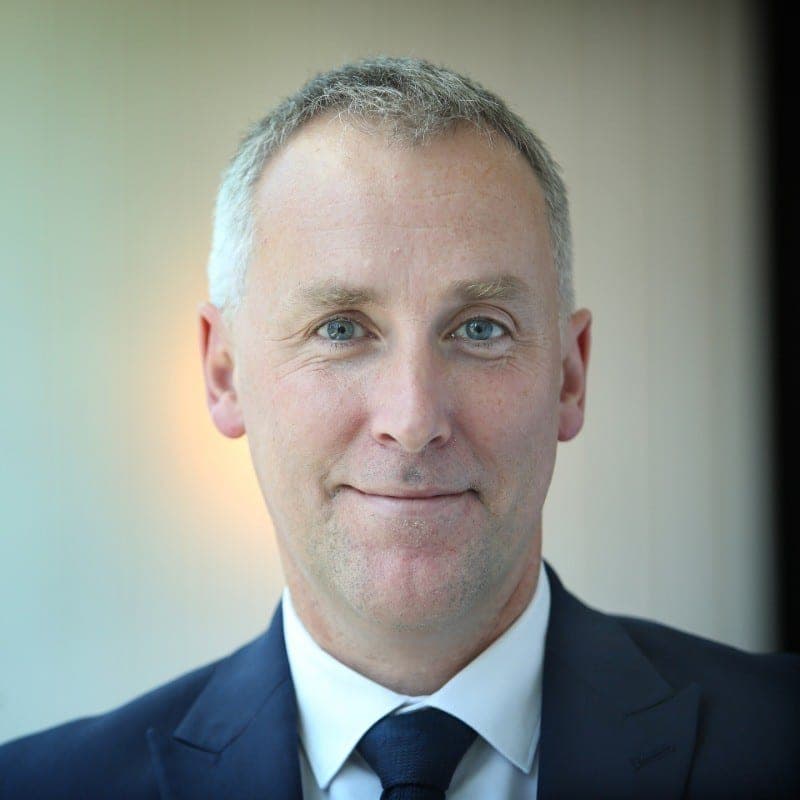
Ciaran Martin
Cybersecurity Policy Expert & Educator
Shipton-under-Wychwood, United Kingdom
Focus area:
#Cybersecurity policy#National cyber strategy#Cyber resilience#Technology policy
Ciaran Martin is an Oxford professor of practice and founding chief executive of the UK's National Cyber Security Centre, where he helped reshape the country's cybersecurity strategy and policy.
Martin led the creation of the NCSC and helped move UK cybersecurity toward a more interventionist, system-level approach. At Oxford, his work incldes cyber strategy, technology policy, crisis management, public administration, and the practical relationship between government and digital security.
Connect with Ciaran:
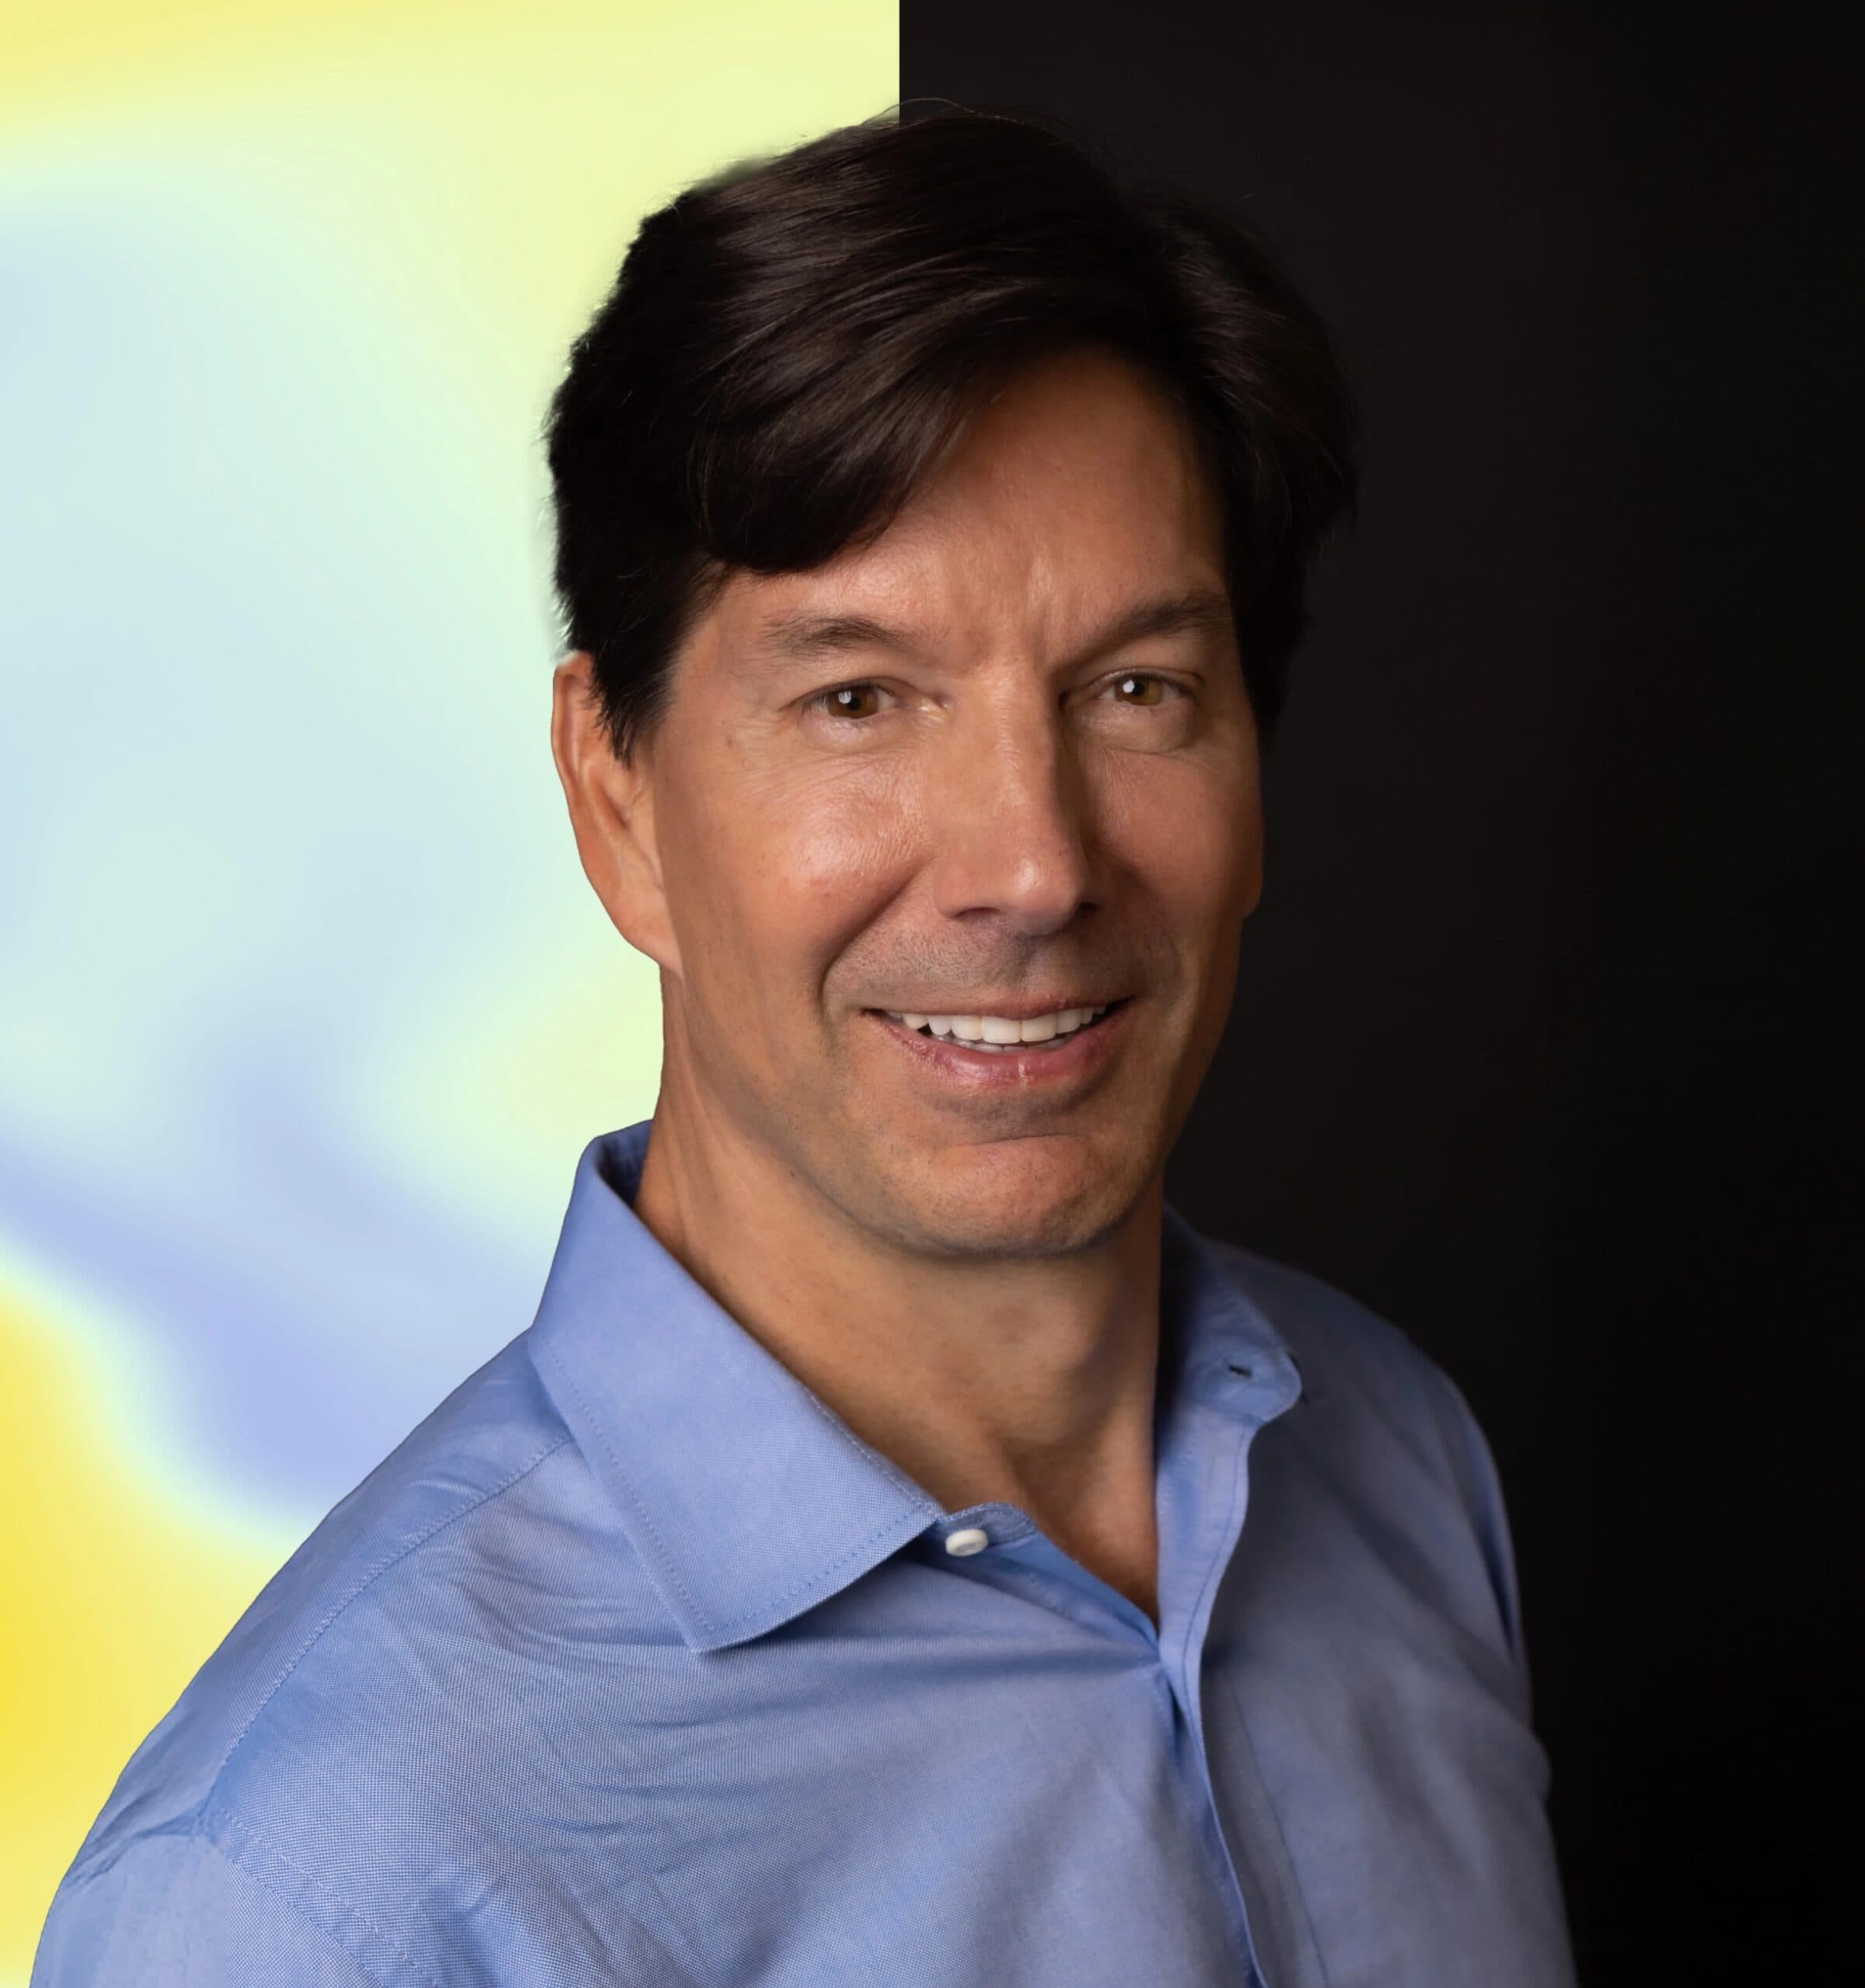
Mark Russinovich
CTO, Deputy CISO & Technical Fellow at Microsoft Azure
Bellevue, United States
Focus area:
#Cloud security#Azure architecture#Security engineering#Systems security#AI infrastructure
Mark Russinovich is CTO, Deputy CISO, and Technical Fellow for Microsoft Azure. He leads technical strategy and helps manage security risk across Azure, operating systems, and engineering.
Russinovich combines deep systems expertise with responsibility for cloud architecture and security risk. His work on Microsoft’s Secure Future Initiative emphasizes durable engineering controls, secure-by-design practices, threat modeling, and security across hyperscale cloud and AI infrastructure.
Connect with Mark:
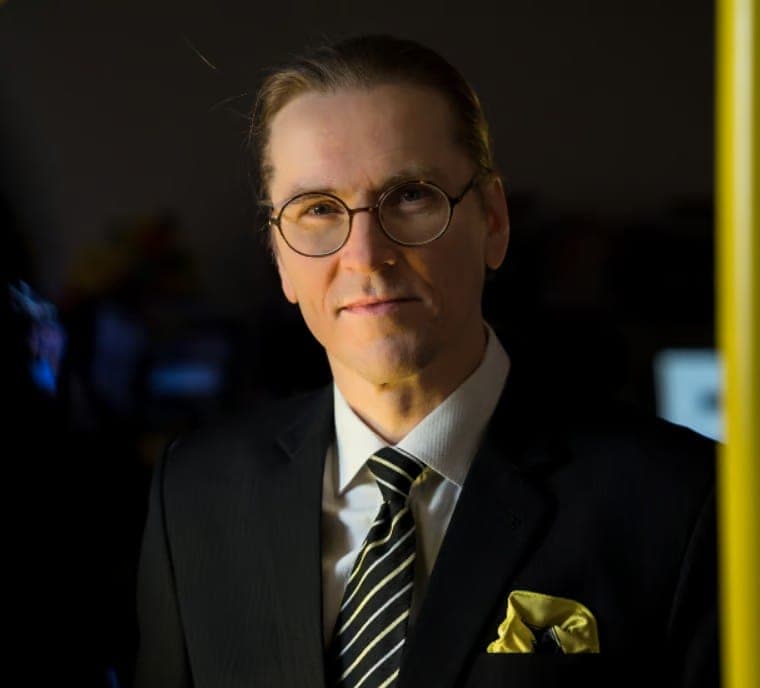
Mikko Hyppönen
Chief Research Officer at Sensofusion
Helsinki, Finland
Focus area:
#Threat research#Malware#Cybercrime#Counter-drone security#Security education
Mikko Hyppönen is Chief Research Officer at Sensofusion, a security researcher and author whose career includes malware analysis, cybercrime, privacy, and now counter-drone technology and defense.
After more than three decades fighting malware, Hyppönen moved into counter-drone research, applying the same adversarial mindset to unmanned systems. His broader work has made complex threats—from viruses and ransomware to online crime and AI—accessible to technical and general audiences.
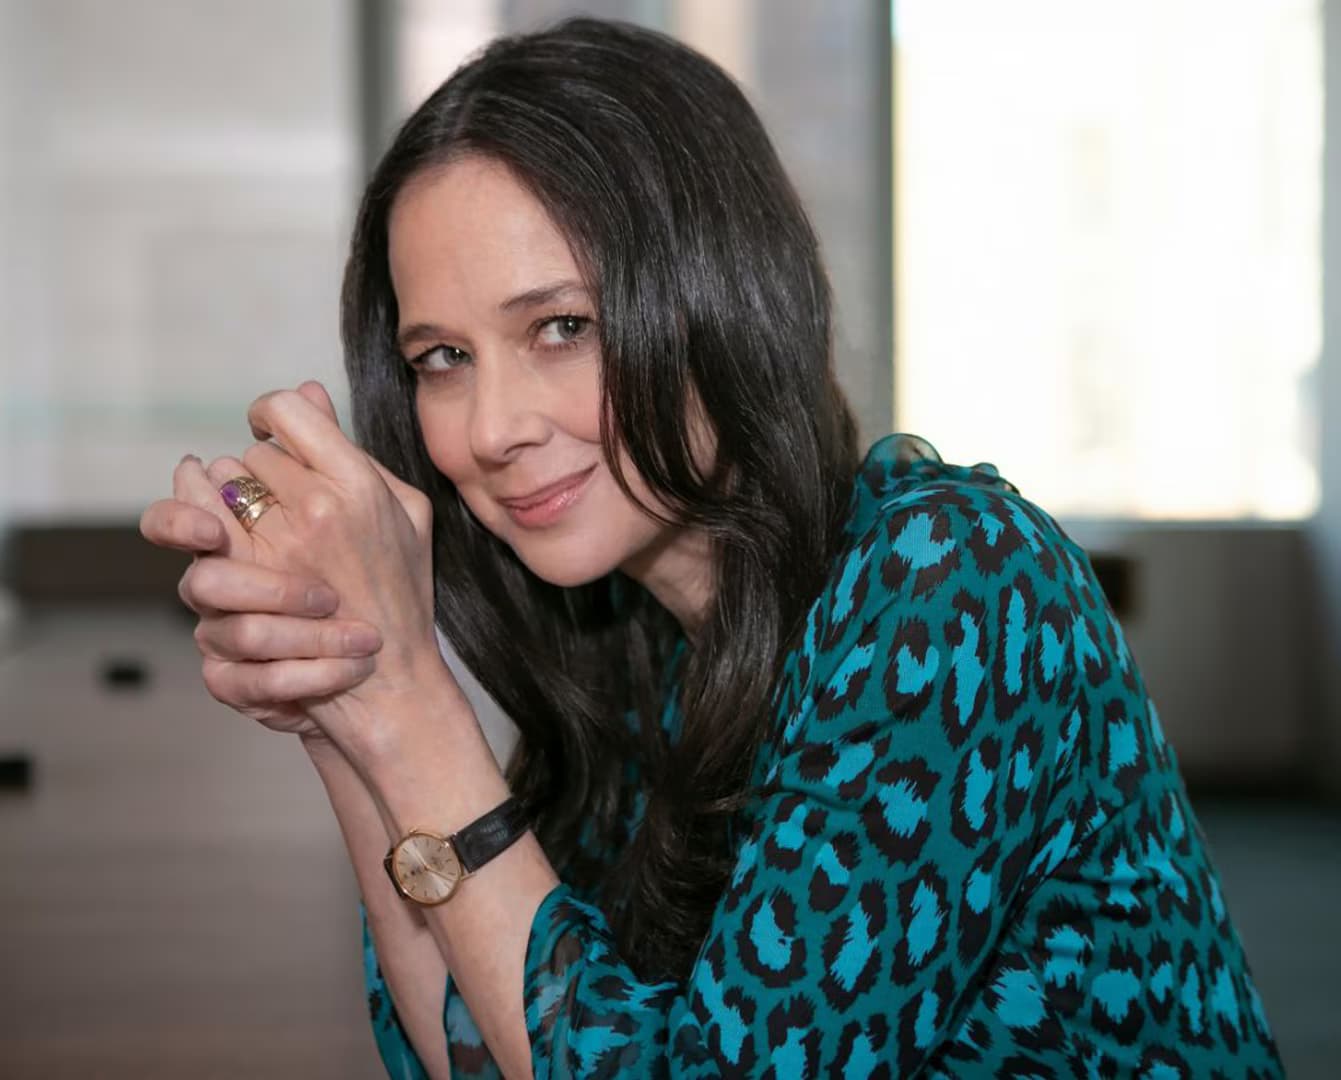
Jen Easterly
CEO at RSAC
United States
Focus area:
#Cyber resilience#Security leadership#Secure software#Public-private collaboration
Jen Easterly is CEO of RSAC and former director of the U.S. Cybersecurity and Infrastructure Security Agency. She has leadership experience across government, intelligence, finance, and security.
Easterly’s work focuses on systemic cyber risk, infrastructure resilience, secure software, and collaboration between government and industry. At RSAC, she leads a global cybersecurity platform spanning its conference, professional community, education, innovation, and AI-security initiatives.
Connect with Jen:
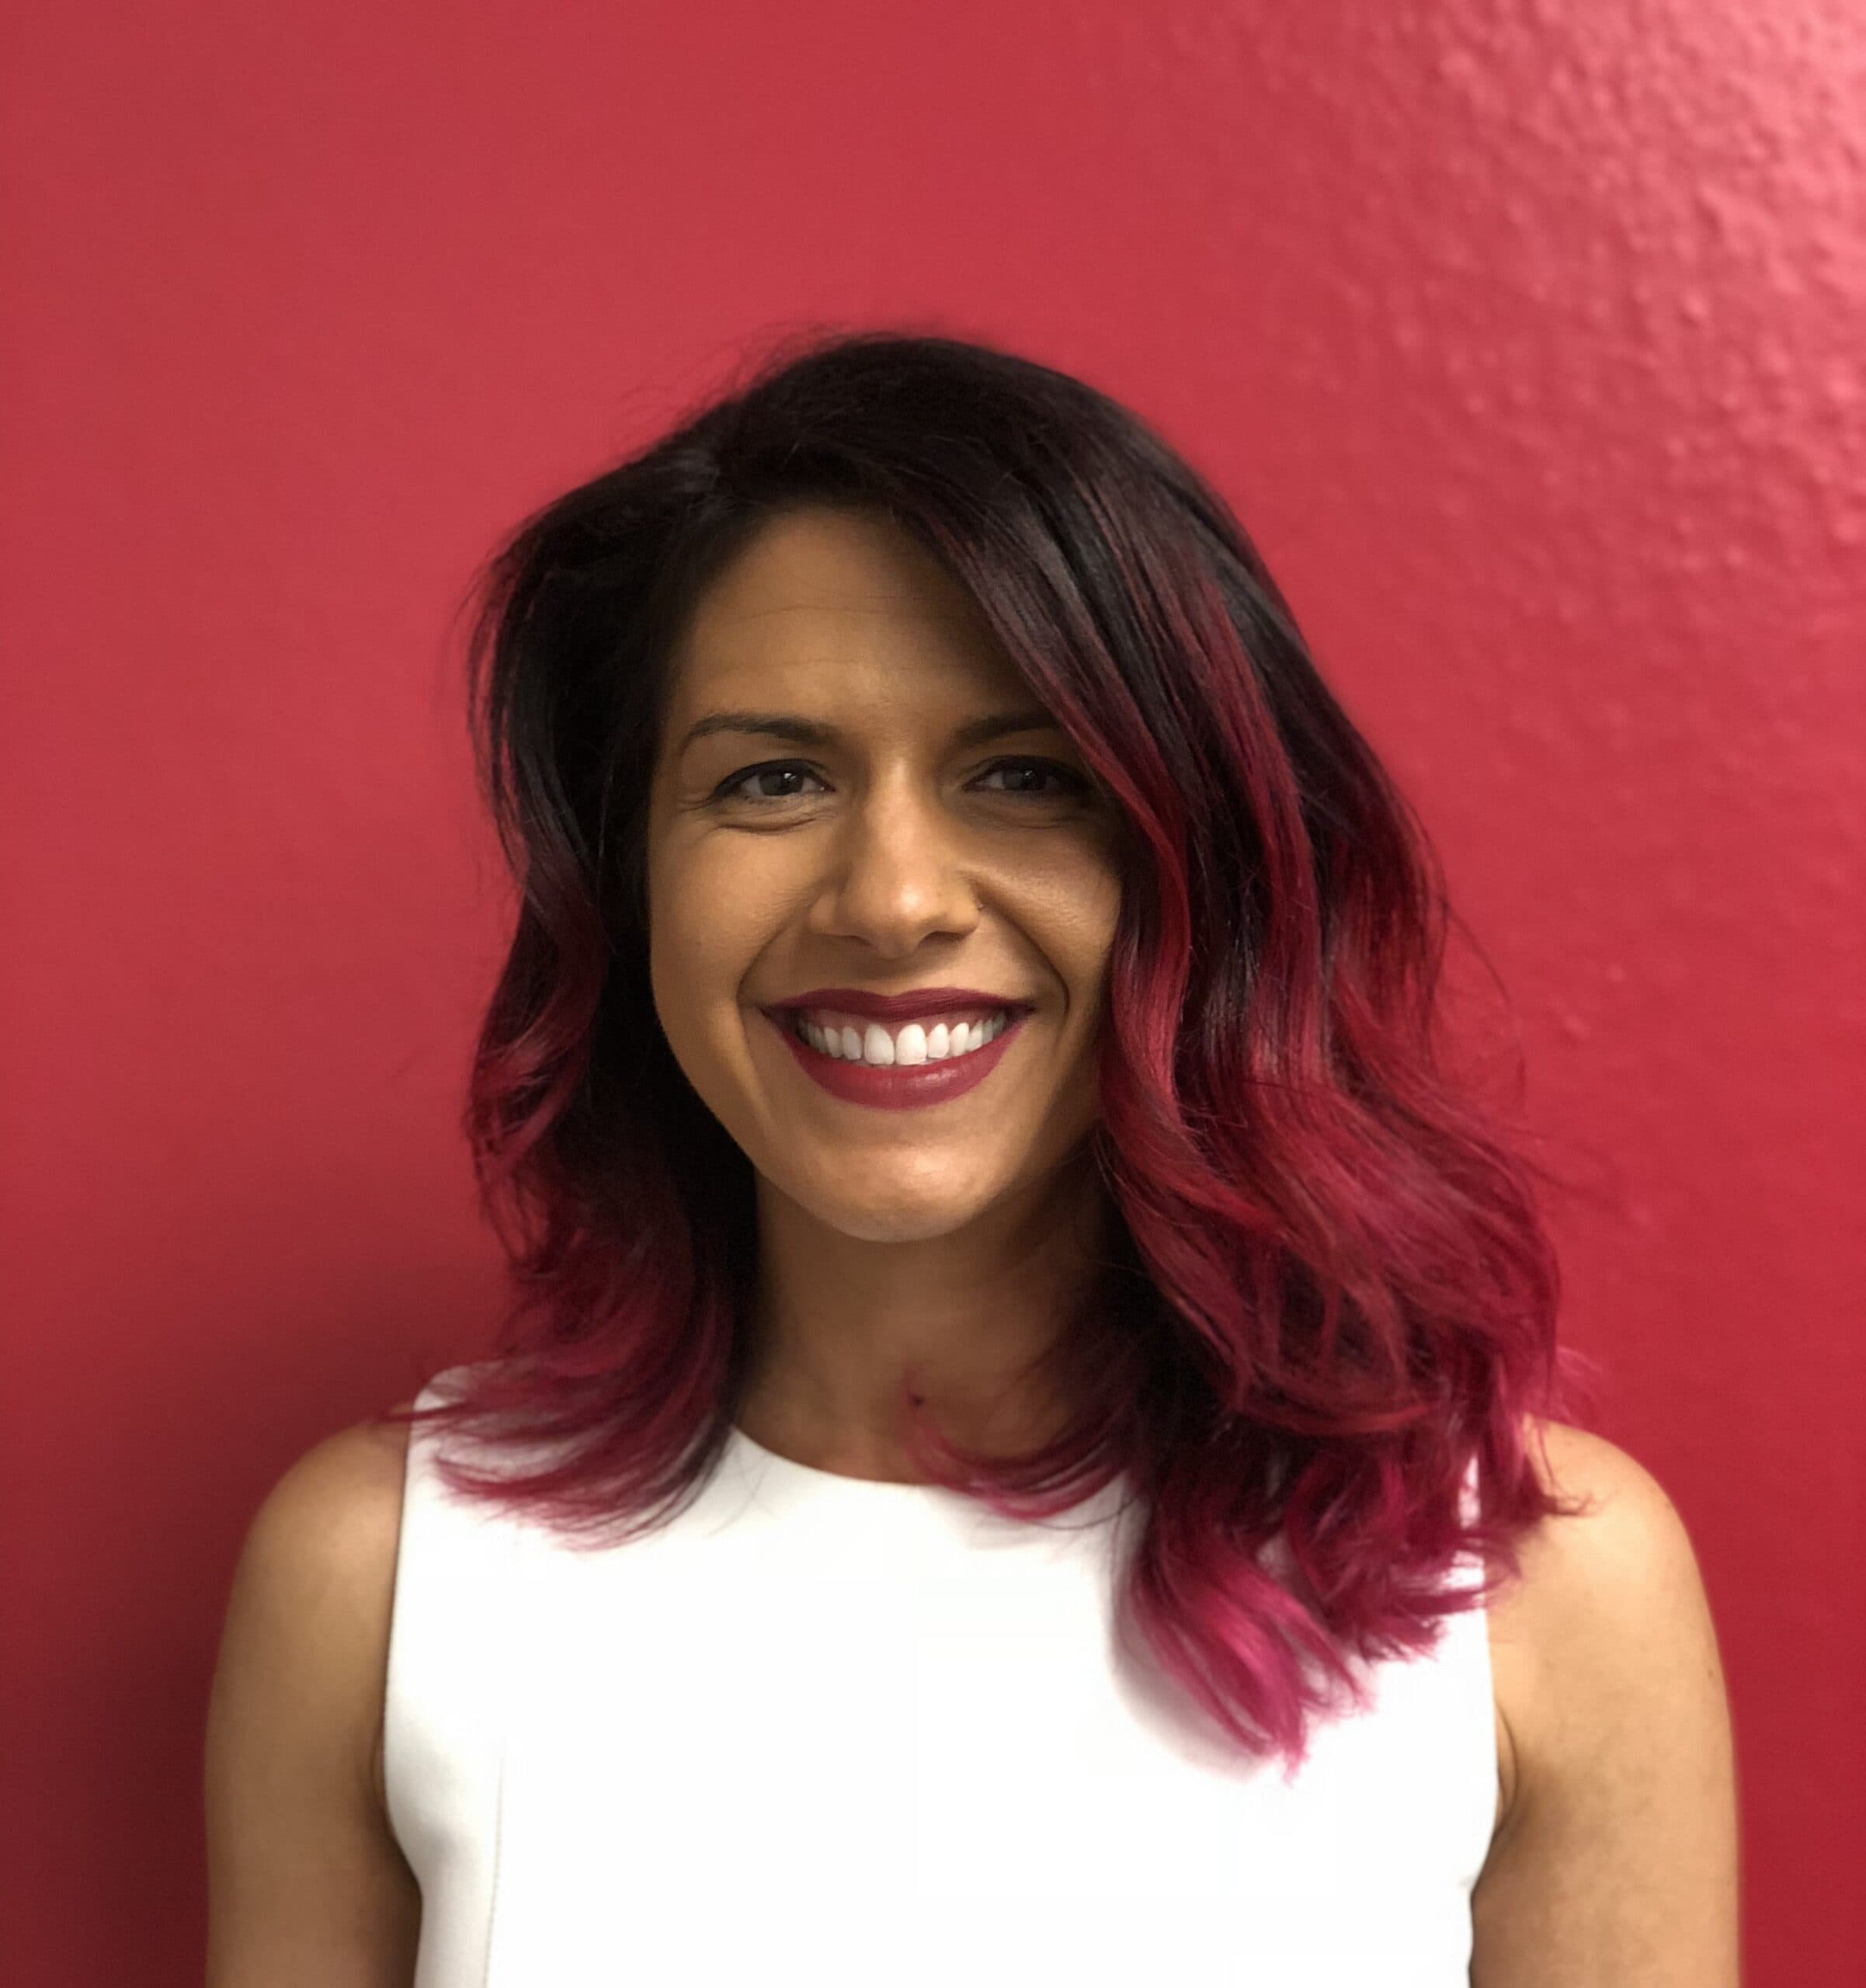
Parisa Tabriz
VP/GM of Chrome at Google
Mountain View, United States
Focus area:
#Browser security#Web security#Vulnerability research#Security engineering#Product security
Parisa Tabriz is VP/GM of Chrome at Google and manager of Project Zero. She product leadership experience and a long record of security research and work to make the web safer at global scale.
Tabriz has helped drive security across Chrome and the wider web, from sandboxing and HTTPS adoption to exploit mitigations and malicious-site defenses. Her leadership of Chrome and Project Zero connects large-scale product development with advanced security research.
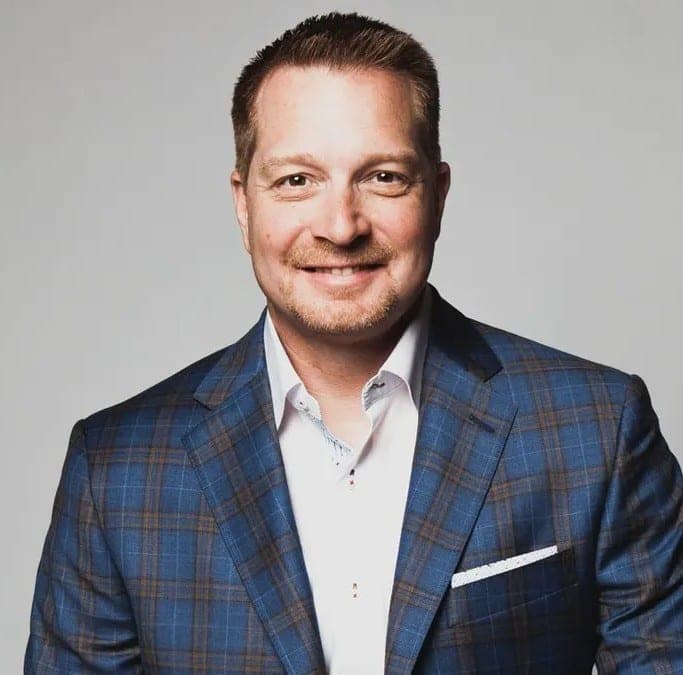
George Kurtz
Founder & CEO at CrowdStrike
Focus area:
#Endpoint security#Threat intelligence#Incident response#Cloud security#Security entrepreneurship
George Kurtz is founder and CEO of CrowdStrike, a cybersecurity entrepreneur and former McAfee worldwide CTO who previously founded Foundstone, a security products and services company.
Kurtz has built security companies around vulnerability management, incident response, endpoint defense, and threat intelligence. At CrowdStrike, his work has centered on cloud-native security and using threat data and AI to identify and stop breaches across enterprise environments.
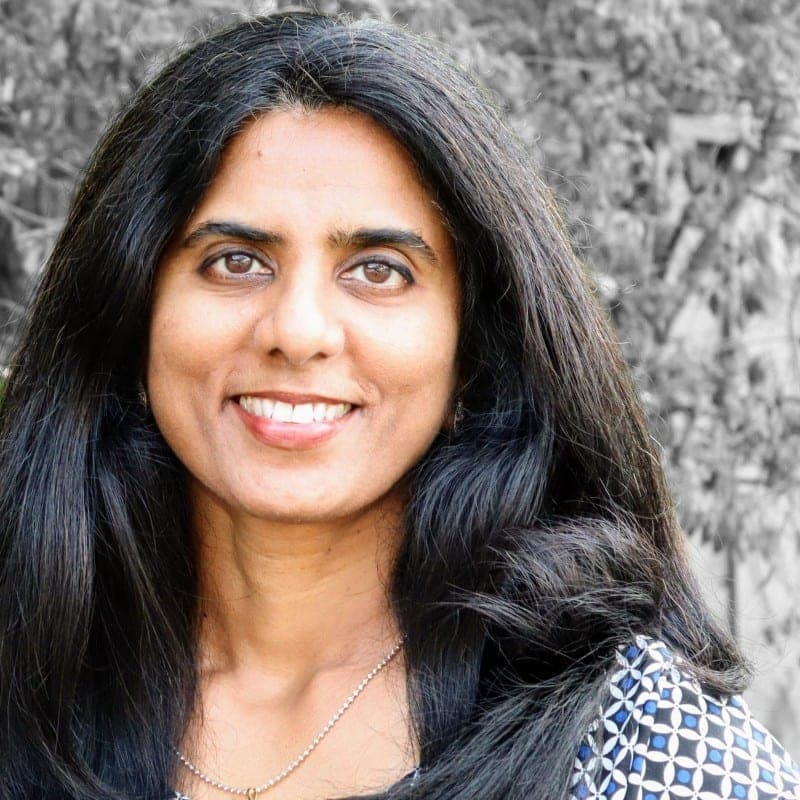
Vijaya Kaza
VP/GM, App & Ecosystem Trust at Google
Focus area:
#Platform security#Trust & safety#AI security#Security engineering#Cloud security
Vijaya Kaza is VP/GM of App and Ecosystem Trust at Google. She previously led security and trust engineering at Airbnb and held senior security and cloud engineering roles across major tech firms.
Kaza’s career spans cybersecurity, AI, cloud engineering, product development, and trust and safety. At Airbnb she led both information security and technology protecting the platform’s community, giving her a broad view of technical security and online ecosystem risk.
Connect with Vijaya:
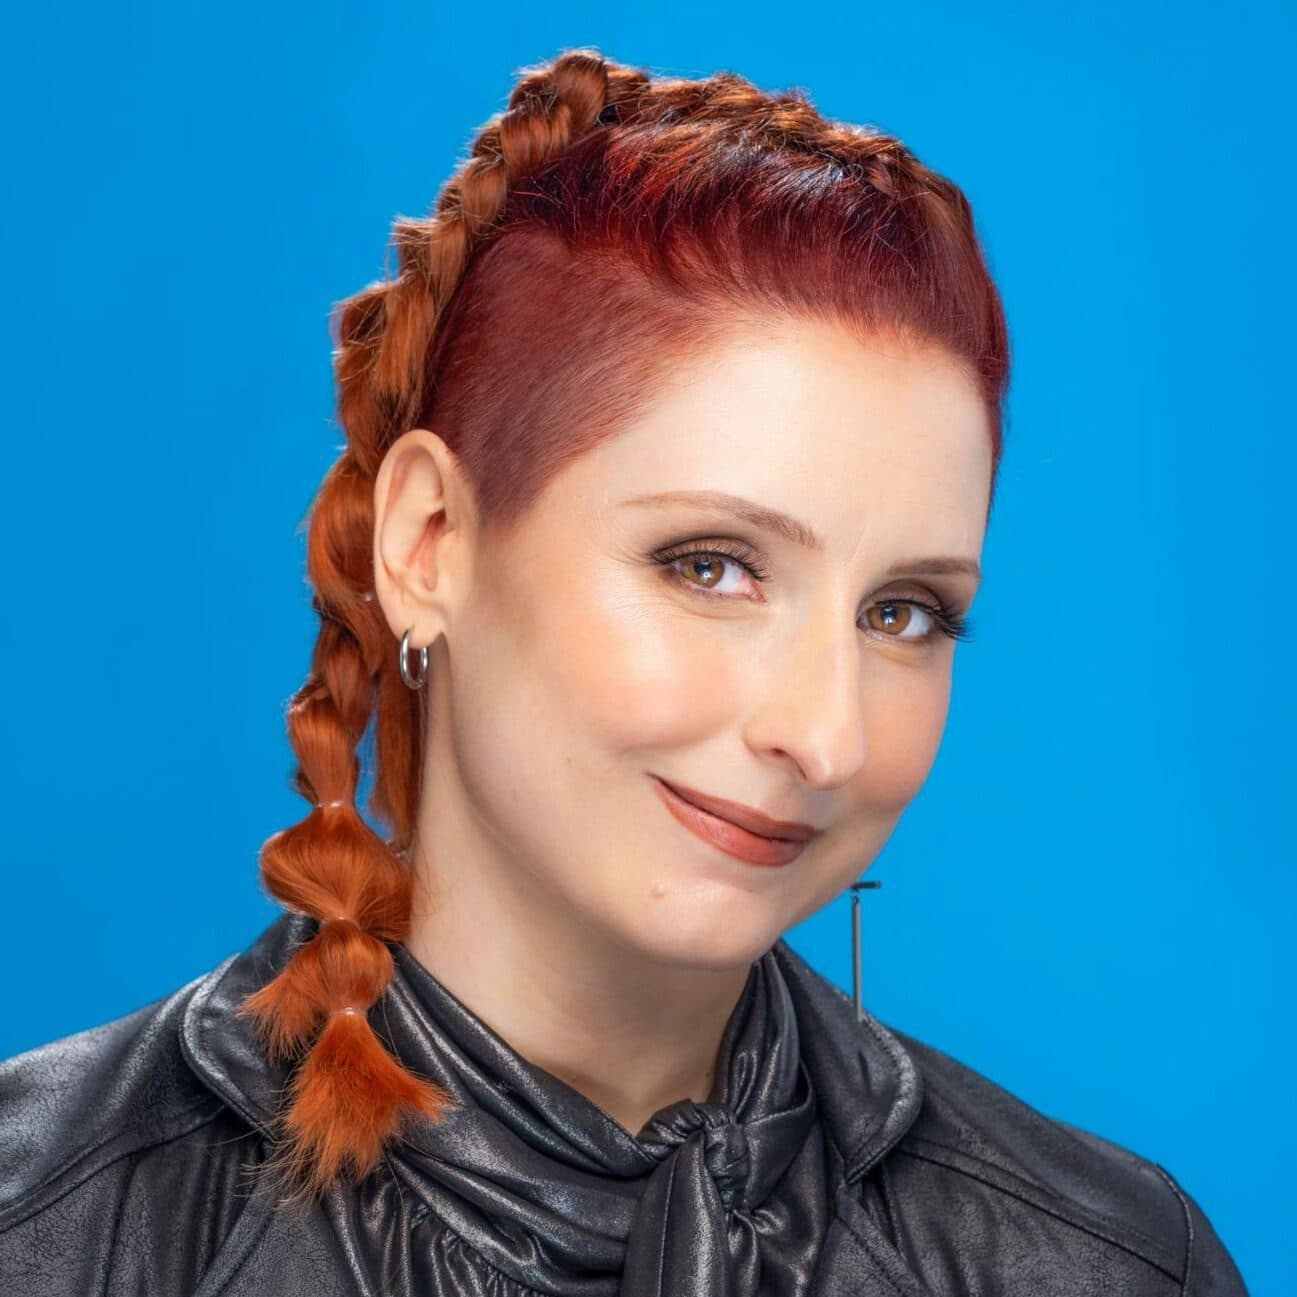
Lesley Carhart
Principal Industrial Incident Responder at Dragos
Melbourne, Australia
Focus area:
#OT security#Incident response#Digital forensics#Threat hunting#Industrial cybersecurity
Lesley Carhart is Dragos' Principal Industrial Incident Responder in Australia, leading investigations and threat hunting in industrial environments after earlier incident response and digital forensics roles.
Carhart specializes in incidents where cybersecurity meets physical operations. Their work spans OT and ICS investigations, ransomware readiness, digital forensics, threat hunting, and training defenders to respond safely when attacks affect industrial and critical-infrastructure environments.
Connect with Lesley:
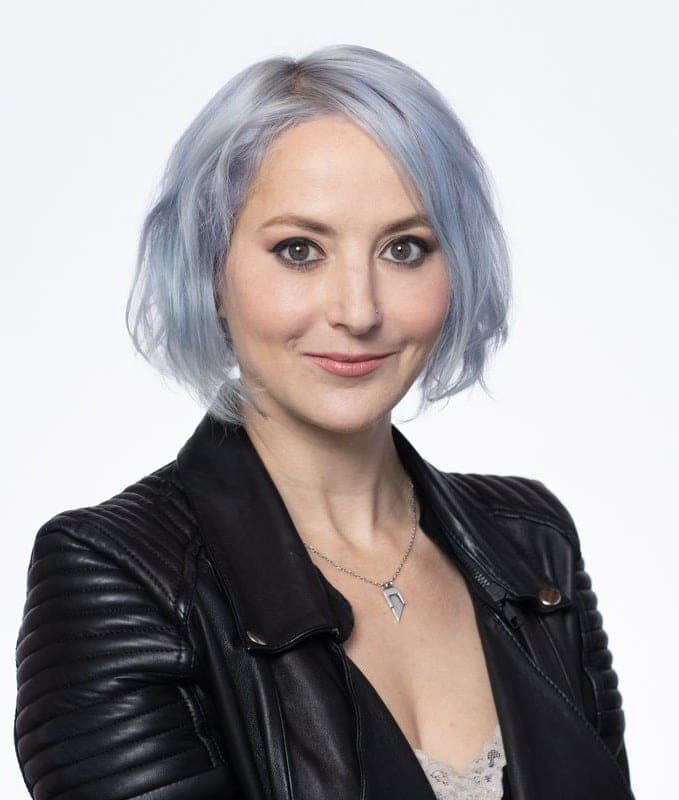
Eva Galperin
Director of Cybersecurity at EFF
San Francisco, United States
Focus area:
#Digital security#Stalkerware#Privacy#Threat research#Vulnerable populations
Eva Galperin is Director of Cybersecurity at the Electronic Frontier Foundation, where she combines security research and digital rights work to protect vulnerable populations around the world.
Galperin has investigated malware and developed practical security resources for people facing surveillance and abuse. As a co-founder of the Coalition Against Stalkerware, she has also helped turn technology-facilitated abuse into a concrete security problem for researchers and vendors to address.
Connect with Eva:
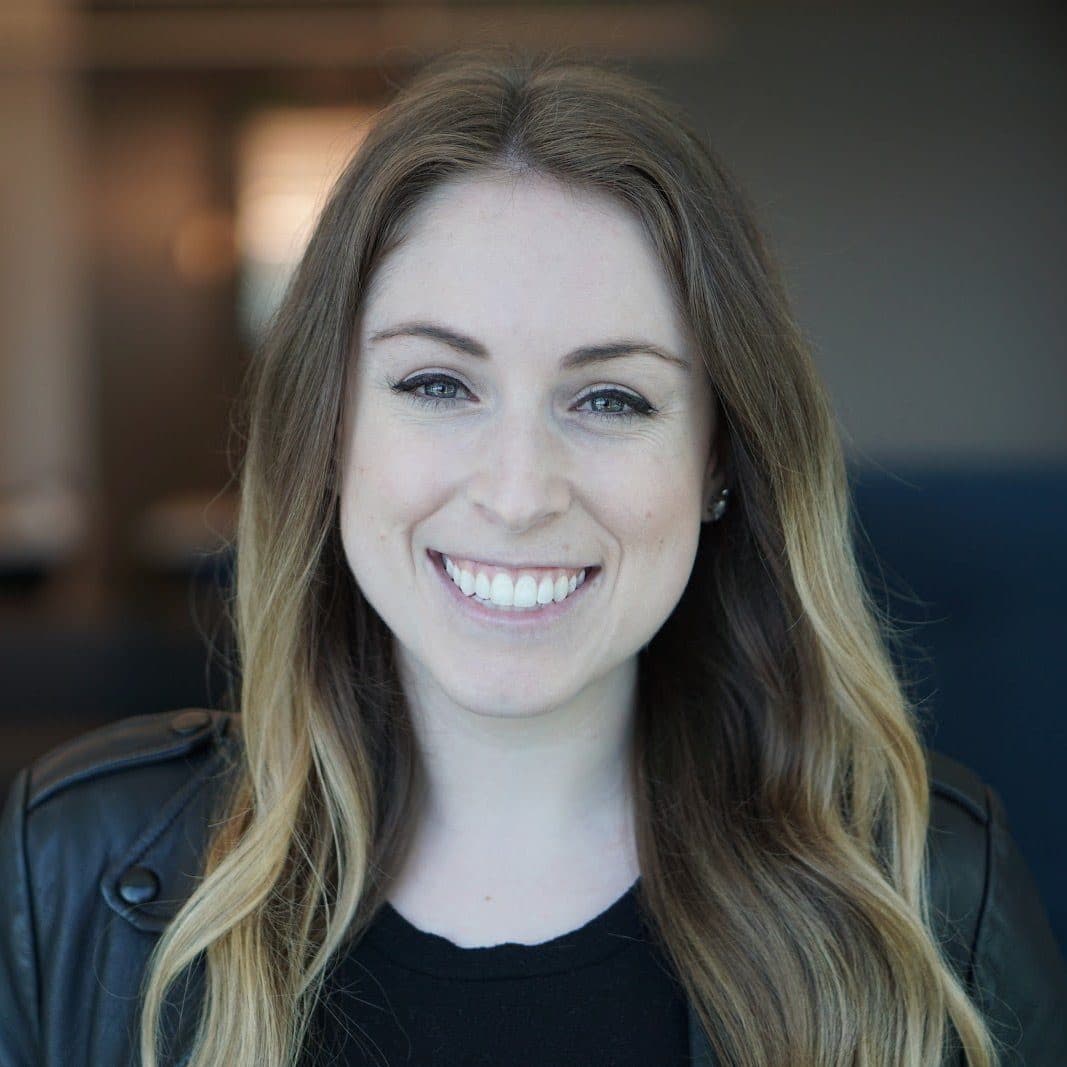
Rachel Tobac
CEO at SocialProof Security
San Francisco, United States
Focus area:
#Social engineering#Security awareness#Phishing#Impersonation defense#Human-centered security
Rachel Tobac is CEO of SocialProof Security, a social engineering specialist and hacker whose work helps organizations strengthen security awareness and resist human-targeted attacks and scams.
Tobac demonstrates how attackers exploit trust rather than just software. Her training, penetration testing, and public education focus on phishing, impersonation, deepfakes, account compromise, and practical habits that help employees and executives recognize social engineering before it succeeds.
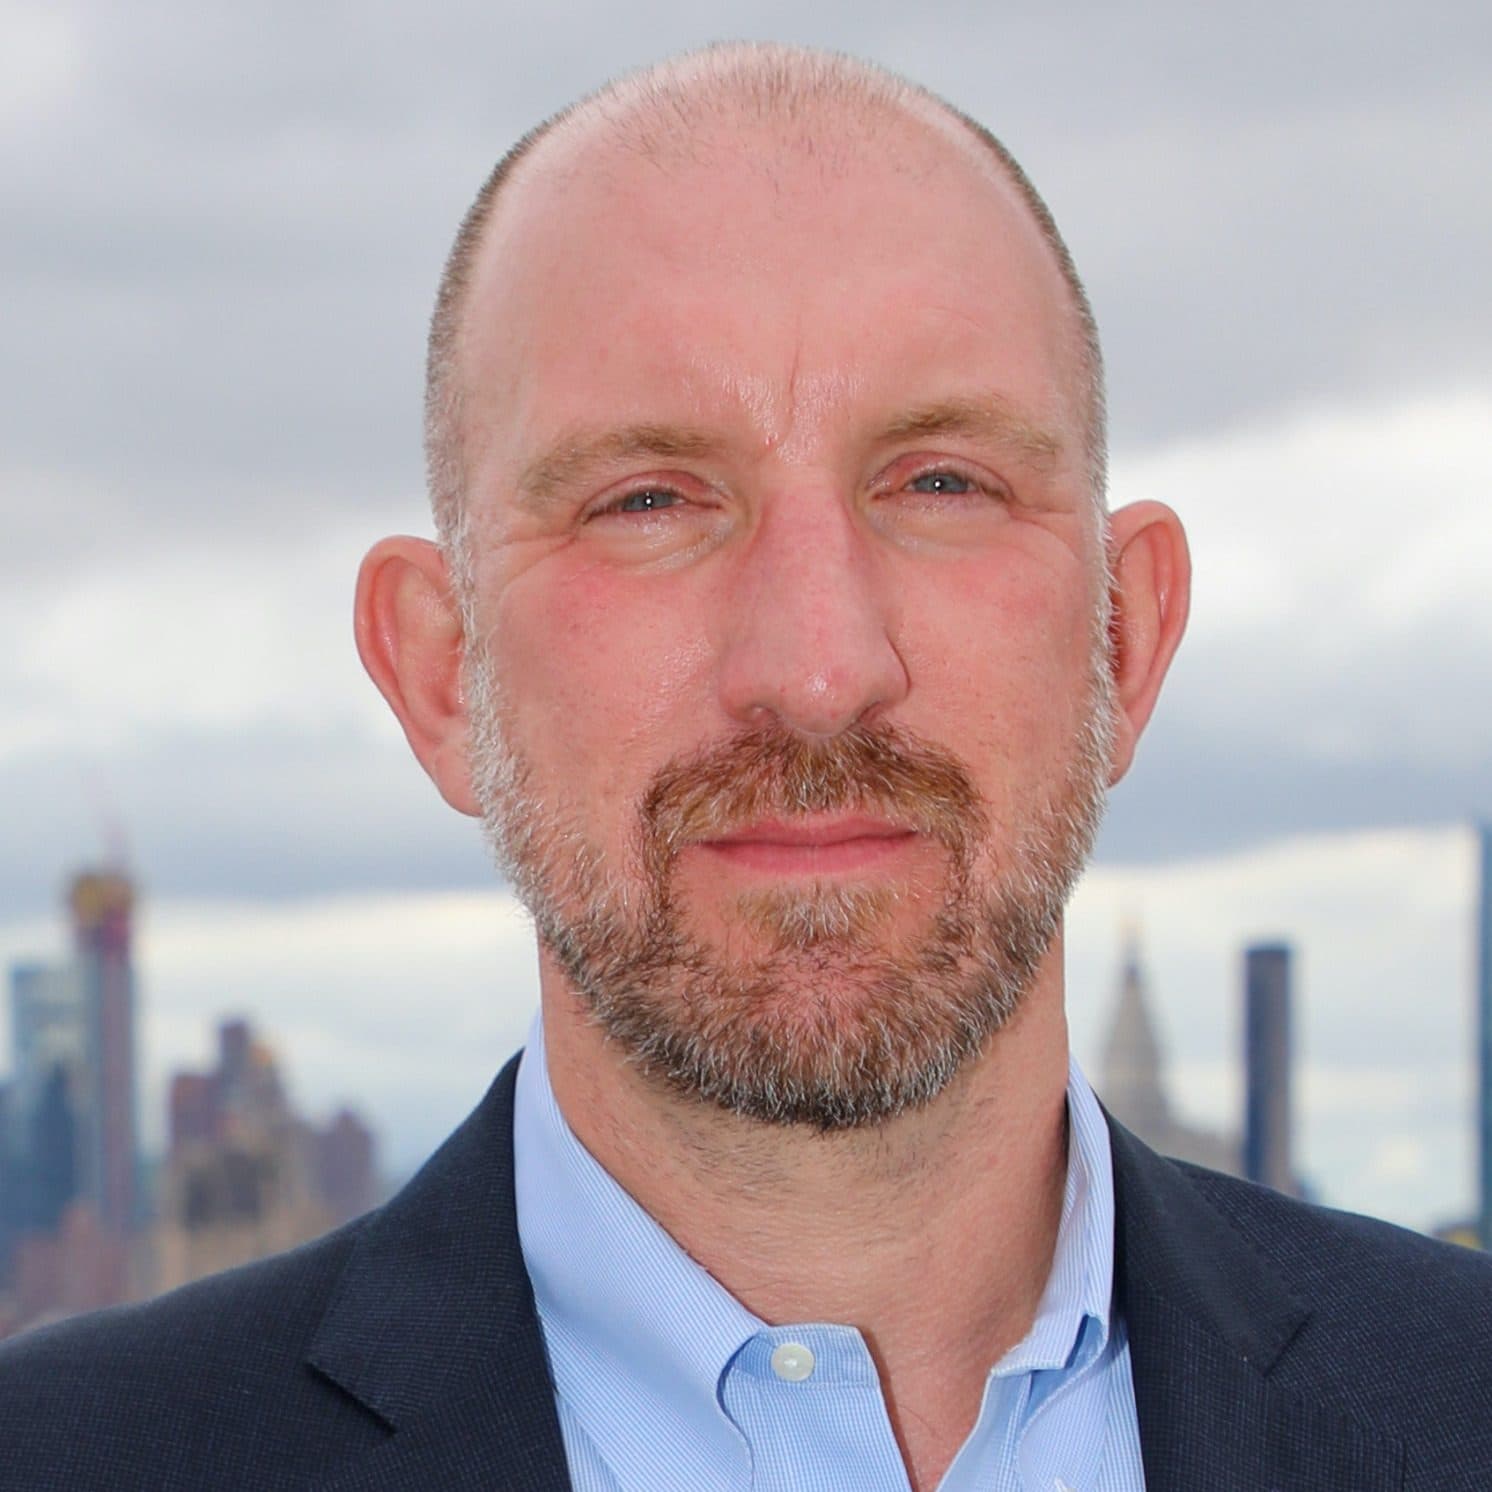
Phil Venables
Cybersecurity Advisor & Investor
New York, United States
Focus area:
#Enterprise security#Cyber risk#Cloud security#AI security#Security governance
Phil Venables is a Ballistic Ventures partner and Google Strategic Security Advisor, after serving as Google Cloud's first CISO and spending decades leading enterprise security and technology risk.
Venables brings a board-level view of cybersecurity shaped by senior roles at Google Cloud and Goldman Sachs. His work connects security engineering with risk, governance, cloud and AI security, while his investing and advisory roles give him a close view of emerging cybersecurity technologies.
Selection Methodology
We selected the leaders on this list based on their relevance, demonstrated expertise and impact, professional credibility, and ongoing contributions to the field.
We look for evidence such as leading meaningful initiatives or delivering notable results within their organizations, developing influential ideas or practices, publishing research or educational resources, speaking or teaching, and other contributions that demonstrate impact within their work or the broader field.
What’s Next?
Boost your SaaS growth and leadership skills. Subscribe to our newsletter for the latest insights from CTOs and aspiring tech leaders. We'll help you scale smarter and lead stronger with guides, resources, and strategies from top experts!