
Avis sur SentinelOne : Avantages, Inconvénients, Fonctionnalités et Tarification Expliqués
SentinelOne se distingue par sa détection et réponse aux menaces autonome, offrant une protection robuste et une grande facilité d'utilisation, mais conviendra surtout aux organisations qui privilégient l'automatisation au contrôle manuel.

Nous évaluons les outils indépendamment ; les commissions aident à financer nos tests. Consultez notre politique de transparence et notre méthodologie.
SentinelOne is a cybersecurity software built around autonomous AI-driven endpoint detection and response, covering endpoints, cloud workloads, identity, and network data from a single platform. I'd consider it if your team needs threat detection and automated remediation without depending heavily on analyst intervention at every step. If you're weighing it against CrowdStrike, SentinelOne tends to be the stronger pick when you want faster autonomous response with less reliance on cloud connectivity and human triage—particularly useful for teams running lean security operations.
SentinelOne Evaluation Summary
4.7/5
- From $179.99/endpoint (billed annually)
- Free demo available
Pourquoi faire confiance à nos recommandations de logiciels
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Notre équipe teste et évalue des logiciels depuis 2012. En tant que leaders technologiques nous-mêmes, nous savons à quel point il est difficile — et important — de choisir le bon logiciel.
Pour ce guide, nous avons évalué les outils grâce à des tests pratiques et une recherche indépendante, en notant les outils selon nos critères de sélection.
Nos avis reflètent notre jugement éditorial humain, et non un argumentaire de vente.
Réviseurs experts:
- Paulo Gardini MiguelDirecteur technique
 Tim FisherVP de l'IA
 Gabriel RosasTech Lead et architecte logiciel
 Christhian GruhnTech Lead et architecte plateforme

SentinelOne Overview
In my experience, SentinelOne delivers as an endpoint detection and response (EDR) solution, with a clean interface and robust functionality. Its AI-driven automation and broad integration options set it apart for teams seeking hands-off protection, though pricing can be higher than some alternatives and advanced manual controls are less granular. I think it's a strong choice for organizations prioritizing automation, endpoint security, and rapid incident response—especially in environments with limited security staff or high endpoint diversity. If you're judging by ease of use and automation, SentinelOne is tough to beat.
Pros
- AI-driven detection stops advanced threats quickly
- Automated rollback restores endpoints after ransomware attacks
- Minimal system impact on user devices
Cons
- Higher cost than many competitors
- Occasional false positives require manual review
- Console outages reported during updates
Is SentinelOne Right For Your Needs?
Who Would be a Good Fit for SentinelOne?
SentinelOne is a strong choice for organizations that need autonomous threat detection, rapid response, and scalable protection across diverse endpoints. I think it's especially well-suited for industries with strict compliance needs, companies with distributed workforces, and teams with limited security staff. SentinelOne's AI-driven automation, ransomware rollback, and minimal device impact make it a practical fit for environments where speed and reliability are essential. User reviews consistently highlight the platform's machine learning capabilities and response capabilities as key differentiators for mid-to-large security operations.
- Healthcare ProvidersSentinelOne's automated response and compliance features help protect sensitive patient data.
- Financial ServicesReal-time threat detection supports strict regulatory requirements and high-value assets.
- Remote WorkforcesCloud-based management and low device impact suit distributed teams.
- Education InstitutionsAutomated rollback and easy deployment help protect large, diverse device fleets.
- IT DepartmentsCentralized console and broad OS support simplify endpoint management.
- Mid-Size EnterprisesScalable licensing and automation reduce the need for large security teams.
Who Would be a Bad Fit for SentinelOne?
SentinelOne may not be the best fit for organizations with tight budgets, highly specialized manual security workflows, or those needing deep integration with legacy systems. If your team relies on granular manual controls or has minimal endpoints to protect, you might find SentinelOne's automation and pricing less appealing compared to other EDR solutions.
- Small NonprofitsHigher pricing and advanced features may exceed basic network security needs.
- Legacy System OperatorsLimited support for outdated OS versions can hinder deployment.
- Highly Regulated GovernmentSome agencies require on-premises solutions SentinelOne doesn't offer.
- Micro StartupsCost and feature set may be overkill for very small teams.
- Manual-First SOC TeamsAutomation focus limits deep manual investigation and tuning.
- Retail Chains With POSPOS-specific security needs may require more specialized solutions.
Notre méthodologie d'évaluation
Comment nous testons et notons les outils
Nous avons passé des années à développer, affiner et améliorer notre système de test et de notation des logiciels. Cette grille d’évaluation est conçue pour saisir les subtilités de la sélection des logiciels et ce qui rend un outil efficace, en se concentrant sur les aspects critiques du processus de décision.
Vous trouverez ci-dessous le détail de notre processus de test et de notation sur sept critères. Cela nous permet de fournir une évaluation impartiale du logiciel basée sur les fonctionnalités principales, les caractéristiques distinctives, la facilité d’utilisation, l’intégration, l’accompagnement lors de la prise en main, le support client, les avis utilisateurs et le rapport qualité-prix.
Fonctionnalité principale (25% de la note finale)
Le point de départ de notre évaluation est toujours la fonctionnalité principale de l’outil. Possède-t-il les fonctions de base auxquelles un utilisateur s’attend ? Certaines de ces fonctionnalités principales sont-elles limitées à des forfaits plus chers ? Nous attendons d’un outil qu’il soit au moins à la hauteur des capacités de base de ses concurrents.
Fonctionnalités remarquables (25% de la note finale)
Ensuite, nous évaluons les fonctionnalités exceptionnelles qui dépassent la fonctionnalité de base habituellement trouvée dans ce type d’outil. Un score élevé reflète des fonctionnalités spécialisées ou uniques rendant le produit plus rapide, plus efficace ou apportant une valeur ajoutée à l’utilisateur.
Nous évaluons aussi la facilité d’intégration avec d’autres outils courants dans la pile technologique pour élargir les fonctionnalités et l’utilité du logiciel. Les outils dotés de nombreuses intégrations natives, de connexions tierces et d’un accès API facilitant des intégrations personnalisées obtiennent les meilleurs scores.
Facilité d’utilisation (10% de la note finale)
Nous considérons la rapidité et la simplicité d’exécution des tâches principales avec l’outil. Les logiciels les mieux notés sont bien conçus, intuitifs, proposent des applications mobiles, offrent des modèles et rendent des tâches relativement complexes très simples.
Accompagnement lors de la prise en main (10% de la note finale)
Nous savons que l’adoption rapide d’une nouvelle plateforme au sein d’une équipe est cruciale. Nous évaluons donc la facilité avec laquelle un nouvel utilisateur peut apprendre et utiliser un outil avec un minimum de formation. Les meilleures solutions permettent une mise en route rapide, sans nécessité de support.
Support client (10% de la note finale)
Nous analysons la facilité et la rapidité avec lesquelles il est possible d’obtenir de l’aide par téléphone, chat en direct ou base de connaissances. Les outils et entreprises offrant une assistance en temps réel obtiennent les meilleurs scores, tandis que les chatbots sont moins bien notés.
Avis utilisateurs (10% de la note finale)
Au-delà de nos propres tests et évaluations, nous tenons compte du net promoter score des utilisateurs actuels et passés. Nous regardons la probabilité qu’ils choisiraient à nouveau l’outil pour ses fonctionnalités principales. Un logiciel bien noté reflète un net promoter score élevé.
Rapport qualité-prix (10% de la note finale)
Enfin, en tenant compte de tous les autres critères, nous examinons le prix moyen des forfaits d’entrée de gamme par rapport aux fonctionnalités principales et à la valeur des autres critères. Un logiciel offrant plus, pour moins cher, obtiendra un meilleur score.
Core Features
Autonomous Threat Detection
SentinelOne uses AI to identify and stop threats in real time without human intervention. This reduces response times and helps streamline vulnerability management.
Ransomware Rollback
The platform can automatically restore files and system states after a ransomware attack. This rollback feature minimizes downtime and data loss for affected endpoints.
Behavioral AI Engine
SentinelOne uses machine learning to analyze device and user behavior and spot suspicious activity. It adapts to new threats, catching malware that signature-based tools might miss.
Automated Remediation
When a threat is detected, SentinelOne can isolate, kill, and remove malicious files automatically. This limits the impact of attacks and reduces manual workload for IT teams.
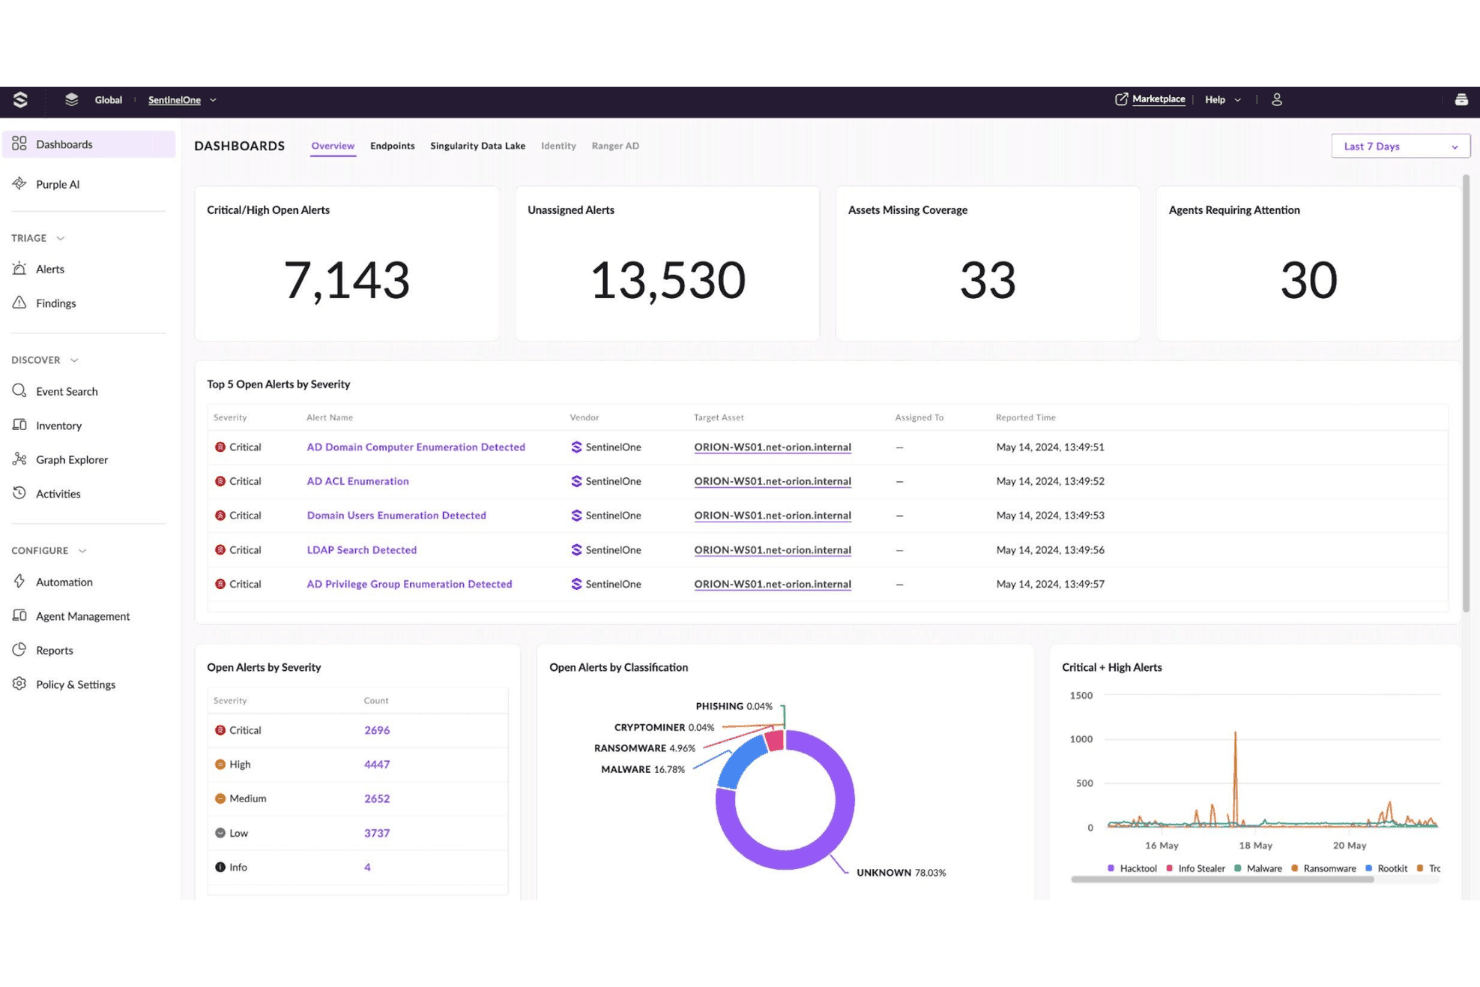
Centralized Management Console
Admins manage all endpoints and policies from a single, cloud-based dashboard. This makes it easy to monitor, configure, and respond across large environments.
Device Control
SentinelOne lets you set policies for USB and peripheral device usage. This helps prevent data exfiltration and blocks unauthorized hardware access.
Ease of Use
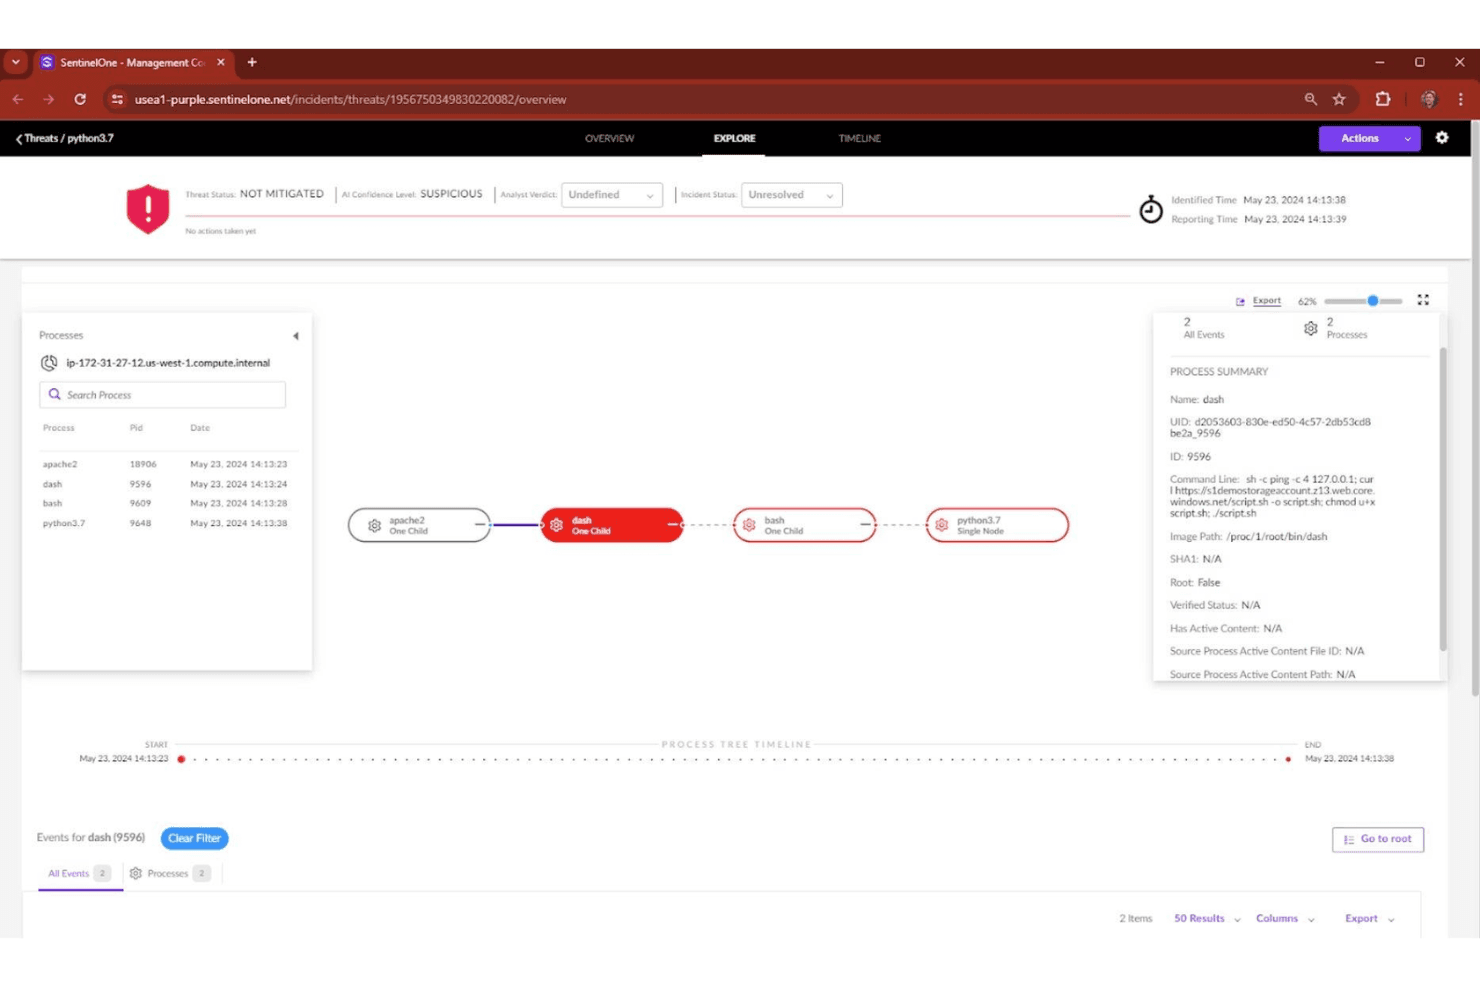
SentinelOne is widely praised for its intuitive interface and straightforward deployment, making it accessible even for teams without deep security expertise. The centralized console simplifies monitoring and policy management across many endpoints. Automated responses and clear visualizations reduce manual effort and speed up investigations. I think most users will find the platform easy to navigate, with helpful documentation and responsive support that further smooth out the onboarding process.
Integrations
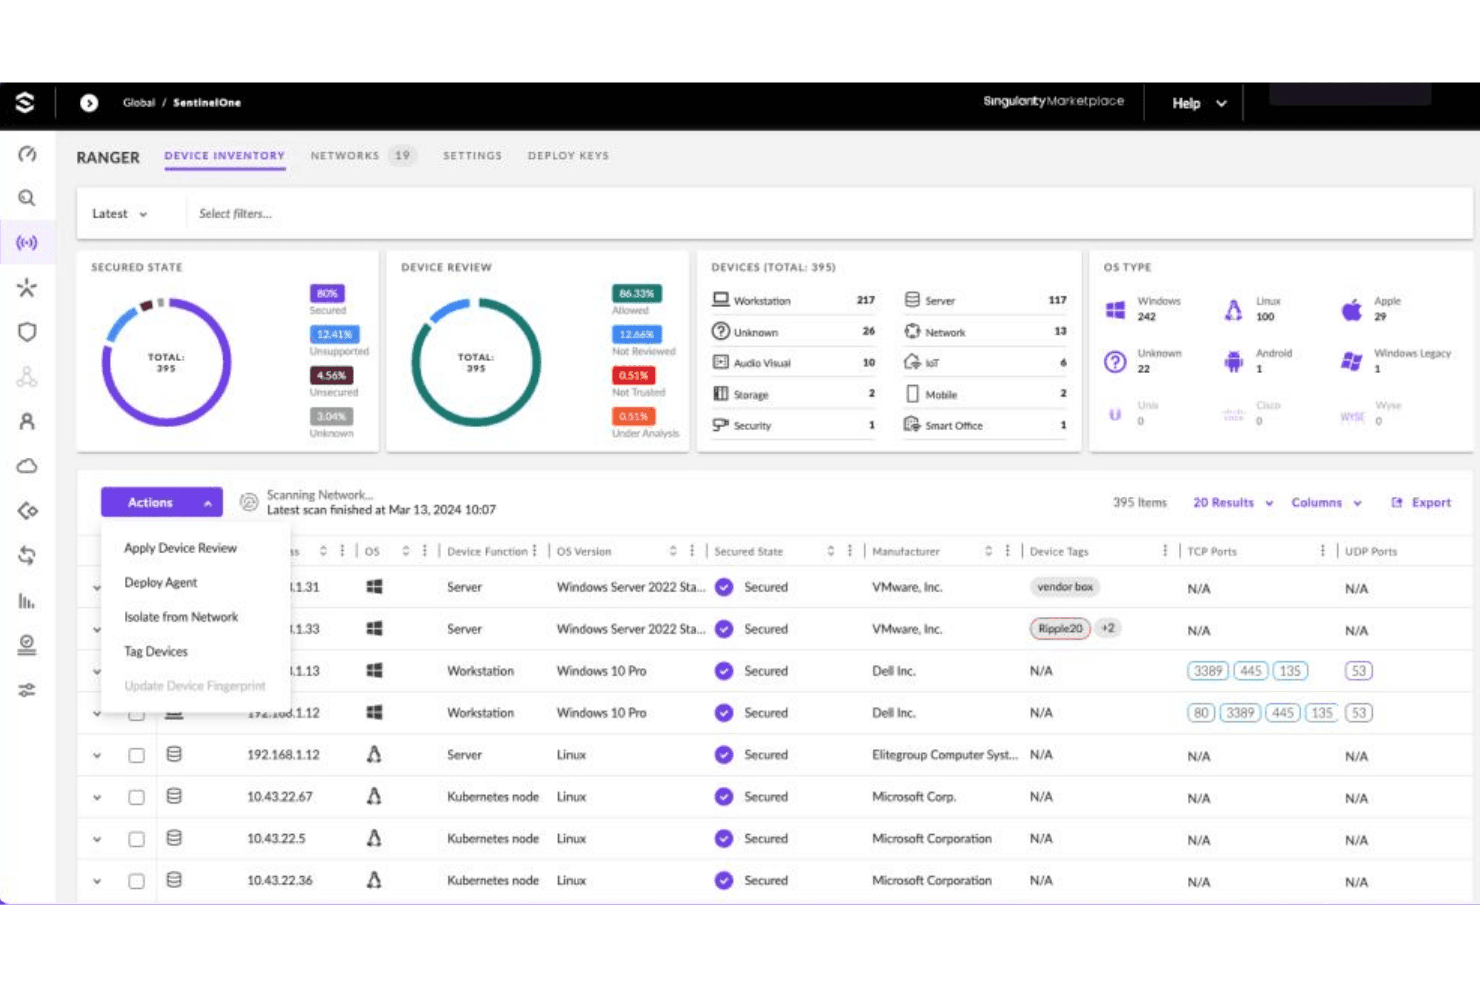
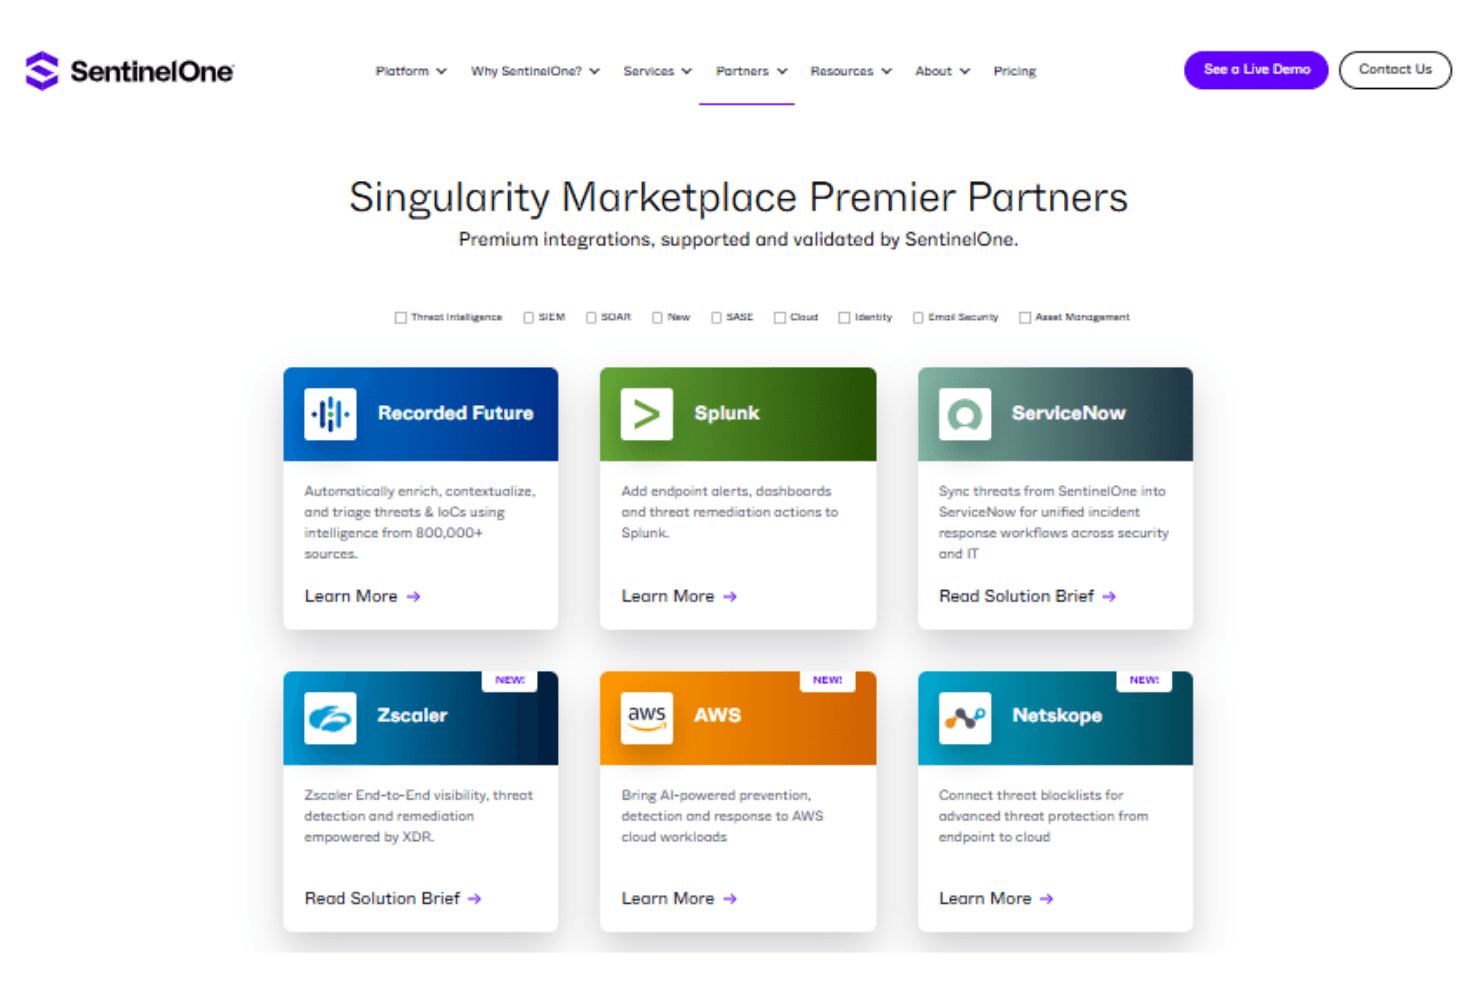
SentinelOne integrates with Splunk, Zscaler, AWS, Netskope, Okta, and IBM Security, among others.
SentinelOne also offers a robust API and connects with third-party integration tools through its Singularity Marketplace.
SentinelOne Specs
- 2-Factor Authentication: Yes
- Access Management: Yes
- Anti-Virus: Yes
- API: Yes
- Audit Management: Yes
- Audit Trail: Yes
- Batch Permissions & Access: Yes
- Compliance Tracking: Yes
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- DDoS Protection: Yes
- External Integrations: Yes
- File Sharing: Yes
- File Transfer: Yes
- Firewall: Yes
- Incident Management: Yes
- Malware Protection: Yes
- Multi-User: Yes
- Notifications: Yes
- Password & Access Management: Yes
- Policy Management: Yes
- Real-time Alerts: Yes
- Report & Compliance: Yes
- Risk Assessment: Yes
- Security Migration: Yes
- Threat Detection: Yes
- Workflow Management: Yes


