

10 bästa programvarorna för sårbarhetsskanning för QA-team (2026)

10 Bästa programvarorna för sårbarhetsskanning – kortlista


Med så många olika programvaror för sårbarhetsskanning att välja mellan är det svårt att avgöra vilken som passar dig bäst. Du vet att du vill upptäcka och åtgärda säkerhetsluckor proaktivt innan de kan utnyttjas, men du behöver ta reda på vilket verktyg som är bäst. Jag hjälper dig! I det här inlägget gör jag ditt val enklare genom att dela med mig av mina personliga erfarenheter av att använda dussintals olika verktyg för sårbarhetsskanning med olika team och i olika projekt, samt mina val av de bästa programvarorna för sårbarhetsskanning.
Why Trust Our Software Reviews
We’ve been testing and reviewing software since 2023. As tech leaders ourselves, we know how critical and difficult it is to make the right decision when selecting software.
We invest in deep research to help our audience make better software purchasing decisions. We’ve tested more than 2,000 tools for different tech use cases and written over 1,000 comprehensive software reviews. Learn how we stay transparent & our software review methodology.
Sammanfattning av de bästa programvarorna för sårbarhetsskanning
Det här jämförelsediagrammet sammanfattar prisuppgifterna för mina främsta val av programvara för sårbarhetsskanning, så att du kan hitta det bästa alternativet för din budget och verksamhetens behov.
| Tool | Best For | Trial Info | Price | ||
|---|---|---|---|---|---|
| 1 | Best for enterprise vulnerability mitigation | Free 30-day trial and demo available | $1,195 for 100 workstations and a single-user license | Website | |
| 2 | Best for CI/CD-integrated code quality checks | Free plan + 14-day free trial + free demo available | From $34/month | Website | |
| 3 | Best for proactive vulnerability management | 14-day free trial + free demo available | From $149/month | Website | |
| 4 | Best for identifying potential security weaknesses across an organization's network | 30-day free trial + free demo available | From $338.50/year | Website | |
| 5 | Best for proof-based vulnerability scanning | Free demo available | Pricing upon request | Website | |
| 6 | Best for continuous vulnerability scanning & pentesting for 9300+ test cases | Free demo available | From $69/month | Website | |
| 7 | Information security solution that provides deep visibility into global assets | Free trial available | Pricing upon request | Website | |
| 8 | Best vulnerability scanning software to lower the rate of false positives | Free plan available | From $99/user/month | Website | |
| 9 | Best for hybrid scanning with AcuSensor Technology | Free demo available | Pricing upon request | Website | |
| 10 | Vulnerability scanning tool great for crawling JavaScript-heavy applications | Free plan available | From $475/user/year | Website |
Recensioner av de bästa programvarorna för sårbarhetsskanning
Nedan finns mina detaljerade sammanfattningar av de bästa programvarorna för sårbarhetsskanning som kom med på min kortlista. I mina recensioner får du en detaljerad genomgång av de viktigaste funktionerna, fördelarna och nackdelarna, integrationerna och de idealiska användningsområdena för varje verktyg, så att du kan hitta det bästa alternativet för dig.

Best for enterprise vulnerability mitigation

ManageEngine Vulnerability Manager Plus is a comprehensive tool designed for enterprise vulnerability management, offering features such as secure configuration deployment, compliance, automated patch deployment, and zero-day vulnerability mitigation. It goes beyond the capabilities of traditional vulnerability management tools, providing executive reports, antivirus audits, deployment policies, and role-based administration.
Its ability to automate vulnerability assessment, patch management, and compliance management from a single console makes it a standout choice for large organizations with complex security needs. ManageEngine Vulnerability Manager Plus distinguishes itself with its robust capabilities, including detailed insights and reports that streamline the vulnerability management process. Its all-in-one platform for managing network vulnerabilities and its prioritization-focused approach to identifying and addressing vulnerabilities make it an ideal choice for enterprises.
ManageEngine Vulnerability Manager Plus offers a comprehensive Vulnerability Assessment feature that identifies and prioritizes a wide array of vulnerabilities, considering factors like exploitability and severity. Its integrations include Active Directory, Azure AD, AWS, and G Suite, which facilitates the management and monitoring of vulnerabilities across different platforms and services. The software provides tools for vulnerability assessment, compliance, patch management, network device security configuration management, and zero-day vulnerability mitigation.

Best for CI/CD-integrated code quality checks

SonarQube is a static application security testing tool that analyzes source code for vulnerabilities, IaC misconfigurations, and secrets, covering 40+ languages with compliance reporting and automated quality gates.
Who Is SonarQube Best For?
SonarQube is a strong fit for development and security teams at mid-size to enterprise organizations that need security analysis embedded directly into their software development lifecycle.
Why I Picked SonarQube
I've included SonarQube in my top picks because of how deeply it embeds into CI/CD workflows. It automatically scans every branch, pull request, and merge as soon as code is pushed, then decorates pull requests with actionable findings. What I find especially useful are the quality gates: they enforce go/no-go deployment decisions so that code failing your security or quality thresholds can't be merged or released. Combined with native support for GitHub, GitLab, Bitbucket, and Azure DevOps, getting analysis running in an existing pipeline takes minutes, not days.
SonarQube Key Features
- SAST taint analysis: Traces untrusted data across code execution paths to detect injection vulnerabilities, XSS, and other data-flow security issues.
- Secrets detection: Scans source code and config files for hardcoded secrets using 400+ detection patterns across 340+ rule types.
- IaC scanning: Analyzes Terraform, CloudFormation, Kubernetes, and Docker files for security misconfigurations before deployment.
- AI CodeFix: Surfaces one-click, AI-generated remediation suggestions directly alongside flagged vulnerabilities in the developer's workflow.
SonarQube Integrations
SonarQube offers native integrations with GitHub, GitLab, Atlassian Bitbucket, Azure DevOps, Atlassian Jira, Slack, Jenkins, JFrog, CircleCI, and Datadog, plus IDE plugins for VS Code, IntelliJ, and Eclipse. The integrations page lists 30+ first-party integrations and additional third-party and Sonar Certified options across CI/CD, IDE, security, and observability categories, and an API is available for custom integrations.
Pros and Cons
Pros:
- Low false-positive rate on security findings
- SCA add-on detects third-party dependency vulnerabilities
- Over 6,000 built-in rules across 35+ languages
Cons:
- Self-hosted setup requires significant DevOps effort
- Security depth lags dedicated SAST tools
New Product Updates from SonarQube
SonarQube Cloud Adds DataWeave, Gosu, Groovy, and PowerShell
SonarQube Cloud now supports MuleSoft DataWeave, Gosu, Groovy, and PowerShell, extending deterministic analysis with bug, security, and maintainability checks across existing SCM integrations. For more information, visit SonarQube's official site.
 .
Intruder
Best for proactive vulnerability management

Intruder is a cloud-based vulnerability scanner that aims to help businesses of all sizes discover security weaknesses in their online systems. The tool provides continuous monitoring of the network to identify vulnerabilities and reduce the attack surface.
Intruder provides a proactive security monitoring service, which includes regular scans to detect new threats as they emerge. Its network vulnerability scanning checks for over 10,000 vulnerabilities automatically. The tool then prioritizes the results to help focus on the issues that matter most and provide clear information on how to fix them.
Integrations are natively available with Slack, MS Teams, Jira, Github, and Gitlab. Other integrations can be accessed through Zapier and API.
Intruder costs from $196/month/application. A 14-day free trial is also available.
New Product Updates from Intruder
Intruder Launches On-Demand AI Pentesting for Web Apps
Intruder adds on-demand AI pentesting for web applications, allowing teams to launch assessments in minutes and receive audit-ready reports on the same day. For more information, visit Intruder’s official site.
 .

Best for identifying potential security weaknesses across an organization's network
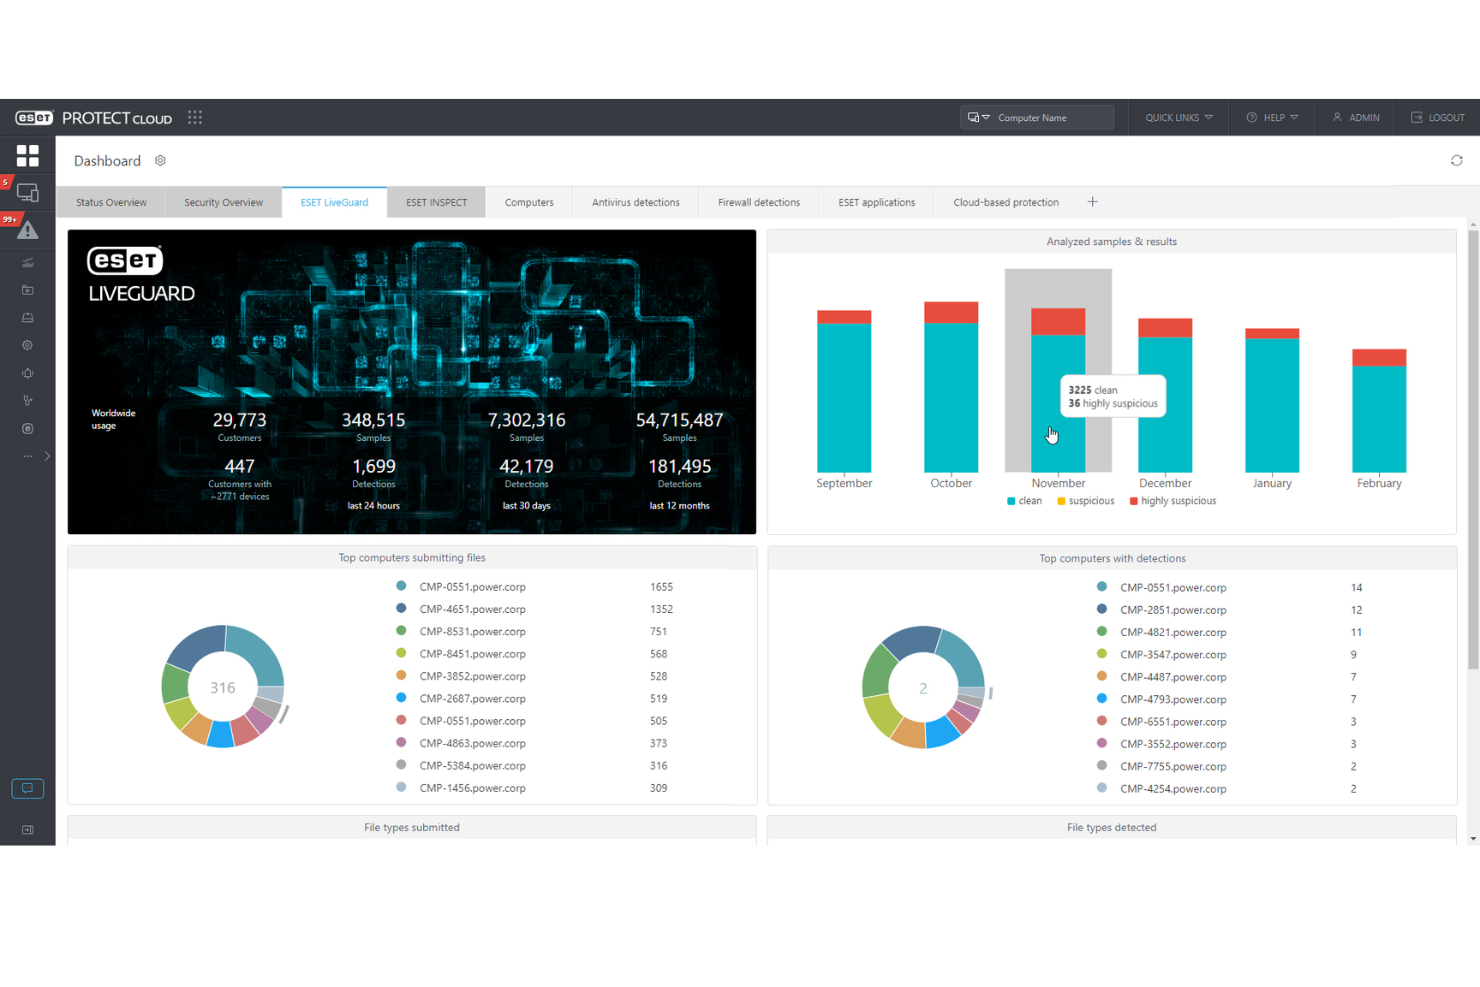
ESET PROTECT Complete provides a robust cybersecurity framework designed to protect businesses from a wide range of digital threats. This solution offers a suite of tools including endpoint protection, cloud sandboxing, and data encryption, aiming to deliver a secure, manageable, and comprehensive defense mechanism against malware, ransomware, and phishing attacks.
As a vulnerability scanning software, ESET PROTECT Complete excels in identifying and addressing potential security weaknesses across an organization's network. It provides detailed vulnerability reports, highlighting areas of concern and recommending actionable steps to mitigate risks. Its scanning engine is both thorough and efficient, ensuring minimal disruption to operational activities while maintaining a high level of security awareness.
ESET PROTECT Complete natively integrates with a variety of tools, including ESET Endpoint Security, ESET Endpoint Antivirus, ESET Security Management Center, ESET Dynamic Threat Defense, ESET Secure Authentication, ESET File Security for Microsoft Windows Server, ESET Mail Security for Microsoft Exchange Server, ESET Full Disk Encryption, Microsoft Active Directory, and SIEM tools.
ESET PROTECT Complete offers pricing upon request + a 30-day free trial.

Invicti
Best for proof-based vulnerability scanning

Invicti is a comprehensive web application and API security tool designed to help enterprises identify and fix vulnerabilities in their web assets. It offers automated discovery and security testing for web applications and APIs, integrating seamlessly into the software development lifecycle.
Invicti offers proof-based scanning technology. Unlike traditional scanners that merely identify potential vulnerabilities, Invicti goes a step further by safely exploiting these vulnerabilities in a read-only manner to confirm their existence. This can reduce false positives, saving development teams valuable time that would otherwise be spent on manual verification.
The software's comprehensive scanning capabilities cover a wide range of vulnerabilities, including those in complex applications and server configurations. Integrations include MuleSoft Anypoint Exchange, Amazon API Gateway, Apigee API hub, Kubernetes, Azure Boards, Bitbucket, Bugzilla, FogBugz, DefectDojo, Freshservice, GitHub, GitLab, Jazz Team Server, and Jira.
Best for continuous vulnerability scanning & pentesting for 9300+ test cases

Astra Pentest is a comprehensive, developer-friendly pentest software that combines continuous vulnerability scanning with manual pentests by security professionals to promote deep testing coverage and zero false positives. The software covers scanning and pentesting for web applications, cloud security, mobile apps, APIs, network security, and blockchain.
The platform can run 9300+ test cases and ensure compliance with standards like GDPR, SOC, HIPAA, ISO, SANS, and OWASP. The vulnerability scanner can also scan logged-in pages, single-page apps, and progressive web apps. Additionally, Astra Pentest offers robust reporting features with the ability to track progress and manage teams.
The platform also has a collaborative dashboard to allow team members to communicate with security experts in real time. Furthermore, the AI-powered chatbot can offer detailed recommendations for fixing vulnerabilities. The software even has a publicly verifiable security certificate to demonstrate a commitment to security. Integrations include Jira, Slack, GitLab, and GitHub. and more.

Qualys
Information security solution that provides deep visibility into global assets

Qualys analyzes misconfigurations and threats across your global tech environment with six sigma accuracy. The system provides real-time alerts on zero-day vulnerabilities, compromised assets, and network irregularities. You can quarantine compromised assets with a single click, buying you more time to investigate and contain an attack.
To protect your IT environment, you need to know which assets are connected to your network. Qualys’ free Global AssetView application helps security teams accomplish this by automatically identifying all known and unknown assets on a network. You can quickly grab detailed information about each asset, including installed software, running services, and vendor lifecycle information. The application also helps with asset organization, enabling teams to categorize assets into product families with custom tagging.
Qualys supports native integrations with AWS, Azure, and Google Cloud.
Pricing is based on several factors, including the number of user licenses, Qualys Cloud Platform Apps, internal web applications, and IP addresses your team will be utilizing.
Best vulnerability scanning software to lower the rate of false positives

New Relic is an all-in-one observability platform that helps you monitor, troubleshoot, and tune your full stack. It allows companies to monitor and enhance their network’s security by identifying possible weaknesses that could be exploited by hackers. With New Relic, you can proactively scan their systems for potential vulnerabilities, getting a comprehensive overview of their security status, which can help in making informed decisions and creating effective cybersecurity strategies.
Moreover, New Relic offers real-time vulnerability scanning, which is exceptionally crucial in today's rapidly-evolving digital landscape where new threats emerge by the minute. With its continuous and automatic scanning, you can quickly detect and resolve any security issues. The platform's vulnerability triage feature gives you information based on criticality. Then, it displays a prioritized list of your vulnerable libraries as well as suggestions on which libraries to update to. This is perfect if you are not sure what to prioritize.
Lastly, New Relic's vulnerability scanning is known for its accuracy. The tool's comprehensive scanning capabilities dramatically reduce false positives, ensuring that the IT team's focus is not diverted by irrelevant alerts. The quality of its reporting also provides teams with all the crucial information needed to address vulnerabilities effectively. By providing a clear picture of the security landscape of a system, New Relic makes it easier.
New Relic integrates with over 600 applications within the categories of application monitoring, infrastructure, security, traffic simulation, logging, AWS, Azure, Google Cloud Services, open-source monitoring, machine learning ops, and Prometheus.

Acunetix
Best for hybrid scanning with AcuSensor Technology

Acunetix is a web application and API security scanner designed to automate security testing for organizations, providing a robust solution for identifying, testing, and addressing vulnerabilities in web applications and APIs.
One of the most notable features is its AcuSensor Technology, which combines black-box scanning techniques with feedback from sensors placed inside the source code. This hybrid approach allows for highly accurate scanning with a low false-positive rate, ensuring that developers can trust the results and focus on genuine vulnerabilities.
The software is designed to be user-friendly, with a Login Sequence Recorder that simplifies the testing of password-protected areas and DeepScan technology that can interpret SOAP, XML, AJAX, and JSON. These features make it easier for security teams to conduct comprehensive scans without extensive manual intervention.

Burp Suite
Vulnerability scanning tool great for crawling JavaScript-heavy applications

Burp Suite offers vulnerability scanning tools to fit the needs of enterprises and individual QA testers. Enterprise DevSecOps teams benefit from Burp Suite’s ability to automate security testing at scale. Manual and automated penetration testing is available in Burp Suite Professional Edition, which was designed for individual use by security engineers and bug bounty hunters.
Burp Suite features a research-based vulnerability scanning tool known as Burp Scanner. PortSwigger’s research team regularly discovers vulnerabilities before hackers can exploit them, providing advanced protection to users.
Burp Scanner also has a powerful crawl engine that can easily navigate obstacles like CSRF tokens and volatile URLs. It can also handle crawling JavaScript-heavy applications other scanners can’t with its embedded Chromium browser.
Development teams can easily integrate Burp Suite into their tech stack with integrations available for Jenkins and Jira.
Burp Suite Enterprise starts at $6,995/year. Burp Suite Professional costs $399 with a free trial available.
Andra programvaror för sårbarhetsskanning
Här är några ytterligare alternativ för programvara för sårbarhetsskanning som inte kom med på min kortlista, men som ändå är värda att titta närmare på:
- Rapid7
Offers external threat intelligence solution with clear and dark web monitoring
- Tenable
Automates threat prioritization based on in-depth threat analysis
- Imperva
Enterprise-grade cybersecurity solution that guards against complex DDoS attacks
- CyCognito
For attacker-perspective vulnerability check
- Microsoft Baseline Security Analyzer
Free Windows security scanner with built-in remediation guidance
- Intruder
Vulnerability scanner that tracks average remediation time
- Probely
Web app and API vulnerability scanner that’s easily accessible to developers
- Cyberpion
EASM solution with multi-layer vulnerability assessment engine
- beSECURE
Leading provider of governance, risk, and managed security solutions
- GFI Languard
Network security software with patch management tool


How I Evaluate Vulnerability Scanning Software
I evaluate tools in two layers: baseline capabilities every scanner must have—like automated CVE detection and asset discovery—and differentiators that separate better options from the rest.
Core Functionality (Table Stakes For This List)
When I'm selecting tools for my list, I rank each one on a scale from 0 (does not offer the functionality) to 5 (excels in this area) for each core functionality listed below. Then, I calculate the tool's total score into a percentage. Each tool needs to achieve a minimum total score of 75% to be considered for inclusion.
- Automated Vulnerability Detection: I check whether the scanner covers multiple asset types—network hosts, web apps, cloud workloads—and how frequently its CVE database updates.
- Asset Discovery & Inventory: A good scanner finds what you forgot about. I look for auto-discovery across hybrid environments with grouping, tagging, and real-time visibility.
- Risk-Based Prioritization: CVSS alone isn't enough. I evaluate whether a tool layers in exploit intelligence like EPSS or CISA KEV data to surface what actually matters first.
- Remediation Guidance & Tracking: Beyond flagging issues, I look for clear fix instructions and status tracking so teams can assign, patch, and verify without jumping between systems.
- Compliance Reporting: I check for pre-built report templates mapped to frameworks like PCI DSS, HIPAA, and ISO 27001 that auditors will actually accept as evidence.
- Integrations & Continuous Scanning: Scheduled scans are a starting point. I evaluate native connections to SIEMs, ticketing tools, CI/CD pipelines, and patch management platforms.
Once I have a list of tools that meet this criteria, I consider what sets each platform apart.
Differentiating Factors (What Sets Vendors Apart)
Here's how I compare and contrast different vendors:
Standout Features
Container and IaC scanning is a major differentiator. Teams deploying with Terraform or running Kubernetes clusters need a scanner that catches misconfigurations before they reach production. I also evaluate attack surface management capabilities, which discover internet-facing assets your org may not even know about. Deployment flexibility matters too. Some environments need lightweight agents on endpoints, while ephemeral cloud workloads call for agentless scanning. Tools that support both give you broader coverage without locking you into one approach.
Beyond Features
Threat intelligence quality varies widely. I look at how often a vendor updates its vulnerability database and whether it incorporates feeds like CISA KEV and EPSS scores. Pricing structure also matters—per-asset licensing can spiral fast in cloud environments where workloads scale daily. I check whether pricing stays predictable as your asset count grows. Finally, I evaluate vendor certifications like SOC 2 Type II and FedRAMP, especially for teams in regulated industries who need assurance that the scanning platform itself meets the same standards it helps enforce.
Så väljer du programvara för sårbarhetsskanning
Det är lätt att fastna i långa funktionslistor och komplexa prisstrukturer. För att hjälpa dig att hålla fokus när du går igenom din unika process för att välja programvara kommer här en checklista över faktorer att tänka på:
| Faktor | Vad du bör tänka på |
|---|---|
| Skalbarhet | Kan programvaran växa med dina behov? Kontrollera om den stöder ökande mängder tillgångar eller ytterligare användare utan försämrad prestanda eller orimligt höga kostnader. |
| Integrationer | Integreras den med dina befintliga verktyg? Kontrollera kompatibiliteten med dina nuvarande system, såsom CI/CD-pipelines, ärendehanteringssystem och kommunikationsplattformar. |
| Anpassningsbarhet | Kan du anpassa programvaran efter dina arbetsflöden? Leta efter alternativ för att anpassa instrumentpaneler, rapporter och aviseringar så att de passar teamets processer och preferenser. |
| Användarvänlighet | Är gränssnittet intuitivt för ditt team? Utvärdera om utformningen minimerar inlärningskurvan och ger snabb åtkomst till viktiga funktioner. |
| Implementering och introduktion | Hur lång tid tar det att komma igång? Ta hänsyn till vilka resurser som behövs för installationen, inklusive utbildningsmaterial, tillgänglig support och eventuella driftstopp under övergången. |
| Kostnad | Är prissättningen transparent och ryms den inom budgeten? Jämför abonnemangsmodeller, dolda avgifter och värdet som erbjuds på varje prisnivå för att säkerställa att den överensstämmer med din ekonomiska plan. |
| Säkerhetsskydd | Erbjuder den tillräckligt skydd för dina data? Granska krypteringsstandarder, policyer för datalagring och efterlevnad av branschregler för att säkerställa att din information förblir säker. |
| Efterlevnadskrav | Uppfyller den branschens regulatoriska standarder? Kontrollera om verktyget stöder ramverk som GDPR, HIPAA eller PCI DSS, vilka är avgörande för laglig efterlevnad inom många sektorer. |
Vad är programvara för sårbarhetsskanning?
Programvara för sårbarhetsskanning är ett verktyg som kontrollerar datorsystem, nätverk och appar efter svagheter som hackare kan utnyttja. IT-team, säkerhetsanalytiker och efterlevnadsansvariga använder den för att upptäcka sådant som föråldrad programvara, saknade uppdateringar eller svaga punkter i inställningarna. Den hjälper dig att upptäcka problem innan angripare gör det, visar vad som bör åtgärdas först och säkerställer att du följer säkerhetsreglerna.
Funktioner
När du väljer programvara för sårbarhetsskanning bör du hålla utkik efter följande viktiga funktioner:
- Automatiserad skanning: Identifierar automatiskt säkerhetssårbarheter utan manuella åtgärder, vilket sparar tid och minskar risken för mänskliga fel.
- Detaljerad rapportering: Tillhandahåller omfattande rapporter som hjälper till att prioritera sårbarheter och styra åtgärdande insatser.
- Integrationsmöjligheter: Ansluter till befintliga verktyg som CI/CD-pipelines och ärendehanteringssystem för att effektivisera arbetsflöden.
- Riskbedömning: Utvärderar allvaret i identifierade sårbarheter för att hjälpa till att prioritera åtgärder utifrån potentiell påverkan.
- Stöd för efterlevnad: Säkerställer att branschregler som GDPR, HIPAA eller PCI DSS följs, vilket upprätthåller den lagstadgade efterlevnaden.
- Anpassningsbara instrumentpaneler: Gör det möjligt för användare att anpassa vyer och rapporter efter specifika behov och preferenser.
- Aviseringar i realtid: Meddelar användare om nyupptäckta sårbarheter eller hot, vilket möjliggör snabba åtgärder.
- Hantering av säkerhetskorrigeringar: Automatiserar distributionen av säkerhetskorrigeringar, vilket minskar arbetsbelastningen för IT-teamen.
- Avancerad genomsökningsteknik: Upptäcker dolda hot i webbapplikationer och säkerställer en heltäckande täckning.
- Bevisbaserad skanning: Bekräftar sårbarheter för att minska antalet falska positiva resultat och fokusera insatserna på verkliga hot.
Fördelar
Implementering av programvara för sårbarhetsskanning ger flera fördelar för ditt team och din verksamhet. Här är några av dem:
- Förbättrad säkerhetsstatus: Regelbundna skanningar hjälper till att identifiera och åtgärda sårbarheter, vilket minskar risken för dataintrång.
- Tidsbesparingar: Automatiserad skanning och hantering av säkerhetskorrigeringar frigör teamets tid för andra viktiga uppgifter.
- Efterlevnad av regelverk: Säkerställer att dina system uppfyller branschstandarder och hjälper till att undvika rättsliga påföljder.
- Riskprioritering: Detaljerade rapporter och riskbedömningar hjälper till att fokusera resurserna på de mest betydande hoten.
- Förbättrat beslutsfattande: Anpassningsbara instrumentpaneler och rapporter ger insikter som stöder välgrundade säkerhetsstrategier.
- Snabb respons på hot: Aviseringar i realtid gör det möjligt för teamet att agera snabbt när nya sårbarheter upptäcks.
- Minskning av falska positiva resultat: Bevisbaserad skanning säkerställer att insatserna riktas mot verkliga hot och inte falska larm.
Kostnader och prissättning
Att välja programvara för sårbarhetsskanning kräver en förståelse av de olika prismodellerna och planerna som finns tillgängliga. Kostnaderna varierar beroende på funktioner, teamstorlek, tillägg och annat. Tabellen nedan sammanfattar vanliga planer, deras genomsnittliga priser och typiska funktioner som ingår i programvarulösningar för sårbarhetsskanning:
Jämförelsetabell över planer för programvara för sårbarhetsskanning
| Plantyp | Genomsnittligt pris | Vanliga funktioner |
|---|---|---|
| Gratisplan | $0 | Grundläggande skanningsfunktioner, begränsad rapportering och support från communityn. |
| Personlig plan | $5-$25/användare/månad | Automatiserad skanning, anpassningsbara instrumentpaneler och e-postaviseringar. |
| Företagsplan | $25-$100/användare/månad | Avancerad rapportering, integrationsmöjligheter och stöd för efterlevnad. |
| Stor företagsplan | $100-$500/användare/månad | Full tillgång till funktioner, dedikerad support, avancerad analys och anpassade integrationer. |
Vanliga frågor om programvara för sårbarhetsskanning
Här är några svar på vanliga frågor om programvara för sårbarhetsskanning:
Vad är skillnaden mellan sårbarhetsskanning och penetrationstestning?
Sårbarhetsskanning identifierar potentiella säkerhetssvagheter i ditt system, medan penetrationstestning innebär att dessa sårbarheter aktivt utnyttjas för att bedöma deras påverkan. Skanning är vanligtvis automatiserad och ger en bred överblick, medan penetrationstestning är mer manuell och detaljerad. Använd sårbarhetsskanning för regelbundna kontroller och penetrationstestning för djupgående analyser.
Hur ofta bör du köra sårbarhetsskanningar?
Kör sårbarhetsskanningar minst en gång i månaden, men oftare om dina system ändras ofta. Regelbunden skanning hjälper dig att upptäcka nya sårbarheter och hålla dina säkerhetsåtgärder uppdaterade. Om du arbetar i en starkt reglerad bransch kan du behöva skanna oftare för att uppfylla kraven på efterlevnad.
Kan programvara för sårbarhetsskanning upptäcka alla säkerhetsproblem?
Nej, programvara för sårbarhetsskanning kan inte upptäcka alla säkerhetsproblem. Även om den identifierar kända sårbarheter kan den missa nolldagshot eller nyligen upptäckta sårbarheter. Kombinera skanning med andra säkerhetsåtgärder, som penetrationstestning och övervakning, för att skapa ett mer heltäckande säkerhetsarbete.
Är programvara för sårbarhetsskanning svår att konfigurera?
Nej, de flesta moderna programvaror för sårbarhetsskanning är utformade för att vara användarvänliga och snabba att konfigurera. Vanligtvis följer du en guidad konfigurationsprocess, och många verktyg erbjuder mallar eller automatiserade konfigurationer. Mer avancerade funktioner kan dock kräva en djupare förståelse av din nätverksarkitektur.
Nästa steg:
Om du håller på att undersöka programvara för sårbarhetsskanning kan du kontakta en rådgivare från SoftwareSelect för kostnadsfria rekommendationer.
Du fyller i ett formulär och har ett kort samtal där de går igenom dina specifika behov. Därefter får du en kortlista med programvara att granska. De hjälper dig även genom hela köpprocessen, inklusive prisförhandlingar.