
Red Sift-Bewertung: Vorteile, Nachteile, Funktionen und Preise erklärt
Dive into my hands-on take: here’s how Red Sift’s DMARC platform doesn’t just crunch email data—it actually transforms how you spot, investigate, and resolve email threats in 2026.

Wir bewerten Tools unabhängig; Provisionen helfen, unsere Tests zu finanzieren. Siehe unsere Transparenzrichtlinie und unsere Methodik.
Red Sift is a DMARC software for security and IT teams that need to authenticate outbound email, monitor sending sources, and enforce DMARC, SPF, DKIM, and BIMI across their domains. I'd reach for it over a tool like Valimail when you want deeper visibility into your email ecosystem paired with broader domain and certificate discovery, rather than a narrower DMARC-only workflow. Red Sift OnDMARC is the piece that drives DMARC enforcement, and it arrives bundled with the wider domain-security tooling rather than sold separately.
Red Sift Evaluation Summary
4.8/5
- From $9/month (billed annually)
- Free trial available
Warum Sie unseren Software-Empfehlungen vertrauen können
6,700+
Reviews
20
Industry experts
16+
Evaluation factors
14
Years
Unser Team testet und bewertet Software seit 2012. Als Tech-Führungskräfte wissen wir selbst, wie schwierig – und wichtig – es ist, die richtige Software auszuwählen.
Für diesen Leitfaden haben wir Tools mithilfe von praktischen Tests und unabhängiger Recherche bewertet und dabei unsere Bewertungskriterien angewendet.
Unsere Bewertungen spiegeln unser menschliches redaktionelles Urteilsvermögen wider, keine Verkaufsstrategie.
Expertenprüfer:
- Paulo Gardini MiguelTech-Direktor
 Tim FisherVP für KI
 Gabriel RosasTech Lead & Software-Architekt
 Christhian GruhnTech Lead & Plattform-Architekt

Red Sift Overview
I think Red Sift stands out for its rich reporting, automated DMARC setup, and unified visibility across multiple domains, making it easy to judge your compliance posture at a glance. I find its clear interface and responsive support make initial onboarding smooth. It writes and validates the DNS records for you, which is where most rollouts stall and where email deliverability quietly suffers. Pricing lands on the higher end, and you might miss granular API integrations available elsewhere, but if you’re selecting a solution for complex enterprise or multi-brand environments, Red Sift is a strong, reliable choice.
Pros
- Offers BIMI automation and hosted MTA-STS management
- Gives detailed reporting for threat detection and source analysis
- Supports monitoring multiple domains and subdomain activity in a single dashboard
Cons
- Most plans require a quote
- Can overwhelm small teams with the feature set
- Lacks in-depth guided remediation for advanced authentication issues
Is Red Sift Right For Your Needs?
Who Would be a Good Fit for Red Sift?
Teams in regulated industries, companies managing a high volume of external email, and those with limited IT resources are going to see real value with Red Sift. Its guided onboarding, automation, and clear dashboards help lean security teams, while deep integrations appeal to organizations with complex compliance or reporting needs. If email impersonation is a live threat to your brand rather than a theoretical one, the breadth here starts to justify itself. If email authentication is non-negotiable or you prioritize proactive security, Red Sift stands out.
- Financial Services FirmsRed Sift delivers visual DMARC analytics and granular reporting that support industry regulatory requirements and help prevent phishing attacks.
- Midsize EnterprisesFeature-rich plans and API access suit businesses with multiple domains, supporting IT teams that need scalable and hands-off DMARC management.
- Public SectorGovernment and education organizations get value from Red Sift’s automation and compliance tools, which streamline reporting and lower management workload.
- Managed Service ProvidersThe multi-tenant support and automated alerts allow MSPs to serve multiple customers and reduce overhead.
- Security Operations TeamsSIEM and SOAR integrations enable proactive incident detection and response directly from the same interface.
- Companies With No Security StaffAutomated workflows, easy onboarding, and strong support mean non-specialists can set up and manage DMARC fast.
Who Would be a Bad Fit for Red Sift?
Red Sift isn’t ideal if you just need one-off DMARC lookups, operate at a very small scale, or want total hands-on script control. Organizations with advanced in-house capabilities or teams outside traditional corporate environments may also find it limiting. If you have no subdomain estate to protect and domain takeovers aren’t on your risk register, the breadth is wasted. If you work in a niche sector, it pays to confirm compatibility first.
- FreelancersThe feature set and cost overshoot what solo users or tiny businesses typically require for basic domain monitoring.
- Startups With No DomainsWithout multiple domains or established sending infrastructure, Red Sift’s tools go underused.
- DIY Security TeamsTeams that build and script everything themselves may find Red Sift’s managed platform too restrictive.
- Manufacturing With No Email FocusIndustries that rarely use outbound email for customer contact won’t benefit from DMARC analytics or reporting.
- Small CharitiesOrganizations with little to no security budget may struggle to justify the spend, even with entry-level plans.
- Informal Clubs or GroupsRed Sift is overpowered for volunteer groups or clubs that don’t deal with sophisticated email infrastructure or threat models.
Unsere Bewertungsmethodik
Wie wir Werkzeuge testen & bewerten
Wir haben Jahre damit verbracht, unser System zur Softwareprüfung und -bewertung aufzubauen, zu verfeinern und zu verbessern. Das Bewertungsraster ist darauf ausgelegt, die Feinheiten der Softwareauswahl und Effektivität eines Tools einzufangen, wobei wir uns auf kritische Aspekte des Entscheidungsprozesses konzentrieren.
Nachfolgend sehen Sie genau, wie unser Test- und Bewertungssystem anhand von sieben Kriterien funktioniert. Es ermöglicht uns eine unparteiische Bewertung der Software basierend auf Grundfunktionalität, besonderen Funktionen, Benutzerfreundlichkeit, Onboarding, Kundensupport, Integrationen, Kundenbewertungen und Preis-Leistungs-Verhältnis.
Grundfunktionalität (25 % der Endbewertung)
Der Ausgangspunkt unserer Bewertung ist immer die Grundfunktionalität des Werkzeugs. Verfügt es über die grundlegenden Funktionen und Merkmale, die ein Benutzer erwarten würde? Sind grundlegende Funktionen auf höherpreisige Tarife beschränkt? Im Kern erwarten wir, dass ein Tool den Basisfähigkeiten seiner Konkurrenten standhält.
Besondere Features (25 % der Endbewertung)
Anschließend bewerten wir ungewöhnliche, herausragende Funktionen, die über die typische Grundfunktionalität von Tools dieser Art hinausgehen. Eine hohe Bewertung zeigt spezialisierte oder einzigartige Eigenschaften, die das Produkt schneller, effizienter oder für den Nutzer wertvoller machen.
Wir bewerten außerdem, wie einfach sich das Tool mit anderen üblichen Werkzeugen im Technologie-Stack integrieren lässt, um die Funktionalität und den Nutzen der Software zu erweitern. Tools mit vielen nativen Integrationen, Drittanbieter-Anbindungen und API-Zugang zur Erstellung kundenspezifischer Integrationen erhalten die besten Bewertungen.
Benutzerfreundlichkeit (10 % der Endbewertung)
Wir betrachten, wie schnell und einfach Aufgaben aus dem Bereich der Grundfunktionalität mit dem Tool erledigt werden können. Gut bewertete Software ist durchdacht gestaltet, intuitiv bedienbar, bietet mobile Apps, Vorlagen und lässt relativ komplexe Aufgaben einfach erscheinen.
Onboarding (10 % der Endbewertung)
Wir wissen, wie wichtig die schnelle Einführung eines neuen Tools für das Team ist, daher bewerten wir, wie leicht sich ein Werkzeug mit minimalem Training erlernen und nutzen lässt. Wir bewerten, wie schnell ein Teammitglied ohne Vorerfahrung anfangen kann. Hoch bewertete Lösungen benötigen wenig bis gar keine Unterstützung.
Kundensupport (10 % der Endbewertung)
Wir prüfen, wie schnell und einfach man bei Problemen Hilfe per Telefon, Live-Chat oder Wissensdatenbank erhält. Tools und Anbieter mit Echtzeit-Support werden besser bewertet, während Chatbots schlechter abschneiden.
Kundenbewertungen (10 % der Endbewertung)
Neben unserer eigenen Prüfung beziehen wir den Net Promoter Score aktueller und ehemaliger Kunden mit ein. Wir bewerten, wie wahrscheinlich es ist, dass sie sich erneut für das Werkzeug entscheiden würden. Hoch bewertete Software weist einen hohen Net Promoter Score auf.
Preis-Leistungs-Verhältnis (10 % der Endbewertung)
Abschließend vergleichen wir unter Berücksichtigung aller Kriterien den durchschnittlichen Preis der Einstiegspakete mit den Grundfunktionen und bewerten den Mehrwert aus den anderen Bewertungsbereichen. Software, die mehr fürs gleiche Geld bietet, schneidet besser ab.
Core Features
Automated DMARC Report Analysis
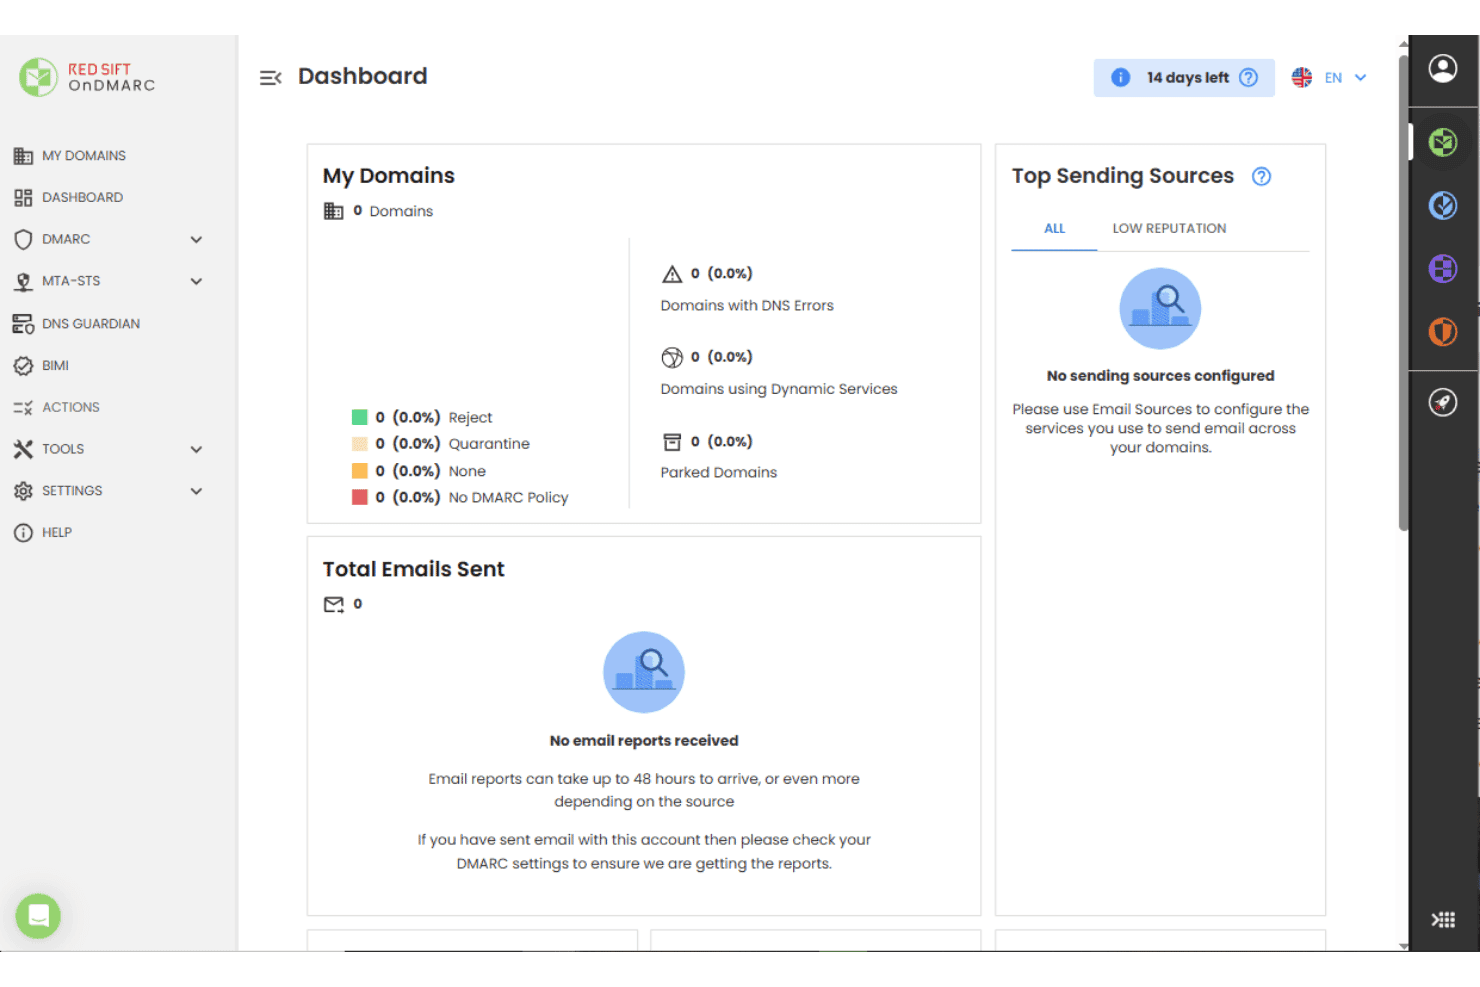
Red Sift auto-collects, aggregates, and analyzes DMARC reports to surface threat trends. You see source-specific insights without needing manual parsing.
BIMI and MTA-STS Automation
The platform manages BIMI records, VMC provisioning, and hosted MTA-STS policies out of the box. This streamlines brand authentication and transport security.
Multi-Domain Monitoring
Monitor and compare authentication activity across all domains in one dashboard. DNS Guardian watches for subdomain takeover attempts as that estate grows.
Threat Intelligence Integration
Red Sift correlates report data with global threat feeds to identify malicious senders fast. Teams spot business email compromise sooner than with raw logs.
Visual Policy Builder
A drag-and-drop interface lets you create and update DMARC, SPF records, and DKIM policies. This reduces misconfigurations and simplifies enforcement for non-experts.
Real-Time Alerts and Recommendations
Actionable alerts and practical guidance land when new risks, policy failures, or lookalike domains appear. This helps you remediate before issues escalate.
Ease of Use
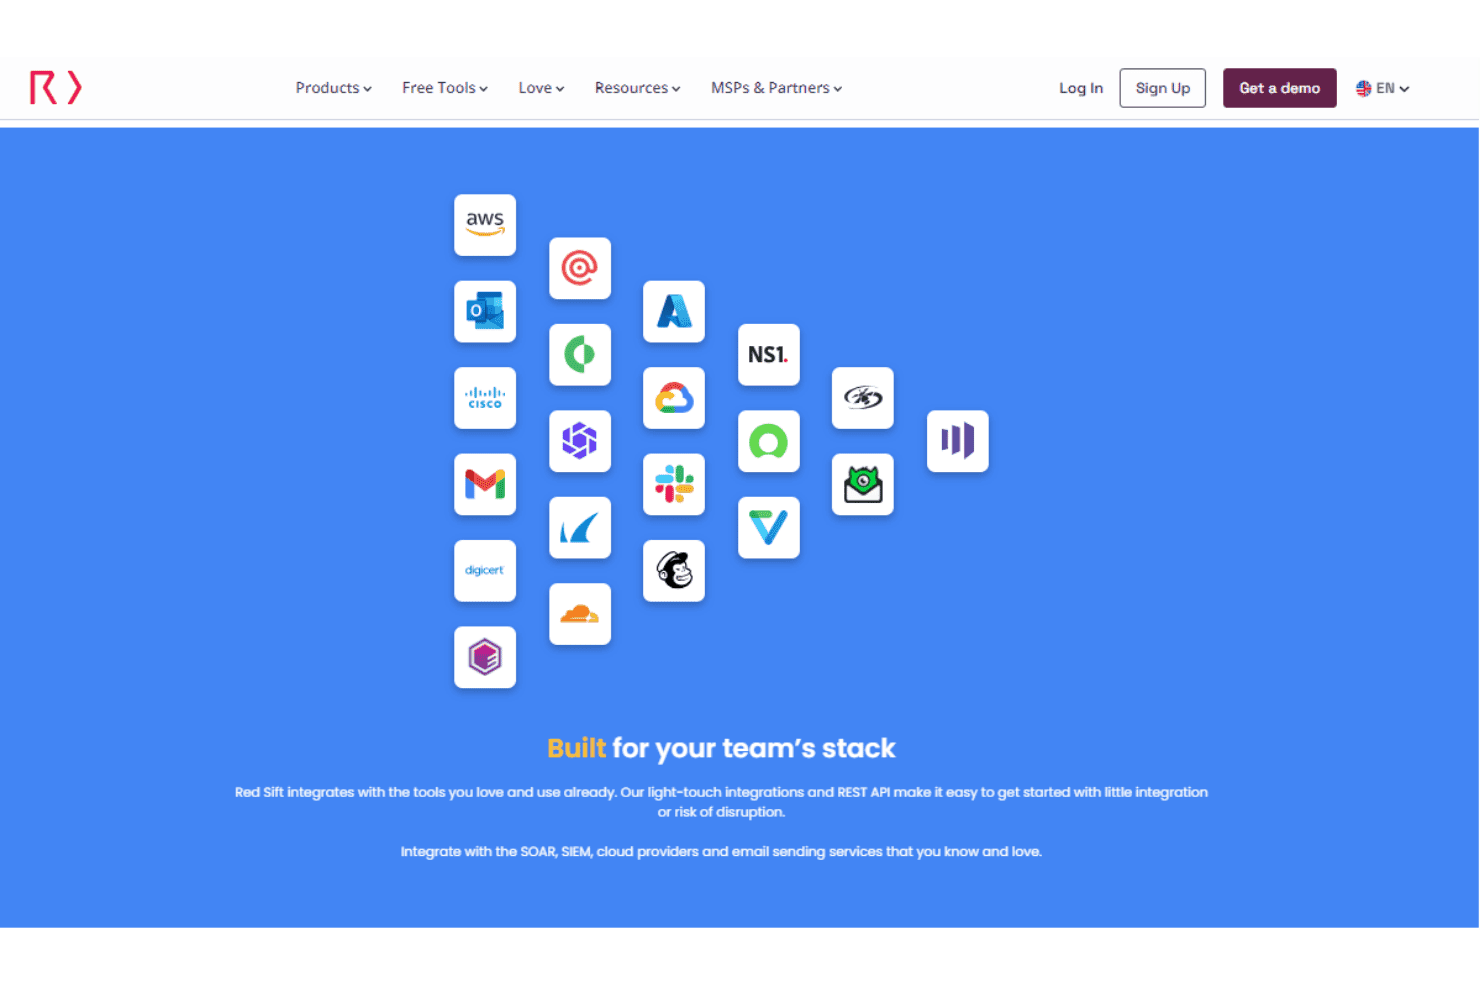
Red Sift feels approachable for both technical and non-technical users thanks to its clear dashboards, guided setup flows, and policy wizards. I think the real value shows up in how quickly you can move from DMARC data to prioritized actions, with plenty of context provided in alerts and reports. Dynamic SPF is a small mercy here too, since it keeps you inside the 10 SPF lookup limit without hand-editing records every time a vendor changes. Some users say the breadth of features can be a bit much early on, but most find it intuitive after initial onboarding.

Integrations
Red Sift integrates with AWS, Microsoft Outlook, Cisco, Gmail, DigiCert, Cloudflare, and NS1, alongside supported SIEM, SOAR, cloud, and email-sending services.
Red Sift also provides light-touch integrations and a REST API for connecting its platform with external tools and custom workflows.
Red Sift Specs
- 2-Factor Authentication: Yes
- Access Management: Yes
- Anti-Virus: No
- API: Yes
- Audit Management: Yes
- Audit Trail: Yes
- Batch Permissions & Access: No
- Compliance Tracking: Yes
- Dashboard: Yes
- Data Export: Yes
- Data Import: Yes
- DDoS Protection: No
- External Integrations: Yes
- File Sharing: No
- File Transfer: No
- Firewall: No
- Incident Management: No
- Malware Protection: No
- Multi-User: Yes
- Notifications: Yes
- Password & Access Management: Yes
- Policy Management: Yes
- Real-time Alerts: Yes
- Report & Compliance: Yes
- Risk Assessment: Yes
- Security Migration: No
- Threat Detection: Yes
- Workflow Management: No


